THE GRC STACK V 2 0 Understanding and
- Slides: 114
THE GRC STACK (V 2. 0) Understanding and applying the CSA GRC stack for payoffs and protection A learning workshop from the CSA © 2011 Cloud Security Alliance, Inc. All rights reserved.
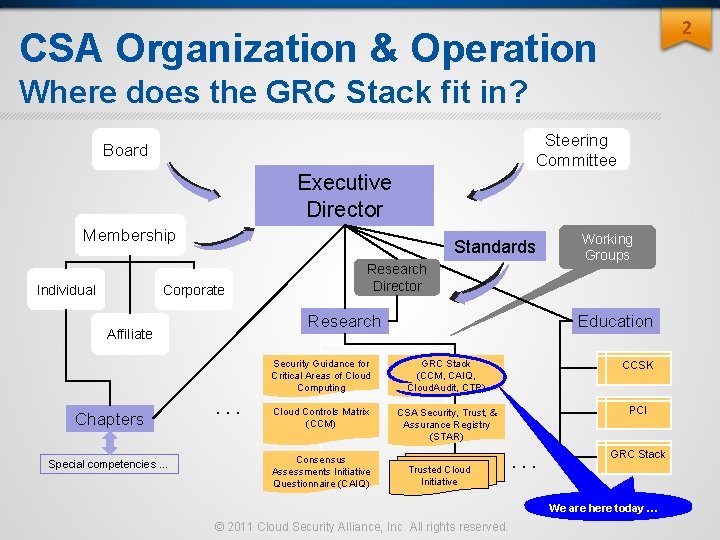
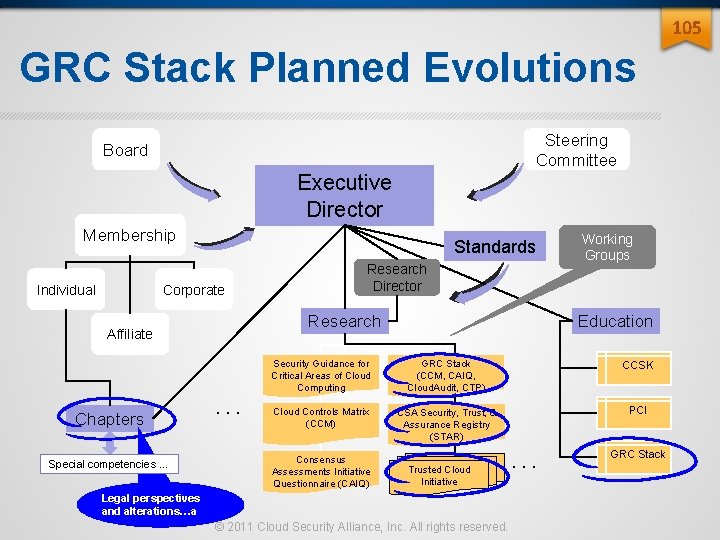
2 CSA Organization & Operation Where does the GRC Stack fit in? Steering Committee Board Executive Director Membership Individual Standards Corporate Research Affiliate Chapters Special competencies … Research Director . . . Working Groups Education Security Guidance for Critical Areas of Cloud Computing GRC Stack (CCM, CAIQ, Cloud. Audit, CTP) CCSK Cloud Controls Matrix (CCM) CSA Security, Trust, & Assurance Registry (STAR) PCI Consensus Assessments Initiative Questionnaire (CAIQ) Trusted Cloud Initiative . . . GRC Stack We We are here today … … © 2011 Cloud Security Alliance, Inc. All rights reserved.
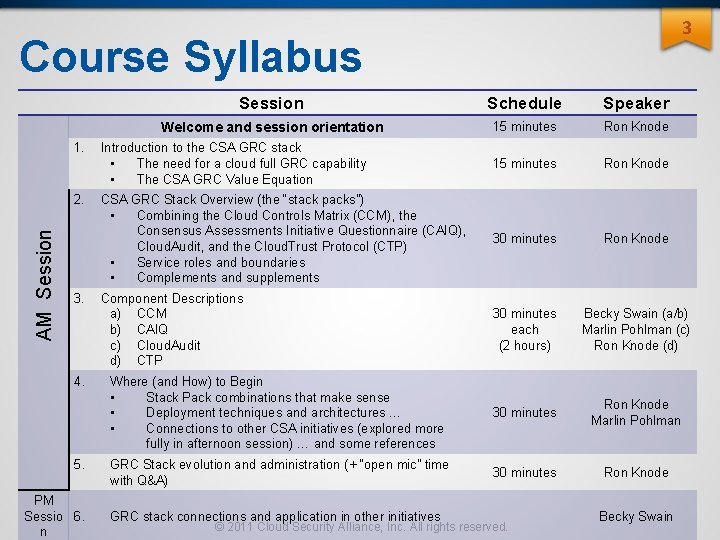
3 Course Syllabus 1. AM Session 2. 3. 4. 5. PM Sessio 6. n Session Schedule Speaker Welcome and session orientation 15 minutes Ron Knode Introduction to the CSA GRC stack • The need for a cloud full GRC capability • The CSA GRC Value Equation 15 minutes Ron Knode CSA GRC Stack Overview (the “stack packs”) • Combining the Cloud Controls Matrix (CCM), the Consensus Assessments Initiative Questionnaire (CAIQ), Cloud. Audit, and the Cloud. Trust Protocol (CTP) • Service roles and boundaries • Complements and supplements 30 minutes Ron Knode Component Descriptions a) CCM b) CAIQ c) Cloud. Audit d) CTP 30 minutes each (2 hours) Becky Swain (a/b) Marlin Pohlman (c) Ron Knode (d) Where (and How) to Begin • Stack Pack combinations that make sense • Deployment techniques and architectures … • Connections to other CSA initiatives (explored more fully in afternoon session) … and some references 30 minutes Ron Knode Marlin Pohlman GRC Stack evolution and administration (+ “open mic” time with Q&A) 30 minutes Ron Knode GRC stack connections and application in other initiatives © 2011 Cloud Security Alliance, Inc. All rights reserved. Becky Swain
SESSION 1 // Why a cloud GRC stack? The GRC stack value equation © 2011 Cloud Security Alliance, Inc. All rights reserved.
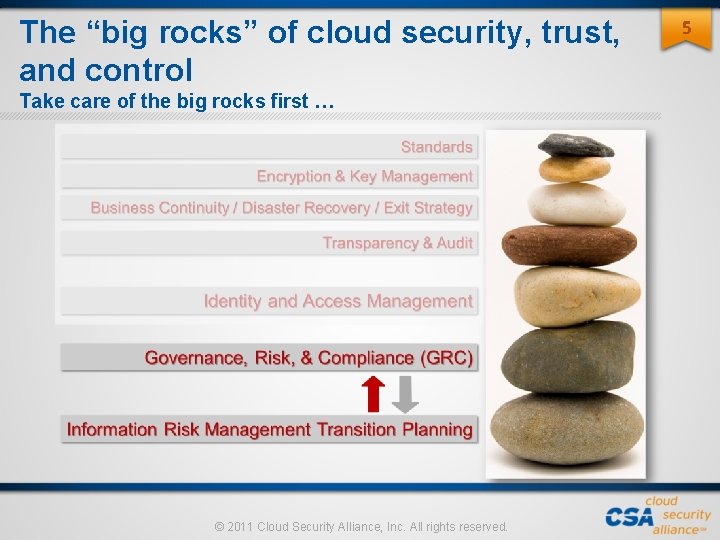
The “big rocks” of cloud security, trust, and control Take care of the big rocks first … © 2011 Cloud Security Alliance, Inc. All rights reserved. 5
Key Cloud Security Problems From CSA Top Threats Research: –Trust: Lack of Provider transparency, impacts Governance, Risk Management, Compliance, and the capture of real value –Data: Leakage, Loss or Storage in unfriendly geography –Insecure Cloud software –Malicious use of Cloud services –Account/Service Hijacking –Malicious Insiders –Cloud-specific attacks 6
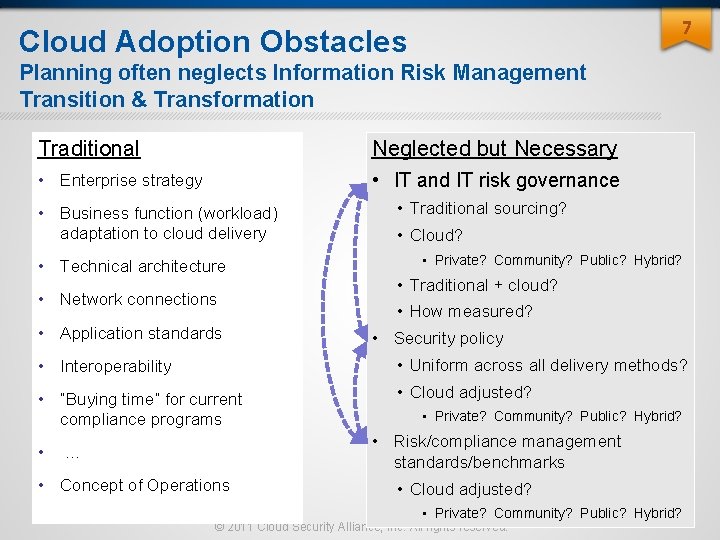
7 Cloud Adoption Obstacles Planning often neglects Information Risk Management Transition & Transformation Traditional Neglected but Necessary • Enterprise strategy • IT and IT risk governance • Business function (workload) adaptation to cloud delivery • Technical architecture • Network connections • Application standards • Traditional sourcing? • Cloud? • Private? Community? Public? Hybrid? • Traditional + cloud? • How measured? • Security policy • Interoperability • Uniform across all delivery methods? • “Buying time” for current compliance programs • Cloud adjusted? • • Private? Community? Public? Hybrid? • Risk/compliance management standards/benchmarks … • Concept of Operations • Cloud adjusted? • Private? Community? Public? Hybrid? © 2011 Cloud Security Alliance, Inc. All rights reserved.
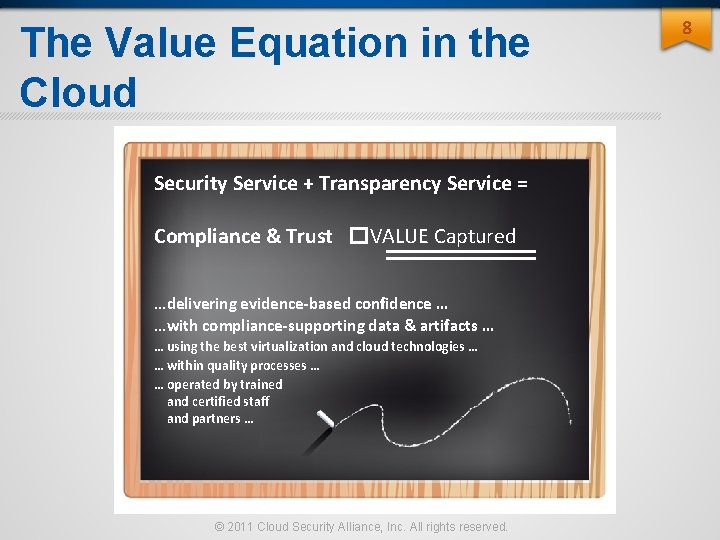
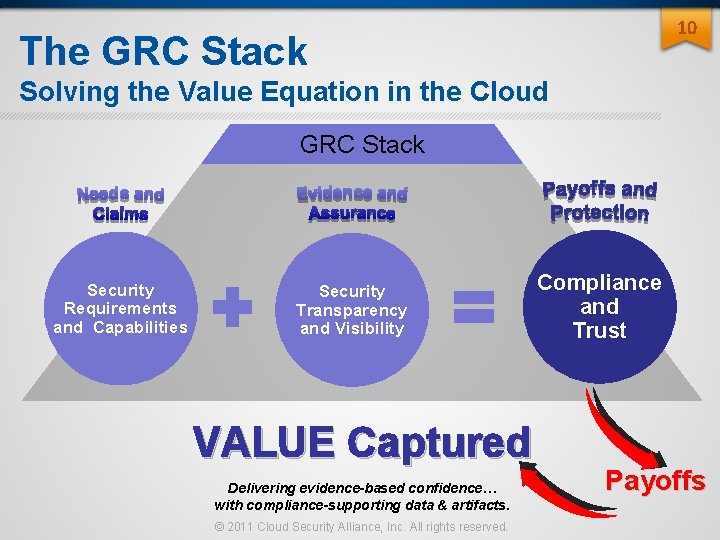
The Value Equation in the Cloud Security Service + Transparency Service = Compliance & Trust �VALUE Captured … delivering evidence-based confidence … … with compliance-supporting data & artifacts … … using the best virtualization and cloud technologies … … within quality processes … … operated by trained and certified staff and partners … © 2011 Cloud Security Alliance, Inc. All rights reserved. 8
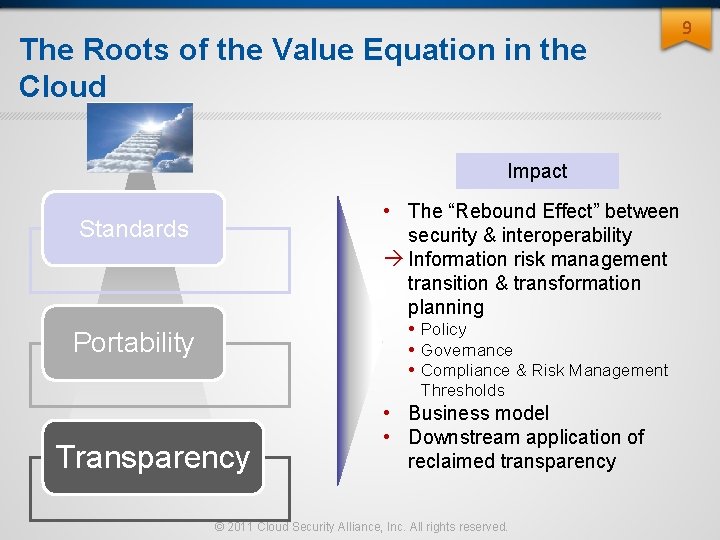
The Roots of the Value Equation in the Cloud Impact • The “Rebound Effect” between Standards security & interoperability Information risk management transition & transformation planning • Policy • Governance • Compliance & Risk Management Portability Thresholds Transparency • Business model • Downstream application of reclaimed transparency © 2011 Cloud Security Alliance, Inc. All rights reserved. 9
10 The GRC Stack Solving the Value Equation in the Cloud GRC Stack Security Requirements and Capabilities Security Transparency and Visibility VALUE Captured Delivering evidence-based confidence… with compliance-supporting data & artifacts. © 2011 Cloud Security Alliance, Inc. All rights reserved. Compliance and Trust Payoffs
SESSION 2 // GRC Stack Overview “The Stack Packs” © 2011 Cloud Security Alliance, Inc. All rights reserved.
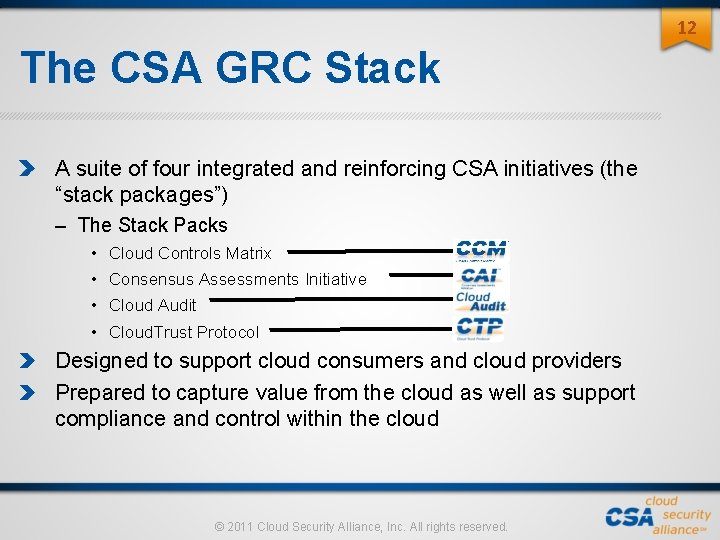
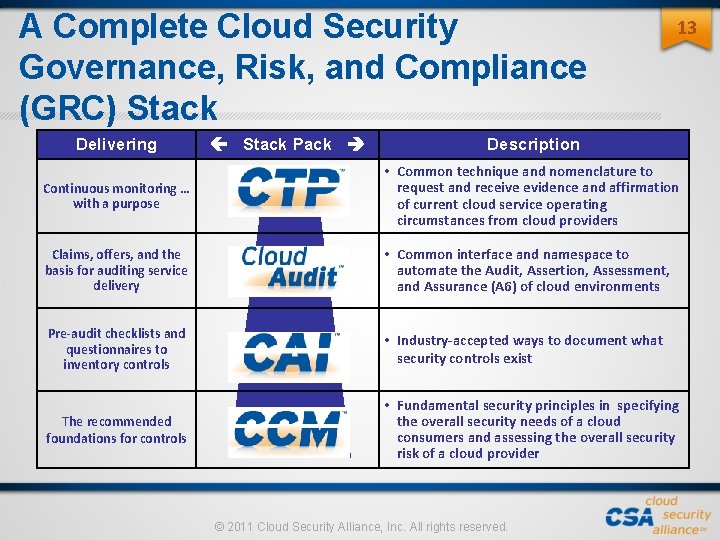
12 The CSA GRC Stack A suite of four integrated and reinforcing CSA initiatives (the “stack packages”) – The Stack Packs • Cloud Controls Matrix • Consensus Assessments Initiative • Cloud Audit • Cloud. Trust Protocol Designed to support cloud consumers and cloud providers Prepared to capture value from the cloud as well as support compliance and control within the cloud © 2011 Cloud Security Alliance, Inc. All rights reserved.
A Complete Cloud Security Governance, Risk, and Compliance (GRC) Stack Delivering Stack Pack 13 Description Continuous monitoring … with a purpose • Common technique and nomenclature to request and receive evidence and affirmation of current cloud service operating circumstances from cloud providers Claims, offers, and the basis for auditing service delivery • Common interface and namespace to automate the Audit, Assertion, Assessment, and Assurance (A 6) of cloud environments Pre-audit checklists and questionnaires to inventory controls • Industry-accepted ways to document what security controls exist The recommended foundations for controls • Fundamental security principles in specifying the overall security needs of a cloud consumers and assessing the overall security risk of a cloud provider © 2011 Cloud Security Alliance, Inc. All rights reserved.
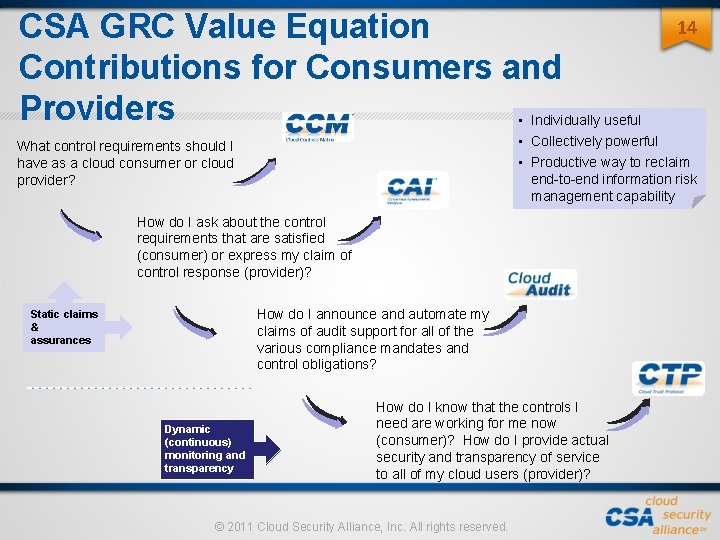
CSA GRC Value Equation Contributions for Consumers and Providers • Individually useful • Collectively powerful • Productive way to reclaim end-to-end information risk management capability What control requirements should I have as a cloud consumer or cloud provider? How do I ask about the control requirements that are satisfied (consumer) or express my claim of control response (provider)? How do I announce and automate my claims of audit support for all of the various compliance mandates and control obligations? Static claims & assurances Dynamic (continuous) monitoring and transparency 14 How do I know that the controls I need are working for me now (consumer)? How do I provide actual security and transparency of service to all of my cloud users (provider)? © 2011 Cloud Security Alliance, Inc. All rights reserved.
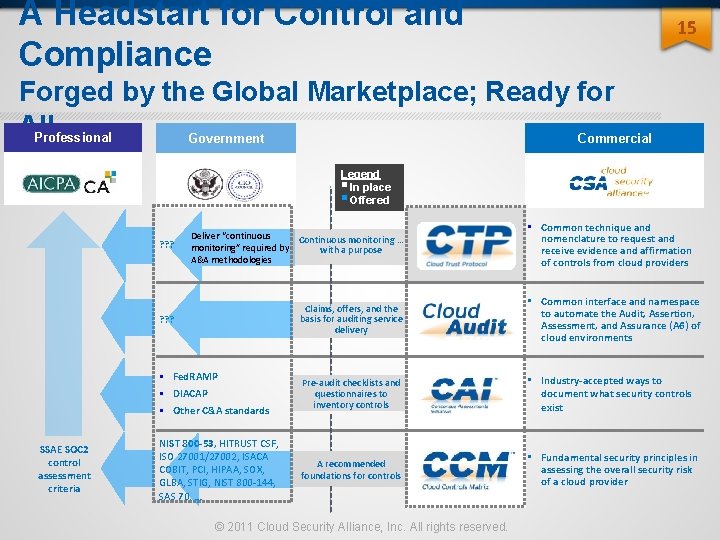
A Headstart for Control and Compliance 15 Forged by the Global Marketplace; Ready for All Professional Government Commercial Legend § In place § Offered SSAE SOC 2 control assessment criteria • Common technique and nomenclature to request and receive evidence and affirmation of controls from cloud providers ? ? ? Deliver “continuous Continuous monitoring … monitoring” required by with a purpose A&A methodologies ? ? ? Claims, offers, and the basis for auditing service delivery • Common interface and namespace to automate the Audit, Assertion, Assessment, and Assurance (A 6) of cloud environments • Fed. RAMP • DIACAP • Other C&A standards Pre-audit checklists and questionnaires to inventory controls • Industry-accepted ways to document what security controls exist NIST 800 -53, HITRUST CSF, ISO 27001/27002, ISACA COBIT, PCI, HIPAA, SOX, GLBA, STIG, NIST 800 -144, SAS 70, … A recommended foundations for controls • Fundamental security principles in assessing the overall security risk of a cloud provider © 2011 Cloud Security Alliance, Inc. All rights reserved.
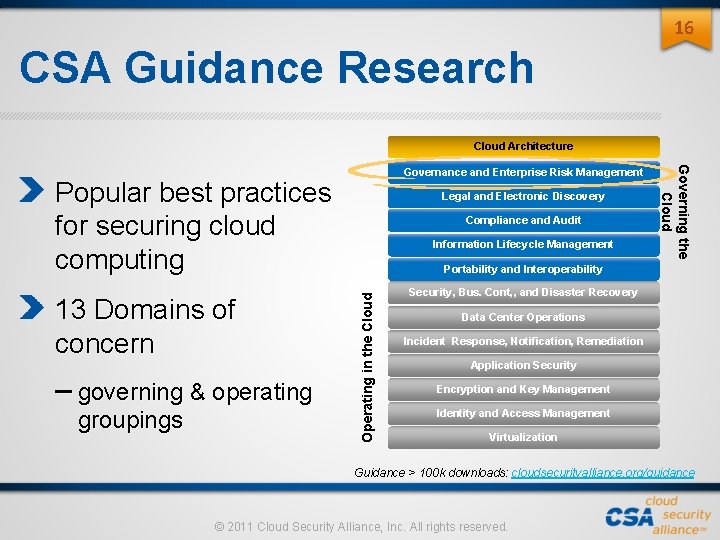
16 CSA Guidance Research Cloud Architecture Popular best practices for securing cloud computing – governing & operating groupings Compliance and Audit Information Lifecycle Management Portability and Interoperability Operating in the Cloud 13 Domains of concern Legal and Electronic Discovery Governing the Cloud Governance and Enterprise Risk Management Security, Bus. Cont, , and Disaster Recovery Data Center Operations Incident Response, Notification, Remediation Application Security Encryption and Key Management Identity and Access Management Virtualization Guidance > 100 k downloads: cloudsecurityalliance. org/guidance © 2011 Cloud Security Alliance, Inc. All rights reserved.
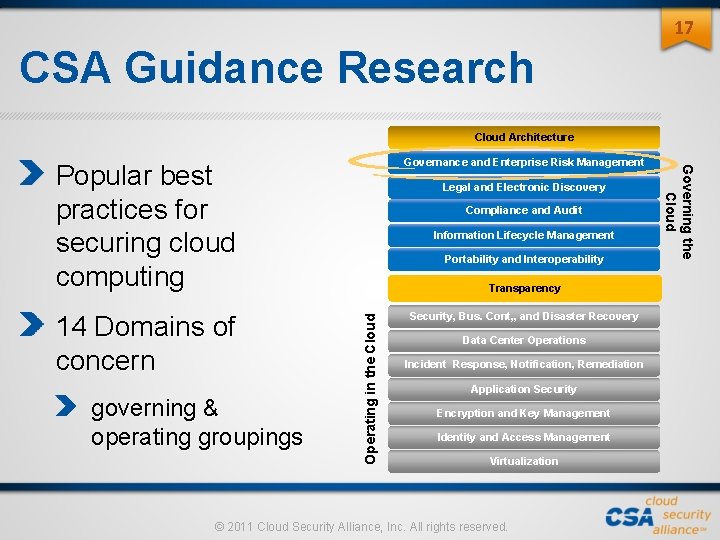
17 CSA Guidance Research Cloud Architecture 14 Domains of concern Security, Bus. Cont, , and Disaster Recovery Compliance and Audit Information Lifecycle Management Portability and Interoperability Transparency Operating in the Cloud governing & operating groupings Legal and Electronic Discovery Data Center Operations Incident Response, Notification, Remediation Application Security Encryption and Key Management Identity and Access Management Virtualization © 2011 Cloud Security Alliance, Inc. All rights reserved. Governing the Cloud Popular best practices for securing cloud computing Governance and Enterprise Risk Management
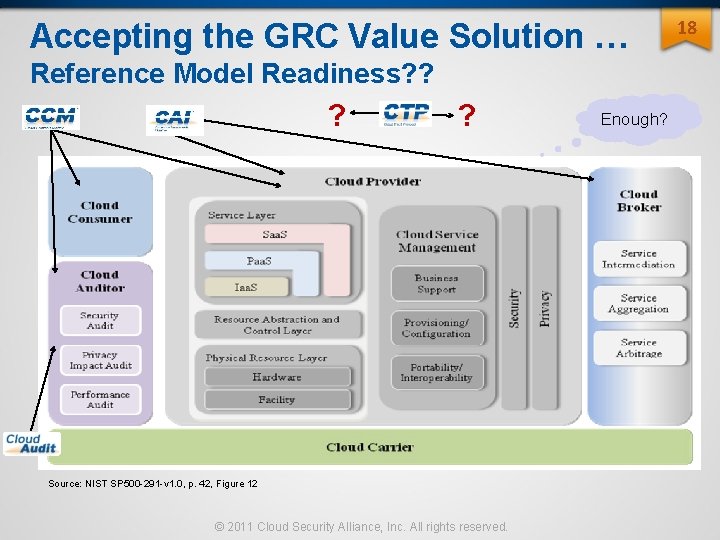
Accepting the GRC Value Solution … Reference Model Readiness? ? ? ? Source: NIST SP 500 -291 -v 1. 0, p. 42, Figure 12 © 2011 Cloud Security Alliance, Inc. All rights reserved. Enough? 18
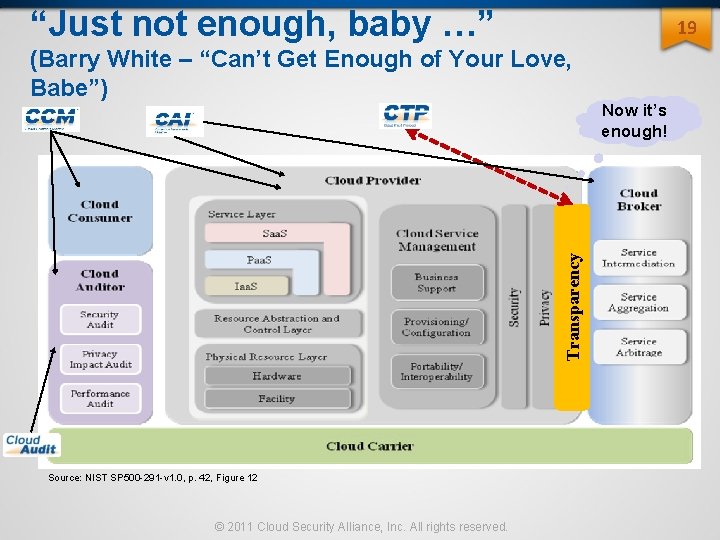
“Just not enough, baby …” 19 Transparency (Barry White – “Can’t Get Enough of Your Love, Babe”) Source: NIST SP 500 -291 -v 1. 0, p. 42, Figure 12 © 2011 Cloud Security Alliance, Inc. All rights reserved. Now it’s enough!
SESSION 3 // Component Descriptions © 2011 Cloud Security Alliance, Inc. All rights reserved.
THE CLOUD CONTROLS MATRIX © 2011 Cloud Security Alliance, Inc. All rights reserved.
22 Cloud Controls Matrix (CCM) Leadership Team Becky Swain – EKKO Consulting Philip Agcaoili – Cox Communications Marlin Pohlman – EMC, RSA Kip Boyle – CSA V 1. 0 (Apr 2010), v 1. 1 (Dec 2010, v 1. 2 (Aug 2011), V 2. 0 (2012) Controls baselined and mapped to: COBIT HIPAA/HITECH Act ISO/IEC 27001 -2005 NISTSP 800 -53 Fed. RAMP PCI DSSv 2. 0 BITS Shared Assessments Jericho Forum NERC CIP © 2011 Cloud Security Alliance, Inc. All rights reserved.
23 What is the CCM? First ever baseline control framework specifically designed for managing risk in the Cloud Supply Chain: – Addressing the inter and intra-organizational challenges of persistent information security by clearly delineating control ownership. – Providing an anchor point and common language for balanced measurement of security and compliance postures. – Providing the holistic adherence to the vast and ever evolving landscape of global data privacy regulations and security standards. Serves as the basis for new industry standards and certifications. © 2011 Cloud Security Alliance, Inc. All rights reserved.
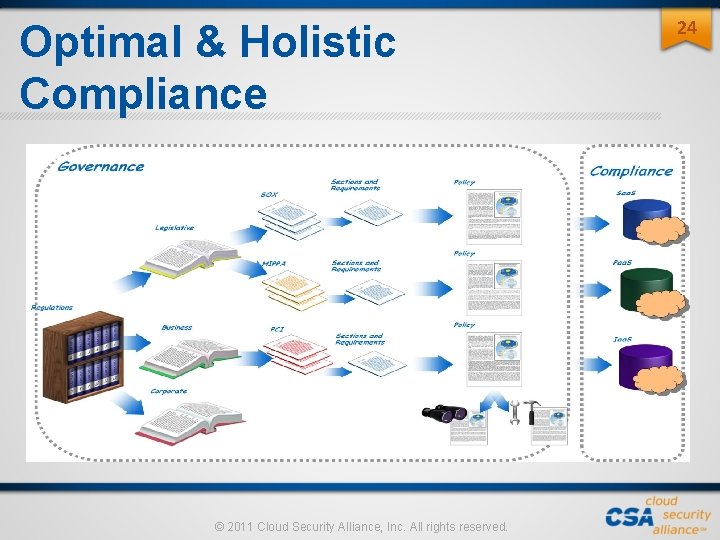
Optimal & Holistic Compliance © 2011 Cloud Security Alliance, Inc. All rights reserved. 24
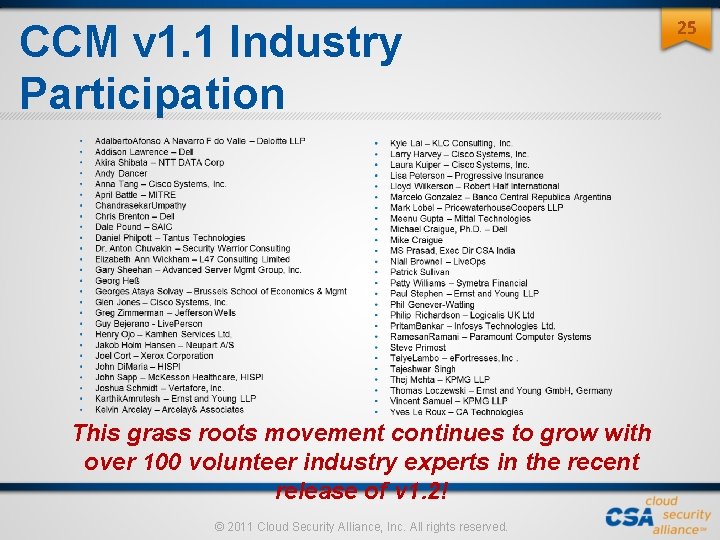
CCM v 1. 1 Industry Participation This grass roots movement continues to grow with over 100 volunteer industry experts in the recent release of v 1. 2! © 2011 Cloud Security Alliance, Inc. All rights reserved. 25
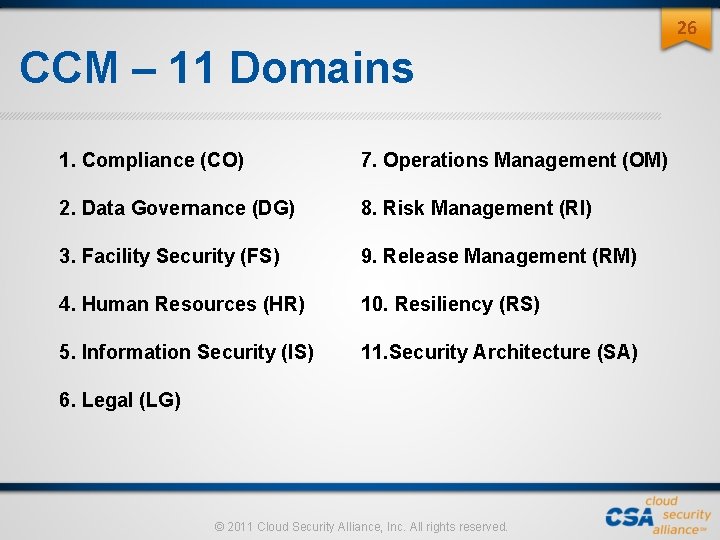
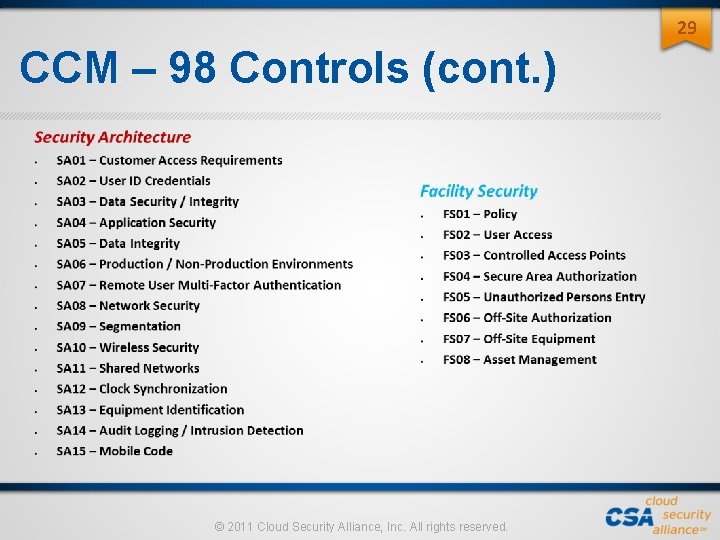
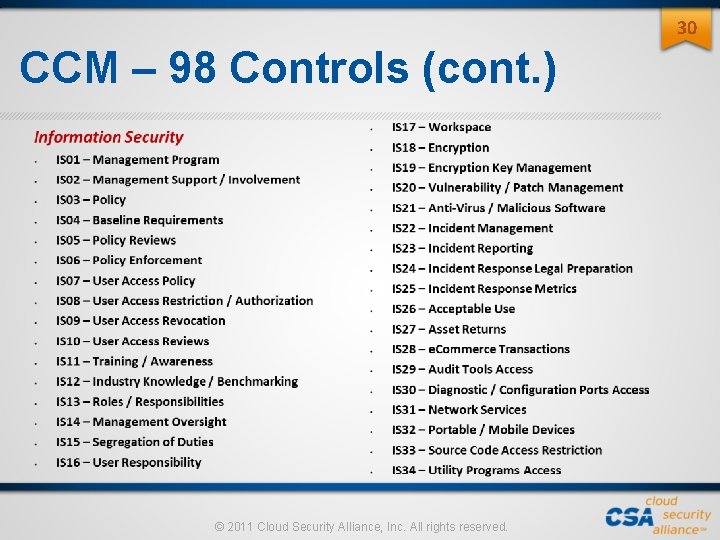
26 CCM – 11 Domains 1. Compliance (CO) 7. Operations Management (OM) 2. Data Governance (DG) 8. Risk Management (RI) 3. Facility Security (FS) 9. Release Management (RM) 4. Human Resources (HR) 10. Resiliency (RS) 5. Information Security (IS) 11. Security Architecture (SA) 6. Legal (LG) © 2011 Cloud Security Alliance, Inc. All rights reserved.
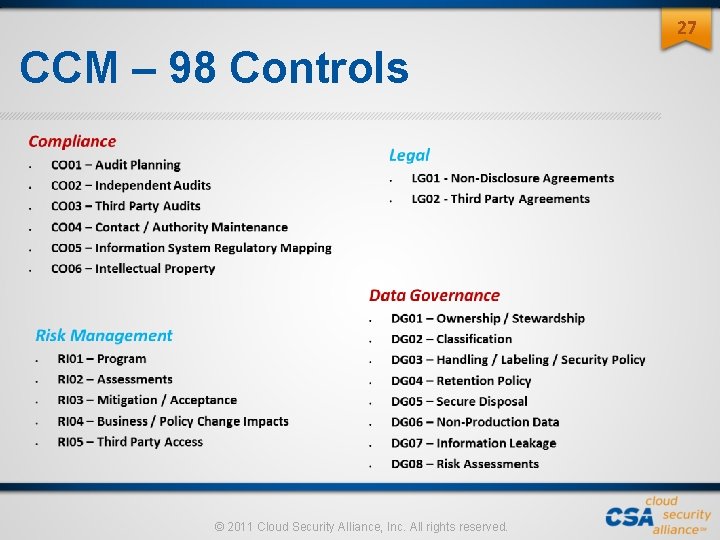
27 CCM – 98 Controls © 2011 Cloud Security Alliance, Inc. All rights reserved.
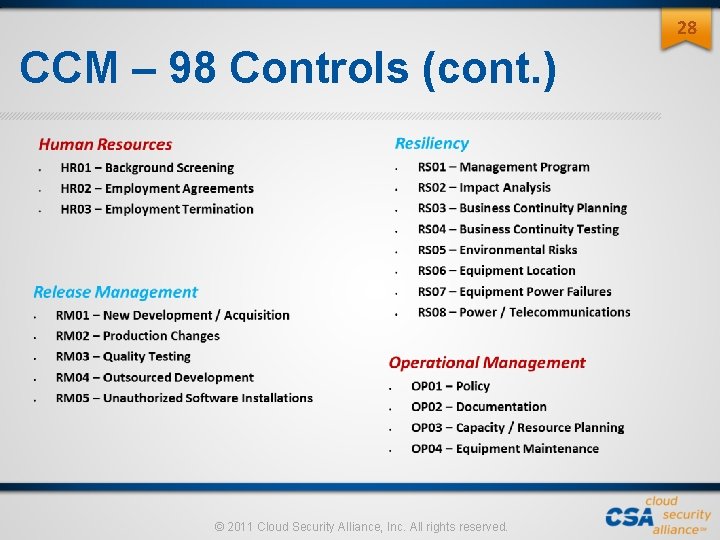
28 CCM – 98 Controls (cont. ) © 2011 Cloud Security Alliance, Inc. All rights reserved.
29 CCM – 98 Controls (cont. ) © 2011 Cloud Security Alliance, Inc. All rights reserved.
30 CCM – 98 Controls (cont. ) © 2011 Cloud Security Alliance, Inc. All rights reserved.
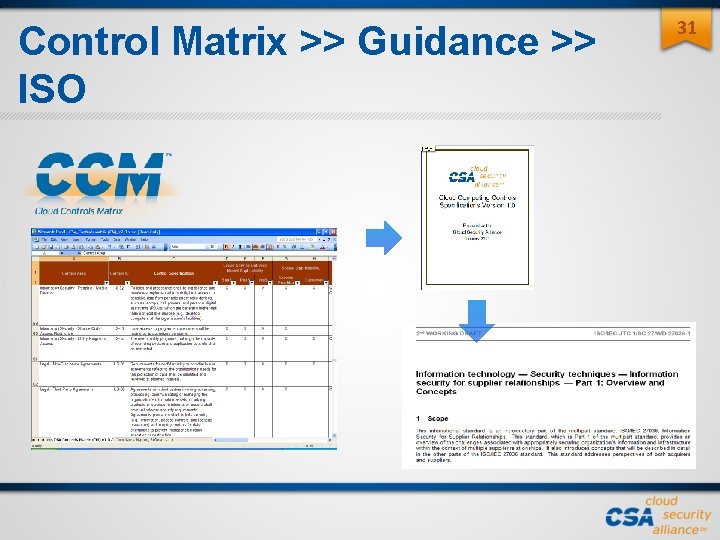
Control Matrix >> Guidance >> ISO 31
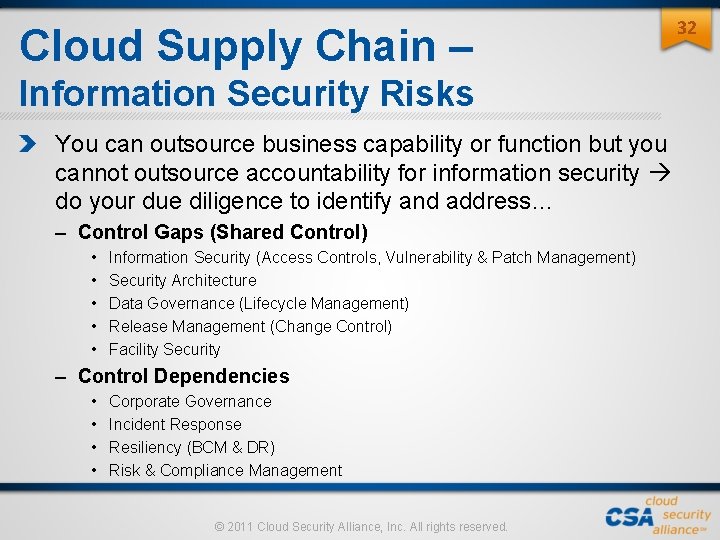
Cloud Supply Chain – Information Security Risks You can outsource business capability or function but you cannot outsource accountability for information security do your due diligence to identify and address… – Control Gaps (Shared Control) • • • Information Security (Access Controls, Vulnerability & Patch Management) Security Architecture Data Governance (Lifecycle Management) Release Management (Change Control) Facility Security – Control Dependencies • • Corporate Governance Incident Response Resiliency (BCM & DR) Risk & Compliance Management © 2011 Cloud Security Alliance, Inc. All rights reserved. 32
THE CONSENSUS ASSESSMENT INITIATIVE © 2011 Cloud Security Alliance, Inc. All rights reserved.
Consensus Assessments Initiative Questionnaire (CAIQ) © 2011 Cloud Security Alliance, Inc. All rights reserved. 34
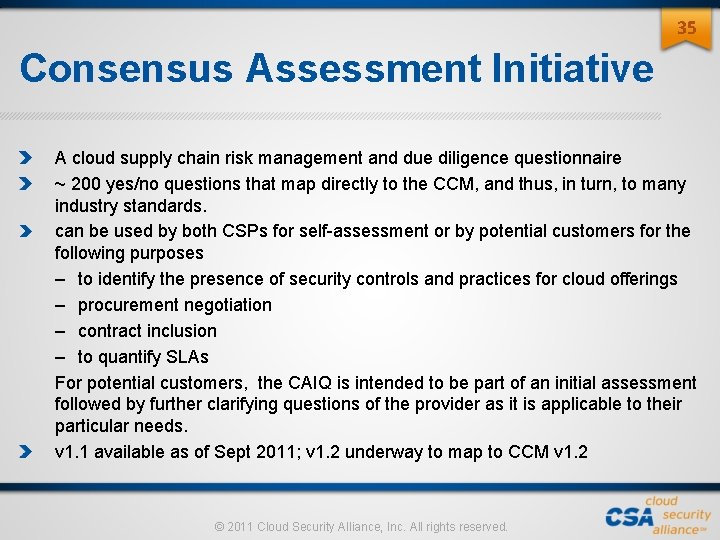
35 Consensus Assessment Initiative A cloud supply chain risk management and due diligence questionnaire ~ 200 yes/no questions that map directly to the CCM, and thus, in turn, to many industry standards. can be used by both CSPs for self-assessment or by potential customers for the following purposes – to identify the presence of security controls and practices for cloud offerings – procurement negotiation – contract inclusion – to quantify SLAs For potential customers, the CAIQ is intended to be part of an initial assessment followed by further clarifying questions of the provider as it is applicable to their particular needs. v 1. 1 available as of Sept 2011; v 1. 2 underway to map to CCM v 1. 2 © 2011 Cloud Security Alliance, Inc. All rights reserved.
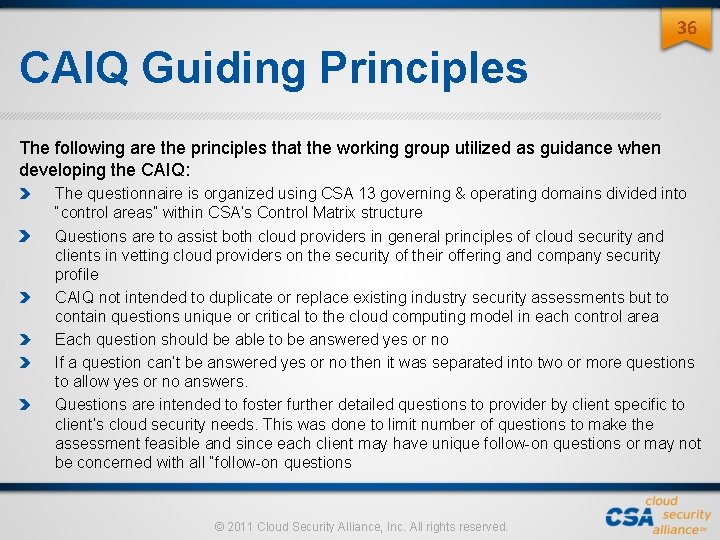
36 CAIQ Guiding Principles The following are the principles that the working group utilized as guidance when developing the CAIQ: The questionnaire is organized using CSA 13 governing & operating domains divided into “control areas” within CSA’s Control Matrix structure Questions are to assist both cloud providers in general principles of cloud security and clients in vetting cloud providers on the security of their offering and company security profile CAIQ not intended to duplicate or replace existing industry security assessments but to contain questions unique or critical to the cloud computing model in each control area Each question should be able to be answered yes or no If a question can’t be answered yes or no then it was separated into two or more questions to allow yes or no answers. Questions are intended to foster further detailed questions to provider by client specific to client’s cloud security needs. This was done to limit number of questions to make the assessment feasible and since each client may have unique follow-on questions or may not be concerned with all “follow-on questions © 2011 Cloud Security Alliance, Inc. All rights reserved.
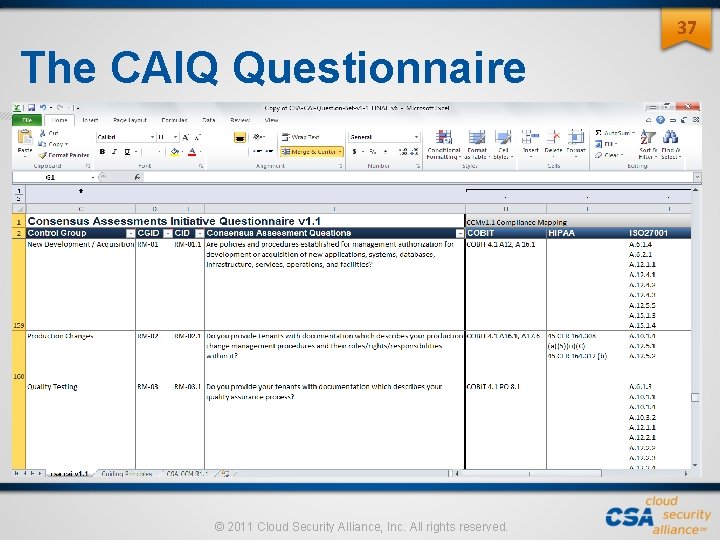
37 The CAIQ Questionnaire © 2011 Cloud Security Alliance, Inc. All rights reserved.
38 CAIQ Questionnaire Control Group, Control Group ID (CGID) and Control Identifier (CID) all map the CAIQ question being asked directly to the CCM control that is being addressed. Relevant compliance and standards are mapped line by line to the CAIQ, which, in turn, also map to the CCM. The CAIQ v 1. 1 maps to the following compliance areas – HIPPA, ISO 27001, COBIT, SP 800_53, Fed. RAMP, PCI_DSS, BITS and GAPP. V 1. 2 will additionally include mappings to Jericho Forum and NERC CIP. Each question can be answered by a provider with a yes or no answer. © 2011 Cloud Security Alliance, Inc. All rights reserved.
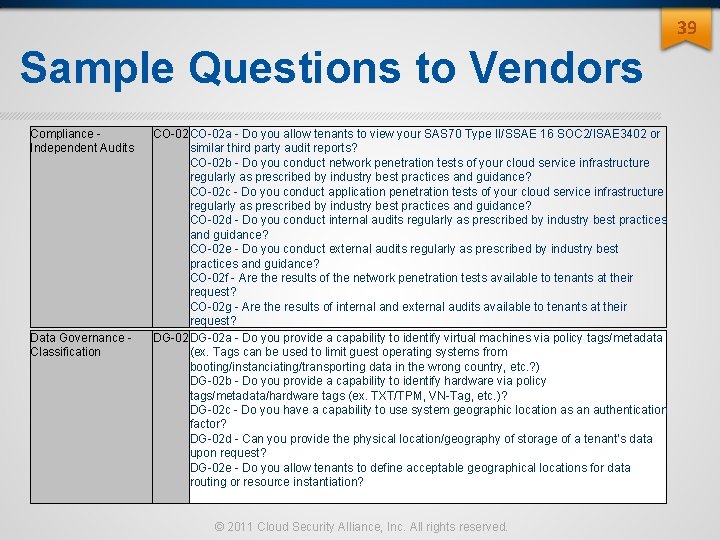
39 Sample Questions to Vendors Compliance Independent Audits Data Governance Classification CO-02 a - Do you allow tenants to view your SAS 70 Type II/SSAE 16 SOC 2/ISAE 3402 or similar third party audit reports? CO-02 b - Do you conduct network penetration tests of your cloud service infrastructure regularly as prescribed by industry best practices and guidance? CO-02 c - Do you conduct application penetration tests of your cloud service infrastructure regularly as prescribed by industry best practices and guidance? CO-02 d - Do you conduct internal audits regularly as prescribed by industry best practices and guidance? CO-02 e - Do you conduct external audits regularly as prescribed by industry best practices and guidance? CO-02 f - Are the results of the network penetration tests available to tenants at their request? CO-02 g - Are the results of internal and external audits available to tenants at their request? DG-02 a - Do you provide a capability to identify virtual machines via policy tags/metadata (ex. Tags can be used to limit guest operating systems from booting/instanciating/transporting data in the wrong country, etc. ? ) DG-02 b - Do you provide a capability to identify hardware via policy tags/metadata/hardware tags (ex. TXT/TPM, VN-Tag, etc. )? DG-02 c - Do you have a capability to use system geographic location as an authentication factor? DG-02 d - Can you provide the physical location/geography of storage of a tenant’s data upon request? DG-02 e - Do you allow tenants to define acceptable geographical locations for data routing or resource instantiation? © 2011 Cloud Security Alliance, Inc. All rights reserved.
CLOUDAUDIT © 2011 Cloud Security Alliance, Inc. All rights reserved.
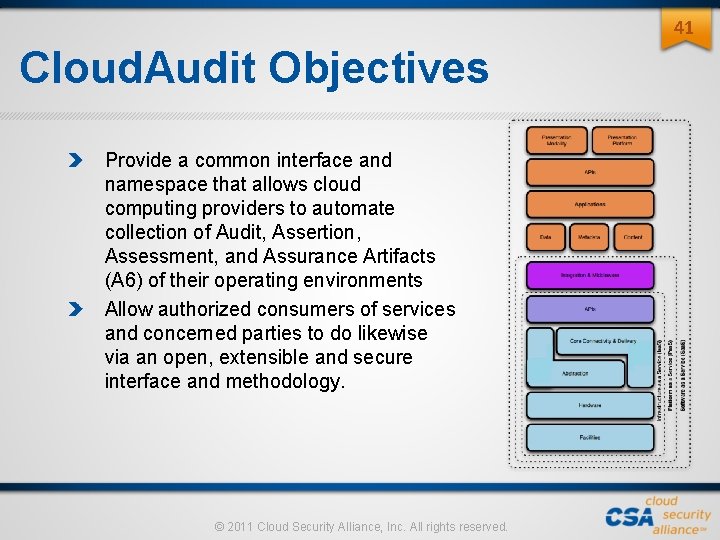
41 Cloud. Audit Objectives Provide a common interface and namespace that allows cloud computing providers to automate collection of Audit, Assertion, Assessment, and Assurance Artifacts (A 6) of their operating environments Allow authorized consumers of services and concerned parties to do likewise via an open, extensible and secure interface and methodology. © 2011 Cloud Security Alliance, Inc. All rights reserved.
42 What Cloud. Audit Does Provide a structure for organizing assertions and supporting documentation for specific controls across different compliance frameworks in a way that simplifies discovery by humans and tools. – Define a namespace that can support diverse frameworks – Express compliance frameworks in that namespace – Define the mechanisms for requesting and responding to queries relating to specific controls – Integrate with portals and AAA systems © 2011 Cloud Security Alliance, Inc. All rights reserved.
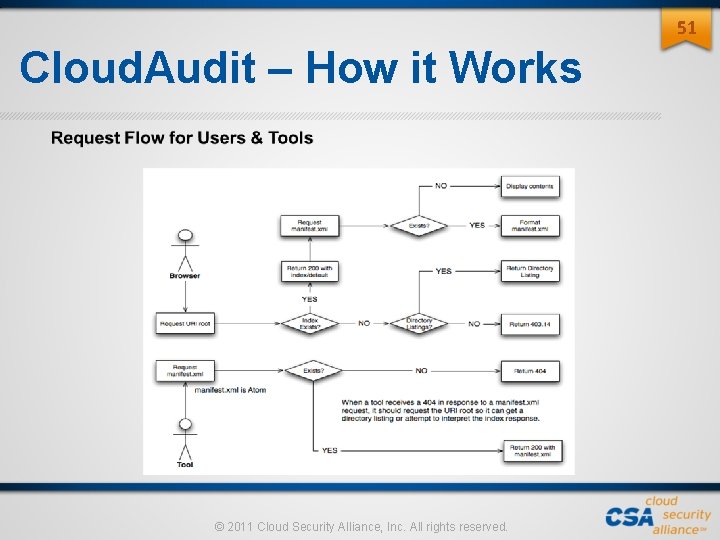
43 How Cloud. Audit Works Utilize security automation capabilities with existing tools/protocols/frameworks via a standard, open and extensible set of interfaces Keep it simple, lightweight and easy to implement; offer primitive definitions & language structure using HTTP(S) first at a very basic level Allow for extension and elaboration by providers and choice of trusted assertion validation sources, checklist definitions, etc. © 2011 Cloud Security Alliance, Inc. All rights reserved.
44 Context for Cloud. Audit is not designed to validate or attest “compliance” Automates collection and presentation of data supporting queries using a common set of namespaces aligned CSA Cloud Control Matrix Artifacts are accessible by a human operating a web browser or a tool capable of utilizing Cloud. Audit over HTTP(S). The consumers of this information are internal & external auditors, compliance teams, risk managers, security teams, etc. & in the longer term, brokers © 2011 Cloud Security Alliance, Inc. All rights reserved.
Aligned to CSA Control Matrix 45 Officially folded Cloud. Audit under the Cloud Security Alliance in October, 2010 First efforts aligned to compliance frameworks as established by CSA Control Matrix: – – – PCI DSS NIST 800 -53 HIPAA COBIT ISO 27002 Incorporate CSA’s CAI and additional Compliance. Packs Expand alignment to “infrastructure” and “operations” -centric views also © 2011 Cloud Security Alliance, Inc. All rights reserved.
What Was Delivered The first release of Cloud. Audit provides for the scoped capability for providers to store evidentiary data in welldefined namespaces aligned to the 5 CSA Control Matrix Mappings (PCI, HIPAA, NIST 800 -53, ISO 27002, COBIT)* The data in these namespaces is arbitrary and can be named and file-typed as such, so we need a way of dealing with what can be one to hundreds of supporting files, the contents of some of which are actually URIs to other locations * Update v 1. 1 packaging available to include CSA CCM Updates © 2011 Cloud Security Alliance, Inc. All rights reserved.
47 Current Discussions Stack Providers with whom we have discussed Cloud. Audit: – VMware, Citrix, Microsoft, Open. Stack Cloud Service Providers with whom we have discussed Cloud. Audit: – AWS, Google, Microsoft, Terremark, Savvis, Rackspace Cloud. Audit is bundled with the Piston Cloud, Open. Stack based cloud stack Tool (GRC) solution providers with whom we are discussing Cloud. Audit Implementation: – Agiliance, RSA Audit/Standards associations with whom we are discussing Cloud. Audit: – ISACA, ODCA, BITS, ISO, ITU-T, Open Group, DMTF, IETF © 2011 Cloud Security Alliance, Inc. All rights reserved.
48 What’s On The Roadmap Extend ATOM in manifest. xml to provide for timestamps, signatures and version control [need XML/ATOM expertise] Version control and change notification in conjunction with… …Architecture for registry services [cloudaudit. net] and extensions of such (public and/or private) Implementation architecture for “atomic queries” (e. g. “PCI Compliant, ” or “SAS-70 Certified” Expand On Specific Cloud. Audit Use Cases: – – Cloud. Audit for Federal Government Cloud. Audit for Cloud Providers Cloud. Audit for Auditors/Assessors Cloud. Audit as Evidence for Proper Financial Due Dilligance Intensify and clarify connection between Cloud. Audit and the CTP © 2011 Cloud Security Alliance, Inc. All rights reserved.
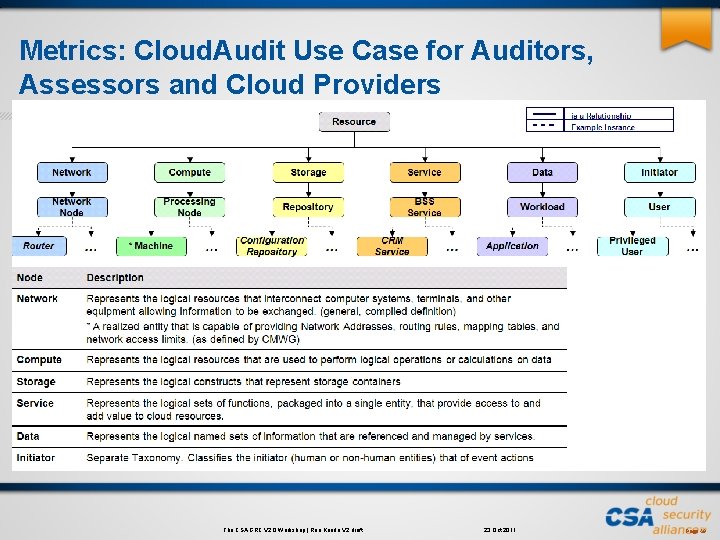
Metrics: Cloud. Audit Use Case for Auditors, Assessors and Cloud Providers The CSA GRC V 2. 0 Workshop | Ron Knode V 2 draft 23 Oct 2011 Page 49
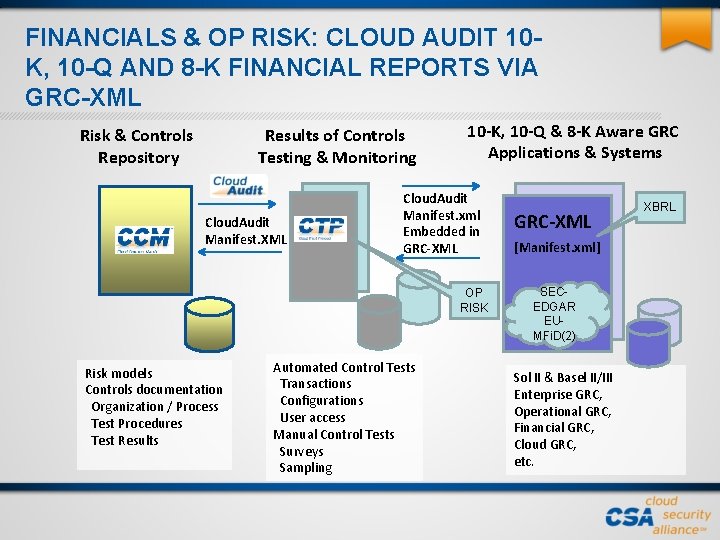
FINANCIALS & OP RISK: CLOUD AUDIT 10 K, 10 -Q AND 8 -K FINANCIAL REPORTS VIA GRC-XML Risk & Controls Repository Results of Controls Testing & Monitoring Cloud. Audit Manifest. XML 10 -K, 10 -Q & 8 -K Aware GRC Applications & Systems Cloud. Audit Manifest. xml Embedded in GRC-XML OP RISK Risk models Controls documentation Organization / Process Test Procedures Test Results Automated Control Tests Transactions Configurations User access Manual Control Tests Surveys Sampling GRC-XML [Manifest. xml] SECEDGAR EUMFi. D(2) Sol II & Basel II/III Enterprise GRC, Operational GRC, Financial GRC, Cloud GRC, etc. XBRL
51 Cloud. Audit – How it Works © 2011 Cloud Security Alliance, Inc. All rights reserved.
Atom Specification (RFC 4287) http: //www. ietf. org/rfc 4287. txt Atom is an XML-based document format that describes lists of related information known as "feeds". Feeds are composed of a number of items, known as "entries", each with an extensible set of attached metadata. For example, each entry has a title. The primary use case that Atom addresses is the syndication of Web content such as weblogs and news headlines to Web sites as well as directly to user agents. © 2011 Cloud Security Alliance, Inc. All rights reserved.
53 Manifest. xml Structured listing of control contents Can be extended to provide contextual information Primarily aimed at tool consumption In Atom format © 2011 Cloud Security Alliance, Inc. All rights reserved.
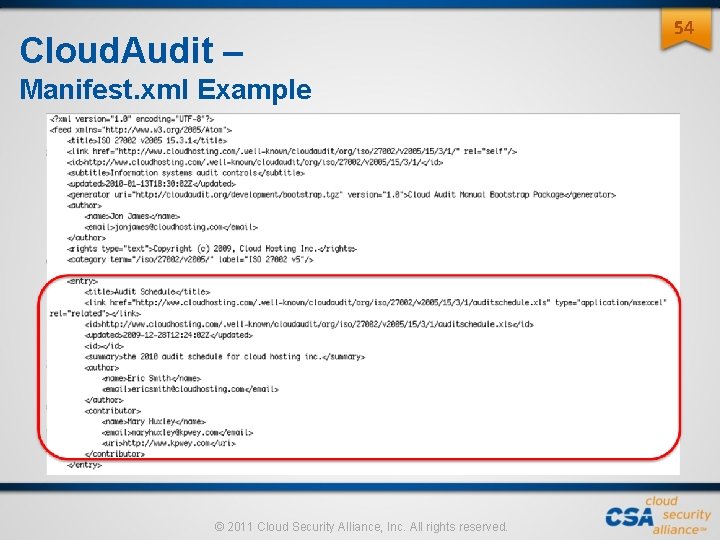
Cloud. Audit – Manifest. xml Example © 2011 Cloud Security Alliance, Inc. All rights reserved. 54
55 index. html/default. jsp/etc. Index. html is for dumb browser consumption – Typically, the direct human user use case It can be omitted if directory browsing is enabled (not recommended) It contains Java. Script to look for the manifest. xml file, parse it, and render it as HTML. If no manifest. xml exists, it should list the directory contents relevant to the control in question © 2011 Cloud Security Alliance, Inc. All rights reserved.
56 Atom Specification (RFC 4287) http: //www. ietf. org/rfc 4287. txt Atom is an XML-based document format that describes lists of related information known as "feeds". Feeds are composed of a number of items, known as "entries", each with an extensible set of attached metadata. For example, each entry has a title. The primary use case that Atom addresses is the syndication of Web content such as weblogs and news headlines to Web sites as well as directly to user agents. © 2011 Cloud Security Alliance, Inc. All rights reserved.
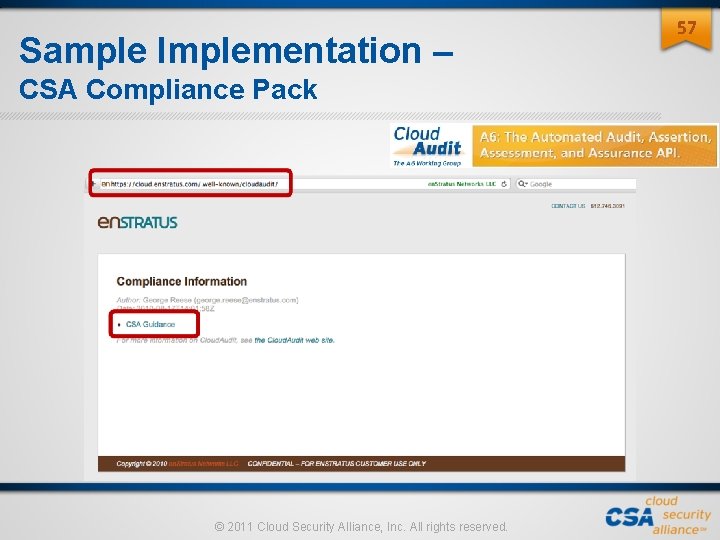
Sample Implementation – CSA Compliance Pack © 2011 Cloud Security Alliance, Inc. All rights reserved. 57
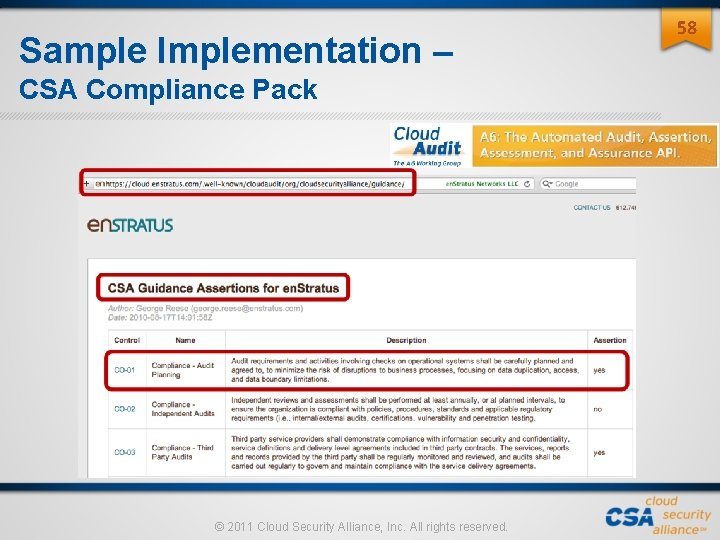
Sample Implementation – CSA Compliance Pack © 2011 Cloud Security Alliance, Inc. All rights reserved. 58
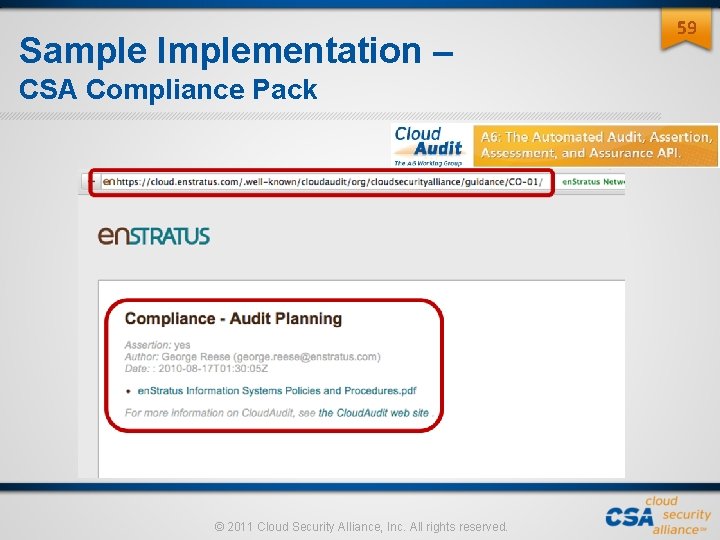
Sample Implementation – CSA Compliance Pack © 2011 Cloud Security Alliance, Inc. All rights reserved. 59
Sample Implementation – CSA Compliance Pack © 2011 Cloud Security Alliance, Inc. All rights reserved. 60
CLOUD TRUST PROTOCOL © 2011 Cloud Security Alliance, Inc. All rights reserved.
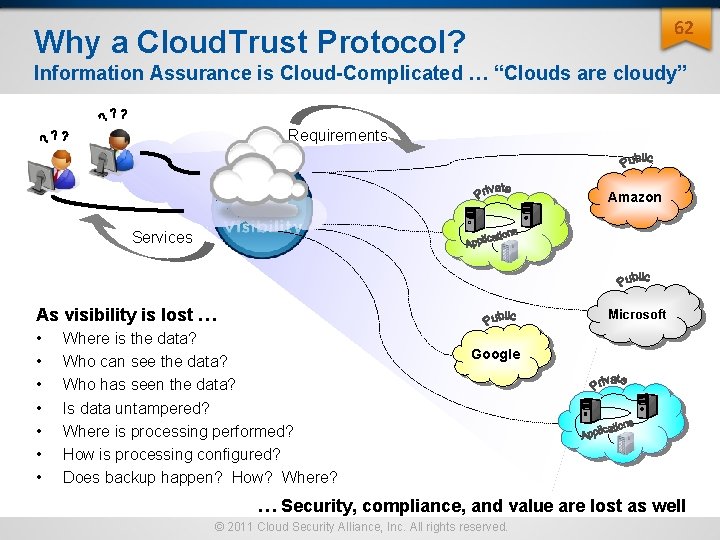
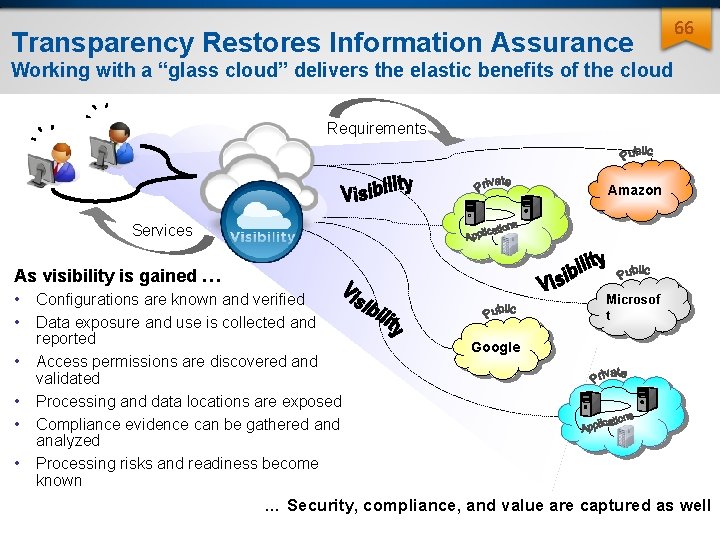
62 Why a Cloud. Trust Protocol? Information Assurance is Cloud-Complicated … “Clouds are cloudy” Requirements Amazon Services As visibility is lost … • • Microsoft Where is the data? Who can see the data? Who has seen the data? Is data untampered? Where is processing performed? How is processing configured? Does backup happen? How? Where? Google … Security, compliance, and value are lost as well © 2011 Cloud Security Alliance, Inc. All rights reserved.
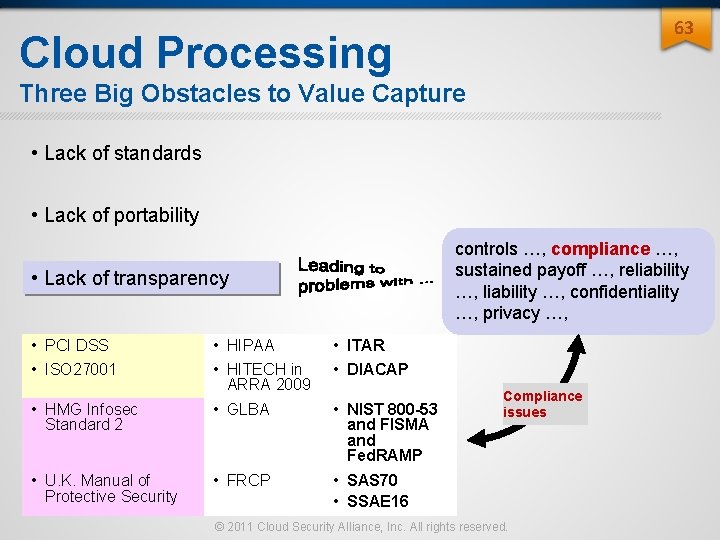
63 Cloud Processing Three Big Obstacles to Value Capture • Lack of standards • Lack of portability controls …, compliance …, sustained payoff …, reliability …, confidentiality …, privacy …, • Lack of transparency • PCI DSS • ISO 27001 • HMG Infosec Standard 2 • U. K. Manual of Protective Security • HIPAA • HITECH in ARRA 2009 • GLBA • ITAR • DIACAP • FRCP • SAS 70 • SSAE 16 • NIST 800 -53 and FISMA and Fed. RAMP Compliance issues © 2011 Cloud Security Alliance, Inc. All rights reserved.
64 Absent Transparency … Some Big Problems For example, … without transparency … No confirmed chain of custody for information No way to conduct investigative forensics Little confidence in the ability to detect attempts or occurrences of illegal disclosure Little capability to discover or enforce configurations No ability to monitor operational access or service management actions (e. g. , change management, patch management, vulnerability management, …) © 2011 Cloud Security Alliance, Inc. All rights reserved.
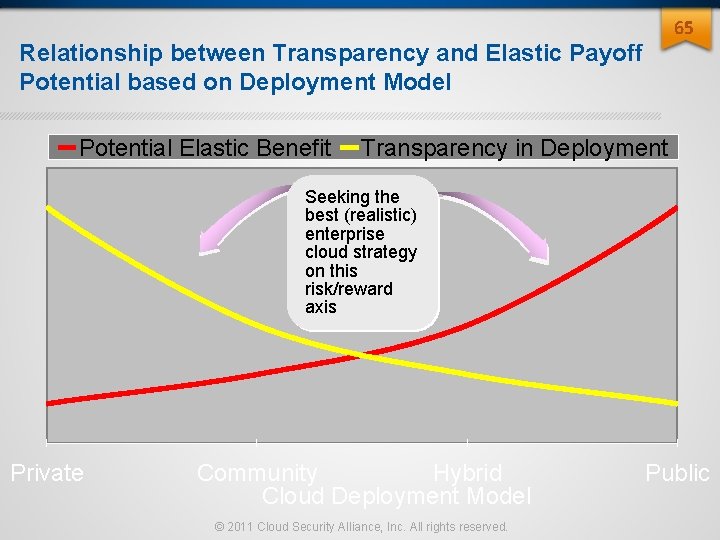
65 Relationship between Transparency and Elastic Payoff Potential based on Deployment Model Potential Elastic Benefit Transparency in Deployment Seeking the best (realistic) enterprise cloud strategy on this risk/reward axis Private Community Hybrid Cloud Deployment Model © 2011 Cloud Security Alliance, Inc. All rights reserved. Public
Transparency Restores Information Assurance 66 Working with a “glass cloud” delivers the elastic benefits of the cloud Requirements Amazon Services As visibility is gained … • • • Configurations are known and verified Data exposure and use is collected and reported Access permissions are discovered and validated Processing and data locations are exposed Compliance evidence can be gathered analyzed Processing risks and readiness become known Microsof t Google … Security, compliance, and value are captured as well © 2011 Cloud Security Alliance, Inc. All rights reserved.
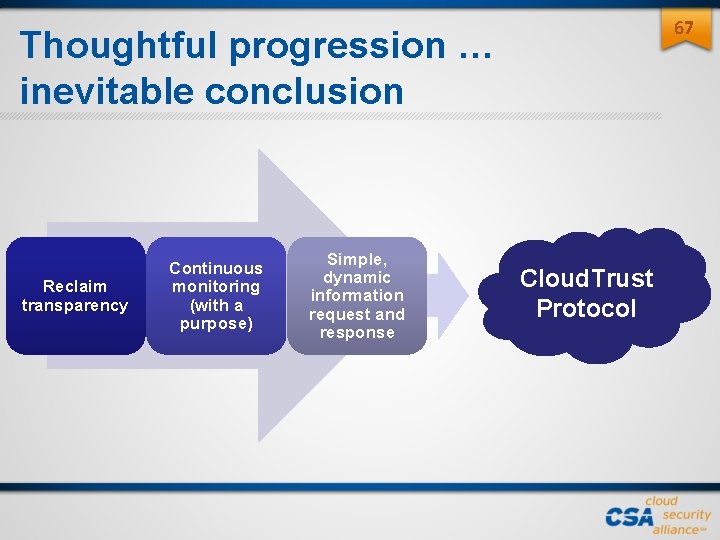
67 Thoughtful progression … inevitable conclusion Reclaim transparency Continuous monitoring (with a purpose) Simple, dynamic information request and response Cloud. Trust Protocol
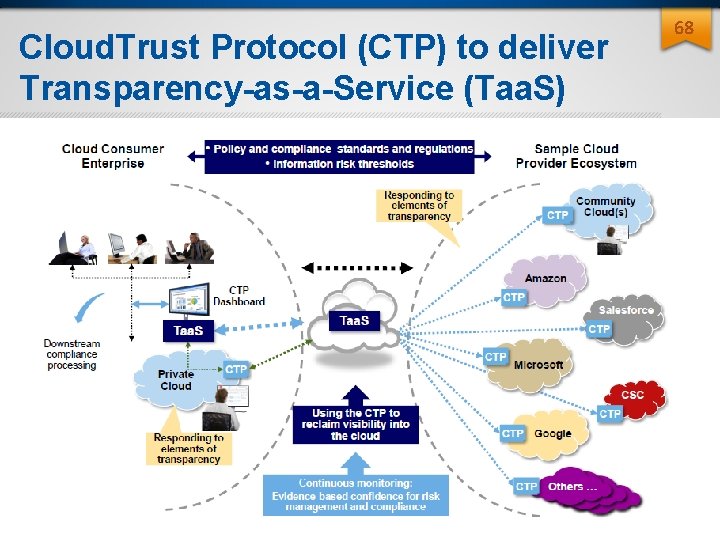
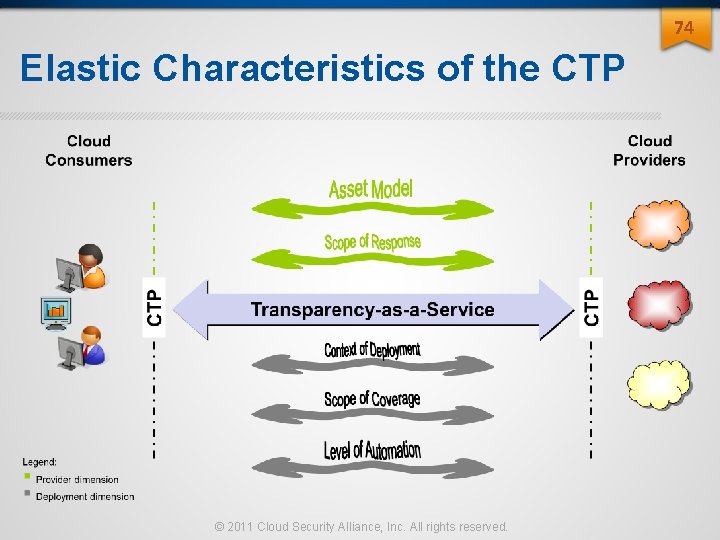
Cloud. Trust Protocol (CTP) to deliver Transparency-as-a-Service (Taa. S) 68
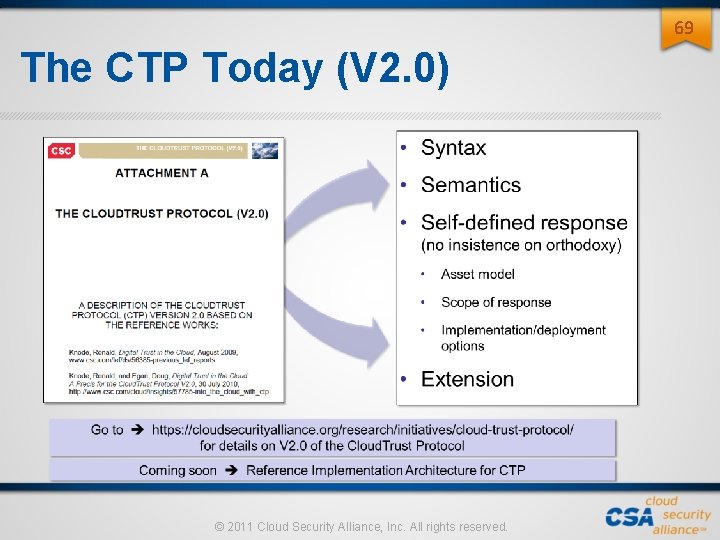
69 The CTP Today (V 2. 0) © 2011 Cloud Security Alliance, Inc. All rights reserved.
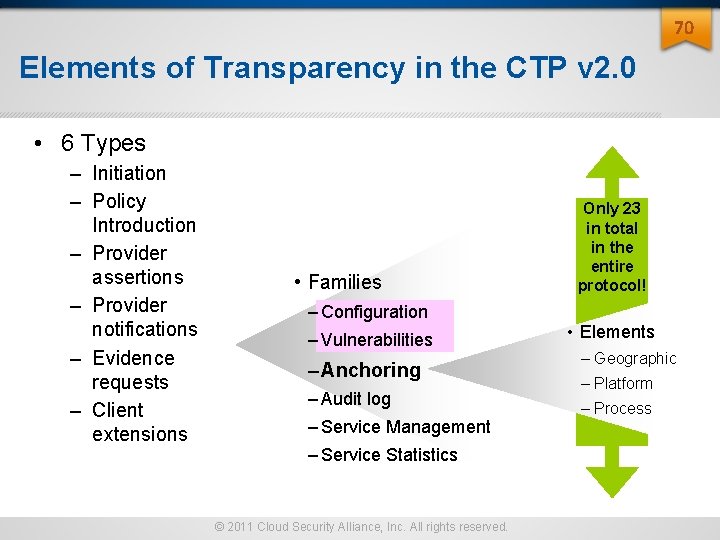
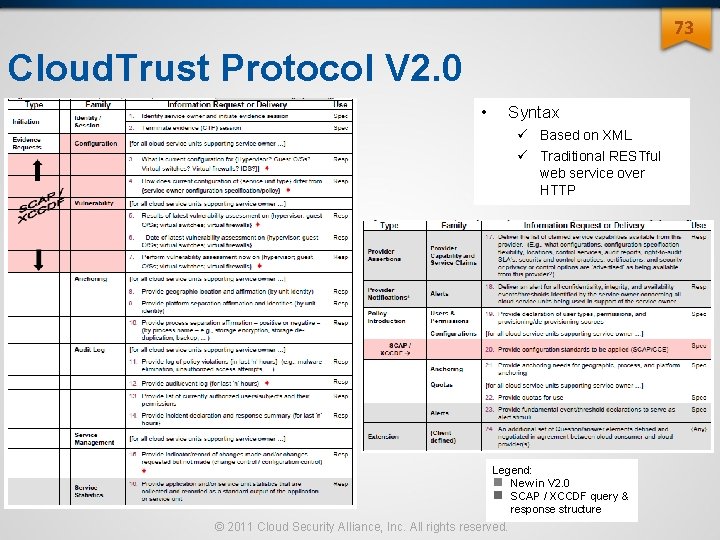
70 Elements of Transparency in the CTP v 2. 0 • 6 Types – Initiation – Policy Introduction – Provider assertions – Provider notifications – Evidence requests – Client extensions • Families Only 23 in total in the entire protocol! – Configuration – Vulnerabilities – Anchoring – Audit log – Service Management – Service Statistics © 2011 Cloud Security Alliance, Inc. All rights reserved. • Elements – Geographic – Platform – Process
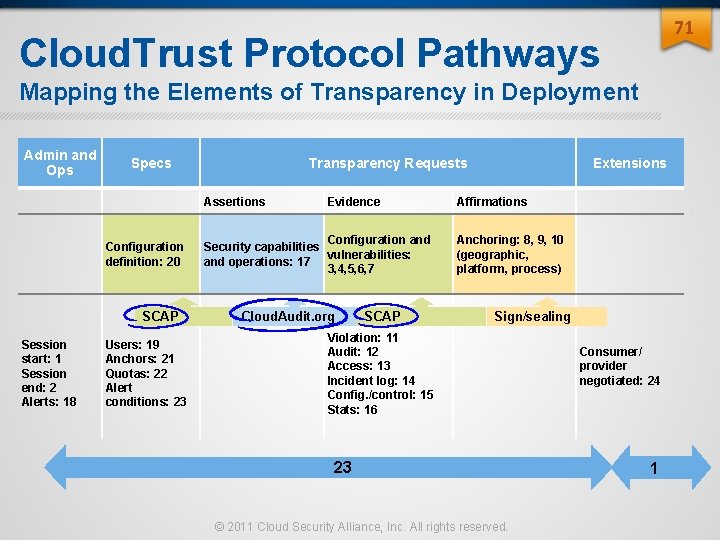
71 Cloud. Trust Protocol Pathways Mapping the Elements of Transparency in Deployment Admin and Ops Specs Transparency Requests Assertions Configuration definition: 20 SCAP Session start: 1 Session end: 2 Alerts: 18 Users: 19 Anchors: 21 Quotas: 22 Alert conditions: 23 Evidence Configuration and Security capabilities vulnerabilities: and operations: 17 3, 4, 5, 6, 7 Cloud. Audit. org SCAP Extensions Affirmations Anchoring: 8, 9, 10 (geographic, platform, process) Sign/sealing Violation: 11 Audit: 12 Access: 13 Incident log: 14 Config. /control: 15 Stats: 16 23 © 2011 Cloud Security Alliance, Inc. All rights reserved. Consumer/ provider negotiated: 24 1
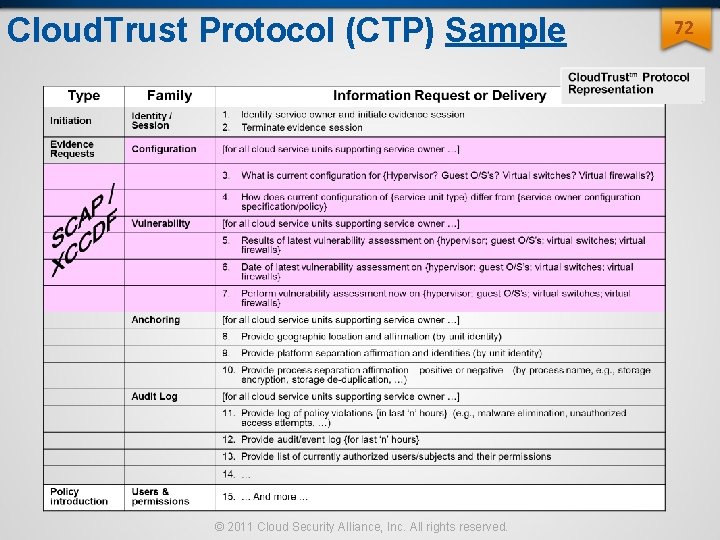
Cloud. Trust Protocol (CTP) Sample © 2011 Cloud Security Alliance, Inc. All rights reserved. 72
73 Cloud. Trust Protocol V 2. 0 • Syntax ü Based on XML ü Traditional RESTful web service over HTTP Legend: New in V 2. 0 SCAP / XCCDF query & response structure © 2011 Cloud Security Alliance, Inc. All rights reserved.
74 Elastic Characteristics of the CTP © 2011 Cloud Security Alliance, Inc. All rights reserved.
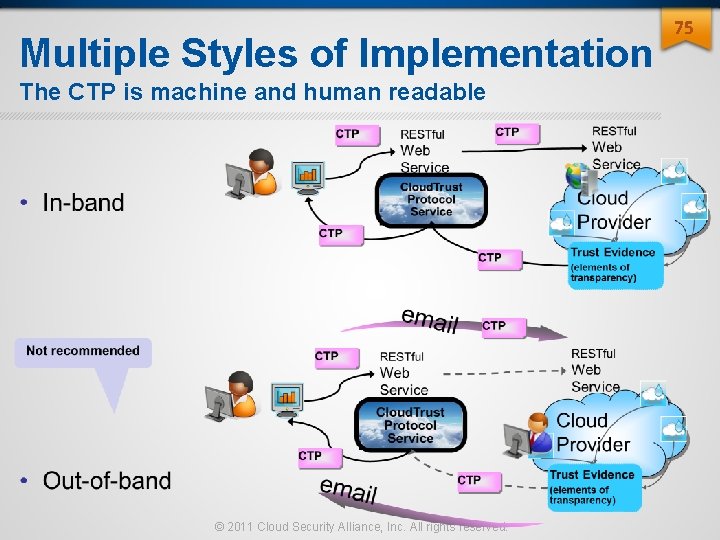
Multiple Styles of Implementation The CTP is machine and human readable © 2011 Cloud Security Alliance, Inc. All rights reserved. 75
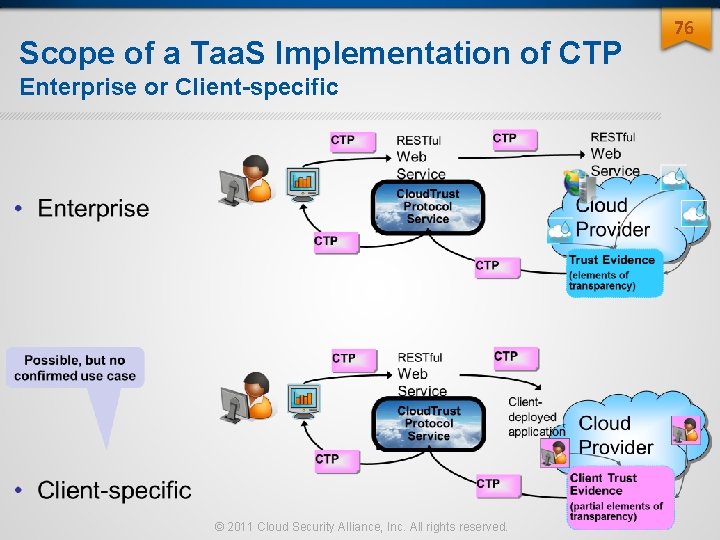
Scope of a Taa. S Implementation of CTP Enterprise or Client-specific © 2011 Cloud Security Alliance, Inc. All rights reserved. 76
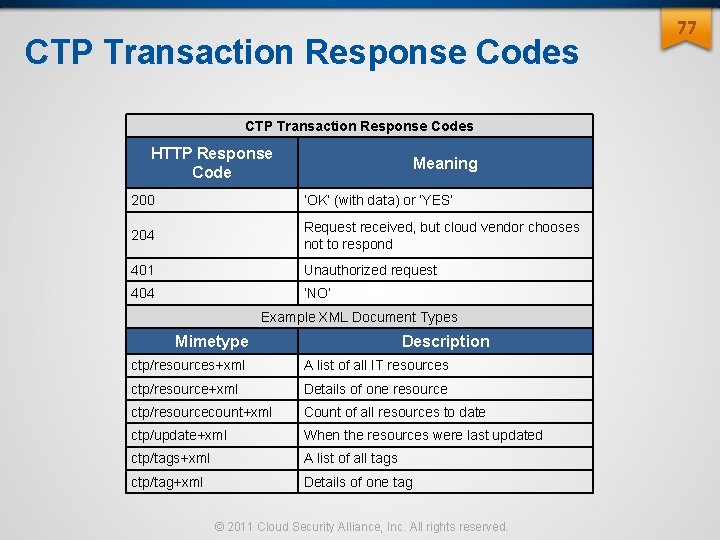
CTP Transaction Response Codes HTTP Response Code Meaning 200 ‘OK’ (with data) or ‘YES’ 204 Request received, but cloud vendor chooses not to respond 401 Unauthorized request 404 ‘NO’ Example XML Document Types Mimetype Description ctp/resources+xml A list of all IT resources ctp/resource+xml Details of one resource ctp/resourcecount+xml Count of all resources to date ctp/update+xml When the resources were last updated ctp/tags+xml A list of all tags ctp/tag+xml Details of one tag © 2011 Cloud Security Alliance, Inc. All rights reserved. 77
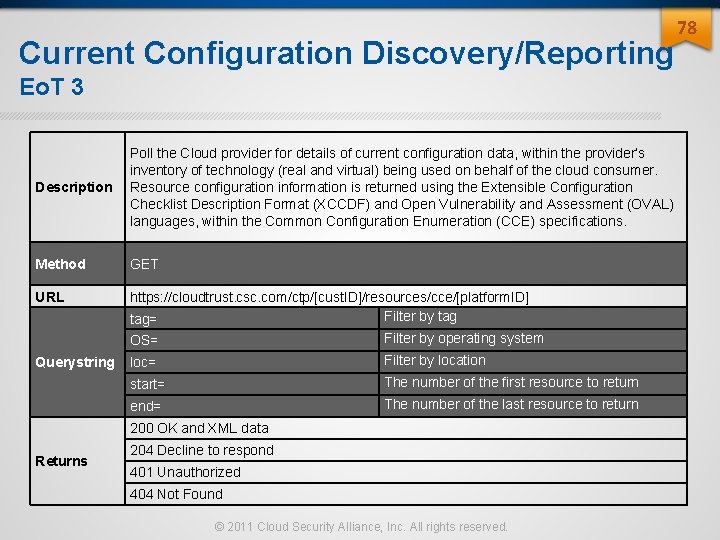
Current Configuration Discovery/Reporting Eo. T 3 Description Poll the Cloud provider for details of current configuration data, within the provider’s inventory of technology (real and virtual) being used on behalf of the cloud consumer. Resource configuration information is returned using the Extensible Configuration Checklist Description Format (XCCDF) and Open Vulnerability and Assessment (OVAL) languages, within the Common Configuration Enumeration (CCE) specifications. Method GET URL https: //cloudtrust. csc. com/ctp/[cust. ID]/resources/cce/[platform. ID] Filter by tag= Querystring OS= Filter by operating system loc= Filter by location start= The number of the first resource to return end= The number of the last resource to return 200 OK and XML data Returns 204 Decline to respond 401 Unauthorized 404 Not Found © 2011 Cloud Security Alliance, Inc. All rights reserved. 78
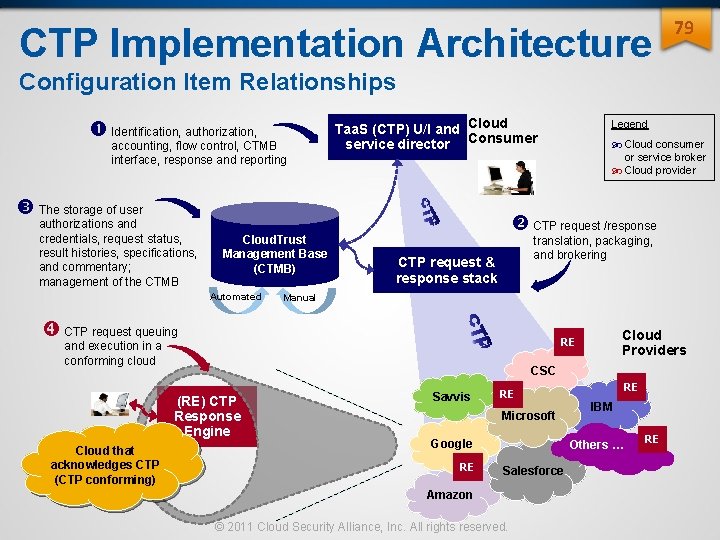
CTP Implementation Architecture 79 Configuration Item Relationships Identification, authorization, accounting, flow control, CTMB interface, response and reporting Taa. S (CTP) U/I and Cloud service director Consumer The storage of user authorizations and credentials, request status, result histories, specifications, and commentary; management of the CTMB Cloud. Trust Management Base (CTMB) Automated Cloud consumer or service broker Cloud provider CTP request /response translation, packaging, and brokering CTP request & response stack Manual CTP request queuing Cloud Providers RE and execution in a conforming cloud CSC (RE) CTP Response Engine Cloud that acknowledges CTP (CTP conforming) Legend Savvis RE Microsoft Google RE RE IBM Others … Salesforce Amazon © 2011 Cloud Security Alliance, Inc. All rights reserved. RE
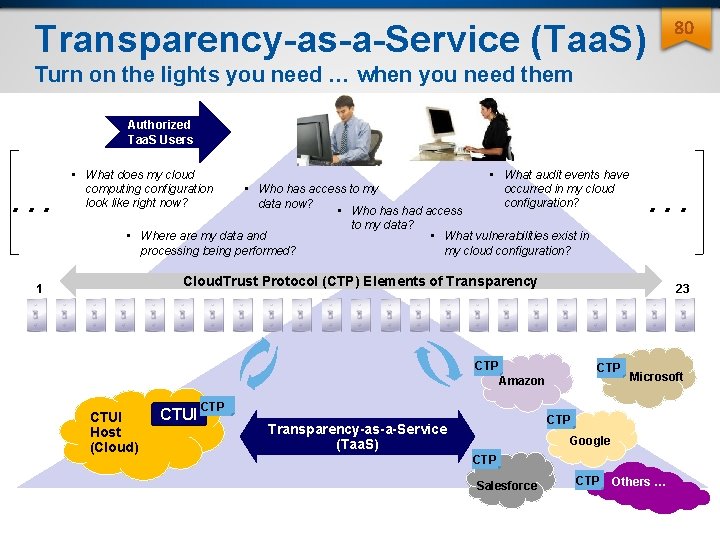
80 Transparency-as-a-Service (Taa. S) Turn on the lights you need … when you need them Authorized Taa. S Users . . . • What does my cloud computing configuration look like right now? • What audit events have occurred in my cloud configuration? • Who has access to my data now? • Who has had access to my data? • Where are my data and • What vulnerabilities exist in processing being performed? my cloud configuration? . . . Cloud. Trust Protocol (CTP) Elements of Transparency 1 23 CTP Amazon CTUI Host (Cloud) CTUI Microsoft CTP Transparency-as-a-Service (Taa. S) Google CTP Salesforce CTP Others …
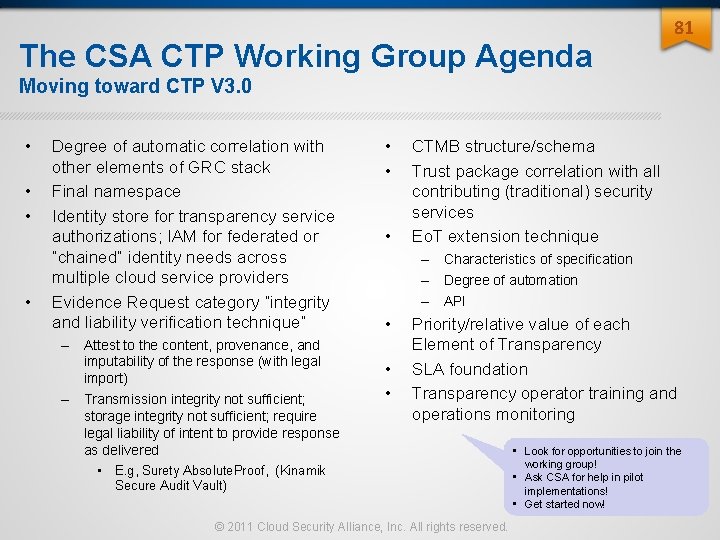
The CSA CTP Working Group Agenda 81 Moving toward CTP V 3. 0 • • Degree of automatic correlation with other elements of GRC stack Final namespace Identity store for transparency service authorizations; IAM for federated or “chained” identity needs across multiple cloud service providers Evidence Request category “integrity and liability verification technique” – Attest to the content, provenance, and imputability of the response (with legal import) – Transmission integrity not sufficient; storage integrity not sufficient; require legal liability of intent to provide response as delivered • • • CTMB structure/schema Trust package correlation with all contributing (traditional) security services Eo. T extension technique – Characteristics of specification – Degree of automation – API • • • Priority/relative value of each Element of Transparency SLA foundation Transparency operator training and operations monitoring • E. g, Surety Absolute. Proof, (Kinamik Secure Audit Vault) © 2011 Cloud Security Alliance, Inc. All rights reserved. • Look for opportunities to join the working group! • Ask CSA for help in pilot implementations! • Get started now!
SESSION 4 // Where and How to Begin Connections to Other CSA Initiatives © 2011 Cloud Security Alliance, Inc. All rights reserved.
Using the GRC Stack 83 Making the Stack Pack Approach Work for You Easy to get started Many successful combinations Benefits accrue with each stack pack addition Multiple alternatives to application and deployment Mapped across multiple compliance mandates © 2011 Cloud Security Alliance, Inc. All rights reserved.
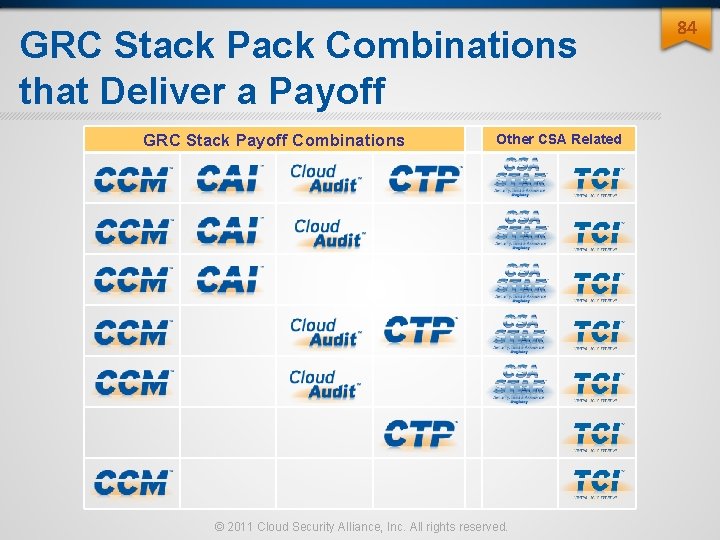
GRC Stack Pack Combinations that Deliver a Payoff GRC Stack Payoff Combinations Other CSA Related © 2011 Cloud Security Alliance, Inc. All rights reserved. 84
Security, Trust, and Assurance Registry (CSA STAR) • CSA STAR (Security, Trust and Assurance Registry) • Public Registry of Cloud Provider self assessments • Leverages GRC Stack Projects – Consensus Assessments Initiative Questionnaire – Provider may substitute documented Cloud Controls Matrix compliance • Voluntary industry action promoting transparency • Free market competition to provide quality assessments • Available October 2011 85
86 Security, Trust, and Assurance Registry (CSA STAR) Expose control claims Compete to improve GRC capabilities GRC Stack Encourage transparency of security practices within cloud providers Documents the security controls provided by various cloud computing offerings Free and open to all cloud providers Option to use data/report based on CCM or the CAIQ © 2011 Cloud Security Alliance, Inc. All rights reserved.
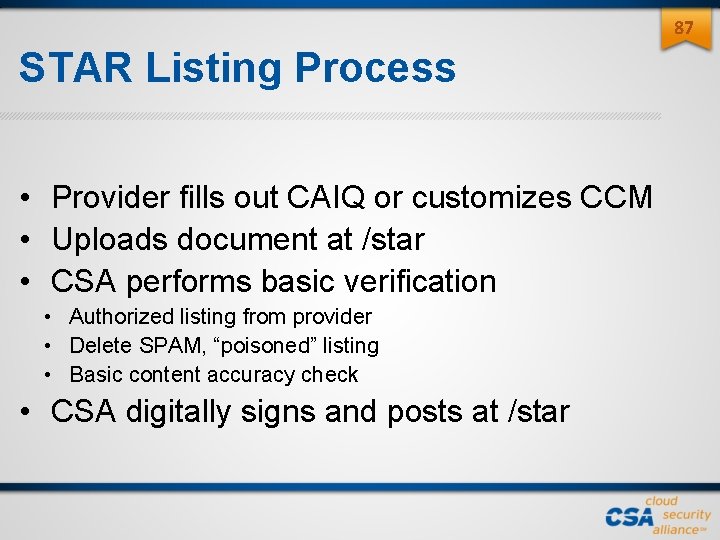
87 STAR Listing Process • Provider fills out CAIQ or customizes CCM • Uploads document at /star • CSA performs basic verification • Authorized listing from provider • Delete SPAM, “poisoned” listing • Basic content accuracy check • CSA digitally signs and posts at /star
88 FAQ • Where? www. cloudsecurityalliance. org/star/ • Help? Special Linked. In support group and private mailbox moderated by CSA volunteers, online next week • Costs? Free to post, free to use • Is this a new hacker threat vector? No, it is responsible disclosure of security practices • Will CSA police STAR? Initial verification and maintenance of “Abuse” mailbox • Do listings expire? Yes, 1 year limit • Full FAQ to be posted at /star next week
Why not certification or assessment? 3 rd party 89 • Complex to do certification right – Many uses of cloud, many customer needs – Different risk profiles for each • CSA supporting broad industry consortia and standards bodies – ISO, ITU-T – Common Assurance Maturity Model (CAMM – 3 rd Party assessment) – GRC Stack aligns with common requirements (e. g. PCI/DSS, HIPAA, Fed. RAMP, 27001, Co. BIT, etc) • Self assessment & transparency complements all – STAR could be part of SSAE 16 SOC II report (SAS 70 replacement)
Is CSA STAR temporary or the ultimate assurance solution? 90 • Neither • Permanent effort to drive transparency, competition, innovation and self regulation with agility – crowdsourcing cloud security • Does not provide automation, 3 rd party assessment, relative/absolute scoring, real-time controls monitoring, etc • Ultimate assurance is real time GRC (enabled by Cloud. Audit) complemented by CSA STAR and 3 rd party attestation. Will look to solution providers to deliver this integration
91 Trusted Cloud Initiative (TCI) CSA certification criteria and seal program for cloud providers Initial focus on secure & interoperable identity in the cloud, and its alignment with data encryption Assemble with existing standards Reference models & Proof of concept Outline responsibilities for Identity Providers, Enterprises, Cloud Providers, Consumers www. cloudsecurityalliance. org/trustedcloud. html © 2011 Cloud Security Alliance, Inc. All rights reserved.
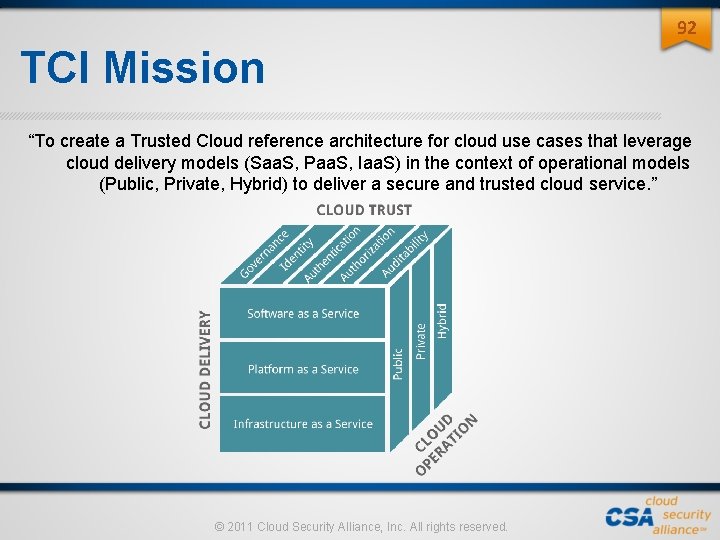
92 TCI Mission “To create a Trusted Cloud reference architecture for cloud use cases that leverage cloud delivery models (Saa. S, Paa. S, Iaa. S) in the context of operational models (Public, Private, Hybrid) to deliver a secure and trusted cloud service. ” © 2011 Cloud Security Alliance, Inc. All rights reserved.
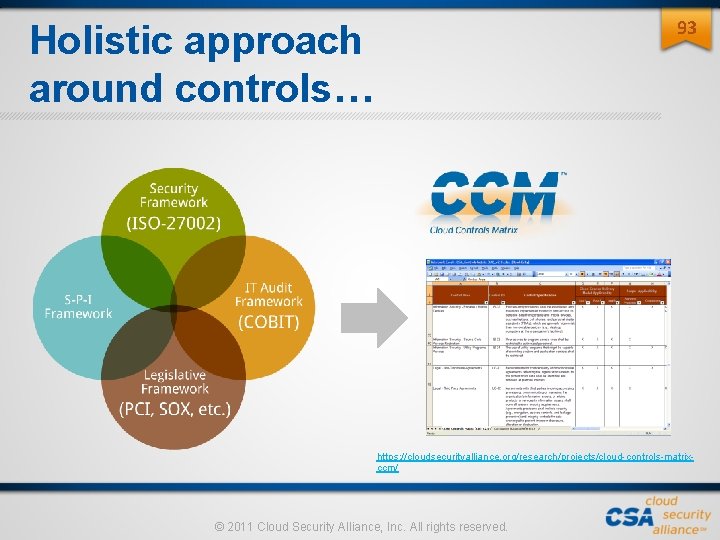
93 Holistic approach around controls… https: //cloudsecurityalliance. org/research/projects/cloud-controls-matrixccm/ © 2011 Cloud Security Alliance, Inc. All rights reserved.
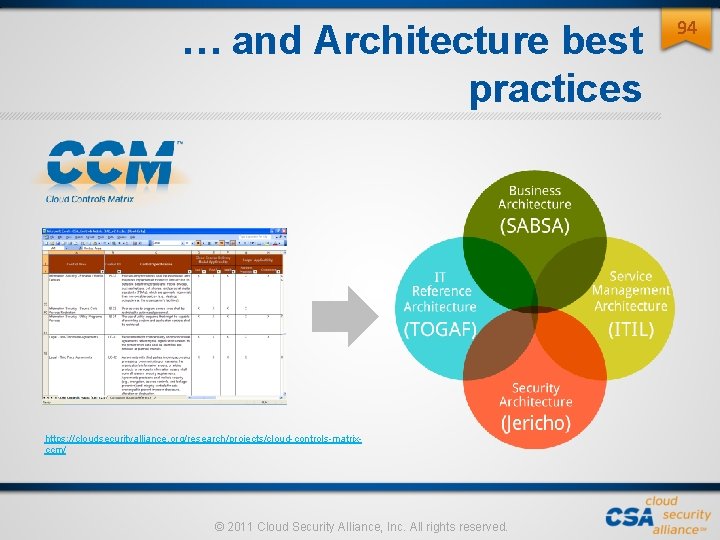
… and Architecture best practices https: //cloudsecurityalliance. org/research/projects/cloud-controls-matrixccm/ © 2011 Cloud Security Alliance, Inc. All rights reserved. 94
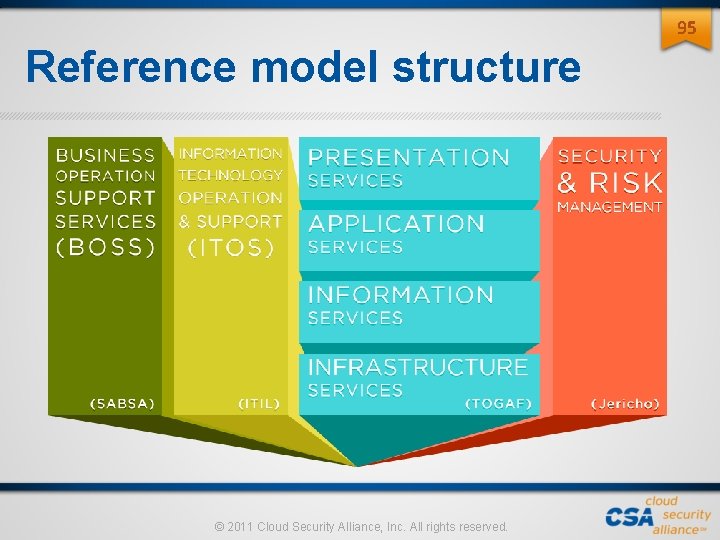
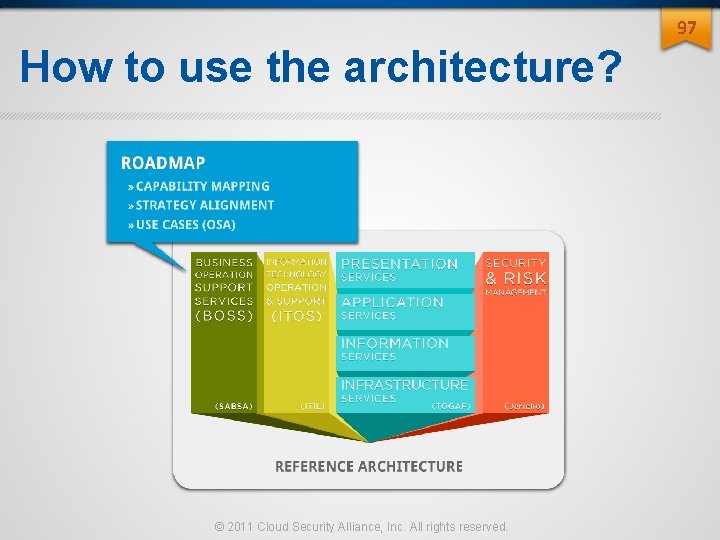
95 Reference model structure © 2011 Cloud Security Alliance, Inc. All rights reserved.
96 How to use the architecture? © 2011 Cloud Security Alliance, Inc. All rights reserved.
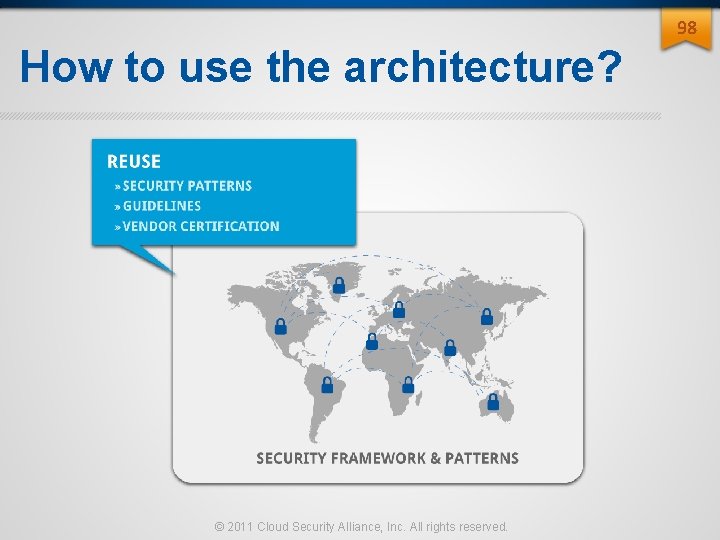
97 How to use the architecture? © 2011 Cloud Security Alliance, Inc. All rights reserved.
98 How to use the architecture? © 2011 Cloud Security Alliance, Inc. All rights reserved.
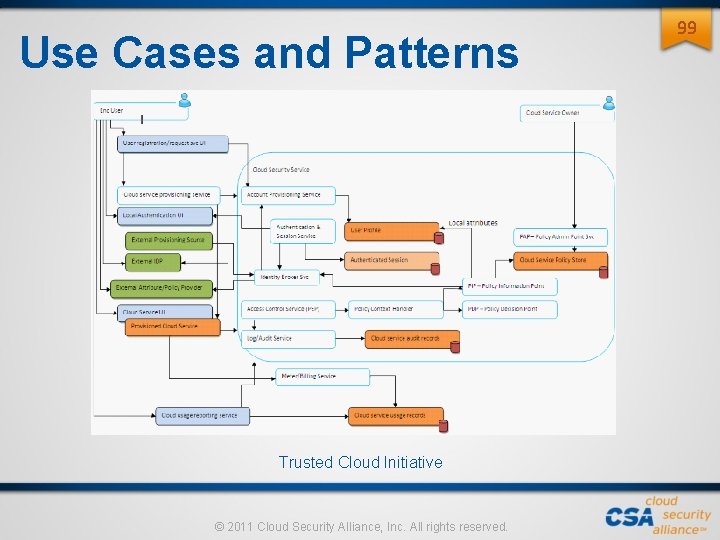
Use Cases and Patterns Trusted Cloud Initiative © 2011 Cloud Security Alliance, Inc. All rights reserved. 99
100 CAMM The Common Assurance Maturity Model (CAMM) is designed to provide trustworthiness (safety, security and reliability) of the supply chain working within and across the Internet in the new information world. It offers the following benefits to customer and service provider organizations: © 2011 Cloud Security Alliance, Inc. All rights reserved.
101 CAMM Objectives Purpose – Provide a framework to provide the necessary transparency in attesting the Information Assurance Maturity of a third party (e. g. Cloud provider). – Allow the publication of results to be performed in an open and transparent manner, without the mandatory need for third party audit functions. – Allow for data processors to demonstratively publicise their attention to Information Assurance over other suppliers that may not take it as seriously. – Avoid the subjective and bespoke arrangements that customers of such services are currently faced with. Method – Utilise existing standards such as ISO 27001, BS 25999, NIST SP 800 -53, etc to develop a series of control questions specific to the organisation. – Responses to such questions (and the subsequent detail) to be published and available. – Output to also include a score that details the providers Common Assurance Maturity score © 2011 Cloud Security Alliance, Inc. All rights reserved.
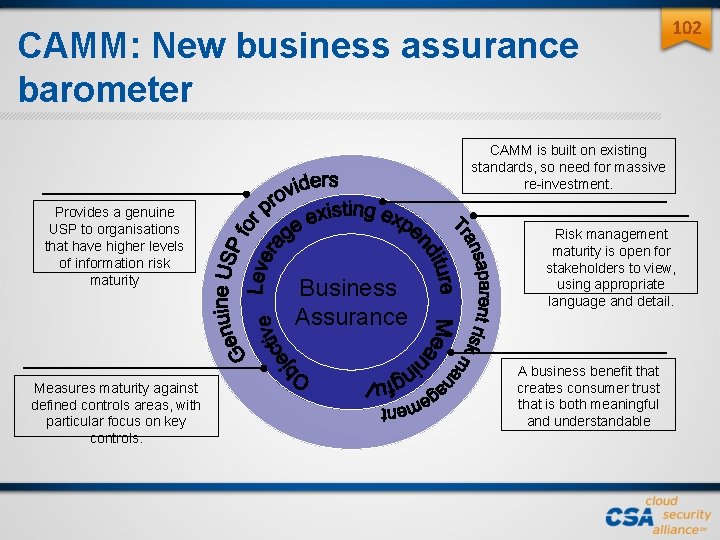
CAMM: New business assurance barometer 102 CAMM is built on existing standards, so need for massive re-investment. Provides a genuine USP to organisations that have higher levels of information risk maturity Measures maturity against defined controls areas, with particular focus on key controls. Business Assurance Risk management maturity is open for stakeholders to view, using appropriate language and detail. A business benefit that creates consumer trust that is both meaningful and understandable
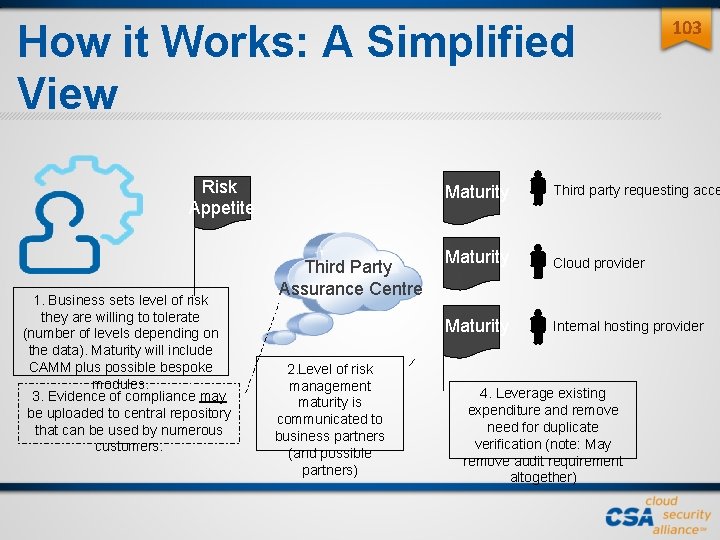
How it Works: A Simplified View Risk Appetite 1. Business sets level of risk they are willing to tolerate (number of levels depending on the data). Maturity will include CAMM plus possible bespoke modules. 3. Evidence of compliance may be uploaded to central repository that can be used by numerous customers. Third Party Assurance Centre 2. Level of risk management maturity is communicated to business partners (and possible partners) Maturity 103 Third party requesting acce Cloud provider Internal hosting provider 4. Leverage existing expenditure and remove need for duplicate verification (note: May remove audit requirement altogether)
SESSION 5 // GRC Stack Evolution and Administration © 2011 Cloud Security Alliance, Inc. All rights reserved.
105 GRC Stack Planned Evolutions Steering Committee Board Executive Director Membership Individual Standards Corporate Research Affiliate Chapters Special competencies … Research Director . . . Working Groups Education Security Guidance for Critical Areas of Cloud Computing GRC Stack (CCM, CAIQ, Cloud. Audit, CTP) CCSK Cloud Controls Matrix (CCM) CSA Security, Trust, & Assurance Registry (STAR) PCI Consensus Assessments Initiative Questionnaire (CAIQ) Trusted Cloud Initiative Legal perspectives and alterations…a © 2011 Cloud Security Alliance, Inc. All rights reserved. . GRC Stack
106 The GRC Stack Evolution Plan What is the current expansion/evolution plan for the GRC stack? Evolution 2 • Content • Timeframe Evolution 1 © 2011 Cloud Security Alliance, Inc. All rights reserved. Evolution 3
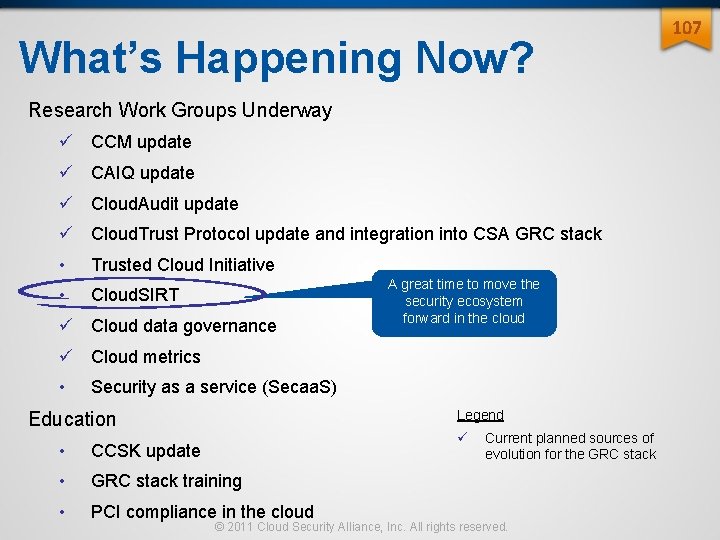
What’s Happening Now? Research Work Groups Underway ü CCM update ü CAIQ update ü Cloud. Audit update ü Cloud. Trust Protocol update and integration into CSA GRC stack • Trusted Cloud Initiative • Cloud. SIRT ü Cloud data governance A great time to move the security ecosystem forward in the cloud ü Cloud metrics • Security as a service (Secaa. S) Legend Education ü • CCSK update • GRC stack training • PCI compliance in the cloud Current planned sources of evolution for the GRC stack © 2011 Cloud Security Alliance, Inc. All rights reserved. 107
109 Cloud Security Alliance: Industry Efforts to Secure Cloud Computing A Workshop on the CSA Governance, Risk, and Compliance (GRC) Stack Jim Reavis, CSA Executive Director Ron Knode (CSC), Marlin Pohlman (EMC), Kip Boyle (…), Becky Swain (…), John Yeoh (CSA) November 2011 © 2011 Cloud Security Alliance, Inc. All rights reserved.
PM SESSIONS SESSION 9 // Connections and applications of GRC stack components in other initiatives (inside and outside the CSA) © 2011 Cloud Security Alliance, Inc. All rights reserved.
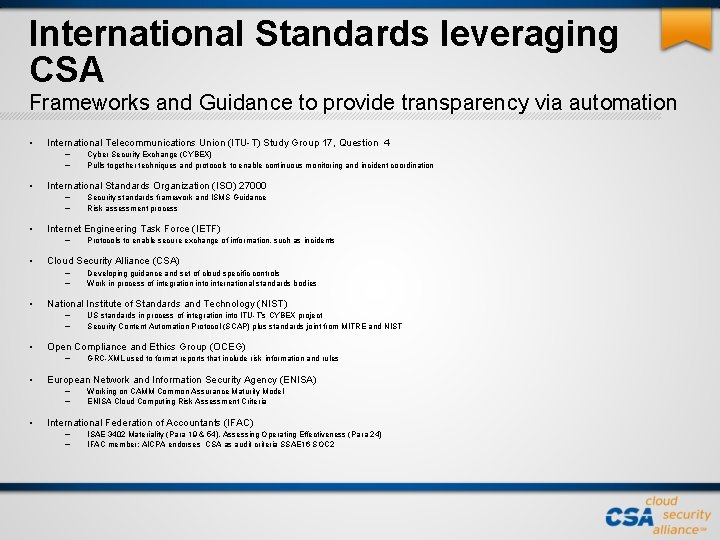
International Standards leveraging CSA Frameworks and Guidance to provide transparency via automation • International Telecommunications Union (ITU-T) Study Group 17, Question 4 – – • International Standards Organization (ISO) 27000 – – • GRC-XML used to format reports that include risk information and rules European Network and Information Security Agency (ENISA) – – • US standards in process of integration into ITU-T’s CYBEX project Security Content Automation Protocol (SCAP) plus standards joint from MITRE and NIST Open Compliance and Ethics Group (OCEG) – • Developing guidance and set of cloud specific controls Work in process of integration into international standards bodies National Institute of Standards and Technology (NIST) – – • Protocols to enable secure exchange of information, such as incidents Cloud Security Alliance (CSA) – – • Security standards framework and ISMS Guidance Risk assessment process Internet Engineering Task Force (IETF) – • Cyber Security Exchange (CYBEX) Pulls together techniques and protocols to enable continuous monitoring and incident coordination Working on CAMM Common Assurance Maturity Model ENISA Cloud Computing Risk Assessment Criteria International Federation of Accountants (IFAC) – – ISAE 3402 Materiality (Para 19 & 54), Assessing Operating Effectiveness (Para 24) IFAC member: AICPA endorses CSA as audit criteria SSAE 16 SOC 2
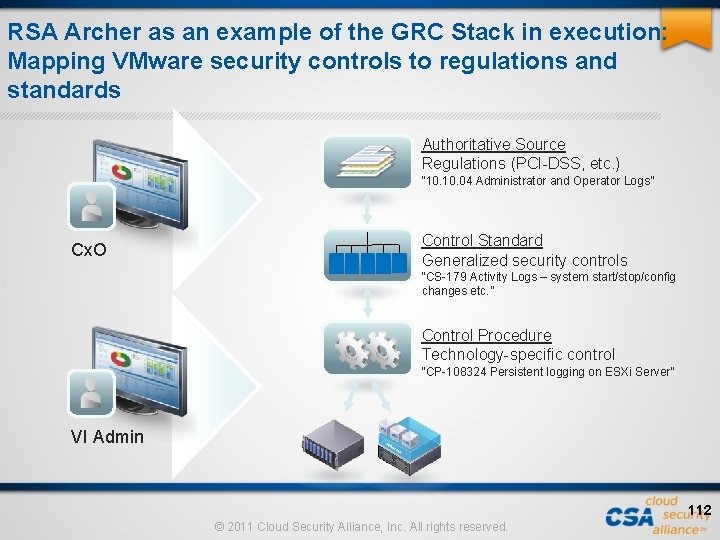
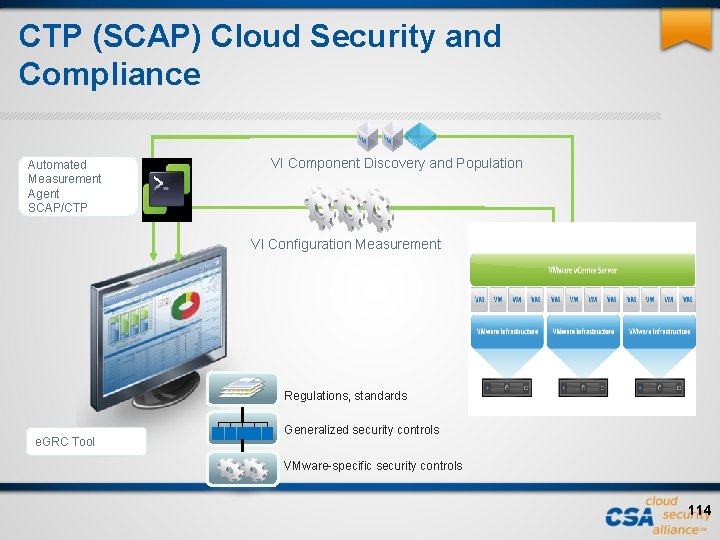
RSA Archer as an example of the GRC Stack in execution: Mapping VMware security controls to regulations and standards Authoritative Source Regulations (PCI-DSS, etc. ) “ 10. 04 Administrator and Operator Logs” Cx. O Control Standard Generalized security controls “CS-179 Activity Logs – system start/stop/config changes etc. ” Control Procedure Technology-specific control “CP-108324 Persistent logging on ESXi Server” VI Admin 112 © 2011 Cloud Security Alliance, Inc. All rights reserved.
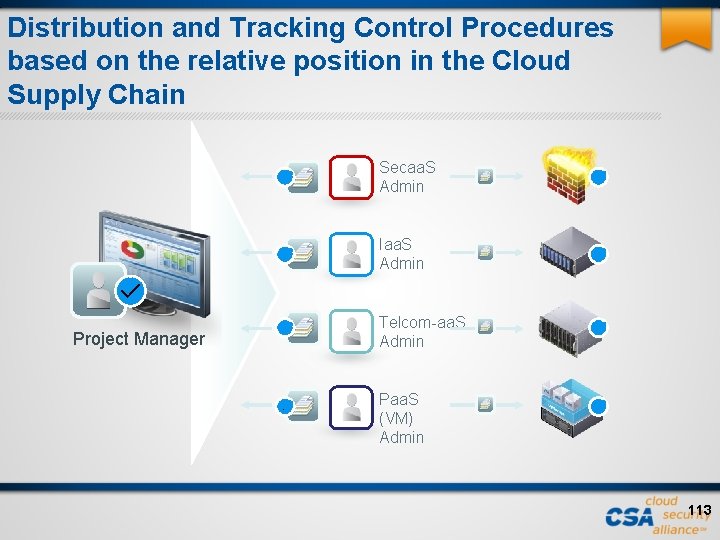
Distribution and Tracking Control Procedures based on the relative position in the Cloud Supply Chain Secaa. S Admin Iaa. S Admin Project Manager Telcom-aa. S Admin Paa. S (VM) Admin 113
CTP (SCAP) Cloud Security and Compliance Automated Measurement Agent SCAP/CTP VI Component Discovery and Population VI Configuration Measurement Regulations, standards e. GRC Tool Generalized security controls VMware-specific security controls 114
THANK YOU © 2011 Cloud Security Alliance, Inc. All rights reserved.