RIOREY DDOS The DDOS Specialist http www riorey
- Slides: 43
RIOREY DDOS 공격 방어 솔루션 The DDOS Specialist • 리오레이 웹사이트 : http: //www. riorey. co. kr / http: //www. riorey. com 콤우시스템 신상윤 010 -4842 -9153
AGENDA 1. DDOS 현황 2. RIOREY DDOS 솔루션 3. RIOREY M. B. A 알고리즘 4. RIOREY 특징 5. RIOREY r. View & r. Care http: //ddos. tistory. com 5
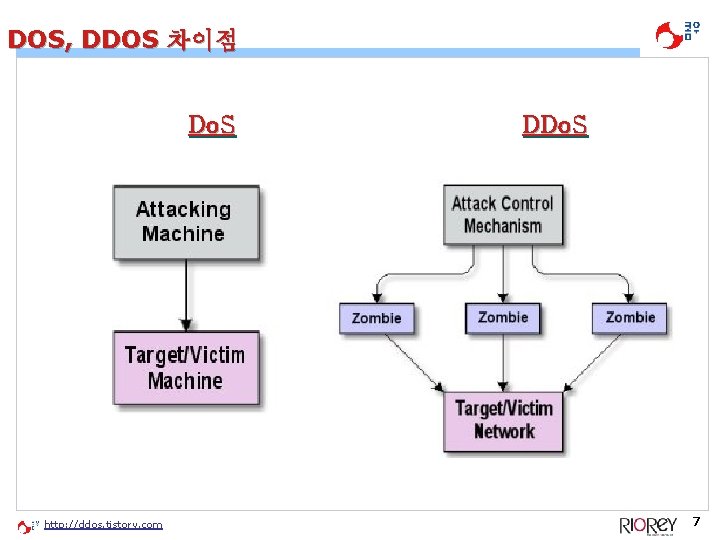
DOS, DDOS 차이점 Do. S http: //ddos. tistory. com DDo. S 7
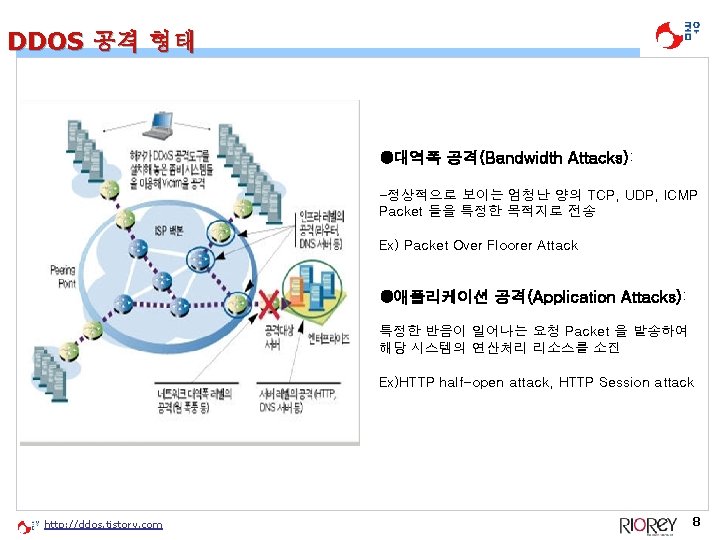
DDOS 공격 형태 ●대역폭 공격(Bandwidth Attacks): -정상적으로 보이는 엄청난 양의 TCP, UDP, ICMP Packet 들을 특정한 목적지로 전송 Ex) Packet Over Floorer Attack ●애플리케이션 공격(Application Attacks): 특정한 반응이 일어나는 요청 Packet 을 발송하여 해당 시스템의 연산처리 리소스를 소진 Ex)HTTP half-open attack, HTTP Session attack http: //ddos. tistory. com 8
2. RIOREY DDOS 솔루션 • RIOREY Over view • The DDOS Challenge • RIOREY benefit • High Availability By Design http: //ddos. tistory. com 12
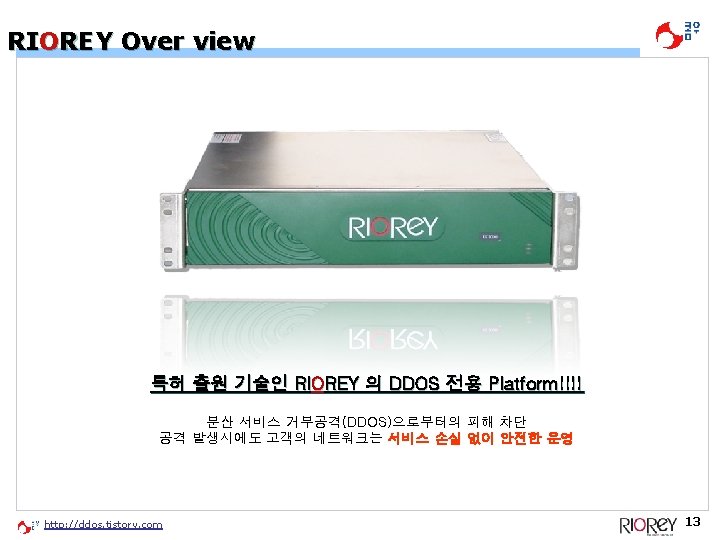
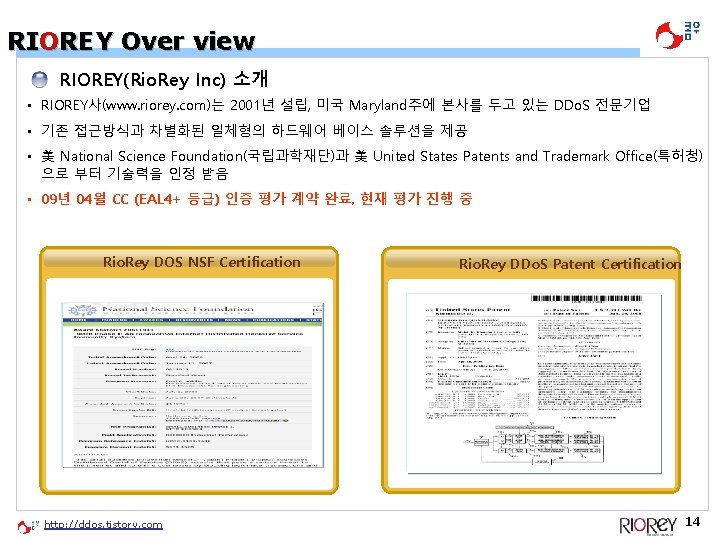
RIOREY Over view RIOREY(Rio. Rey Inc) 소개 • RIOREY사(www. riorey. com)는 2001년 설립, 미국 Maryland주에 본사를 두고 있는 DDo. S 전문기업 • 기존 접근방식과 차별화된 일체형의 하드웨어 베이스 솔루션을 제공 • 美 National Science Foundation(국립과학재단)과 美 United States Patents and Trademark Office(특허청) 으로 부터 기술력을 인정 받음 • 09년 04월 CC (EAL 4+ 등급) 인증 평가 계약 완료, 현재 평가 진행 중 Rio. Rey DOS NSF Certification http: //ddos. tistory. com Rio. Rey DDo. S Patent Certification 14
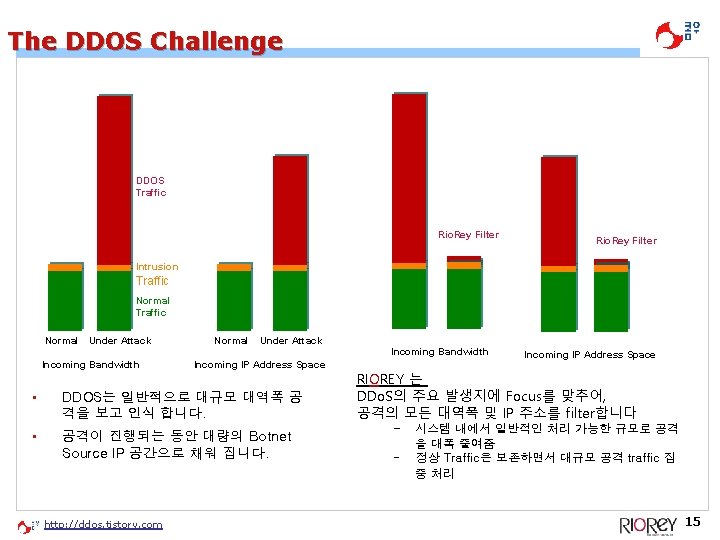
The DDOS Challenge DDOS Traffic Rio. Rey Filter Intrusion Traffic Normal Under Attack Incoming Bandwidth Incoming IP Address Space • DDOS는 일반적으로 대규모 대역폭 공 격을 보고 인식 합니다. • 공격이 진행되는 동안 대량의 Botnet Source IP 공간으로 채워 집니다. http: //ddos. tistory. com Incoming IP Address Space RIOREY 는 DDo. S의 주요 발생지에 Focus를 맞추어, 공격의 모든 대역폭 및 IP 주소를 filter합니다 - 시스템 내에서 일반적인 처리 가능한 규모로 공격 을 대폭 줄여줌 정상 Traffic은 보존하면서 대규모 공격 traffic 집 중 처리 15
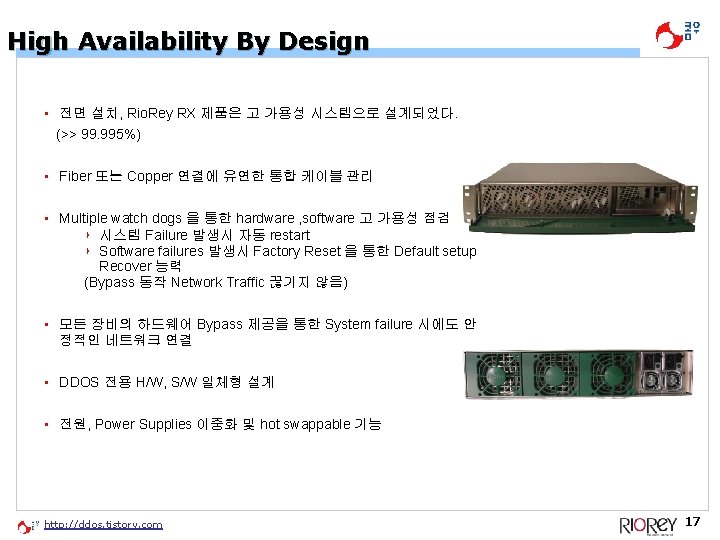
High Availability By Design • 전면 설치, Rio. Rey RX 제품은 고 가용성 시스템으로 설계되었다. (>> 99. 995%) • Fiber 또는 Copper 연결에 유연한 통합 케이블 관리 • Multiple watch dogs 을 통한 hardware , software 고 가용성 점검 ‣ 시스템 Failure 발생시 자동 restart ‣ Software failures 발생시 Factory Reset 을 통한 Default setup Recover 능력 (Bypass 동작 Network Traffic 끊기지 않음) • 모든 장비의 하드웨어 Bypass 제공을 통한 System failure 시에도 안 정적인 네트워크 연결 • DDOS 전용 H/W, S/W 일체형 설계 • 전원, Power Supplies 이중화 및 hot swappable 기능 http: //ddos. tistory. com 17
(Micro-Behavioral Analysis) 3. RIOREY M. B. A 알고리즘 • Detect Engine • Protocol Conformance Engine • Scan Identification Engine • Application Conformance Engine http: //ddos. tistory. com 18
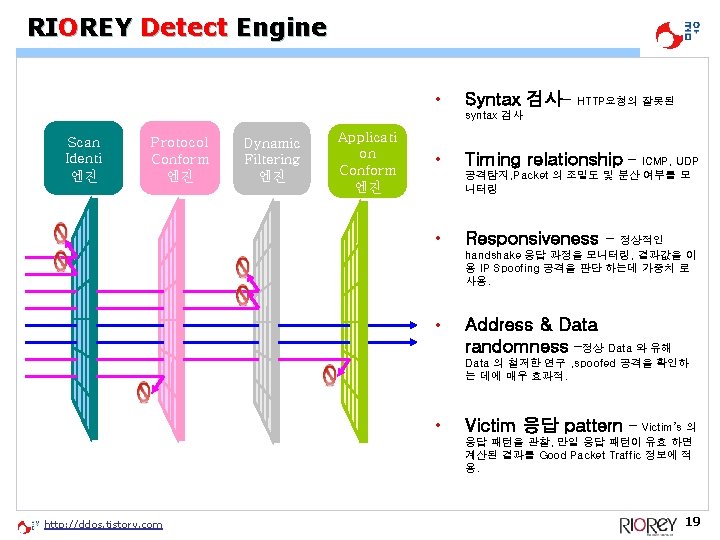
RIOREY Detect Engine • Syntax 검사- HTTP요청의 잘못된 syntax 검사 Scan Identi 엔진 Protocol Conform 엔진 Dynamic Filtering 엔진 Applicati on Conform 엔진 • Timing relationship – ICMP, UDP 공격탐지, Packet 의 조밀도 및 분산 여부를 모 니터링 • Responsiveness - 정상적인 handshake 응답 과정을 모니터링, 결과값을 이 용 IP Spoofing 공격을 판단 하는데 가중치 로 사용. • Address & Data randomness –정상 Data 와 유해 Data 의 철저한 연구 , spoofed 공격을 확인하 는 데에 매우 효과적. • Victim 응답 pattern – Victim’s 의 응답 패턴을 관찰, 만일 응답 패턴이 유효 하면 계산된 결과를 Good Packet Traffic 정보에 적 용. http: //ddos. tistory. com 19 19
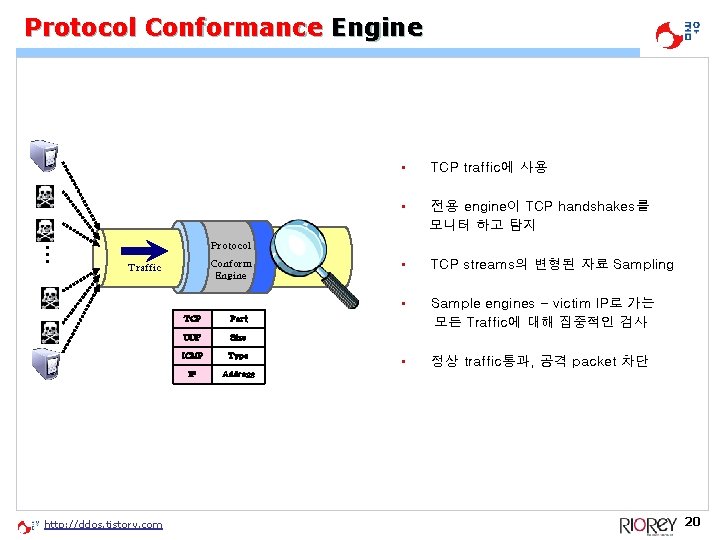
… Protocol Conformance Engine • TCP traffic에 사용 • 전용 engine이 TCP handshakes를 모니터 하고 탐지 • TCP streams의 변형된 자료 Sampling • Sample engines - victim IP로 가는 모든 Traffic에 대해 집중적인 검사 • 정상 traffic통과, 공격 packet 차단 Protocol Conform Engine Traffic http: //ddos. tistory. com TCP Port UDP Size ICMP Type IP Address 20
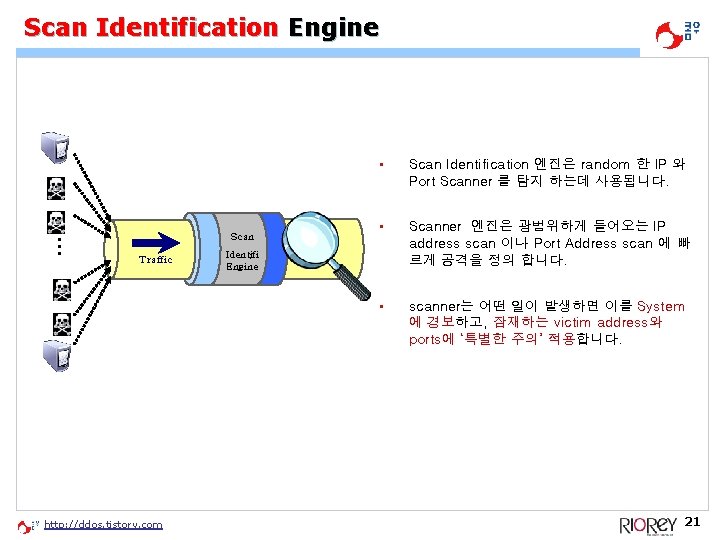
… Scan Identification Engine Scan Traffic http: //ddos. tistory. com • Scan Identification 엔진은 random 한 IP 와 Port Scanner 를 탐지 하는데 사용됩니다. • Scanner 엔진은 광범위하게 들어오는 IP address scan 이나 Port Address scan 에 빠 르게 공격을 정의 합니다. • scanner는 어떤 일이 발생하면 이를 System 에 경보하고, 잠재하는 victim address와 ports에 ‘특별한 주의’ 적용합니다. Identifi Engine 21
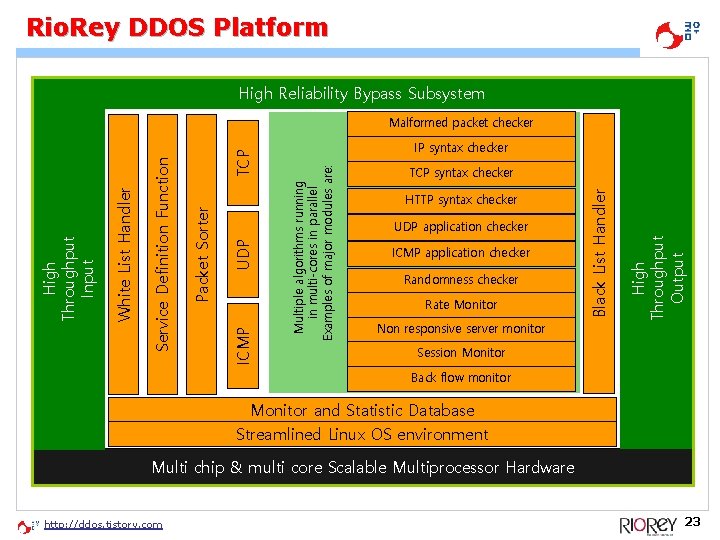
Rio. Rey DDOS Platform High Reliability Bypass Subsystem IP syntax checker HTTP syntax checker UDP application checker ICMP application checker Randomness checker Rate Monitor Non responsive server monitor High Throughput Output TCP syntax checker Black List Handler Multiple algorithms running in multi-cores in parallel Examples of major modules are: TCP UDP ICMP Packet Sorter Service Definition Function White List Handler High Throughput Input Malformed packet checker Session Monitor Back flow monitor Monitor and Statistic Database Streamlined Linux OS environment Multi chip & multi core Scalable Multiprocessor Hardware http: //ddos. tistory. com 23
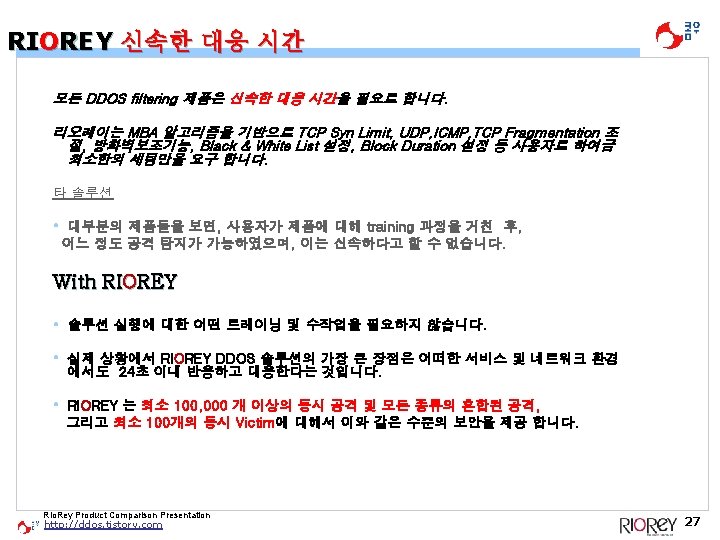
4. RIOREY 특징 • 정상 Traffics 보장 • 자동 실행 • 신속한 대응 시간 • 다양한 Product Series http: //ddos. tistory. com 24
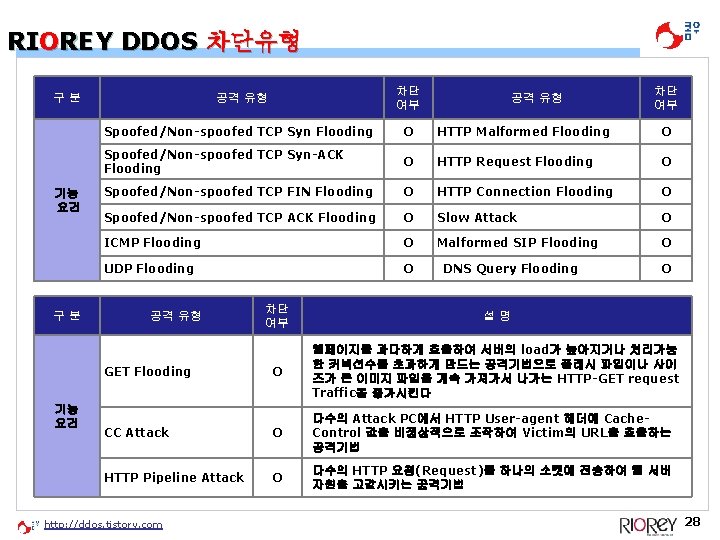
RIOREY DDOS 차단유형 공격 유형 차단 여부 Spoofed/Non-spoofed TCP Syn Flooding O HTTP Malformed Flooding O Spoofed/Non-spoofed TCP Syn-ACK Flooding O HTTP Request Flooding O Spoofed/Non-spoofed TCP FIN Flooding O HTTP Connection Flooding O Spoofed/Non-spoofed TCP ACK Flooding O Slow Attack O ICMP Flooding O Malformed SIP Flooding O UDP Flooding O 구분 기능 요건 구분 DNS Query Flooding 차단 여부 O 차단 여부 설명 O 웹페이지를 과다하게 호출하여 서버의 load가 높아지거나 처리가능 한 커넥션수를 초과하게 만드는 공격기법으로 플래시 파일이나 사이 즈가 큰 이미지 파일을 계속 가져가서 나가는 HTTP-GET request Traffic을 증가시킨다 CC Attack O 다수의 Attack PC에서 HTTP User-agent 헤더에 Cache. Control 값을 비정상적으로 조작하여 Victim의 URL을 호출하는 공격기법 HTTP Pipeline Attack O 다수의 HTTP 요청(Request)를 하나의 소켓에 전송하여 웹 서버 자원을 고갈시키는 공격기법 공격 유형 GET Flooding 기능 요건 공격 유형 http: //ddos. tistory. com 28
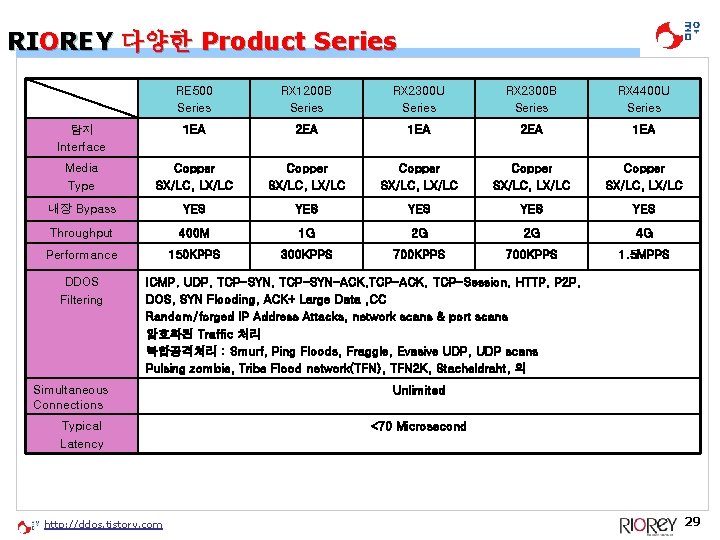
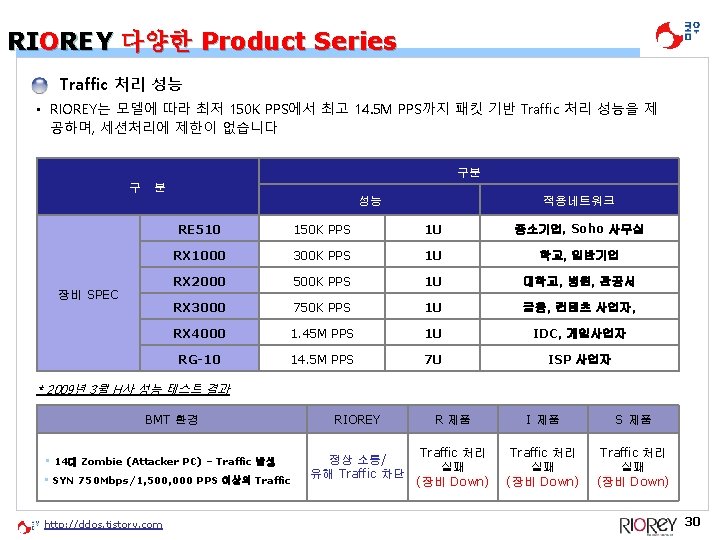
RIOREY 다양한 Product Series RE 500 Series RX 1200 B Series RX 2300 U Series RX 2300 B Series RX 4400 U Series 탐지 Interface 1 EA 2 EA 1 EA Media Type Copper SX/LC, LX/LC Copper SX/LC, LX/LC 내장 Bypass YES YES YES Throughput 400 M 1 G 2 G 2 G 4 G Performance 150 KPPS 300 KPPS 700 KPPS 1. 5 MPPS DDOS Filtering ICMP, UDP, TCP-SYN-ACK, TCP-Session, HTTP, P 2 P, DOS, SYN Flooding, ACK+ Large Data , CC Random/forged IP Address Attacks, network scans & port scans 암호화된 Traffic 처리 복합공격처리 : Smurf, Ping Floods, Fraggle, Evasive UDP, UDP scans Pulsing zombie, Tribe Flood network(TFN), TFN 2 K, Stacheldraht, 외 Simultaneous Connections Typical Latency http: //ddos. tistory. com Unlimited <70 Microsecond 29
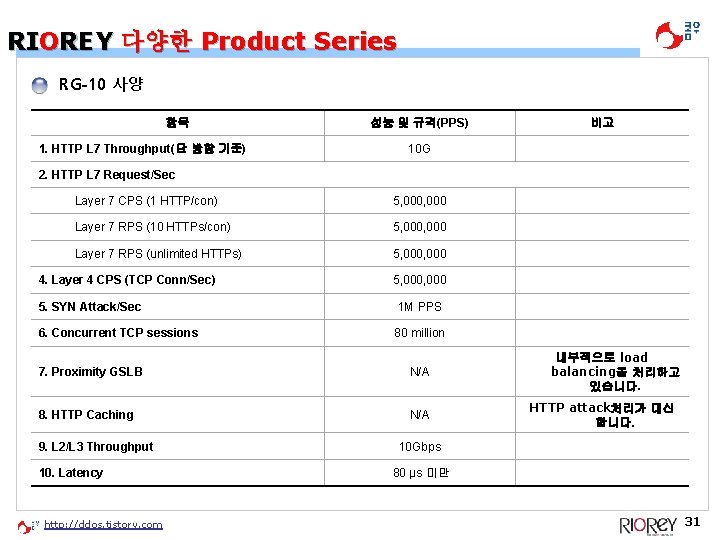
RIOREY 다양한 Product Series RG-10 사양 항목 1. HTTP L 7 Throughput(단 방향 기준) 성능 및 규격(PPS) 비고 10 G 2. HTTP L 7 Request/Sec Layer 7 CPS (1 HTTP/con) 5, 000 Layer 7 RPS (10 HTTPs/con) 5, 000 Layer 7 RPS (unlimited HTTPs) 5, 000 4. Layer 4 CPS (TCP Conn/Sec) 5, 000 5. SYN Attack/Sec 1 M PPS 6. Concurrent TCP sessions 80 million 7. Proximity GSLB N/A 8. HTTP Caching N/A 9. L 2/L 3 Throughput 10. Latency http: //ddos. tistory. com 내부적으로 load balancing을 처리하고 있습니다. HTTP attack처리가 대신 합니다. 10 Gbps 80 μs 미만 31
5. RIOREY r. View & r. Care • r. VIEW • r. CARE • 주요 References http: //ddos. tistory. com 32
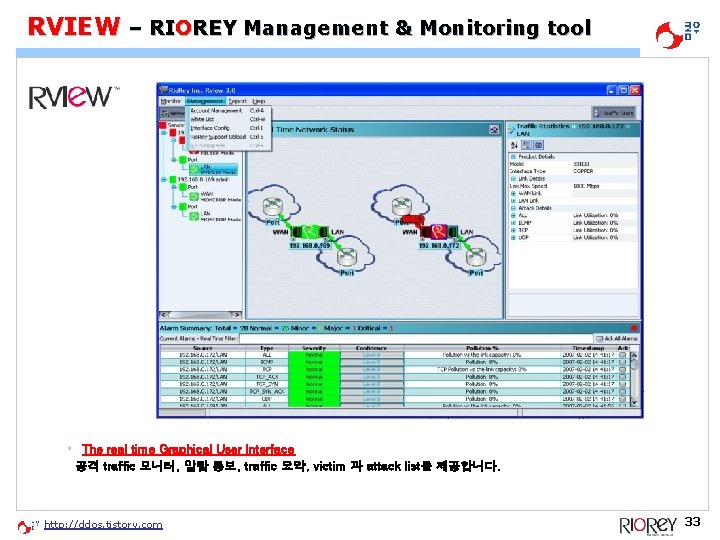
RVIEW – RIOREY Management & Monitoring tool • The real time Graphical User Interface 공격 traffic 모니터, 알람 통보, traffic 요약, victim 과 attack list를 제공합니다. http: //ddos. tistory. com 33 33
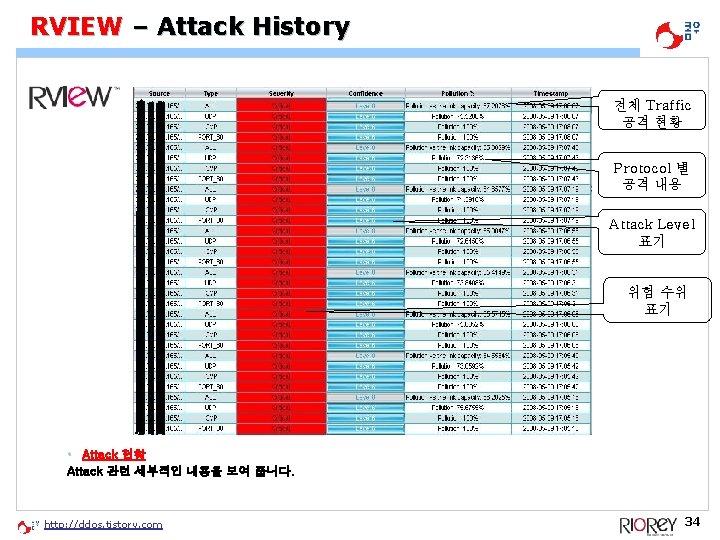
RVIEW – Attack History 전체 Traffic 공격 현황 Protocol 별 공격 내용 Attack Level 표기 위험 수위 표기 • Attack 현황 Attack 관련 세부적인 내용을 보여 줍니다. http: //ddos. tistory. com 34 34
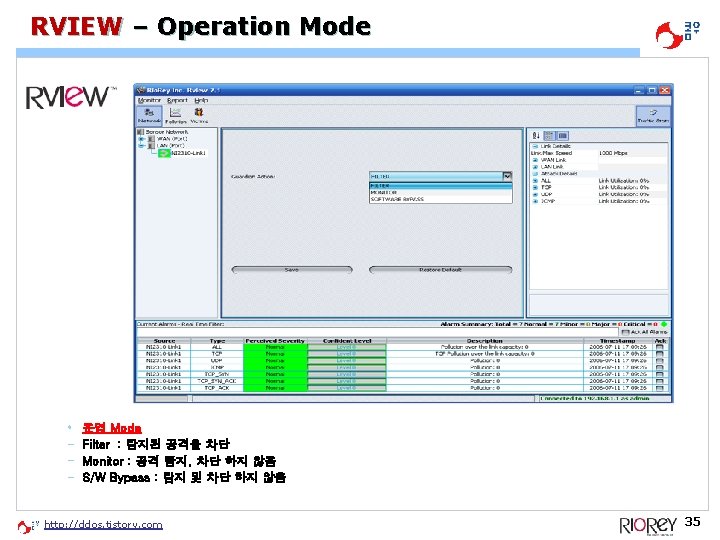
RVIEW – Operation Mode • - 운영 Mode Filter : 탐지된 공격을 차단 Monitor : 공격 탐지, 차단 하지 않음 S/W Bypass : 탐지 및 차단 하지 않음 http: //ddos. tistory. com 35 35
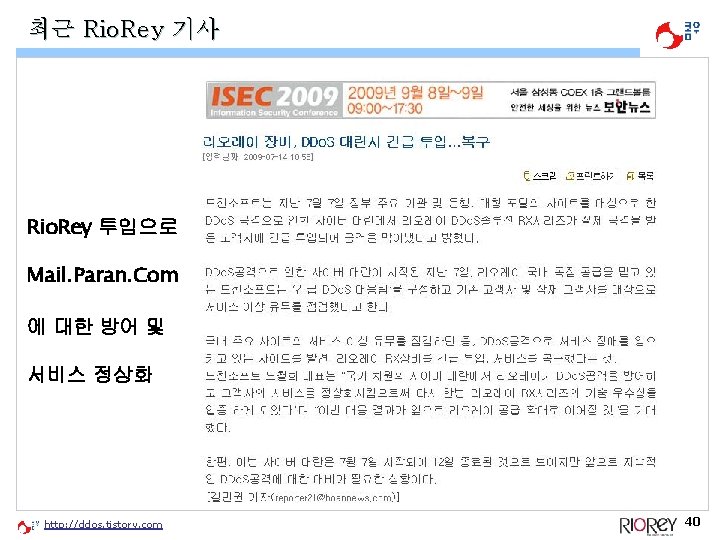
최근 Rio. Rey 기사 Rio. Rey 투입으로 Mail. Paran. Com 에 대한 방어 및 서비스 정상화 http: //ddos. tistory. com 40
최근 Rio. Rey 기사 http: //ddos. tistory. com 41
최근 Rio. Rey 기사 http: //ddos. tistory. com 42
T h a n k Y o u