Neutering Ettercap in Cisco Switched Networks For fun
- Slides: 68
Neutering Ettercap in Cisco Switched Networks For fun and Profit
What’s With the Title? (AKA Scope) v. How the protocols function under normal and malicious circumstances v. Ettercap’s Capabilities for Protocol Abuse DHCP Spoofing - ARP Poisoning ICMP Redirects - Port Stealing v. Countermeasures to defend against these kind of abuses 2
What’s With the Title? (AKA Scope) v. Configuring Countermeasures for Cisco. IOS v. Best Practices for implementation v. This is for CISCO NETWORKS ONLY! (sorry Juniper) 3
Why Protocol Abuse Works Ø The Protocols are OLD! Created during a more friendly time in networking. Ø Were not created with authentication measures or security in mind Ø Engineers were focused on transmitting data without errors, not who was sending it or what was being sent. 4
Lets spoof some DHCP! You can trust me, I’m a nice DHCP Server. ; ) 5
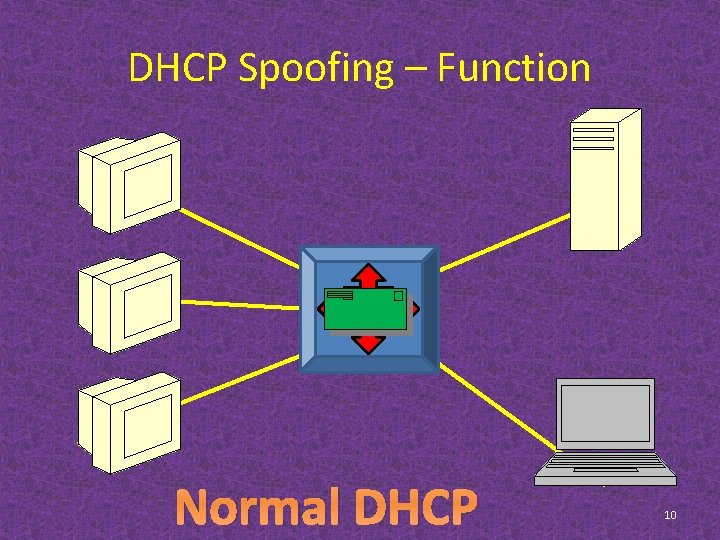
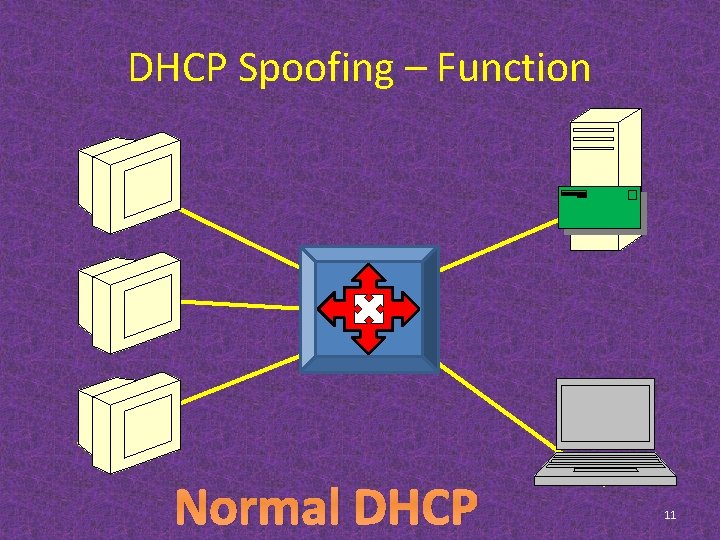
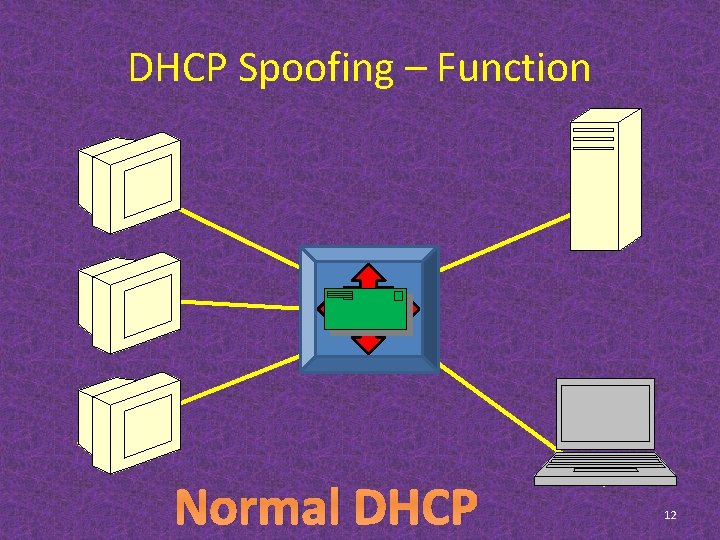
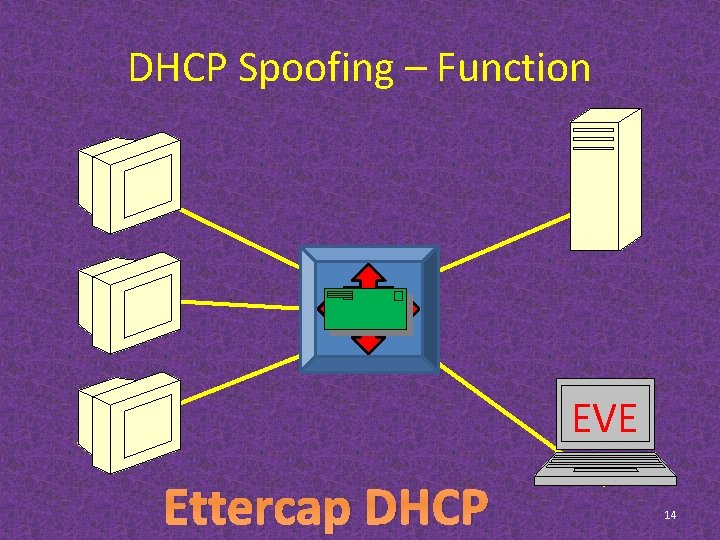
DHCP Spoofing – Function Dynamic Host Configuration Protocol(DHCP), permits host connected to a Local Area Network(LAN) segment to be dynamically assigned parameters necessary for the host to send and receive data over a network. The exchange of DHCP information is sent as a 'broadcast', which means that any host on the LAN segment will receive a copy of the DHCP exchange. 6
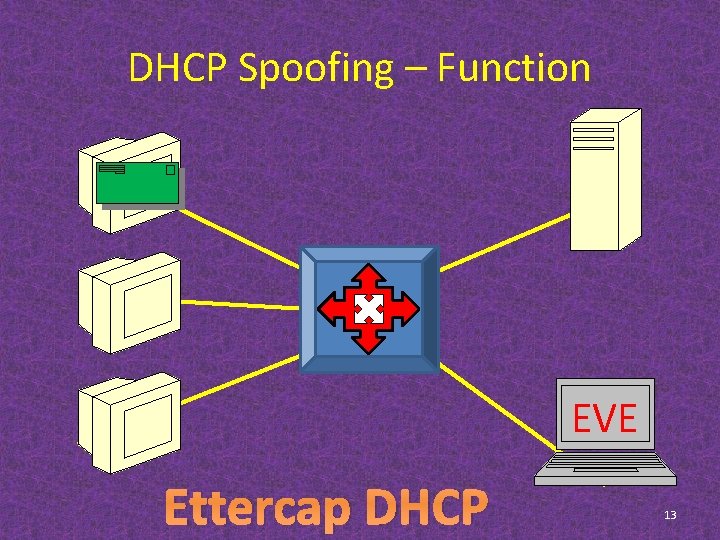
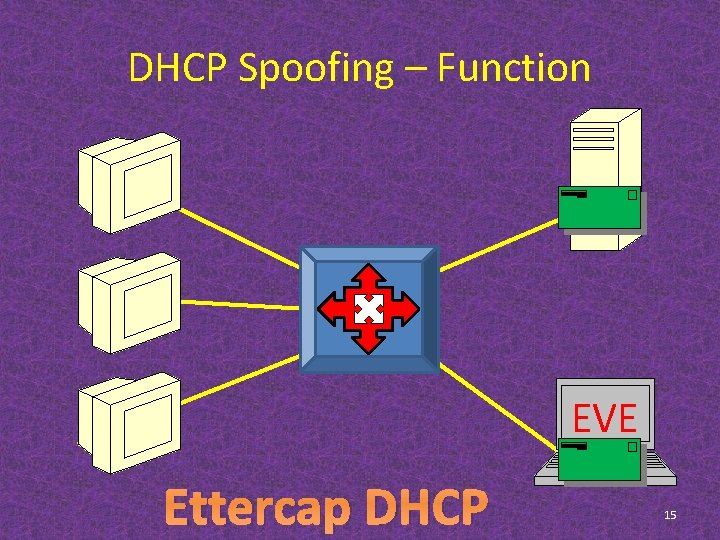
DHCP Spoofing – Function Normally, a host would ignore this exchange, but Ettercap has a feature built in to intercept and quickly reply to these DHCP messages before the authentic DHCP server can reply. This will cause the host to continue the exchange with the Ettercap and ignore the authenticate server. 7
DHCP Spoofing – Function The main purpose of this is to tell the host to use the Ettercap machine as its 'Default Gateway', the address it will forward data destined for off the network. This will allow for a 'Half. Duplex' Mit. M, meaning the attacker will only see half of the exchange, as the return packets will not be seen by the attacker unless combined with tunneling techniques. 8
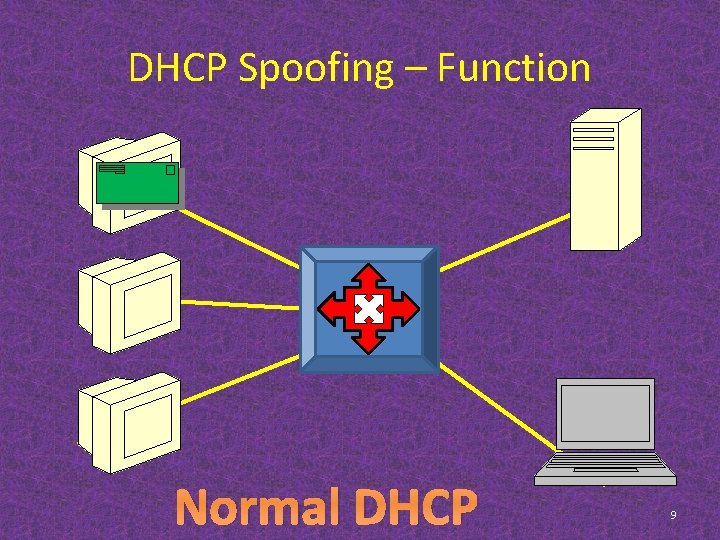
DHCP Spoofing – Function Normal DHCP 9
DHCP Spoofing – Function Normal DHCP 10
DHCP Spoofing – Function Normal DHCP 11
DHCP Spoofing – Function Normal DHCP 12
DHCP Spoofing – Function EVE Ettercap DHCP 13
DHCP Spoofing – Function EVE Ettercap DHCP 14
DHCP Spoofing – Function EVE Ettercap DHCP 15
DHCP Spoofing – Countermeasures To combat not only Ettercap, but all rogue DHCP Servers, the ‘IP DHCP Snooping’ process will be enabled. Available on both Layer 2&3 switches, DHCP Snooping applies a two pronged approach. 16
DHCP Spoofing – Countermeasures IP DHCP Snooping only allows authentic DHCP servers to be able to reply to transactions. Rogue servers that send replies to DHCP request will have the reply packet dropped by the switch and a log message will be generated. The DHCP Transaction will still be visible to all host on the LAN segment, but replies are strictly policed using 'Trusted Interfaces'. 17
DHCP Spoofing – Countermeasures DHCP replies received on a Trusted Interface(Switch port) are forwarded automatically, however, all ports on the switch will be Untrusted by default. Only ports leading to Gateway Routers and/or other DHCP Snooping enabled switches should be set to Trusted. 18
DHCP Spoofing – Countermeasures IMPORTANT NOTE: Unless your DHCP server supports Option 82 tagging, you must disable it! Cisco switches by default will tag snooped DHCP transactions with Option 82 information before forwarding. This will more than likely cause the DHCP server to ignore the request, creating an inadvertent Do. S situation. 19
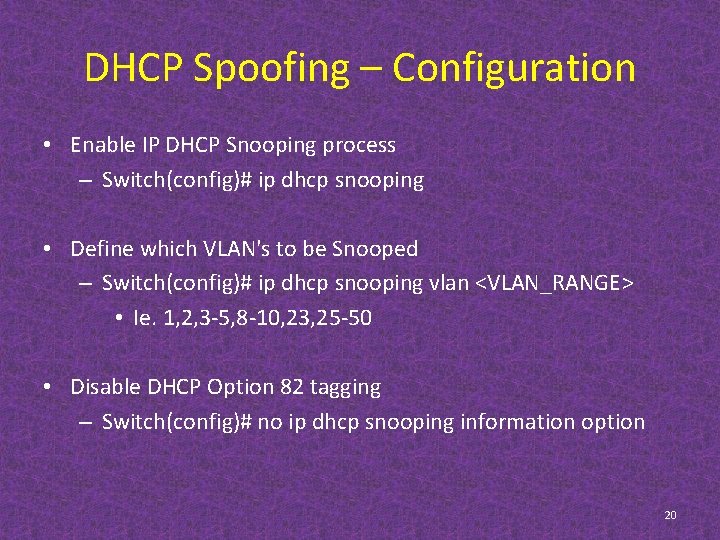
DHCP Spoofing – Configuration • Enable IP DHCP Snooping process – Switch(config)# ip dhcp snooping • Define which VLAN's to be Snooped – Switch(config)# ip dhcp snooping vlan <VLAN_RANGE> • Ie. 1, 2, 3 -5, 8 -10, 23, 25 -50 • Disable DHCP Option 82 tagging – Switch(config)# no ip dhcp snooping information option 20
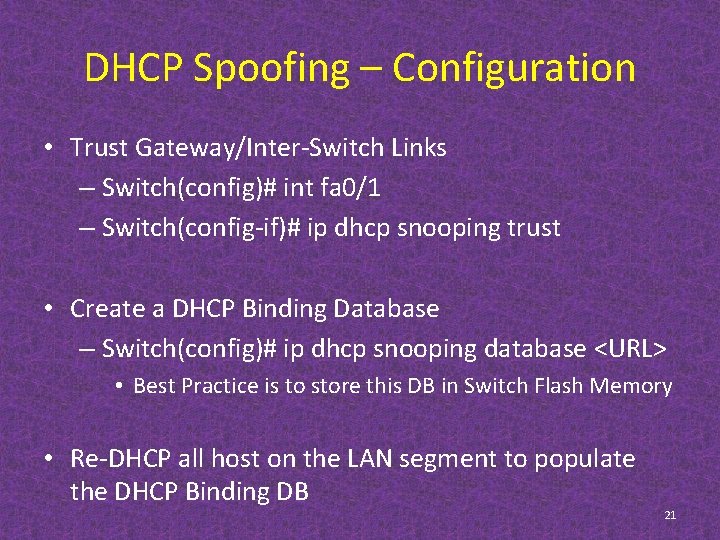
DHCP Spoofing – Configuration • Trust Gateway/Inter-Switch Links – Switch(config)# int fa 0/1 – Switch(config-if)# ip dhcp snooping trust • Create a DHCP Binding Database – Switch(config)# ip dhcp snooping database <URL> • Best Practice is to store this DB in Switch Flash Memory • Re-DHCP all host on the LAN segment to populate the DHCP Binding DB 21
DHCP Spoofing – Countermeasures Bonus! • To prevent DHCP Starvation Attacks, set a DHCP packet-per-second limit on untrusted interfaces – Switch(config-if)# int range fa 0/2 -24 – Switch(config-if)# ip dhcp snooping limit rate <#_OF_DHCP_PPS> • 3 DHCP Packets-Per-Second is a best practice 22
Won’t some one think of the child. . Er… ARPs? ! All your ARPS are belongs to us! 23
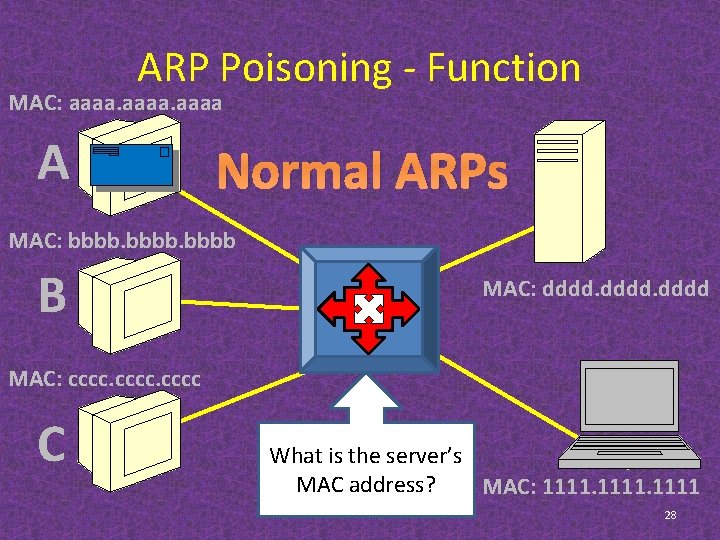
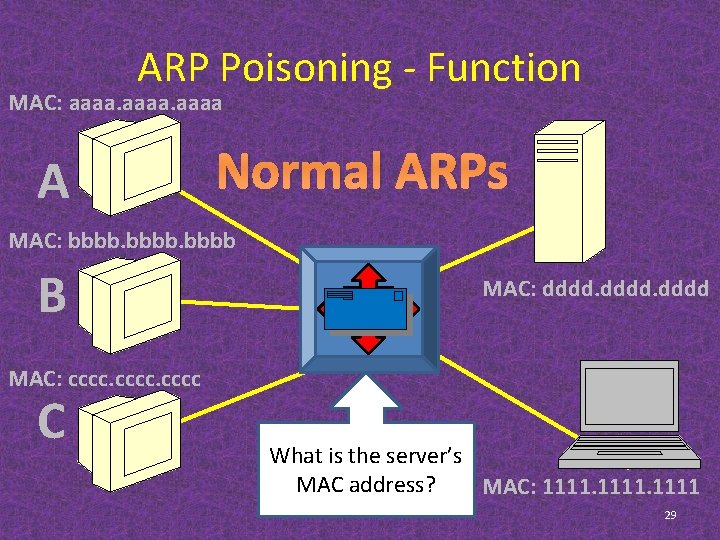
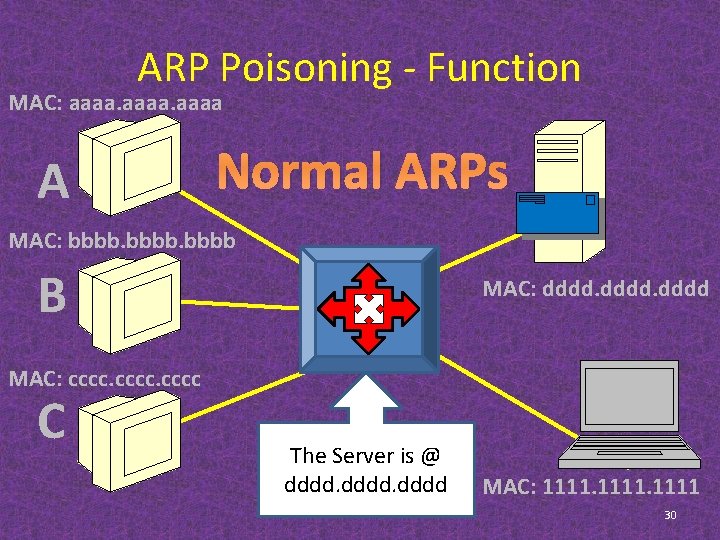
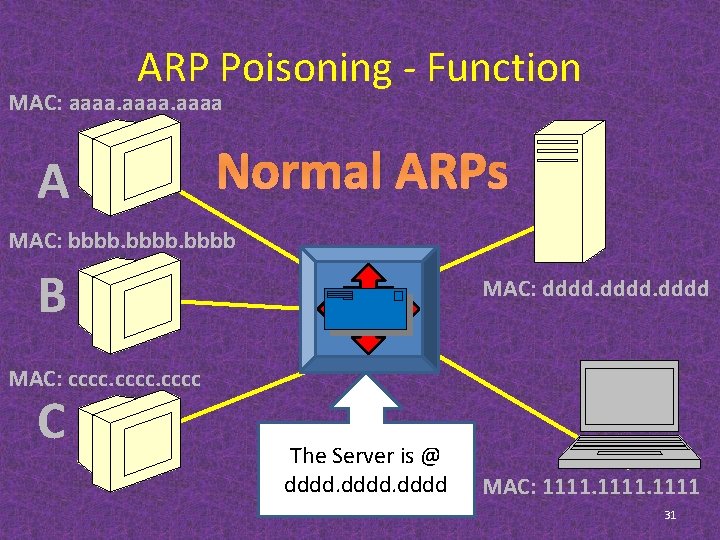
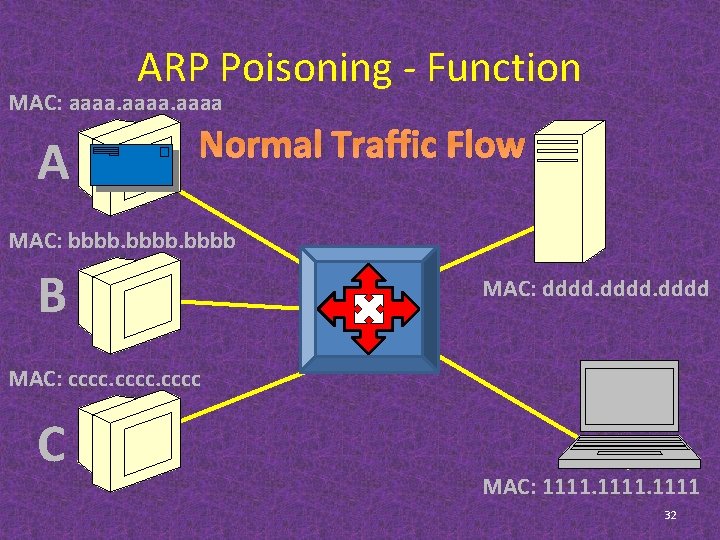
ARP Poisoning - Function Address Resolution Protocol(ARP), allows host to communicate over a LAN segment with each other. Networks are defined by their physical(Layer 2), and logical(Layer 3) design, or topology. It is normal for the two topologies to be completely different, and ARP allows for a mapping between the two. 24
ARP Poisoning - Function This is important due to the fact of how switches and routers forward data. Switches forward data primarily based on the physical topology, where as Routers forward based solely on the logical topology. If layer 2 can be controlled, so can every other OSI Layer above it. 25
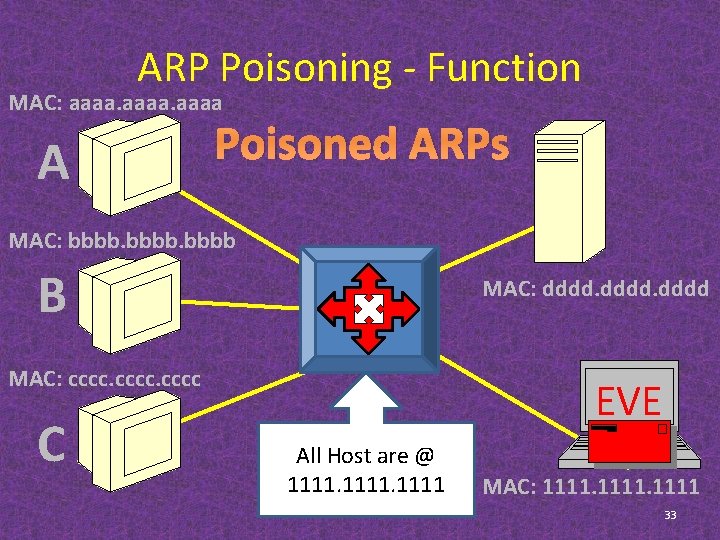
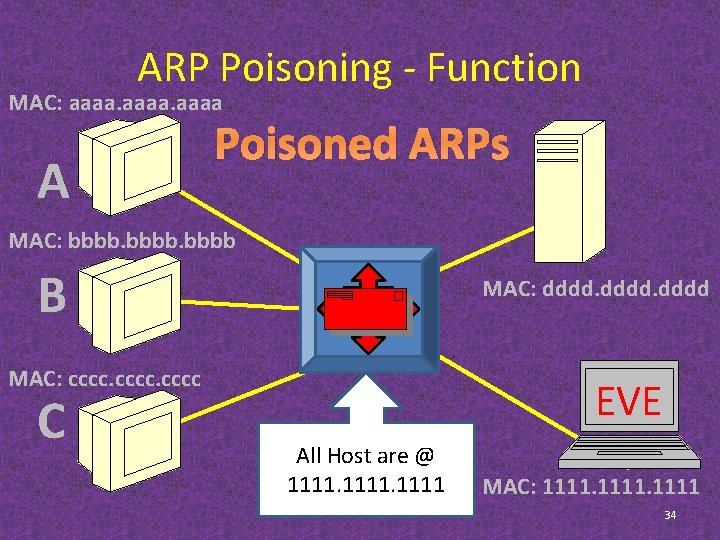
ARP Poisoning - Function By producing falsified ARP broadcast, Ettercap can convince both host and Routers alike to forward all of their traffic through the attacker's host physical address. Ettercap will basically trick all or some of the host on the LAN, that its physical address is equal to the victim's logical address. 26
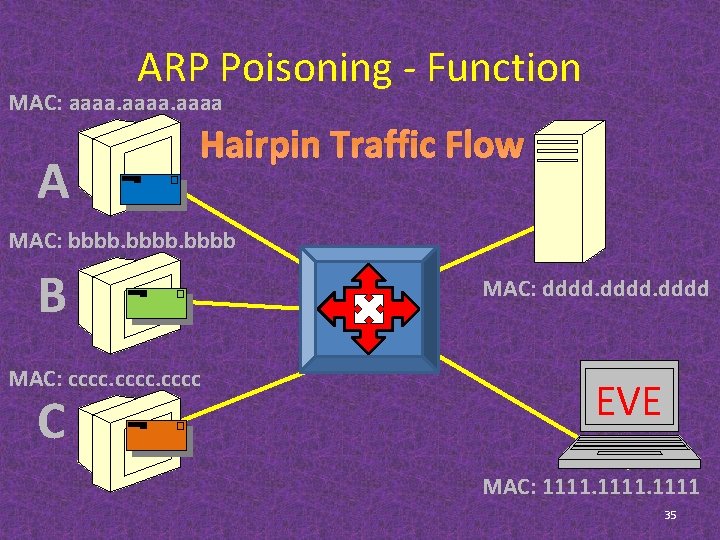
ARP Poisoning - Function This is very powerful, as it creates a Full. Duplex Mit. M, in that both sent and received data will be seen by the attacker. Particularly powerful functionality of Ettercap is the ability to intercept negotiation of encryption parameters for SSH and SSL tunnels, allowing the attacker to read the encrypted data in plain text. 27
ARP Poisoning - Function MAC: aaaa A Normal ARPs MAC: bbbb B MAC: dddd MAC: cccc C What is the server’s MAC address? MAC: 1111 28
ARP Poisoning - Function MAC: aaaa A Normal ARPs MAC: bbbb B MAC: dddd MAC: cccc C What is the server’s MAC address? MAC: 1111 29
ARP Poisoning - Function MAC: aaaa A Normal ARPs MAC: bbbb B MAC: dddd MAC: cccc C The Server is @ dddd MAC: 1111 30
ARP Poisoning - Function MAC: aaaa A Normal ARPs MAC: bbbb B MAC: dddd MAC: cccc C The Server is @ dddd MAC: 1111 31
ARP Poisoning - Function MAC: aaaa A Normal Traffic Flow MAC: bbbb B MAC: dddd MAC: cccc C MAC: 1111 32
ARP Poisoning - Function MAC: aaaa A Poisoned ARPs MAC: bbbb B MAC: dddd MAC: cccc C EVE All Host are @ 1111 MAC: 1111 33
ARP Poisoning - Function MAC: aaaa A Poisoned ARPs MAC: bbbb B MAC: dddd MAC: cccc C EVE All Host are @ 1111 MAC: 1111 34
ARP Poisoning - Function MAC: aaaa A Hairpin Traffic Flow MAC: bbbb B MAC: cccc C MAC: dddd EVE MAC: 1111 35
ARP Poisoning - Countermeasures Cisco Switches, both layer 2 & layer 3, support a process called 'Dynamic ARP Inspection'(DAI). The DAI process works in tandem with DHCP Snooping builds an internal database of Layer 2 -to-3 mappings, the very thing ARP is used to determine. 36
ARP Poisoning - Countermeasures Since the switch has seen the entire DHCP transaction, and knows which of its switch ports the request came from, it is able to track these bindings to indentify false ARP broadcast and kill them before they propagate to other host. 37
ARP Poisoning - Countermeasures Every Invalid ARP Reply will be dropped by the switch and generates a log message. ARP Request will still be allowed to propagate as normal, since they need to reach their target to elicit a reply. 38
ARP Poisoning - Countermeasures Only ARP Replies are being policed, and must pass inspection of the first receiving switch, which will then place it in a 'trust-zone' of clean ARPs. DAI places all interfaces in an untrusted state by default, meaning ARP replies received on that interface must be validated. 39
ARP Poisoning - Countermeasures Router/Inter-switch Links connected only to other DAI enabled switches should be trusted(ARP Access-List is a more secure option for routers). Host that have static network assignments, will have a static binding set on the switch they are directly connected too. 40
ARP Poisoning - Configuration • Enable DAI Process on appropriate VLANs – Switch(config)#ip arp inspection <VLAN_RANGE> • Trust links connected ONLY to Routers & other DAI enabled switches – Switch(config)# int fa 0/1 – Switch(config-if)# ip arp inspection trust • Set a ARP PPS limit on untrusted interfaces – Switch(config)# int range fa 0/2 -24 – Switch(config-if)# ip arp inspection limit rate <#_OF_ARP_PPS> 41
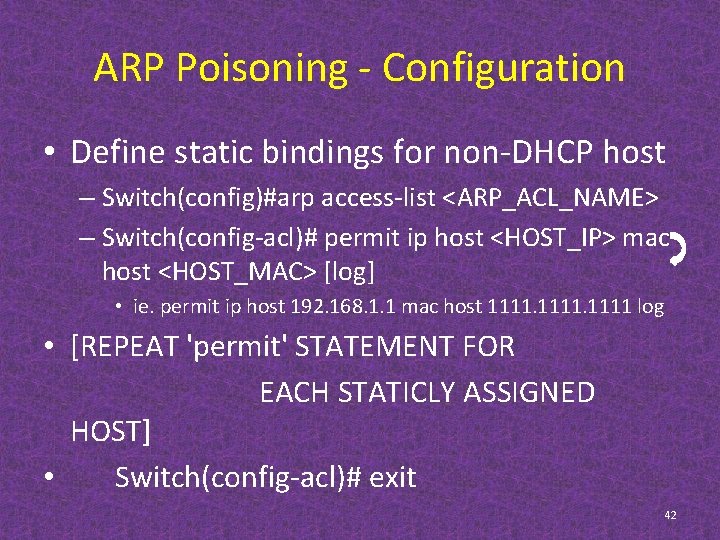
ARP Poisoning - Configuration • Define static bindings for non-DHCP host – Switch(config)#arp access-list <ARP_ACL_NAME> – Switch(config-acl)# permit ip host <HOST_IP> mac host <HOST_MAC> [log] • ie. permit ip host 192. 168. 1. 1 mac host 1111 log • [REPEAT 'permit' STATEMENT FOR EACH STATICLY ASSIGNED HOST] • Switch(config-acl)# exit 42
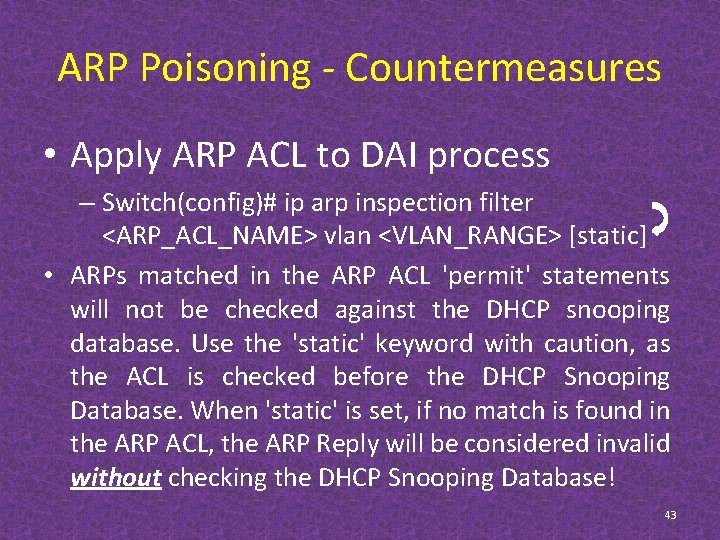
ARP Poisoning - Countermeasures • Apply ARP ACL to DAI process – Switch(config)# ip arp inspection filter <ARP_ACL_NAME> vlan <VLAN_RANGE> [static] • ARPs matched in the ARP ACL 'permit' statements will not be checked against the DHCP snooping database. Use the 'static' keyword with caution, as the ACL is checked before the DHCP Snooping Database. When 'static' is set, if no match is found in the ARP ACL, the ARP Reply will be considered invalid without checking the DHCP Snooping Database! 43
ICMP; Networking Ballistic Missiles! Break Out the SPF 9000! 44
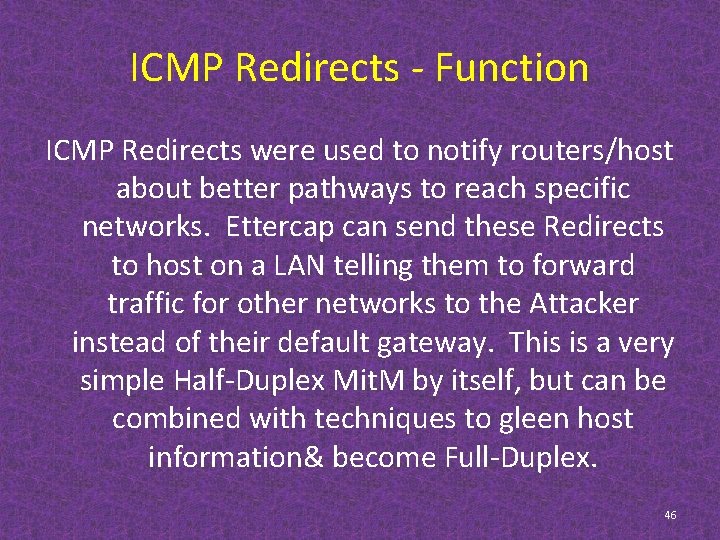
ICMP Redirects - Function The Internet Control Message Protocol(ICMP) is in reality a small suite of protocols used to pass network information between nodes. ICMP is more or less a legacy protocol, in that most of its functionality has been replaced and improved upon by other protocols. However, host operating systems still process most, if not all, ICMP request in the spirit of backwards compatibility. 45
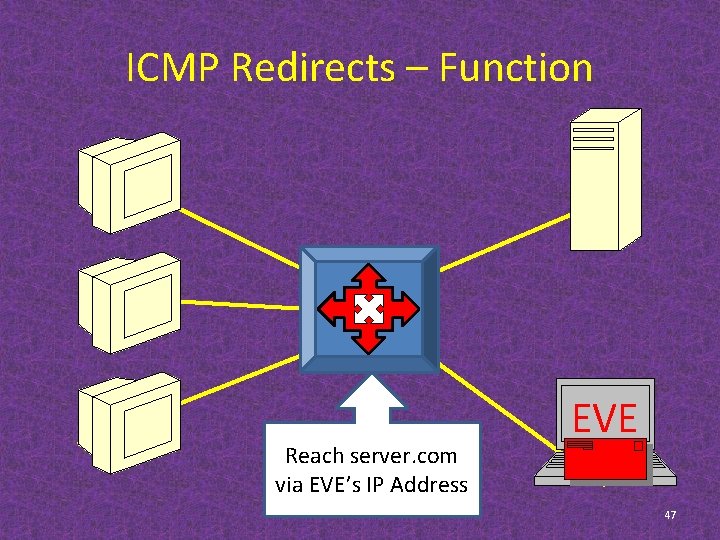
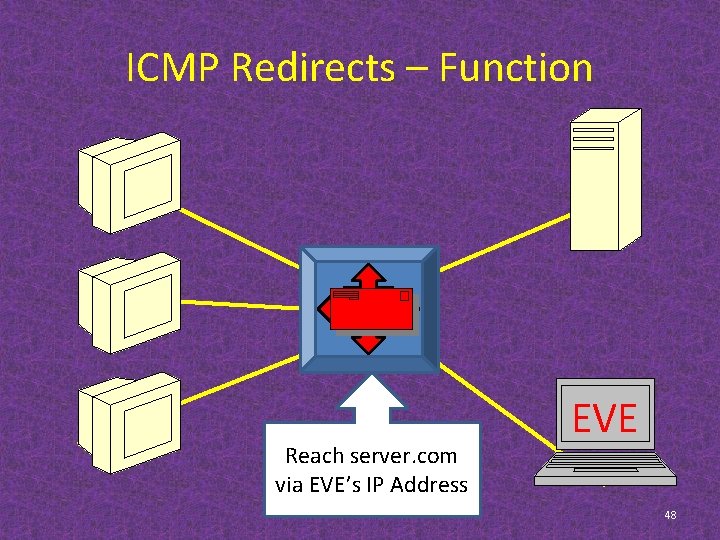
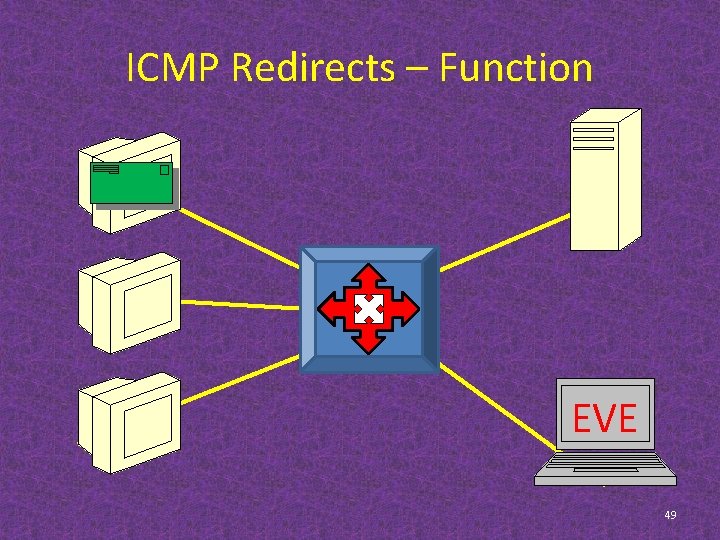
ICMP Redirects - Function ICMP Redirects were used to notify routers/host about better pathways to reach specific networks. Ettercap can send these Redirects to host on a LAN telling them to forward traffic for other networks to the Attacker instead of their default gateway. This is a very simple Half-Duplex Mit. M by itself, but can be combined with techniques to gleen host information& become Full-Duplex. 46
ICMP Redirects – Function Reach server. com via EVE’s IP Address EVE 47
ICMP Redirects – Function Reach server. com via EVE’s IP Address EVE 48
ICMP Redirects – Function EVE 49
ICMP Redirects - Countermeasures VLAN Access-Control Lists(VACLs), can be configured on Layer 3 switches to police traffic passing within a VLAN. Unlike traditional ACLs, VLANs do not understand the concept of 'inbound' or 'outbound', so they are applied with the use of a ‘VLAN access-map'. VLAN Access-maps can reference ACLs to determine protocols that can be allowed or denied on the VLAN segment. 50
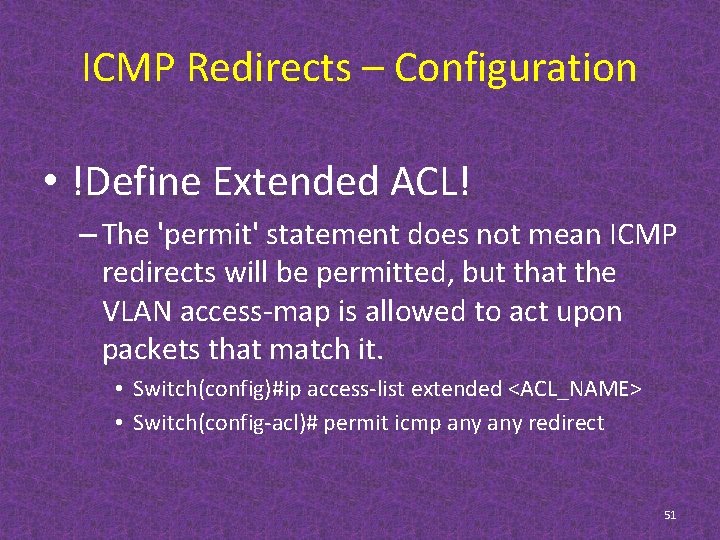
ICMP Redirects – Configuration • !Define Extended ACL! – The 'permit' statement does not mean ICMP redirects will be permitted, but that the VLAN access-map is allowed to act upon packets that match it. • Switch(config)#ip access-list extended <ACL_NAME> • Switch(config-acl)# permit icmp any redirect 51
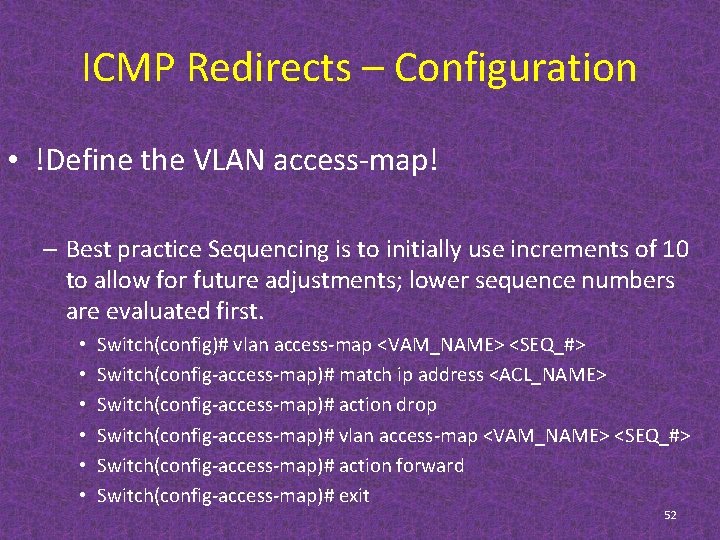
ICMP Redirects – Configuration • !Define the VLAN access-map! – Best practice Sequencing is to initially use increments of 10 to allow for future adjustments; lower sequence numbers are evaluated first. • • • Switch(config)# vlan access-map <VAM_NAME> <SEQ_#> Switch(config-access-map)# match ip address <ACL_NAME> Switch(config-access-map)# action drop Switch(config-access-map)# vlan access-map <VAM_NAME> <SEQ_#> Switch(config-access-map)# action forward Switch(config-access-map)# exit 52
ICMP Redirects – Configuration • !Apply VACL filter to the VLAN(s)! – Switch(config)# vlan filter <VAM_NAME> vlan-list <VLAN_RANGE> 53
Thou Shall Not Port Steal! I promise to bring it right back! 54
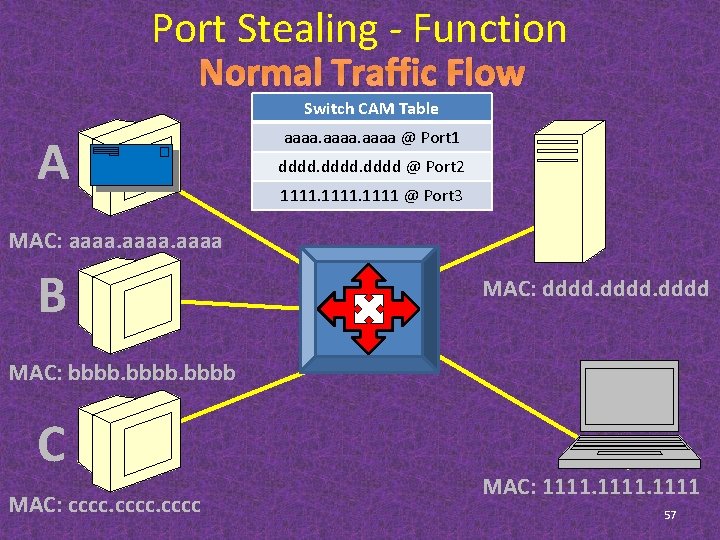
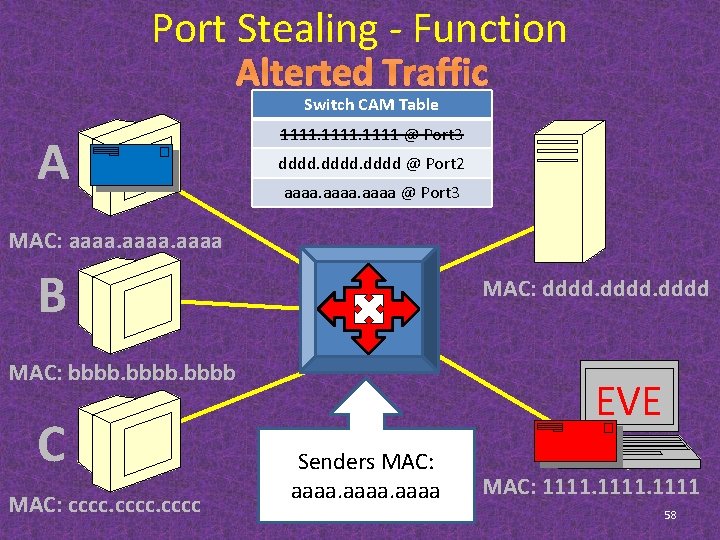
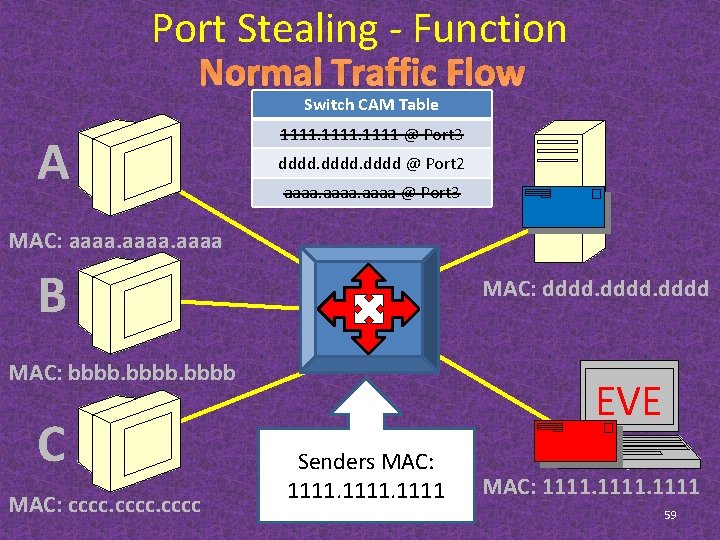
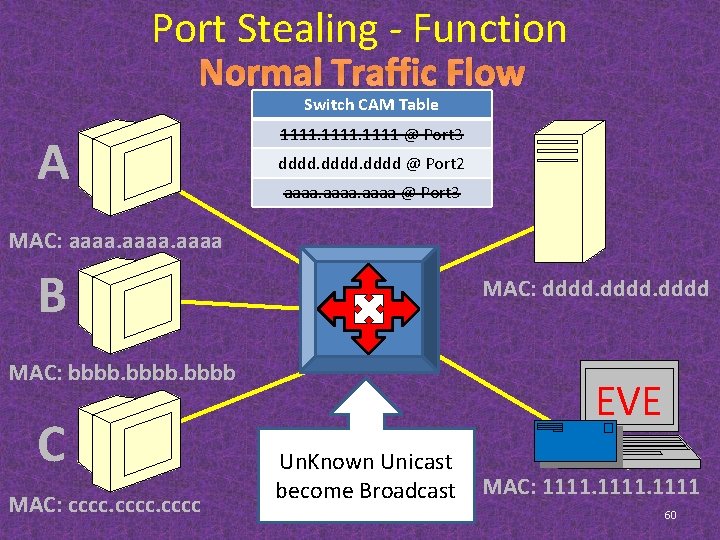
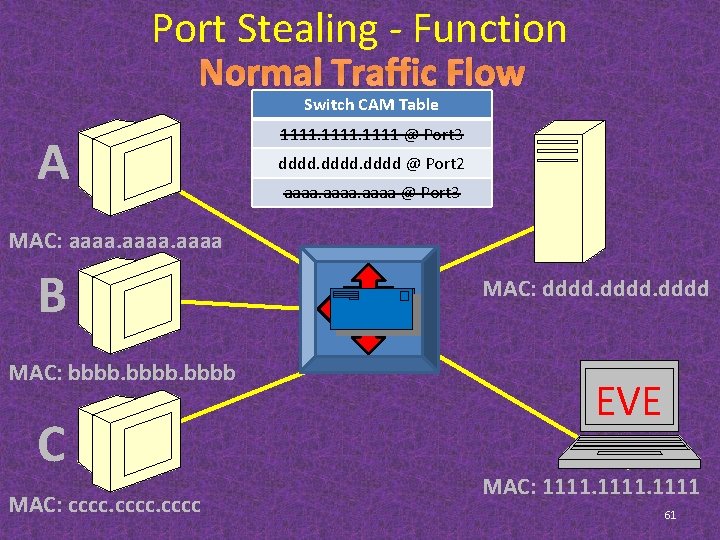
Port Stealing - Function Port Stealing is not the best term to describe this particular Mit. M. This method of Ettercap abuses how switches build their Layer 2 forwarding table. When data is sent from a host, it is tagged with Destination and Sender addresses. 55
Port Stealing - Function Switches will note the Sender Layer 2 address and associate it will the port it was recieved on. In this way, the switch maps Layer 2 to Layer 1 addresses so it can forward data as quickly as possible. 56
Port Stealing - Function Normal Traffic Flow Switch CAM Table A aaaa @ Port 1 dddd @ Port 2 1111 @ Port 3 MAC: aaaa B MAC: dddd MAC: bbbb C MAC: cccc MAC: 1111 57
Port Stealing - Function A Alterted Traffic Switch CAM Table Flow@@ Port 1 1111 aaaa Port 3 dddd @ Port 2 1111 aaaa @ @ Port 3 MAC: aaaa B MAC: dddd MAC: bbbb C MAC: cccc EVE Senders MAC: aaaa MAC: 1111 58
Port Stealing - Function Normal Traffic Flow Switch CAM Table A 1111 @ Port 3 Port 1 dddd @ Port 2 aaaa @ Port 3 MAC: aaaa B MAC: dddd MAC: bbbb C MAC: cccc EVE Senders MAC: 1111 59
Port Stealing - Function Normal Traffic Flow Switch CAM Table A 1111 @ Port 3 dddd @ Port 2 aaaa @ Port 3 MAC: aaaa B MAC: dddd MAC: bbbb C MAC: cccc EVE Un. Known Unicast become Broadcast MAC: 1111 60
Port Stealing - Function Normal Traffic Flow Switch CAM Table A 1111 @ Port 3 dddd @ Port 2 aaaa @ Port 3 MAC: aaaa B MAC: bbbb C MAC: cccc MAC: dddd EVE MAC: 1111 61
Port Stealing - Countermeasures With modern day fast & gigabit Ethernet standards, and improved switching hardware, this particular Mit. M is the least effective of Ettercap's arsenal, and it also the easiest to defend against. Using Cisco port-security, forged Layer 2 sender data can trigger a number of responses, including up to completely disabling an interface. The parameters for Cisco port-security will vary depending on network requirements. 62
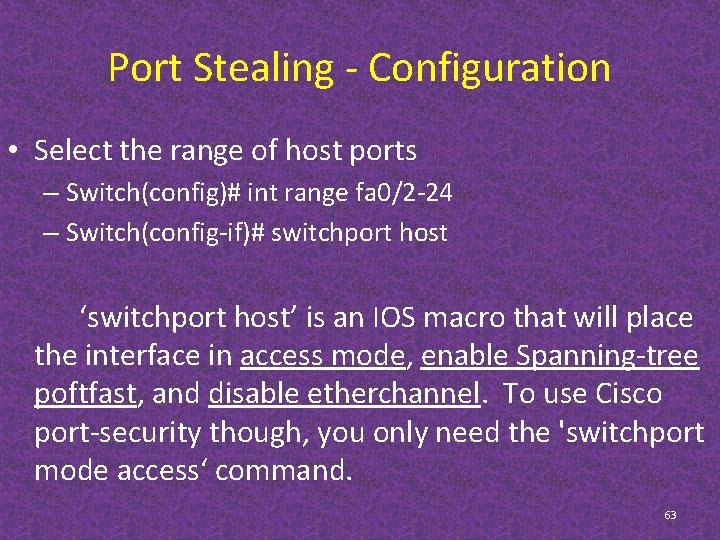
Port Stealing - Configuration • Select the range of host ports – Switch(config)# int range fa 0/2 -24 – Switch(config-if)# switchport host ‘switchport host’ is an IOS macro that will place the interface in access mode, enable Spanning-tree poftfast, and disable etherchannel. To use Cisco port-security though, you only need the 'switchport mode access‘ command. 63
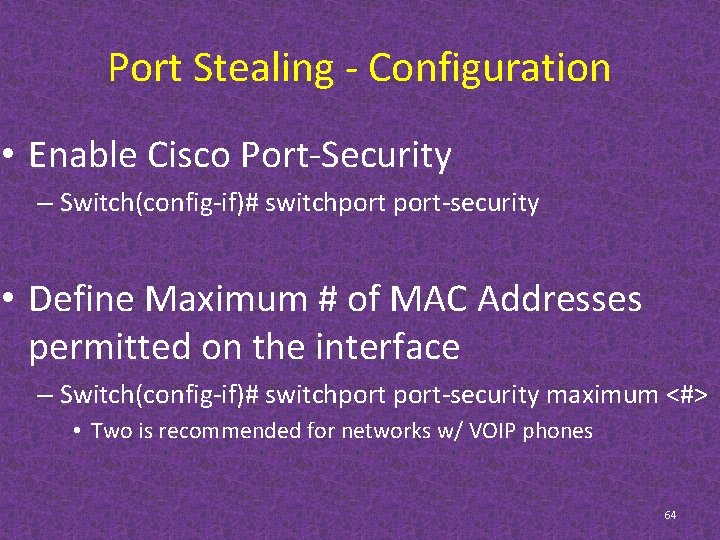
Port Stealing - Configuration • Enable Cisco Port-Security – Switch(config-if)# switchport-security • Define Maximum # of MAC Addresses permitted on the interface – Switch(config-if)# switchport-security maximum <#> • Two is recommended for networks w/ VOIP phones 64
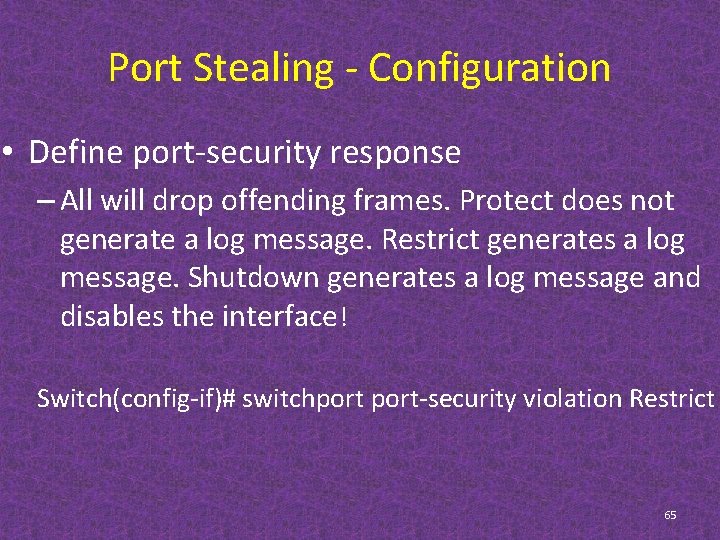
Port Stealing - Configuration • Define port-security response – All will drop offending frames. Protect does not generate a log message. Restrict generates a log message. Shutdown generates a log message and disables the interface! Switch(config-if)# switchport-security violation Restrict 65
Port Stealing - Configuration • Define host MAC address or allow dynamic learning with 'sticky‘ – Switch(config-if)# switchport-security macaddress [<H. H. H>|sticky] 66
Conclusion Y’all play nice now. 67
Conclusion While Ettercap is not the only program to perform DHCP Spoofing, ARP Poisoning, ICMP Redirect, & Port Stealing Mit. Ms, it is one of the most popular. Keeping vigilant and understanding threats facing networks are fundamental for network security officers. Understanding the functions of Ettercap and similar tools can give administrators new insight to reassessing security measures. 68