Network Attacks 1 Topics q Sniffing q IP
- Slides: 82
Network Attacks 1
Topics q Sniffing q IP address spoofing q Session hijacking q Netcat o General-purpose network tool Network Attacks 2
Sniffing q Sniffer gathers traffic from LAN o Can see packets in real time o Usually, interface put in promiscuous mode o Gathers everything, regardless of IP address q Sniffer is useful for attacker o And useful for administrator q Sniffer can collect data such as … o ID/password sent over telnet, DNS, email messages, files sent over NFS, etc. Network Attacks 3
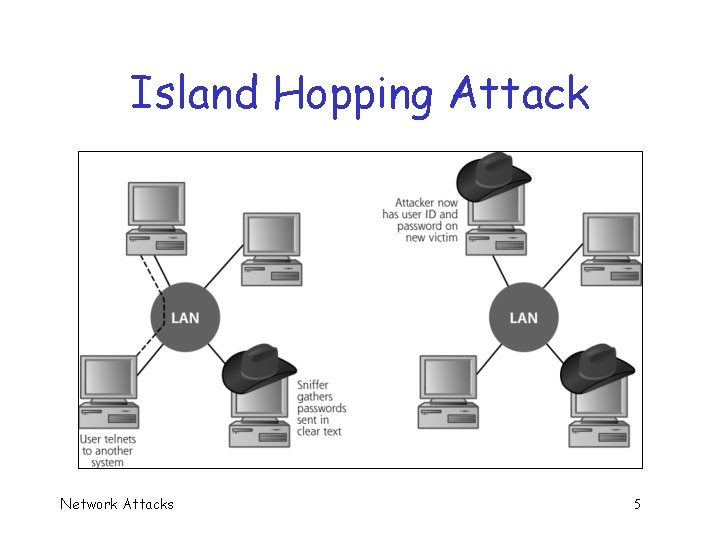
Sniffing q Attacker who has access to LAN can sniff packets o Usually requires admin/root privilege o Typically, use sniffer to gather pwds q Sniffing can be used in “island hopping” attack o Next slide Network Attacks 4
Island Hopping Attack Network Attacks 5
Sniffers q Freeware sniffers include o windump --- port of tcpdump o Snort --- sniffer/IDS o Wireshark (formerly, Ethereal) --- able to decode lots of protocols o Sniffit --- popular with attackers o Dsniff --- perhaps most powerful Network Attacks 6
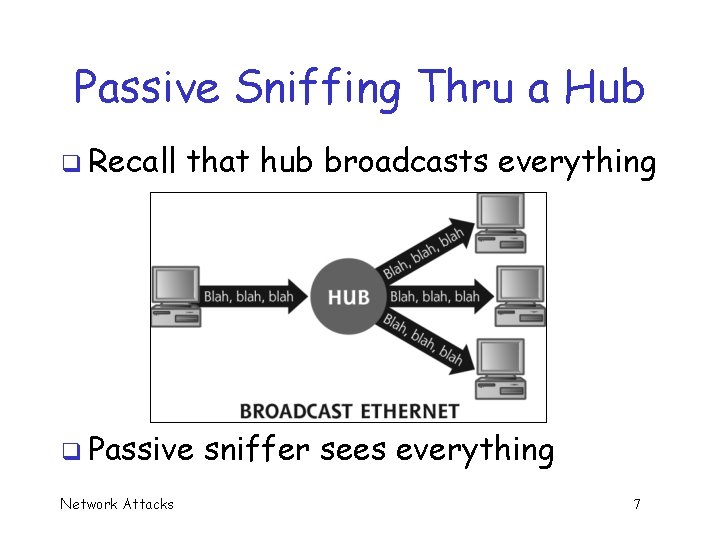
Passive Sniffing Thru a Hub q Recall that hub broadcasts everything q Passive Network Attacks sniffer sees everything 7
Snort q Snort: open source, UNIX-based IDS q Started out as a sniffer o Still can serve as a capable sniffer o Why does sniffer-to-IDS make sense? q Snort not often used by attackers o Has more features than attacker needs Network Attacks 8
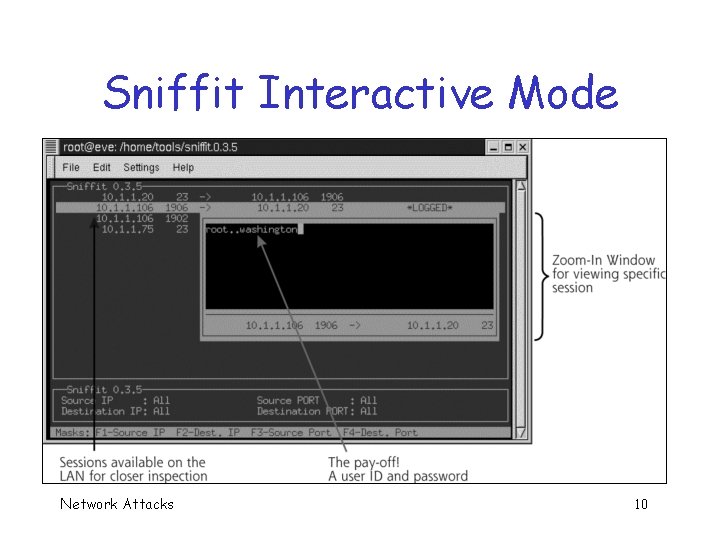
Sniffit q Sniffit popular with attackers o UNIX-based q Sniffit has “interactive mode” o Keeps track of individual sessions o Can view these as separate conversations Network Attacks 9
Sniffit Interactive Mode Network Attacks 10
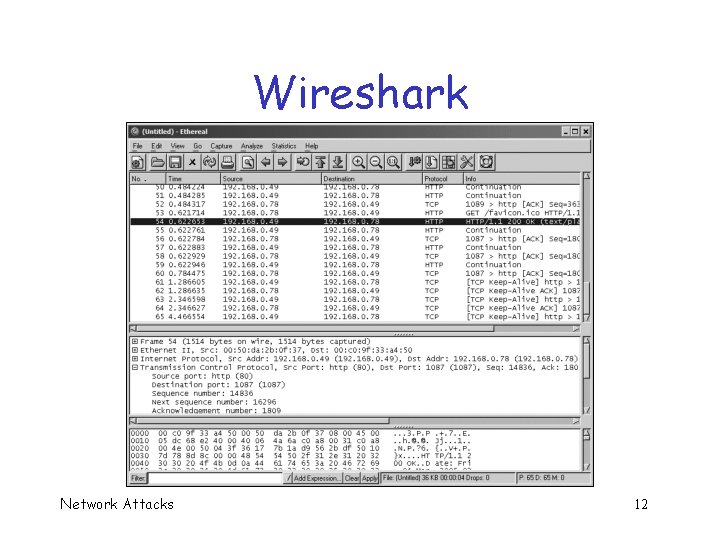
Wireshark q Wireshark (formerly Ethereal) o Available for many platforms o Probably easiest sniffer to use, great UI, etc. q Wireshark is a “protocol genius” o Decodes every bit of packet q “Follow TCP stream” function o Select a TCP packet, view entire connection Network Attacks 11
Wireshark Network Attacks 12
Sniffer as Scanning Tool q Nmap, Nessus, etc. , may be detected o Active q Sniffer is passive, so no such risk o What can be determined by sniffing? q May be able to ID OS (maybe even version of OS) o E. g. , based on way connections are made Network Attacks 13
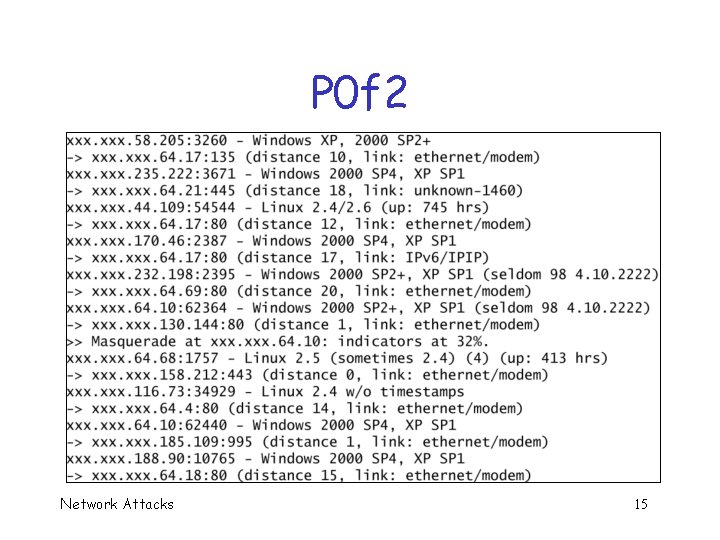
P 0 f 2 q Tool to passively ID OS q Available for most platforms q To “fingerprint” OS’s network stack o Can also ID firewall, NAT, etc. q What info does it use? q TTL, IP ID, other? Network Attacks 14
P 0 f 2 Network Attacks 15
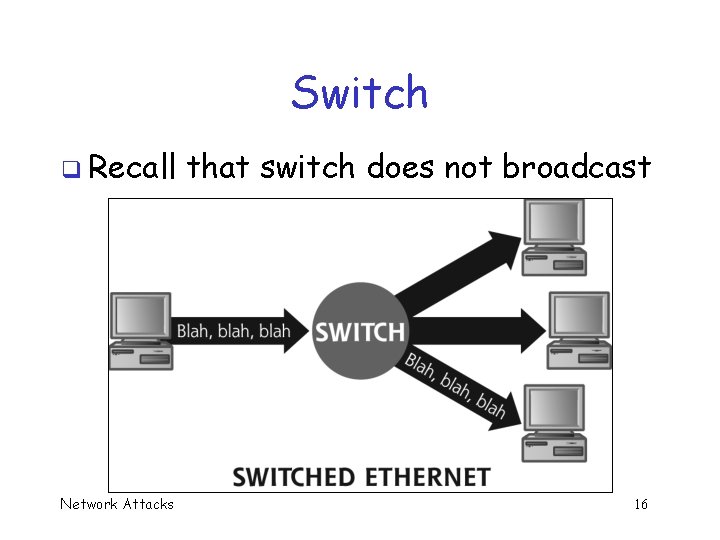
Switch q Recall that switch does not broadcast Network Attacks 16
Active Sniffing q Sniffing thru a switch? q Switch limits what you see with sniffers such as Wireshark q May be able to “sniff” thru switch by inserting traffic o Dsniff and Ettercap Network Attacks 17
Dsniff q Developed by developer of Frag. Router q Dsniff decodes lots application level protocols o FTP, telnet, POP, …, Napster, pc. Anywhere o Makes it easy to find passwords q Dsniff Network Attacks also has active operations 18
Dsniff Switch remembers MAC addresses q MAC address flooding q o Dsniff sends packets with random spoofed MAC addresses o Switches address memory eventually exhausted q Then what does switch do? o It depends…, but some start acting like hubs o If so, then passive sniffing works Network Attacks 19
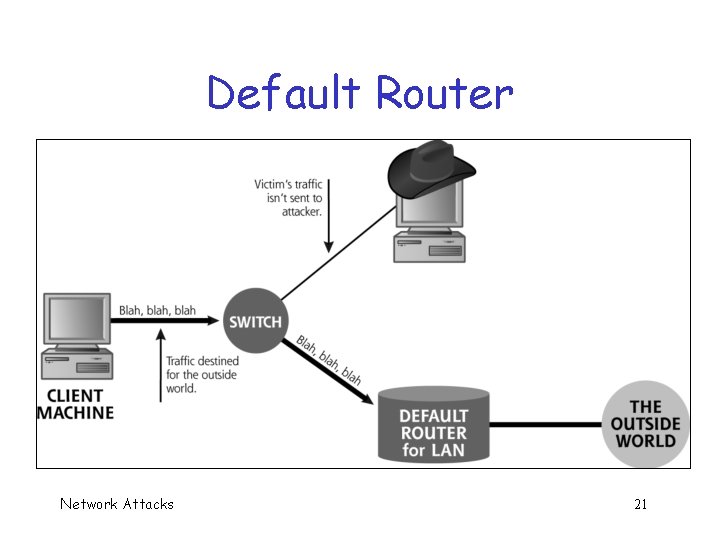
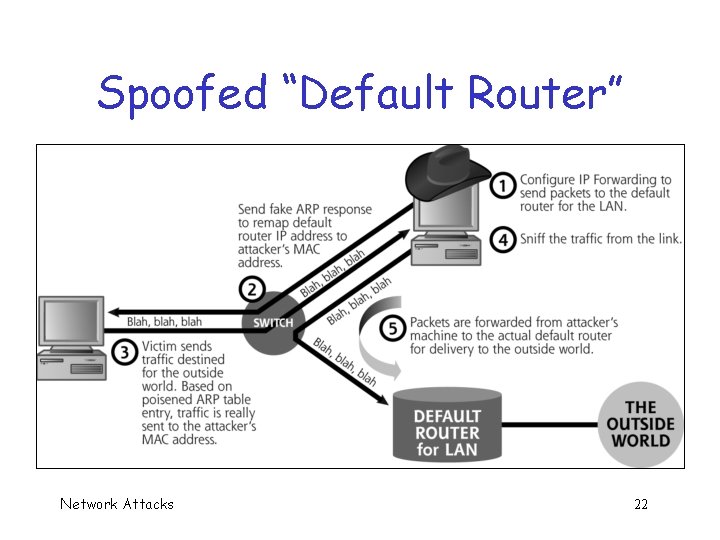
Dsniff What to do if flooding fails? q ARP spoofing (ARP cache poisoning) q o Attacker sets “IP forwarding” on his machine to default gateway (router) o Attacker poisons ARP cache so that he appears to be default gateway o Attacker see all traffic destined for outside world, and traffic still sent to default gateway Network Attacks 20
Default Router Network Attacks 21
Spoofed “Default Router” Network Attacks 22
Dsniff ARP Spoofing q How could this be detected? q What happens when packet sent from attacker to default gateway? o IP forwarding is “really simple routing” o So, TTL is decremented o Could be detected by, say, traceroute q How can attacker avoid this? Network Attacks 23
Ettercap q Ettercap uses method known as “port stealing” to sniff switched LAN o Sometimes, hard-coded MAC addresses o In such case, ARP poisoning not possible q Port stealing may be an option Network Attacks 24
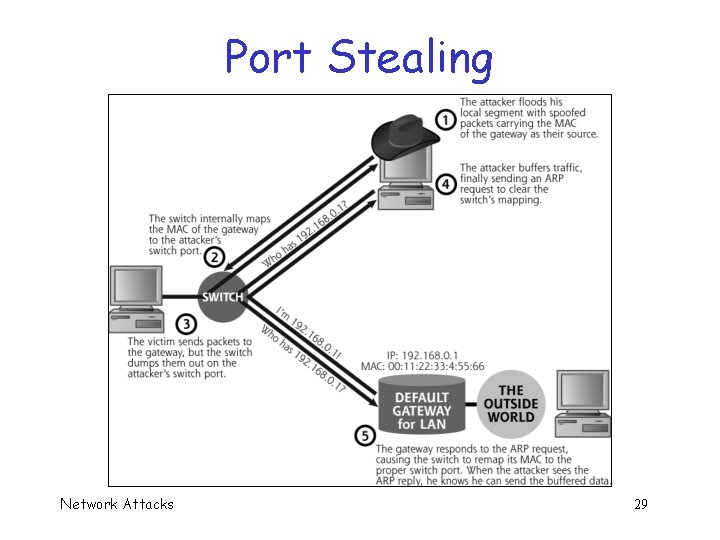
Ettercap q Switch associates MAC addresses to each of its physical ports o Mapping created by examining packets q Ettercap floods LAN with frames o Attacker’s MAC address is destination o Source MAC address is victim machine (e. g. , default gateway) q What does this accomplish? o Switch associates default gateway with its physical port on which attacker resides Network Attacks 25
Ettercap Port stealing q So far… switch thinks default gateway on same physical port as attacker q o Note: ARP tables on hosts not affected Then attacker can sniff data intended for victim q How does attacker then get these packets to the default gateway? q Network Attacks 26
Ettercap q So far… packets intended for gateway can be sniffed by attacker q How to get these packets to gateway? o Forward packets to switch with gateway’s MAC address? o That won’t work! Network Attacks 27
Ettercap Attacker sends ARP request for IP address of gateway q When attacker sees response q o Knows switch has also seen response q So what? o Now switch send data intended for gateway to the gateway o Attacker can then send buffered data q Brilliant! Network Attacks 28
Port Stealing Network Attacks 29
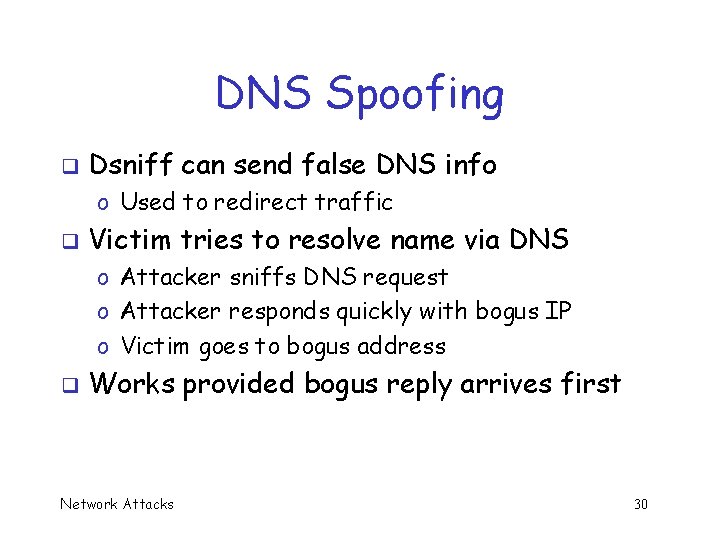
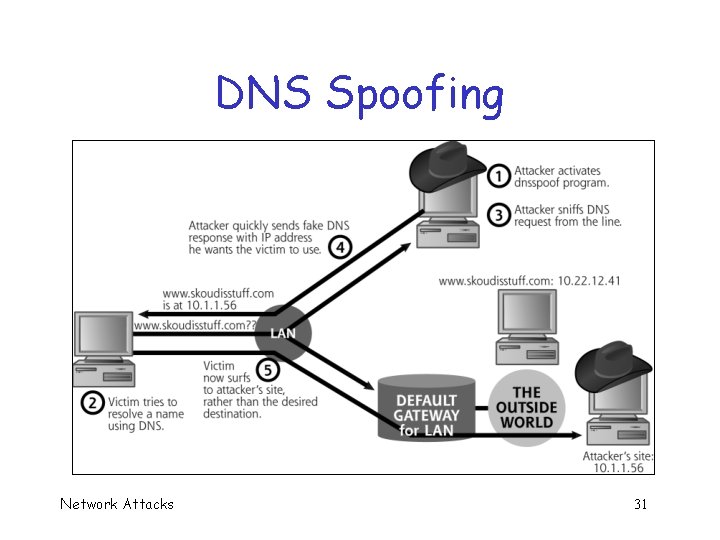
DNS Spoofing q Dsniff can send false DNS info o Used to redirect traffic q Victim tries to resolve name via DNS o Attacker sniffs DNS request o Attacker responds quickly with bogus IP o Victim goes to bogus address q Works provided bogus reply arrives first Network Attacks 30
DNS Spoofing Network Attacks 31
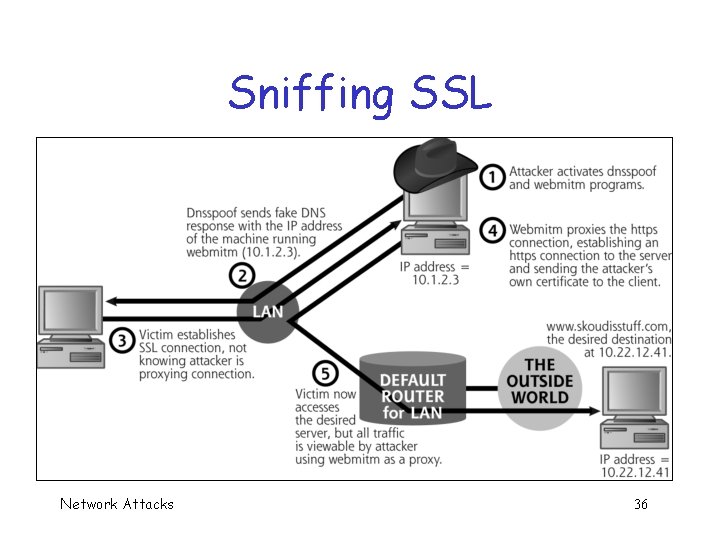
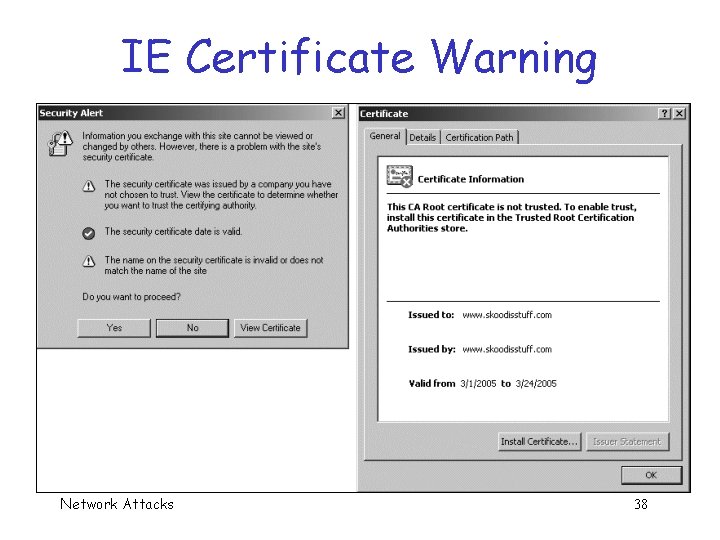
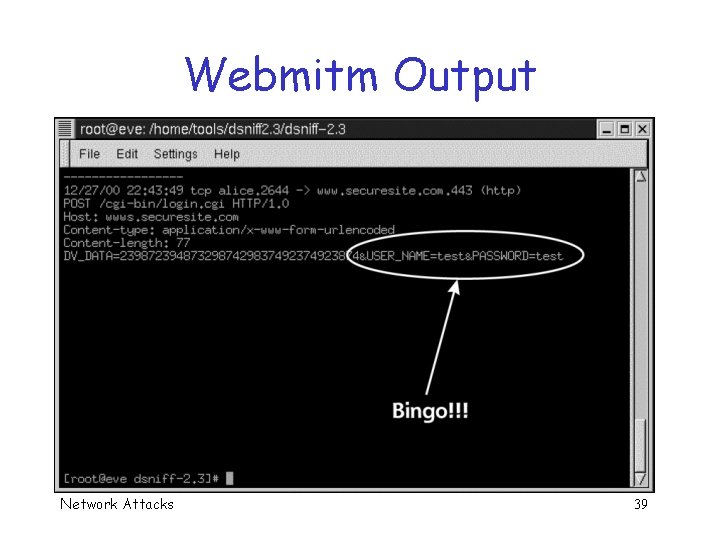
Sniffing SSL and SSH q Dsniff webmitm enables man-in-themiddle (MIM) attack q Send certificate signed by bogus “CA” o o In SSL, browser warns use, and … …warning is ignored In SSH user is warned, and … …warning is ignored Network Attacks 32
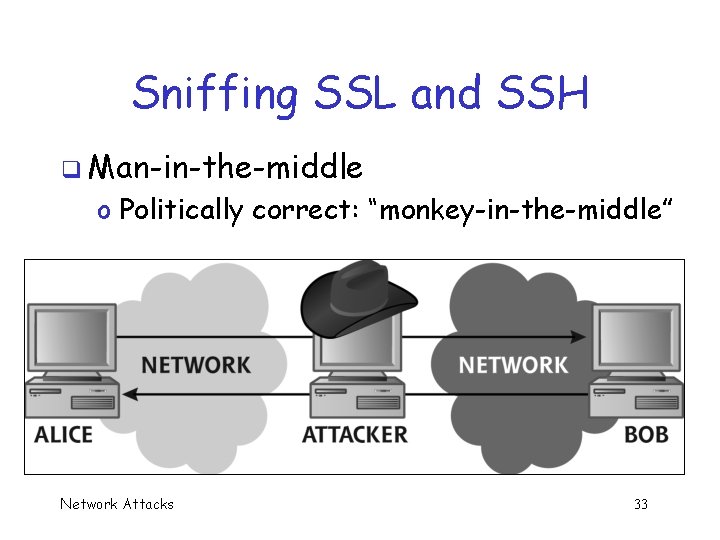
Sniffing SSL and SSH q Man-in-the-middle o Politically correct: “monkey-in-the-middle” Network Attacks 33
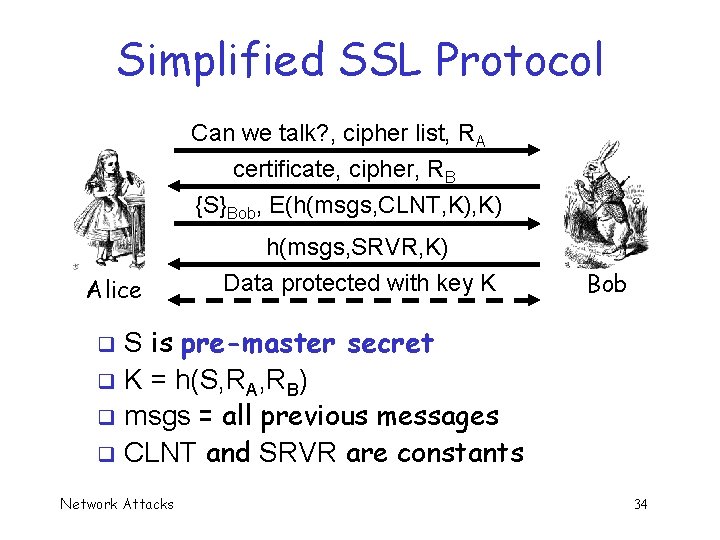
Simplified SSL Protocol Can we talk? , cipher list, RA certificate, cipher, RB {S}Bob, E(h(msgs, CLNT, K) Alice h(msgs, SRVR, K) Data protected with key K Bob S is pre-master secret q K = h(S, RA, RB) q msgs = all previous messages q CLNT and SRVR are constants q Network Attacks 34
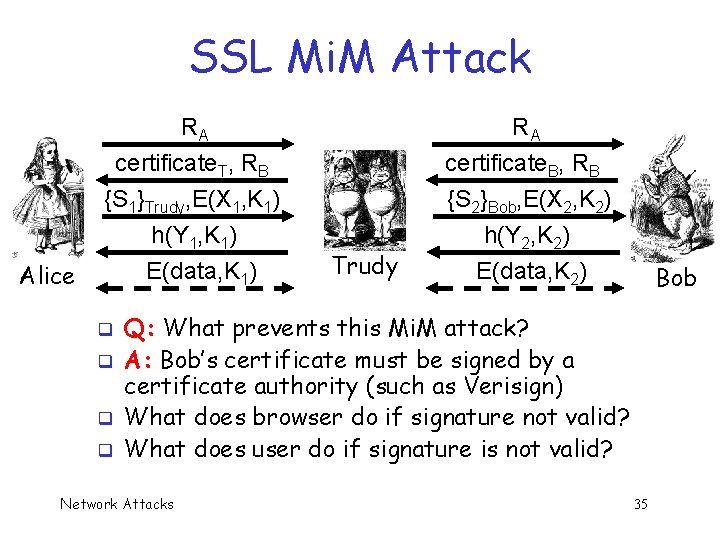
SSL Mi. M Attack Alice RA RA certificate. T, RB {S 1}Trudy, E(X 1, K 1) h(Y 1, K 1) E(data, K 1) certificate. B, RB {S 2}Bob, E(X 2, K 2) h(Y 2, K 2) E(data, K 2) q q Trudy Bob Q: What prevents this Mi. M attack? A: Bob’s certificate must be signed by a certificate authority (such as Verisign) What does browser do if signature not valid? What does user do if signature is not valid? Network Attacks 35
Sniffing SSL Network Attacks 36
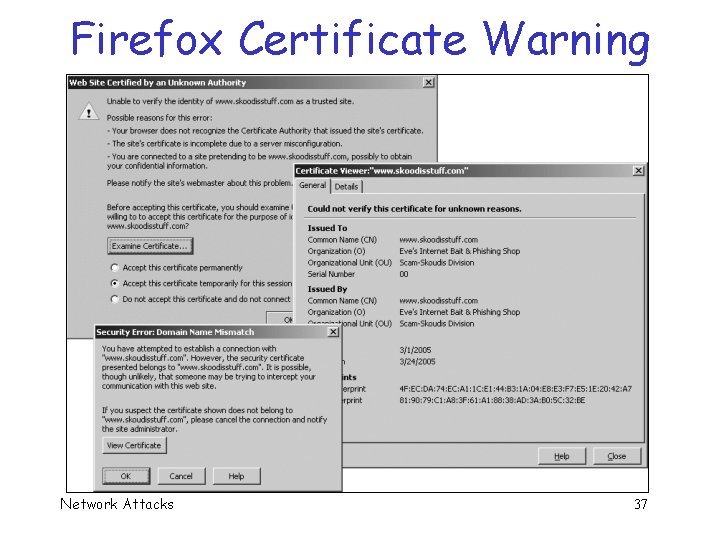
Firefox Certificate Warning Network Attacks 37
IE Certificate Warning Network Attacks 38
Webmitm Output Network Attacks 39
SSH Sniffing q SSH gives a warning too o Specifically mentions Mi. M attack o Still, it’s easy to ignore q Ettercap also does SSH Mi. M o But Ettercap is not really in the “middle” o It establishes key with client, then connects client to server using same key Network Attacks 40
Other Dsniff Features Tcpkill --- kill active TCP connection q Tcpnice --- “shape traffic” using, e. g. , ICMP source quench q Filesnarf --- grab NFS files q Mailsnarf --- grab email q Msgsnarf --- grab IM traffic q Urlsnarf --- grab URLs from HTTP traffic q Webspy --- view web pages victim views q Network Attacks 41
Sniffing Defenses q Use secure protocols o SSL, SSH, SMIME, PGP, IPSec Do not use telnet for sensitive info q Take certificate warnings seriously q Prefer switches to hubs q Hard code MAC addresses, if possible q Static ARP tables, where possible q Network Attacks 42
Sniffing Defenses Use tools to detect promiscuous mode q Ipconfig (UNIX), Promisc. Detect (Windows) q Sentinel looks for anomalies on LAN that indicate sniffing q o Send packet (ping, for example) with bogus destination MAC address o Any reply indicates sniffing q Also, some Windows-specific tools Network Attacks 43
IP Address Spoofing q IP Address Spoofing o Changing source IP address q Enables Trudy to… o Cover her tracks o Break applications that use IP address for authentication q Previous Network Attacks examples: Nmap, Dsniff, … 44
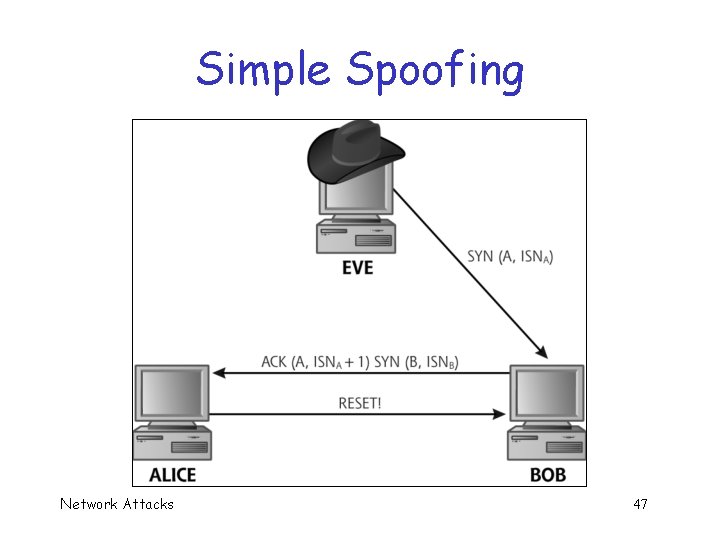
Simple Spoofing q Simply change the IP address o Ipconfig or Windows network Control Panel q Works when Trudy does not need response o Do. S, for example q Tools for packet crafting o Hping 2 o Nemesis o Net. Dude Network Attacks 45
Simple Spoofing q Limitations of simple spoofing o Trudy cannot easily interact with target o Spoofing TCP especially difficult q Interactive simple spoofing works if Trudy on same LAN as spoofed address Network Attacks 46
Simple Spoofing Network Attacks 47
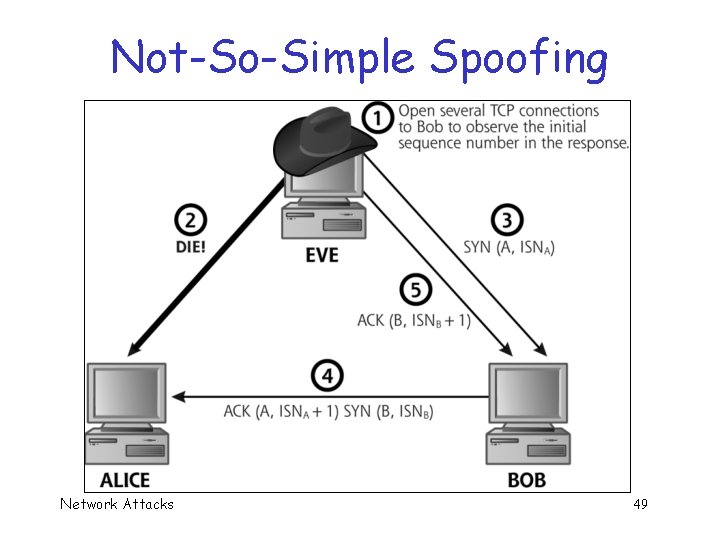
Predicting Sequence Numbers q Not-so-simple spoofing… o Trusted machines often require no authentication beyond TCP connection q Trudy can pretend to be trusted machine by spoofing IP address o To establish connection, Trudy must predict initial sequence number Network Attacks 48
Not-So-Simple Spoofing Network Attacks 49
Not-So-Simple Spoofing q Note that… o Trudy must correctly guess ISNB o Trudy does not see responses (not a true interactive session) o Bob thinks packets came from Alice o Good attack for r-commands Network Attacks 50
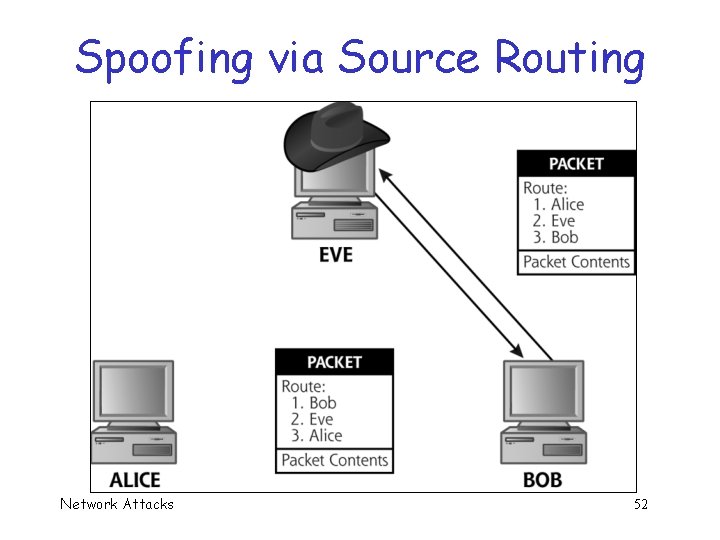
Spoofing via Source Routing q Source routing o Specify path packet will take q Loose source routing o Specify some hops q Source routing makes Trudy’s life much easier o Next slide Network Attacks 51
Spoofing via Source Routing Network Attacks 52
Spoofing via Source Routing q Seldom works across Internet o Source routing blocked by gateway q May work on internal network o Makes insider attacks easy Network Attacks 53
IP Spoofing Defenses q Be sure ISNs are reasonably random q Avoid using r-commands o Or use only with SSH or VPN q IP address for authentication … NOT! q Do not allow source routing q Be careful with trust relationships Network Attacks 54
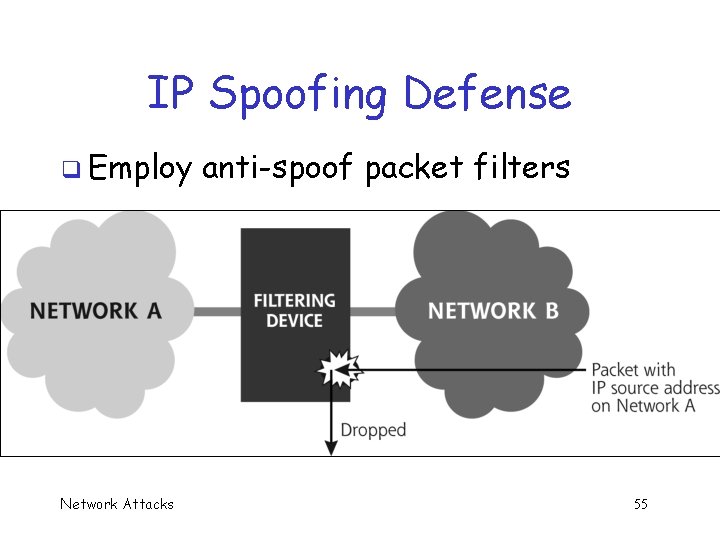
IP Spoofing Defense q Employ Network Attacks anti-spoof packet filters 55
Session Hijacking Trudy “steals” an existing session q Network-based session hijacking q o o o q Combines spoofing and sniffing Alice and Bob have existing connection Trudy is sniffing packets (on LAN) Trudy starts injecting packets Bob thinks packets came from Alice This works even if strong authentication used, provided there is no encryption Network Attacks 56
Session Hijacking q Also, host-based session hijacking q Tools for session hijacking o o o Hunt Dsniff --- sshmitm Ettercap Juggernaut IP Watcher, TTYSnoop Network Attacks 57
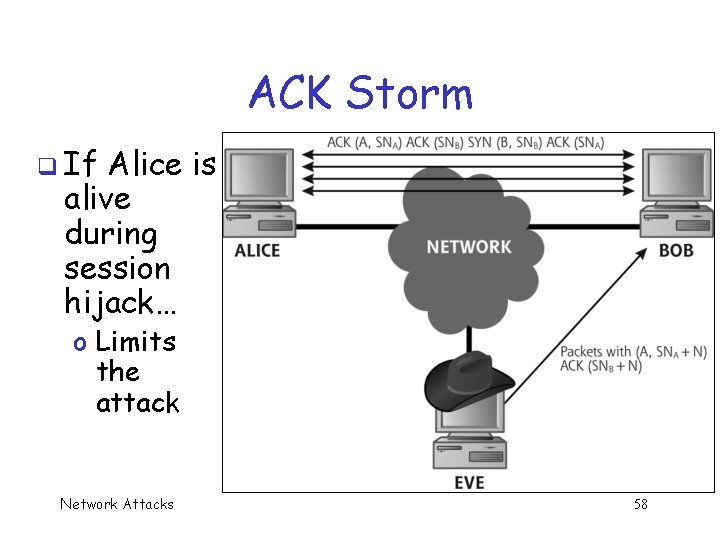
ACK Storm q If Alice is alive during session hijack… o Limits the attack Network Attacks 58
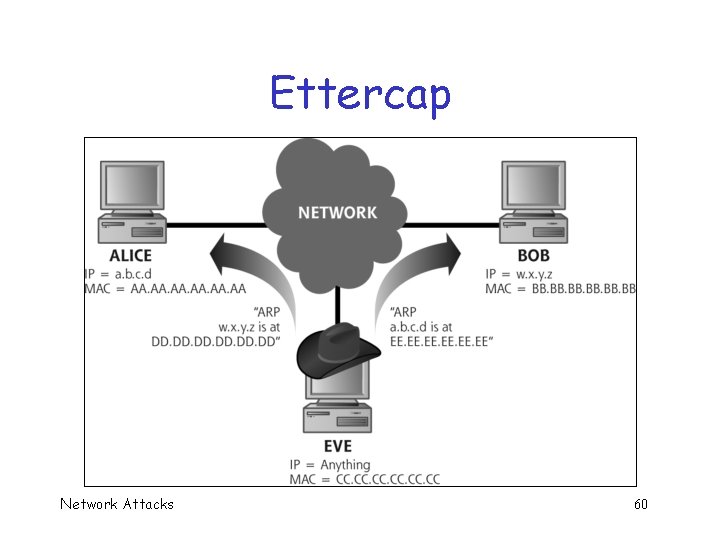
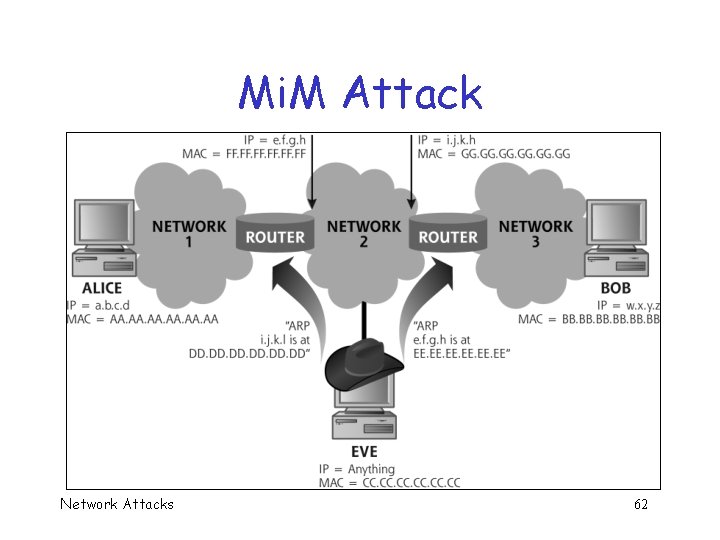
Ettercap q Ettercap can prevent ACK storm q ARP cache poisoning o Ettercap makes Trudy Mi. M Network Attacks 59
Ettercap Network Attacks 60
Hunt offers similar feature as Ettercap q Includes a “resync” feature that may allow Trudy out of Mi. M q o And allow Alice and Bob to continue q Ettercap and Hunt attacks can work even if Trudy not on same LAN o Trudy must be on network between Alice & Bob Network Attacks 61
Mi. M Attack Network Attacks 62
Wireless Access Points All attacks so far also work on wireless networks q But wireless has unique attack… q Access point hijacking q o Given SSID, pretend to be access point o Then need to get victims to associate with fake access point o Tool for this: Air. Jack Network Attacks 63
Session Hijacking Defenses q Use defenses against spoofing and sniffing q Use SSH version 2 o Dsniff and Ettercap Mi. M work against SSH version 1 q Pay careful attention to certificate warnings Network Attacks 64
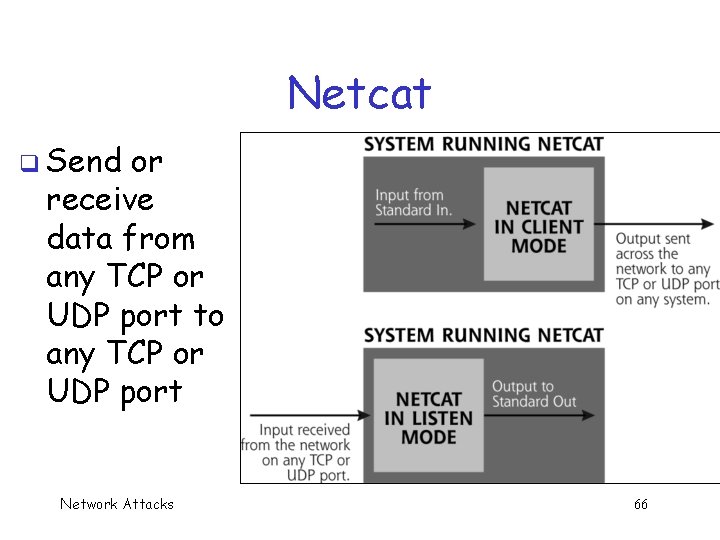
Netcat q General-purpose networking tool o “…single most useful tool … for interacting with a system across a network” o “Swiss army knife of network tools” o If you were stranded on a desert island, your one attack tool would be Netcat q You get the idea… Network Attacks 65
Netcat q Send or receive data from any TCP or UDP port to any TCP or UDP port Network Attacks 66
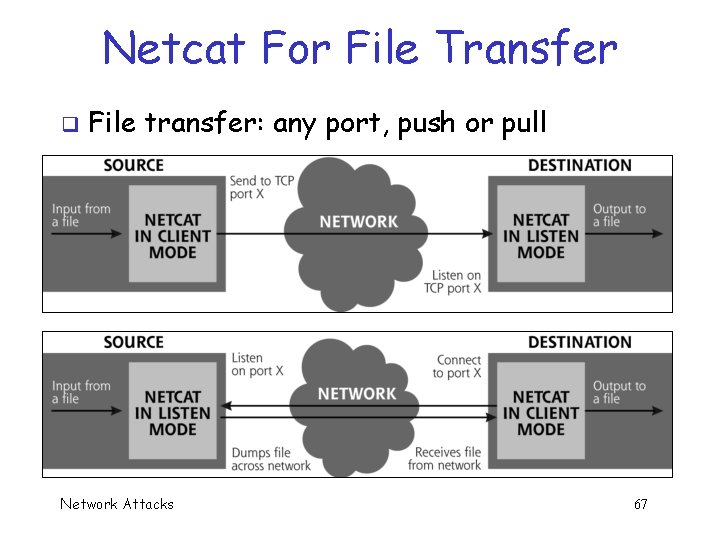
Netcat For File Transfer q File transfer: any port, push or pull Network Attacks 67
Netcat For Port Scanning q Plain vanilla port scanning o Unlike Nmap, which has many options Network Attacks 68
Netcat: Connect to Open Ports q Connect to open port o Send data and see what comes back q Better than telnet because o o o Easier to redirect output to file Easier to drop a connection No telnet control data/characters No telnet error messages telnet cannot make UDP connections Network Attacks 69
Netcat: Vulnerability Scanning q Netcat as “vulnerability engine” o I. e. , attacker writes scripts that use Netcat’s capabilities o Netcat comes with scripts to check for vulnerabilites in RPC, NFS, trust, FTP, a really weak passwords (very limited compared to Nessus) Network Attacks 70
Netcat Backdoors q With access to a machine, Trudy can o Start a Netcat listener for future access o Create an active backdoor (i. e. , push data) q These are most common uses of Netcat by bad guys Network Attacks 71
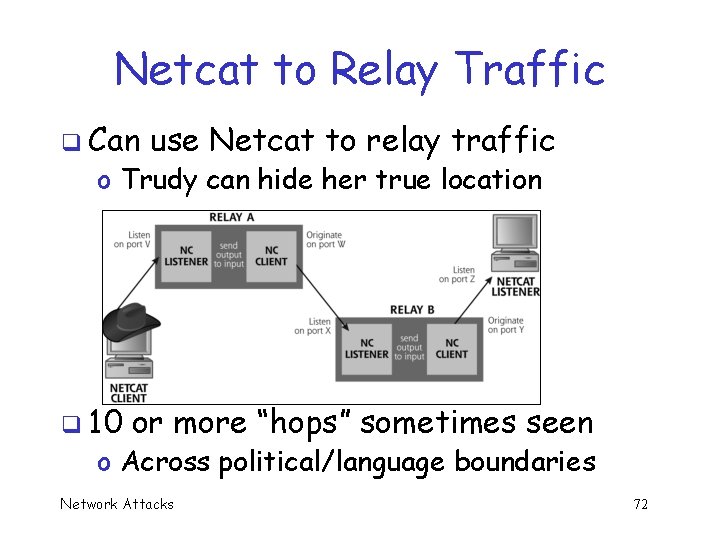
Netcat to Relay Traffic q Can use Netcat to relay traffic o Trudy can hide her true location q 10 or more “hops” sometimes seen o Across political/language boundaries Network Attacks 72
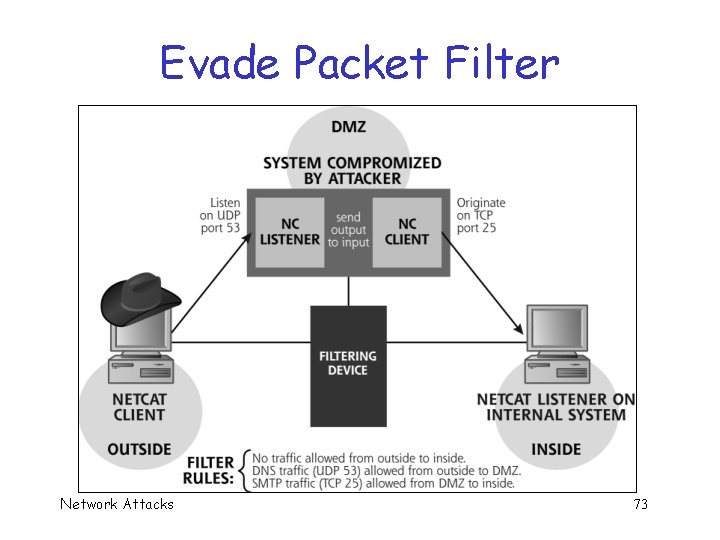
Evade Packet Filter Network Attacks 73
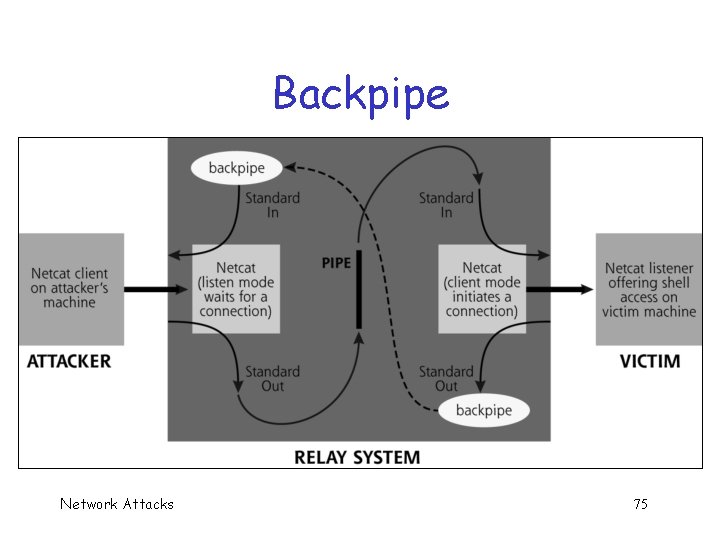
How to Create Netcat Relay? q Three popular techniques q Modify inted in UNIX/Linux o Add a line to inted. conf file q “backpipe” on UNIX/Linux o Use mknod: pipes data in FIFO order q Relay Network Attacks bat file in Windows 74
Backpipe Network Attacks 75
Netcat Listeners By default, Netcat listener is nonpersistent q In Windows version, can create persistent listeners q In UNIX, requires a little more work from Trudy to get same effect q o see book for details Network Attacks 76
Netcat Honeypots q Good guys can create Netcat (persistent) listeners o These can be used as honeypots Network Attacks 77
Netcat Defenses q Prevent Netcat file transfers o Firewall configuration issue q Secure against port scanning o Minimal number of listening ports q Block arbitrary connections to ports o Close unused ports q Protect against vulnerability scanning o Apply patches Network Attacks 78
Netcat Defenses q Stop backdoors o Need to know what processes are running so you can detect rogue processes q Prevent relay attacks o No single point that attacker can relay around q Stop persistent listeners o Periodically check for unexpected listening ports Network Attacks 79
Conclusions Network Attacks 80
Summary Network Attacks 81
Netcat Network Attacks 82