Packet Filtering TCPIP q q Kernel q Hooking
- Slides: 94
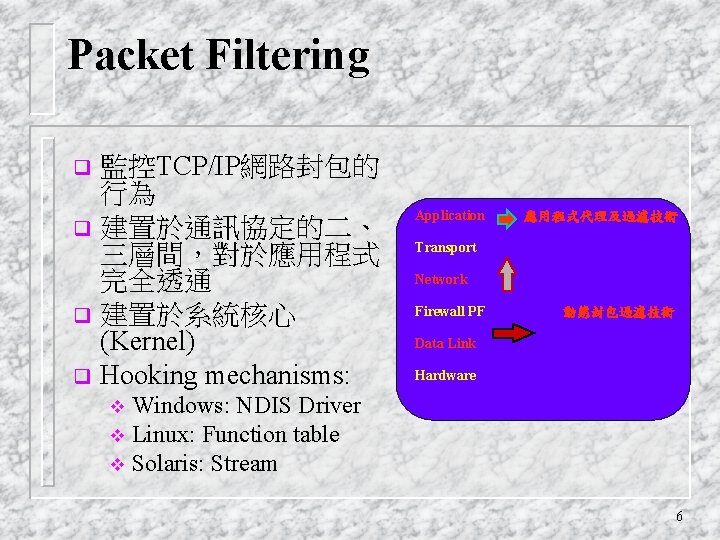
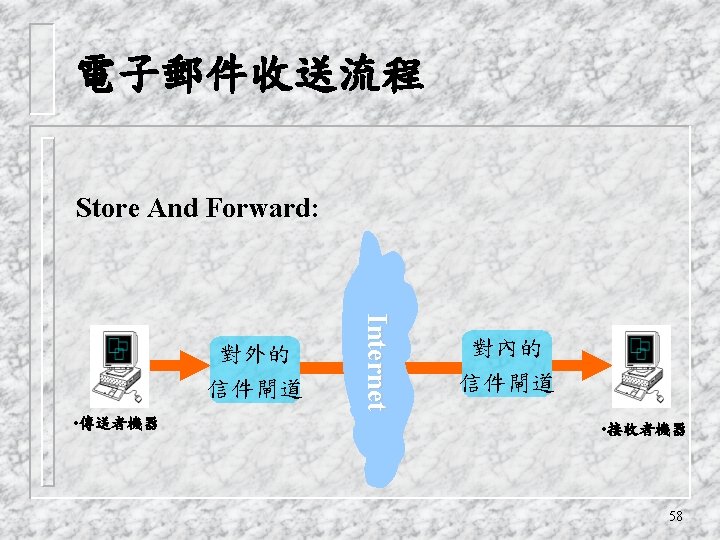
Packet Filtering 監控TCP/IP網路封包的 行為 q 建置於通訊協定的二、 三層間,對於應用程式 完全透通 q 建置於系統核心 (Kernel) q Hooking mechanisms: q Application 應用程式代理及過濾技術 Transport Network Firewall PF 動態封包過濾技術 Data Link Hardware Windows: NDIS Driver v Linux: Function table v Solaris: Stream v 6
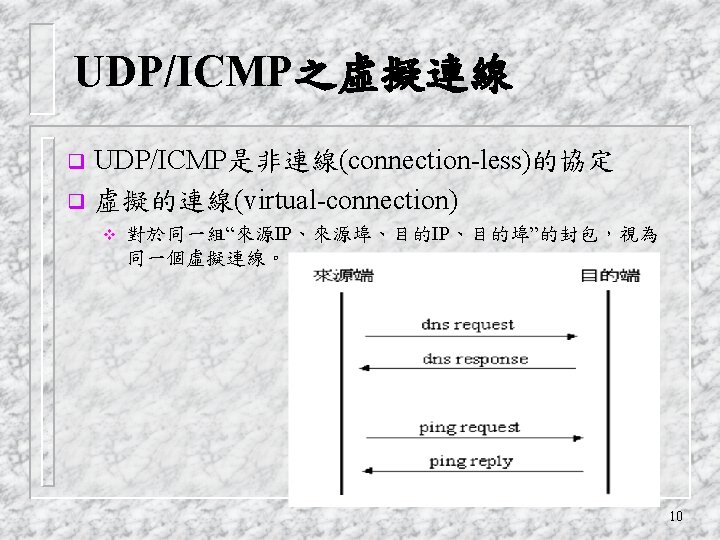
Criteria of Packet Filtering 靜態封包檢視的資訊 v 來源IP、來源埠、目的IP、目的埠 q 動態封包檢視的資訊 v Sequence number v Acknowledgement number v SYN/RST/FIN… v Virtual connection v FTP Command q 7
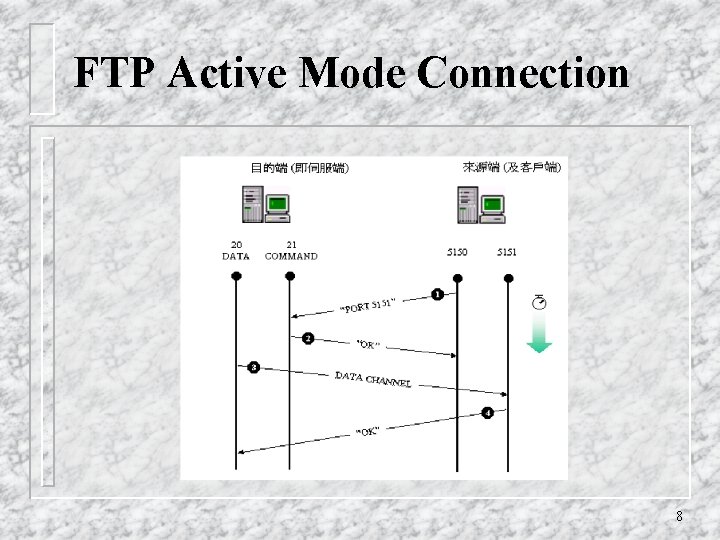
FTP Active Mode Connection 8
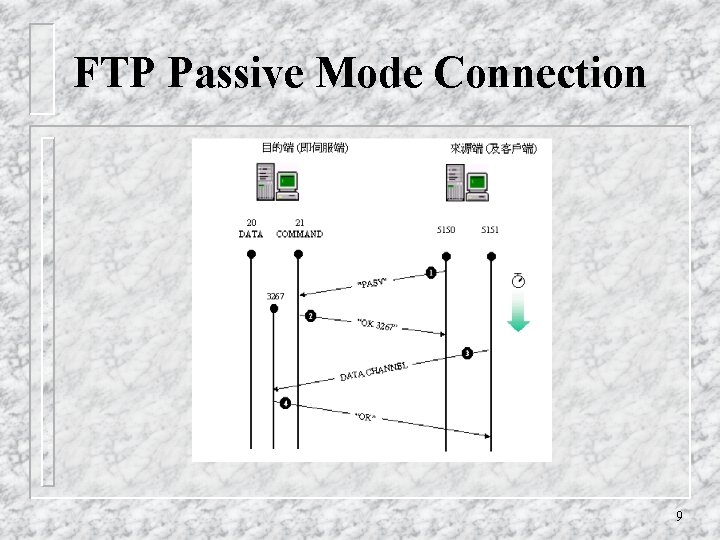
FTP Passive Mode Connection 9
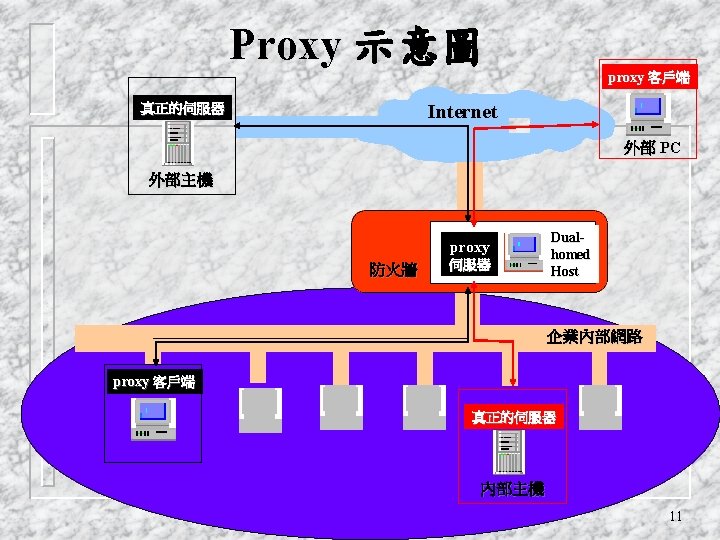
Proxy之功用 q 內外網路阻隔 q Application Filtering q User Authentication q Detail Logging 12
Application Filtering (1) q 檔案傳輸( FTP)的限制 v 設定Read / Write權限 v 設定可傳輸的檔名 v FTP Virus Check q HTTP的限制 v 設定可否使用FTP、HTTP 、GOPHER等權限 v 設定HTML內容可否含有GET、POST、HEAD、 PUT等 v 使用Wildcard(*)設定URL Location的內容 v Java Applet, Java Script與Active. X Blocking v Anti-X 不當網站瀏覽過濾 v HTTP Virus Check 13
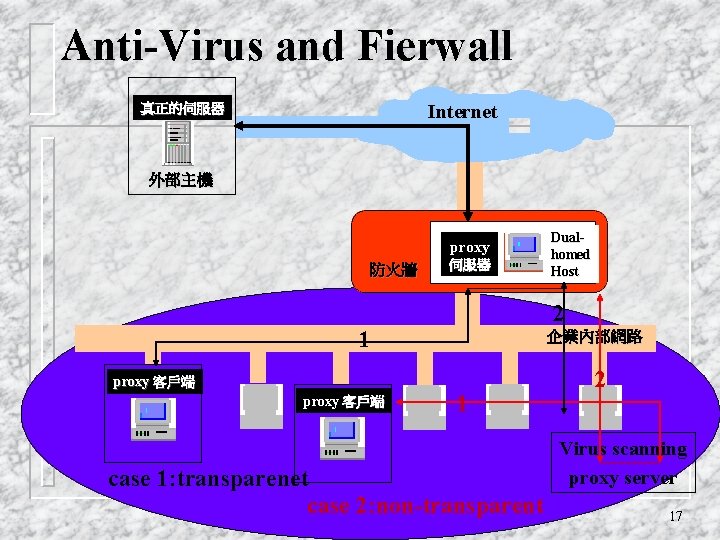
Transparent v. s. Non_Transparent Proxy q Transparent: 靠Firewall Redirect過往的網 路封包來達成 v封包必須經過Firewall q Non_transparent: 必須修改客戶端程式或 改變使用者程序 16
Anti-Virus and Fierwall Internet 真正的伺服器 外部主機 proxy 防火牆 伺服器 2 1 proxy 客戶端 Dualhomed Host 企業內部網路 1 case 1: transparenet case 2: non-transparent 2 Virus scanning proxy server 17
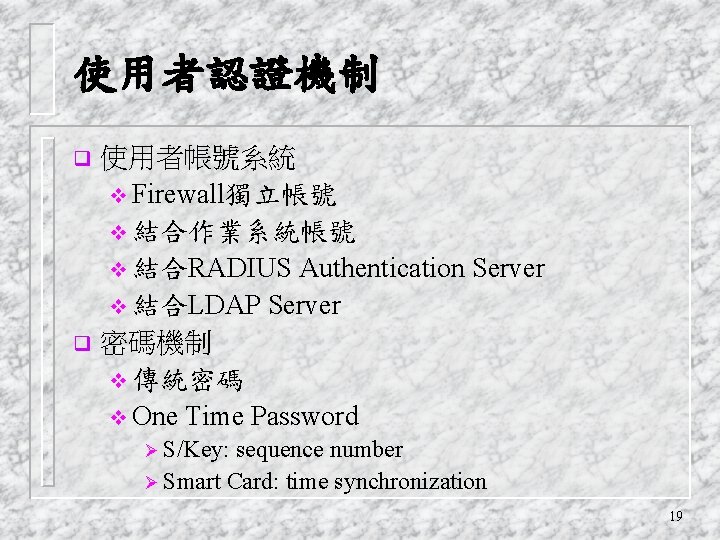
使用者認證機制 使用者帳號系統 v Firewall獨立帳號 v 結合作業系統帳號 v 結合RADIUS Authentication Server v 結合LDAP Server q 密碼機制 v 傳統密碼 v One Time Password q Ø S/Key: sequence number Ø Smart Card: time synchronization 19
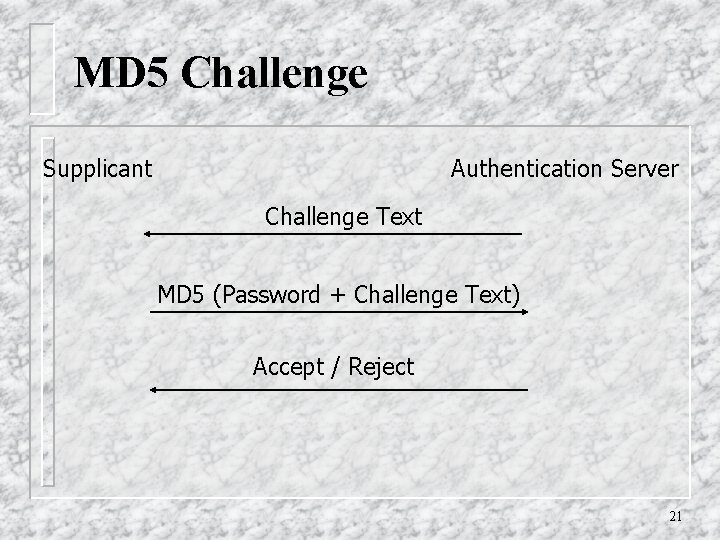
S/Key One Time Password q One Way Hash Function MD 5 y=F(x), 已知y, 反求x很難 q s=F(password, seed) p 0=Fn(s) p 1=Fn-1(s) … pi=Fn-i(s) Server儲存每個user之seed,上一次之OTP, 上 一次之sequence q Challenge - Response q Verify: F(pi)=F(Fn-i(s))=Fn-(i-1)(s) == Pi-1 q 20
MD 5 Challenge Supplicant Authentication Server Challenge Text MD 5 (Password + Challenge Text) Accept / Reject 21
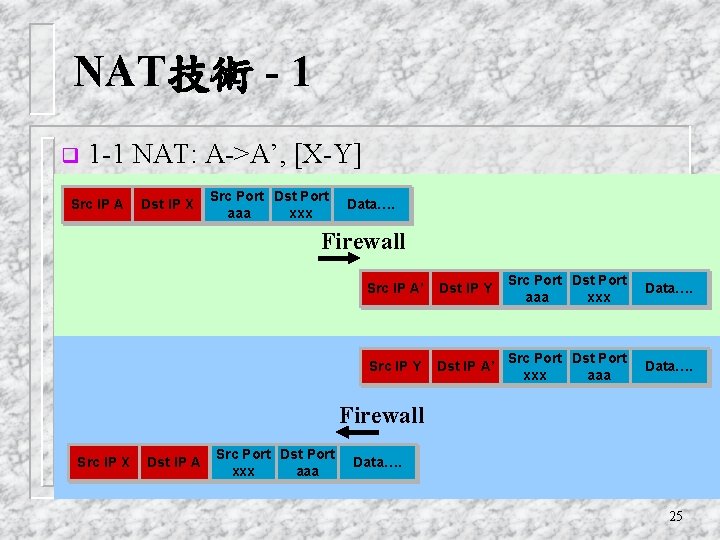
NAT技術 - 1 q 1 -1 NAT: A->A’, [X-Y] Src IP A Dst IP X Src Port Dst Port aaa xxx Data…. Firewall Src IP A’ Dst IP Y Src Port Dst Port aaa xxx Data…. Src IP Y Dst IP A’ Src Port Dst Port xxx aaa Data…. Firewall Src IP X Dst IP A Src Port Dst Port xxx aaa Data…. 25
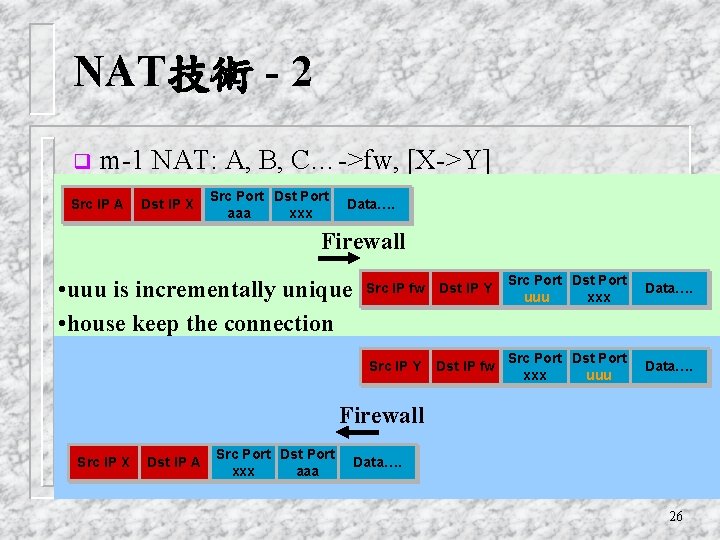
NAT技術 - 2 q m-1 NAT: A, B, C…->fw, [X->Y] Src IP A Dst IP X Src Port Dst Port aaa xxx Data…. Firewall • uuu is incrementally unique • house keep the connection Src IP fw Dst IP Y Src Port Dst Port uuu xxx Data…. Src IP Y Dst IP fw Src Port Dst Port xxx uuu Data…. Firewall Src IP X Dst IP A Src Port Dst Port xxx aaa Data…. 26
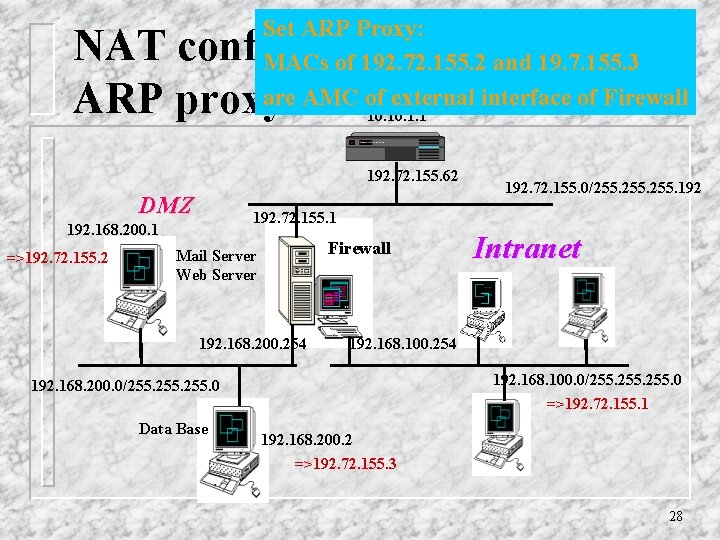
Set ARP Proxy: MACs of 192. 72. 155. 2 and 19. 7. 155. 3 are AMC of external interface of Firewall NAT configuration – case 1 ARP proxy 10. 1. 1 192. 72. 155. 62 DMZ 192. 72. 155. 1 192. 168. 200. 1 =>192. 72. 155. 2 192. 72. 155. 0/255. 192 Firewall Mail Server Web Server 192. 168. 200. 254 192. 168. 100. 0/255. 0 =>192. 72. 155. 1 192. 168. 200. 0/255. 0 Data Base Intranet 192. 168. 200. 2 =>192. 72. 155. 3 28
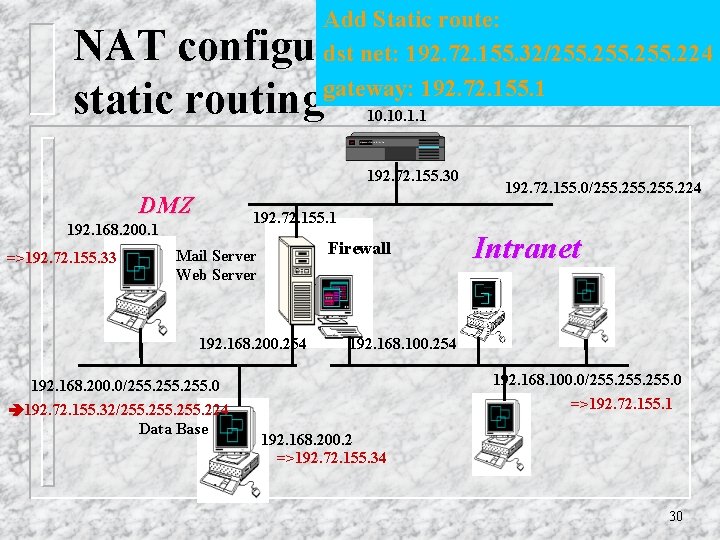
Add Static route: dst net: 192. 72. 155. 32/255. 224 gateway: 192. 72. 155. 1 NAT configuration– case 2 static routing 10. 1. 1 192. 72. 155. 30 DMZ 192. 72. 155. 1 192. 168. 200. 1 =>192. 72. 155. 33 192. 72. 155. 0/255. 224 Firewall Mail Server Web Server 192. 168. 200. 254 192. 168. 200. 0/255. 0 192. 72. 155. 32/255. 224 Data Base Intranet 192. 168. 100. 254 192. 168. 100. 0/255. 0 =>192. 72. 155. 1 192. 168. 200. 2 =>192. 72. 155. 34 30
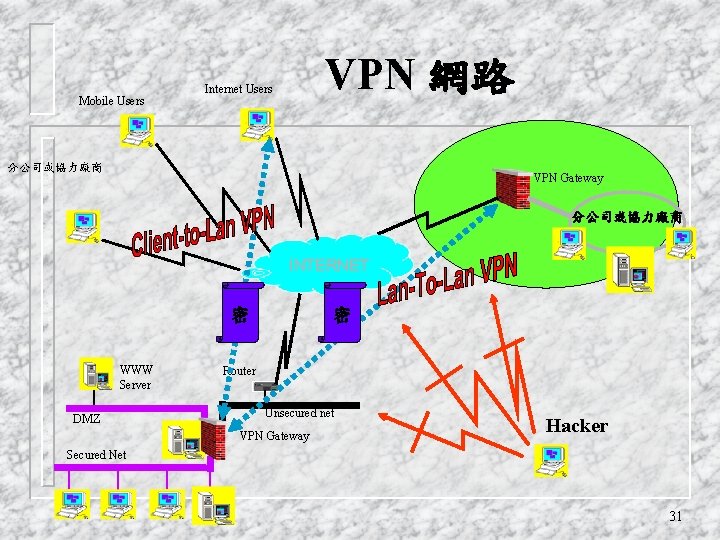
Mobile Users VPN 網路 Internet Users 分公司或協力廠商 VPN Gateway 分公司或協力廠商 INTERNET 密 WWW Server DMZ 密 Router Unsecured net VPN Gateway Hacker Secured Net 31
防範部份的網路攻擊 阻絕網路層的攻擊 v Ping Of Death, Source Routing, Tiny Fragment, Port Scanning, Land Attack, Teardrop, Out Of Band q 利用Packet Filtering Rules, Anti-Spoofing Rules 防止網站成為DDOS的第三者(Agent)利用Smurf、 SYN Flooding等DOS攻擊手段攻擊其他網站 q 攻擊追蹤 q 與即時入侵偵測系統(IDS)的整合或引發相 關安全規則的修正 q 32
網路層的攻擊 (1) q Ping o’ Death Attack q Send q ping (ICMP) packets larger than 64 K. Source Routing Attack q The source station specifies the route that a packet should take as it crosses the Internet. q Tiny Fragment Attack q Use the IP fragmentation to create extremely small fragments and force the TCP header information into a separate packet fragment. q Port Scanning Attack v Try different ports of the same destination address. 33
網路層的攻擊 (2) q Land Attack q Send a packet to a machine with the source host/port the same as the destination host/port. q Teardrop Attack q Packet fragments are deliberately fabricated with overlapping offset fields causing the host to hang or crash when it tries to reassemble them. q Out Of Band Attack 1. Makes TCP connection with port, 139, and then transmits data over the connection using a tag called MSG_OOB which tells Winsock to send Out of Band data. 34
網路層的攻擊 (3) q Smurf Attack v. Send ICMP echo request packets to an Internet broadcast address. q SYN Flooding Attack v. Send a high volume of TCP SYN packets without responding to the server’s acknowledgements (SYN ACK ). 35
記錄與預警 q 各種層次的記錄 q 預警方式 v. Console v. E-Mail v. Pager v. SNMP Trap v. User Defined Program 36
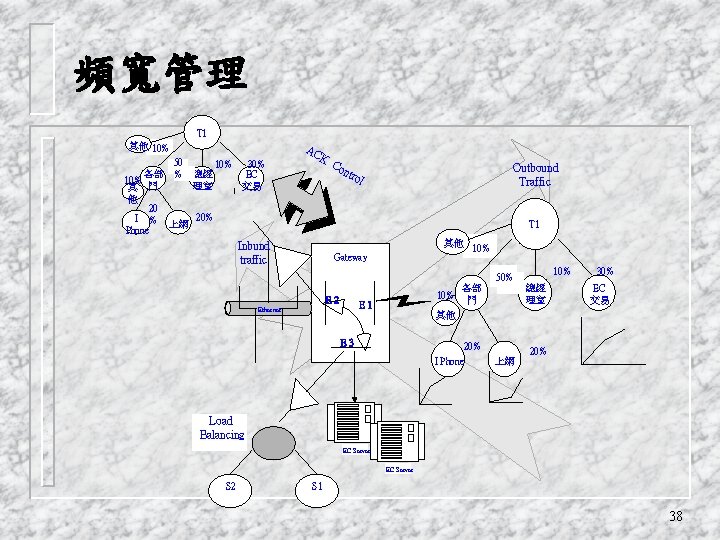
頻寬管理 T 1 其他 10% 50 10% 各部 % 總經 10% 理室 其 門 他 20 20% I % 上網 Phone AC 30% EC 交易 K Co Outbound Traffic ntr ol T 1 Inbund traffic 其他 10% Gateway 10% 50% E 2 10% E 1 Ethernet 各部 門 總經 理室 30% EC 交易 其他 E 3 20% I Phone 上網 20% Load Balancing EC Server S 2 S 1 38
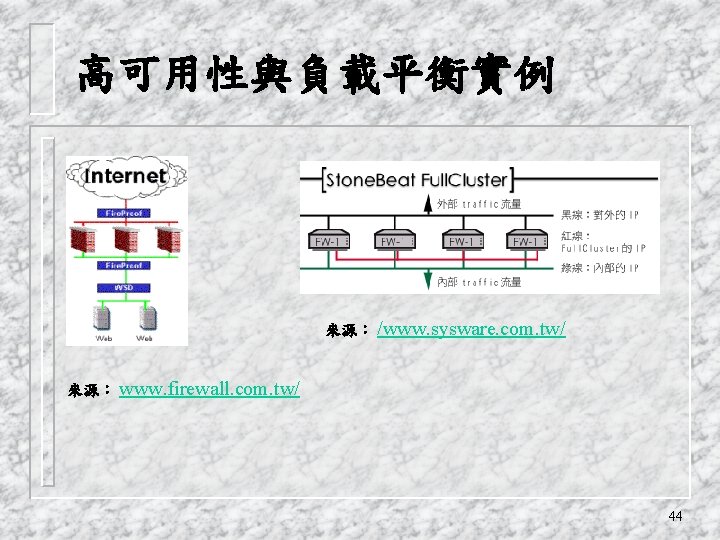
高可用性與負載平衡實例 來源: /www. sysware. com. tw/ 來源: www. firewall. com. tw/ 44
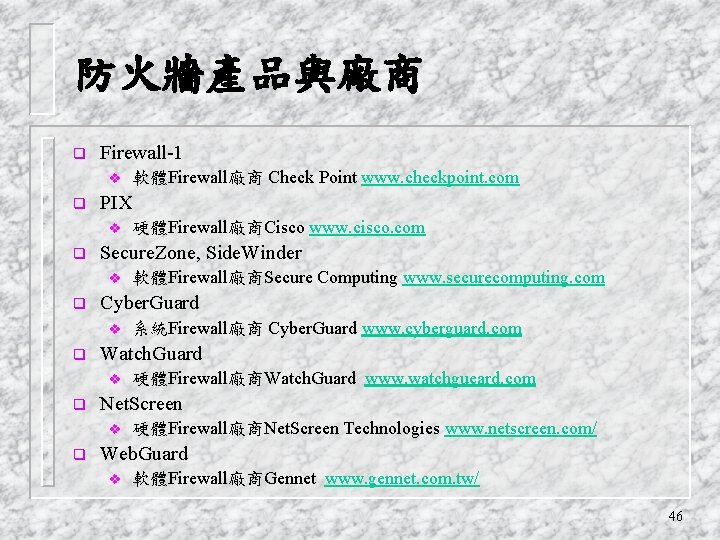
防火牆產品與廠商 q Firewall-1 v q PIX v q 硬體Firewall廠商Watch. Guard www. watchgueard. com Net. Screen v q 系統Firewall廠商 Cyber. Guard www. cyberguard. com Watch. Guard v q 軟體Firewall廠商Secure Computing www. securecomputing. com Cyber. Guard v q 硬體Firewall廠商Cisco www. cisco. com Secure. Zone, Side. Winder v q 軟體Firewall廠商 Check Point www. checkpoint. com 硬體Firewall廠商Net. Screen Technologies www. netscreen. com/ Web. Guard v 軟體Firewall廠商Gennet www. gennet. com. tw/ 46
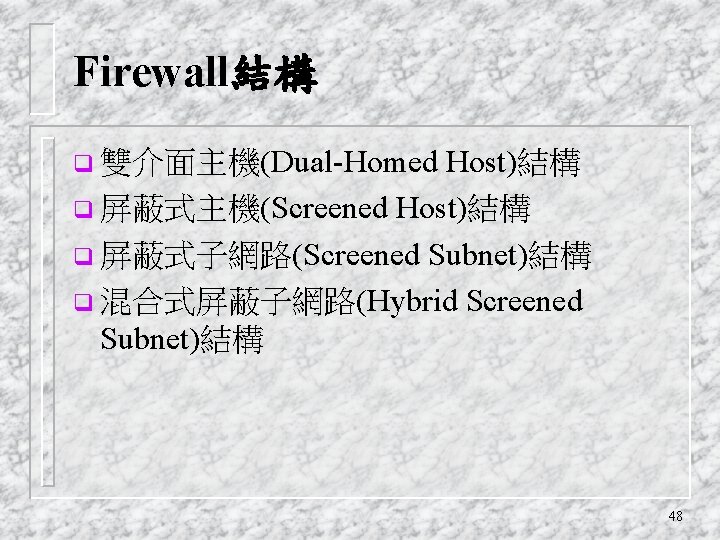
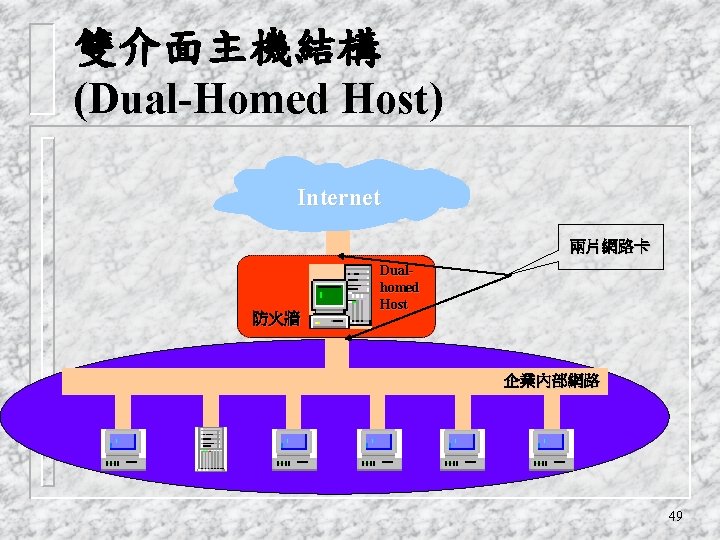
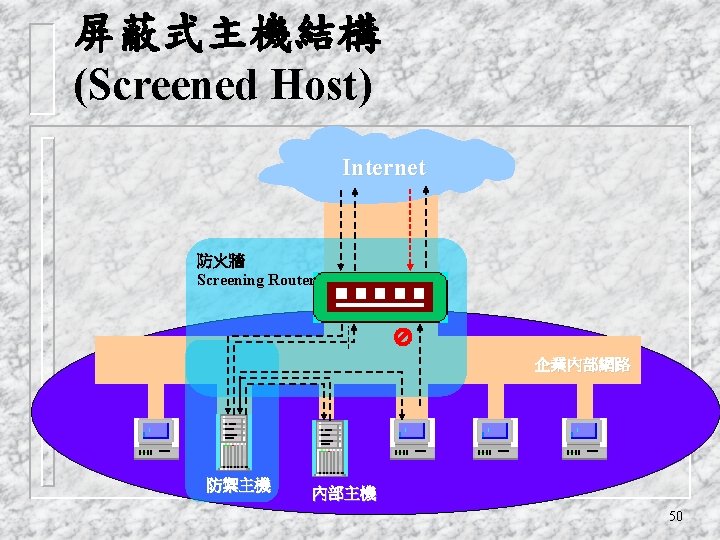
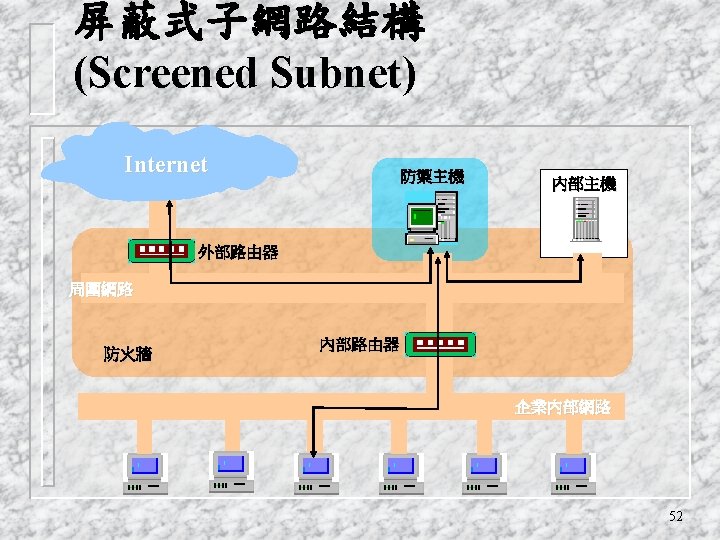
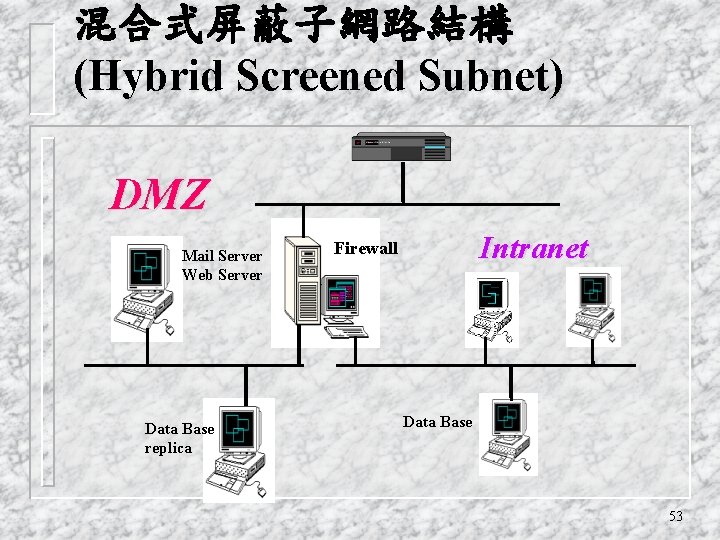
Firewall結構 Host)結構 q 屏蔽式主機(Screened Host)結構 q 屏蔽式子網路(Screened Subnet)結構 q 混合式屏蔽子網路(Hybrid Screened Subnet)結構 q 雙介面主機(Dual-Homed 48
雙介面主機結構 (Dual-Homed Host) Internet 兩片網路卡 防火牆 Dualhomed Host 企業內部網路 49
混合式屏蔽子網路結構 (Hybrid Screened Subnet) DMZ Mail Server Web Server Data Base replica Intranet Firewall Data Base 53
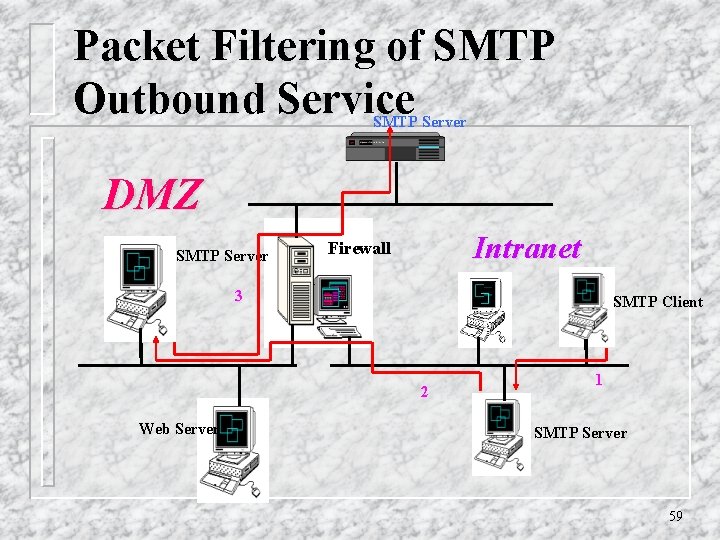
Packet Filtering of SMTP Outbound Service SMTP Server DMZ SMTP Server Intranet Firewall 3 SMTP Client 2 Web Server 1 SMTP Server 59
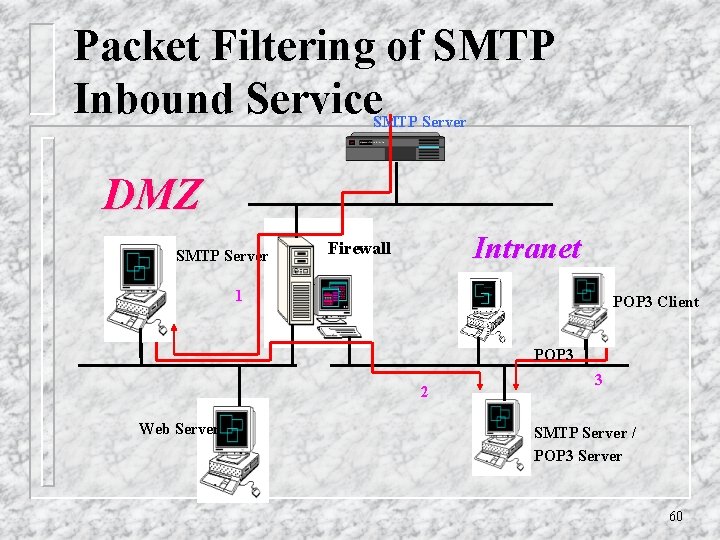
Packet Filtering of SMTP Inbound Service SMTP Server DMZ SMTP Server Intranet Firewall 1 POP 3 Client POP 3 2 Web Server 3 SMTP Server / POP 3 Server 60
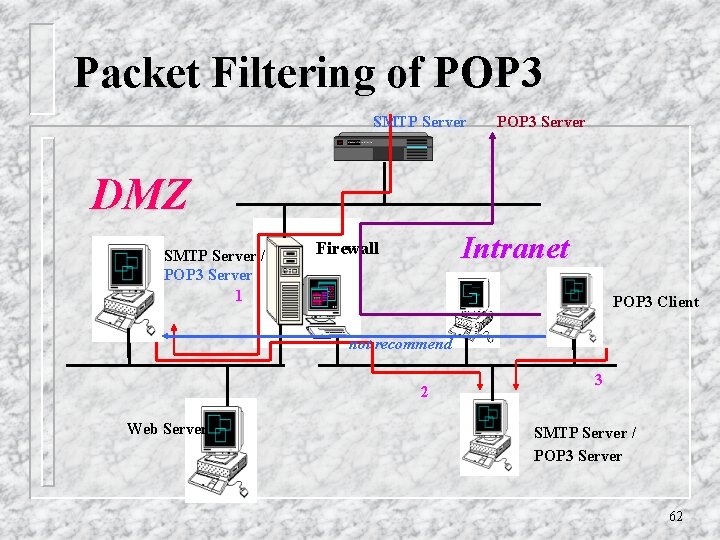
Packet Filtering of POP 3 SMTP Server POP 3 Server DMZ SMTP Server / POP 3 Server 1 Intranet Firewall POP 3 Client not recommend 2 Web Server 3 SMTP Server / POP 3 Server 62
Packet Filtering of FTP q Command Channel and Data Channel q Active and Passive Mode 63
Packet Filtering of Telnet q 盡量限制進入的Telnet q 利用Packet Filtering允許出去的Telnet 64
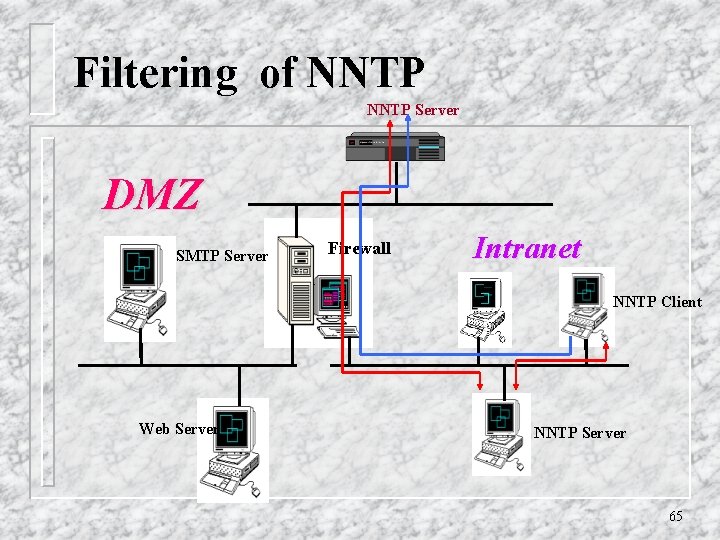
Filtering of NNTP Server DMZ SMTP Server Firewall Intranet NNTP Client Web Server NNTP Server 65
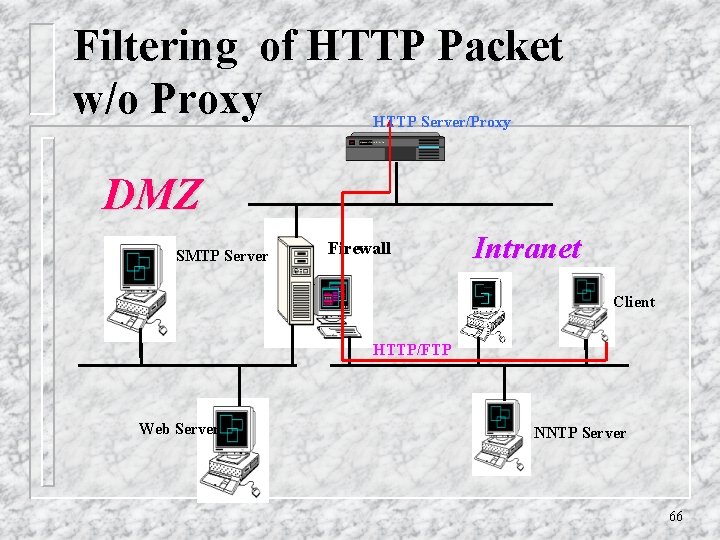
Filtering of HTTP Packet w/o Proxy HTTP Server/Proxy DMZ SMTP Server Firewall Intranet Client HTTP/FTP Web Server NNTP Server 66
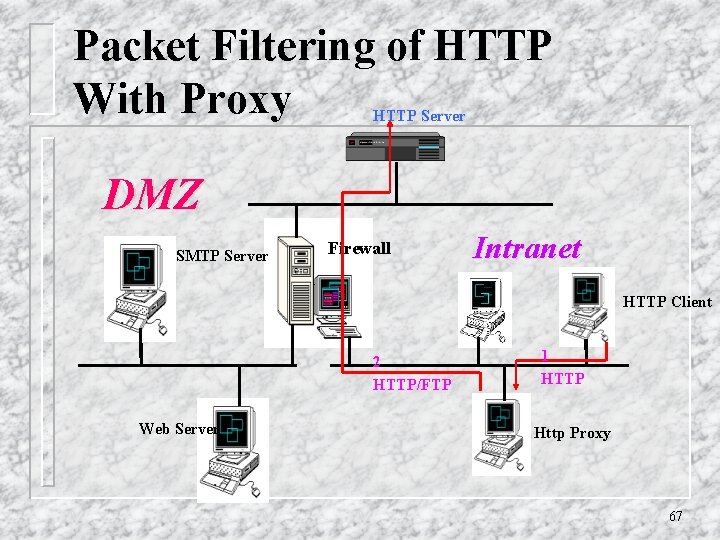
Packet Filtering of HTTP With Proxy HTTP Server DMZ SMTP Server Firewall Intranet HTTP Client 2 HTTP/FTP Web Server 1 HTTP Http Proxy 67
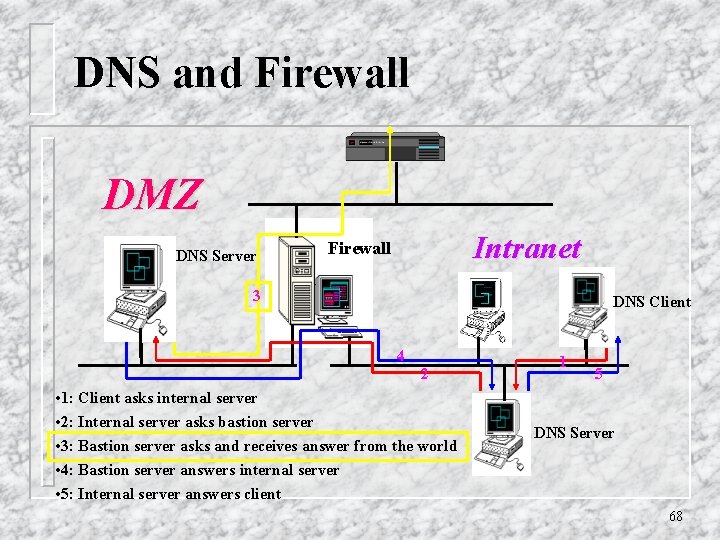
DNS and Firewall DMZ DNS Server Intranet Firewall 3 DNS Client 4 2 • 1: Client asks internal server • 2: Internal server asks bastion server • 3: Bastion server asks and receives answer from the world • 4: Bastion server answers internal server • 5: Internal server answers client 1 5 DNS Server 68
Security Policy q What and Why to Protect, instead of How 69
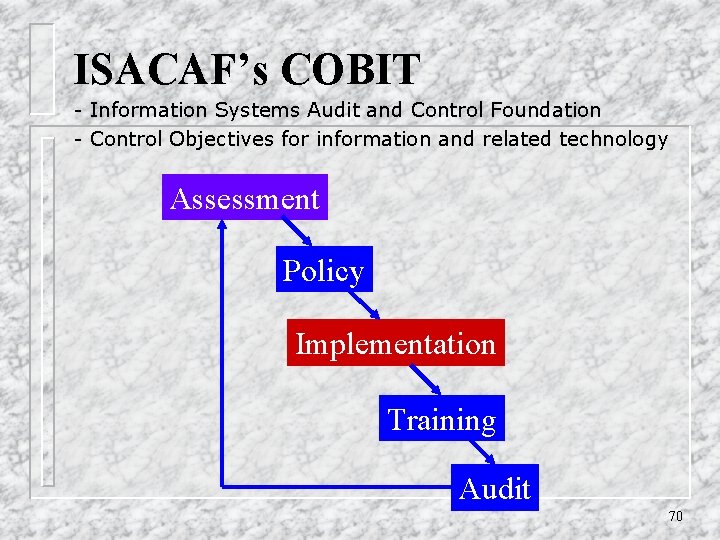
ISACAF’s COBIT - Information Systems Audit and Control Foundation - Control Objectives for information and related technology Assessment Policy Implementation Training Audit 70
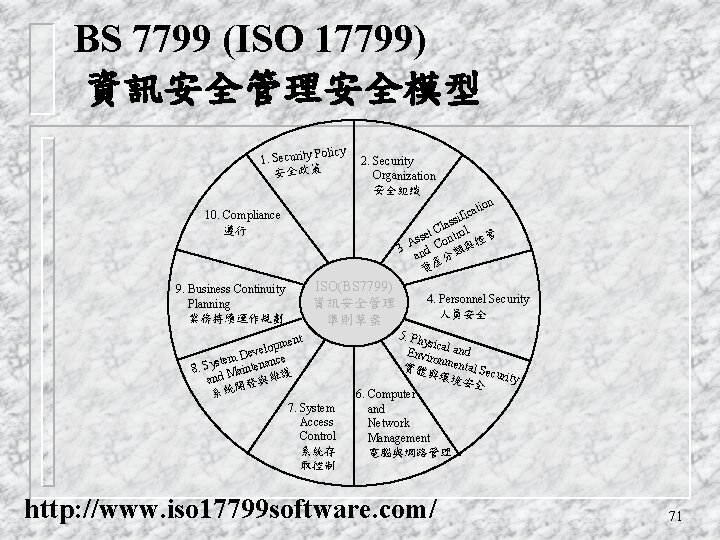
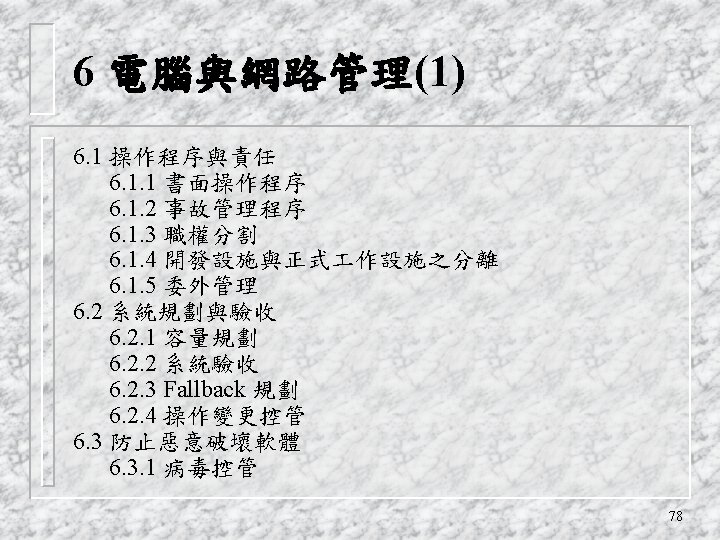
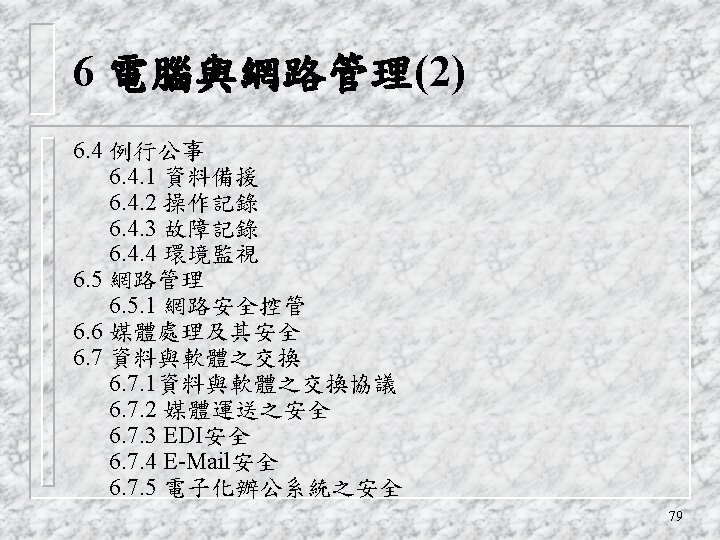
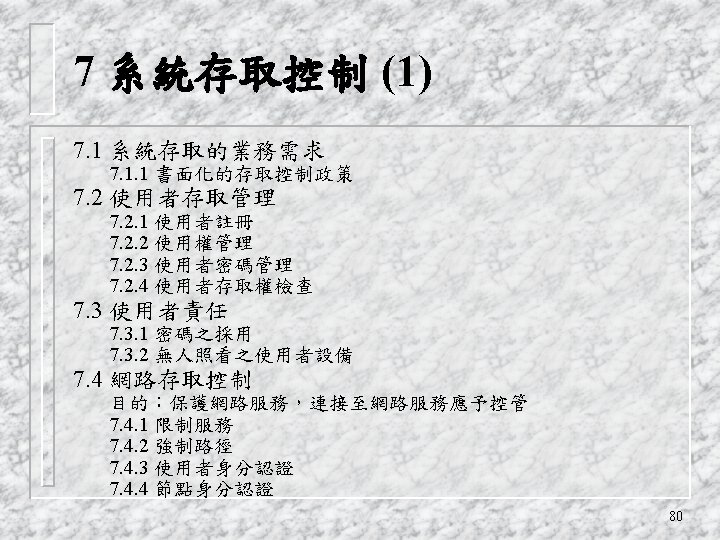
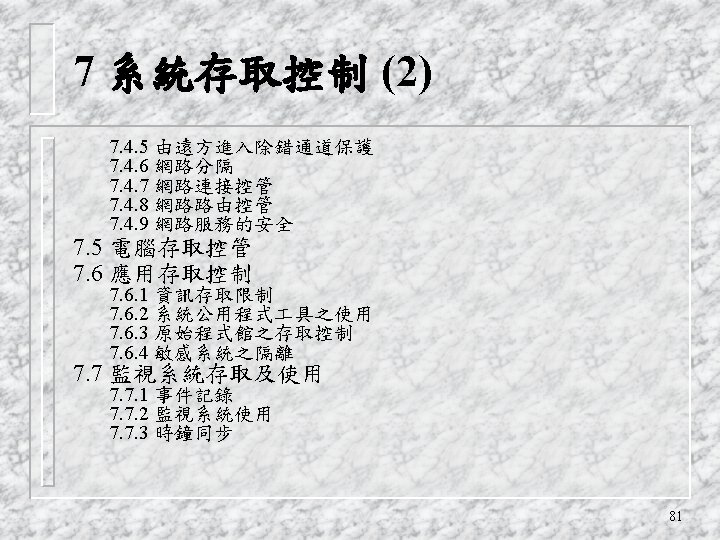
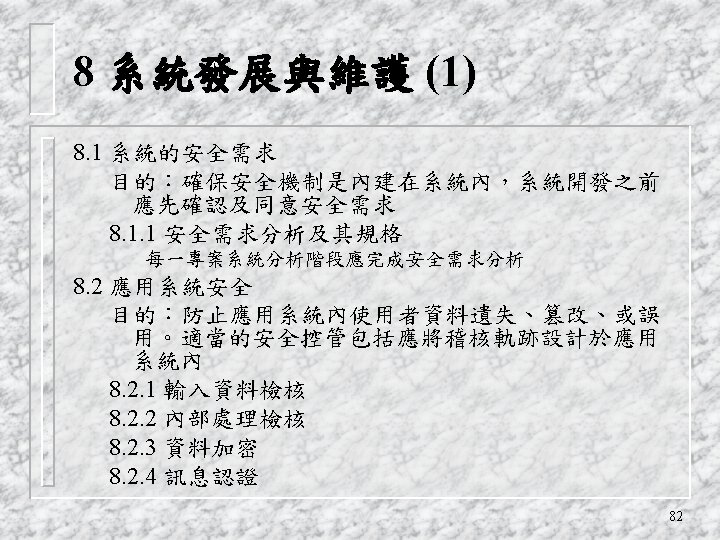
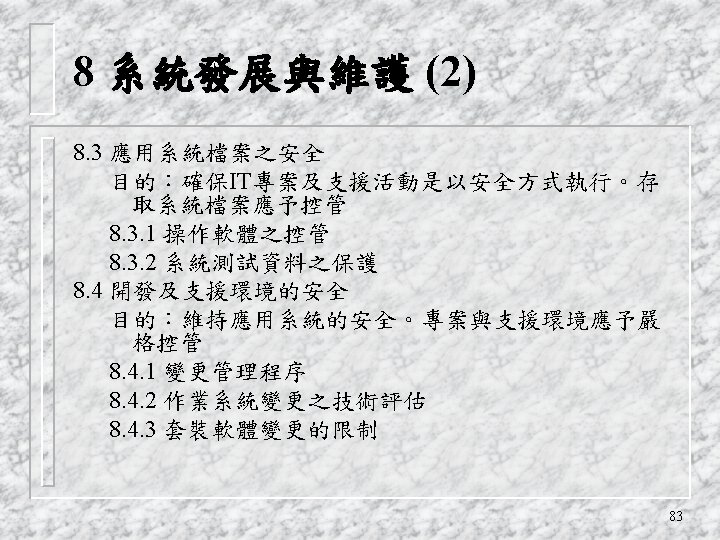
BS 7799 (ISO 17799) 資訊安全管理安全模型 olicy 1. Security P 安全政策 2. Security Organization 安全組織 tion a c i sif las l C t o sse ontr 控管 A C. 3 nd 類與 a 分 資產 10. Compliance 遵行 9. Business Continuity Planning 業務持續運作規劃 ISO(BS 7799) 資訊安全管理 準則草案 t pmen o l e v De stem tenance y S. 8 ain 護 and M 發與維 開 系統 7. System Access Control 系統存 取控制 4. Personnel Security 人員安全 5. Phy sica Envir l and on 實體與 mental Se 環境安 curity 全 6. Computer and Network Management 電腦與網路管理 http: //www. iso 17799 software. com/ 71
Maintaining Firewalls (1) q Housekeeping v. Backing Ø access Up Your Firewall control rules, router configurations v. Managing Your Accounts Ø adding new accounts, removing old ones, aging passwords v. Managing Ø check Your Disk Space data, back up and clean up log 89
Maintaining Firewalls (2) q Monitoring Your System v Analyzing your firewall log and making report v What should you watch for? Ø All dropped packets, denied connections, and rejected attempts Ø At least the time, protocol, and user name for every successful connection to or through your bastion host Ø All error messages from your routers, your bastion host, and any proxying programs Ø All error messages 90
Maintaining Firewalls (3) Keeping Up to Date v Keeping Yourself Up to Date v Mailing lists v Newsgroups v Magazines v Professional forums q Keeping Your Systems Up to Date v Don’t be in a hurry to upgrade v Don’t patch problems you don’t have v Beware of interdependent patches q 91
Responding to Security Incidents q Evaluate the Situation q Disconnect or Shutdown q Analyze and Respond q Notifications q Snapshot the System q Restore and Recover q Document the Incident 92
網路安全相關網站 (1) q 安全漏洞描述 vwww. ntbugtraq. com voliver. efri. hr/~crv/security/bugs/ vwww. sans. org/ q CERT: v. CERT: www. cert. org v. TW CERT: www. cert. org. tw 93
網路安全相關網站 (2) OS Patches v SUN OS Patches: access 1. sun. com v HP-UX Patches: us-support 2. external. hp. com v Microsoft: www. microsoft. com/security q 網路掃描器 v SATAN: www. fish. com/~zen/satan. html v NESSUS: www. nessus. org v ISS: www. iss. net q 94