Windows Kernel Team Pwn 4 Fun Agenda 1
- Slides: 26
Windows Kernel 취약점 분석 취약점 Team Pwn 4 Fun
Agenda 1. Outline 2. Syscall Fuzzer 3. API Fuzzer 4. Fuzzer Platform 5. Current Result 6. Future Plan
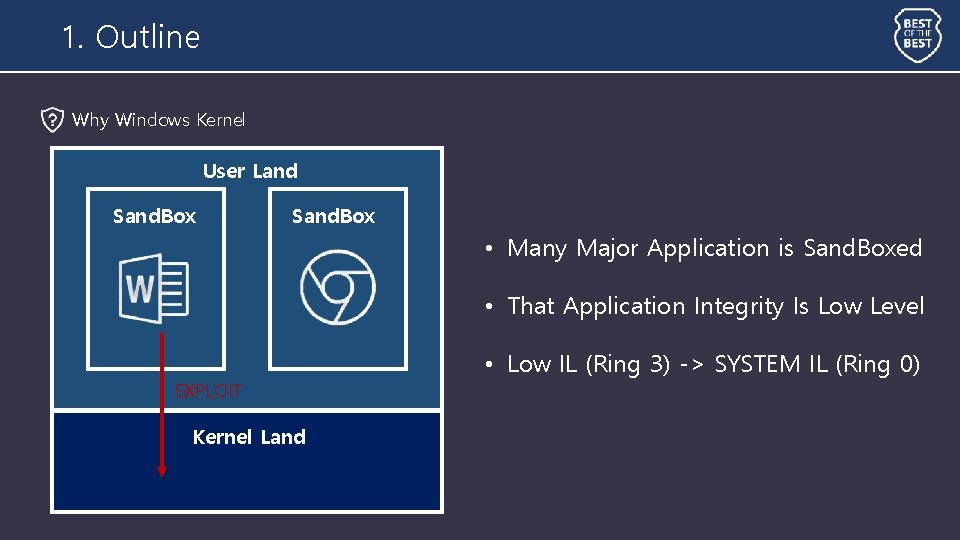
1. Outline Why Windows Kernel User Land Sand. Box • Many Major Application is Sand. Boxed • That Application Integrity Is Low Level EXPLOIT Kernel Land • Low IL (Ring 3) -> SYSTEM IL (Ring 0)
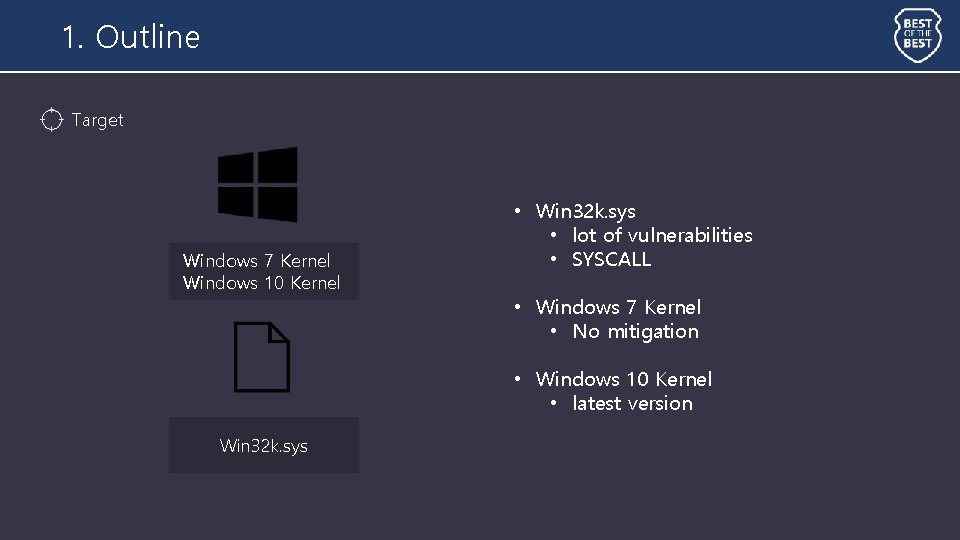
1. Outline Target Windows 7 Kernel Windows 10 Kernel • Win 32 k. sys • lot of vulnerabilities • SYSCALL • Windows 7 Kernel • No mitigation • Windows 10 Kernel • latest version Win 32 k. sys
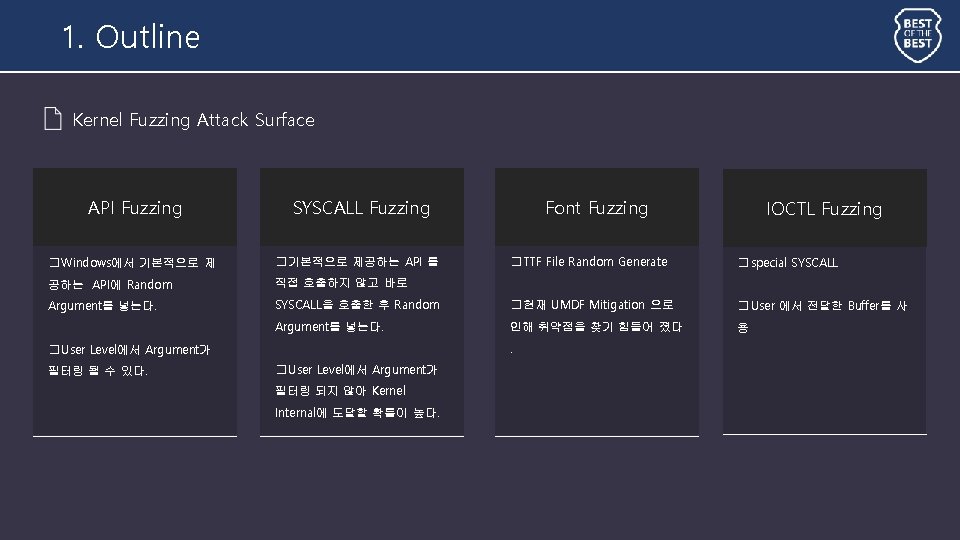
1. Outline Kernel Fuzzing Attack Surface API Fuzzing SYSCALL Fuzzing � Windows에서 기본적으로 제 � 기본적으로 제공하는 API 를 공하는 API에 Random 직접 호출하지 않고 바로 Argument를 넣는다. IOCTL Fuzzing � TTF File Random Generate � special SYSCALL을 호출한 후 Random � 현재 UMDF Mitigation 으로 � User 에서 전달한 Buffer를 사 Argument를 넣는다. 인해 취약점을 찾기 힘들어 졌다 용 . � User Level에서 Argument가 필터링 될 수 있다. Font Fuzzing � User Level에서 Argument가 필터링 되지 않아 Kernel Internal에 도달할 확률이 높다.
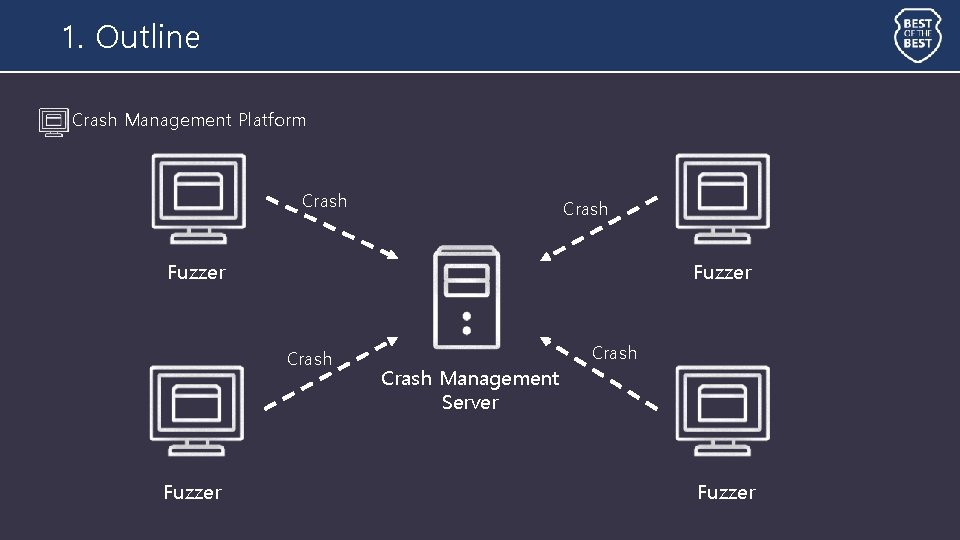
1. Outline Crash Management Platform Crash Fuzzer Crash Management Server Crash Fuzzer
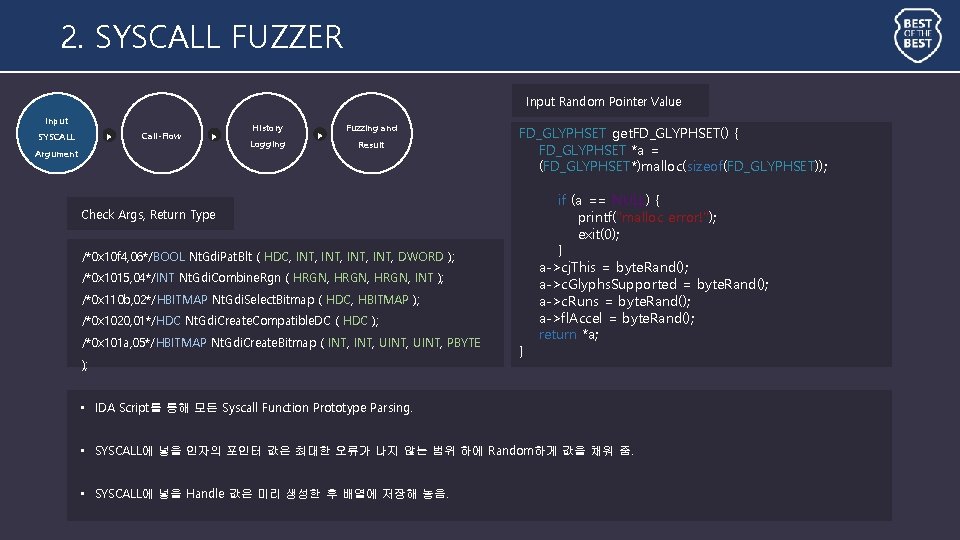
2. SYSCALL FUZZER Input Random Pointer Value Input SYSCALL ▶ Call-Flow ▶ Argument History Logging ▶ Fuzzing and Result FD_GLYPHSET get. FD_GLYPHSET() { FD_GLYPHSET *a = (FD_GLYPHSET*)malloc(sizeof(FD_GLYPHSET)); Check Args, Return Type /*0 x 10 f 4, 06*/BOOL Nt. Gdi. Pat. Blt ( HDC, INT, DWORD ); /*0 x 1015, 04*/INT Nt. Gdi. Combine. Rgn ( HRGN, INT ); /*0 x 110 b, 02*/HBITMAP Nt. Gdi. Select. Bitmap ( HDC, HBITMAP ); /*0 x 1020, 01*/HDC Nt. Gdi. Create. Compatible. DC ( HDC ); /*0 x 101 a, 05*/HBITMAP Nt. Gdi. Create. Bitmap ( INT, UINT, PBYTE ); } if (a == NULL) { printf("malloc error!"); exit(0); } a->cj. This = byte. Rand(); a->c. Glyphs. Supported = byte. Rand(); a->c. Runs = byte. Rand(); a->fl. Accel = byte. Rand(); return *a; • IDA Script를 통해 모든 Syscall Function Prototype Parsing. • SYSCALL에 넣을 인자의 포인터 값은 최대한 오류가 나지 않는 범위 하에 Random하게 값을 채워 줌. • SYSCALL에 넣을 Handle 값은 미리 생성한 후 배열에 저장해 놓음.
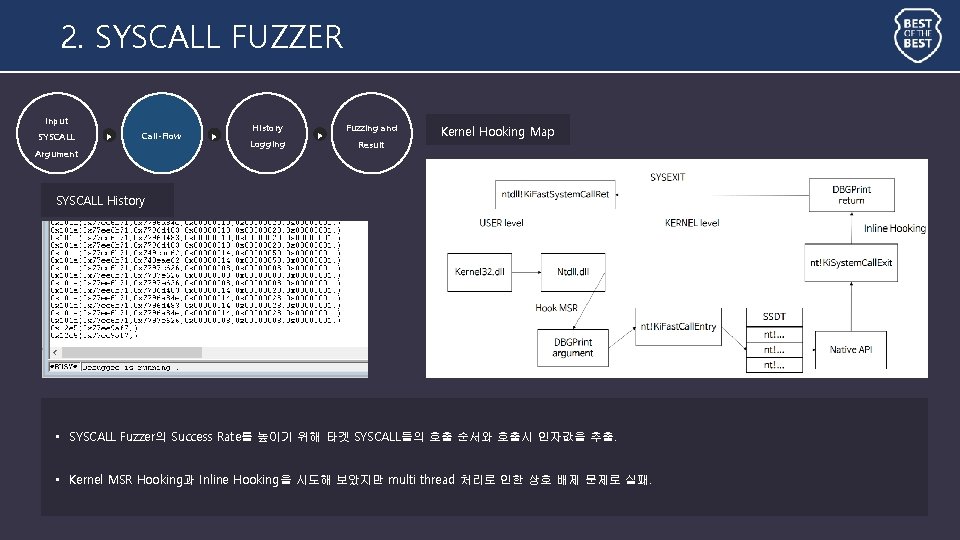
2. SYSCALL FUZZER Input SYSCALL ▶ Call-Flow Argument ▶ History Logging ▶ Fuzzing and Result Kernel Hooking Map SYSCALL History • SYSCALL Fuzzer의 Success Rate를 높이기 위해 타겟 SYSCALL들의 호출 순서와 호출시 인자값을 추출. • Kernel MSR Hooking과 Inline Hooking을 시도해 보았지만 multi thread 처리로 인한 상호 배제 문제로 실패.
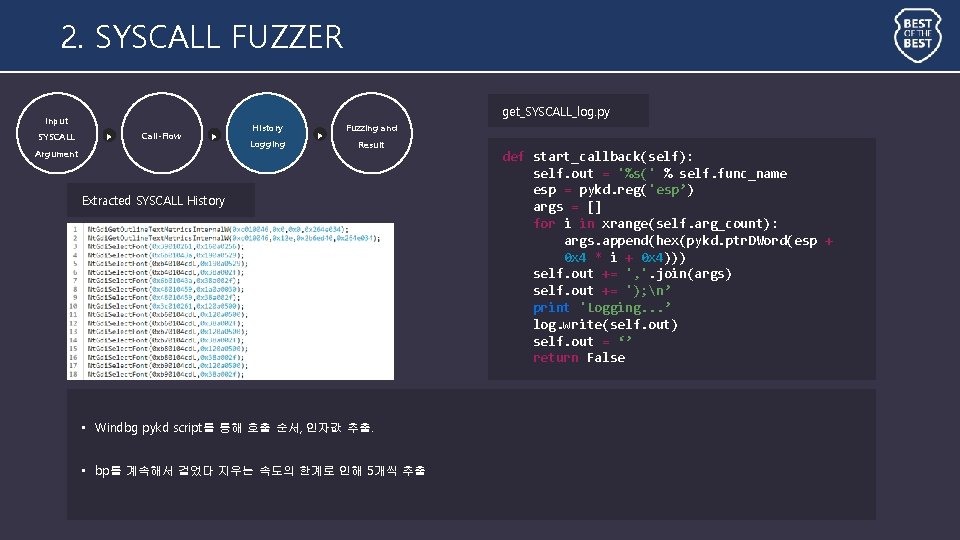
2. SYSCALL FUZZER get_SYSCALL_log. py Input SYSCALL ▶ Call-Flow ▶ Argument History Logging ▶ Fuzzing and Result Extracted SYSCALL History • Windbg pykd script를 통해 호출 순서, 인자값 추출. • bp를 계속해서 걸었다 지우는 속도의 한계로 인해 5개씩 추출 def start_callback(self): self. out = '%s(' % self. func_name esp = pykd. reg('esp’) args = [] for i in xrange(self. arg_count): args. append(hex(pykd. ptr. DWord(esp + 0 x 4 * i + 0 x 4))) self. out += ', '. join(args) self. out += '); n’ print 'Logging. . . ’ log. write(self. out) self. out = ‘’ return False
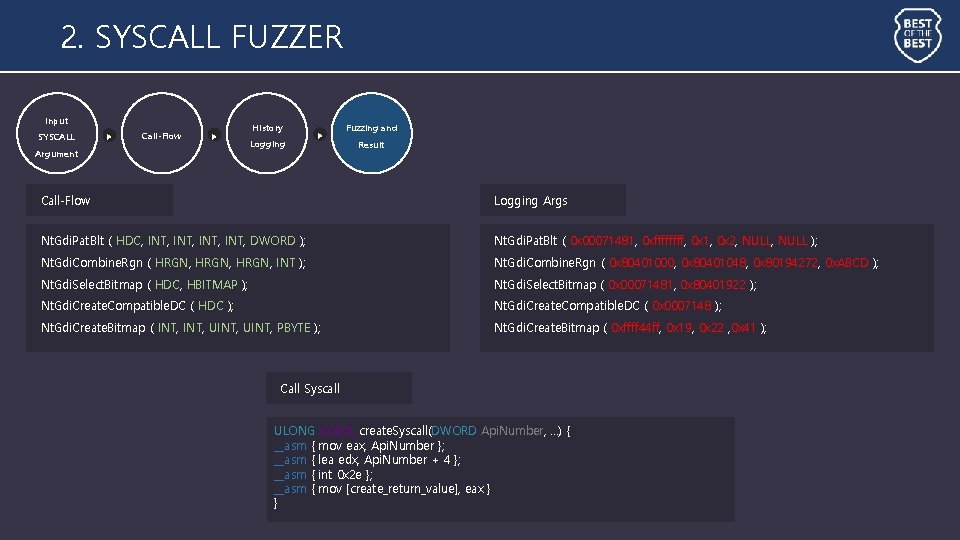
2. SYSCALL FUZZER Input SYSCALL ▶ Call-Flow ▶ Argument History Logging ▶ Fuzzing and Result Call-Flow Logging Args Nt. Gdi. Pat. Blt ( HDC, INT, DWORD ); Nt. Gdi. Pat. Blt ( 0 x 00071481, 0 xffff, 0 x 1, 0 x 2, NULL ); Nt. Gdi. Combine. Rgn ( HRGN, INT ); Nt. Gdi. Combine. Rgn ( 0 x 80401000, 0 x 80401048, 0 x 80194272, 0 x. ABCD ); Nt. Gdi. Select. Bitmap ( HDC, HBITMAP ); Nt. Gdi. Select. Bitmap ( 0 x 00071481, 0 x 80401922 ); Nt. Gdi. Create. Compatible. DC ( HDC ); Nt. Gdi. Create. Compatible. DC ( 0 x 0007148 ); Nt. Gdi. Create. Bitmap ( INT, UINT, PBYTE ); Nt. Gdi. Create. Bitmap ( 0 xffff 44 ff, 0 x 19, 0 x 22 , 0 x 41 ); Call Syscall ULONG CDECL create. Syscall(DWORD Api. Number, . . . ) { __asm { mov eax, Api. Number }; __asm { lea edx, Api. Number + 4 }; __asm { int 0 x 2 e }; __asm { mov [create_return_value], eax } }
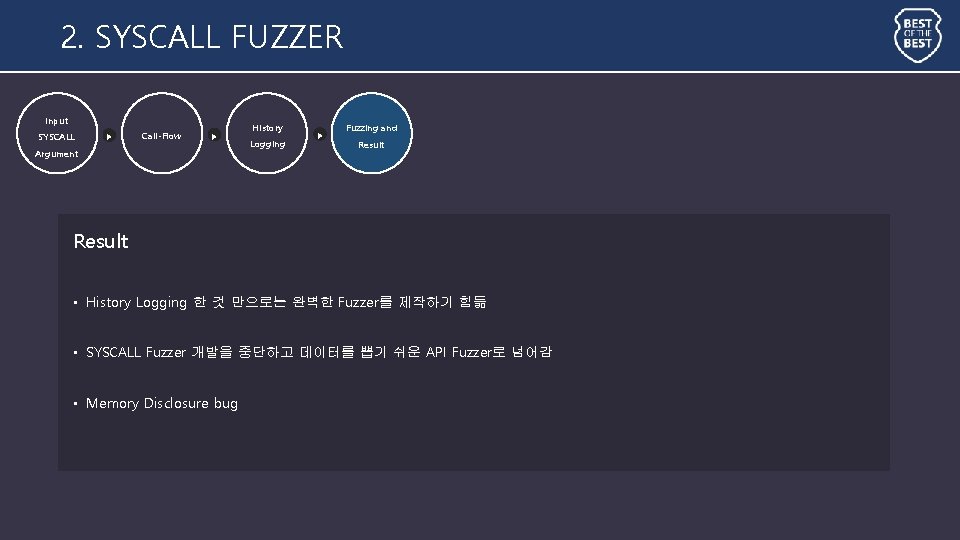
2. SYSCALL FUZZER Input SYSCALL ▶ Call-Flow ▶ Argument History Logging ▶ Fuzzing and Result • History Logging 한 것 만으로는 완벽한 Fuzzer를 제작하기 힘듦 • SYSCALL Fuzzer 개발을 중단하고 데이터를 뽑기 쉬운 API Fuzzer로 넘어감 • Memory Disclosure bug
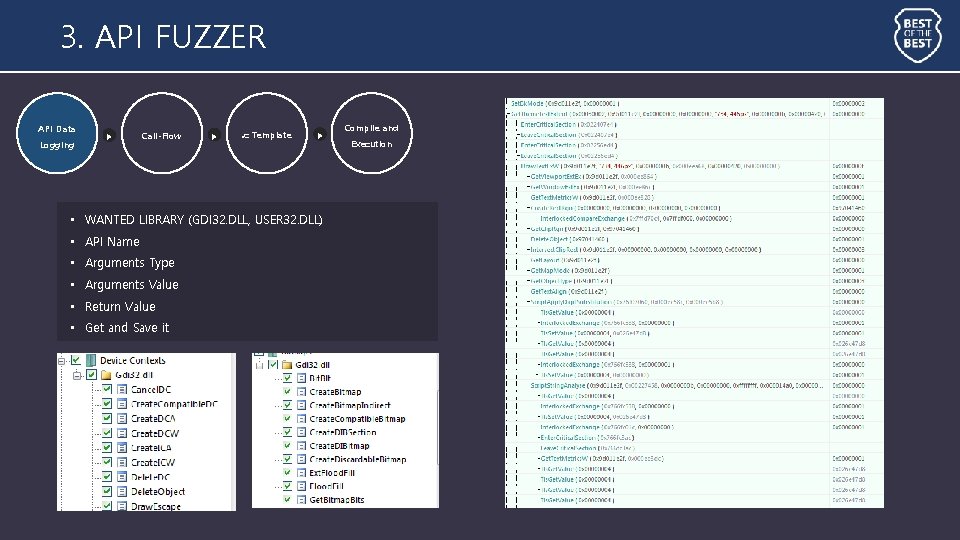
3. API FUZZER API Data Logging ▶ Call-Flow ▶ . c Template ▶ • WANTED LIBRARY (GDI 32. DLL, USER 32. DLL) • API Name • Arguments Type • Arguments Value • Return Value • Get and Save it Compile and Execution
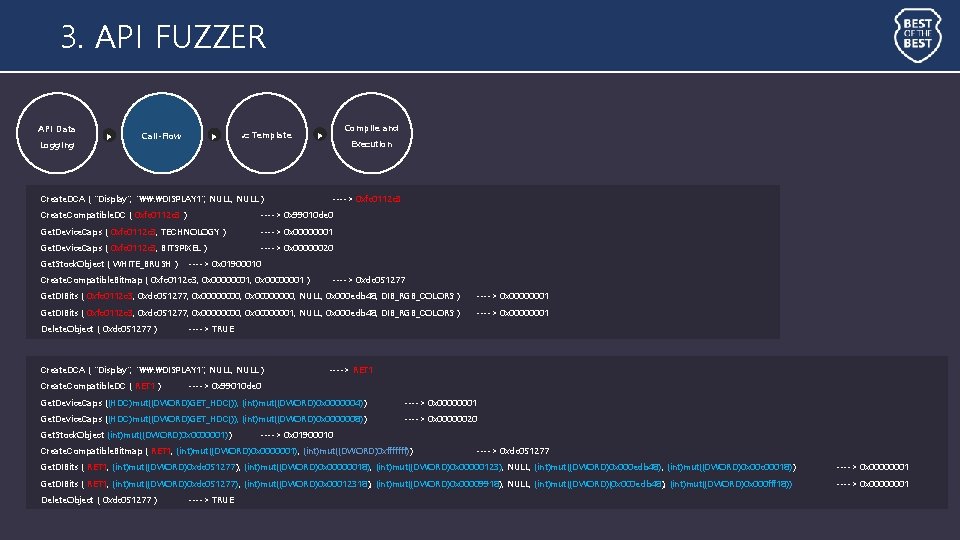
3. API FUZZER API Data Logging ▶ Call-Flow ▶ . c Template Create. DCA ( "Display", "\. DISPLAY 1", NULL ) Compile and ▶ Execution ----> 0 xfc 0112 c 3 Create. Compatible. DC ( 0 xfc 0112 c 3 ) ----> 0 x 99010 de 0 Get. Device. Caps ( 0 xfc 0112 c 3, TECHNOLOGY ) ----> 0 x 00000001 Get. Device. Caps ( 0 xfc 0112 c 3, BITSPIXEL ) ----> 0 x 00000020 Get. Stock. Object ( WHITE_BRUSH ) ----> 0 x 01900010 Create. Compatible. Bitmap ( 0 xfc 0112 c 3, 0 x 00000001 ) ----> 0 xdc 051277 Get. DIBits ( 0 xfc 0112 c 3, 0 xdc 051277, 0 x 00000000, NULL, 0 x 000 edb 48, DIB_RGB_COLORS ) ----> 0 x 00000001 Get. DIBits ( 0 xfc 0112 c 3, 0 xdc 051277, 0 x 0000, 0 x 00000001, NULL, 0 x 000 edb 48, DIB_RGB_COLORS ) ----> 0 x 00000001 Delete. Object ( 0 xdc 051277 ) ----> TRUE Create. DCA ( "Display", "\. DISPLAY 1", NULL ) Create. Compatible. DC ( RET 1 ) ----> RET 1 ----> 0 x 99010 de 0 Get. Device. Caps ((HDC)mut((DWORD)GET_HDC()), (int)mut((DWORD)0 x 0000004) ) ----> 0 x 00000001 Get. Device. Caps ((HDC)mut((DWORD)GET_HDC()), (int)mut((DWORD)0 x 0000008) ) ----> 0 x 00000020 Get. Stock. Object (int)mut((DWORD)0 x 0000001)) ----> 0 x 01900010 Create. Compatible. Bitmap ( RET 1, (int)mut((DWORD)0 x 0000001), (int)mut((DWORD)0 xfffffff)) ----> 0 xdc 051277 Get. DIBits ( RET 1, (int)mut((DWORD)0 xdc 051277), (int)mut((DWORD)0 x 00000018), (int)mut((DWORD)0 x 00000123), NULL, (int)mut((DWORD)0 x 000 edb 48), (int)mut((DWORD)0 x 00 c 00018)) ----> 0 x 00000001 Get. DIBits ( RET 1, (int)mut((DWORD)0 xdc 051277), (int)mut((DWORD)0 x 00012318), (int)mut((DWORD)0 x 00009918), NULL, (int)mut((DWORD)(0 x 000 edb 48), (int)mut((DWORD)0 x 000 fff 18)) ----> 0 x 00000001 Delete. Object ( 0 xdc 051277 ) ----> TRUE
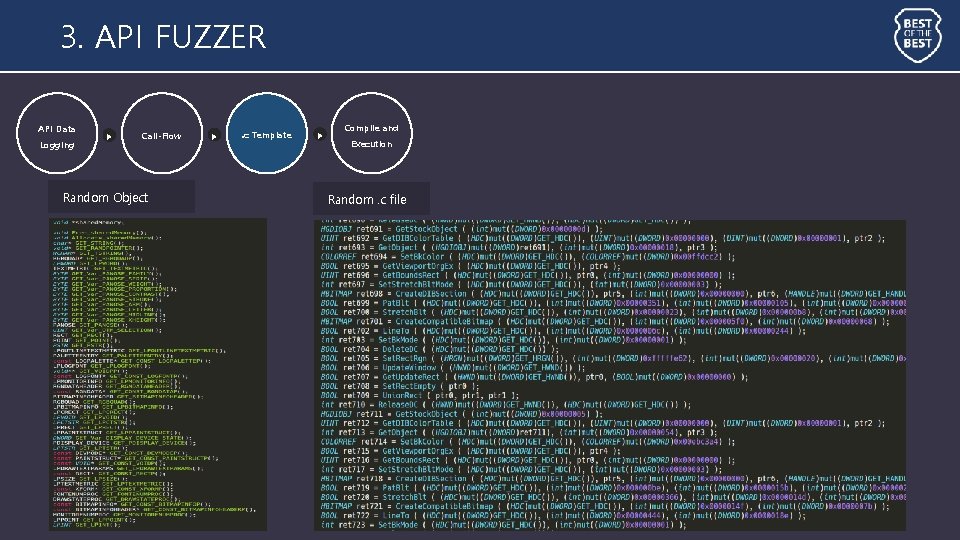
3. API FUZZER API Data Logging ▶ Call-Flow Random Object ▶ . c Template ▶ Compile and Execution Random. c file
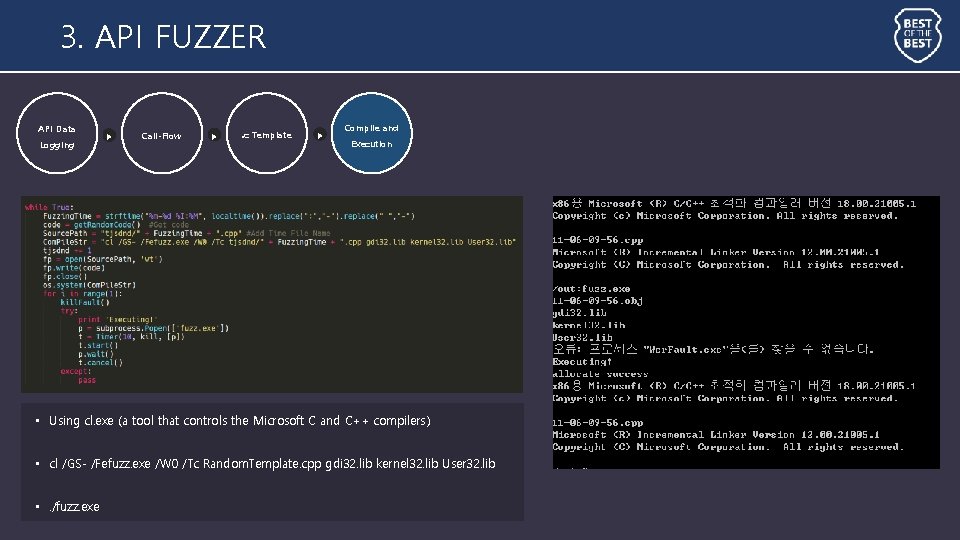
3. API FUZZER API Data Logging ▶ Call-Flow ▶ . c Template ▶ Compile and Execution • Using cl. exe (a tool that controls the Microsoft C and C++ compilers) • cl /GS- /Fefuzz. exe /W 0 /Tc Random. Template. cpp gdi 32. lib kernel 32. lib User 32. lib • . /fuzz. exe
3. API FUZZER API Fuzzer Demo
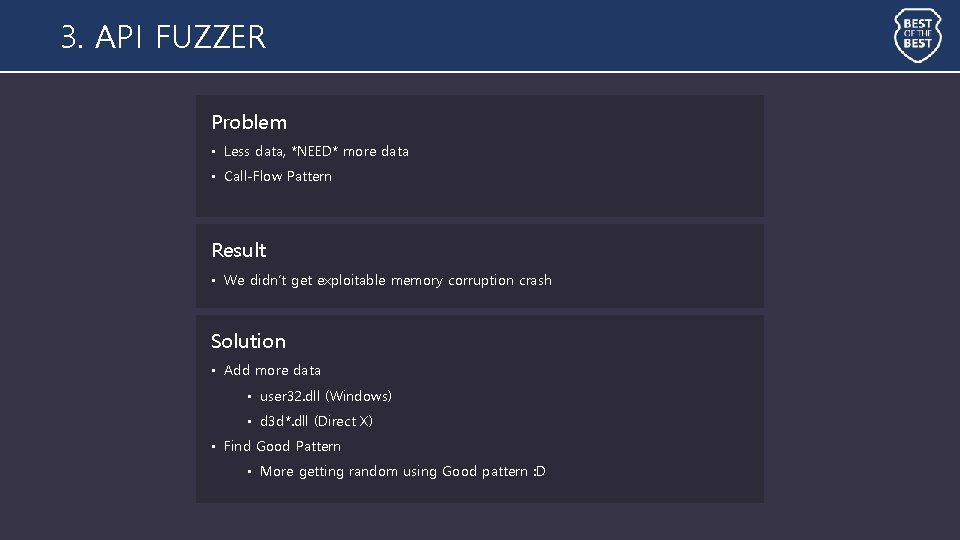
3. API FUZZER Problem • Less data, *NEED* more data • Call-Flow Pattern Result • We didn’t get exploitable memory corruption crash Solution • Add more data • user 32. dll (Windows) • d 3 d*. dll (Direct X) • Find Good Pattern • More getting random using Good pattern : D
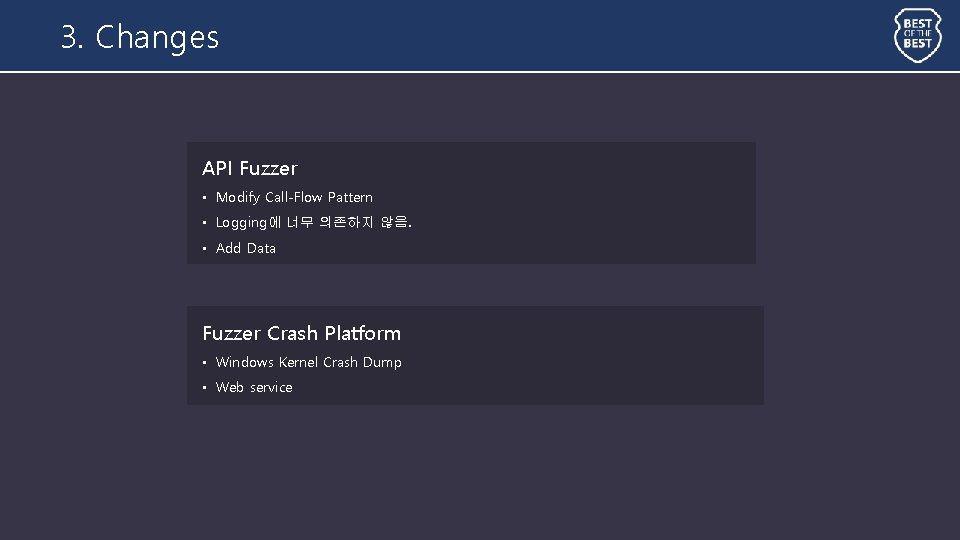
3. Changes API Fuzzer • Modify Call-Flow Pattern • Logging에 너무 의존하지 않음. • Add Data Fuzzer Crash Platform • Windows Kernel Crash Dump • Web service
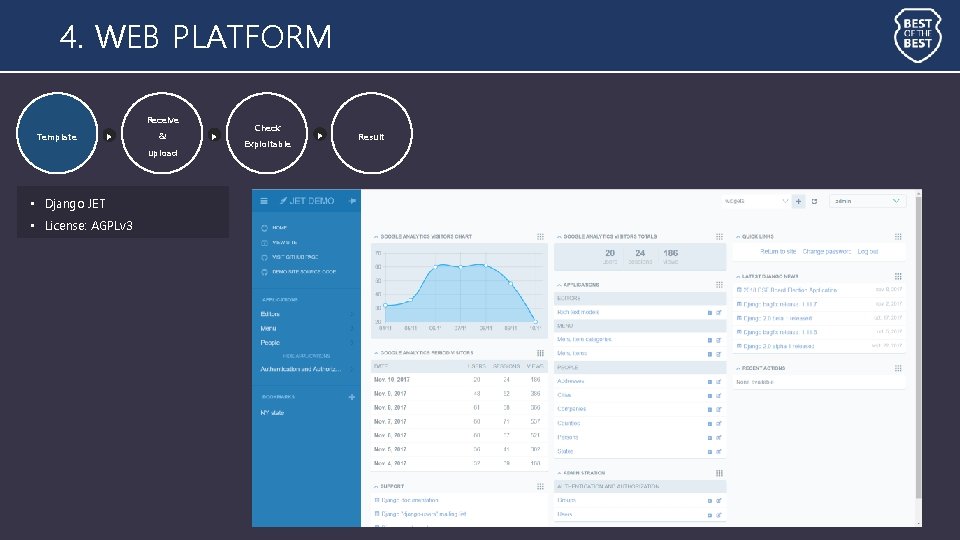
4. WEB PLATFORM Receive Template ▶ & upload • Django JET • License: AGPLv 3 ▶ Check Exploitable ▶ Result
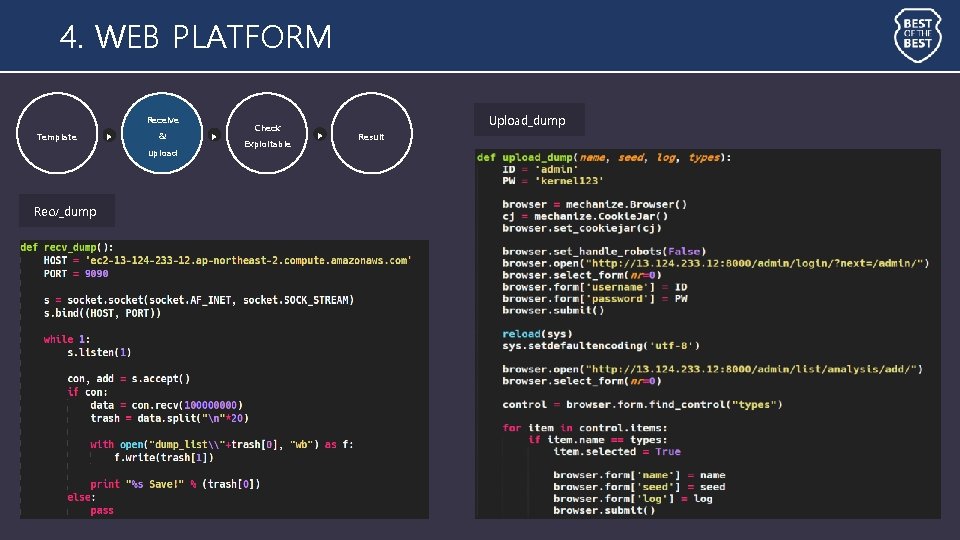
4. WEB PLATFORM Receive Template ▶ & upload Recv_dump ▶ Check Exploitable Upload_dump ▶ Result
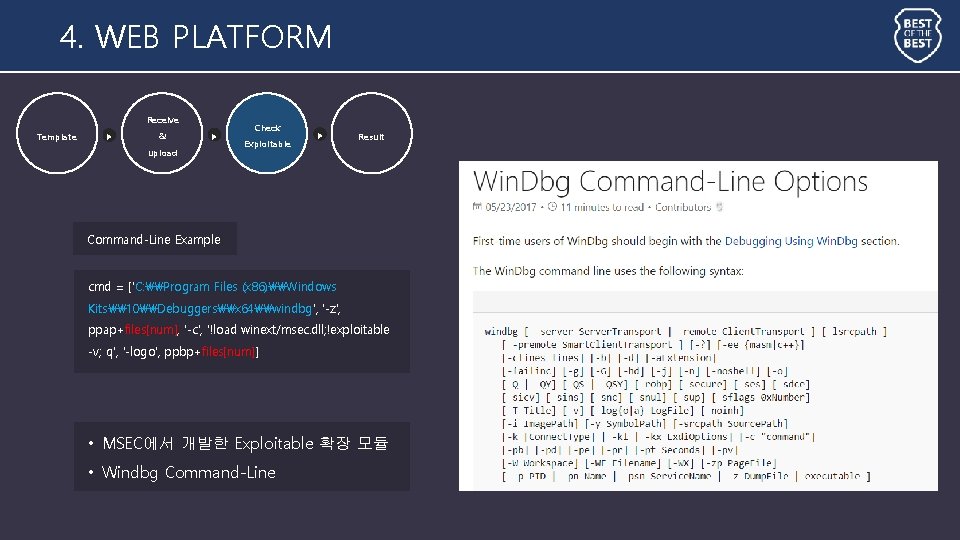
4. WEB PLATFORM Receive Template ▶ & ▶ upload Check Exploitable ▶ Result Command-Line Example cmd = ['C: \Program Files (x 86)\Windows Kits\10\Debuggers\x 64\windbg', '-z', ppap+files[num], '-c', '!load winext/msec. dll; !exploitable -v; q', '-logo', ppbp+files[num]] • MSEC에서 개발한 Exploitable 확장 모듈 • Windbg Command-Line
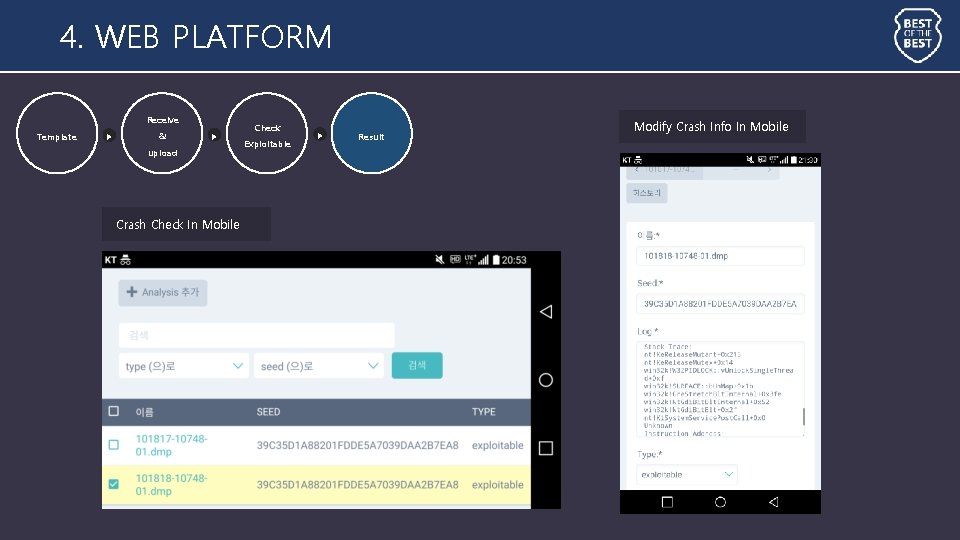
4. WEB PLATFORM Receive Template ▶ & ▶ upload Crash Check In Mobile Check Exploitable ▶ Result Modify Crash Info In Mobile
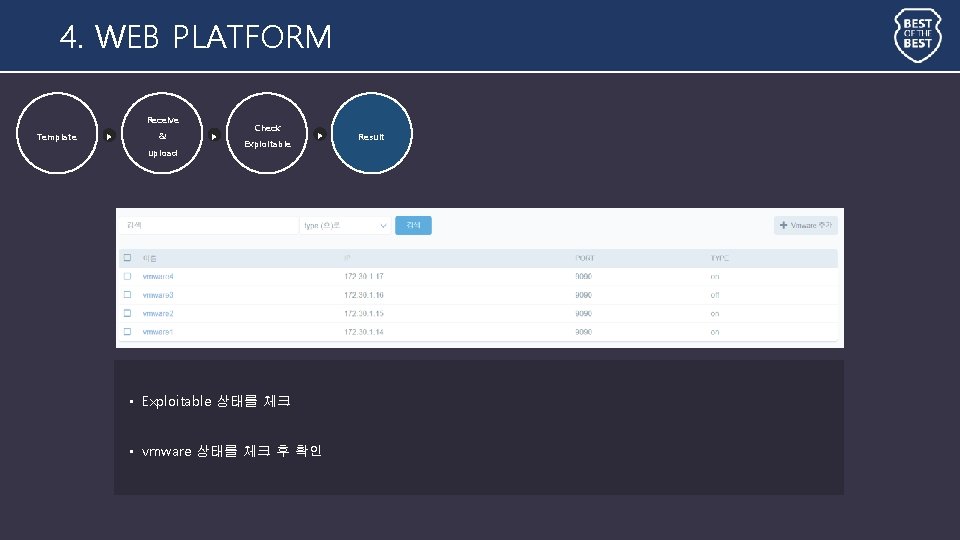
4. WEB PLATFORM Receive Template ▶ & upload ▶ Check Exploitable ▶ • Exploitable 상태를 체크 • vmware 상태를 체크 후 확인 Result
5. CURRENT RESULT Two Kernel Crash Four Kernel Information Address Leak Windows Kernel Crash • Windows 7~8. 1 NULL De-reference • Windows 10 RS 4 v 1709, VMware Guest Crash (vm 3 dmp. sys) Win 32 k. sys Information Address Leak Vulnerability • CVE-2017 -11852 • CVE-2017 -? ? ? • CVE-2017 -? ? ? • Credit Pwn 4 fun from BOB(Best of the Best)
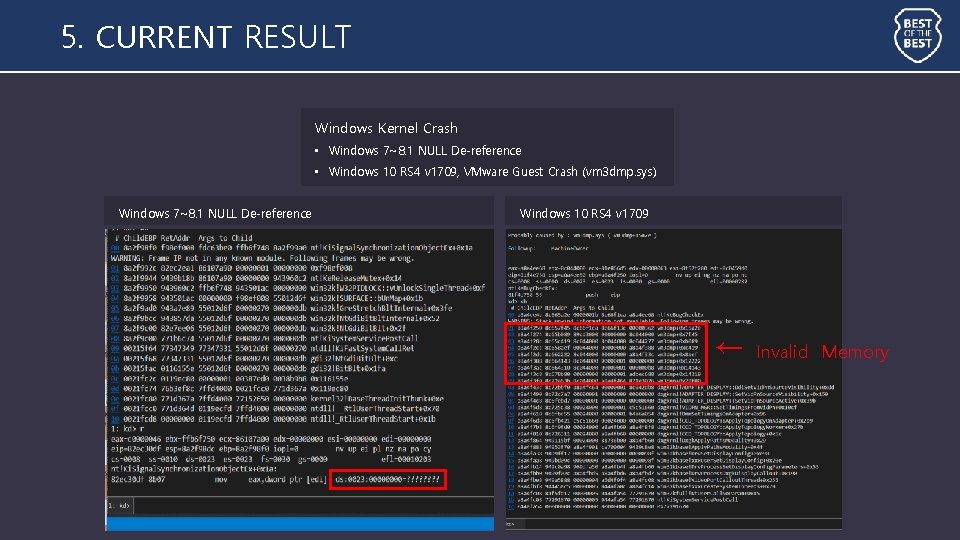
5. CURRENT RESULT Windows Kernel Crash • Windows 7~8. 1 NULL De-reference • Windows 10 RS 4 v 1709, VMware Guest Crash (vm 3 dmp. sys) Windows 7~8. 1 NULL De-reference Windows 10 RS 4 v 1709 ← Invalid Memory
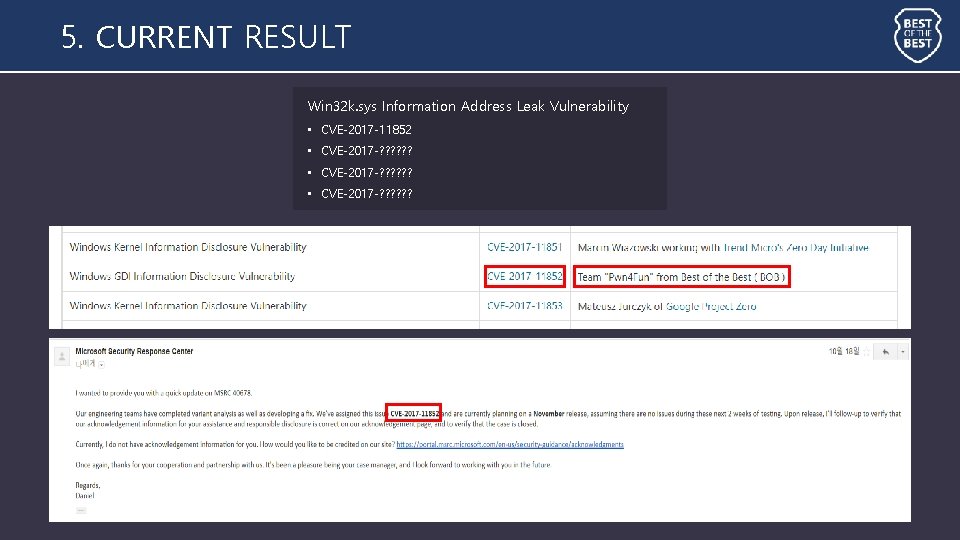
5. CURRENT RESULT Win 32 k. sys Information Address Leak Vulnerability • CVE-2017 -11852 • CVE-2017 -? ? ? • CVE-2017 -? ? ?