Virtualizing Network IO on EndHost OS Takashi taka
- Slides: 48
Virtualizing Network I/O on End-Host OS Takashi “taka” Okumura Department of Computer Science University of Pittsburgh
Who’s taka? . D. h D/P M • A Ph. D. student • Working with Dr. Mosse' • Semantics-aware Control of Medical Network • Virtualization of network I/O on end-host OS
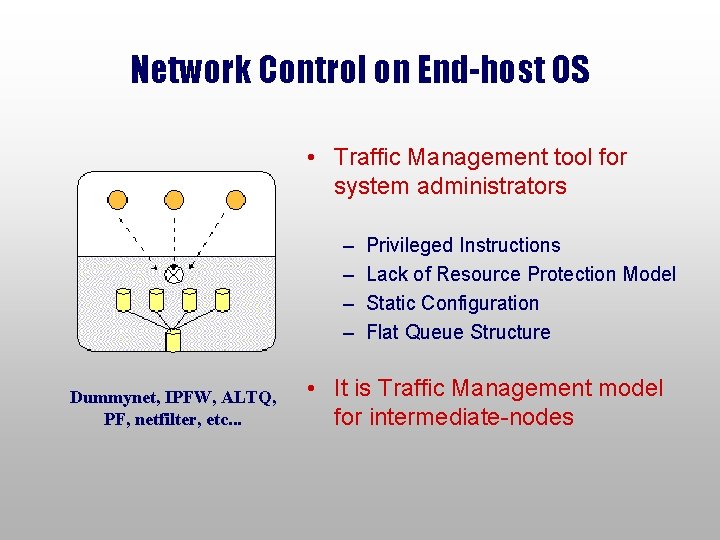
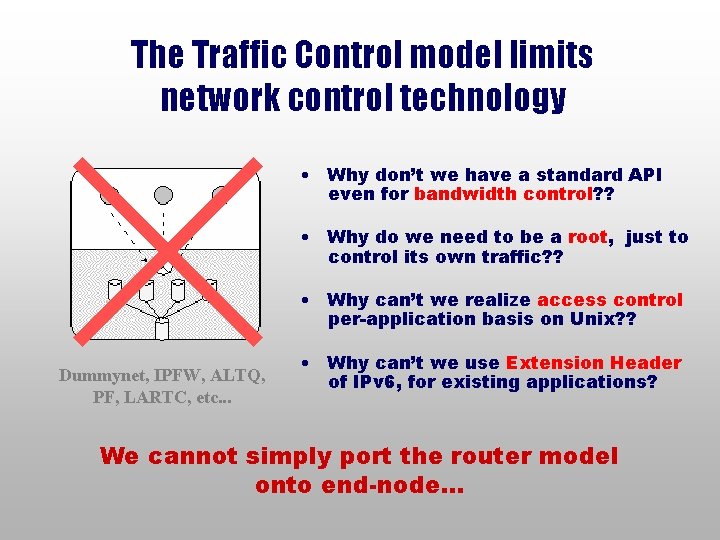
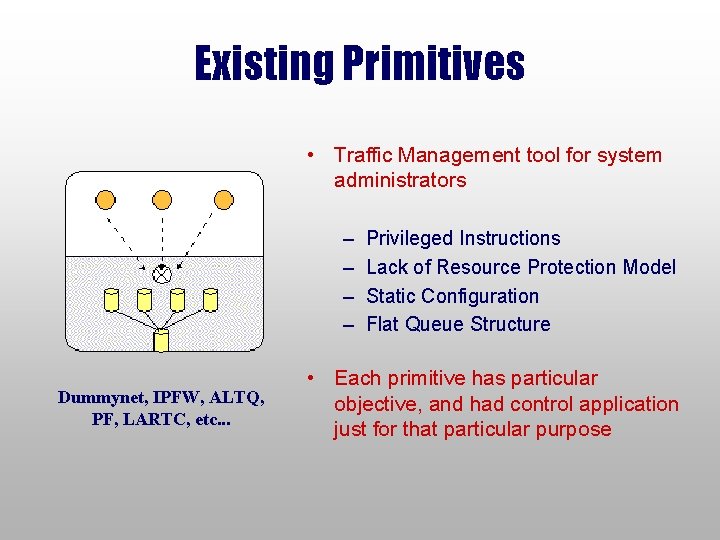
Network Control on End-host OS • Traffic Management tool for system administrators – – Dummynet, IPFW, ALTQ, PF, netfilter, etc. . . Privileged Instructions Lack of Resource Protection Model Static Configuration Flat Queue Structure • It is Traffic Management model for intermediate-nodes
The Traffic Control model limits network control technology • Why don’t we have a standard API even for bandwidth control? ? • Why do we need to be a root, just to control its own traffic? ? • Why can’t we realize access control per-application basis on Unix? ? Dummynet, IPFW, ALTQ, PF, LARTC, etc. . . • Why can’t we use Extension Header of IPv 6, for existing applications? We cannot simply port the router model onto end-node. . .
What can we do ?
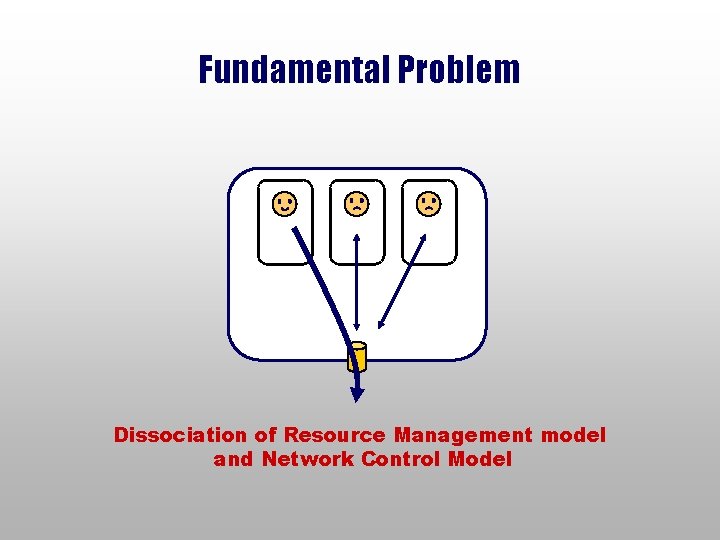
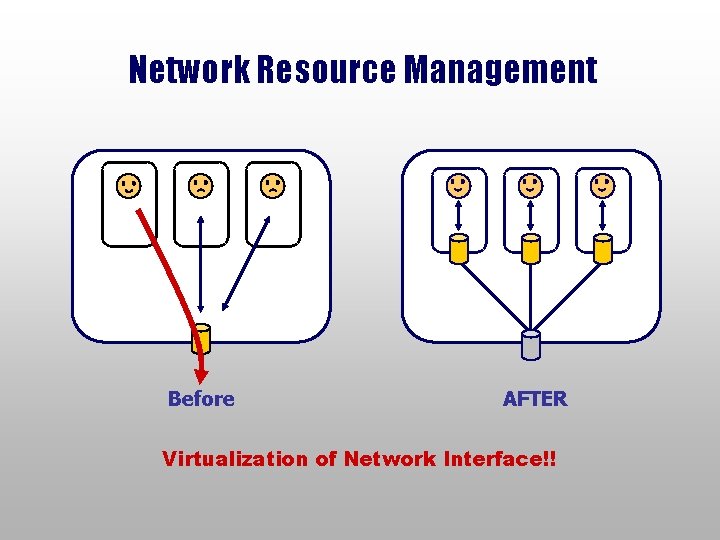
Fundamental Problem Dissociation of Resource Management model and Network Control Model
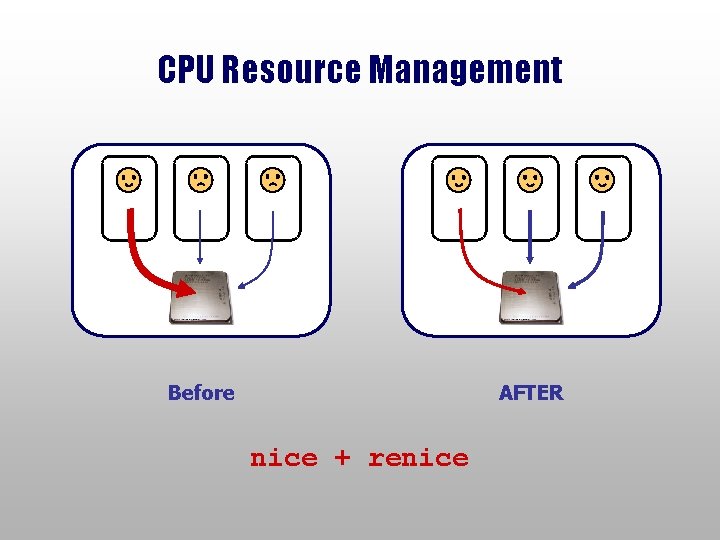
CPU Resource Management Before AFTER nice + renice
Network Resource Management Before AFTER Virtualization of Network Interface!!
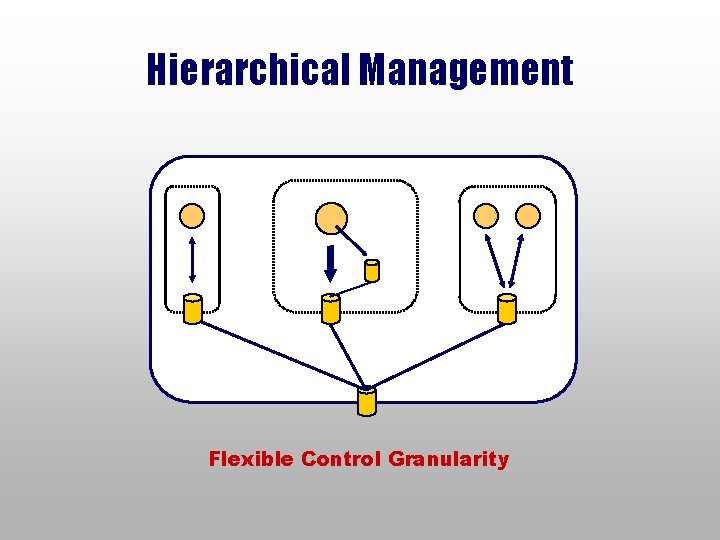
Hierarchical Management Flexible Control Granularity
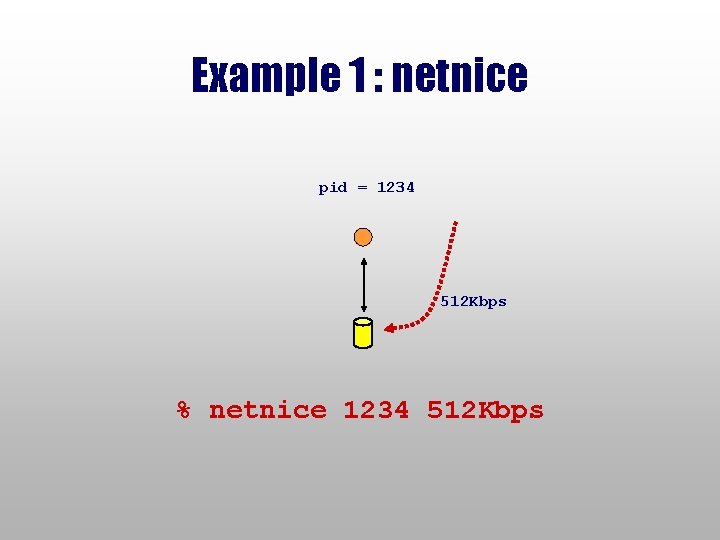
Example 1 : netnice pid = 1234 512 Kbps % netnice 1234 512 Kbps
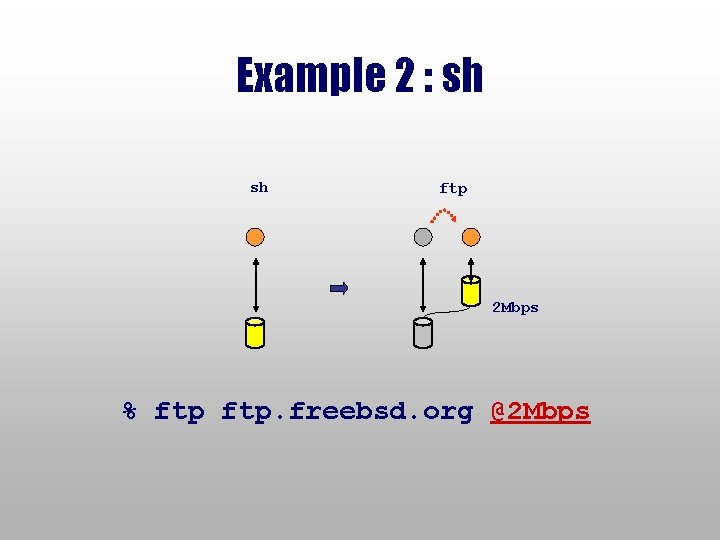
Example 2 : sh sh ftp 2 Mbps % ftp. freebsd. org @2 Mbps
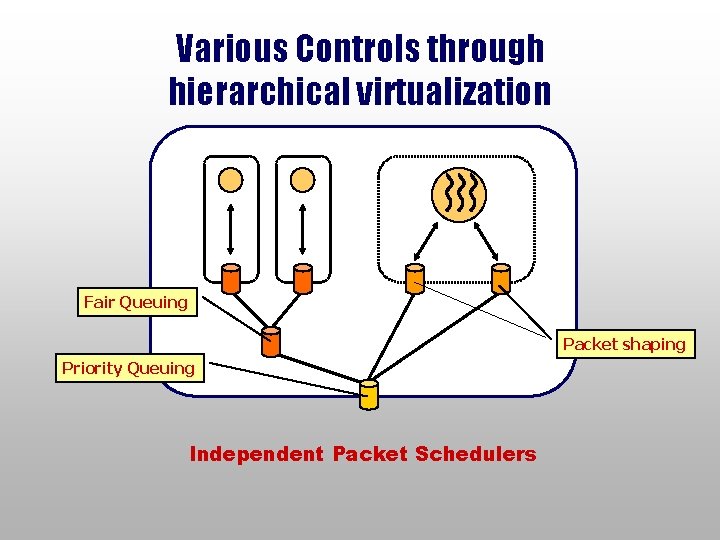
Various Controls through hierarchical virtualization Fair Queuing Packet shaping Priority Queuing Independent Packet Schedulers
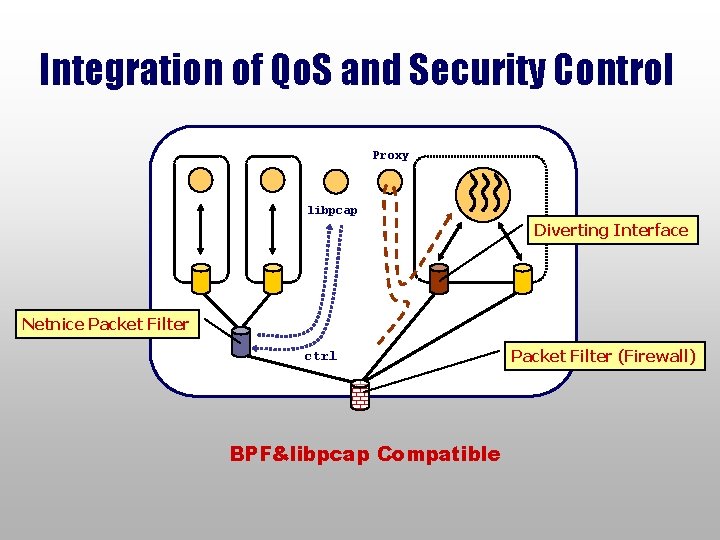
Integration of Qo. S and Security Control Proxy libpcap Diverting Interface Netnice Packet Filter ctrl BPF&libpcap Compatible Packet Filter (Firewall)
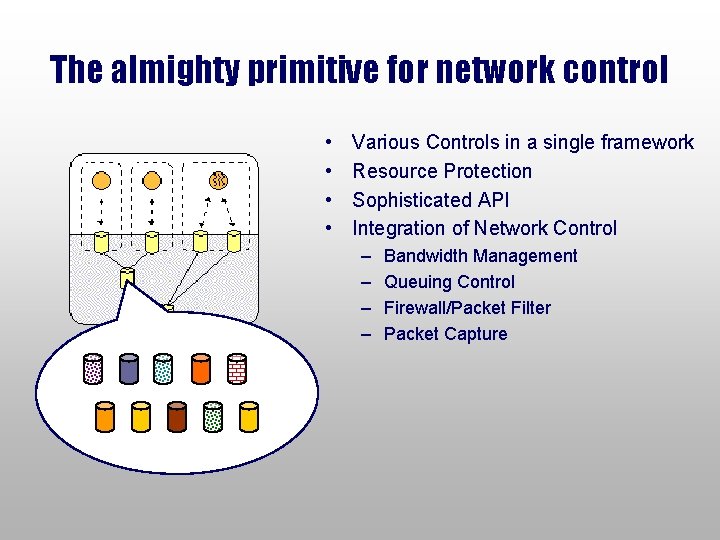
The almighty primitive for network control • • Various Controls in a single framework Resource Protection Sophisticated API Integration of Network Control – – Bandwidth Management Queuing Control Firewall/Packet Filter Packet Capture
Intermission - Project Status -
India Gate, Bombay (Mumbai)
Why did Taka go to India? • Loves Indian Food! • To collaborate with Indian Hackers! Gate Taka
Netnice ORG an Opensource Project • Kernel Development - Porting • Application Development - Porting • (Research Division; discussed later)
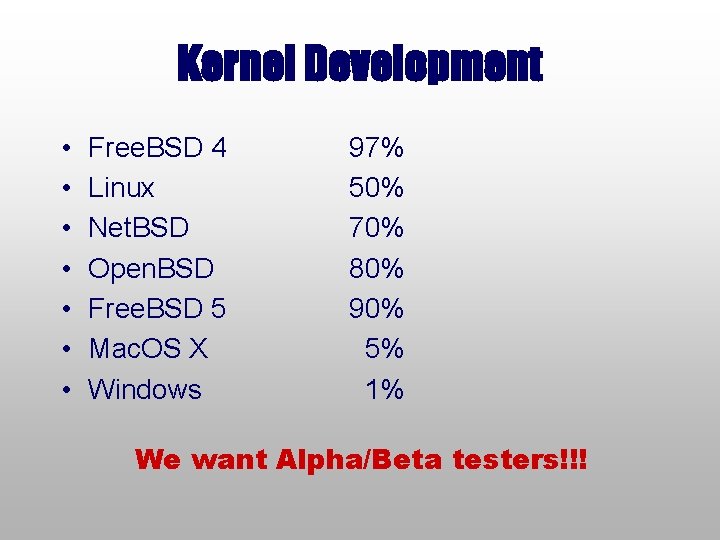
Kernel Development • • Free. BSD 4 Linux Net. BSD Open. BSD Free. BSD 5 Mac. OS X Windows 97% 50% 70% 80% 90% 5% 1% We want Alpha/Beta testers!!!
Applications • • • Firewall Builder Netnice Daemon 3 D-tcpdump Apache module inetd
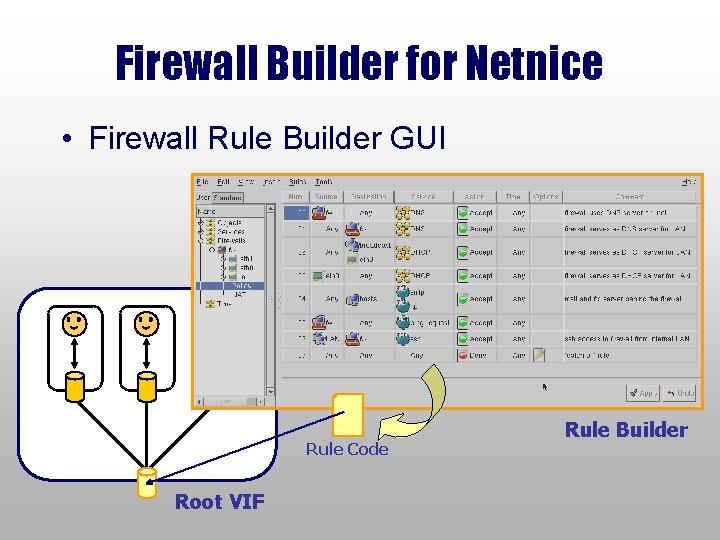
Firewall Builder for Netnice • Firewall Rule Builder GUI Rule Code Root VIF Rule Builder
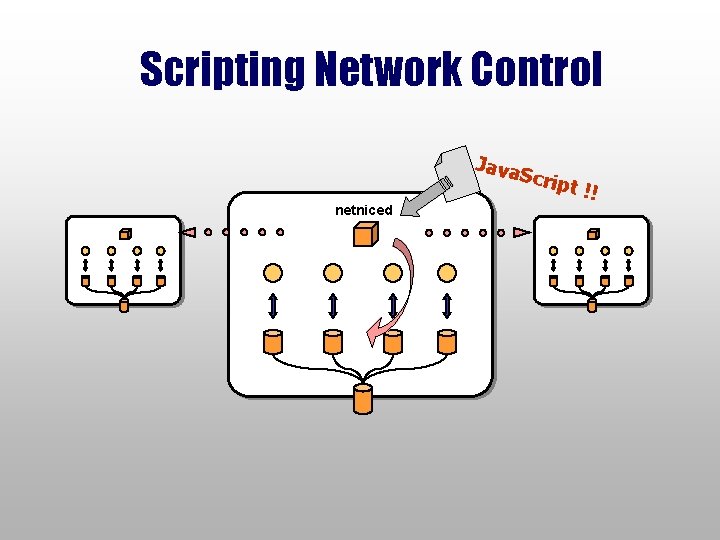
Scripting Network Control Java netniced Scrip t !!
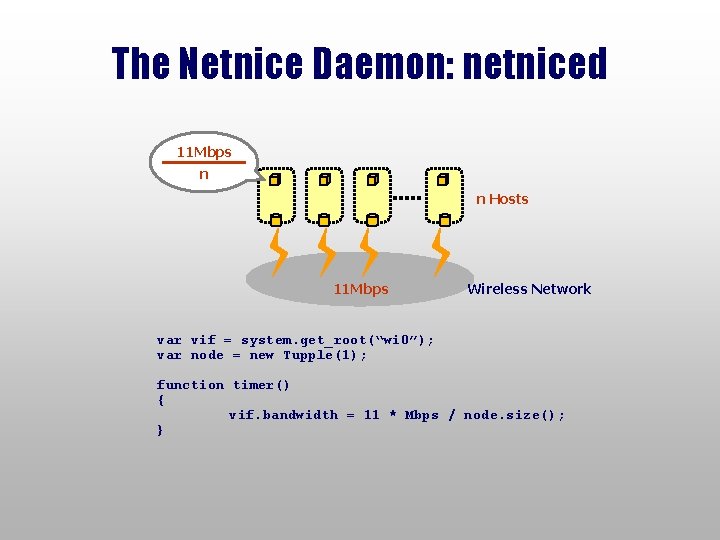
The Netnice Daemon: netniced 11 Mbps n n Hosts 11 Mbps Wireless Network var vif = system. get_root(“wi 0”); var node = new Tupple(1); function timer() { vif. bandwidth = 11 * Mbps / node. size(); }
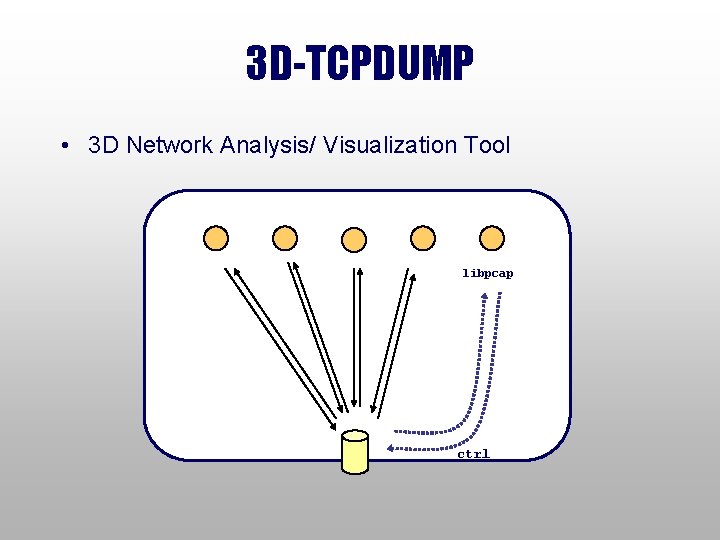
3 D-TCPDUMP • 3 D Network Analysis/ Visualization Tool libpcap ctrl
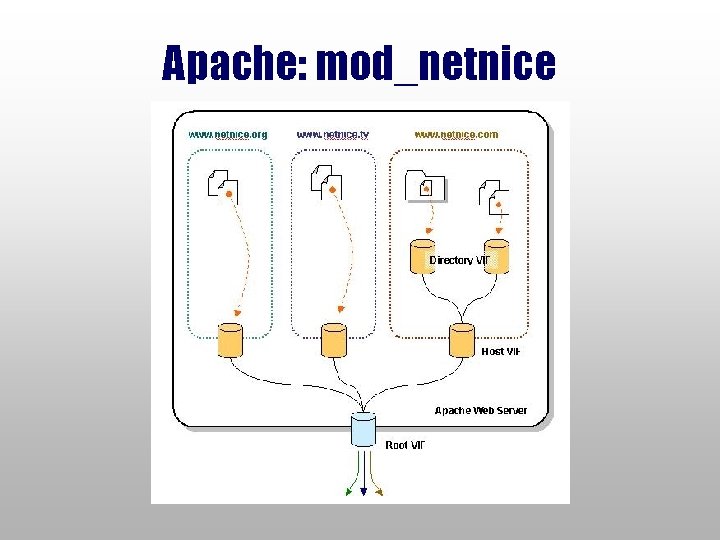
Apache: mod_netnice
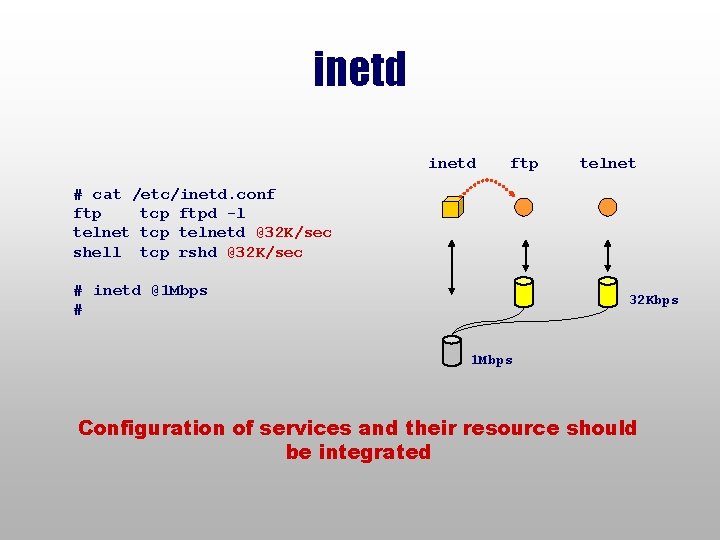
inetd ftp telnet # cat /etc/inetd. conf ftp tcp ftpd -l telnet tcp telnetd @32 K/sec shell tcp rshd @32 K/sec # inetd @1 Mbps # 32 Kbps 1 Mbps Configuration of services and their resource should be integrated
Got bored?
Existing Primitives • Traffic Management tool for system administrators – – Dummynet, IPFW, ALTQ, PF, LARTC, etc. . . Privileged Instructions Lack of Resource Protection Model Static Configuration Flat Queue Structure • Each primitive has particular objective, and had control application just for that particular purpose
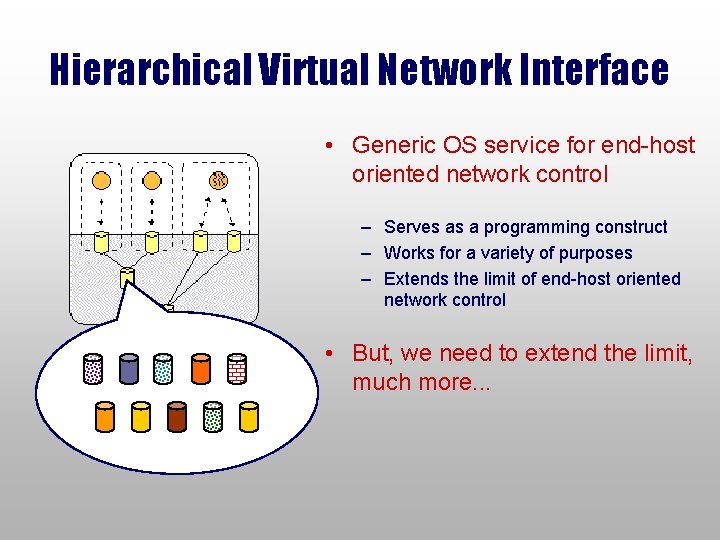
Hierarchical Virtual Network Interface • Generic OS service for end-host oriented network control – Serves as a programming construct – Works for a variety of purposes – Extends the limit of end-host oriented network control • But, we need to extend the limit, much more. . .
Research
TOPICS • • • Architecture Compiler Algorithm Operating System Artificial Intelligence
Architecture Dynamic Extension of Protocol Stack by Virtual Machine technology
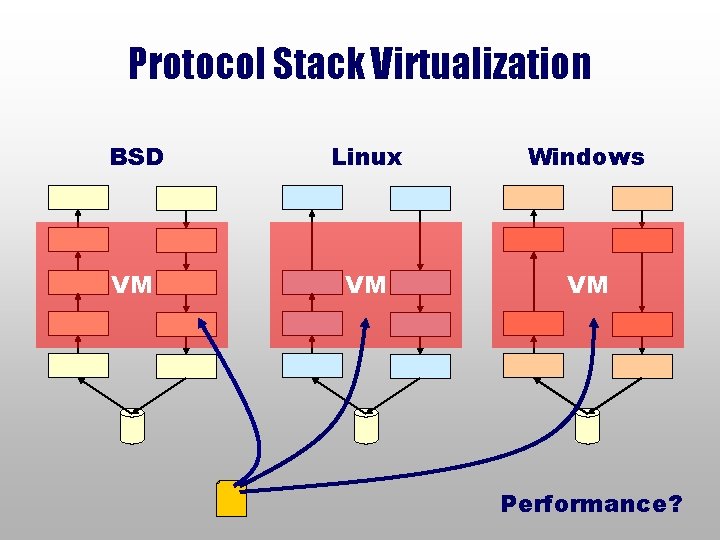
Protocol Stack Virtualization BSD Linux Windows VM VM VM Performance?
Compiler for High-performance Firewall
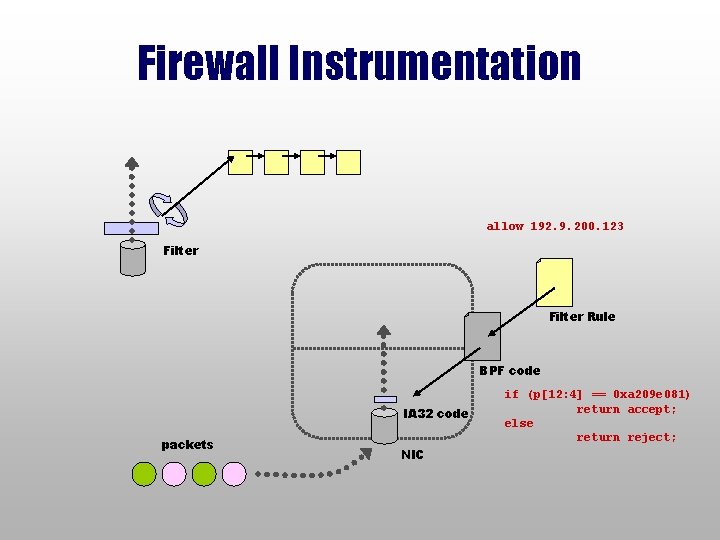
Firewall Instrumentation allow 192. 9. 200. 123 Filter Rule BPF code IA 32 code packets NIC if (p[12: 4] == 0 xa 209 e 081) return accept; else return reject;
Algorithm Distributed Caching and Traffic Control Algorithm for Fermi FS
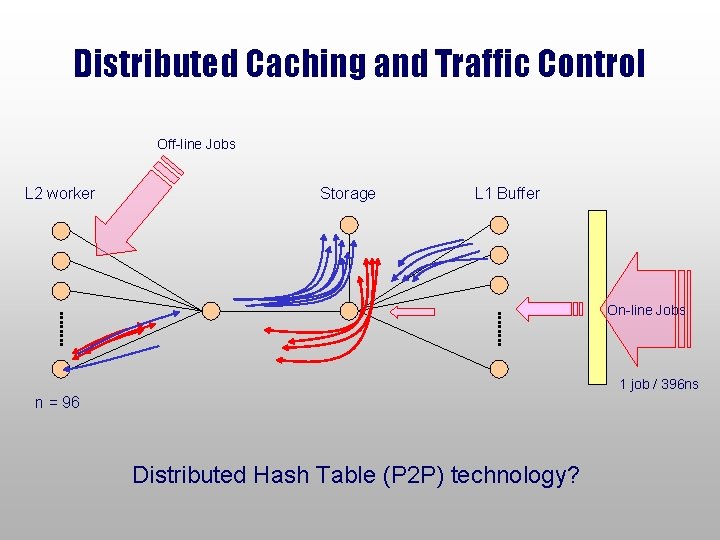
Distributed Caching and Traffic Control Off-line Jobs L 2 worker Storage L 1 Buffer On-line Jobs 1 job / 396 ns n = 96 Distributed Hash Table (P 2 P) technology?
Operating System Coupled Scheduling Mechanism for CPU and Network
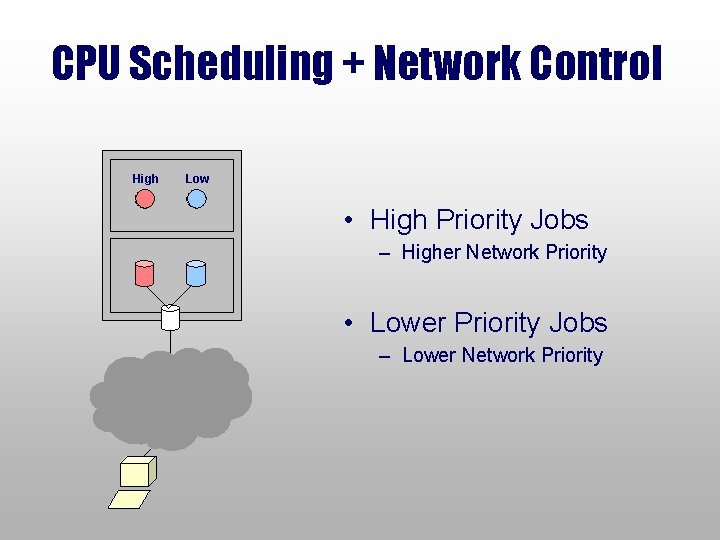
CPU Scheduling + Network Control High Low • High Priority Jobs – Higher Network Priority • Lower Priority Jobs – Lower Network Priority
Artificial Intelligence Traffic Control based on Semantics analysis of on-going communication
Semantics-Aware Medical Network • Needs for better fairness, safety, and security – ex) Resource contention between traffic for. . . • Emergency Case (such as Acute MI) • Common cold
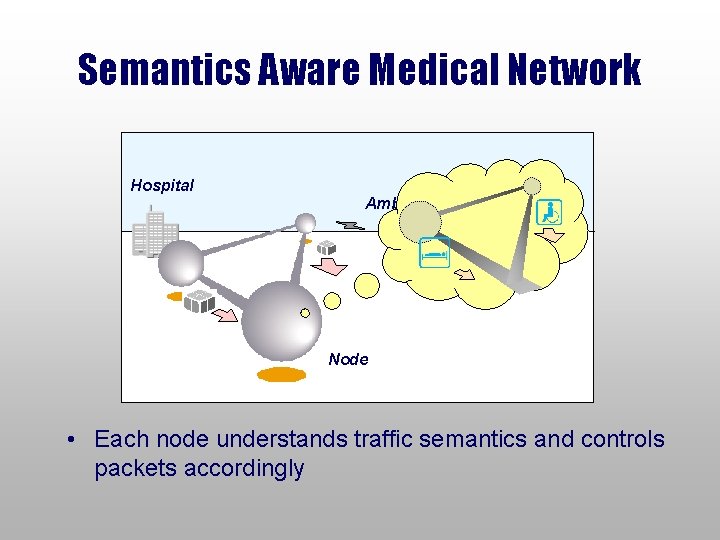
Semantics Aware Medical Network Hospital Ambulance Node • Each node understands traffic semantics and controls packets accordingly
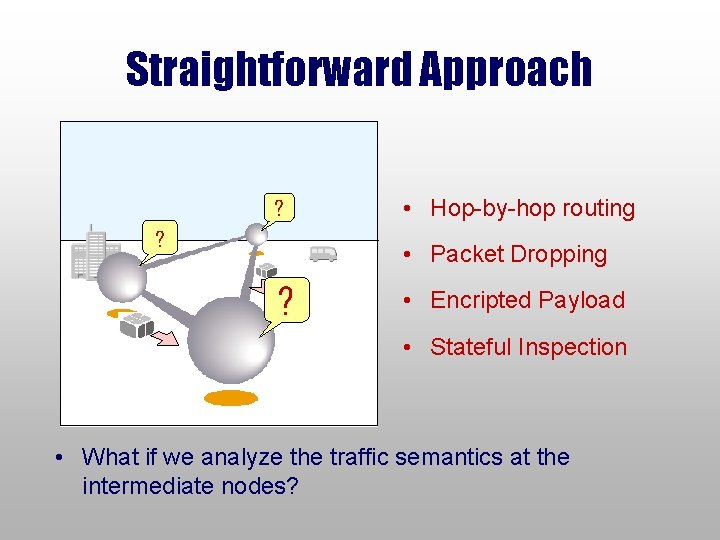
Straightforward Approach ? ? • Hop-by-hop routing • Packet Dropping ? • Encripted Payload • Stateful Inspection • What if we analyze the traffic semantics at the intermediate nodes?
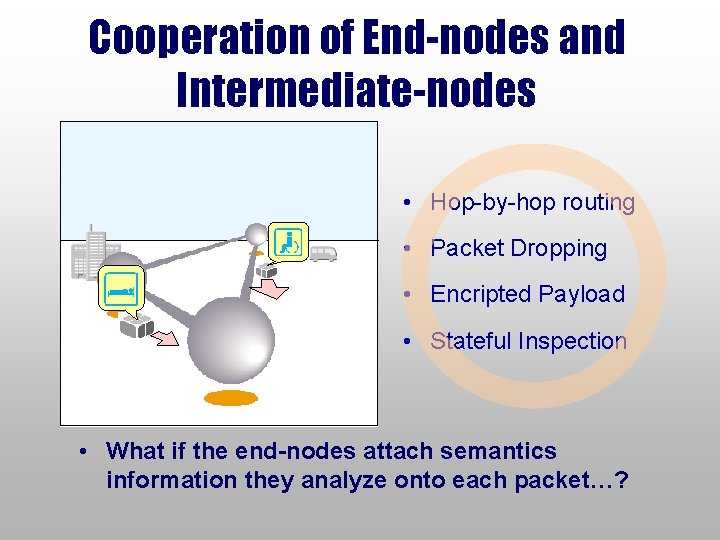
Cooperation of End-nodes and Intermediate-nodes • Hop-by-hop routing • Packet Dropping • Encripted Payload • Stateful Inspection • What if the end-nodes attach semantics information they analyze onto each packet…?
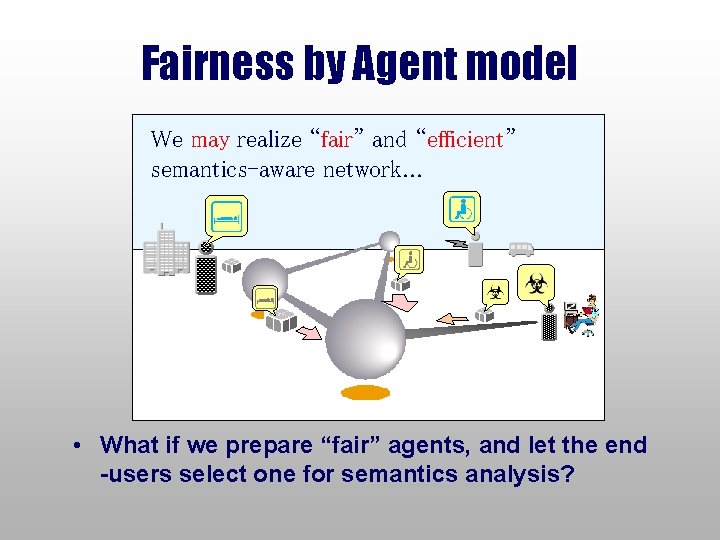
Fairness by Agent model We may realize “fair” and “efficient” semantics-aware network. . . • What if we prepare “fair” agents, and let the end -users select one for semantics analysis?
To realize such a technology, we need an end-node mechanism! which allows analysis of flows at flexible granularity and active control of them just monitored.