
SPB Improvements and Network Analytics for ML Jorge
SPB Improvements and Network Analytics for ML Jorge Arasanz (Jorge. Arasanz@al-enterprise. com)
Network Evolution SDH Ethernet/IP PDH 2 § Ethernet/IP Knowledge is basic § Both CAPEX and OPEX optimized § Modern O&M: Dev. Ops, IEC-61850 § SCADA Transition to Ethernet/IP – Io. T (IEC-104, Modbus) § Open Platforms for low-cost tailored solutions § Protocols Improving: Low Latency, multipath, multicast, etc. § Security: Widely knowledge, MORE RISK: Need to CONTROL and ISOLATE
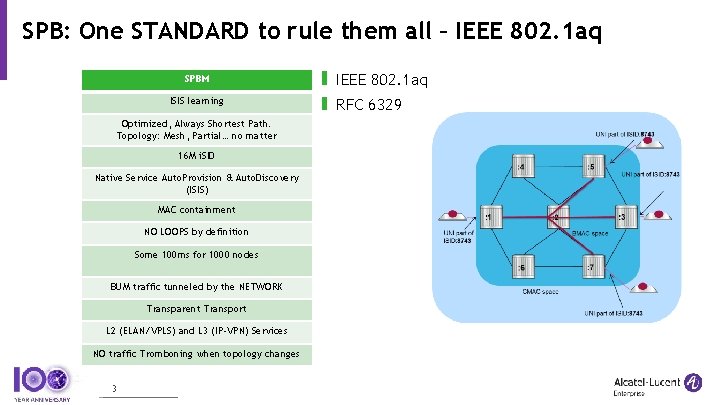
SPB: One STANDARD to rule them all – IEEE 802. 1 aq SPBM ISIS learning Optimized, Always Shortest Path. Topology: Mesh, Partial… no matter 16 M i. SID Native Service Auto. Provision & Auto. Discovery (ISIS) MAC containment NO LOOPS by definition Some 100 ms for 1000 nodes BUM traffic tunneled by the NETWORK Transparent Transport L 2 (ELAN/VPLS) and L 3 (IP-VPN) Services NO traffic Tromboning when topology changes 3 IEEE 802. 1 aq RFC 6329
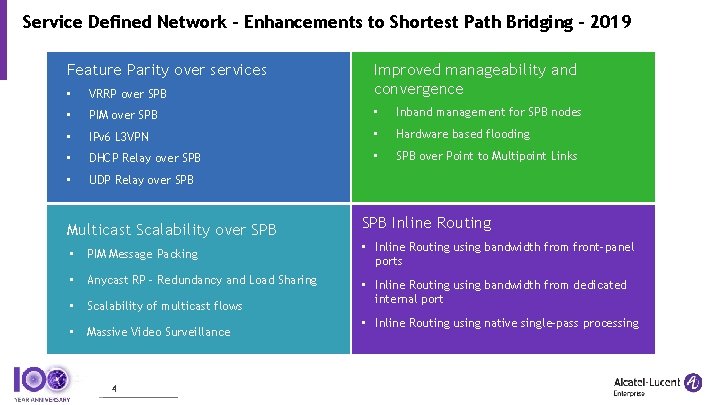
Service Defined Network – Enhancements to Shortest Path Bridging - 2019 • VRRP over SPB Improved manageability and convergence • PIM over SPB • Inband management for SPB nodes • IPv 6 L 3 VPN • Hardware based flooding • DHCP Relay over SPB • SPB over Point to Multipoint Links • UDP Relay over SPB Feature Parity over services Multicast Scalability over SPB • PIM Message Packing • Anycast RP – Redundancy and Load Sharing • Scalability of multicast flows • Massive Video Surveillance 4 SPB Inline Routing • Inline Routing using bandwidth from front-panel ports • Inline Routing using bandwidth from dedicated internal port • Inline Routing using native single-pass processing
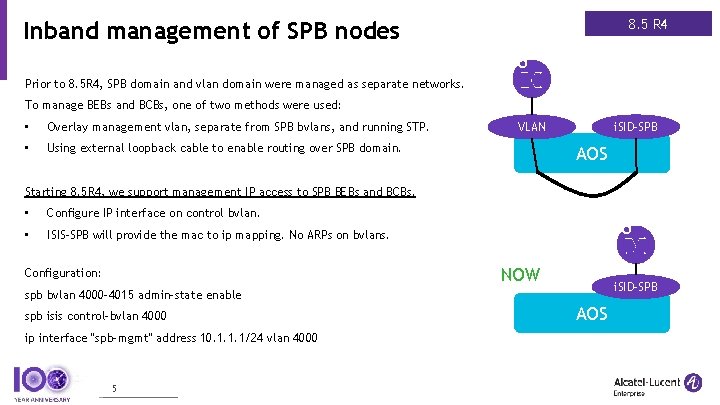
8. 5 R 4 Inband management of SPB nodes Prior to 8. 5 R 4, SPB domain and vlan domain were managed as separate networks. To manage BEBs and BCBs, one of two methods were used: • Overlay management vlan, separate from SPB bvlans, and running STP. • Using external loopback cable to enable routing over SPB domain. VLAN i. SID-SPB AOS Starting 8. 5 R 4, we support management IP access to SPB BEBs and BCBs. • Configure IP interface on control bvlan. • ISIS-SPB will provide the mac to ip mapping. No ARPs on bvlans. NOW Configuration: i. SID-SPB spb bvlan 4000 -4015 admin-state enable spb isis control-bvlan 4000 ip interface "spb-mgmt" address 10. 1. 1. 1/24 vlan 4000 5 AOS

VRRP over SPB 8. 5 R 2 VRRP is now configured on an IP interface, instead of being configured on a vlan, thereby providing a common way for enabling VRRP on both vlans and SPB services. vrf <vrf. Name>] [ip | ipv 6] vrrp <virtual-router-id> interface <ip_if. Name> [vrf <vrf. Name>] show [ip | ipv 6] vrrp [<virtual-router-id> interface <ip_if. Name>] All platforms vrrp i. SID-SPB AOS 6 i. SID-SPB AOS
SPB fast convergence: HW LSP forwarding 8. 5 R 4, Mar 2019 § Improve fast convergence of an SPB network in response to a topology update event due to a link failure event. § The SPB ISIS LSP Flooding does interoperate with earlier AOS and also other vendor SPB nodes that may not support this feature. § Instantly forward and trap links failures to all nodes in the network instead of waiting for each node to process the update and then forward it. § This operations expedites the SPF calculation in response to the topology change § Using this method, convergence is achieve in <100 ms convergence • spb isis rapid-lsp-converge { [admin-state <enable> | <disable>] | [isid <isid_num>]} • Defaults: admin-state = enable ; • isid_num = 16776961 or 255. 1 (0 x. FFFF 01) is the reserved default on all AOS platform Range 2560 xffffff 7
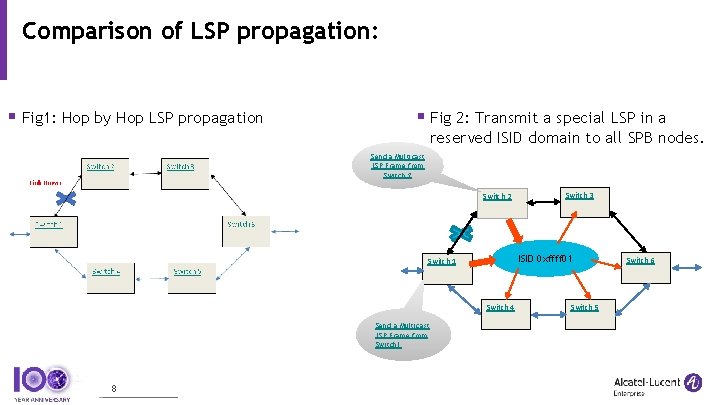
Comparison of LSP propagation: § Fig 1: Hop by Hop LSP propagation § Fig 2: Transmit a special LSP in a reserved ISID domain to all SPB nodes. Send a Multicast LSP Frame from Switch 2 ISID 0 xffff 01 Switch 4 Send a Multicast LSP Frame from Switch 1 8 Switch 3 Switch 5 Switch 6
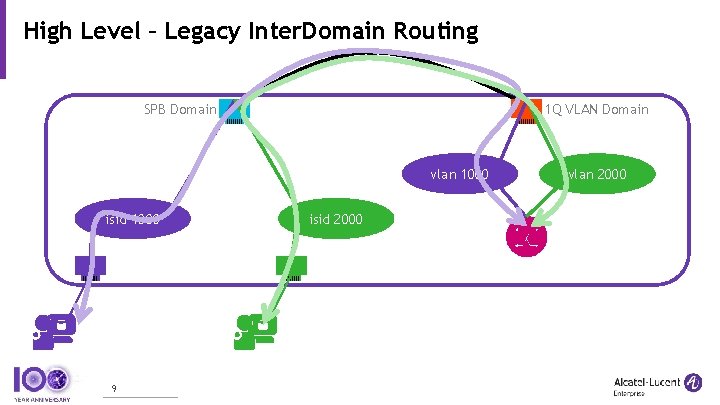
High Level – Legacy Inter. Domain Routing SPB Domain 1 Q VLAN Domain vlan 1000 isid 1000 9 isid 2000 vlan 2000
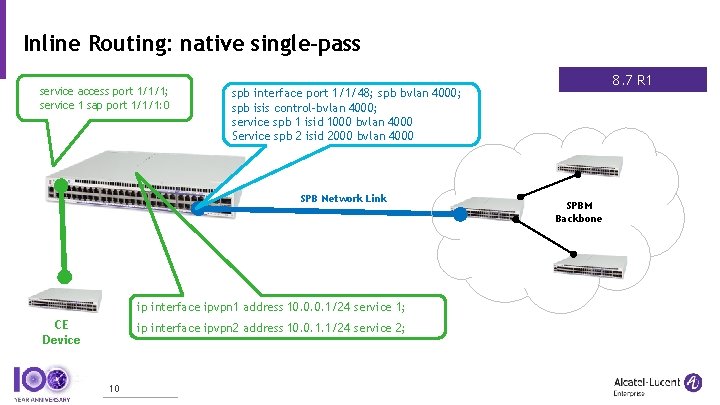
Inline Routing: native single-pass service access port 1/1/1; service 1 sap port 1/1/1: 0 SPB Network Link ip interface ipvpn 1 address 10. 0. 0. 1/24 service 1; CE Device ip interface ipvpn 2 address 10. 0. 1. 1/24 service 2; 10 8. 7 R 1 spb interface port 1/1/48; spb bvlan 4000; spb isis control-bvlan 4000; service spb 1 isid 1000 bvlan 4000 Service spb 2 isid 2000 bvlan 4000 SPBM Backbone
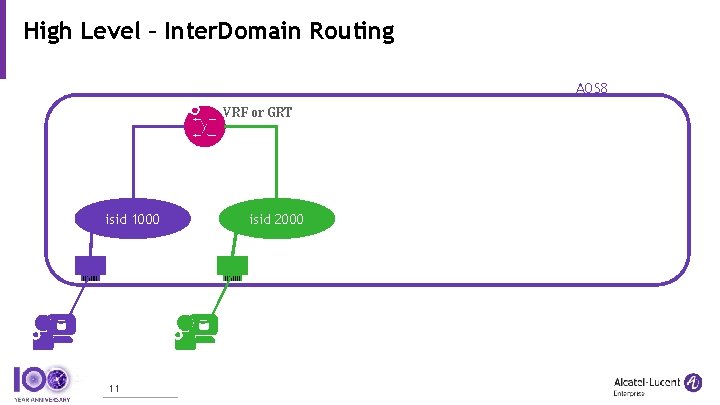
High Level – Inter. Domain Routing AOS 8 VRF or GRT isid 1000 11 isid 2000
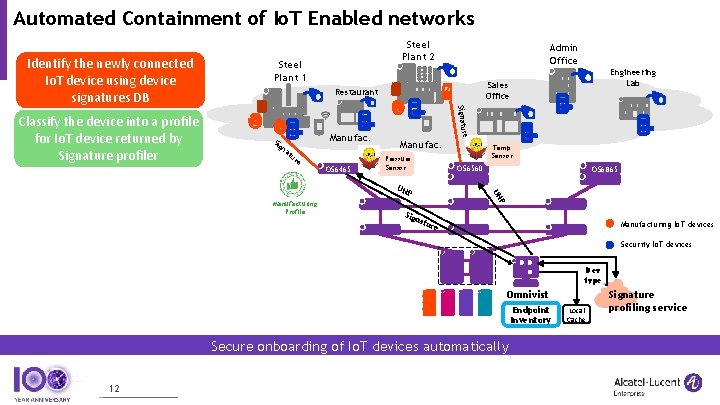
Automated Containment of Io. T Enabled networks Restaurant Sig Manufac. na tu re OS 6465 Manufac. Pressure Sensor Temp Sensor OS 6560 UN OS 6865 P UN P Manufacturing Profile Engineering Lab Sales Office re Classify the device into a profile for Io. T device returned by Signature profiler Steel Plant 1 Admin Office Signatu Identify the newly connected Io. T device using device signatures DB Steel Plant 2 Sig nat ure Manufacturing Io. T devices Security Io. T devices Dev type Omnivist a. Endpoint Inventory Secure onboarding of Io. T devices automatically 12 Local Cache Signature profiling service
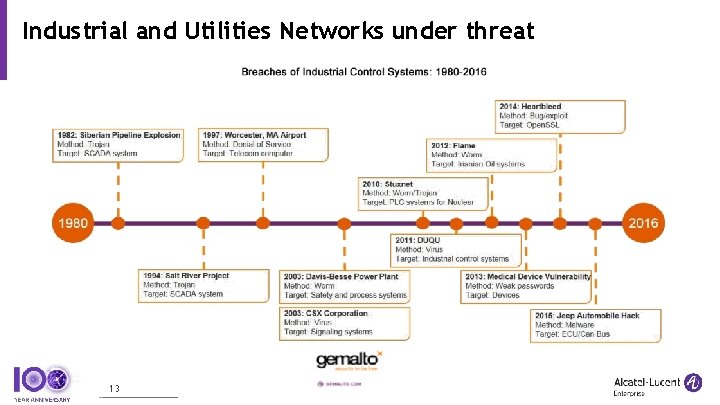
Industrial and Utilities Networks under threat 13
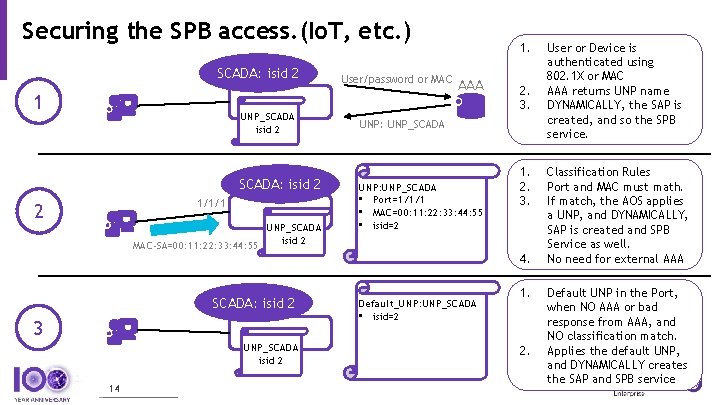
Securing the SPB access. (Io. T, etc. ) SCADA: isid 2 1 UNP_SCADA isid 2 SCADA: isid 2 1/1/1 2 UNP_SCADA isid 2 MAC-SA=00: 11: 22: 33: 44: 55 SCADA: isid 2 3 UNP_SCADA isid 2 14 User/password or MAC 1. AAA 2. 3. UNP: UNP_SCADA • Port=1/1/1 • MAC=00: 11: 22: 33: 44: 55 • isid=2 1. 2. 3. 4. Default_UNP: UNP_SCADA • isid=2 1. 2. User or Device is authenticated using 802. 1 X or MAC AAA returns UNP name DYNAMICALLY, the SAP is created, and so the SPB service. Classification Rules Port and MAC must math. If match, the AOS applies a UNP, and DYNAMICALLY, SAP is created and SPB Service as well. No need for external AAA Default UNP in the Port, when NO AAA or bad response from AAA, and NO classification match. Applies the default UNP, and DYNAMICALLY creates the SAP and SPB service
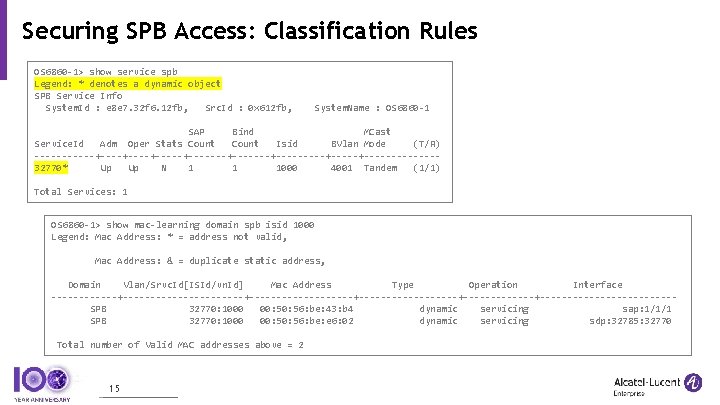
Securing SPB Access: Classification Rules OS 6860 -1> show service spb Legend: * denotes a dynamic object SPB Service Info System. Id : e 8 e 7. 32 f 6. 12 fb, Src. Id : 0 x 612 fb, System. Name : OS 6860 -1 SAP Bind MCast Service. Id Adm Oper Stats Count Isid BVlan Mode (T/R) ------+----+-------+---------+-------32770* Up Up N 1 1 1000 4001 Tandem (1/1) Total Services: 1 OS 6860 -1> show mac-learning domain spb isid 1000 Legend: Mac Address: * = address not valid, Mac Address: & = duplicate static address, Domain Vlan/Srvc. Id[ISId/vn. Id] Mac Address Type Operation Interface ------------+-------------------+-------------+------------SPB 32770: 1000 00: 56: be: 43: b 4 dynamic servicing sap: 1/1/1 SPB 32770: 1000 00: 56: be: e 6: 02 dynamic servicing sdp: 32785: 32770 Total number of Valid MAC addresses above = 2 15
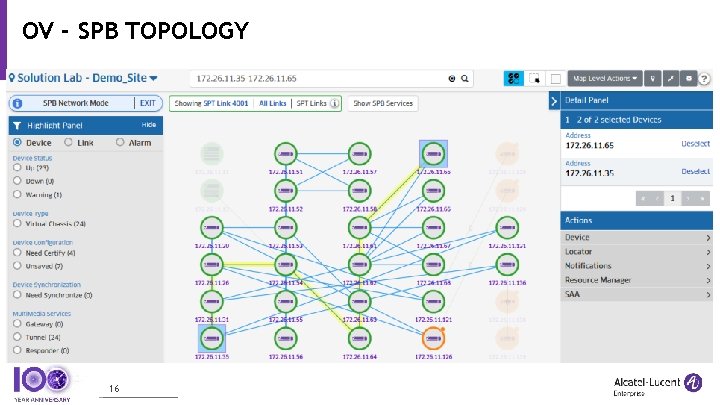
OV - SPB TOPOLOGY 16
Analytics for ML
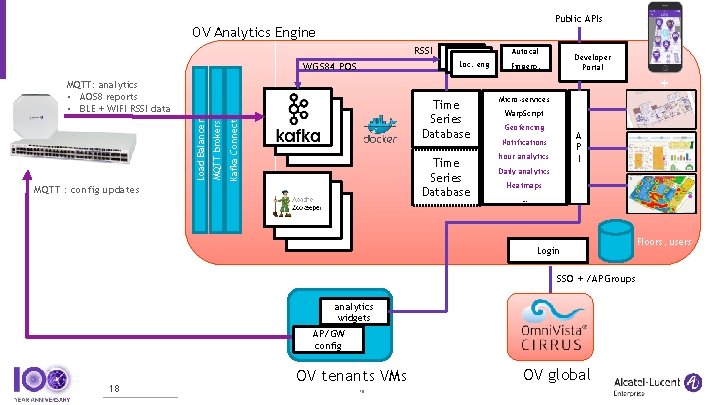
Public APIs OV Analytics Engine RSSI Autocal Loc. eng WGS 84 POS MQTT: analytics • AOS 8 reports • BLE + WIFI RSSI data Developer Portal Fingerp. + Kafka Connect MQTT brokers Load Balancer Architecture Time Series Database MQTT : config updates Micro-services UI: map & positions Warp. Script Geofencing A P I Notifications hour analytics Daily analytics Heatmaps UI: heatmaps … Login SSO + /APGroups analytics widgets AP/GW config 18 OV tenants VMs 18 UI: analytics OV global Floors, users
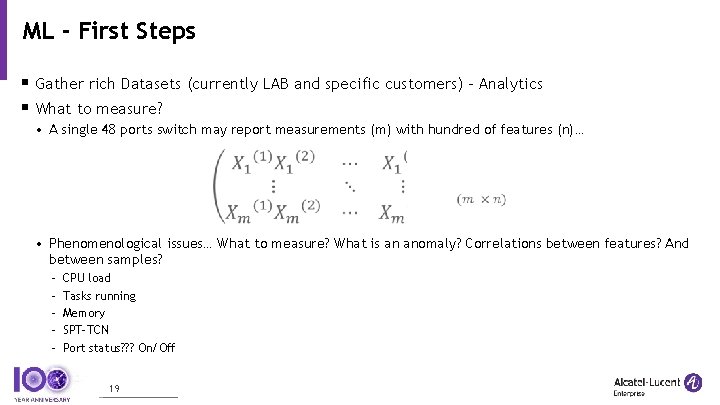
ML - First Steps § Gather rich Datasets (currently LAB and specific customers) - Analytics § What to measure? • A single 48 ports switch may report measurements (m) with hundred of features (n)… • Phenomenological issues… What to measure? What is an anomaly? Correlations between features? And between samples? CPU load Tasks running Memory SPT-TCN Port status? ? ? On/Off 19
Anomaly Detection § Traditional approach vs ML approach § ML approaches can be easier and faster, specially with large (m x n), although providing a fair accuracy. § Supervised vs Unsupervised learning Difficult or near impossible to label measurements. Unsupervised learning could be more suited for MLaa. S (each customer’s network will be different) § Trying: Multivariable Normal Distribution K-mean clustering STL decomposition (Trend, Seasonality and Residual) … Neural Networks (MLP) under analysis. § Current ML mantra: “The key is the Dataset”. 20
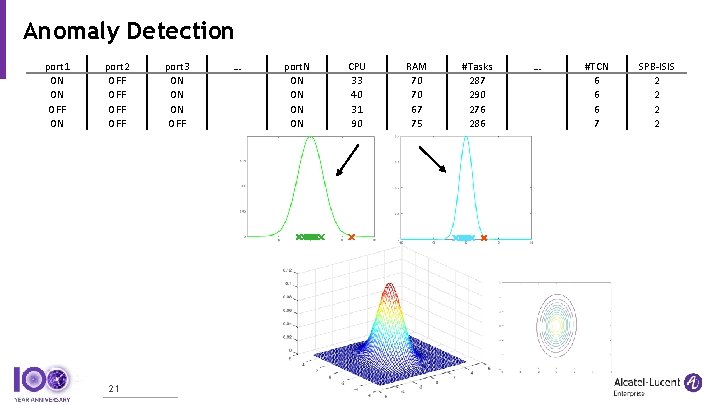
Anomaly Detection port 1 ON ON OFF ON port 2 OFF OFF 21 port 3 ON ON ON OFF … port. N ON ON CPU 33 40 31 90 RAM 70 70 67 75 #Tasks 287 290 276 286 … #TCN 6 6 6 7 SPB-ISIS 2 2
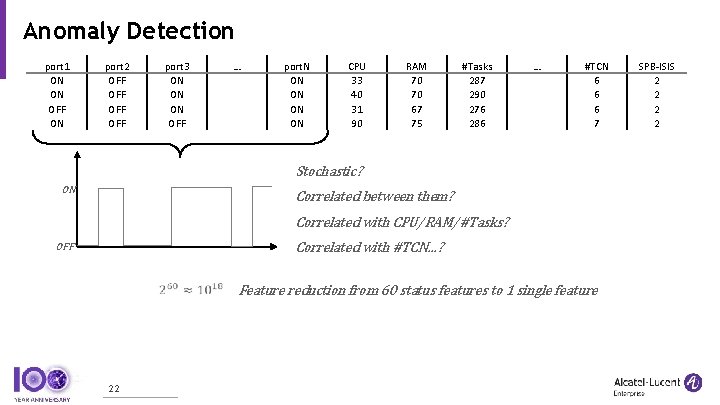
Anomaly Detection port 1 ON ON OFF ON port 2 OFF OFF port 3 ON ON ON OFF … port. N ON ON CPU 33 40 31 90 RAM 70 70 67 75 #Tasks 287 290 276 286 … #TCN 6 6 6 7 Stochastic? ON Correlated between them? Correlated with CPU/RAM/#Tasks? Correlated with #TCN…? OFF 22 Feature reduction from 60 status features to 1 single feature SPB-ISIS 2 2
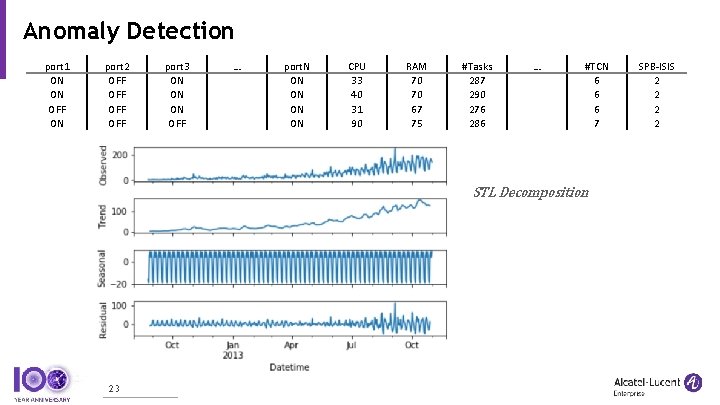
Anomaly Detection port 1 ON ON OFF ON port 2 OFF OFF port 3 ON ON ON OFF … port. N ON ON CPU 33 40 31 90 RAM 70 70 67 75 #Tasks 287 290 276 286 … #TCN 6 6 6 7 STL Decomposition 23 SPB-ISIS 2 2
Summary § Managing ML in Time Series for Anomaly Detection in Networks is a work in progress. § In our initial work, GOOD DATASET seems to be more important than the algorithm (still pending NN) – Very few features used. § Out aim is NOT ONLY detect Anomalies, but be able to “rewind” and see the “events” that lead to the Anomaly. 24
MUCHAS GRACIAS www. al-enterprise. com Y síguenos en: Twitter. com/ALUEnterprise Facebook. com/ALUEnterprise Youtube. com/user/enterprise. ALU Linkedin. com/company/alcatellucententerprise Slideshare. net/Alcatel-Lucent_Enterprise 25
- Slides: 25