N REPORTER Integrated Management of Security incident and
- Slides: 48
N REPORTER Integrated Management of Security incident and Network System Solutions 20130816
? ? ? Do you really secure the protection after purchasing the equipments of Network Security? è Protection from IPS/IDP/UTM/NGFW/WAF. è How to make sure the effect of protection of Network Security? è Potential inner threatens are not radically eliminated. è Blind spot of Network Security Equipments -legal behavior with wrong executor. è Who is playing tricks inside the IP dynamic allocated IP environment.
? ? ? What corporations need when facing threatens of Security Incident? è Trojans, worms, virus and spy software. è websites, fishing websites. è Various html injection attack. è Threatens from 3 G mobile internet.
An analyzable report system is necessary of your Network Security!
? ? ? What is LOG? Why is there LOG Management? All equipments in network environment have LOG è LOG will record the time and events between users. è Network Security Equipment IPS, firewall will record the activities of a certain IP with permit / block. è Router will record the traffic utilization of a certain IP. è Server will record works executed by a certain user from a certain IP. The purpose of LOG management is to returning the original condition back when incident occurred!
! !! Blind spots of LOG Management è Numerous kinds of equipments. Every kind of complicated LOG should be managed by professionals. è How to get the real problem when facing a great huge of LOG? è How to store and inquire efficiently? è How to conform the laws and regulations?
! !! Impacts on corporations from the new version of Personal Information Protection Act!! è The new version of Personal Information Protection Act applies to all the corporations and individuals. è The maximum indemnity can be up to 2 hundred million dollars for the loss of a single event. è When facing the accusation, corporation has to prove for being unintentional and unimpeachable.
! !! LOG management is no more just for audit but for reducing the loss of company!! è Centralized control management of all LOGs. è LOG Normalization → standardized format and inquiring interface. è Ability of long-term preservation and to quickly examining history records. è Ability for real-time alerts → 24 hours non-interruptible protection. è Ability to ensure the integrity of LOG.
If you are looking for. . . ►Syslog record – Storing / Audit / Inquiry equipments ►Flow (Netflow / s. Flow) - Analysis system ►Incidents correlation and risk management platform ►Immediately trend analysis for abnormalities ►Chinese reports generate and deliver regularly N-Reporter integrates all the above functions into one machine !
Syslog record Storing / Audit / Inquiring equipments Syslog Data storing / inquiry function è Simple installation with best performance under Appliance structure. è Integrated analysis for all network equipments. è The best assistant audit tool to Personal Information Protection Act.
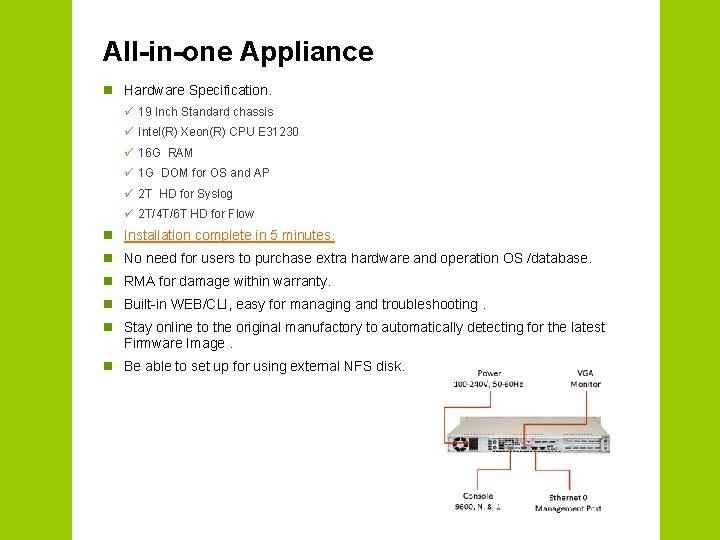
All-in-one Appliance n Hardware Specification. ü 19 Inch Standard chassis ü Intel(R) Xeon(R) CPU E 31230 ü 16 G RAM ü 1 G DOM for OS and AP ü 2 T HD for Syslog ü 2 T/4 T/6 T HD for Flow n Installation complete in 5 minutes. n No need for users to purchase extra hardware and operation OS /database. n RMA for damage within warranty. n Built-in WEB/CLI, easy for managing and troubleshooting. n Stay online to the original manufactory to automatically detecting for the latest Firmware Image. n Be able to set up for using external NFS disk.
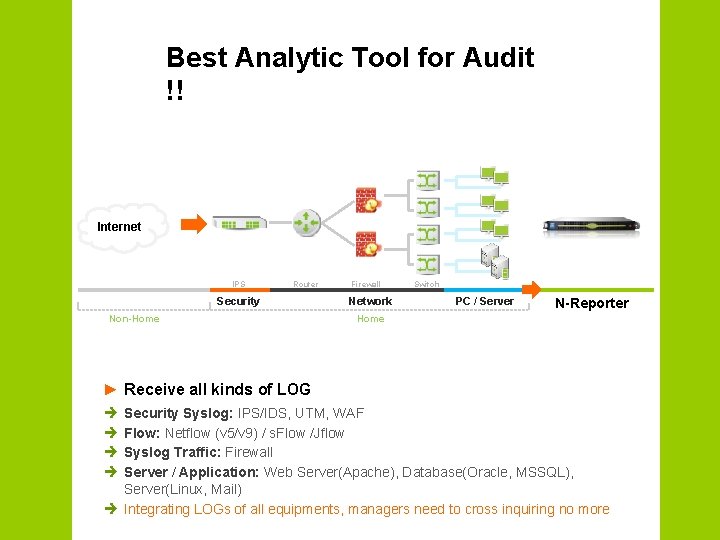
Best Analytic Tool for Audit !! Internet IPS Router Security Non-Home Firewall Network Switch PC / Server N-Reporter Home ► Receive all kinds of LOG è è Security Syslog: IPS/IDS, UTM, WAF Flow: Netflow (v 5/v 9) / s. Flow /Jflow Syslog Traffic: Firewall Server / Application: Web Server(Apache), Database(Oracle, MSSQL), Server(Linux, Mail) è Integrating LOGs of all equipments, managers need to cross inquiring no more
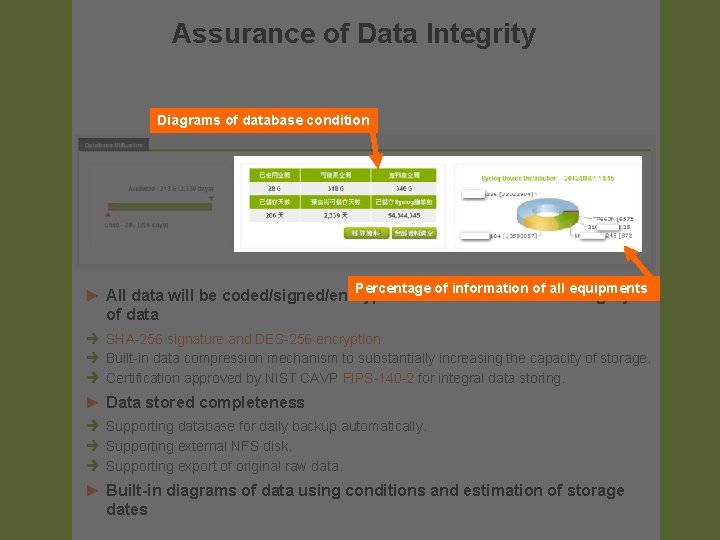
Assurance of Data Integrity Diagrams of database condition Percentage of information of all equipments ► All data will be coded/signed/encrypted stored to ensure the integrity of data è SHA-256 signature and DES-256 encryption. è Built-in data compression mechanism to substantially increasing the capacity of storage. è Certification approved by NIST CAVP FIPS-140 -2 for integral data storing. ► Data stored completeness è Supporting database for daily backup automatically. è Supporting external NFS disk. è Supporting export of original raw data. ► Built-in diagrams of data using conditions and estimation of storage dates
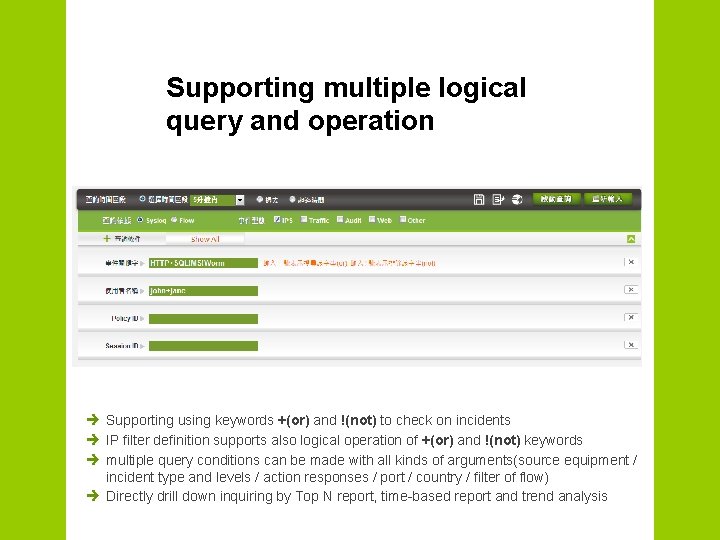
Supporting multiple logical query and operation è Supporting using keywords +(or) and !(not) to check on incidents è IP filter definition supports also logical operation of +(or) and !(not) keywords è multiple query conditions can be made with all kinds of arguments(source equipment / incident type and levels / action responses / port / country / filter of flow) è Directly drill down inquiring by Top N report, time-based report and trend analysis
Analysis Function of Flow / Traffic Flow Analysis Function è Flow analysis and Top N ranking can carry out the comparison of usage between groups. è Flow chart drawn by Flow or Traffic data could support longterm monitoring and provide. è warning when over the threshold.
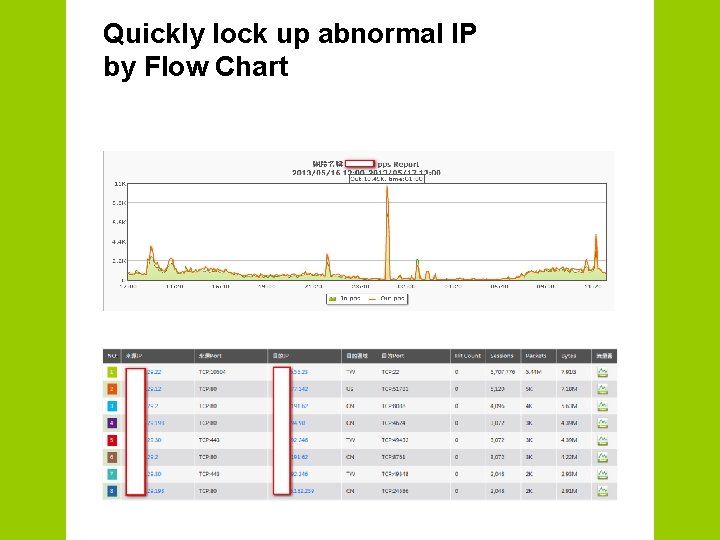
Quickly lock up abnormal IP by Flow Chart
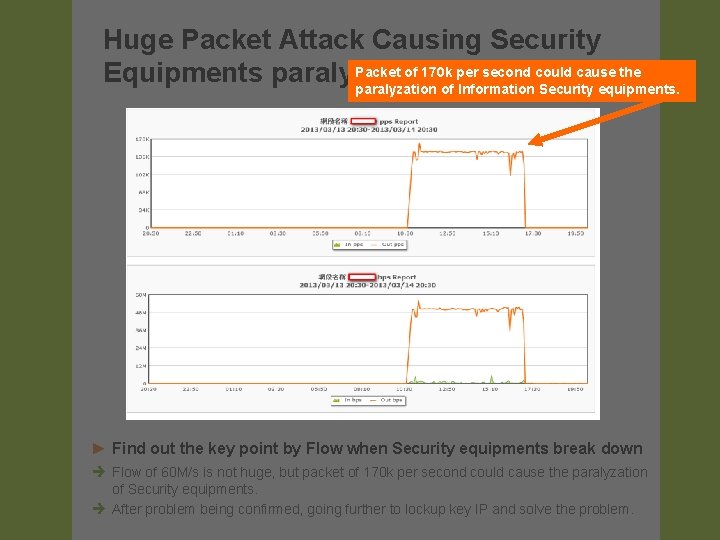
Huge Packet Attack Causing Security Packet of 170 k per second could cause the Equipments paralyzed paralyzation of Information Security equipments. ► Find out the key point by Flow when Security equipments break down è Flow of 60 M/s is not huge, but packet of 170 k per second could cause the paralyzation of Security equipments. è After problem being confirmed, going further to lockup key IP and solve the problem.
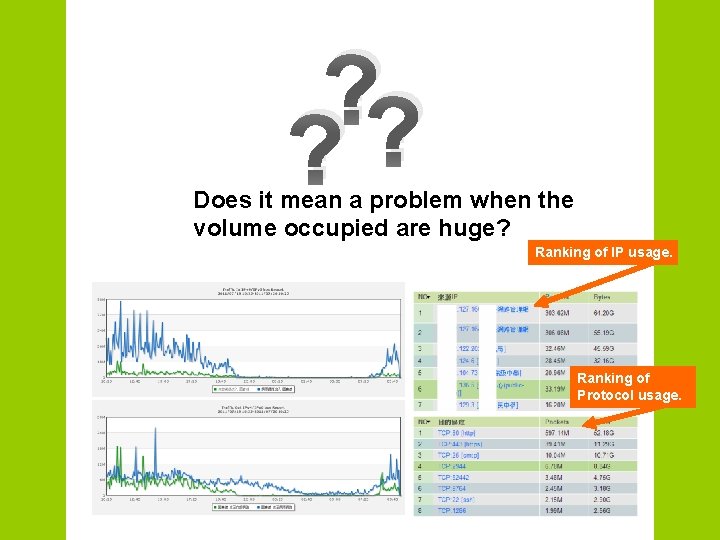
? ? ? Does it mean a problem when the volume occupied are huge? Ranking of IP usage. Ranking of Protocol usage.
Function of Flow Reports ► Condition of Network Flow Usage è List of usage condition of bandwidth in network environment. è Draw out the flow chart with in / out / total traffic of certain IP or certain session. è Draw out the traffic line chart of certain Application. ( such as Web or Mail) è Draw out the flow chart of certain disturbing activities. (such as Bit Torrent or PPStream) or attacks. ( SQL Injection or Malicious Program) è Draw out the flow chart of Critical / Major Information Security Problem cause by network environment. ► Top N Flow Ranking è Listing bandwidth using ranking of IP or Application. è Listing flow usage ranking of certain sessions. (such as comparison between server farm or departments) è Listing Security event ranking cause by IP or session.
Incidents Correlation and Risk Management Platform Incidents Correlation Analysis Function Integrating data of Flow and Security Events completely Performing complete correlation from L 3/L 4 to L 7
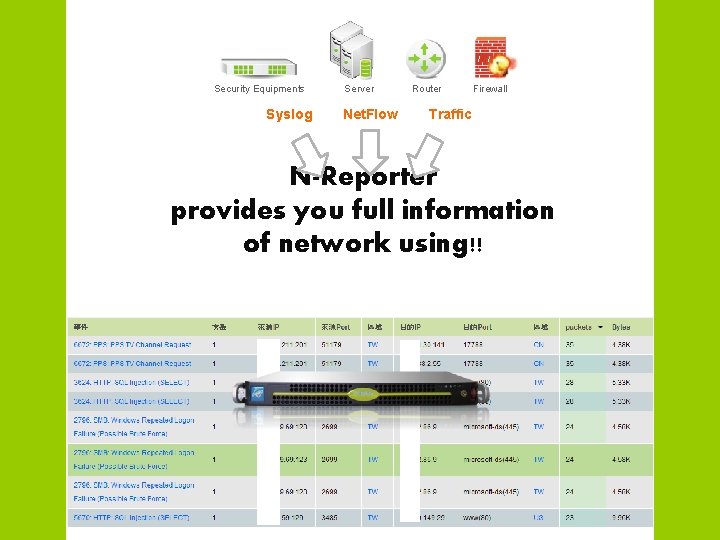
Security Equipments Syslog Server Net. Flow Router Firewall Traffic N-Reporter provides you full information of network using!!
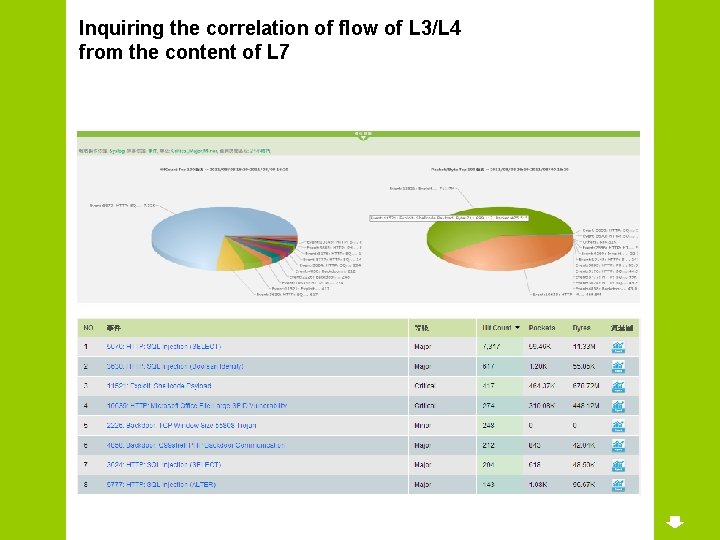
Inquiring the correlation of flow of L 3/L 4 from the content of L 7
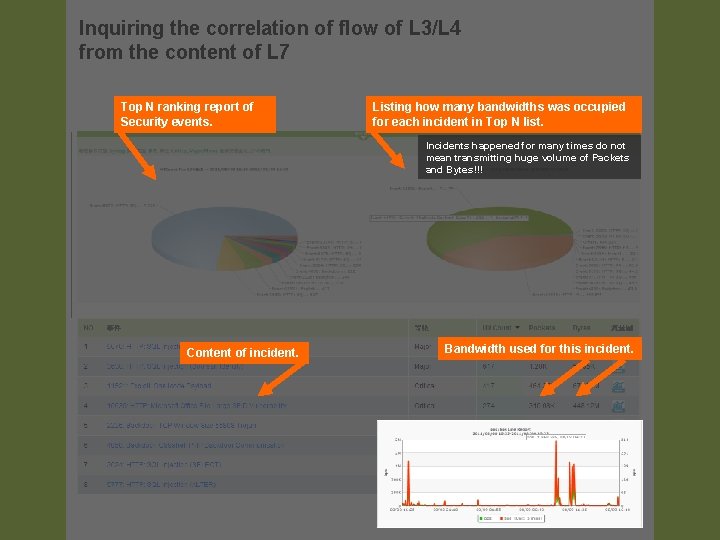
Inquiring the correlation of flow of L 3/L 4 from the content of L 7 Top N ranking report of Security events. Listing how many bandwidths was occupied for each incident in Top N list. Incidents happened for many times do not mean transmitting huge volume of Packets and Bytes!!! Content of incident. Bandwidth used for this incident.
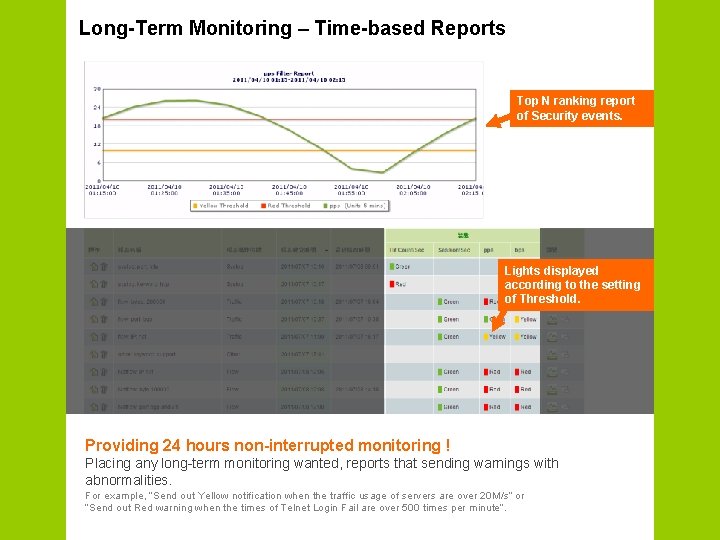
Long-Term Monitoring – Time-based Reports Top N ranking report of Security events. Lights displayed according to the setting of Threshold. Providing 24 hours non-interrupted monitoring ! Placing any long-term monitoring wanted, reports that sending warnings with abnormalities. For example, “Send out Yellow notification when the traffic usage of servers are over 20 M/s” or “Send out Red warning when the times of Telnet Login Fail are over 500 times per minute”.
Abnormal Actions Trend Analysis Realtime abnormalities trend analyzing function è Automatically building Threshold Base Line by learning history. è Immediate warning with increasing abnormalities of Syslog incident / Huge Flow Traffic. è Blocking IP source with increased abnormalities in batches.
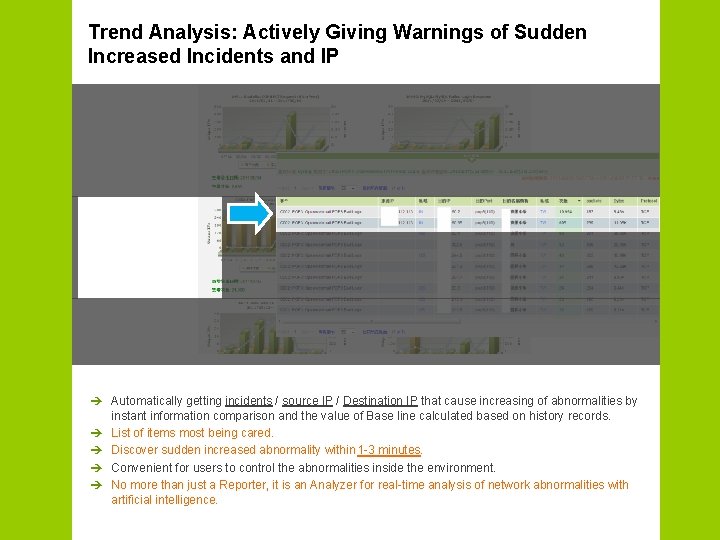
Trend Analysis: Actively Giving Warnings of Sudden Increased Incidents and IP è Automatically getting incidents / source IP / Destination IP that cause increasing of abnormalities by instant information comparison and the value of Base line calculated based on history records. è List of items most being cared. è Discover sudden increased abnormality within 1 -3 minutes. è Convenient for users to control the abnormalities inside the environment. è No more than just a Reporter, it is an Analyzer for real-time analysis of network abnormalities with artificial intelligence.
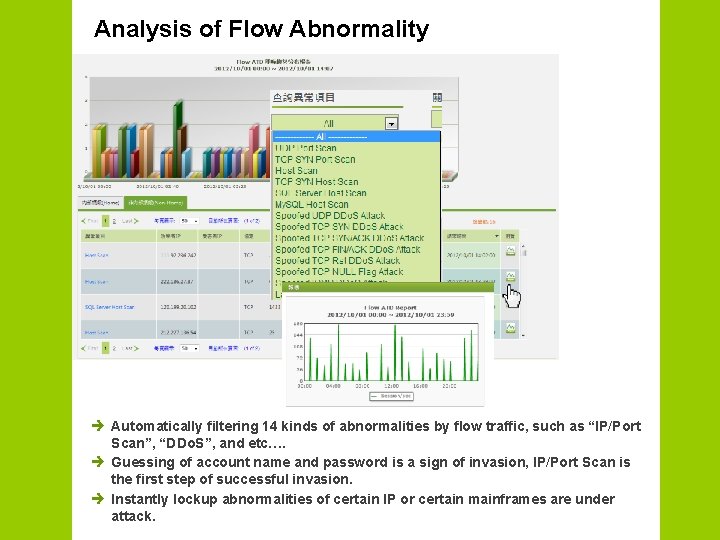
Analysis of Flow Abnormality è Automatically filtering 14 kinds of abnormalities by flow traffic, such as “IP/Port Scan”, “DDo. S”, and etc…. è Guessing of account name and password is a sign of invasion, IP/Port Scan is the first step of successful invasion. è Instantly lockup abnormalities of certain IP or certain mainframes are under attack.
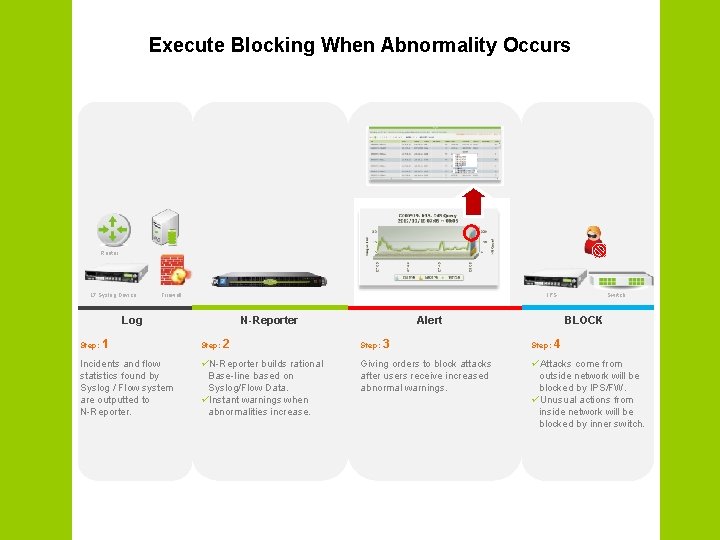
Execute Blocking When Abnormality Occurs Router L 7 Syslog Device Firewall IPS Log N-Reporter Alert Switch BLOCK Step: 1 Step: 2 Step: 3 Step: 4 Incidents and flow statistics found by Syslog / Flow system are outputted to N-Reporter. üN-Reporter builds rational Base-line based on Syslog/Flow Data. üInstant warnings when abnormalities increase. Giving orders to block attacks after users receive increased abnormal warnings. üAttacks come from outside network will be blocked by IPS/FW. üUnusual actions from inside network will be blocked by inner switch.
Chinese reports generating and delivering regularly Function of Chinese Reports è Various arguments setting producing reports for requirements. è Generating and delivering Off-line reports automatically. è Sopporting the IP Name mapping , easier to find out the real identity of IP.
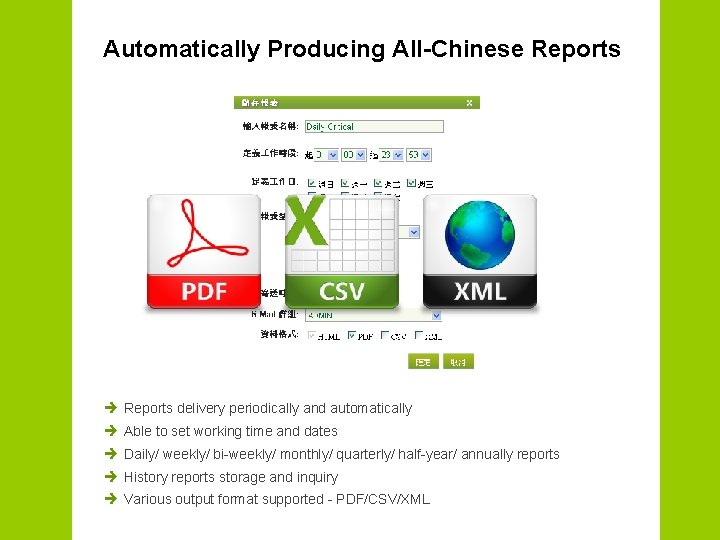
Automatically Producing All-Chinese Reports è Reports delivery periodically and automatically è Able to set working time and dates è Daily/ weekly/ bi-weekly/ monthly/ quarterly/ half-year/ annually reports è History reports storage and inquiry è Various output format supported - PDF/CSV/XML
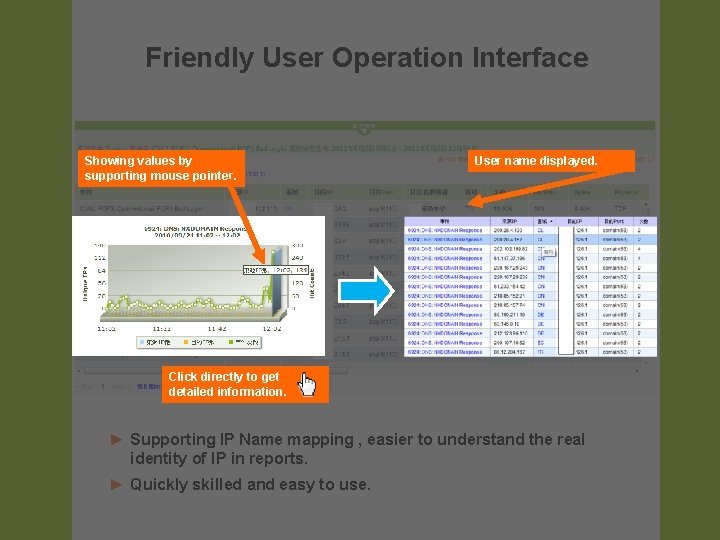
Friendly User Operation Interface Showing values by supporting mouse pointer. User name displayed. Click directly to get detailed information. ► Supporting IP Name mapping , easier to understand the real identity of IP in reports. ► Quickly skilled and easy to use.
Value Added Reports Analysis è Analyzing data by a specific user. è Regulations audit reports. è Abnormal Audit analysis.
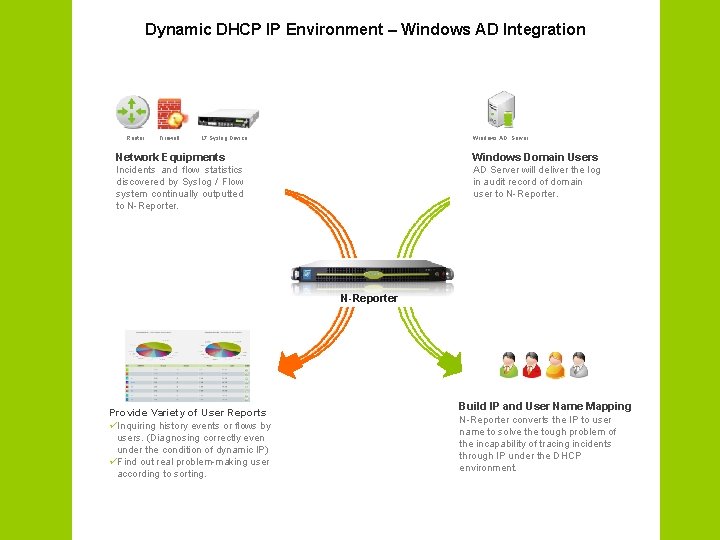
Dynamic DHCP IP Environment – Windows AD Integration Router Firewall L 7 Syslog Device Windows AD Server Network Equipments Windows Domain Users Incidents and flow statistics discovered by Syslog / Flow system continually outputted to N-Reporter. AD Server will deliver the log in audit record of domain user to N-Reporter Provide Variety of User Reports üInquiring history events or flows by users. (Diagnosing correctly even under the condition of dynamic IP) üFind out real problem-making user according to sorting. Build IP and User Name Mapping N-Reporter converts the IP to user name to solve the tough problem of the incapability of tracing incidents through IP under the DHCP environment.
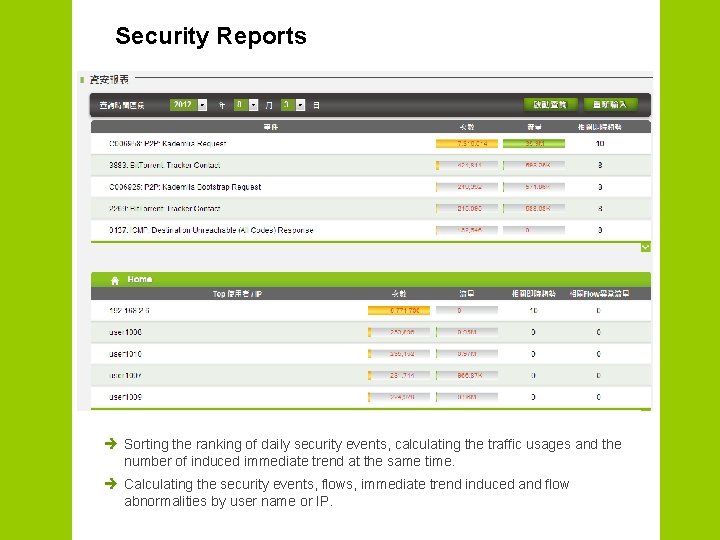
Security Reports è Sorting the ranking of daily security events, calculating the traffic usages and the number of induced immediate trend at the same time. è Calculating the security events, flows, immediate trend induced and flow abnormalities by user name or IP.
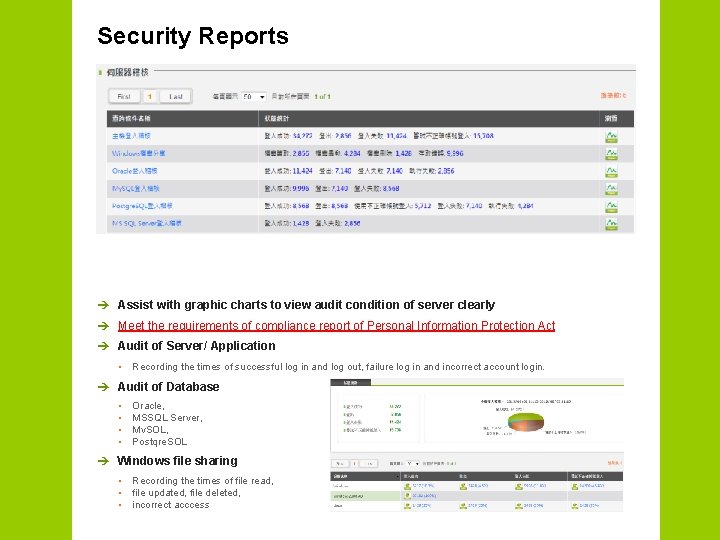
Security Reports è Assist with graphic charts to view audit condition of server clearly è Meet the requirements of compliance report of Personal Information Protection Act è Audit of Server/ Application • Recording the times of successful log in and log out, failure log in and incorrect account login. è Audit of Database • • Oracle, MSSQL Server, Mv. SOL, Postqre. SOL è Windows file sharing • • • Recording the times of file read, file updated, file deleted, incorrect acccess
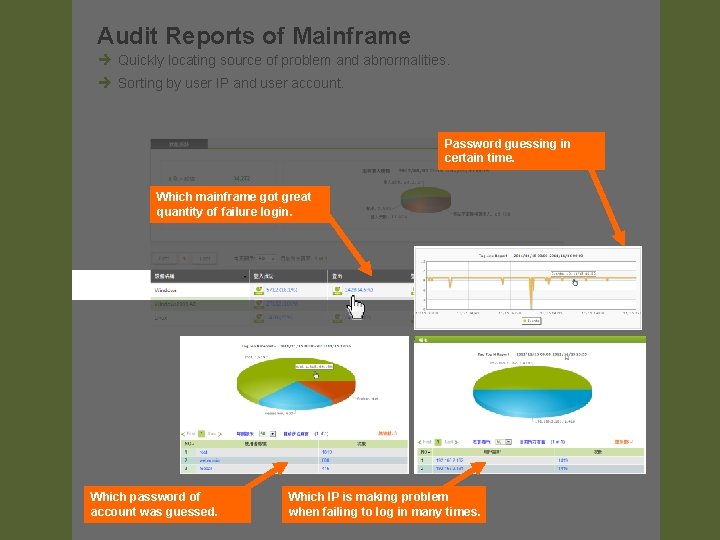
Audit Reports of Mainframe è Quickly locating source of problem and abnormalities. è Sorting by user IP and user account. Password guessing in certain time. Which mainframe got great quantity of failure login. Which password of account was guessed. Which IP is making problem when failing to log in many times.
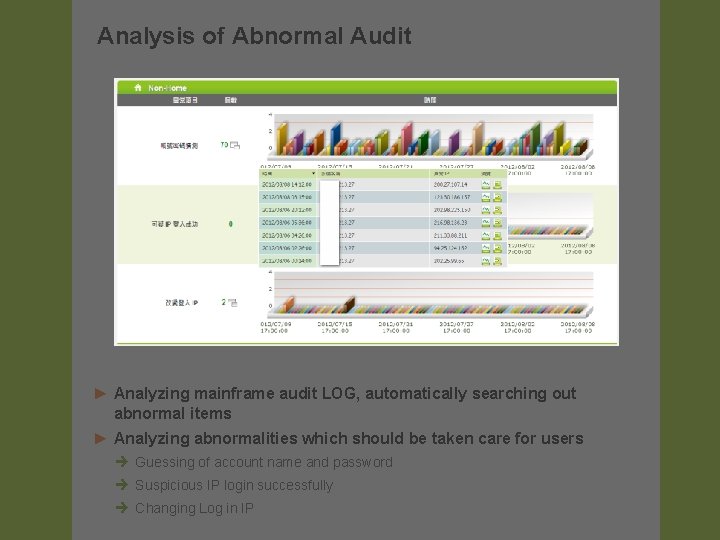
Analysis of Abnormal Audit ► Analyzing mainframe audit LOG, automatically searching out abnormal items ► Analyzing abnormalities which should be taken care for users è Guessing of account name and password è Suspicious IP login successfully è Changing Log in IP
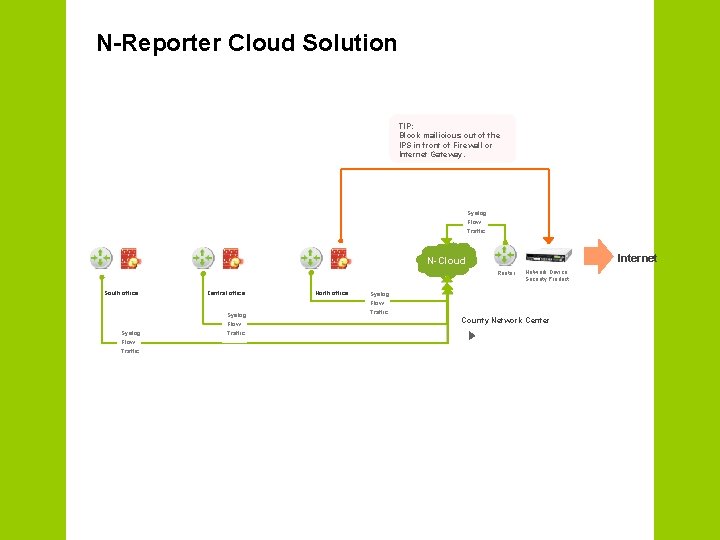
Could Solution N-Reporter Cloud Solution è Hierarchical Management è High Availability Structure è Big Data Collection
N-Reporter Cloud Solution n Hierarchical Decentralized Management ü Departments in corporation see the information of their own department only, just like having a N-Reporter independently. ü Operators and administrators can check up the information of corporation globally. n High Flexibility of Structure ü Apply to centralized and distributed construction. ü Constructing N-Center and N-Receiver as required in every regional branch. ü Head corporation can check up the information of all branches. n Supporting High Availability(HA) Structure ü N-Center / N-Receiver support backup function for non interrupting service. n Big Data Environment ü Support up to 300 thousand EPS. n High Flexibility of Expansion ü Flexible expansion of N-Cloud for future data collection and increase of users.
N-Reporter Cloud Solution TIP: Block mailicious out of the IPS in front of Firewall or Internet Gateway. Syslog Flow Traffic Internet N-Cloud Router South office Central office North office Network Device Security Product Syslog Flow Traffic County Network Center
We Offer You More Than just LOG Management !!
! !! Integrating all kinds of LOG to help forensic corporate collections è Centralized management of LOG to meet audit requirements. è Fetch complete history records with high speed searching. è Guarantee for data integrity. è Best tool for corporations to conform Personal Information Protection Act.
! !! Provide analysis with plentiful reports è TOP N reports providing list of max security incidents in your network. è Time-based reports providing continuous monitoring plan for network security 24 hours a day. è Trend reports automatically analyzing the trends most being watched è Producing daily/weekly/monthly/quarterly/annually reports for policies making. Full protection with instantly monitoring!!!
! !! Cross analysis with security flows è Find network conditions lively with Flow Module. è Analyzing mainframe abnormalities with Server Module. è Quickly remove internet errors with Action Module.
Successful Cases
Successful Cases
Successful Cases
Thank You