Google GDPR and you Data Protection compliance in
- Slides: 41
Google, GDPR and you Data Protection compliance in 2019 Meeting all your data protection and privacy needs
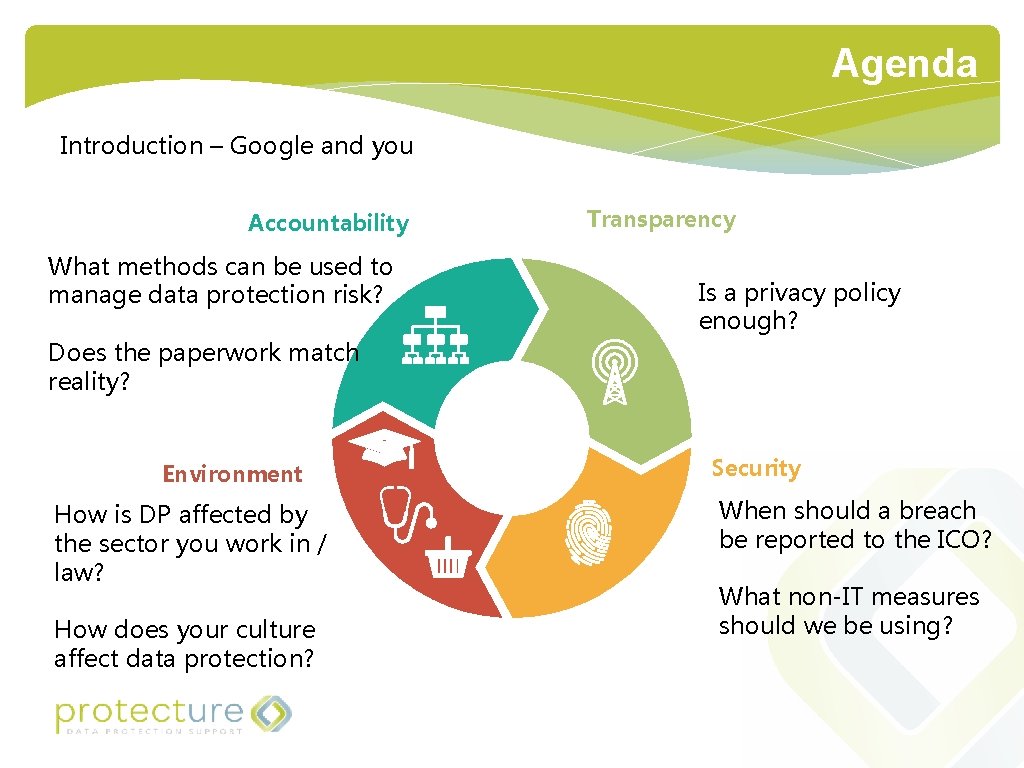
Agenda Introduction – Google and you Accountability What methods can be used to manage data protection risk? Does the paperwork match reality? Environment How is DP affected by the sector you work in / law? How does your culture affect data protection? Transparency Is a privacy policy enough? Security When should a breach be reported to the ICO? What non-IT measures should we be using?
Data protection is… …about people …shorthand for the protection of people against unfair / unwarranted adverse consequences coming from your processing of their data
Data Protection principles… Fair, lawful, transparent Specified purposes Minimisation Accuracy Storage limitation Security Accountability
Where do you want to be? Cosmetic Risk Ethics
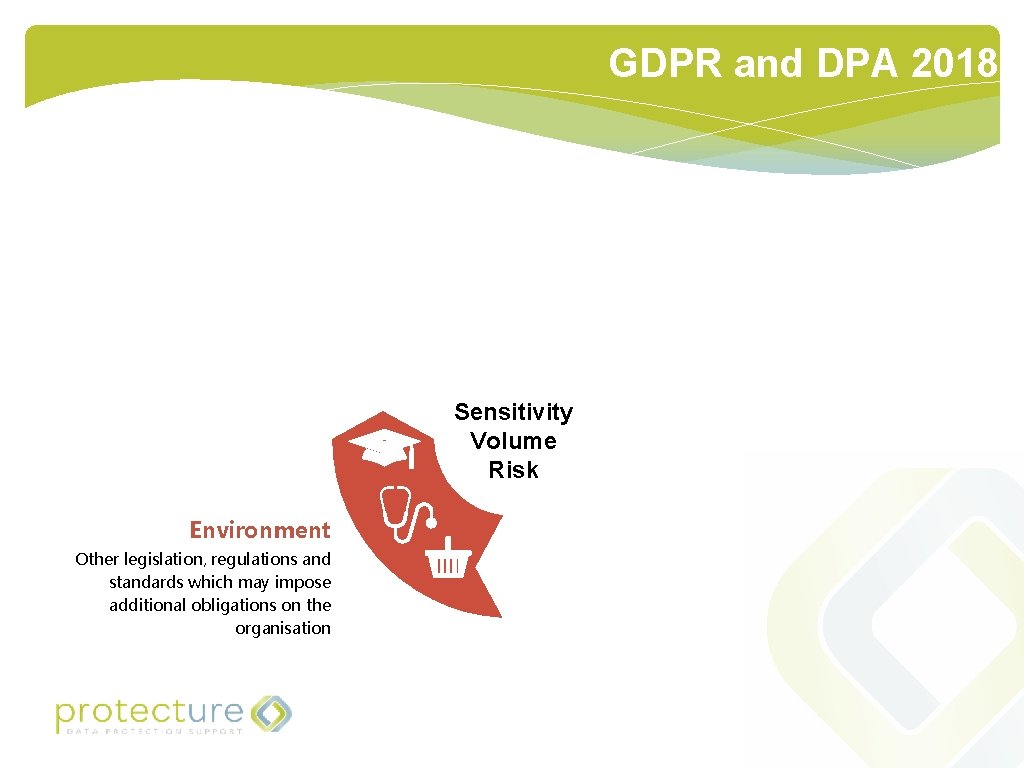
GDPR and DPA 2018 Sensitivity Volume Risk Environment Other legislation, regulations and standards which may impose additional obligations on the organisation
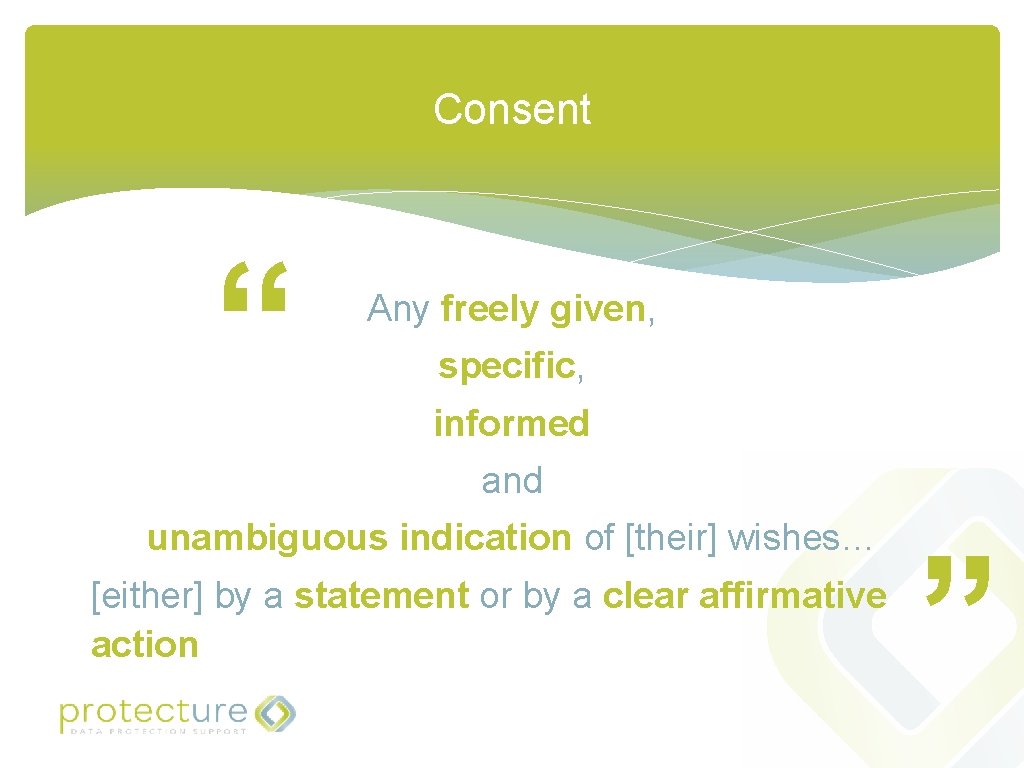
Consent “ Any freely given, specific, informed and unambiguous indication of [their] wishes… [either] by a statement or by a clear affirmative action ”
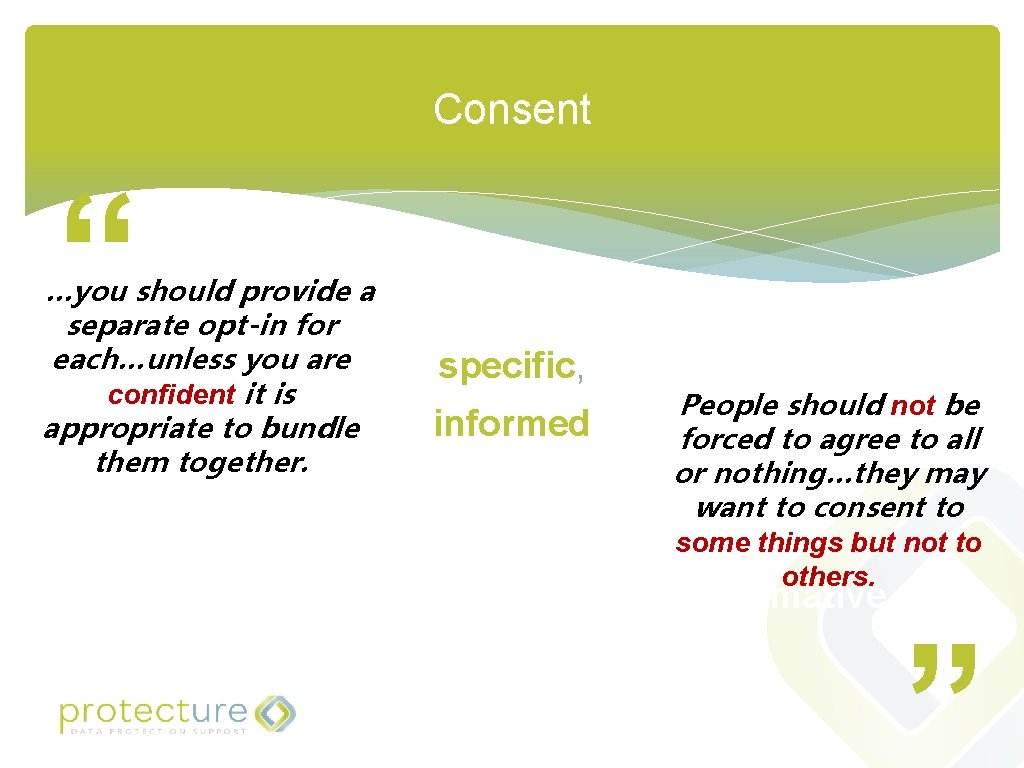
Consent “ …you should provide a separate opt-in for Any freely given, each…unless you are specific, confident it is People should not be informed appropriate to bundle forced to agree to all them together. or nothing…they may and want to consent to unambiguous indication of [their] wishes… some things but not to others. [either] by a statement or by a clear affirmative action ”
Google Consent 1. Informed? 2. Specific 3. Unambiguous ?
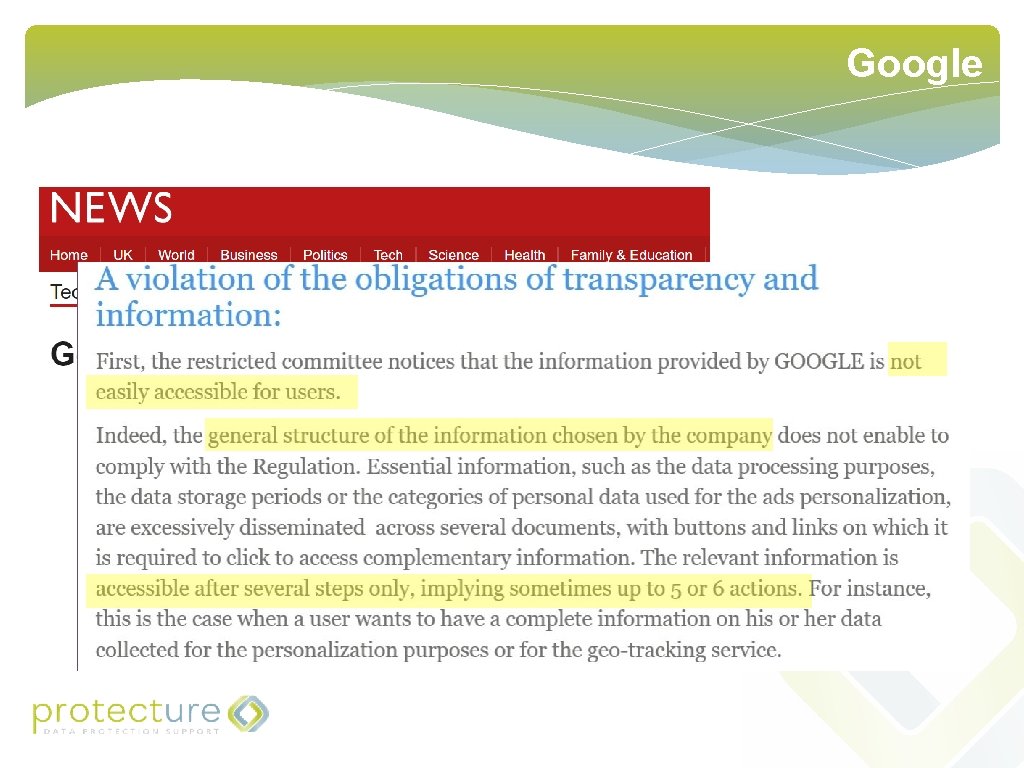
Google Transparency Are you happy to explain your decisions on what goes where, and why, and how? in a concise, transparent, intelligible and easily accessible form, using clear and plain language 1. Reflecting your different audiences? 2. Appropriate for the personal data you’re collecting? 3. Tailored to each of your collection / touch points? 4. Providing the privacy info. up front, on a policy, or later?
GDPR and DPA 2018 Sensitivity Volume Risk Environment Other legislation, regulations and standards which may impose additional obligations on the organisation
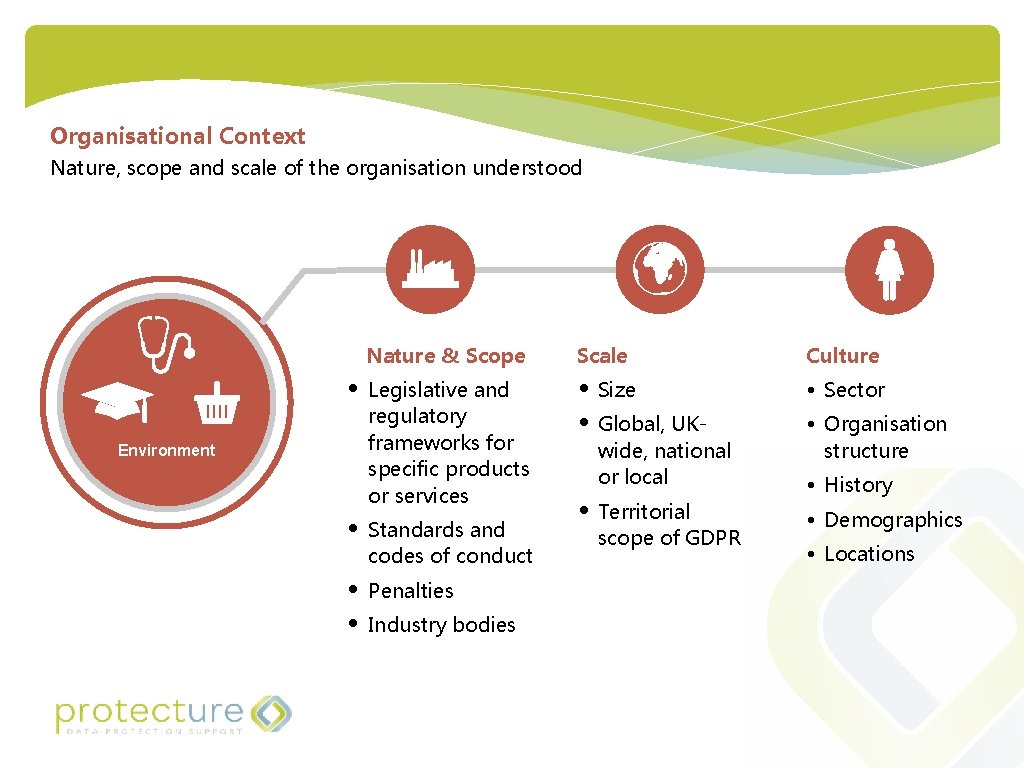
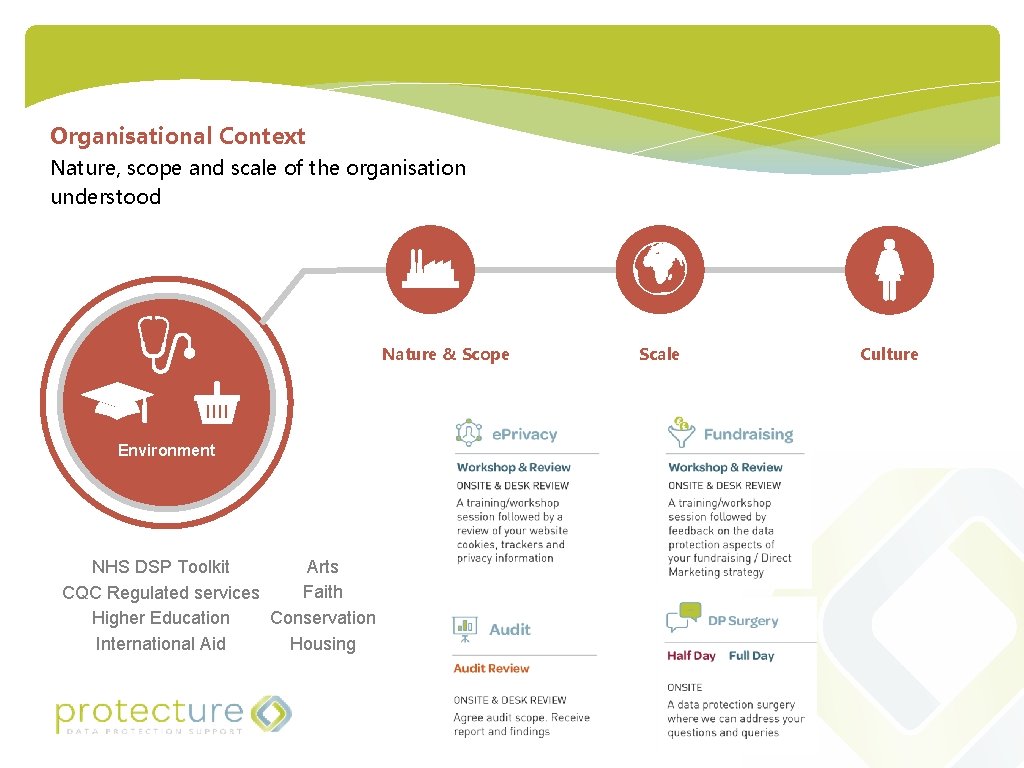
Organisational Context Nature, scope and scale of the organisation understood Nature & Scope • Legislative and Environment regulatory frameworks for specific products or services • Standards and codes of conduct • Penalties • Industry bodies Scale • Size • Global, UK- wide, national or local • Territorial scope of GDPR Culture • Sector • Organisation structure • History • Demographics • Locations
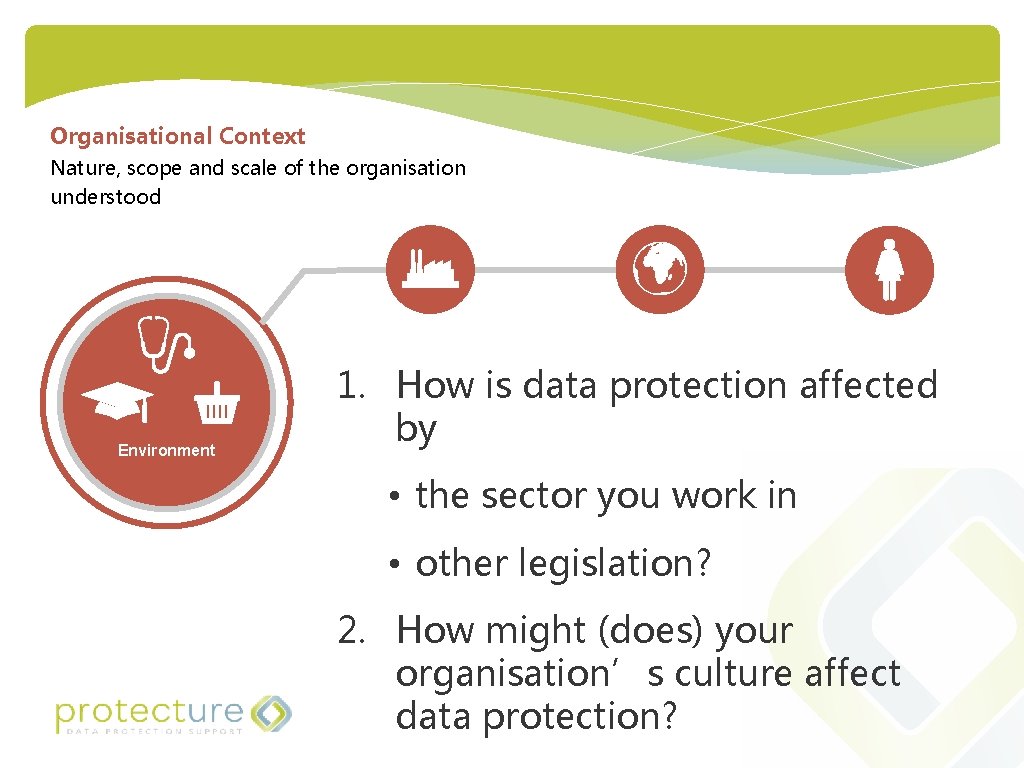
Organisational Context Nature, scope and scale of the organisation understood Environment 1. How is data protection affected by • the sector you work in • other legislation? 2. How might (does) your organisation’s culture affect data protection?
Organisational Context Nature, scope and scale of the organisation understood Nature & Scope Environment Arts NHS DSP Toolkit Faith CQC Regulated services Conservation Higher Education Housing International Aid Scale Culture
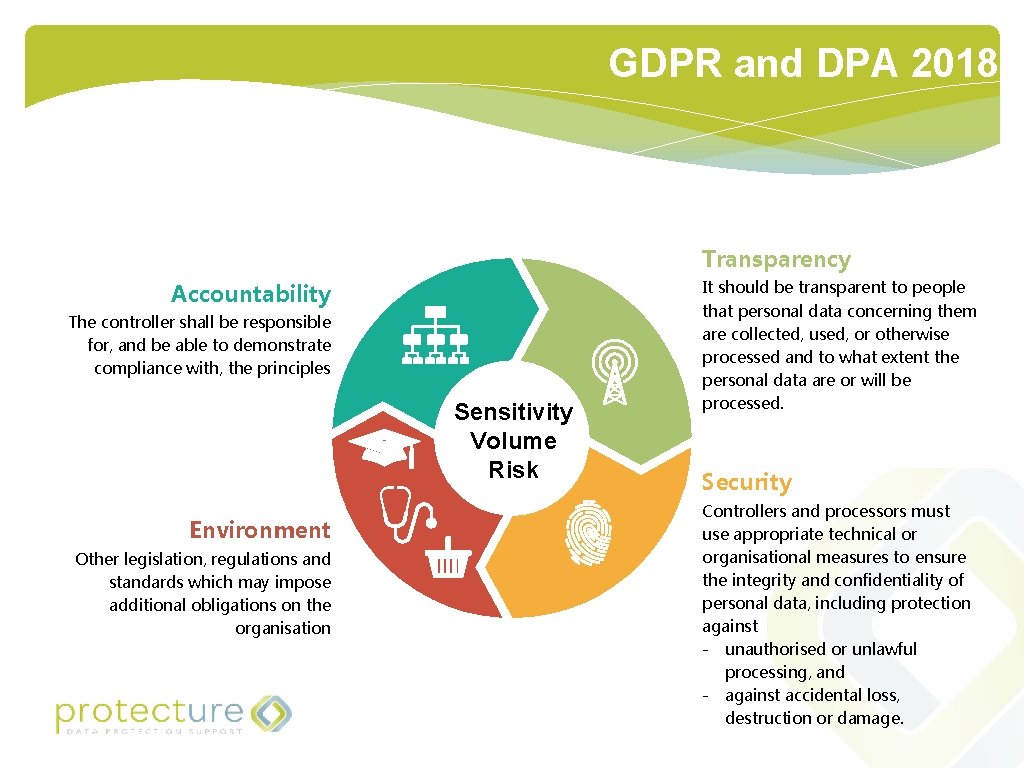
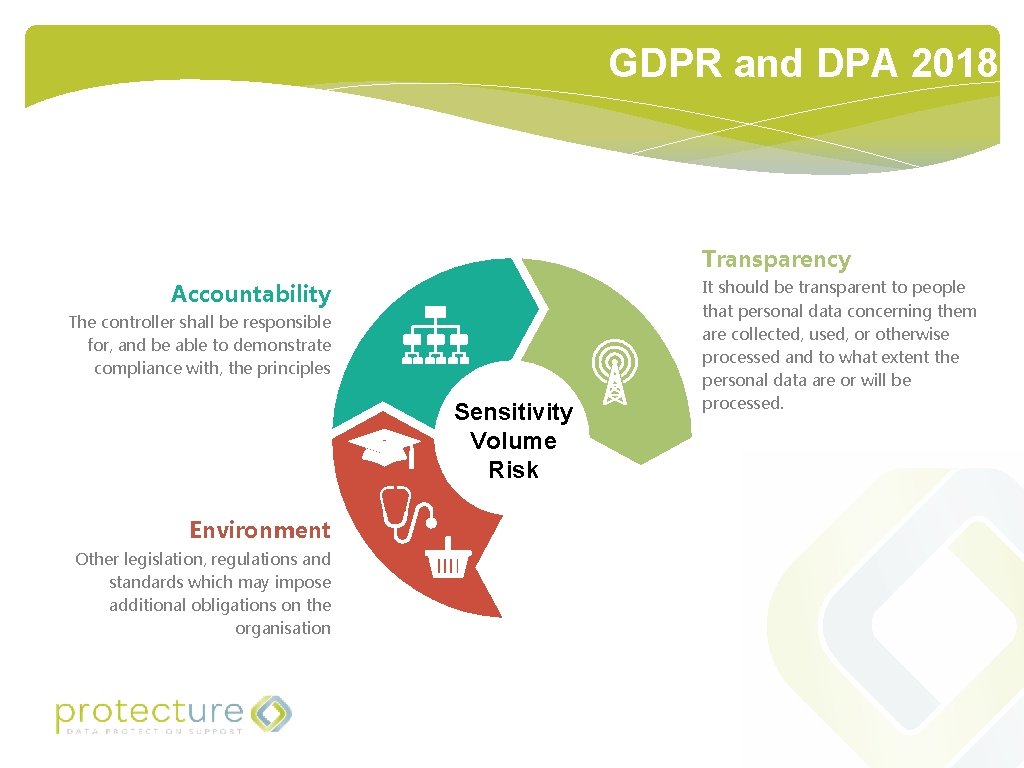
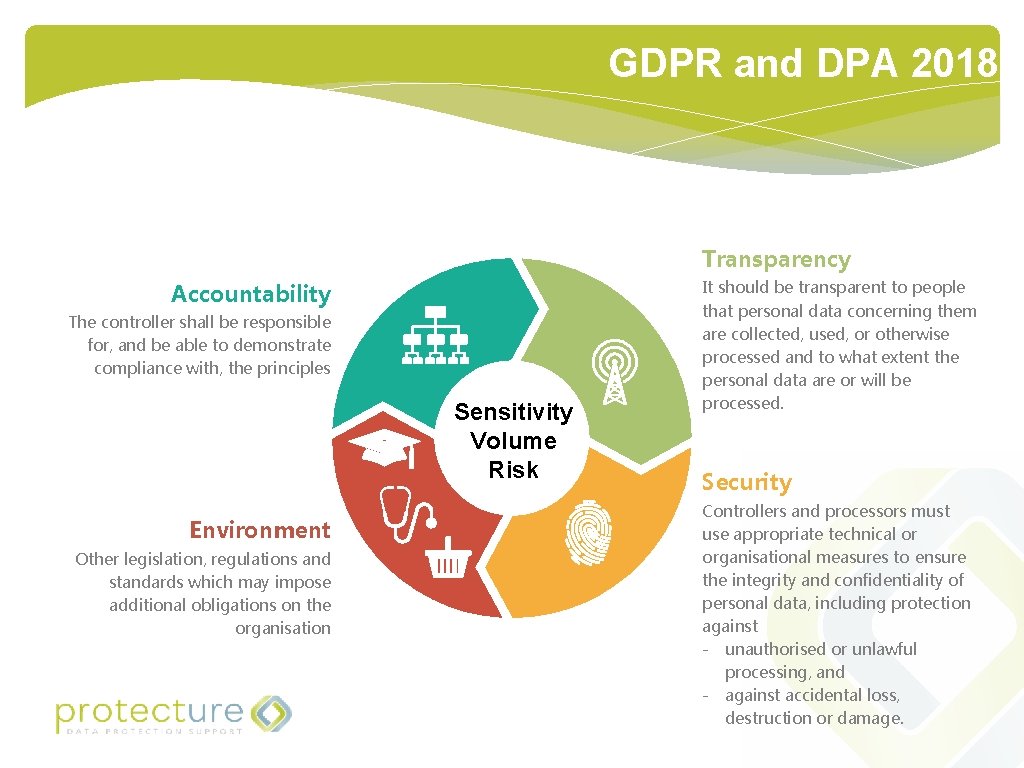
GDPR and DPA 2018 Transparency Accountability The controller shall be responsible for, and be able to demonstrate compliance with, the principles Sensitivity Volume Risk Environment Other legislation, regulations and standards which may impose additional obligations on the organisation It should be transparent to people that personal data concerning them are collected, used, or otherwise processed and to what extent the personal data are or will be processed. Security Controllers and processors must use appropriate technical or organisational measures to ensure the integrity and confidentiality of personal data, including protection against - unauthorised or unlawful processing, and - against accidental loss, destruction or damage.
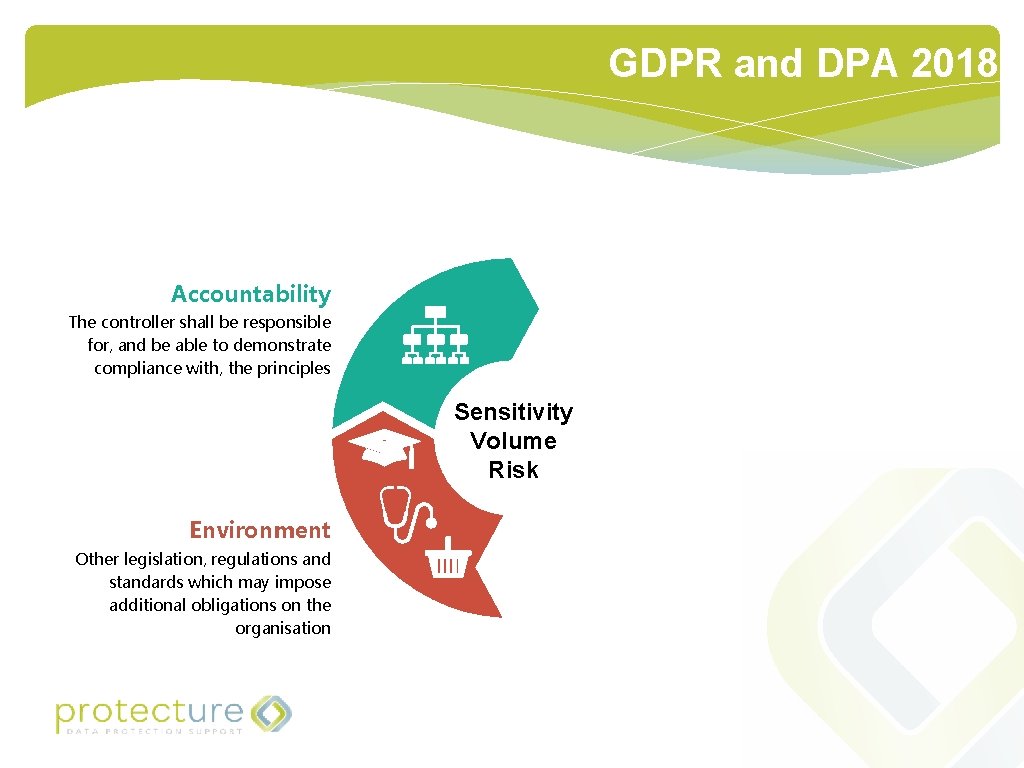
GDPR and DPA 2018 Accountability The controller shall be responsible for, and be able to demonstrate compliance with, the principles Sensitivity Volume Risk Environment Other legislation, regulations and standards which may impose additional obligations on the organisation
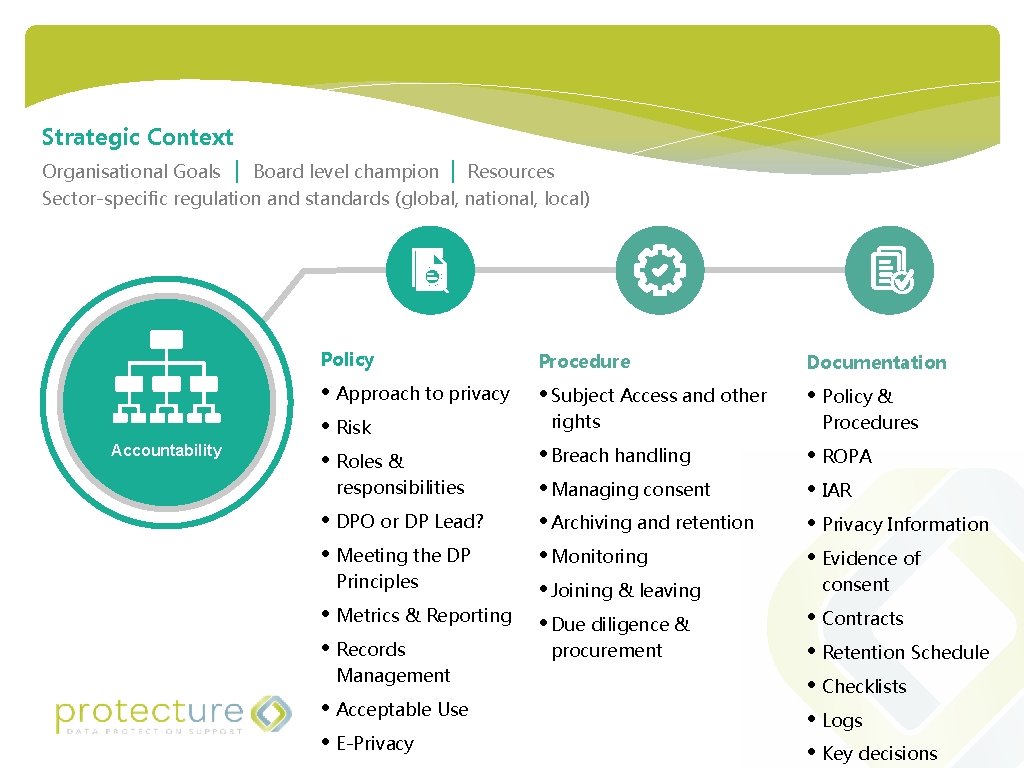
Strategic Context Organisational Goals | Board level champion | Resources Sector-specific regulation and standards (global, national, local) Policy Accountability • Approach to privacy • Risk • Roles & responsibilities • DPO or DP Lead? • Meeting the DP Principles • Metrics & Reporting • Records Management • Acceptable Use • E-Privacy Procedure • Subject Access and other rights • Breach handling • Managing consent • Archiving and retention • Monitoring • Joining & leaving • Due diligence & procurement Documentation • Policy & Procedures • ROPA • IAR • Privacy Information • Evidence of consent • Contracts • Retention Schedule • Checklists • Logs • Key decisions
Strategic Context Organisational Goals | Board level champion | Resources Sector-specific regulation and standards (global, national, local) Accountability “For me, the crucial, crucial change the law brought was around accountability. Accountability encapsulates everything the GDPR is about. It enshrines in law an onus on companies to understand the risks that they create for others with their data processing, and to mitigate those risks… …I don’t see that change in practice yet. I don’t see it in the breaches reported to the ICO. I don’t see it in the cases we investigate, or in the audits we carry out…that’s a problem. Because accountability is a legal requirement. It’s not optional. ”
Strategic Context Organisational Goals | Board level champion | Resources Sector-specific regulation and standards (global, national, local) HMRC Accountability Bounty Caselaw
Strategic Context Organisational Goals | Board level champion | Resources Sector-specific regulation and standards (global, national, local) Accountability Prove your compliance… shall be responsible for and be able to demonstrate compliance with the principles
Strategic Context Organisational Goals | Board level champion | Resources Sector-specific regulation and standards (global, national, local) Accountability Prove your compliance… “Common sense is not so common” Voltaire
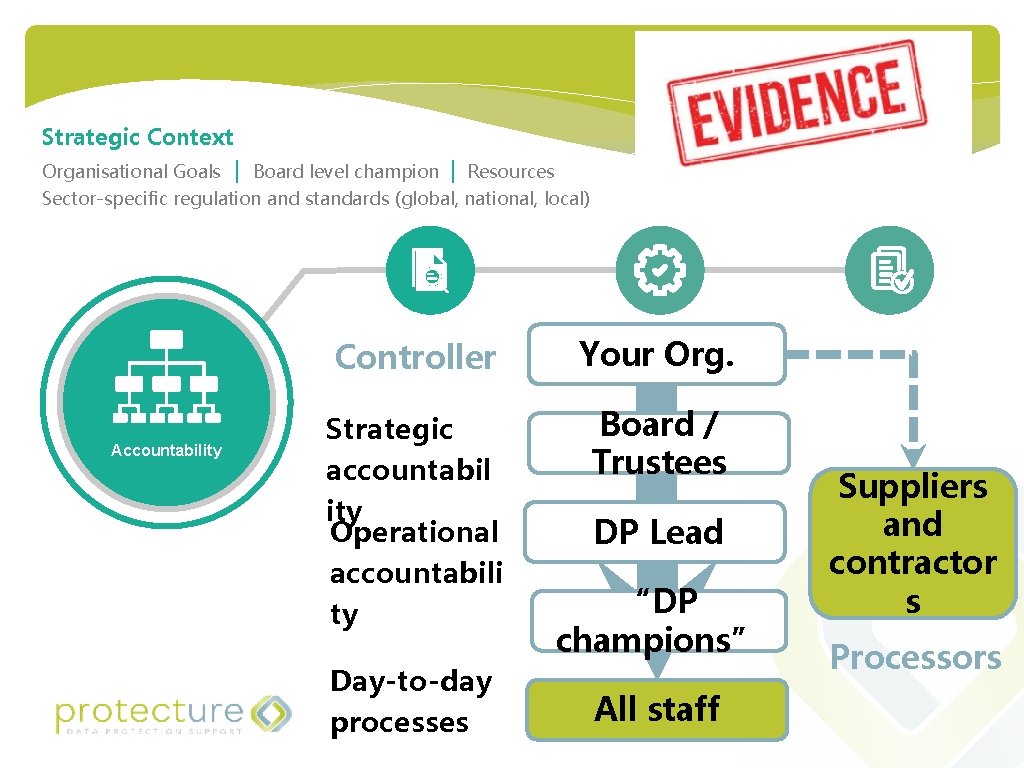
Strategic Context Organisational Goals | Board level champion | Resources Sector-specific regulation and standards (global, national, local) Accountability Controller Your Org. Strategic accountabil ity Operational accountabili ty Board / Trustees Day-to-day processes DP Lead “DP champions” All staff Suppliers and contractor s Processors
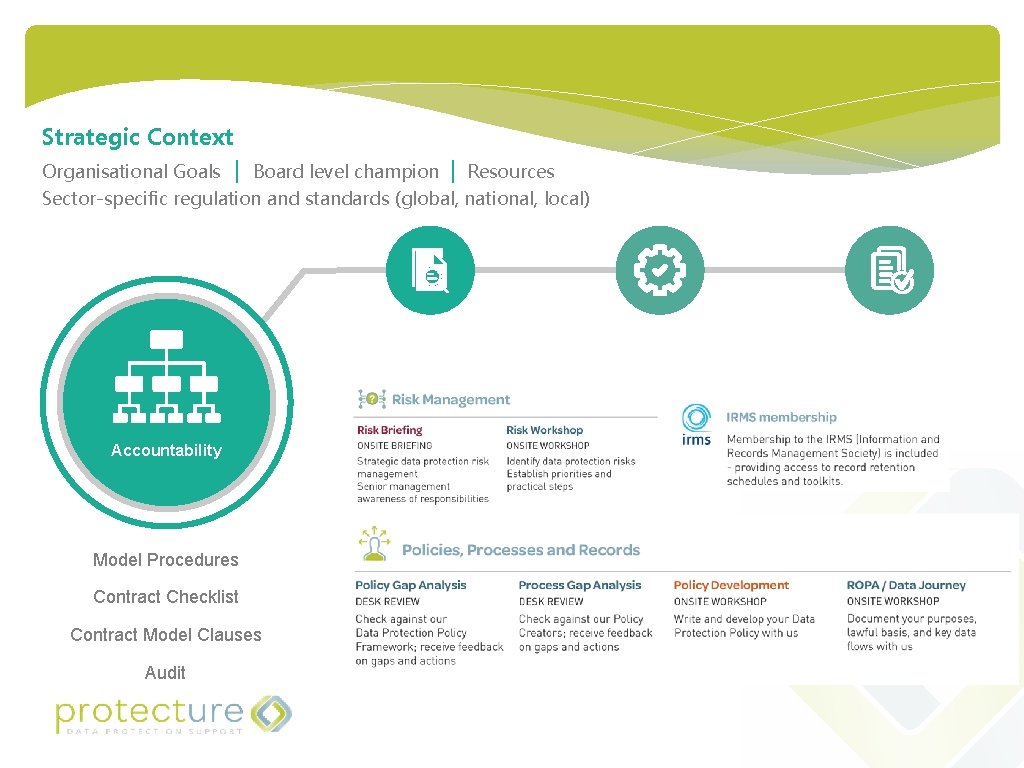
Strategic Context Organisational Goals | Board level champion | Resources Sector-specific regulation and standards (global, national, local) Accountability Model Procedures Contract Checklist Contract Model Clauses Audit
GDPR and DPA 2018 Transparency Accountability The controller shall be responsible for, and be able to demonstrate compliance with, the principles Sensitivity Volume Risk Environment Other legislation, regulations and standards which may impose additional obligations on the organisation It should be transparent to people that personal data concerning them are collected, used, or otherwise processed and to what extent the personal data are or will be processed.
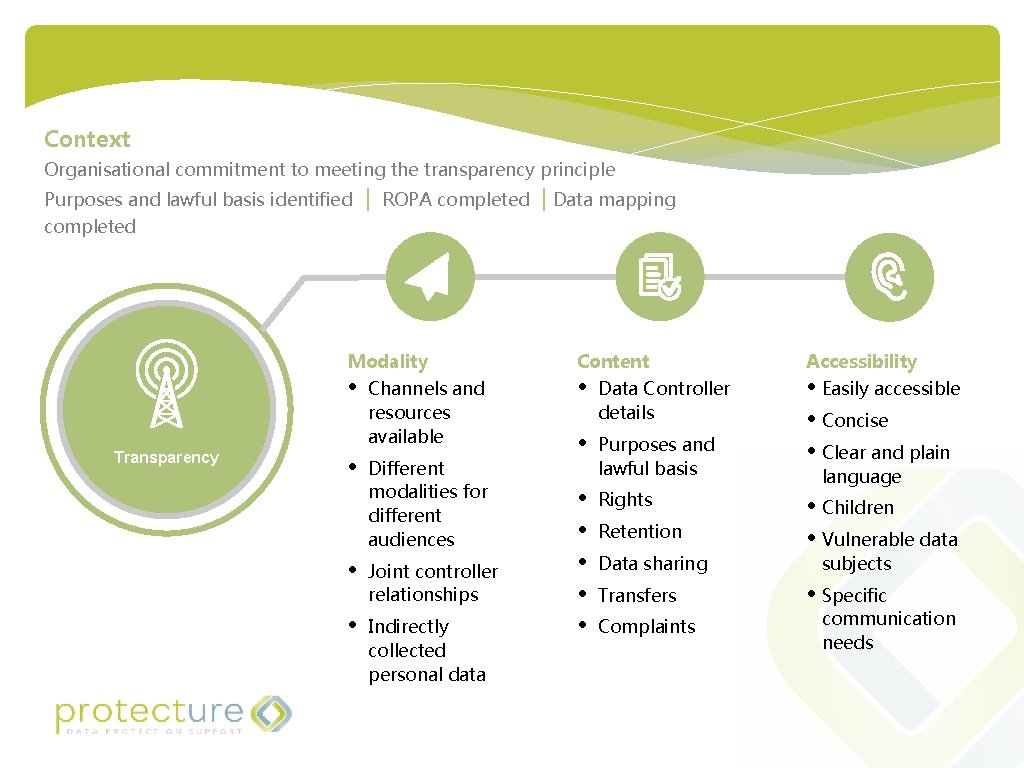
Context Organisational commitment to meeting the transparency principle Purposes and lawful basis identified | ROPA completed | Data mapping completed Modality • Transparency • • • Channels and resources available Different modalities for different audiences Joint controller relationships Indirectly collected personal data Content • • Data Controller details Purposes and lawful basis Rights Retention Data sharing Transfers Complaints Accessibility • Easily accessible • Concise • Clear and plain language • Children • Vulnerable data subjects • Specific communication needs
Context Organisational commitment to meeting the transparency principle Purposes and lawful basis identified | ROPA completed | Data mapping completed Transparency True Visions Productions (TVP) Poland case Case law
Context Organisational commitment to meeting the transparency principle Purposes and lawful basis identified completed Transparency Privacy Strategy Tools Privacy Notice Checklist | ROPA completed | Data mapping
Break
GDPR and DPA 2018 Transparency Accountability The controller shall be responsible for, and be able to demonstrate compliance with, the principles Sensitivity Volume Risk Environment Other legislation, regulations and standards which may impose additional obligations on the organisation It should be transparent to people that personal data concerning them are collected, used, or otherwise processed and to what extent the personal data are or will be processed. Security Controllers and processors must use appropriate technical or organisational measures to ensure the integrity and confidentiality of personal data, including protection against - unauthorised or unlawful processing, and - against accidental loss, destruction or damage.
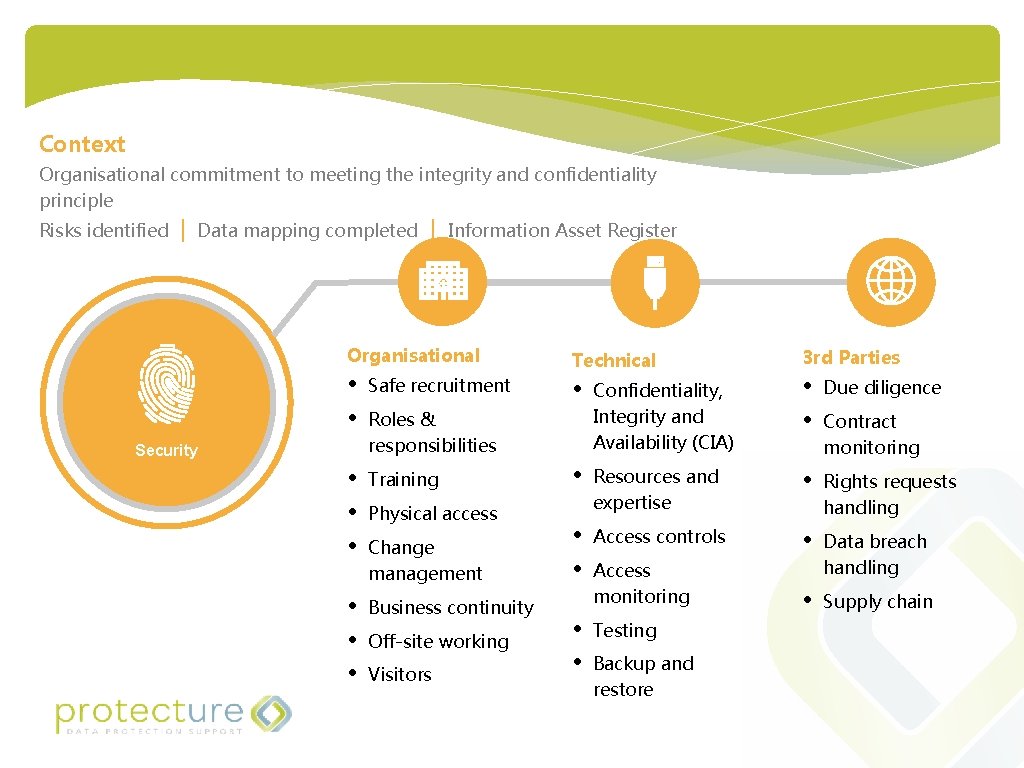
Context Organisational commitment to meeting the integrity and confidentiality principle Risks identified | Data mapping completed | Information Asset Register Organisational • • Security • • • Safe recruitment Roles & responsibilities Training Physical access Change management Business continuity Off-site working Visitors Technical • • • Confidentiality, Integrity and Availability (CIA) 3 rd Parties • • Resources and expertise • Access controls • Access monitoring • Testing Backup and restore Due diligence Contract monitoring Rights requests handling Data breach handling Supply chain
Context Organisational commitment to meeting the integrity and confidentiality principle Risks identified | Data mapping completed | Information Asset Register Security Case law Denmark
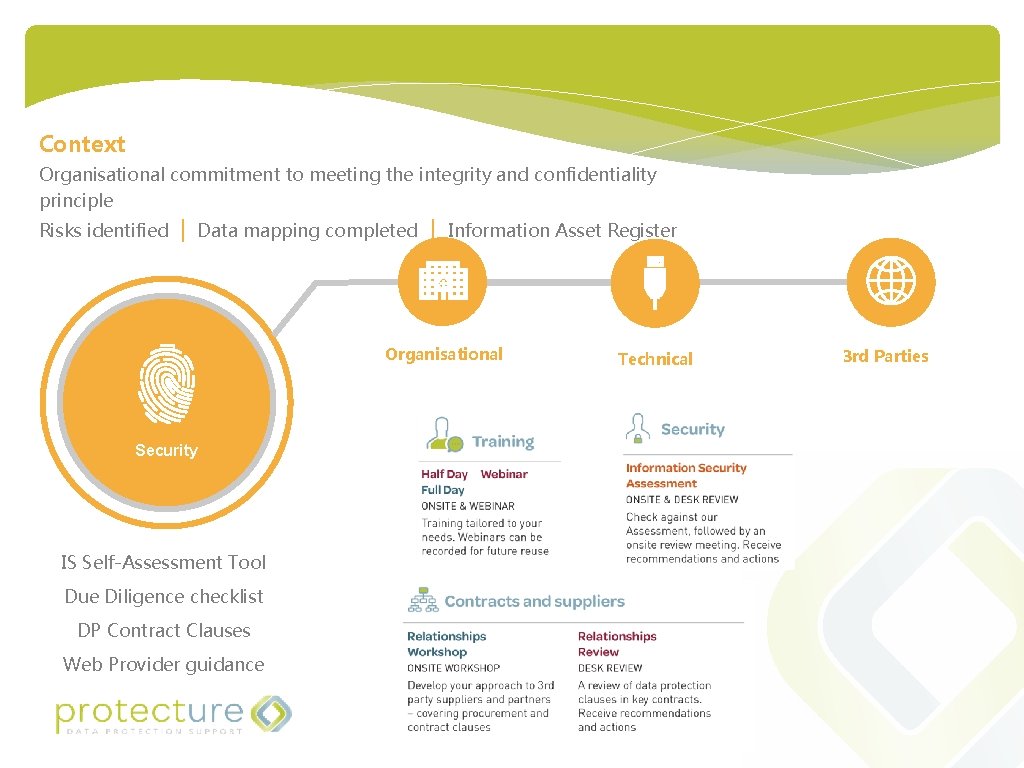
Context Organisational commitment to meeting the integrity and confidentiality principle Risks identified | Data mapping completed | Information Asset Register Organisational Security IS Self-Assessment Tool Due Diligence checklist DP Contract Clauses Web Provider guidance Technical 3 rd Parties
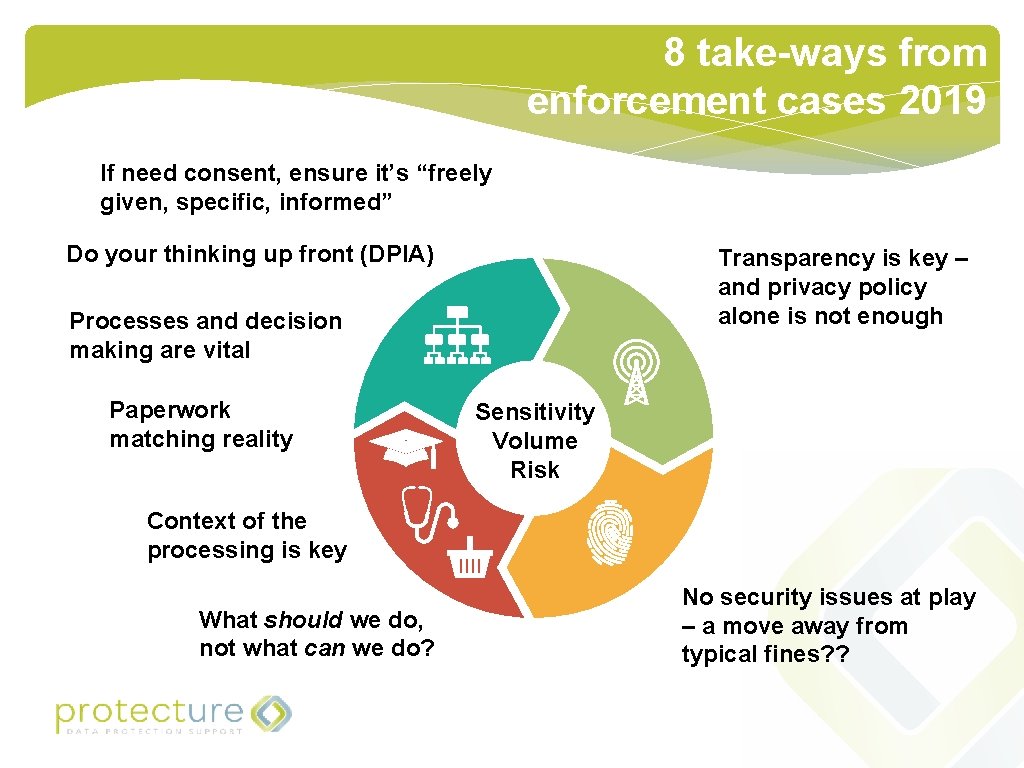
8 take-ways from enforcement cases 2019 If need consent, ensure it’s “freely given, specific, informed” Do your thinking up front (DPIA) Transparency is key – and privacy policy alone is not enough Processes and decision making are vital Paperwork matching reality Sensitivity Volume Risk Context of the processing is key What should we do, not what can we do? No security issues at play – a move away from typical fines? ?
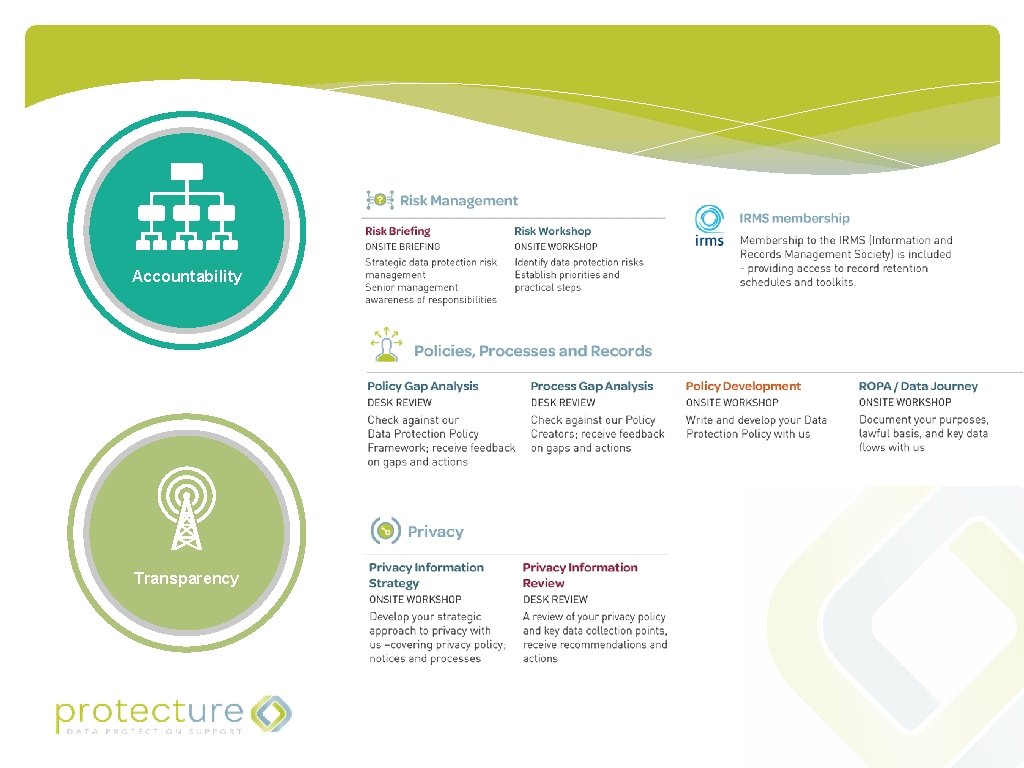
Accountability Transparency
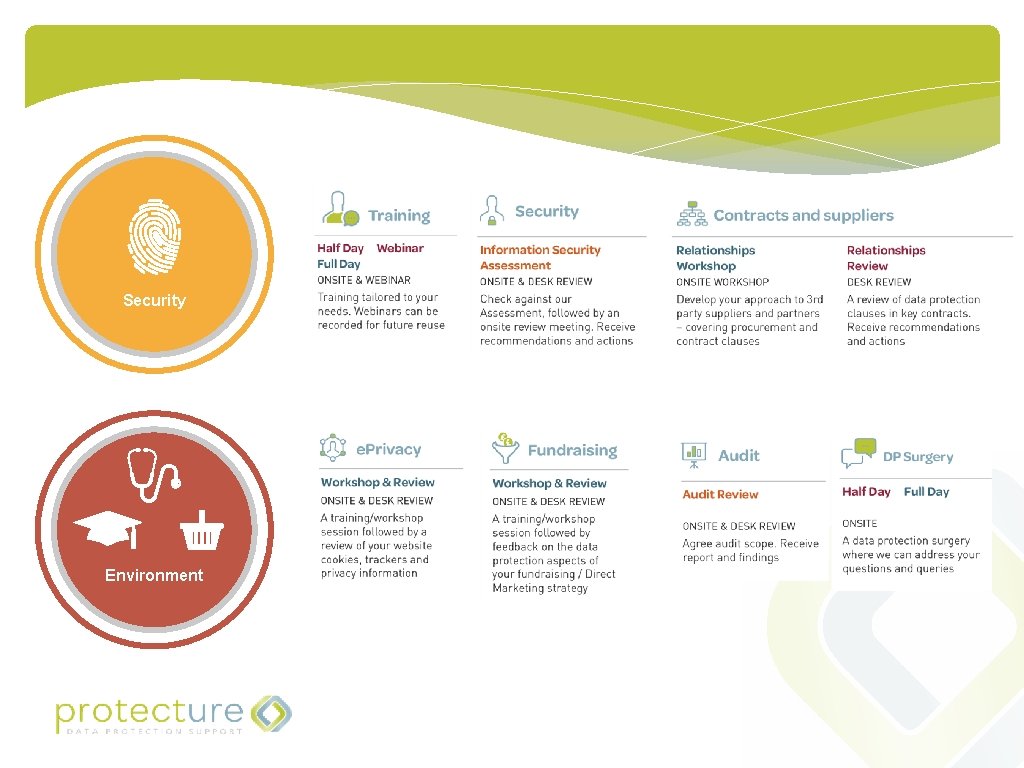
Security Environment
Subscription and Modules Our experts
Free Data Protection Self-Assessment https: //protecture. org. uk/data-protection-self-assessment/ www. protecture. org. uk help@protecture. org. uk @Protecture. DPO