Forward Secure Signatures on Smart Cards A Hlsing
- Slides: 23
Forward Secure Signatures on Smart Cards A. Hülsing, J. Buchmann, C. Busold 16. 08. 2012 | TU Darmstadt | A. Hülsing | 1
Forward Secure Digital Signatures 02. 12. 2011 | TU Darmstadt | A. Huelsing | 2
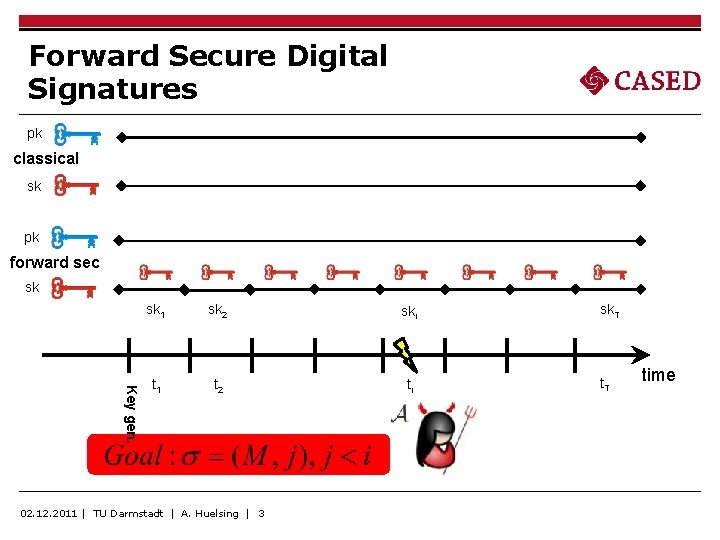
Forward Secure Digital Signatures pk classical sk pk forward sec sk Key gen. sk 1 sk 2 ski t 1 t 2 ti 02. 12. 2011 | TU Darmstadt | A. Huelsing | 3 sk. T time
Forward Secure Digital Signatures Pros: § Fulfill intuition of signature § Replace timestamps § Cuts of some attack vectors for Side-Channel Attacks § Especially interesting for document signatures and PKI Cons: § Stateful § Less efficient than standard signature schemes 02. 12. 2011 | TU Darmstadt | A. Huelsing | 4
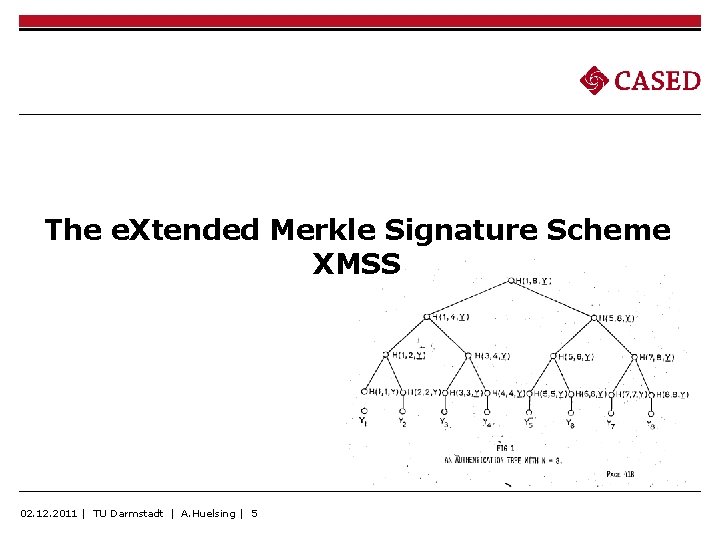
The e. Xtended Merkle Signature Scheme XMSS 02. 12. 2011 | TU Darmstadt | A. Huelsing | 5
The e. Xtended Merkle Signature Scheme (XMSS)[Buchmann et al. , 2011] § “Hash-based” forward secure signature scheme § Provable secure in standard model § Minimal complexity theoretic assumptions (SPR & PRF) § Generic construction (No specific hardness assumption) § Efficient (comparable to RSA) 02. 12. 2011 | TU Darmstadt | A. Huelsing | 6
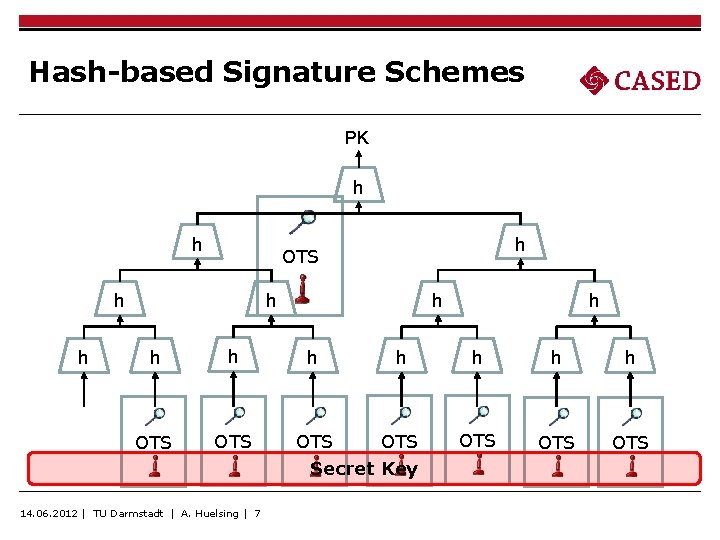
Hash-based Signature Schemes PK h h h OTS h h h h h OTS OTS Secret Key 14. 06. 2012 | TU Darmstadt | A. Huelsing | 7
Goal / Challenges Goal § Implement XMSS on smartcard Challenges § On-card Key generation too expensive [Rohde et al. , 2008] § Stateful / NVM wear out 02. 12. 2011 | TU Darmstadt | A. Huelsing | 8
Construction 02. 12. 2011 | TU Darmstadt | A. Huelsing | 9
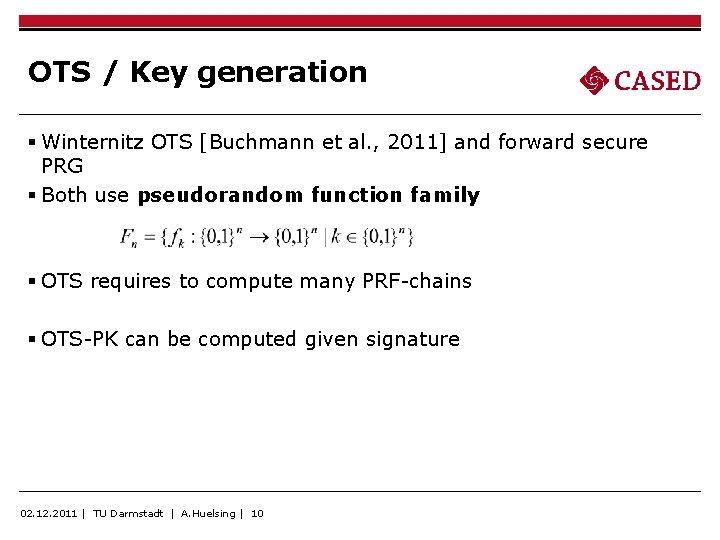
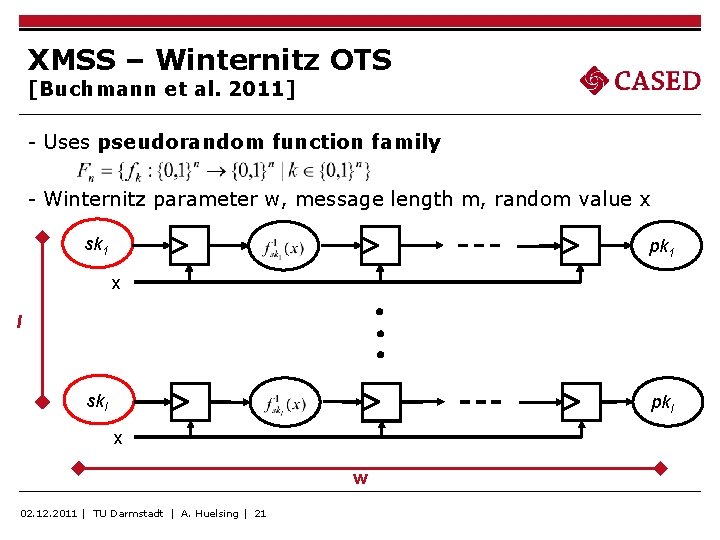
OTS / Key generation § Winternitz OTS [Buchmann et al. , 2011] and forward secure PRG § Both use pseudorandom function family § OTS requires to compute many PRF-chains § OTS-PK can be computed given signature 02. 12. 2011 | TU Darmstadt | A. Huelsing | 10
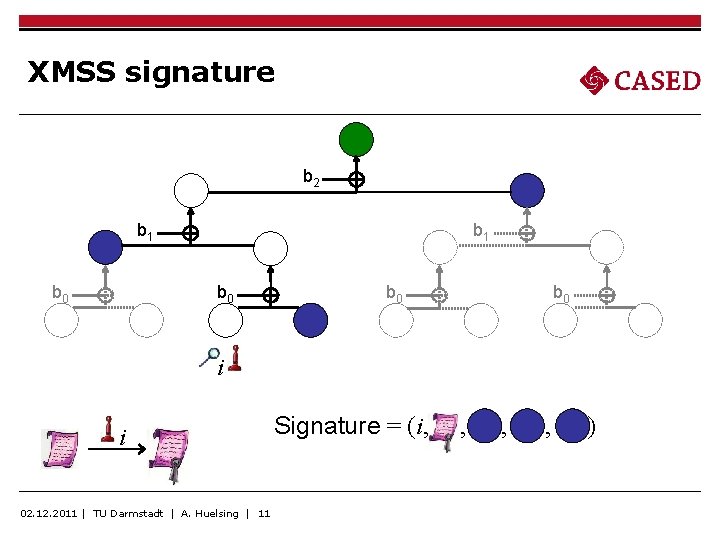
XMSS signature b 2 b 1 b 0 b 0 i i 02. 12. 2011 | TU Darmstadt | A. Huelsing | 11 Signature = (i, , )
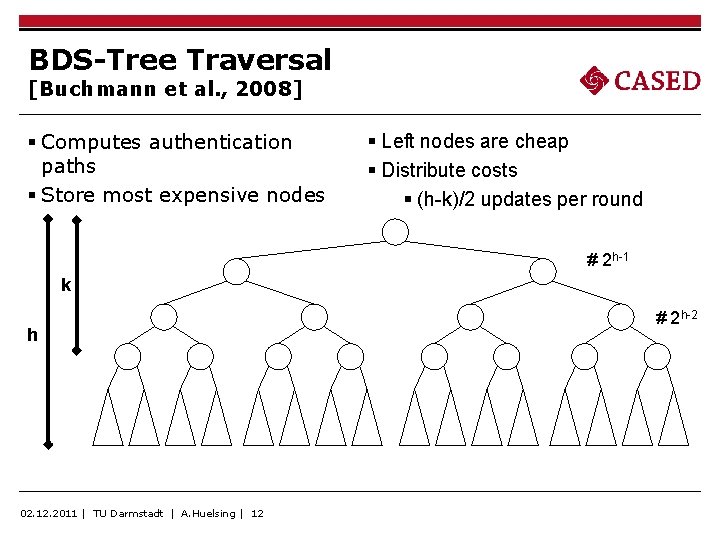
BDS-Tree Traversal [Buchmann et al. , 2008] § Computes authentication paths § Store most expensive nodes § Left nodes are cheap § Distribute costs § (h-k)/2 updates per round # 2 h-1 k h 02. 12. 2011 | TU Darmstadt | A. Huelsing | 12 # 2 h-2
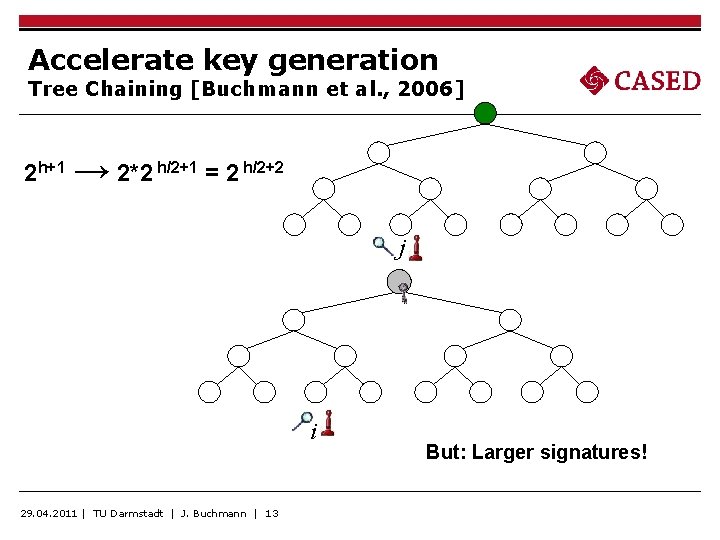
Accelerate key generation Tree Chaining [Buchmann et al. , 2006] 2 h+1 → 2*2 h/2+1 = 2 h/2+2 j i 29. 04. 2011 | TU Darmstadt | J. Buchmann | 13 But: Larger signatures!
Distributed Signature Generation Initial proposal [Buchmann et al. , 2007]: § Distribute signature costs equally among all signatures in lower tree This work: § Use observation: BDS spends more updates than needed § Use unused updates to compute authentication path & signature 02. 12. 2011 | TU Darmstadt | A. Huelsing | 14
Implementation 02. 12. 2011 | TU Darmstadt | A. Huelsing | 15
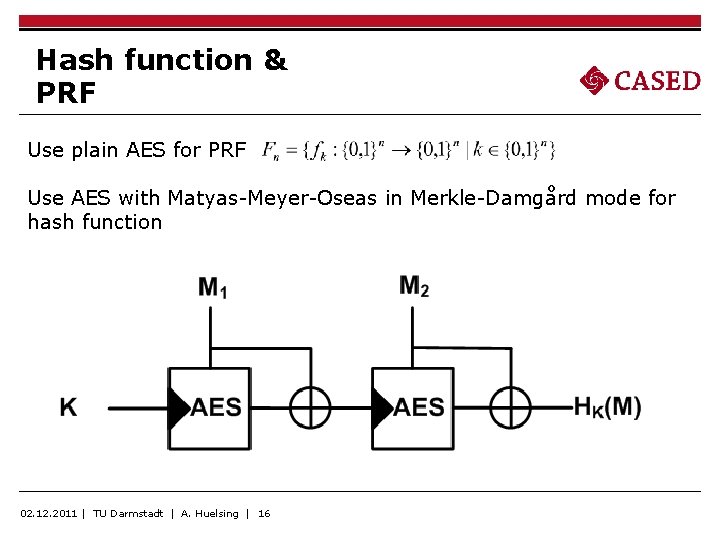
Hash function & PRF Use plain AES for PRF Use AES with Matyas-Meyer-Oseas in Merkle-Damgård mode for hash function 02. 12. 2011 | TU Darmstadt | A. Huelsing | 16
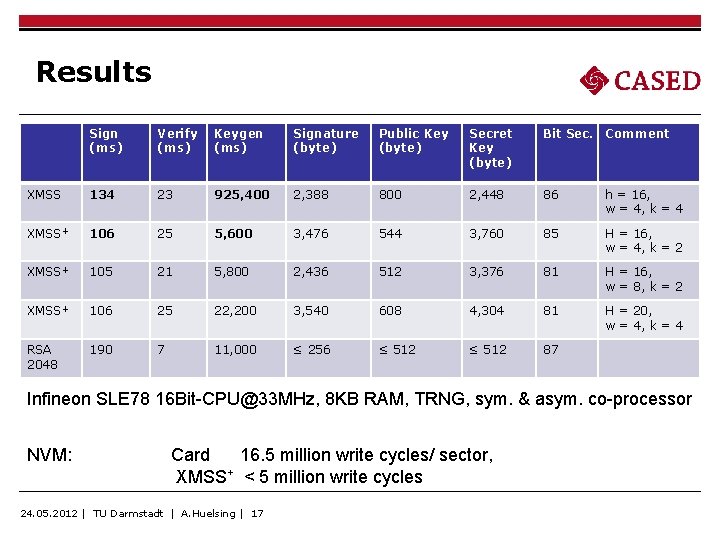
Results Sign (ms) Verify (ms) Keygen (ms) Signature (byte) Public Key (byte) Secret Key (byte) Bit Sec. Comment XMSS 134 23 925, 400 2, 388 800 2, 448 86 h = 16, w = 4, k = 4 XMSS+ 106 25 5, 600 3, 476 544 3, 760 85 H = 16, w = 4, k = 2 XMSS+ 105 21 5, 800 2, 436 512 3, 376 81 H = 16, w = 8, k = 2 XMSS+ 106 25 22, 200 3, 540 608 4, 304 81 H = 20, w = 4, k = 4 RSA 2048 190 7 11, 000 ≤ 256 ≤ 512 87 Infineon SLE 78 16 Bit-CPU@33 MHz, 8 KB RAM, TRNG, sym. & asym. co-processor NVM: Card 16. 5 million write cycles/ sector, XMSS+ < 5 million write cycles 24. 05. 2012 | TU Darmstadt | A. Huelsing | 17
Conclusion 02. 12. 2011 | TU Darmstadt | A. Huelsing | 18
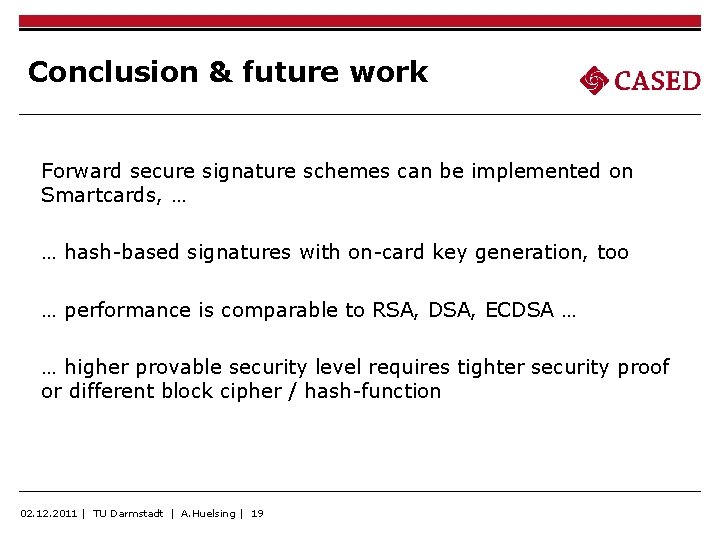
Conclusion & future work Forward secure signature schemes can be implemented on Smartcards, … … hash-based signatures with on-card key generation, too … performance is comparable to RSA, DSA, ECDSA … … higher provable security level requires tighter security proof or different block cipher / hash-function 02. 12. 2011 | TU Darmstadt | A. Huelsing | 19
Thank you, Questions? 02. 12. 2011 | TU Darmstadt | A. Huelsing | 20
XMSS – Winternitz OTS [Buchmann et al. 2011] - Uses pseudorandom function family - Winternitz parameter w, message length m, random value x sk 1 pk 1 x l skl pkl x w 02. 12. 2011 | TU Darmstadt | A. Huelsing | 21
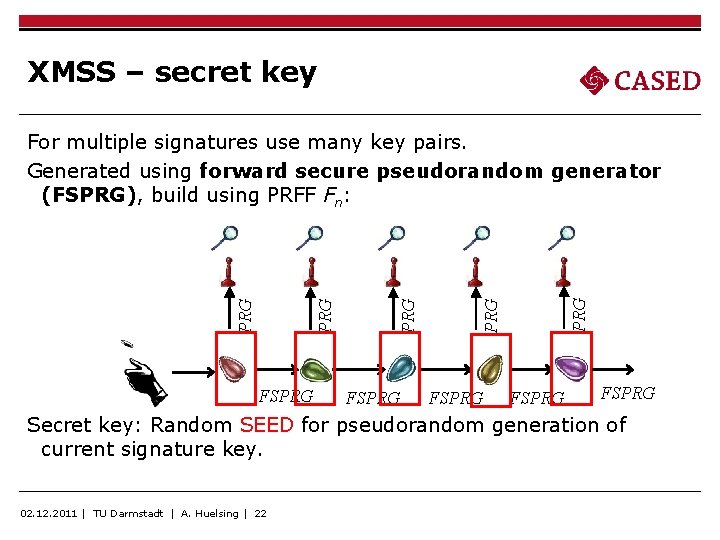
XMSS – secret key FSPRG PRG For multiple signatures use many key pairs. Generated using forward secure pseudorandom generator (FSPRG), build using PRFF Fn: FSPRG Secret key: Random SEED for pseudorandom generation of current signature key. 02. 12. 2011 | TU Darmstadt | A. Huelsing | 22
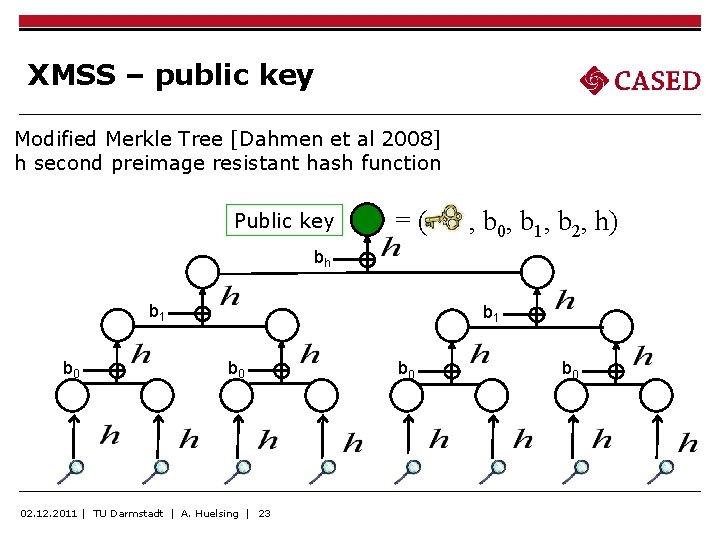
XMSS – public key Modified Merkle Tree [Dahmen et al 2008] h second preimage resistant hash function Public key =( , b 0, b 1, b 2, h) bh b 1 b 0 02. 12. 2011 | TU Darmstadt | A. Huelsing | 23 b 0