SAML and Duo 2 FA Part 3 in
- Slides: 31
SAML and Duo 2 FA Part 3 in the 2 FA series
Overview § A pop quiz!!! § Authentication and Assurance § 2 FA: Duo Security § SAML: ADFS and Shibboleth § Duo Access Gateway § What authentication is right for you? § Adding 2 FA to your application: some examples
A Bit About You…
Who manages an application that authenticates using: § CAS? § Shibboleth? § ADFS?
Does your application support: § Students? § Faculty? § Staff? § Users in more than one of these groups?
Is your application: § On premises? § In the cloud? § Locally developed?
How many of you reuse passwords?
Do you reuse a password on: § 4 sites? § 10 sites? § So many sites you can’t keep track?
How many of you wear a seatbelt when driving or riding in a car?
How many of you remember a time when seatbelts were considered unnecessary or inconvenient?
Authentication and Assurance
Authentication Proving that you are who you claim to be Assurance How confident are we with your proof?
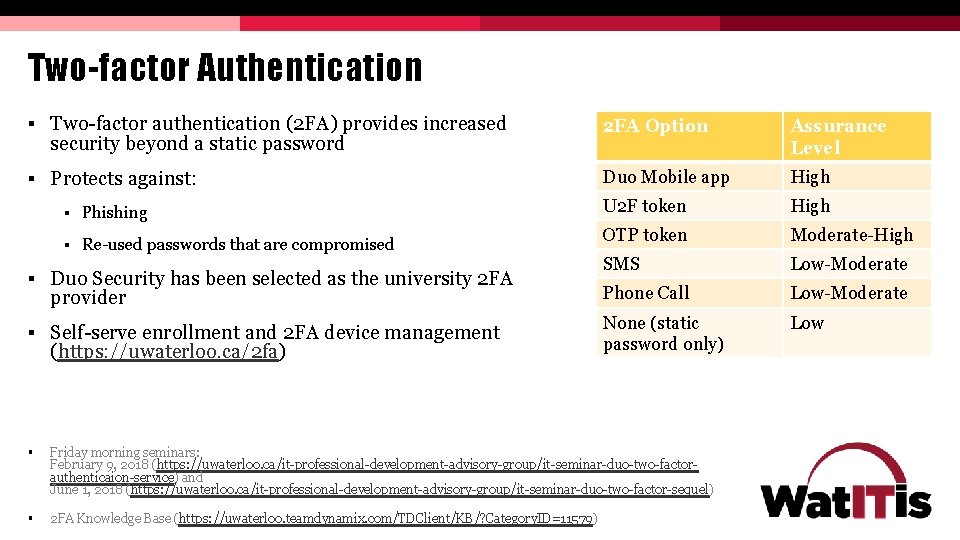
Two-factor Authentication § Two-factor authentication (2 FA) provides increased 2 FA Option Assurance Level § Protects against: Duo Mobile app High U 2 F token High OTP token Moderate-High SMS Low-Moderate Phone Call Low-Moderate None (static password only) Low security beyond a static password § Phishing § Re-used passwords that are compromised § Duo Security has been selected as the university 2 FA provider § Self-serve enrollment and 2 FA device management (https: //uwaterloo. ca/2 fa) § Friday morning seminars: February 9, 2018 (https: //uwaterloo. ca/it-professional-development-advisory-group/it-seminar-duo-two-factorauthenticaion-service) and June 1, 2018 (https: //uwaterloo. ca/it-professional-development-advisory-group/it-seminar-duo-two-factor-sequel) § 2 FA Knowledge Base (https: //uwaterloo. teamdynamix. com/TDClient/KB/? Category. ID=11579)
SAML § Security Assertion Markup Language § An open standard for authentication and authorization data exchange § A trust is established between the identity provider and the service provider (application) to allow authentication transactions to occur § At login time, identity attributes can be asserted to the application, reducing the need for batch consumption of identity data
CAS § CAS simply provides a successful/unsuccessful authentication, with some support for SAML 1. 1 attribute release § Any application can make use of CAS authentication, without any configuration required in CAS § CAS use on campus should be considered deprecated § Plan to migrate applications to authenticate with ADFS (or Shibboleth)
Shibboleth § SAML 2. 0 § Not configured for SSO (1 minute session timeout on Id. P) § Doesn’t provide 2 FA integration § Most extensive set of identity data for assertions § Username (scoped or not), campus email address, given name, student number, HRID, nexus group membership, unique identity identifiers, affiliation (student, faculty, staff, alumni, etc. ) § Only supported during business hours
ADFS § SAML 2. 0/WS-Federation § Provides SSO (24 hour session) § Can include login-time 2 FA § Currently can only assert identity attributes from Nexus, EDU § Will soon be able to assert any of the identity attributes available to Shibboleth § 1 global 2 FA policy from Duo § IST provides some off-hours support
Duo Access Gateway § Provides login-time 2 FA with Shibboleth authentication § A SAML proxy between Id. P and Service Provider that can interject a 2 FA challenge § Mechanism to integrate Duo 2 FA for applications that support SAML, but lack native 2 FA support § Allows custom 2 FA policies per application
Which Option is Right for You?
ADFS or Shibboleth? § Go with ADFS unless: § You require identity attributes asserted that ADFS can’t provide (use Shibboleth)
Duo for [x], Duo ADFS, or Duo Access Gateway? § If your application has delivered Duo integration, use that (Duo for OWA) § If you want step-up Duo challenges, you need Duo integration with your app directly (Duo for [x] for some apps or the Auth API) § If you have ADFS auth and the standard Duo policy is appropriate, use Duo ADFS § If you have unique policy requirements: § Purchased applications: use Duo Access Gateway § Built applications: § Using SAML auth: use Duo Access Gateway § Otherwise: Auth API
Adding 2 FA to Your Application
Web Applications § ADFS/Shibboleth § duo web § Direct integration § Additional Tools
Using ADFS/Shib/Duo Auth Gateway § Apache § mod_auth_mellon, mod_shib (shibboleth only) § PHP § Simple. SAMLphp § Django § djangosaml 2, django-saml-auth, python-saml § Node. js § saml 2 -js …
Duo Web § Create a sign request § Show iframe using Java. Script provided by Duo § Verify response and proceed
Duo Client and Auth API § https: //github. com/duosecurity § Python § Java. Script § PHP § Go § C# § Node. js § Java § Ruby § Perl § Cold. Fusion § ASP. NET § C § …
Duo Client and Auth API § Check if user is authorized to login (based on Duo settings/groups) and retrieve available devices § Present user with selection from devices § Authenticate with selected option
Additional Tools § A few tools that I have worked on for UW (Django specific tools) § https: //git. uwaterloo. ca/uw_django/duo_auth § Library for quickly adding duo to your Django application § @duo_required decorator for views § https: //git. uwaterloo. ca/uw_django/uw_saml_tools § Library for working with SAML authentication in Django § Sync NEXUS groups with Django groups on login § More in the future as needed… § https: //git. uwaterloo. ca/uw_django_templates § Not related to 2 fa or SAML, but helpful for those using Django.
Desktop Applications and Scripts § SSH and/or Linux Desktop (duounix) § Windows (Local Login or RDP) § Mac OSX (Graphical Login only, for SSH, uses duounix) § In house desktop application (use client and auth libraries, similar to web)
Demo
QUESTIONS? amward@uwaterloo. ca ryan. goggin@uwaterloo. ca