Politecnico di Torino Dipartimento di Automatica ed Informatica
- Slides: 29
Politecnico di Torino Dipartimento di Automatica ed Informatica TORSEC Group Performance of Xen’s Secured Virtual Networks Emanuele Cesena Paolo Carlo Pomi Gianluca Ramunno Davide Vernizzi <cesena@mat. uniroma 3. it> <paolo. pomi@polito. it> <ramunno@polito. it> <davide. vernizzi@polito. it>
Outline n n n Introduction Experiments Model Security mechanism Conclusion
Introduction
Motivations n Server consolidation n Planning n Model of virtual network n Emulation n Comparison
Virtualization n “Technique for dividing the resources of a computer into multiple execution environments called virtual machines (VMs)” (A. Singh) n Full virtualization n Complete emulation of the underlying hardware n Unmodified operating system in the VM n Paravirtualization n VM needs a modified OS n Best performance, close to native
Virtualization: XEN n XEN is a free Virtual Machines Monitor (hypervisor) n x 86, Intel Itanium, Power. PC platforms n Paravirtualization, full virtualization (hw support) n Very low overhead when paravirtualized: average 3 -5% n Virtual machines n Domain-0: privileged VM n Direct access to hardware n Direct interface to the hypervisor n Guest domains
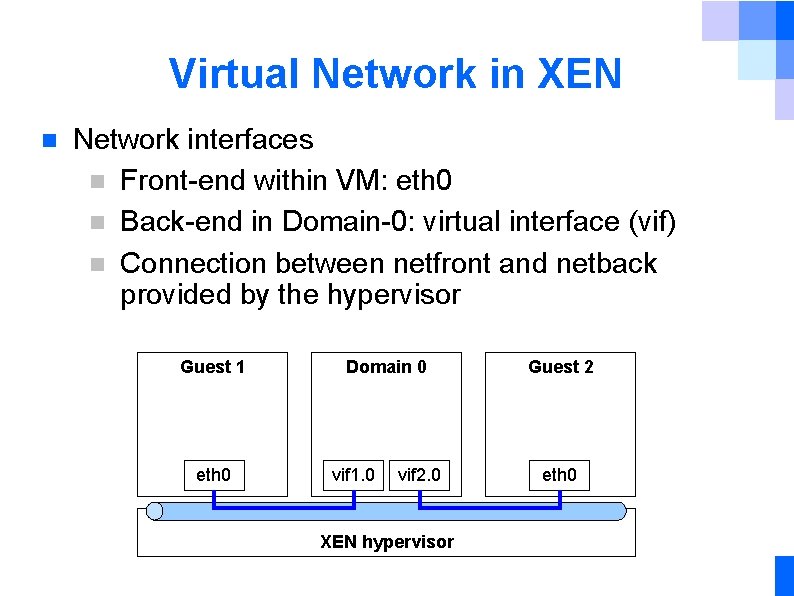
Virtual Network in XEN n Network interfaces n Front-end within VM: eth 0 n Back-end in Domain-0: virtual interface (vif) n Connection between netfront and netback provided by the hypervisor Guest 1 eth 0 Domain 0 vif 1. 0 vif 2. 0 XEN hypervisor Guest 2 eth 0
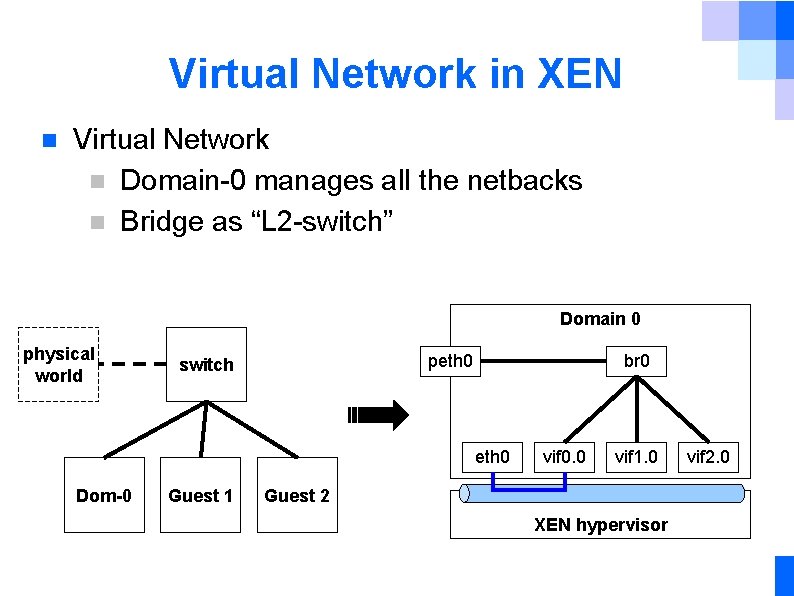
Virtual Network in XEN n Virtual Network n Domain-0 manages all the netbacks n Bridge as “L 2 -switch” Domain 0 physical world peth 0 switch br 0 eth 0 Dom-0 Guest 1 vif 0. 0 vif 1. 0 Guest 2 XEN hypervisor vif 2. 0
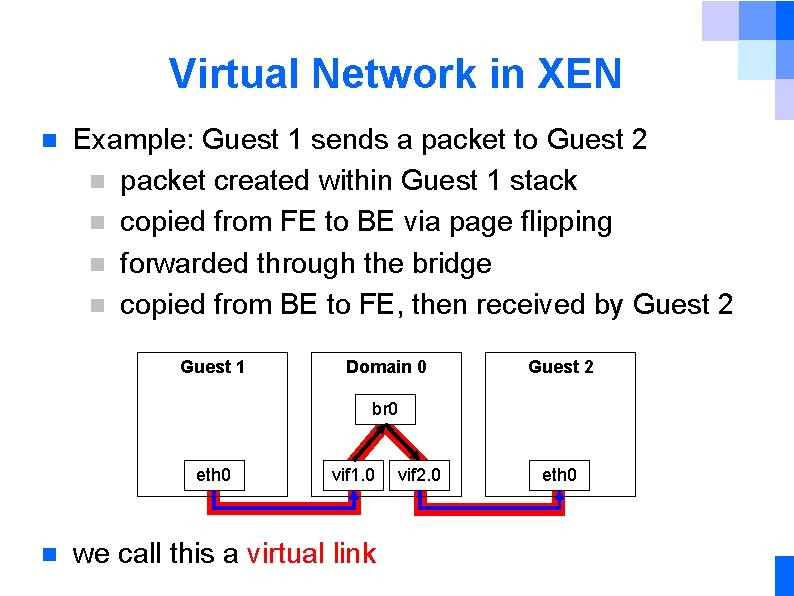
Virtual Network in XEN n Example: Guest 1 sends a packet to Guest 2 n packet created within Guest 1 stack n copied from FE to BE via page flipping n forwarded through the bridge n copied from BE to FE, then received by Guest 2 Guest 1 Domain 0 Guest 2 br 0 eth 0 n vif 1. 0 we call this a virtual link vif 2. 0 eth 0
Experiments
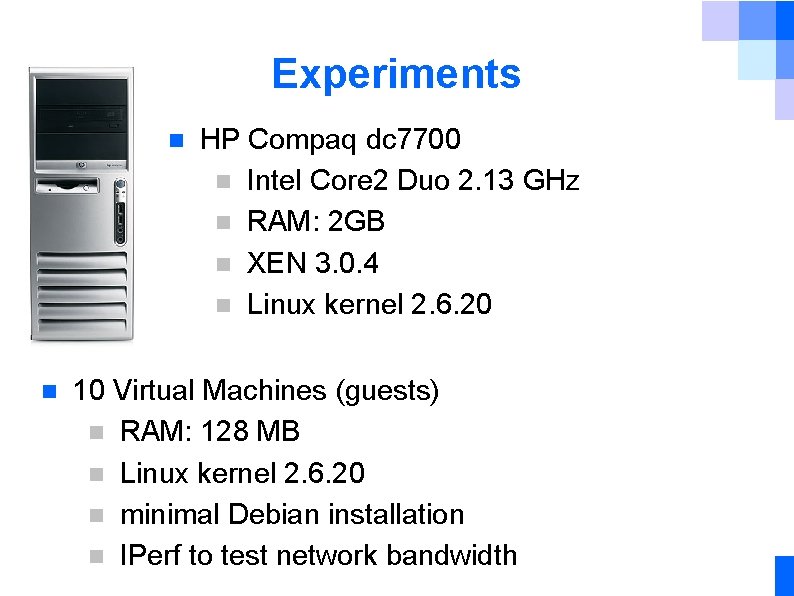
Experiments n n HP Compaq dc 7700 n Intel Core 2 Duo 2. 13 GHz n RAM: 2 GB n XEN 3. 0. 4 n Linux kernel 2. 6. 20 10 Virtual Machines (guests) n RAM: 128 MB n Linux kernel 2. 6. 20 n minimal Debian installation n IPerf to test network bandwidth
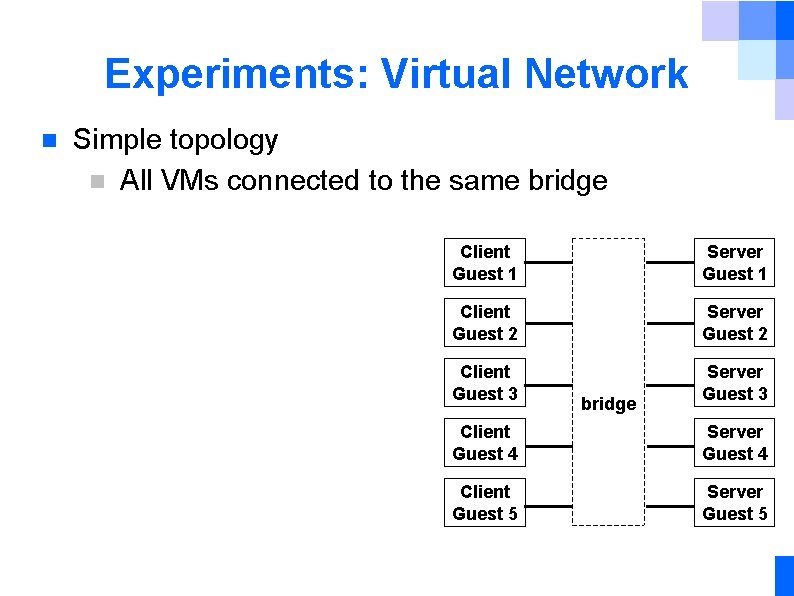
Experiments: Virtual Network n Simple topology n All VMs connected to the same bridge Client Guest 1 Server Guest 1 Client Guest 2 Server Guest 2 Client Guest 3 Server Guest 3 bridge Client Guest 4 Server Guest 4 Client Guest 5 Server Guest 5
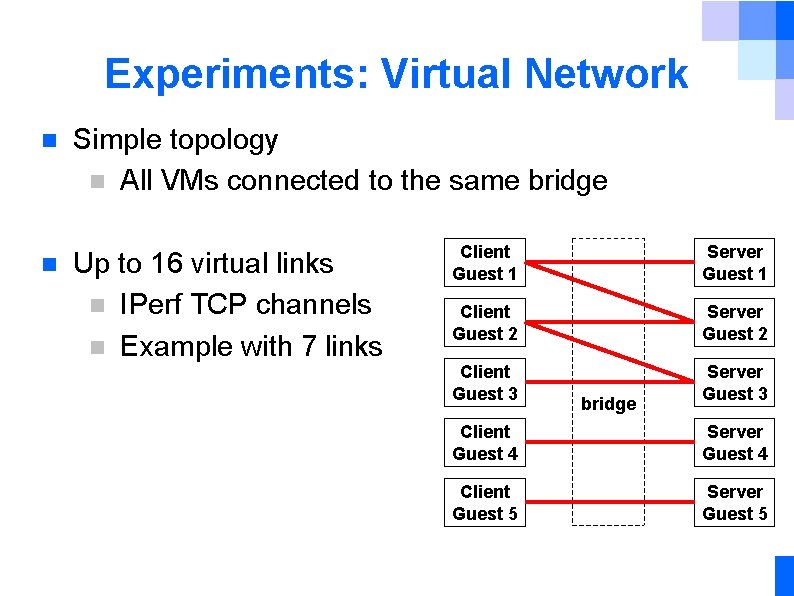
Experiments: Virtual Network n n Simple topology n All VMs connected to the same bridge Up to 16 virtual links n IPerf TCP channels n Example with 7 links Client Guest 1 Server Guest 1 Client Guest 2 Server Guest 2 Client Guest 3 Server Guest 3 bridge Client Guest 4 Server Guest 4 Client Guest 5 Server Guest 5
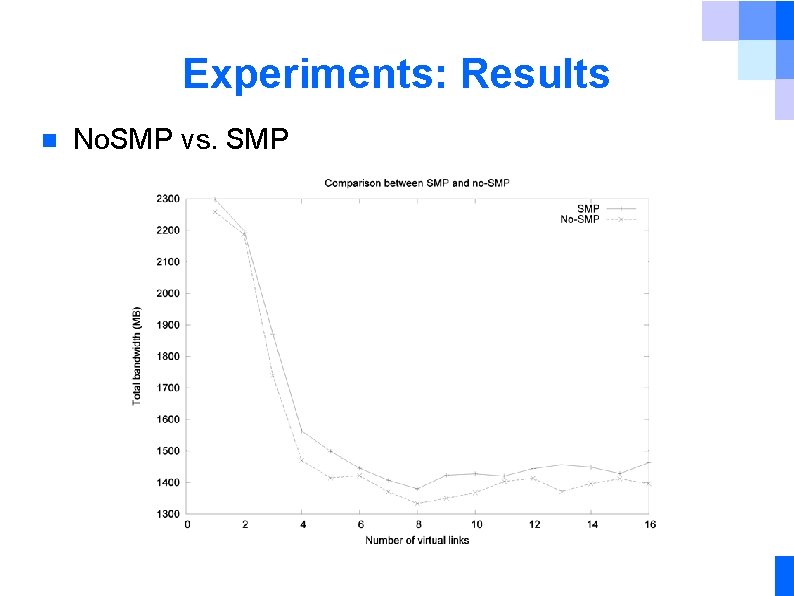
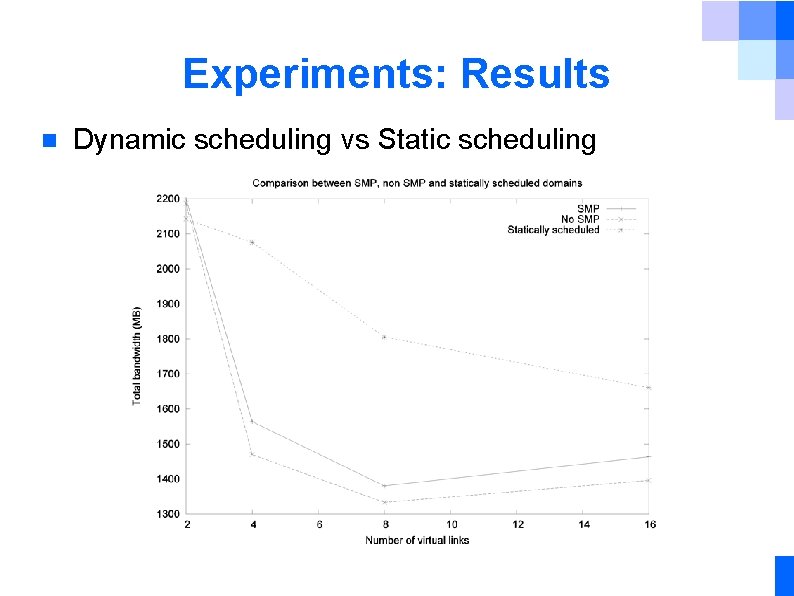
Experiments: tests n n SMP disabled SMP enabled Static domain scheduling 10 iterations for each experiment n 1 minute per link n Samples every 5 sec n Average value
Experiments: Results n No. SMP vs. SMP
Experiments: Results n Dynamic scheduling vs Static scheduling
Model
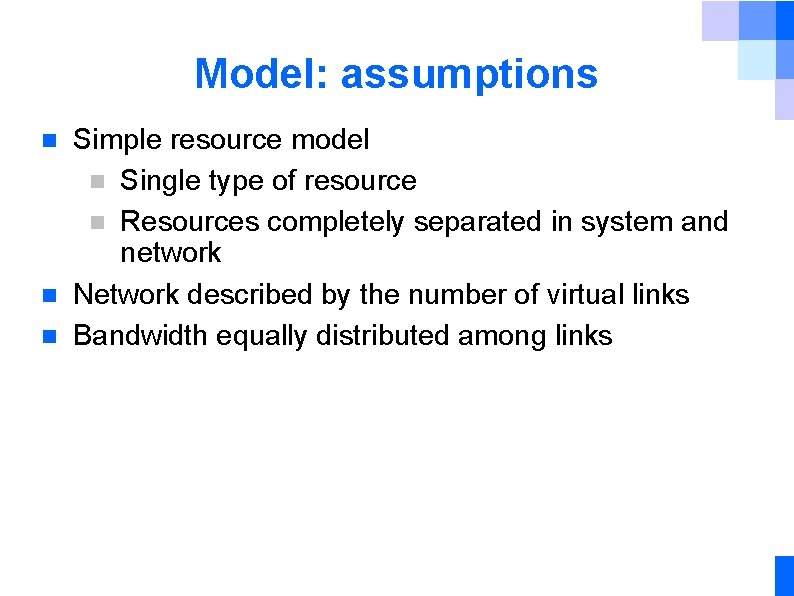
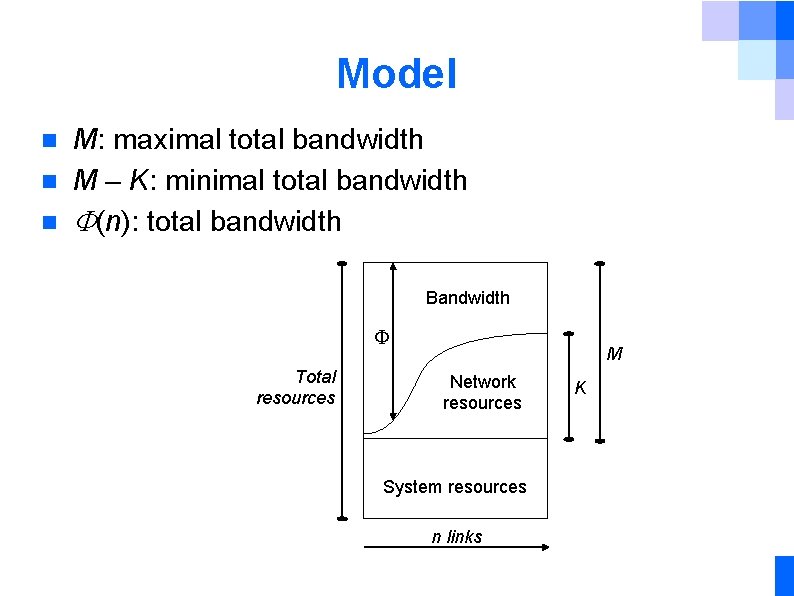
Model: assumptions n n n Simple resource model n Single type of resource n Resources completely separated in system and network Network described by the number of virtual links Bandwidth equally distributed among links
Model n n n M: maximal total bandwidth M – K: minimal total bandwidth F(n): total bandwidth Bandwidth F Total resources M Network resources System resources n links K
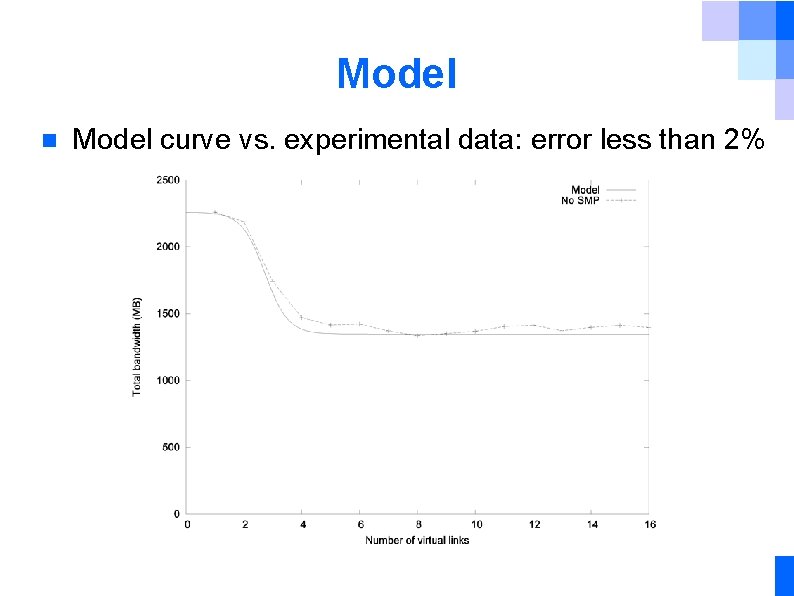
Model n Model curve vs. experimental data: error less than 2%
Security mechanisms
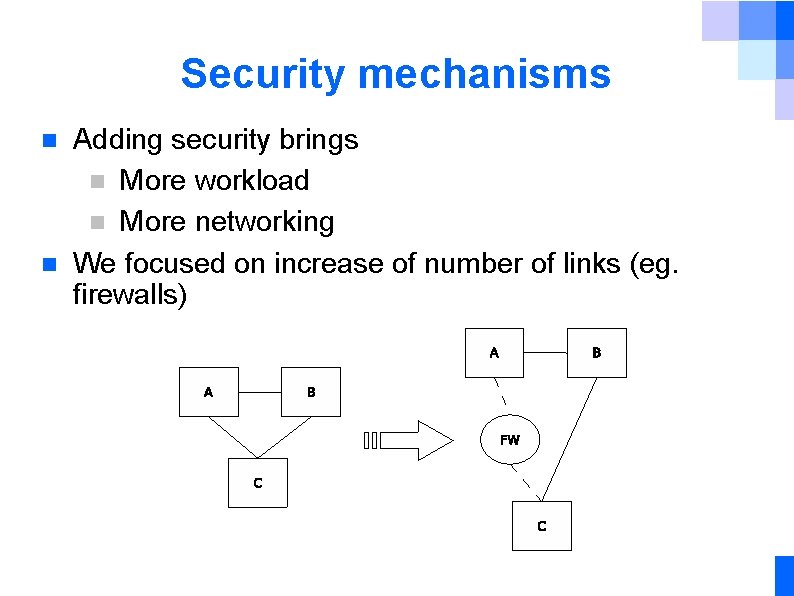
Security mechanisms n n Adding security brings n More workload n More networking We focused on increase of number of links (eg. firewalls)
Security mechanisms n n Number of links increases by a factor s n Depending on topology n Depending on the security mechanism The model allows prediction on the loss of bandwidth
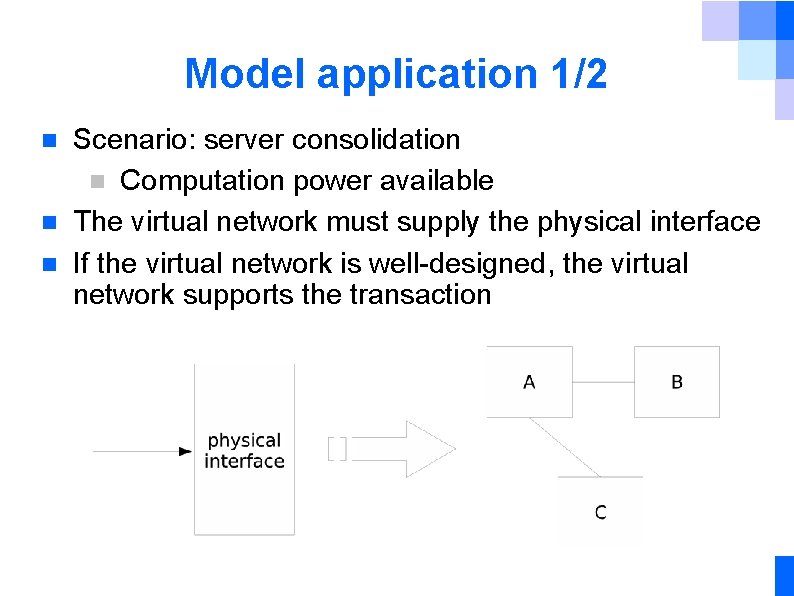
Model application 1/2 n n n Scenario: server consolidation n Computation power available The virtual network must supply the physical interface If the virtual network is well-designed, the virtual network supports the transaction
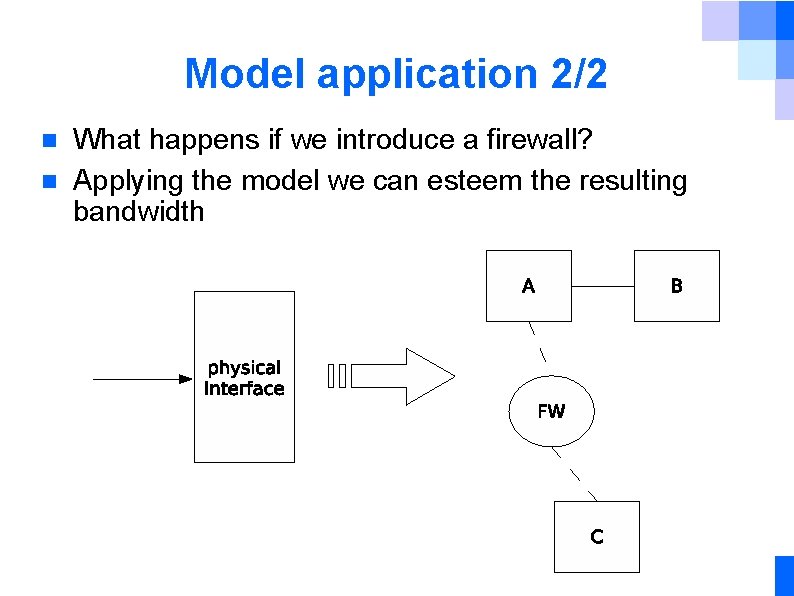
Model application 2/2 n n What happens if we introduce a firewall? Applying the model we can esteem the resulting bandwidth
Conclusions
Future works n n n Improve the model n Relax assumptions n Forecast parameters without experiments Validate the model n Other architecture n Other security solutions Improve Xen n D 2 D communication n Optimization
Conclusions n n We developed a simple (but still effective) model n Explain how virtual networks in Xen n Foresee performance of the virtual network n Planning n Impact of security solutions We show the limits of current Xen’s implementation and suggested improvements
Thank you Any question?