FISMA Privacy Reporting Requirements United States Pacific Command
- Slides: 29
FISMA Privacy Reporting Requirements United States Pacific Command (USPACOM) FOIA & Privacy Act Conference Presented by Samuel P. Jenkins, Director for Privacy, Defense Privacy & Civil Liberties Office January 2011
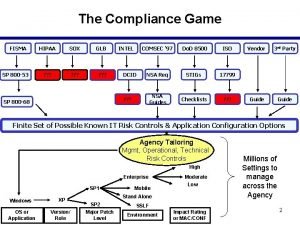
FISMA & Privacy Reporting Requirements Agenda n n n Federal Information Security Management Act (FISMA) – Division of Responsibilities FISMA Purpose The Reporting Requirements as found in the OMB A 130, Appendix I The eleven questions that report on annual Agency Privacy Program Oversight FISMA Annual Report to Congress PACOM Conference 2
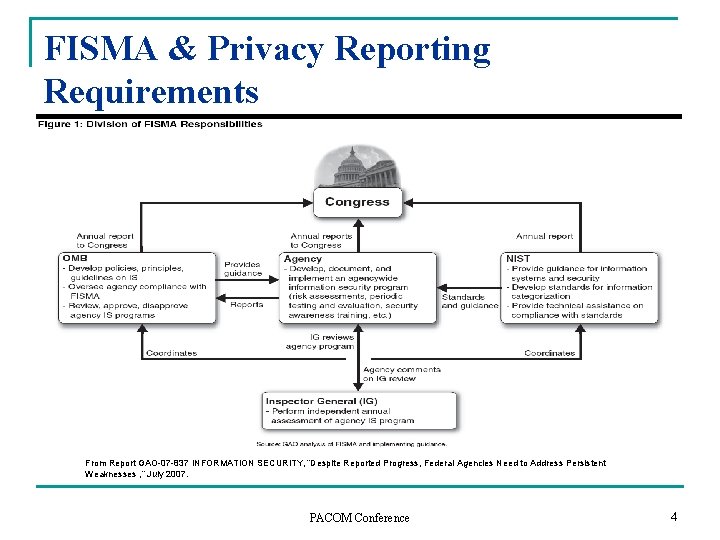
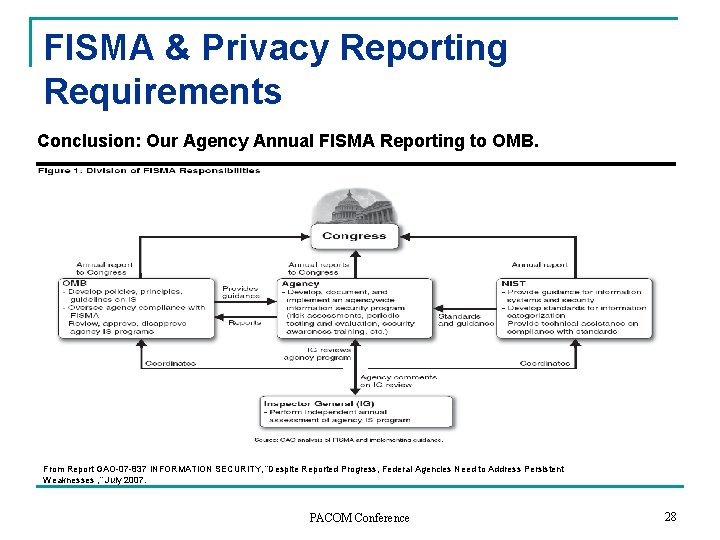
FISMA & Privacy Reporting Requirements Federal Information Security Management Act (FISMA) Division of Responsibilities PACOM Conference 3
FISMA & Privacy Reporting Requirements From Report GAO-07 -837 INFORMATION SECURITY, “Despite Reported Progress, Federal Agencies Need to Address Persistent Weaknesses , “ July 2007. PACOM Conference 4
FISMA & Privacy Reporting Requirements Federal Information Security Management Act Purpose PACOM Conference 5
FISMA & Privacy Reporting Requirements Origin of FISMA The E-Government Act (Public Law 107 -347) passed by the 107 th Congress and signed into law by the President in December 2002. n Recognized the importance of information security to the economic and national security interests of the United States. PACOM Conference 6
FISMA & Privacy Reporting Requirements Title III of the E-Government Act, entitled the Federal Information Security Management Act of 2002 (FISMA) requires: n n Each federal agency to develop, document, and implement an agency-wide program to provide information security for the information and information systems that support the operations and assets of the agency, including those provided or managed by another agency, contractor, or other source. FISMA, along with the Paperwork Reduction Act of 1995 and the Information Technology Management Reform Act of 1996 (Clinger. Cohen Act), explicitly emphasizes a risk-based policy for costeffective security. PACOM Conference 7
FISMA & Privacy Reporting Requirements In support of and reinforcing this legislation, the Office of Management and Budget (OMB) through Circular A-130, Appendix III, Security of Federal Automated Information Resources, requires executive agencies within the federal government to: n n Plan for security Ensure that appropriate officials are assigned security responsibility Periodically review the security controls in their information systems Authorize system processing prior to operations and, periodically, thereafter PACOM Conference 8
FISMA & Privacy Reporting Requirements In June 2005, OMB issued memo M-05 -15, “FY 2005 Reporting Instructions for the Federal Information Security Management Act and Agency Privacy Management” which: n n Initiated a number of questions regarding agency’s privacy program (Section D of the report) Senior Agency Official for Privacy. These questions related, in part, to agency implementation of the privacy provisions of the EGovernment Act of 2002. PACOM Conference 9
FISMA & Privacy Reporting Requirements In April 2010, OMB issued memo M-10 -15 “FY 2010 Reporting Instructions for the Federal Information Security Management Act and Agency Privacy Management ” which formed a comprehensive context for security and privacy of Federal information across government to include: n n The number of each type of privacy reviews conducted during the last fiscal year; Information about the advice-formal written policies, procedures, guidance, or interpretations of privacy requirements. PACOM Conference 10
FISMA & Privacy Reporting Requirements OMB memo M-10 -15 “FY 2010 Reporting Instructions for the Federal Information Security Management Act and Agency Privacy Management” (Continued) n The number of written complaints for each type of privacy issue allegation received to include: q Process and procedural issues (consent, collection, and appropriate notice); q Redress issues (non-Privacy Act inquiries seeking resolution of difficulties or concerns about privacy matters); or q Operational issues (inquiries regarding Privacy Act matters not including Privacy Act requests for access and/or corrections); n For each type of privacy issue received for alleged privacy violations, the number of complaints the agency referred to another agency with jurisdiction. PACOM Conference 11
FISMA & Privacy Reporting Requirements OMB and Annual FISMA Reporting: Senior Agency Official for Privacy (SAOP) Questions PACOM Conference 12
FISMA & Privacy Reporting Requirements Assignment of Responsibilities OMB Circular No. A-130, “Management of Federal Information Resources, ” November 28, 2000, Appendix 1. 3. a. states: q q All Federal Agencies. In addition…the head of each agency shall ensure that the reviews are conducted as often as specified in the accompanying chart. (next slide) Prepare to report to the Director, OMB, the results of such reviews and the corrective action taken to resolve problems uncovered. PACOM Conference 13
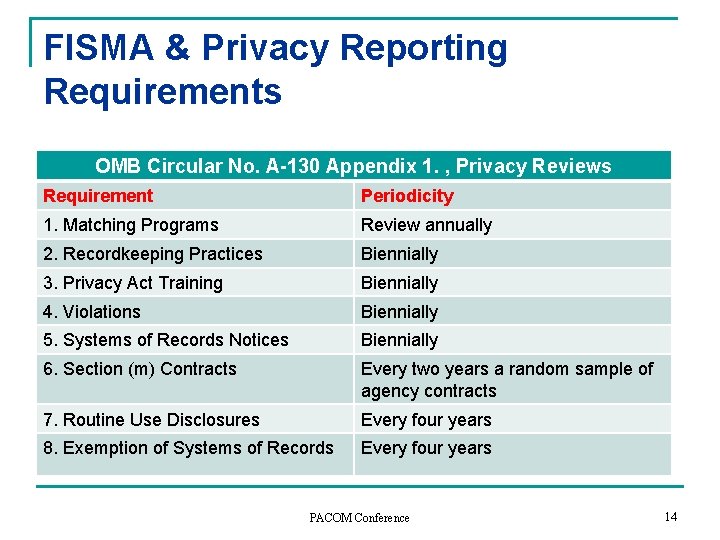
FISMA & Privacy Reporting Requirements OMB Circular No. A-130 Appendix 1. , Privacy Reviews Requirement Periodicity 1. Matching Programs Review annually 2. Recordkeeping Practices Biennially 3. Privacy Act Training Biennially 4. Violations Biennially 5. Systems of Records Notices Biennially 6. Section (m) Contracts Every two years a random sample of agency contracts 7. Routine Use Disclosures Every four years 8. Exemption of Systems of Records Every four years PACOM Conference 14
FISMA & Privacy Reporting Requirements Question 1: Information Security Systems Identify: n n n the number of agency and contractors systems that contain Federal information in identifiable form the number of agency and contractor systems for which a Privacy Impact Assessment (PIA) is required under the E-Gov Act the number of agency and contractor systems covered by an existing PIA the number of systems for which a system of records notice (SORN) is required under the Privacy Act the number of systems for which a current SORN has been published in the Federal Register PACOM Conference 15
FISMA & Privacy Reporting Requirements Question 2: Links to PIAs and SORNS n n Provide the URL of the centrally located page on the agency web site listing working links to agency PIAs. Provide the URL of the centrally located page on the agency web site listing working links to the published SORNs. PACOM Conference 16
FISMA & Privacy Reporting Requirements Question 3: Senior Agency Official for Privacy (SAOP) Responsibilities Yes or No—Can your agency demonstrate through documentation that the privacy official: n Participates in all agency information privacy compliance activities (i. e. , privacy policy as well as IT information policy); n Participates in evaluating the privacy implications of legislative, regulatory, and other policy proposals, as well as testimony and comments under OMB Circular A-19; n Participates in assessing the impact of the agency’s use of technology on privacy and the protection of personal information? PACOM Conference 17
FISMA & Privacy Reporting Requirements Question 4: Information Privacy Training and Awareness Does your agency have: n n A policy to ensure that all personnel (employees, contractors, etc. ) with access to Federal data are generally familiar with information privacy laws, regulations and policies, and understand the ramifications of inappropriate access and disclosure? A program for job-specific and comprehensive information privacy training for all personnel (employees, contractors, etc. ) directly involved in the administration of personal information or information technology systems, or with significant information security responsibilities? PACOM Conference 18
FISMA & Privacy Reporting Requirements Question 5: Does the agency have a written policy or process for each of the following? PIA Practices: n Determining whether a PIA is needed n Conducting a PIA n Evaluating changes in technology or business practices that are identified during the PIA process n Ensuring systems owners, privacy officials, and IT experts participate in conducting the PIA n Making PIAs available to the public as required by law and OMB policy n Monitoring the agency’s systems and practices to determine when and how PIAs should be updated n Assessing the quality and thoroughness of each PIA and performing reviews to ensure that appropriate standards for PIA are maintained PACOM Conference 19
FISMA & Privacy Reporting Requirements Question 5: Does the agency have a written policy or process for each of the following web privacy practices? n n n Determining circumstances where the agency’s webbased activities warrant additional consideration of privacy implications Making appropriate updates and ensuring continued compliance with stated web privacy policies Requiring machine-readability of public-facing agency web sites (i. e. use of P 3 P) PACOM Conference 20
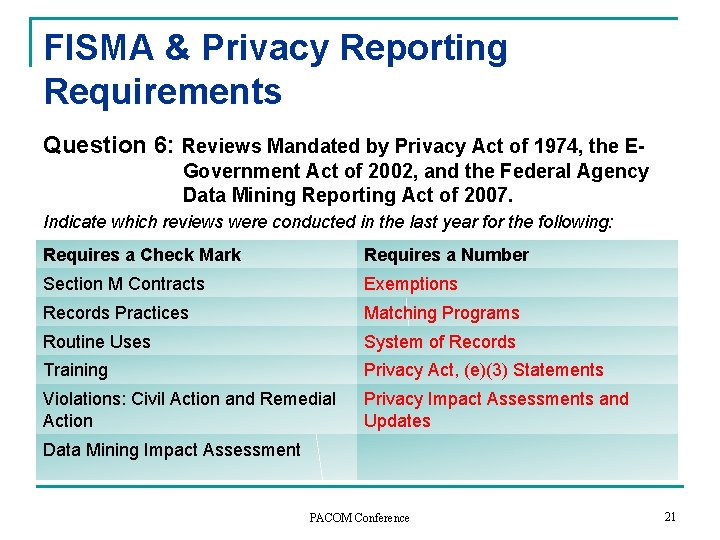
FISMA & Privacy Reporting Requirements Question 6: Reviews Mandated by Privacy Act of 1974, the EGovernment Act of 2002, and the Federal Agency Data Mining Reporting Act of 2007. Indicate which reviews were conducted in the last year for the following: Requires a Check Mark Requires a Number Section M Contracts Exemptions Records Practices Matching Programs Routine Uses System of Records Training Privacy Act, (e)(3) Statements Violations: Civil Action and Remedial Action Privacy Impact Assessments and Updates Data Mining Impact Assessment PACOM Conference 21
FISMA & Privacy Reporting Requirements Question 7: Written Privacy Complaints Indicate the number of written complaints for each type of privacy issue received by the SAOP or others at the agency n n Process and Procedural -- consent, collection, and appropriate notice Redress -- non-Privacy Act inquiries seeking resolution of difficulties or concerns about privacy matters Operational -- inquiries regarding Privacy Act matters not including Privacy Act requests for access and/or correction Referrals – complaints referred to another agency with jurisdiction PACOM Conference 22
FISMA & Privacy Reporting Requirements Question 8: Policy Compliance Review n Does the agency: q q q n have current documentation demonstrating review of compliance with information privacy laws, regulations, and policies? Use technologies that enable continuous auditing of compliance with stated privacy policies and practices? Coordinate with the agency's Inspector General on privacy program oversight? Can the agency provide documentation of planned, in progress, or completed corrective actions necessary to remedy deficiencies identified in compliance reviews? PACOM Conference 23
FISMA & Privacy Reporting Requirements Question 9: Information About Advice Provided by the SAOP (Yes or No) Indicate if the SAOP has provided formal written advice or guidance in each of the listed categories, and briefly describe the advice or guidance if applicable. The categories are: n n n Agency policies, orders, directives, or guidance governing agency handling of personally identifiable information’ Written Agreements (either Interagency or with Non-Federal Entities) pertaining to information sharing, computer matching, and similar issues The agency’s practices for conducting, preparing, and releasing SORNs and PIAs Reviews or feedback outside of the SORN and PIA process (e. g. formal written advice in the context of budgetary or programmatic activities or planning) Privacy Training (either stand-alone or included with training on related issues) q Provide the number of employees (or contractors) who participated in the training. PACOM Conference 24
FISMA & Privacy Reporting Requirements Question 10: Agency Use of Persistent Tracking Technology Indicate Yes or No for each item below: n Does the agency use web management and customization technologies on any web site or application? n Does the agency annually review the use of web management and customization technologies to ensure compliance with all laws, regulations, and OMB guidance? n Can the agency demonstrate, with documentation, the continued justification for, and approval to use, web management and customization technologies? n Can the agency provide the notice language or citation for the web privacy policy that informs visitors about the use of web management and customization technologies? PACOM Conference 25
FISMA & Privacy Reporting Requirements Question 11: Privacy Points of Contact Information Please provide the names, phone numbers, and e-mail addresses of the following officials: Agency Head Chief Privacy Officer Chief Information Officer Privacy Advocate Agency Inspector General Privacy Act Officer Chief Information Security Officer Reviewing Official for PIAs Senior Agency Official for Privacy POC for URL links provided in question #2 PACOM Conference 26
FISMA & Privacy Reporting Requirements Federal Information Security Management Act (FISMA) Privacy Reporting at the Agency Level PACOM Conference 27
FISMA & Privacy Reporting Requirements Conclusion: Our Agency Annual FISMA Reporting to OMB. From Report GAO-07 -837 INFORMATION SECURITY, “Despite Reported Progress, Federal Agencies Need to Address Persistent Weaknesses , “ July 2007. PACOM Conference 28
Resources n n n OMB Memorandum M-10 -15, of April 21, 2010 “FY 2010 Reporting Instructions for the Federal Information Security Management Act and Agency Privacy Management. ” Office of Management and Budget Circular No. A-130, November 28, 2000 “Management of Federal Information Resources” Federal Information Security Management Act of 2002 (Pub. L. 107347). OMB Memorandum M-07 -16, of May 22, 2007 “Safeguarding Against and Responding to the Breach of Personally Identifiable Information. ” FY 2008 Report to Congress on Implementation of The Federal Information Security Management Act of 2002. GAO Report 07 -837: INFORMATION SECURITY, Despite Reported Progress, Federal Agencies Need to Address Persistent Weaknesses, July 2007. PACOM Conference 29