7 Monitoring Analysis Tools Internet Traffic Monitoring and
- Slides: 44
7. Monitoring & Analysis Tools Internet Traffic Monitoring and Analysis: Methods and Applications 1 POSTECH DP&NM Lab.
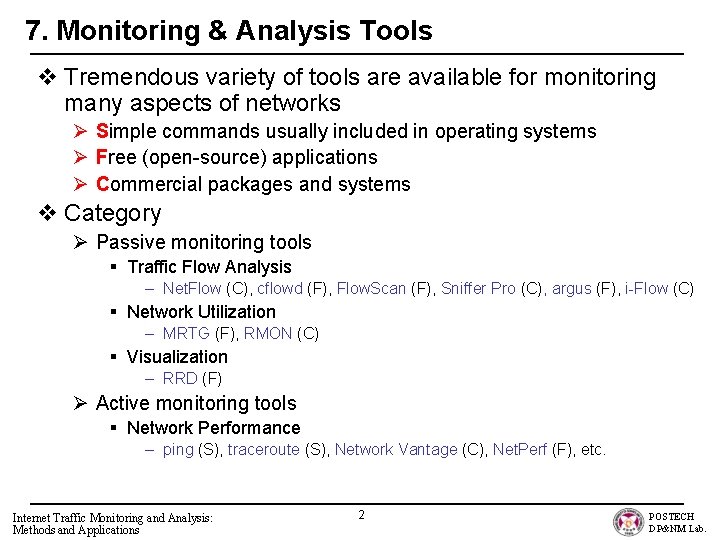
7. Monitoring & Analysis Tools v Tremendous variety of tools are available for monitoring many aspects of networks Ø Simple commands usually included in operating systems Ø Free (open-source) applications Ø Commercial packages and systems v Category Ø Passive monitoring tools § Traffic Flow Analysis – Net. Flow (C), cflowd (F), Flow. Scan (F), Sniffer Pro (C), argus (F), i-Flow (C) § Network Utilization – MRTG (F), RMON (C) § Visualization – RRD (F) Ø Active monitoring tools § Network Performance – ping (S), traceroute (S), Network Vantage (C), Net. Perf (F), etc. Internet Traffic Monitoring and Analysis: Methods and Applications 2 POSTECH DP&NM Lab.
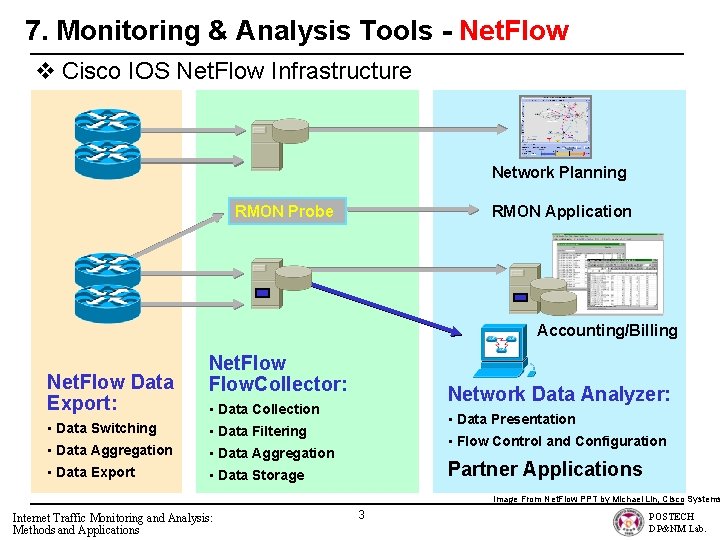
7. Monitoring & Analysis Tools - Net. Flow v Cisco IOS Net. Flow Infrastructure Network Planning RMON Probe RMON Application Accounting/Billing Net. Flow Data Export: Net. Flow. Collector: Network Data Analyzer: • Data Collection • Data Switching • Data Filtering • Data Aggregation • Data Export • Data Storage • Data Presentation • Flow Control and Configuration Partner Applications Image From Net. Flow PPT by Michael Lin, Cisco Systems Internet Traffic Monitoring and Analysis: Methods and Applications 3 POSTECH DP&NM Lab.
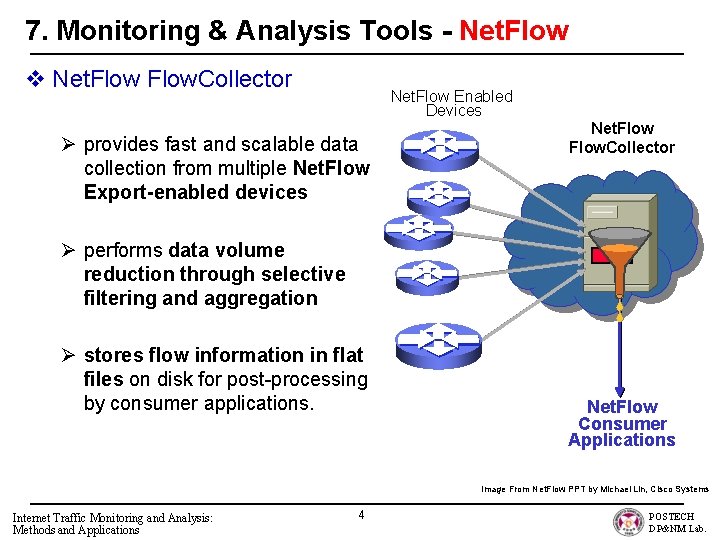
7. Monitoring & Analysis Tools - Net. Flow v Net. Flow. Collector Net. Flow Enabled Devices Ø provides fast and scalable data collection from multiple Net. Flow Export-enabled devices Net. Flow. Collector Ø performs data volume reduction through selective filtering and aggregation Ø stores flow information in flat files on disk for post-processing by consumer applications. Net. Flow Consumer Applications Image From Net. Flow PPT by Michael Lin, Cisco Systems Internet Traffic Monitoring and Analysis: Methods and Applications 4 POSTECH DP&NM Lab.
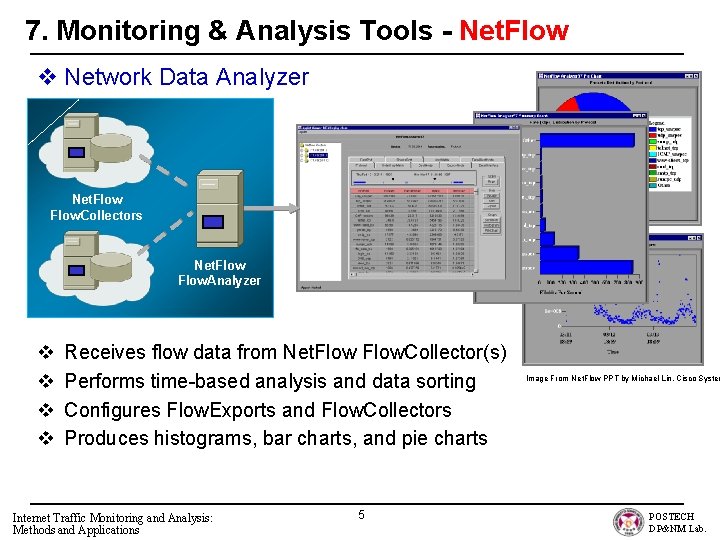
7. Monitoring & Analysis Tools - Net. Flow v Network Data Analyzer Net. Flow. Collectors Net. Flow. Analyzer v v Receives flow data from Net. Flow. Collector(s) Performs time-based analysis and data sorting Configures Flow. Exports and Flow. Collectors Produces histograms, bar charts, and pie charts Internet Traffic Monitoring and Analysis: Methods and Applications 5 Image From Net. Flow PPT by Michael Lin, Cisco System POSTECH DP&NM Lab.
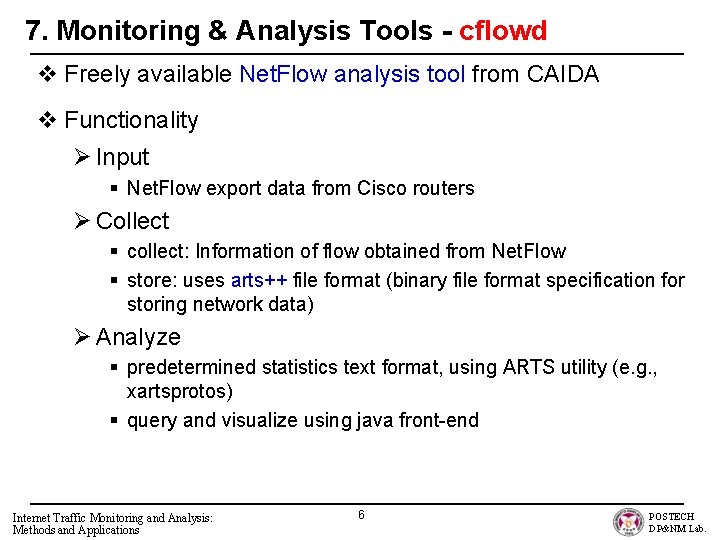
7. Monitoring & Analysis Tools - cflowd v Freely available Net. Flow analysis tool from CAIDA v Functionality Ø Input § Net. Flow export data from Cisco routers Ø Collect § collect: Information of flow obtained from Net. Flow § store: uses arts++ file format (binary file format specification for storing network data) Ø Analyze § predetermined statistics text format, using ARTS utility (e. g. , xartsprotos) § query and visualize using java front-end Internet Traffic Monitoring and Analysis: Methods and Applications 6 POSTECH DP&NM Lab.
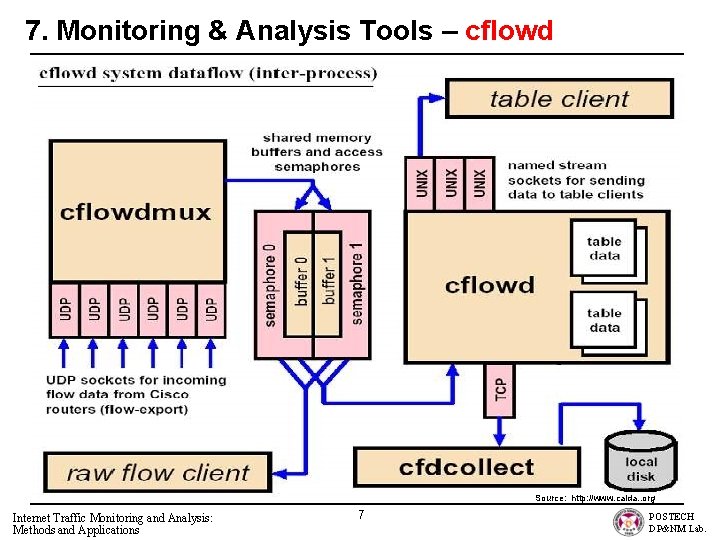
7. Monitoring & Analysis Tools – cflowd Source: http: //www. caida. . org Internet Traffic Monitoring and Analysis: Methods and Applications 7 POSTECH DP&NM Lab.
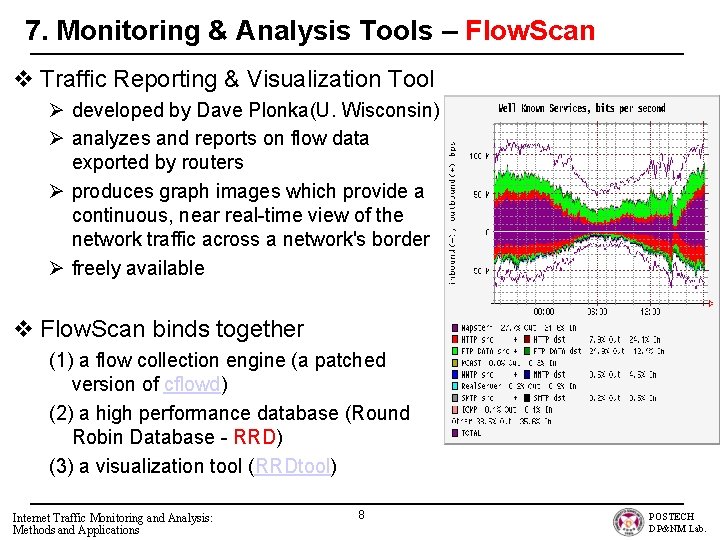
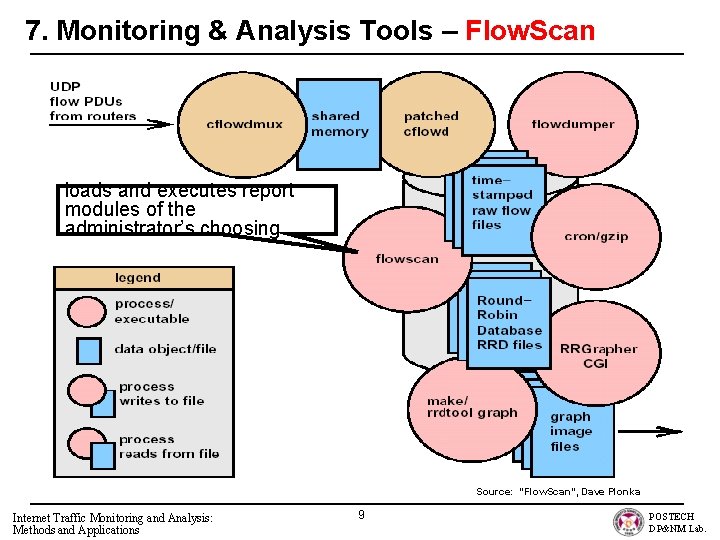
7. Monitoring & Analysis Tools – Flow. Scan v Traffic Reporting & Visualization Tool Ø developed by Dave Plonka(U. Wisconsin) Ø analyzes and reports on flow data exported by routers Ø produces graph images which provide a continuous, near real-time view of the network traffic across a network's border Ø freely available v Flow. Scan binds together (1) a flow collection engine (a patched version of cflowd) (2) a high performance database (Round Robin Database - RRD) (3) a visualization tool (RRDtool) Internet Traffic Monitoring and Analysis: Methods and Applications 8 POSTECH DP&NM Lab.
7. Monitoring & Analysis Tools – Flow. Scan loads and executes report modules of the administrator’s choosing Source: “Flow. Scan”, Dave Plonka Internet Traffic Monitoring and Analysis: Methods and Applications 9 POSTECH DP&NM Lab.
7. Monitoring & Analysis Tools – arts++ v ART is a binary file format specification for storing network data v ART was initially developed at ANS (American Nuclear Society) by David Bolen (1992) v ARTS was licensed to CAIDA (1998) v ARTS data objects are generally composed of three parts: a header, a list of attributes and a data section v CAIDA has developed a C++ class library for ARTS called arts++ v arts++ Functionality Ø Ø efficient data archival aggregation in the time domain (AS, net, port, protocol, interface. . ) version-specific formats support for iostreams and UNIX file descriptors Internet Traffic Monitoring and Analysis: Methods and Applications 10 POSTECH DP&NM Lab.
7. Monitoring & Analysis Tools – ARGUS v Audit Record Generation and Utilization System Ø A powerful flow-based, passive monitoring tool for IP networks Ø Provides tools for various analysis of network activity § Probe system: argus § Collector/Analysis tools: ra, racount, ragator, ramon, rasort, raxml Ø Developed originally by CMU in 1993, now coordinated by Qo. Sient LLC as open source project § Current Release Version : 2. 0. 5 § Current Developing Version: 2. 0. 6 § http: //www. qosient. com/argus Ø Fixed model Real-Time Flow Monitor after IETF RTFM Internet Traffic Monitoring and Analysis: Methods and Applications 11 POSTECH DP&NM Lab.
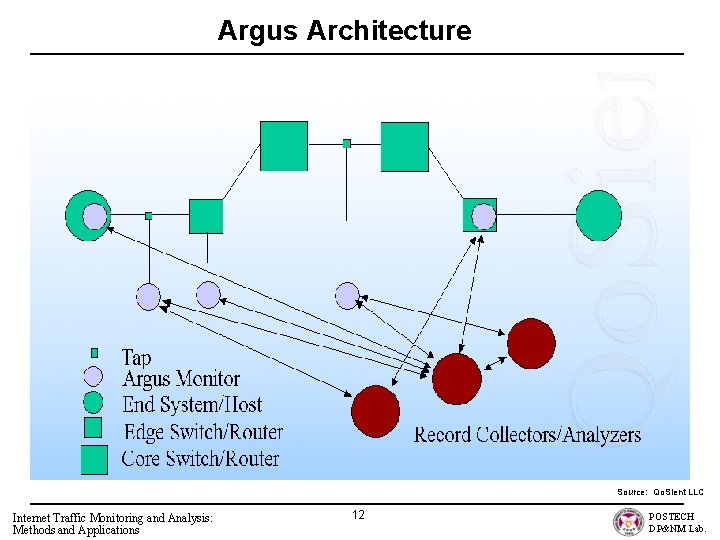
Argus Architecture Source: Qo. Sient LLC Internet Traffic Monitoring and Analysis: Methods and Applications 12 POSTECH DP&NM Lab.
Argus Data Model v Argus flow modeled after IPPM Framework Ø Type-P and Type-P 1 -P 2 flows Ø Bidirectional flow model <- RTFM v Packets of Type-P Ø Defined in RFC 2330 from IETF IPPM WG Ø To remove the ambiguity in the definition of Network Performance Metrics Ø The generic notion where in some contexts P will be explicitly defined(Type-P), partially defined(Type-P 1 P 2), or left generic Ø Example: § IP-connectivity § IP-Type-P-Connectivity, IP-Port-HTTP-Connectivity Internet Traffic Monitoring and Analysis: Methods and Applications 13 POSTECH DP&NM Lab.
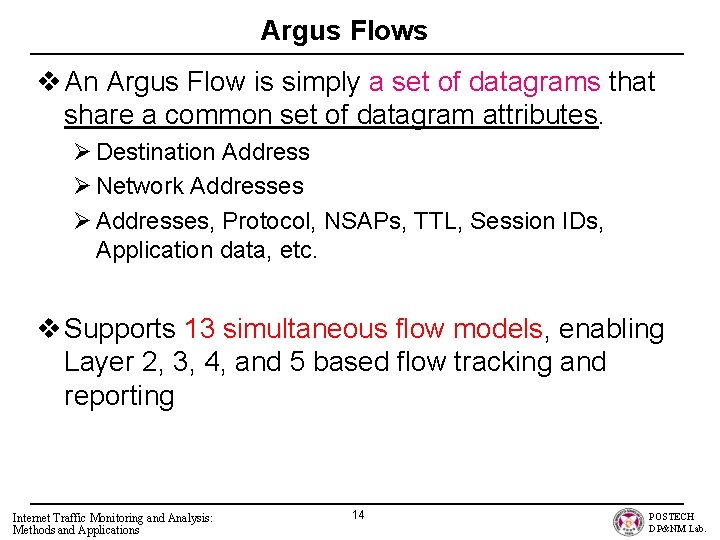
Argus Flows v An Argus Flow is simply a set of datagrams that share a common set of datagram attributes. Ø Destination Address Ø Network Addresses Ø Addresses, Protocol, NSAPs, TTL, Session IDs, Application data, etc. v Supports 13 simultaneous flow models, enabling Layer 2, 3, 4, and 5 based flow tracking and reporting Internet Traffic Monitoring and Analysis: Methods and Applications 14 POSTECH DP&NM Lab.
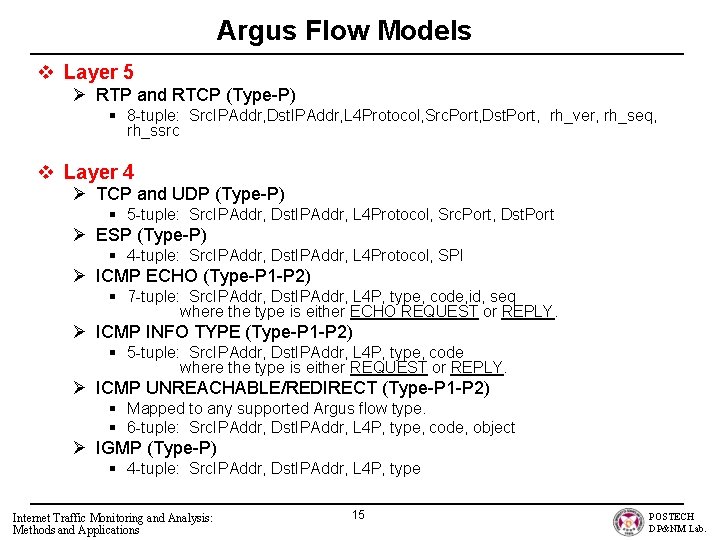
Argus Flow Models v Layer 5 Ø RTP and RTCP (Type-P) § 8 -tuple: Src. IPAddr, Dst. IPAddr, L 4 Protocol, Src. Port, Dst. Port, rh_ver, rh_seq, rh_ssrc v Layer 4 Ø TCP and UDP (Type-P) § 5 -tuple: Src. IPAddr, Dst. IPAddr, L 4 Protocol, Src. Port, Dst. Port Ø ESP (Type-P) § 4 -tuple: Src. IPAddr, Dst. IPAddr, L 4 Protocol, SPI Ø ICMP ECHO (Type-P 1 -P 2) § 7 -tuple: Src. IPAddr, Dst. IPAddr, L 4 P, type, code, id, seq where the type is either ECHO REQUEST or REPLY. Ø ICMP INFO TYPE (Type-P 1 -P 2) § 5 -tuple: Src. IPAddr, Dst. IPAddr, L 4 P, type, code where the type is either REQUEST or REPLY. Ø ICMP UNREACHABLE/REDIRECT (Type-P 1 -P 2) § Mapped to any supported Argus flow type. § 6 -tuple: Src. IPAddr, Dst. IPAddr, L 4 P, type, code, object Ø IGMP (Type-P) § 4 -tuple: Src. IPAddr, Dst. IPAddr, L 4 P, type Internet Traffic Monitoring and Analysis: Methods and Applications 15 POSTECH DP&NM Lab.
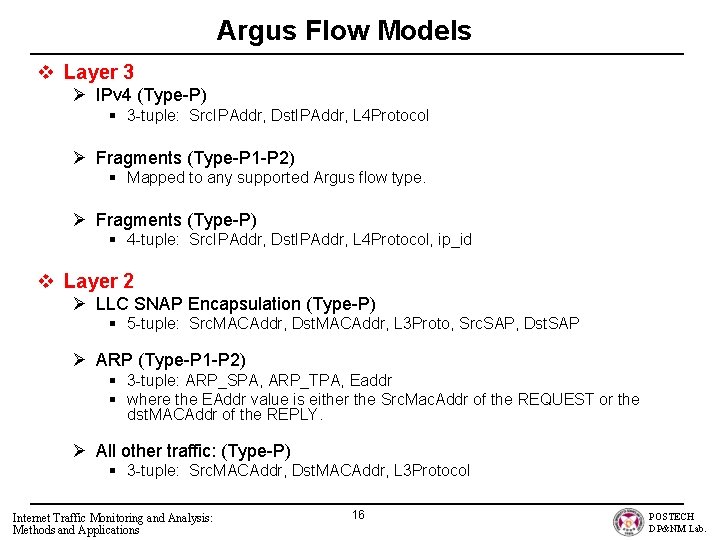
Argus Flow Models v Layer 3 Ø IPv 4 (Type-P) § 3 -tuple: Src. IPAddr, Dst. IPAddr, L 4 Protocol Ø Fragments (Type-P 1 -P 2) § Mapped to any supported Argus flow type. Ø Fragments (Type-P) § 4 -tuple: Src. IPAddr, Dst. IPAddr, L 4 Protocol, ip_id v Layer 2 Ø LLC SNAP Encapsulation (Type-P) § 5 -tuple: Src. MACAddr, Dst. MACAddr, L 3 Proto, Src. SAP, Dst. SAP Ø ARP (Type-P 1 -P 2) § 3 -tuple: ARP_SPA, ARP_TPA, Eaddr § where the EAddr value is either the Src. Mac. Addr of the REQUEST or the dst. MACAddr of the REPLY. Ø All other traffic: (Type-P) § 3 -tuple: Src. MACAddr, Dst. MACAddr, L 3 Protocol Internet Traffic Monitoring and Analysis: Methods and Applications 16 POSTECH DP&NM Lab.
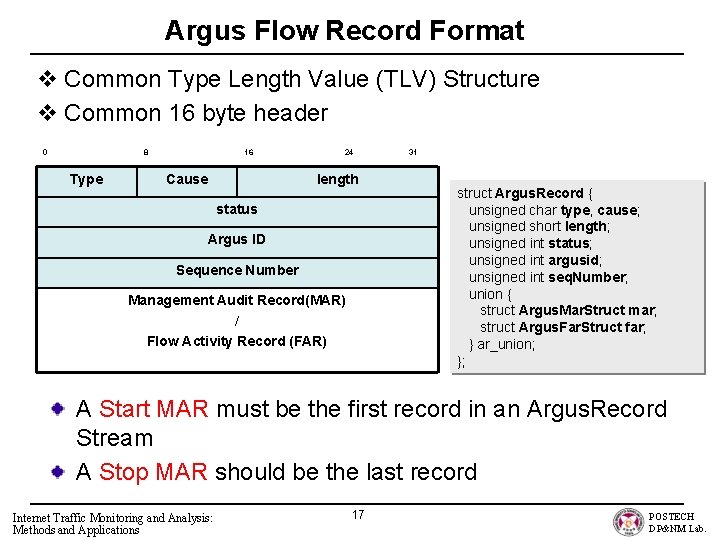
Argus Flow Record Format v Common Type Length Value (TLV) Structure v Common 16 byte header 0 8 Type 16 Cause 24 length status Argus ID Sequence Number Management Audit Record(MAR) / Flow Activity Record (FAR) 31 struct Argus. Record { unsigned char type, cause; unsigned short length; unsigned int status; unsigned int argusid; unsigned int seq. Number; union { struct Argus. Mar. Struct mar; struct Argus. Far. Struct far; } ar_union; }; A Start MAR must be the first record in an Argus. Record Stream A Stop MAR should be the last record Internet Traffic Monitoring and Analysis: Methods and Applications 17 POSTECH DP&NM Lab.
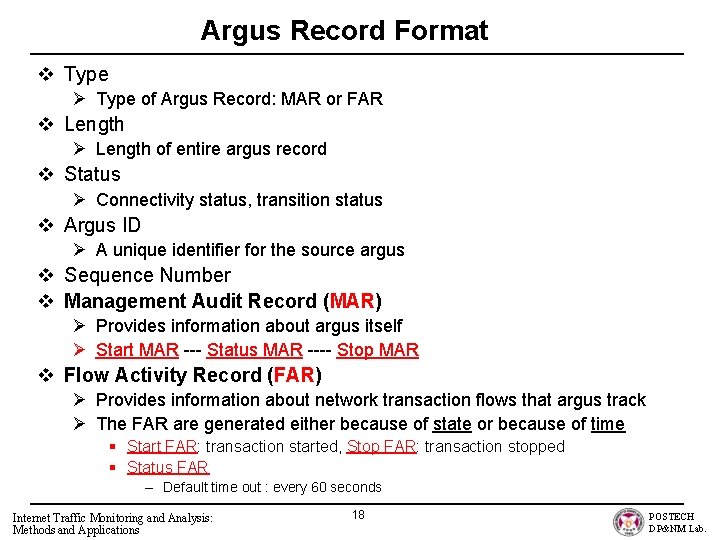
Argus Record Format v Type Ø Type of Argus Record: MAR or FAR v Length Ø Length of entire argus record v Status Ø Connectivity status, transition status v Argus ID Ø A unique identifier for the source argus v Sequence Number v Management Audit Record (MAR) Ø Provides information about argus itself Ø Start MAR --- Status MAR ---- Stop MAR v Flow Activity Record (FAR) Ø Provides information about network transaction flows that argus track Ø The FAR are generated either because of state or because of time § Start FAR: transaction started, Stop FAR: transaction stopped § Status FAR – Default time out : every 60 seconds Internet Traffic Monitoring and Analysis: Methods and Applications 18 POSTECH DP&NM Lab.
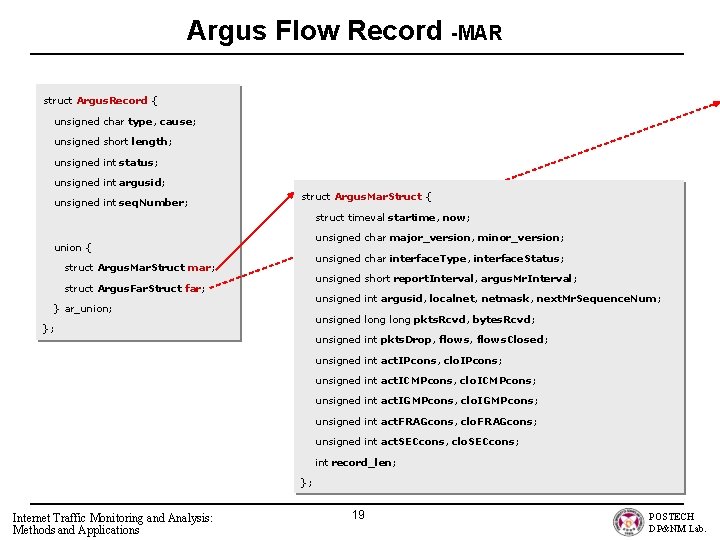
Argus Flow Record -MAR struct Argus. Record { unsigned char type, cause; unsigned short length; unsigned int status; unsigned int argusid; unsigned int seq. Number; struct Argus. Mar. Struct { struct timeval startime, now; union { struct Argus. Mar. Struct mar; struct Argus. Far. Struct far; } ar_union; }; unsigned char major_version, minor_version; unsigned char interface. Type, interface. Status; unsigned short report. Interval, argus. Mr. Interval; unsigned int argusid, localnet, netmask, next. Mr. Sequence. Num; unsigned long pkts. Rcvd, bytes. Rcvd; unsigned int pkts. Drop, flows. Closed; unsigned int act. IPcons, clo. IPcons; unsigned int act. ICMPcons, clo. ICMPcons; unsigned int act. IGMPcons, clo. IGMPcons; unsigned int act. FRAGcons, clo. FRAGcons; unsigned int act. SECcons, clo. SECcons; int record_len; }; Internet Traffic Monitoring and Analysis: Methods and Applications 19 POSTECH DP&NM Lab.
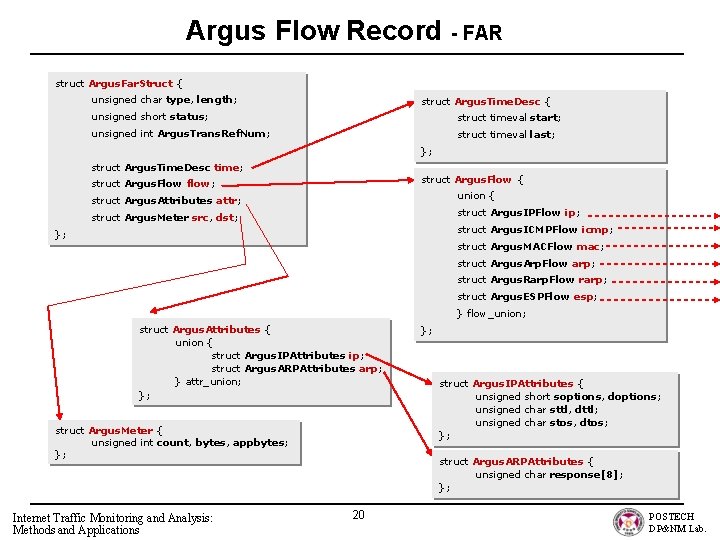
Argus Flow Record - FAR struct Argus. Far. Struct { unsigned char type, length; struct Argus. Time. Desc { unsigned short status; struct timeval start; unsigned int Argus. Trans. Ref. Num; struct timeval last; }; struct Argus. Time. Desc time; struct Argus. Flow { struct Argus. Flow flow; union { struct Argus. Attributes attr; struct Argus. IPFlow ip; struct Argus. Meter src, dst; struct Argus. ICMPFlow icmp; }; struct Argus. MACFlow mac; struct Argus. Arp. Flow arp; struct Argus. Rarp. Flow rarp; struct Argus. ESPFlow esp; } flow_union; struct Argus. Attributes { union { struct Argus. IPAttributes ip; struct Argus. ARPAttributes arp; } attr_union; }; struct Argus. Meter { unsigned int count, bytes, appbytes; }; Internet Traffic Monitoring and Analysis: Methods and Applications }; struct Argus. IPAttributes { unsigned short soptions, doptions; unsigned char sttl, dttl; unsigned char stos, dtos; }; struct Argus. ARPAttributes { unsigned char response[8]; }; 20 POSTECH DP&NM Lab.
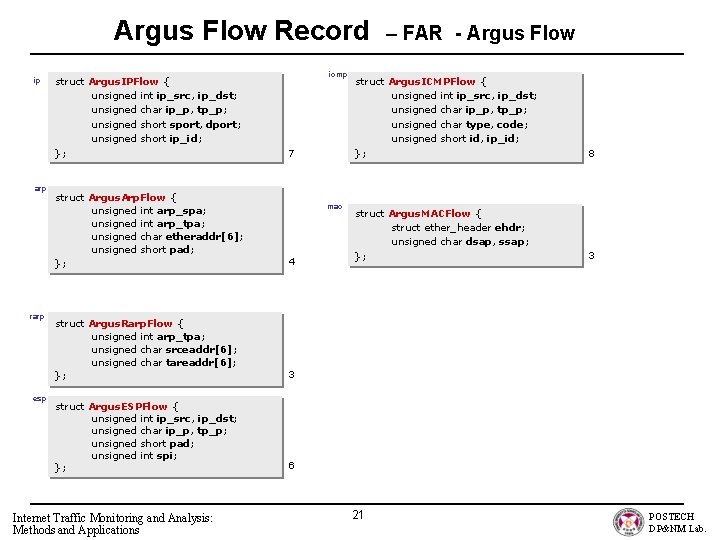
Argus Flow Record ip arp rarp esp struct Argus. IPFlow { unsigned int ip_src, ip_dst; unsigned char ip_p, tp_p; unsigned short sport, dport; unsigned short ip_id; }; icmp 7 struct Argus. Arp. Flow { unsigned int arp_spa; unsigned int arp_tpa; unsigned char etheraddr[6]; unsigned short pad; }; 4 struct Argus. Rarp. Flow { unsigned int arp_tpa; unsigned char srceaddr[6]; unsigned char tareaddr[6]; }; 3 struct Argus. ESPFlow { unsigned int ip_src, ip_dst; unsigned char ip_p, tp_p; unsigned short pad; unsigned int spi; }; 6 Internet Traffic Monitoring and Analysis: Methods and Applications mac – FAR - Argus Flow struct Argus. ICMPFlow { unsigned int ip_src, ip_dst; unsigned char ip_p, tp_p; unsigned char type, code; unsigned short id, ip_id; }; 8 struct Argus. MACFlow { struct ether_header ehdr; unsigned char dsap, ssap; }; 3 21 POSTECH DP&NM Lab.
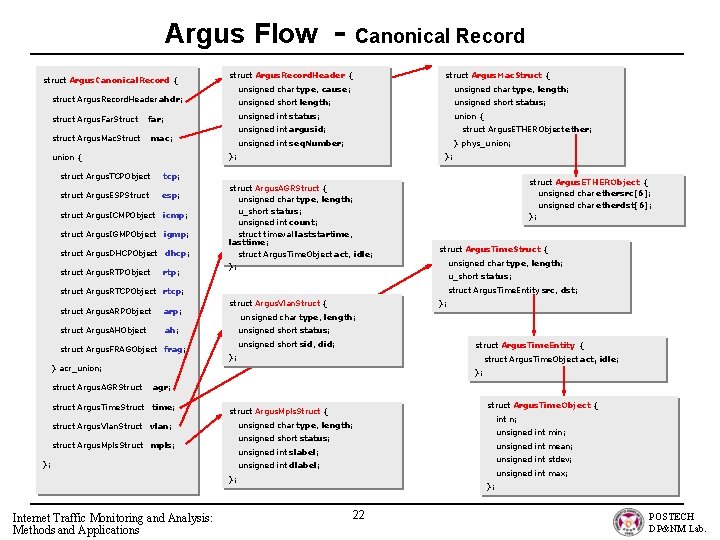
Argus Flow - Canonical Record struct Argus. Record. Header { struct Argus. Mac. Struct { unsigned char type, cause; unsigned char type, length; struct Argus. Record. Header ahdr; unsigned short length; unsigned short status; struct Argus. Far. Struct far; unsigned int status; union { unsigned int argusid; struct Argus. ETHERObject ether; unsigned int seq. Number; } phys_union; }; struct Argus. Canonical. Record { struct Argus. Mac. Struct mac; union { struct Argus. TCPObject tcp; struct Argus. ESPStruct esp; struct Argus. ICMPObject icmp; struct Argus. IGMPObject igmp; struct Argus. DHCPObject dhcp; struct Argus. RTPObject rtp; struct Argus. AGRStruct { unsigned char type, length; u_short status; unsigned int count; struct timeval laststartime, lasttime; struct Argus. Time. Object act, idle; }; struct Argus. AHObject ah; struct Argus. FRAGObject frag; struct Argus. Time. Struct { unsigned char type, length; u_short status; struct Argus. Time. Entity src, dst; struct Argus. RTCPObject rtcp; struct Argus. ARPObject arp; struct Argus. ETHERObject { unsigned char ethersrc[6]; unsigned char etherdst[6]; }; struct Argus. Vlan. Struct { unsigned char type, length; unsigned short status; unsigned short sid, did; struct Argus. Time. Entity { }; struct Argus. Time. Object act, idle; } acr_union; }; struct Argus. AGRStruct agr; struct Argus. Time. Struct time; struct Argus. Vlan. Struct vlan; struct Argus. Mpls. Struct mpls; }; struct Argus. Time. Object { struct Argus. Mpls. Struct { unsigned char type, length; unsigned short status; unsigned int min; unsigned int mean; unsigned int slabel; unsigned int stdev; unsigned int dlabel; unsigned int max; }; Internet Traffic Monitoring and Analysis: Methods and Applications int n; }; 22 POSTECH DP&NM Lab.
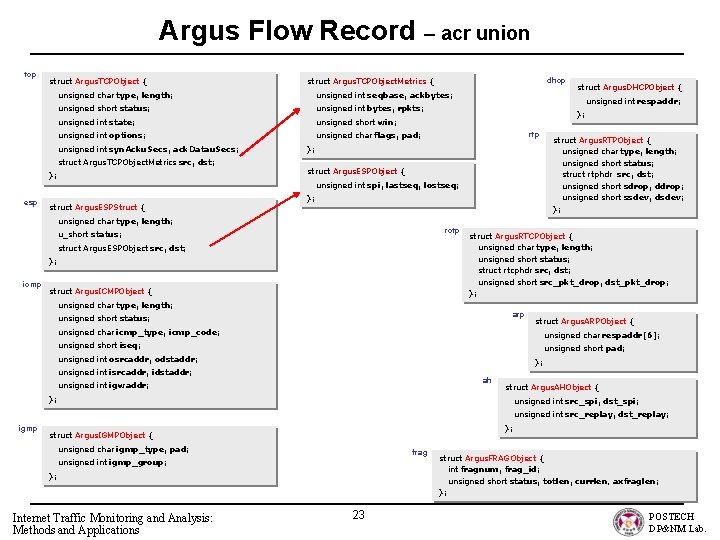
Argus Flow Record – acr union tcp struct Argus. TCPObject. Metrics { unsigned char type, length; unsigned int seqbase, ackbytes; unsigned short status; unsigned int bytes, rpkts; unsigned int state; unsigned short win; unsigned int options; unsigned char flags, pad; unsigned int syn. Acku. Secs, ack. Datau. Secs; }; struct Argus. TCPObject. Metrics src, dst; }; esp dhcp struct Argus. TCPObject { struct Argus. ESPStruct { struct Argus. DHCPObject { unsigned int respaddr; }; rtp struct Argus. ESPObject { unsigned int spi, lastseq, lostseq; }; struct Argus. RTPObject { unsigned char type, length; unsigned short status; struct rtphdr src, dst; unsigned short sdrop, ddrop; unsigned short ssdev, dsdev; }; unsigned char type, length; rctp u_short status; struct Argus. ESPObject src, dst; }; icmp struct Argus. ICMPObject { struct Argus. RTCPObject { unsigned char type, length; unsigned short status; struct rtcphdr src, dst; unsigned short src_pkt_drop, dst_pkt_drop; }; unsigned char type, length; arp unsigned short status; struct Argus. ARPObject { unsigned char icmp_type, icmp_code; unsigned char respaddr[6]; unsigned short iseq; unsigned short pad; unsigned int osrcaddr, odstaddr; }; unsigned int isrcaddr, idstaddr; ah unsigned int igwaddr; }; struct Argus. AHObject { unsigned int src_spi, dst_spi; unsigned int src_replay, dst_replay; igmp }; struct Argus. IGMPObject { unsigned char igmp_type, pad; frag unsigned int igmp_group; }; Internet Traffic Monitoring and Analysis: Methods and Applications 23 struct Argus. FRAGObject { int fragnum, frag_id; unsigned short status, totlen, currlen, axfraglen; }; POSTECH DP&NM Lab.
Argus Transport Model v Record generator (server) supports multiple access methods. Ø Local storage Ø Near-real time record access v Collector (client) initiated associations v TCP based control exchange Ø Proprietary protocol for capability negotiation v TCP or UDP based data transfer v SASL (Simple Authentication and Security Layer, RFC 2222) mediated security Internet Traffic Monitoring and Analysis: Methods and Applications 24 POSTECH DP&NM Lab.
Access Methods v Local Storage Ø Information Base for Transport Reliability § Enable retransmission capability § Support guaranteed delivery § Provide bulk transfer capability v Near-Real Time Access Ø Push based record transfer Ø Integrated management capabilities § Keep Alive/Heartbeat § Probe status and state reporting Internet Traffic Monitoring and Analysis: Methods and Applications 25 POSTECH DP&NM Lab.
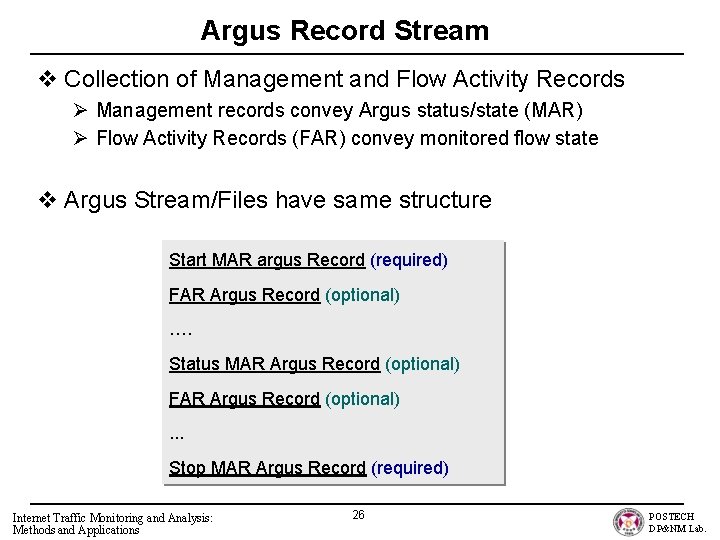
Argus Record Stream v Collection of Management and Flow Activity Records Ø Management records convey Argus status/state (MAR) Ø Flow Activity Records (FAR) convey monitored flow state v Argus Stream/Files have same structure Start MAR argus Record (required) FAR Argus Record (optional) …. Status MAR Argus Record (optional) FAR Argus Record (optional). . . Stop MAR Argus Record (required) Internet Traffic Monitoring and Analysis: Methods and Applications 26 POSTECH DP&NM Lab.
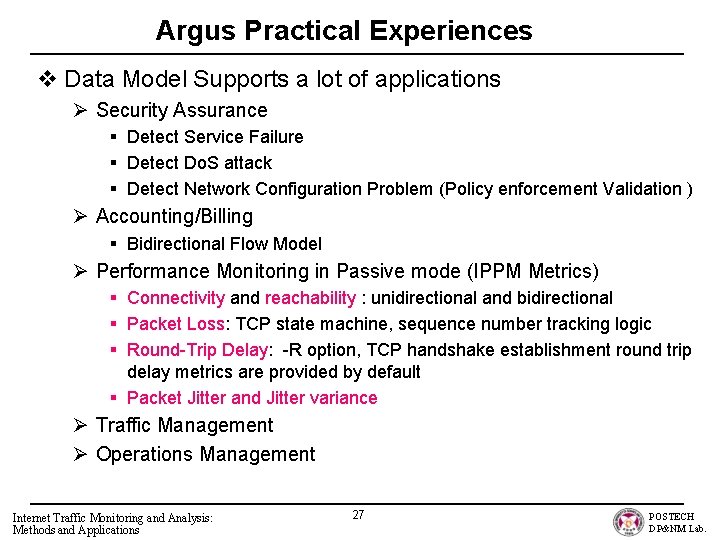
Argus Practical Experiences v Data Model Supports a lot of applications Ø Security Assurance § Detect Service Failure § Detect Do. S attack § Detect Network Configuration Problem (Policy enforcement Validation ) Ø Accounting/Billing § Bidirectional Flow Model Ø Performance Monitoring in Passive mode (IPPM Metrics) § Connectivity and reachability : unidirectional and bidirectional § Packet Loss: TCP state machine, sequence number tracking logic § Round-Trip Delay: -R option, TCP handshake establishment round trip delay metrics are provided by default § Packet Jitter and Jitter variance Ø Traffic Management Ø Operations Management Internet Traffic Monitoring and Analysis: Methods and Applications 27 POSTECH DP&NM Lab.
NG-MON v Next Generation Network Traffic MONitoring and Analysis System Ø Developed at DPNM Lab, POSTECH Ø Targeting 10 Gbps or higher networks Ø To support various analysis applications § § Multimedia streaming & conferencing, P 2 P, game traffic analysis Network security attack detection and analysis SLA monitoring Usage-based billing, Customer relationship management Internet Traffic Monitoring and Analysis: Methods and Applications 28 POSTECH DP&NM Lab.
NG-MON - Requirements v Distributed, load-balancing architecture for scalability Ø subdivide monitoring system into several functional components Ø efficient load sharing between phases and within each phase Ø pipelined and parallel architecture v Lossless packet capture v Flow-based analysis Ø aggregate packet information into flows for efficient processing v Considerations for small storage requirements v Support for various applications Internet Traffic Monitoring and Analysis: Methods and Applications 29 POSTECH DP&NM Lab.
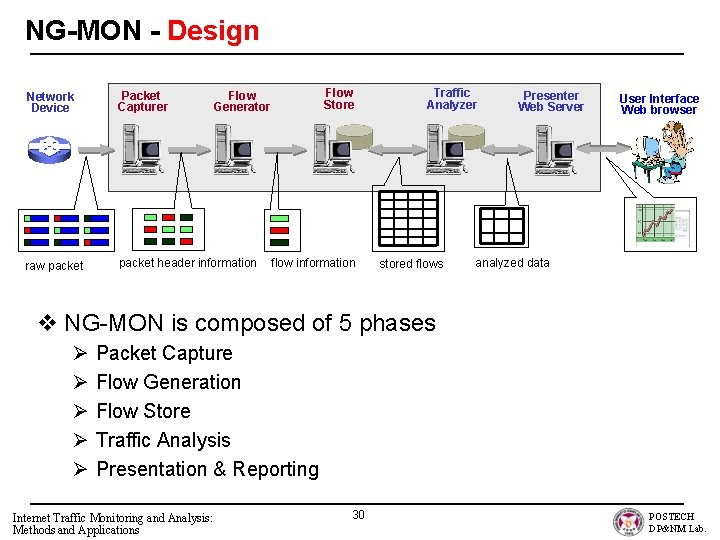
NG-MON - Design Network Device Packet Capturer raw packet header information Flow Store Flow Generator flow information Traffic Analyzer stored flows Presenter Web Server User Interface Web browser analyzed data v NG-MON is composed of 5 phases Ø Ø Ø Packet Capture Flow Generation Flow Store Traffic Analysis Presentation & Reporting Internet Traffic Monitoring and Analysis: Methods and Applications 30 POSTECH DP&NM Lab.
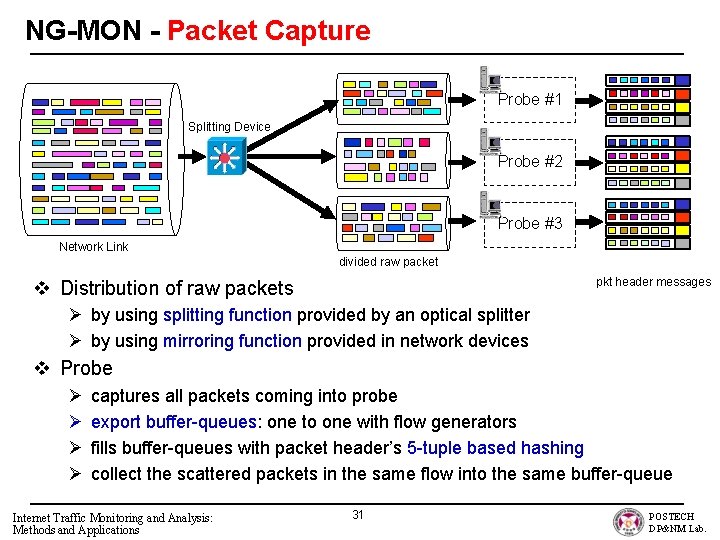
NG-MON - Packet Capture Probe #1 Splitting Device Probe #2 Probe #3 Network Link divided raw packet pkt header messages v Distribution of raw packets Ø by using splitting function provided by an optical splitter Ø by using mirroring function provided in network devices v Probe Ø Ø captures all packets coming into probe export buffer-queues: one to one with flow generators fills buffer-queues with packet header’s 5 -tuple based hashing collect the scattered packets in the same flow into the same buffer-queue Internet Traffic Monitoring and Analysis: Methods and Applications 31 POSTECH DP&NM Lab.
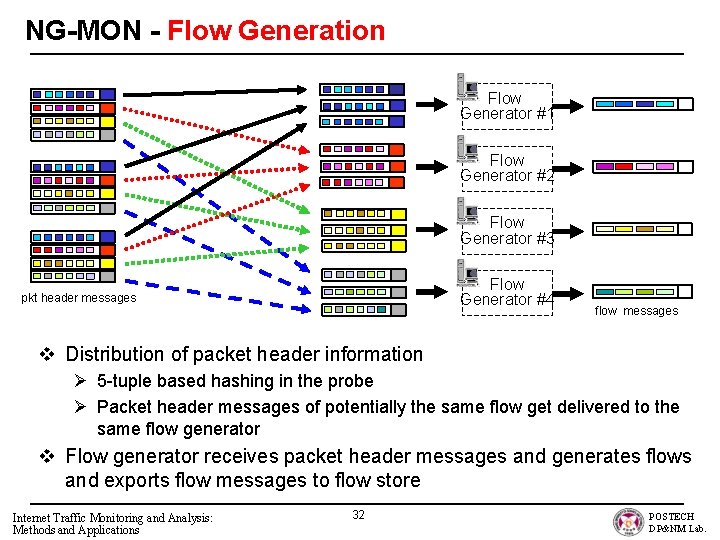
NG-MON - Flow Generation Flow Generator #1 Flow Generator #2 Flow Generator #3 Flow Generator #4 pkt header messages flow messages v Distribution of packet header information Ø 5 -tuple based hashing in the probe Ø Packet header messages of potentially the same flow get delivered to the same flow generator v Flow generator receives packet header messages and generates flows and exports flow messages to flow store Internet Traffic Monitoring and Analysis: Methods and Applications 32 POSTECH DP&NM Lab.
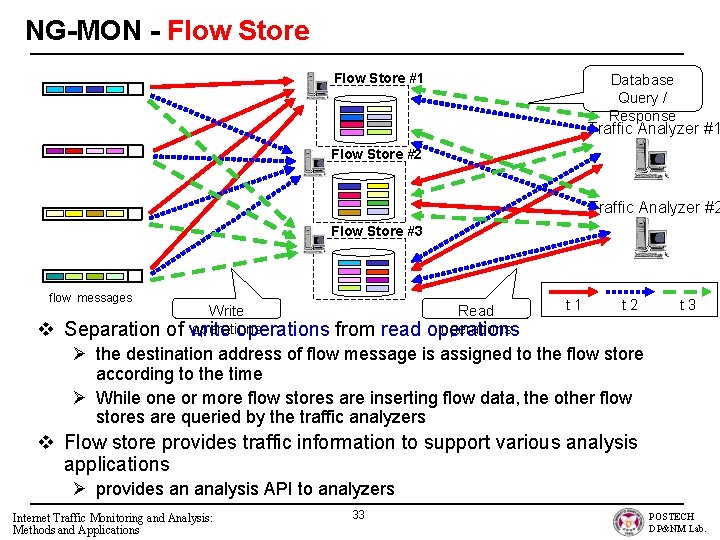
NG-MON - Flow Store #1 Database Query / Response Traffic Analyzer #1 Flow Store #2 Traffic Analyzer #2 Flow Store #3 flow messages v Write Read operations Separation of write operations from read operations t 1 t 2 t 3 Ø the destination address of flow message is assigned to the flow store according to the time Ø While one or more flow stores are inserting flow data, the other flow stores are queried by the traffic analyzers v Flow store provides traffic information to support various analysis applications Ø provides an analysis API to analyzers Internet Traffic Monitoring and Analysis: Methods and Applications 33 POSTECH DP&NM Lab.
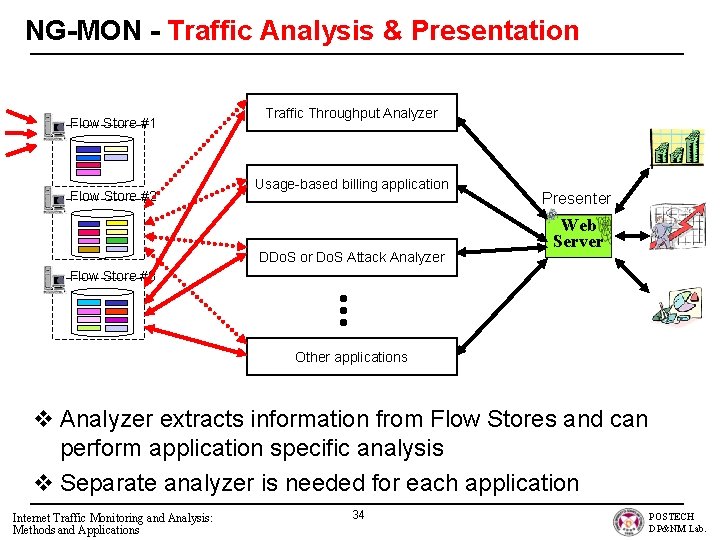
NG-MON - Traffic Analysis & Presentation Flow Store #1 Flow Store #2 Traffic Throughput Analyzer Usage-based billing application DDo. S or Do. S Attack Analyzer Presenter Web Server Flow Store #3 Other applications v Analyzer extracts information from Flow Stores and can perform application specific analysis v Separate analyzer is needed for each application Internet Traffic Monitoring and Analysis: Methods and Applications 34 POSTECH DP&NM Lab.
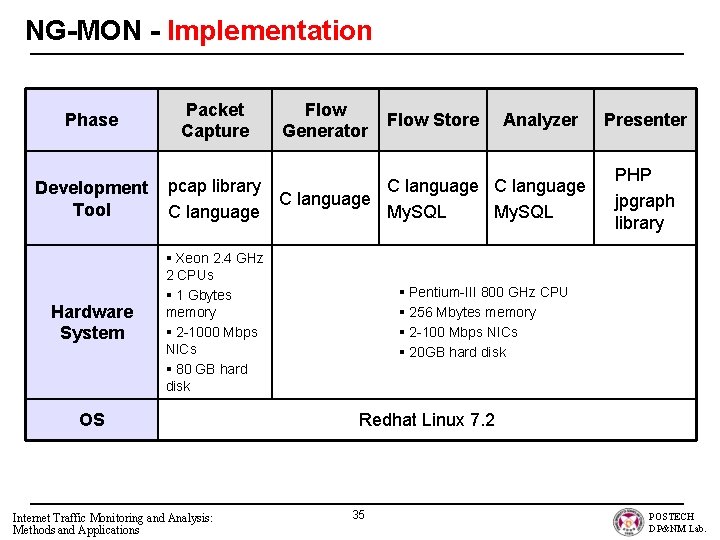
NG-MON - Implementation Phase Packet Capture Development Tool pcap library C language Hardware System § Xeon 2. 4 GHz 2 CPUs § 1 Gbytes memory § 2 -1000 Mbps NICs § 80 GB hard disk OS Internet Traffic Monitoring and Analysis: Methods and Applications Flow Generator Flow Store Analyzer C language My. SQL Presenter PHP jpgraph library § Pentium-III 800 GHz CPU § 256 Mbytes memory § 2 -100 Mbps NICs § 20 GB hard disk Redhat Linux 7. 2 35 POSTECH DP&NM Lab.
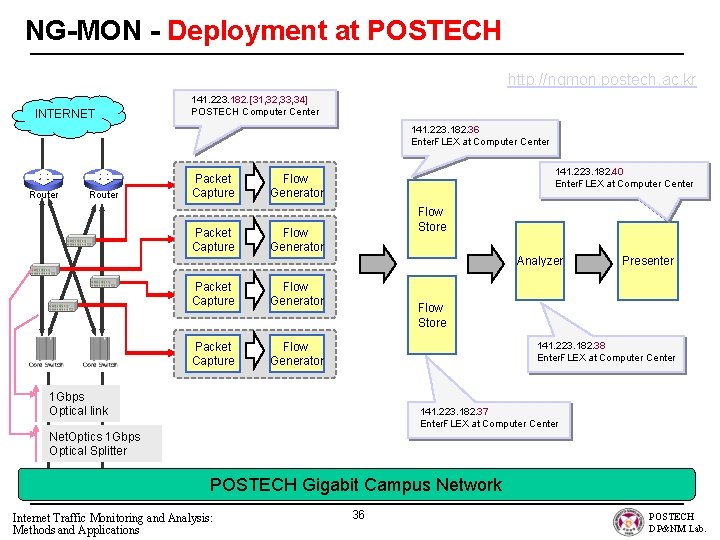
NG-MON - Deployment at POSTECH http: //ngmon. postech. ac. kr INTERNET 141. 223. 182. [31, 32, 33, 34] POSTECH Computer Center 141. 223. 182. 36 Enter. FLEX at Computer Center Router Packet Capture 141. 223. 182. 40 Enter. FLEX at Computer Center Flow Generator Flow Store Flow Generator Analyzer Packet Capture Flow Generator Presenter Flow Store 141. 223. 182. 38 Enter. FLEX at Computer Center 1 Gbps Optical link 141. 223. 182. 37 Enter. FLEX at Computer Center Net. Optics 1 Gbps Optical Splitter POSTECH Gigabit Campus Network Internet Traffic Monitoring and Analysis: Methods and Applications 36 POSTECH DP&NM Lab.
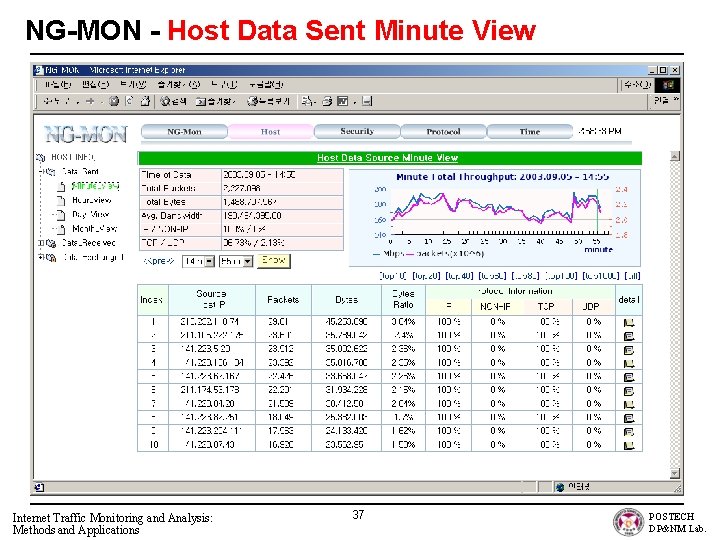
NG-MON - Host Data Sent Minute View Internet Traffic Monitoring and Analysis: Methods and Applications 37 POSTECH DP&NM Lab.
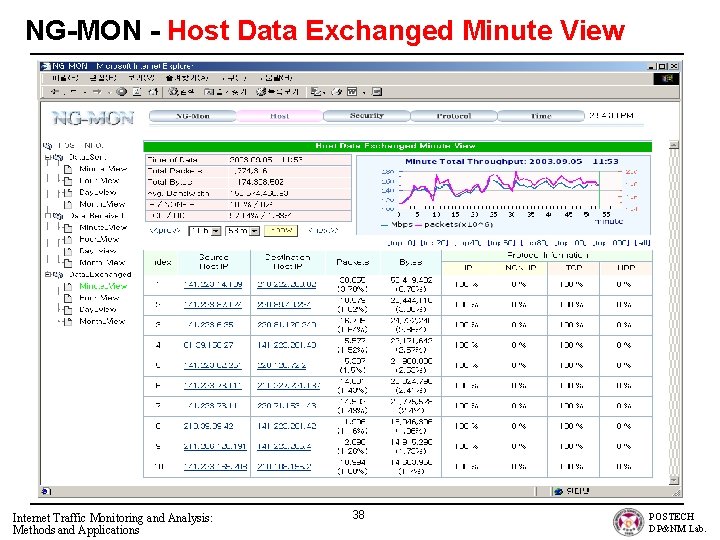
NG-MON - Host Data Exchanged Minute View Internet Traffic Monitoring and Analysis: Methods and Applications 38 POSTECH DP&NM Lab.
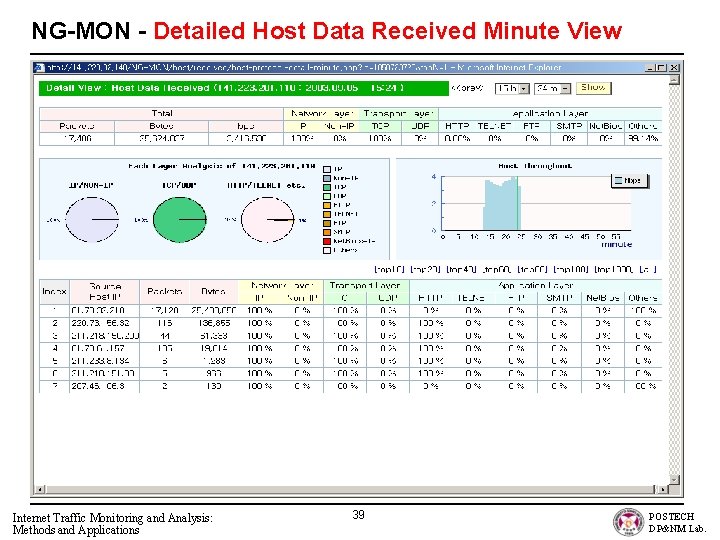
NG-MON - Detailed Host Data Received Minute View Internet Traffic Monitoring and Analysis: Methods and Applications 39 POSTECH DP&NM Lab.
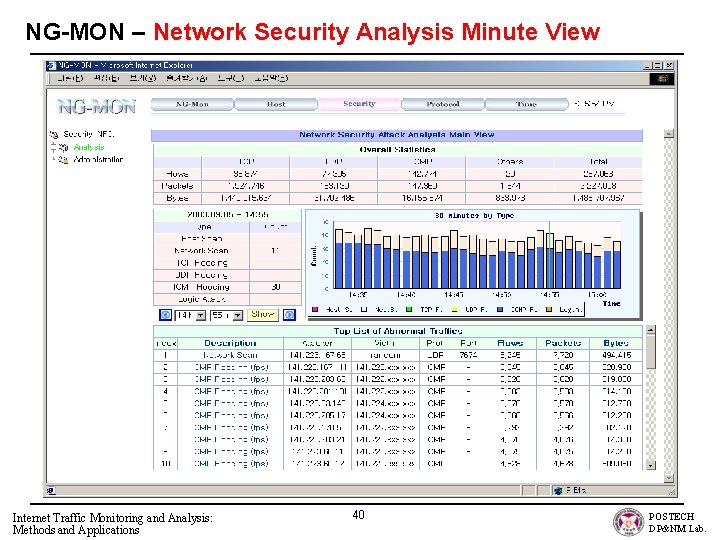
NG-MON – Network Security Analysis Minute View Internet Traffic Monitoring and Analysis: Methods and Applications 40 POSTECH DP&NM Lab.
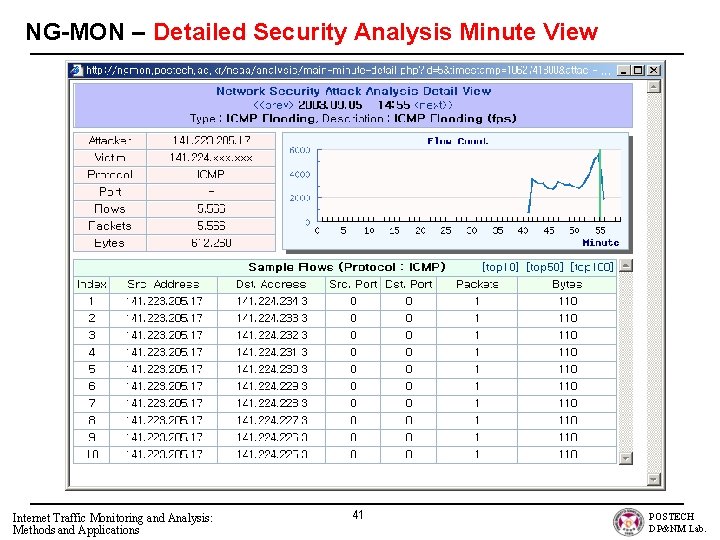
NG-MON – Detailed Security Analysis Minute View Internet Traffic Monitoring and Analysis: Methods and Applications 41 POSTECH DP&NM Lab.
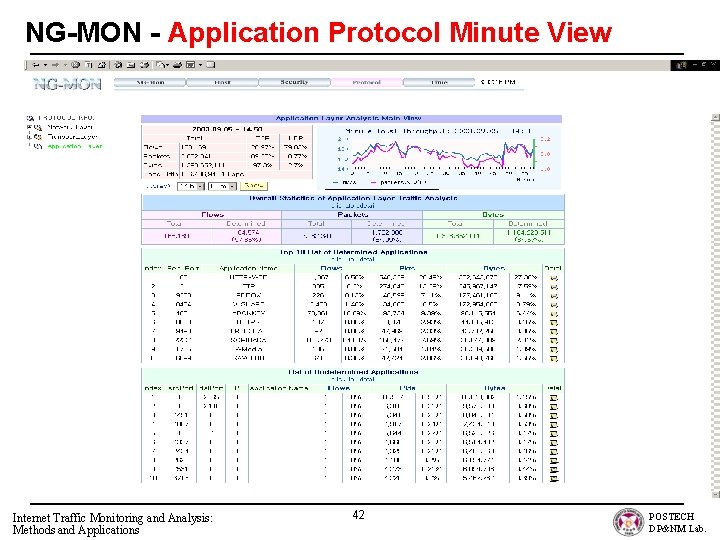
NG-MON - Application Protocol Minute View Internet Traffic Monitoring and Analysis: Methods and Applications 42 POSTECH DP&NM Lab.
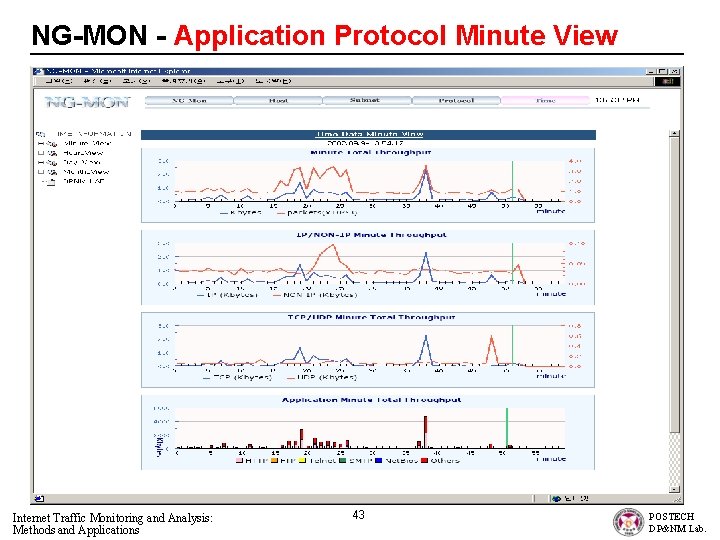
NG-MON - Application Protocol Minute View Internet Traffic Monitoring and Analysis: Methods and Applications 43 POSTECH DP&NM Lab.
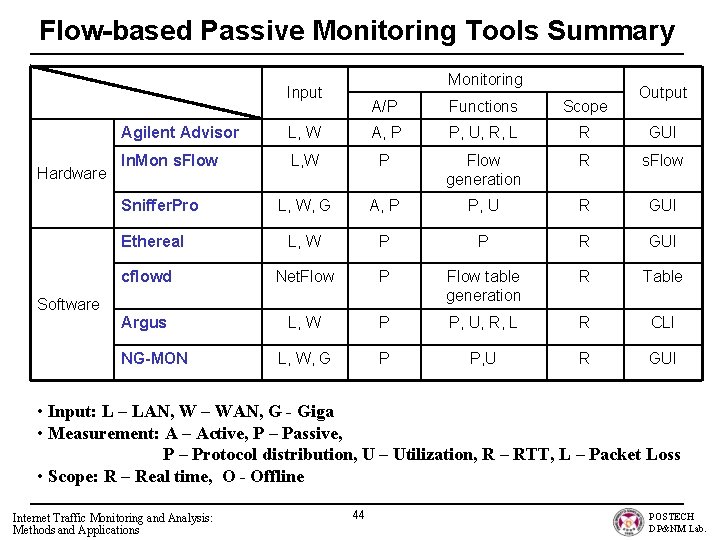
Flow-based Passive Monitoring Tools Summary Monitoring Input Hardware Functions Scope Output Agilent Advisor L, W A, P P, U, R, L R GUI In. Mon s. Flow L, W P Flow generation R s. Flow L, W, G A, P P, U R GUI L, W P P R GUI cflowd Net. Flow P Flow table generation R Table Argus L, W P P, U, R, L R CLI L, W, G P P, U R GUI Sniffer. Pro Ethereal Software A/P NG-MON • Input: L – LAN, W – WAN, G - Giga • Measurement: A – Active, P – Passive, P – Protocol distribution, U – Utilization, R – RTT, L – Packet Loss • Scope: R – Real time, O - Offline Internet Traffic Monitoring and Analysis: Methods and Applications 44 POSTECH DP&NM Lab.