Windows XP SP 2 Stack Protection Jimmy Hermansson
- Slides: 13
Windows XP SP 2 Stack Protection Jimmy Hermansson Johan Tibell
Overview n n n n Goals Stack Smashing in 30 Seconds Use Protection… Attacks! Windows XP SP 2 Demo We can do better! Conclusions
Goals Most common vulnerability according to CERT n Study stack protection mechanisms in general n Look at Windows XP SP 2’s implementation n Write a proof-of-concept exploit n
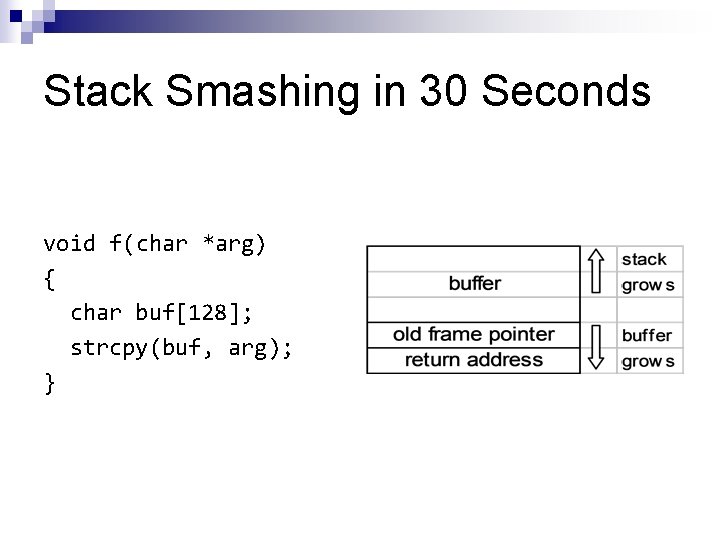
Stack Smashing in 30 Seconds void f(char *arg) { char buf[128]; strcpy(buf, arg); }
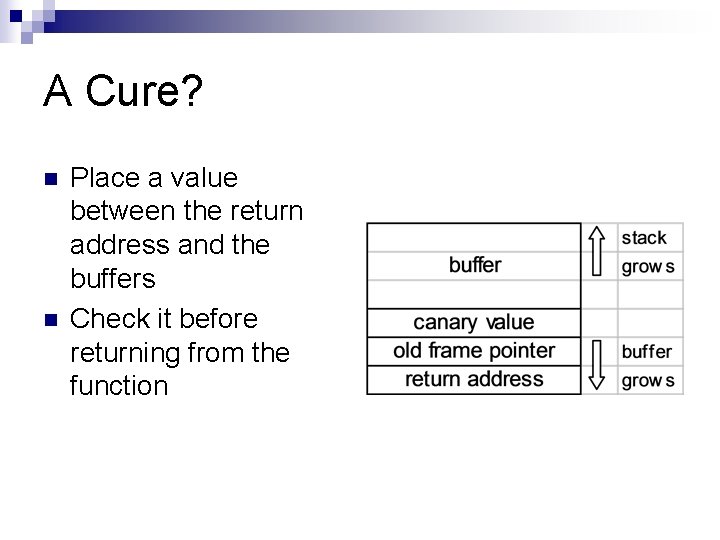
A Cure? n n Place a value between the return address and the buffers Check it before returning from the function
Any Value? If the attacker knows or can predict the value we might run into problems n Terminator canaries n Random XOR canaries n
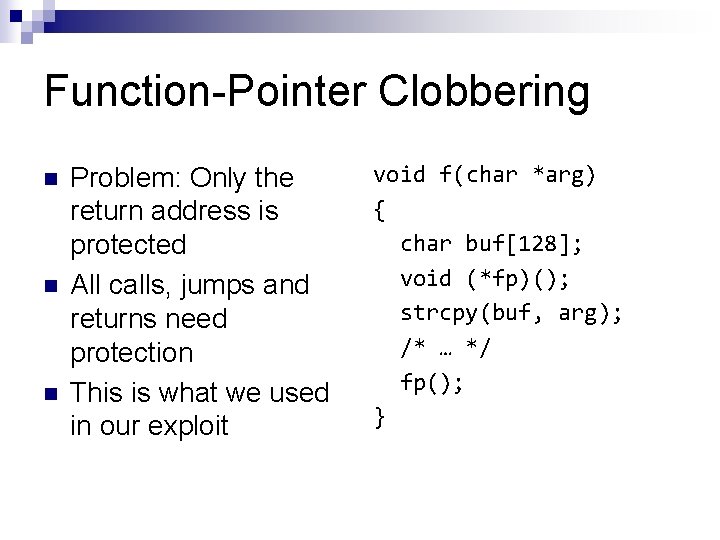
Function-Pointer Clobbering n n n Problem: Only the return address is protected All calls, jumps and returns need protection This is what we used in our exploit void f(char *arg) { char buf[128]; void (*fp)(); strcpy(buf, arg); /* … */ fp(); }
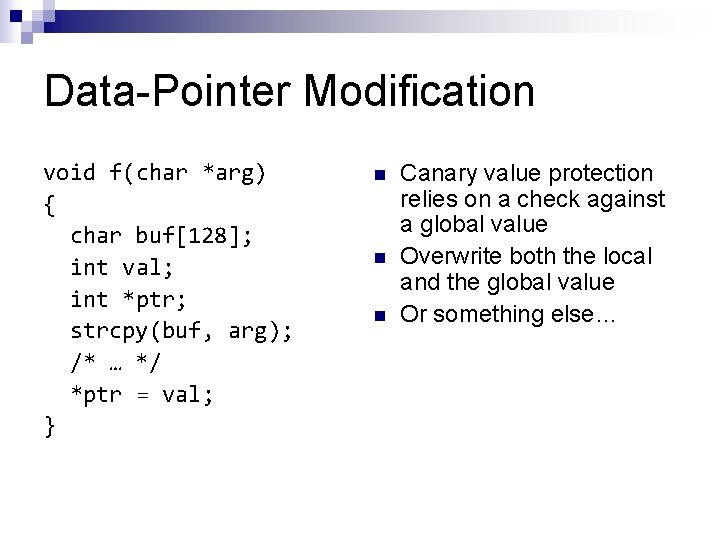
Data-Pointer Modification void f(char *arg) { char buf[128]; int val; int *ptr; strcpy(buf, arg); /* … */ *ptr = val; } n n n Canary value protection relies on a check against a global value Overwrite both the local and the global value Or something else…
Method Compile with Visual Studio 7. 1 and /GS flag n Olly. Dbg n
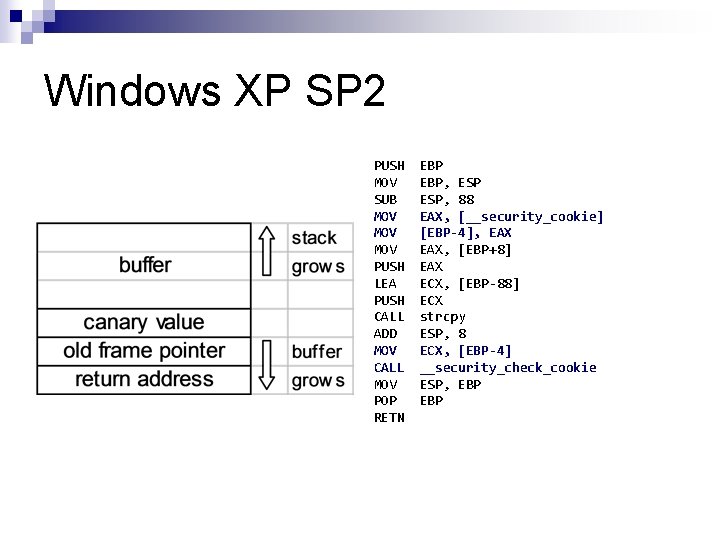
Windows XP SP 2 PUSH MOV SUB MOV MOV PUSH LEA PUSH CALL ADD MOV CALL MOV POP RETN EBP, ESP, 88 EAX, [__security_cookie] [EBP-4], EAX, [EBP+8] EAX ECX, [EBP-88] ECX strcpy ESP, 8 ECX, [EBP-4] __security_check_cookie ESP, EBP
Demo
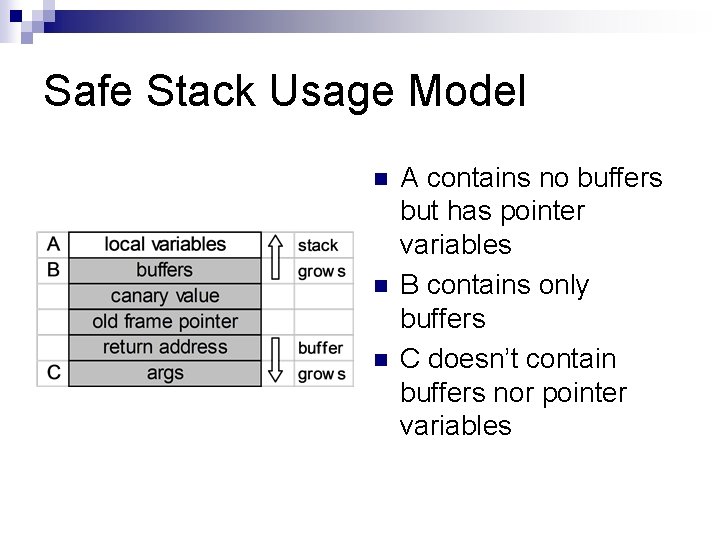
Safe Stack Usage Model n n n A contains no buffers but has pointer variables B contains only buffers C doesn’t contain buffers nor pointer variables
Conclusions Windows XP SP 2 has some stack protection… n …probably not enough (weakest link argument) n The root cause remains, no bounds checking! n We didn’t have time to talk about DEP n