NMap http www insecure org Stealth Scan http




- Slides: 17
弱點掃瞄 具 • NMap • (http: //www. insecure. org) • Stealth Scan • (http: //www. nstalker. com)
NMap
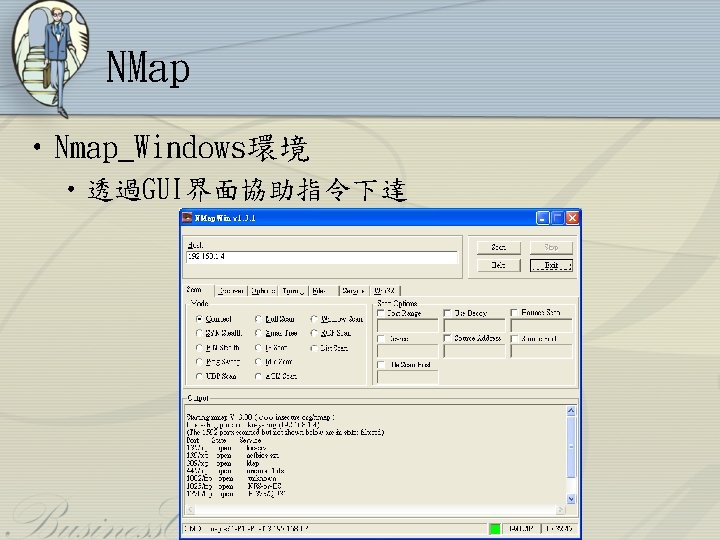
NMap • Nmap_Windows環境 • 透過文字模式 Starting nmap V. 3. 00 ( www. insecure. org/nmap ) Interesting ports on tku-yaling (192. 168. 1. 4): (The 1592 ports scanned but not shown below are in state: filtered) Port State Service 135/tcp open loc-srv 139/tcp open netbios-ssn 389/tcp open ldap 445/tcp open microsoft-ds 1002/tcp open unknown 1025/tcp open NFS-or-IIS 1720/tcp open H. 323/Q. 931 5000/tcp open UPn. P 8888/tcp open sun-answerbook Nmap run completed -- 1 IP address (1 host up) scanned in 408 seconds
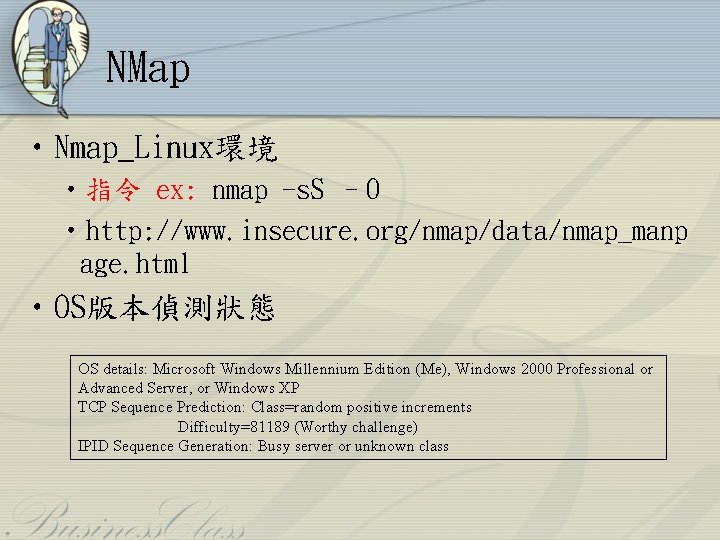
NMap • Nmap_Linux環境 • 指令 ex: nmap -s. S –O • http: //www. insecure. org/nmap/data/nmap_manp age. html • OS版本偵測狀態 OS details: Microsoft Windows Millennium Edition (Me), Windows 2000 Professional or Advanced Server, or Windows XP TCP Sequence Prediction: Class=random positive increments Difficulty=81189 (Worthy challenge) IPID Sequence Generation: Busy server or unknown class
Stealth Scan
N-Stealth Scan • 範例: • N-Stealth Report for 163_13_200_51. htm
N-Stealth Scan • Vulnerability • idq. dll directory traversal(CAN-20000126) • Common HTTP vulnerability/exploit(CAN 2000 -0126) • NT Index Server Directory Traversal Vulnerability(CVE-2000 -0097) • Common Win. CGI Vulnerability/Exploit • Microsoft IIS Vulnerability
CAN-2000 -0126弱點描述 • idq. dll directory traversal • Common HTTP vulnerability/exploit • idq. dll idq • 攻擊者只要發送一個夾帶過長參數的http request 給IIS Server,IIS 轉交給這些DLL 程 式執行時,即會造成這些DLL 產生Buffer Overflow的問題,進而操控DLL 程式為其執行任 意的程式 • Code Red
CAN-2000 -0097弱點描述 • webhits. dll htw • The Web. Hits ISAPI filter in Microsoft Index Server allows remote attackers to read arbitrary files, aka the "Malformed Hit-Highlighting Argument" vulnerability.