The Financial Services Technology Consortium Empowering the Industry
- Slides: 45
The Financial Services Technology Consortium Empowering the Industry Through Innovative Ideas FSTC’s 2008 Annual Conference On the Innovative Edge: Successful Strategies for Financial Services Industry Navigators 1
Capitalizing on a Federated Identity Assurance Program For the Industry FSTC Santa Rosa 2008 FSTC’s 2008 Annual Conference On the Innovative Edge: Successful Strategies for Financial Services Industry Navigators 2
U. S. Federal Identity Management – An Overview Peter Alterman, Ph. D. Chair, U. S. Federal PKI Policy Authority FSTC Santa Rosa 2008
In The Beginning • There was Federal PKI – Rudimentary Assurance – Basic Assurance – Medium Assurance – High Assurance FSTC Santa Rosa 2008 4
Then OMB Decreed 4 Assurance Levels • • 1 2 3 4 • Based on risk FSTC Santa Rosa 2008 5
And Pushed Fed PKI Into Levels 3 and 4 • Cryptographic-based technology • Policy-bound • High assurance FSTC Santa Rosa 2008 6
So We Added New Fed PKI Policies • • Commercial Best Practice versions Medium Hardware Citizen and Commerce Class Common And found HSPD-12 staring us in the face FSTC Santa Rosa 2008 7
And Created a De-Facto Identity Management Federation • That interfederated with other de-facto federations • (though we’d proven the concept in 2001) FSTC Santa Rosa 2008 8
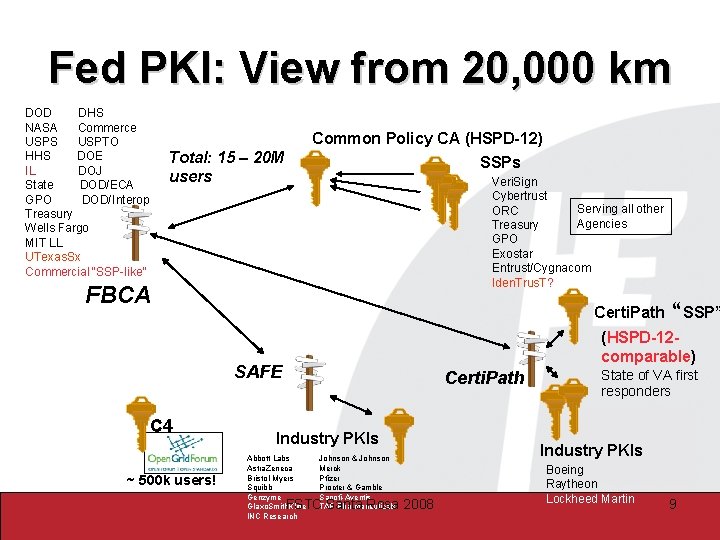
Fed PKI: View from 20, 000 km DOD DHS NASA Commerce USPS USPTO HHS DOE IL DOJ State DOD/ECA GPO DOD/Interop Treasury Wells Fargo MIT LL UTexas. Sx Commercial “SSP-like” Common Policy CA (HSPD-12) SSPs Total: 15 – 20 M users Veri. Sign Cybertrust Serving all other ORC Agencies Treasury GPO Exostar Entrust/Cygnacom Iden. Trus. T? FBCA Certi. Path (HSPD-12 comparable) SAFE C 4 ~ 500 k users! “SSP” Certi. Path Industry PKIs Abbott Labs Astra. Zeneca Bristol-Myers Squibb Genzyme Glaxo. Smith. Kline INC Research Johnson & Johnson Merck Pfizer Procter & Gamble Sanofi-Aventis TAP Pharmaceuticals FSTC Santa Rosa 2008 State of VA first responders Industry PKIs Boeing Raytheon Lockheed Martin 9
While We Were Doing That • We discovered SAML • Mandated that all outward-facing online applications run standard risk assessments, and • declare Assurance Level Requirements for authentication to those systems FSTC Santa Rosa 2008 10
And Then Extended the Id. M Federation Picture to All ALs • And Technologies FSTC Santa Rosa 2008 11
Then It Was 2004 • And we discovered the In. Common Shibboleth-based Identity Federation • And worked for two years to interfederate • Generating useful documents but no agreement FSTC Santa Rosa 2008 12
And In 2007 • NIH and In. Common Interfederated • U. S. Government joined the Liberty Alliance Identity Assurance Expert Group FSTC Santa Rosa 2008 13
Future • Extend interfederation to a metaframework like the Liberty Identity Assurance Framework • Gets the U. S. Government out of the mapping business FSTC Santa Rosa 2008 14
Capitalizing on Federated Identity Assurance: Government + Industry = Global Standard 2008 FSTC Annual Conference June 19 th, Santa Rosa CA Brett Mc. Dowell, Executive Director, Liberty Alliance
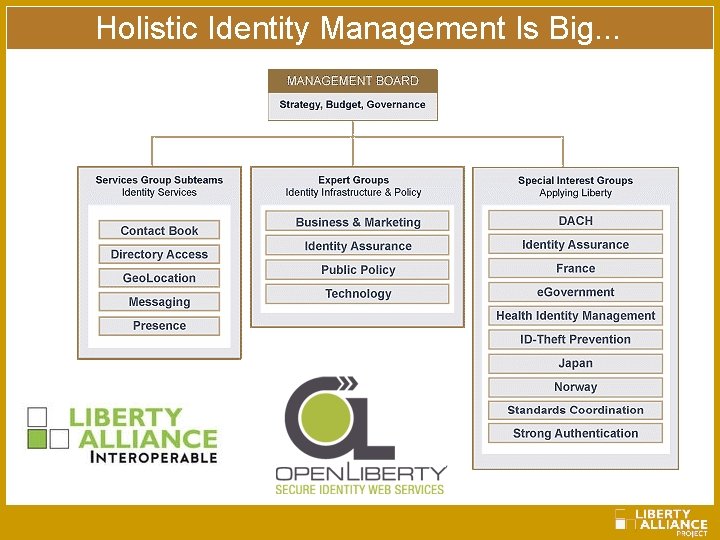
Who is the Liberty Alliance? 150 diverse member companies and organizations representing leaders in government and industry (IT, mobility, service provision, system integration and finance) working collaboratively to address the technology, business and policy aspects of identity management. Management Board Sample of Members 16
Holistic Identity Management Is Big. . .
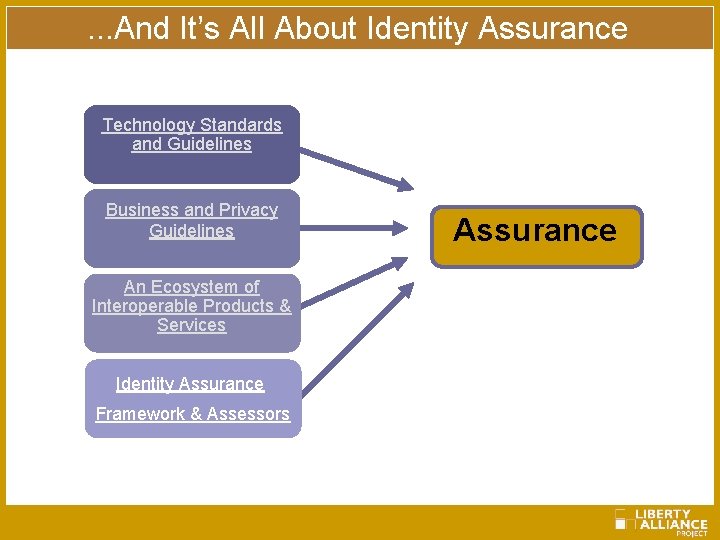
. . . And It’s All About Identity Assurance Technology Standards and Guidelines Business and Privacy Guidelines An Ecosystem of Interoperable Products & Services Identity Assurance Framework & Assessors Assurance
Identity Assurance Expert Group § Founded in August of 2007 following Electronic Authentication Partnership (EAP) merger into Liberty Alliance. § Formed to develop a global standard framework and necessary support programs for validating trusted identity assurance credential service providers (CSP’s) in a way that scales, empowers business processes and benefits individual users § Move beyond pure policy development and into development of actionable and measurable programs including certification, education and broad market promotion § Provide public and private organizations with a uniform means of relying on digital credentials issued by a variety of providers in order to advance trusted identity federation and thereby facilitate access to high value online services and information
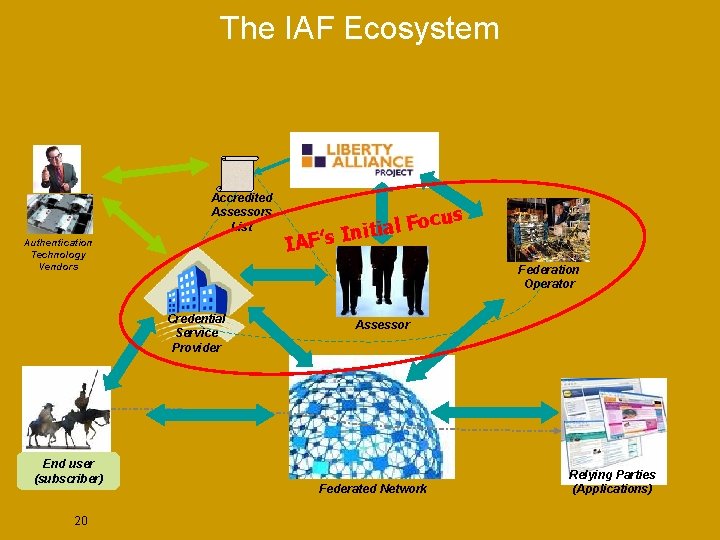
The IAF Ecosystem Accredited Assessors List Authentication Technology Vendors Federation Operator Credential Service Provider End user (subscriber) 20 cus o F l a i nit IAF’s I Assessor Federated Network Relying Parties (Applications)
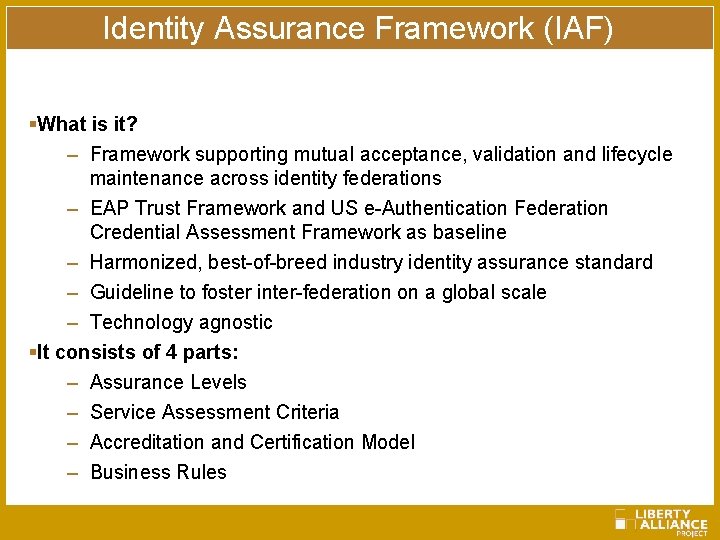
Identity Assurance Framework (IAF) §What is it? – Framework supporting mutual acceptance, validation and lifecycle maintenance across identity federations – EAP Trust Framework and US e-Authentication Federation Credential Assessment Framework as baseline – Harmonized, best-of-breed industry identity assurance standard – Guideline to foster inter-federation on a global scale – Technology agnostic §It consists of 4 parts: – Assurance Levels – Service Assessment Criteria – Accreditation and Certification Model – Business Rules
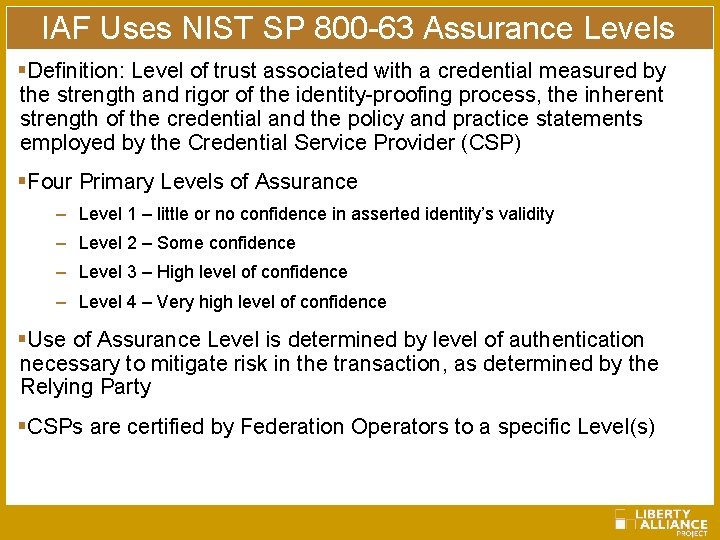
IAF Uses NIST SP 800 -63 Assurance Levels §Definition: Level of trust associated with a credential measured by the strength and rigor of the identity-proofing process, the inherent strength of the credential and the policy and practice statements employed by the Credential Service Provider (CSP) §Four Primary Levels of Assurance – Level 1 – little or no confidence in asserted identity’s validity – Level 2 – Some confidence – Level 3 – High level of confidence – Level 4 – Very high level of confidence §Use of Assurance Level is determined by level of authentication necessary to mitigate risk in the transaction, as determined by the Relying Party §CSPs are certified by Federation Operators to a specific Level(s)
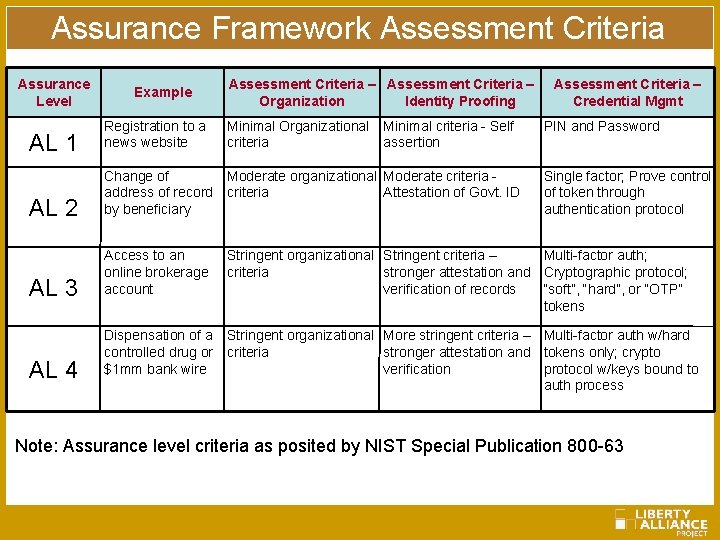
Assurance Framework Assessment Criteria Assurance Level Example Assessment Criteria – Organization Identity Proofing AL 1 Registration to a news website AL 2 Moderate organizational Moderate criteria Change of Attestation of Govt. ID address of record criteria by beneficiary AL 3 Access to an online brokerage account AL 4 Minimal Organizational criteria Minimal criteria - Self assertion Assessment Criteria – Credential Mgmt PIN and Password Single factor; Prove control of token through authentication protocol Stringent organizational Stringent criteria – Multi-factor auth; criteria stronger attestation and Cryptographic protocol; verification of records “soft”, “hard”, or “OTP” tokens Dispensation of a Stringent organizational More stringent criteria – Multi-factor auth w/hard controlled drug or criteria stronger attestation and tokens only; crypto $1 mm bank wire verification protocol w/keys bound to auth process Note: Assurance level criteria as posited by NIST Special Publication 800 -63
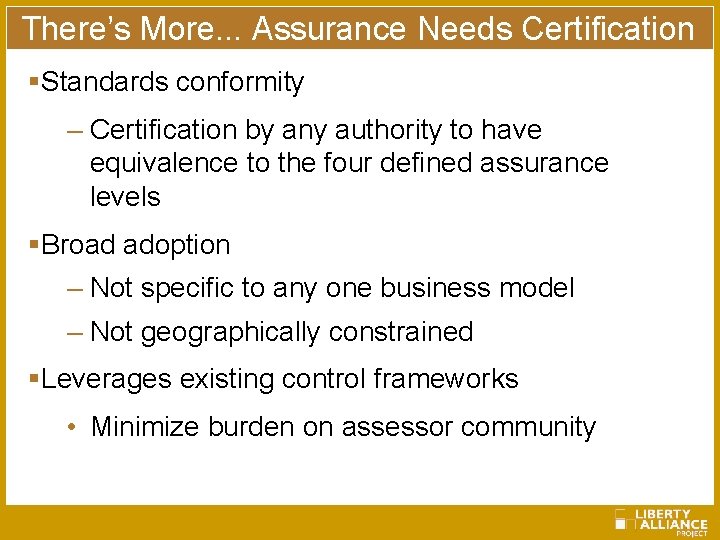
There’s More. . . Assurance Needs Certification §Standards conformity – Certification by any authority to have equivalence to the four defined assurance levels §Broad adoption – Not specific to any one business model – Not geographically constrained §Leverages existing control frameworks • Minimize burden on assessor community
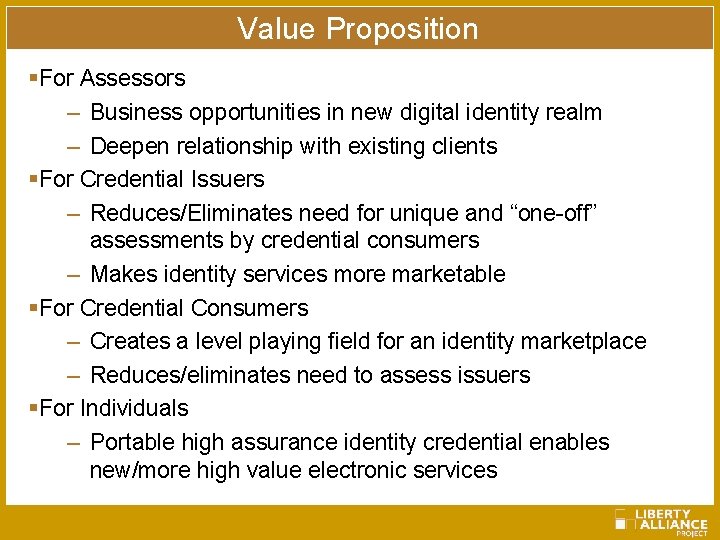
Value Proposition §For Assessors – Business opportunities in new digital identity realm – Deepen relationship with existing clients §For Credential Issuers – Reduces/Eliminates need for unique and “one-off” assessments by credential consumers – Makes identity services more marketable §For Credential Consumers – Creates a level playing field for an identity marketplace – Reduces/eliminates need to assess issuers §For Individuals – Portable high assurance identity credential enables new/more high value electronic services
www. projectliberty. org brett@projectliberty. org Phone: +1. 413. 652. 1248 26
2008 Annual Conference ● June 18, 2008 ● Santa Rosa, CA Capitalizing on Federated Identity Assurance: Financial Services Use Cases Jim Gross Senior 27 Vice President ● Wells. Secure Identity Assurance 2008 Wells Fargo Bank N. A. -- All Rights Reserved
My 2. 0 Agents 28 Buying Stuff Getting In The Door 2008 Wells Fargo Bank N. A. -- All Rights Reserved Always With Me
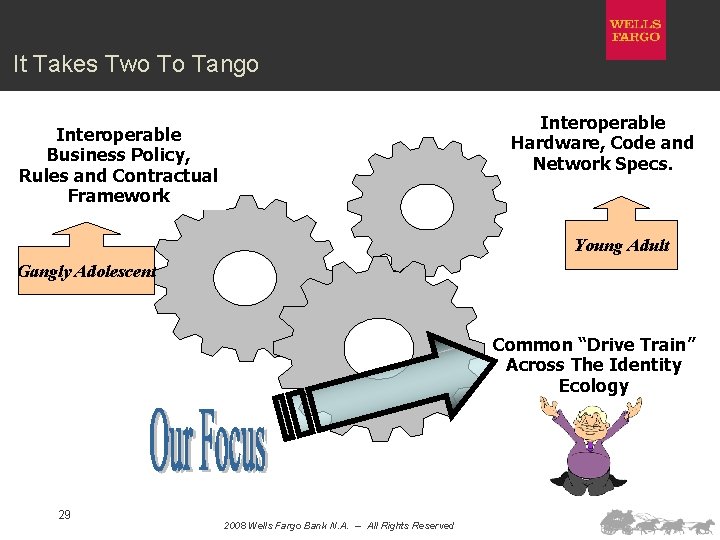
It Takes Two To Tango Interoperable Hardware, Code and Network Specs. Interoperable Business Policy, Rules and Contractual Framework Young Adult Gangly Adolescent Common “Drive Train” Across The Identity Ecology 29 2008 Wells Fargo Bank N. A. -- All Rights Reserved
Key Technology Drivers Toward Mature Convergence § For physical: HSPD-12/FIPS 201/PIV “twins” – Finally brought certification to smart card reader interoperability – NIST 800 -16 (draft out for review) further refines physical access specs. to support identity assurance level § For mobile: secure contactless access to SIM chip § For Web 2. 0: rich metadata – To enable a service – And, to allow dynamic linkage decisioning • Standard identity services are at the top of the list! 30 2008 Wells Fargo Bank N. A. -- All Rights Reserved
Key Business Driver Towards Mature Convergence § Liberty Alliance IAF (Identity Assurance Framework) – Objective is to create a framework of baseline policies, business rules and commercial terms against which identity assurance services can be assessed and certified • Standard, broadly accepted Levels of Assurance allow relying parties (or their agents) to readily determine, on the fly, their confidence in an identity credential – Desired results are: • Less complex/more rapid deployment of digital identity services • Operational streamlining of identity service provider certification/accreditation processes for entire industry 31 2008 Wells Fargo Bank N. A. -- All Rights Reserved
IAF Assurance Level Policy Overview Level of trust is associated with the strength and rigor of the identity-proofing policy and practices statements joined to an identity credential § Four Primary Levels of Assurance § – Level 1 – little or no confidence in asserted identity’s validity – Level 2 – Some confidence – Level 3 – High level of confidence – Level 4 – Very high level of confidence Use of Assurance Level is determined by Relying Party risk and the level of authentication rigor necessary to mitigate a given risk(s) § CSP’s (Credential Service Providers) are certified by Federation Operators to offer services at the given assurance level(s) § 32 2008 Wells Fargo Bank N. A. -- All Rights Reserved
Use Case: Annuity Funds Transfer § Initiation/transfer of $XXMM from demand deposit account to third party annuity product provider – Basic customer financial institution requirement: customer authentication onto network and application in order to submit request. Existing tools satisfy requirement. – Further requirement: customer authorization to submit request. Existing tools partially satisfy requirement. • This is where we lose STP traction today • And it gets messier as Web 2. 0/SOA unfolds 33 – But, do both the financial institution and the third party have high assurance that the identity credential submitted can non -repudiably represent the customer and other dependent parties? IAF framework and supporting network deliver this capability. 2008 Wells Fargo Bank N. A. -- All Rights Reserved
Converged Use Case: Physical § Physical access to storage facility containing negotiable documents – Facility maintains directory of identities authorized to enter – Person x is authorized to enter, but does not have a facility access card to allow authorized entry – Person x does holds a payment card that also holds a high assurance identity credential – Person x can be authorized to enter without further effort via assurance level match 34 2008 Wells Fargo Bank N. A. -- All Rights Reserved
Real World Use Case/Deployment § 35 US Federal: GSA e. Offer procurement site acceptance of federated Wells. Secure certificates 2008 Wells Fargo Bank N. A. -- All Rights Reserved
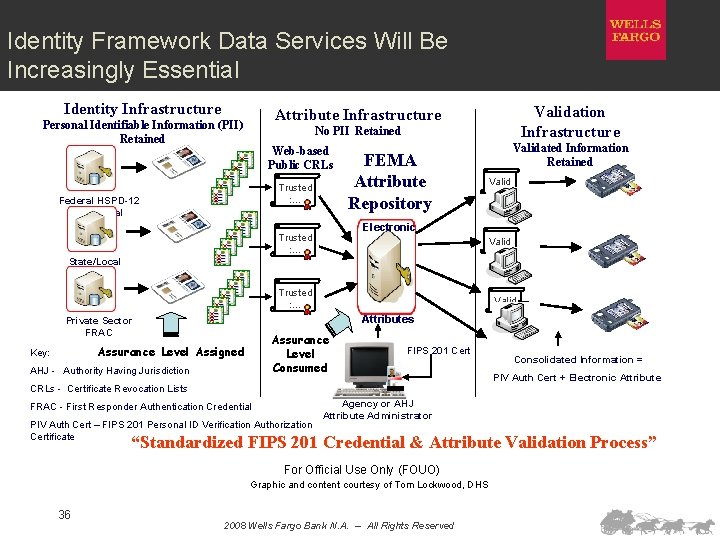
Identity Framework Data Services Will Be Increasingly Essential Identity Infrastructure No PII Retained Web-based Public CRLs Trusted : … Federal HSPD-12 Credential FEMA Attribute Repository Validated Information Retained Valid Electronic Trusted : … State/Local FRAC Valid Trusted : … Valid Attributes Private Sector FRAC Assurance Level Consumed Assurance Level Assigned Key: Validation Infrastructure Attribute Infrastructure Personal Identifiable Information (PII) Retained AHJ - Authority Having Jurisdiction FIPS 201 Cert CRLs - Certificate Revocation Lists FRAC - First Responder Authentication Credential PIV Auth Cert – FIPS 201 Personal ID Verification Authorization Certificate Consolidated Information = PIV Auth Cert + Electronic Attribute Agency or AHJ Attribute Administrator “Standardized FIPS 201 Credential & Attribute Validation Process” For Official Use Only (FOUO) Graphic and content courtesy of Tom Lockwood, DHS 36 2008 Wells Fargo Bank N. A. -- All Rights Reserved
Contact Information Jim Gross Senior Vice President Wells Fargo One Front Street MAC A 0195 -204 20 th Floor San Francisco, CA V: (415) 222 -5007 F: (415) 788 -3039 jgross@wellsfargo. com 37 2008 Wells Fargo Bank N. A. -- All Rights Reserved
University Bancorp (NASDAQ –UNIB) Leveraging Healthcare RHIOs To Create an Identity Assurance Federation Stephen Lange Ranzini President & CEO, University Bancorp President & Chairman, University Bank President & Chairman, University Islamic Financial (+1(734) 741 -5858 xt 226 * ranzini@university-bank. com www. university-bank. com/bancorp. htm June 19, 2008 FSTC Santa Rosa 2008 38
Safe Harbor Statement q Any prediction of the future is inherently not assured. Investors should read the “Risk Factors” listed on pages 23 to 24 in the Company’s report on Form 10 K for the year ended December 31, 2007 and any prediction in this release is intended to be covered by the Safe Harbor provisions of Section 21 E of the Securities Exchange Act of 1934.
Overview of University Bancorp q Bank holding company based in Ann Arbor, Michigan – Founded 1890 & Relocated to Ann Arbor in 1996 q Owns 100% of University Bank – FDIC insured community bank in Ann Arbor, Michigan q Owns 80% of Midwest Loan Services – Mortgage subservicer to the Credit Union industry with $5. 25 billion in mortgages subserviced q Owns 80% of University Islamic Financial – First U. S. Islamic Banking subsidiary run on Sharia’a principles q Owns 50. 01% of University Lending Group – Wholesale HUD/GNMA/VA lender operating in 12 states q Owns 100% of University Insurance & Investment Services – Full-line Insurance Agency and Stock Brokerage Account services q 4, 255, 878 shares of common stock – – – – Board owns 70. 6% of outstanding shares Current Share Price $2. 00 (Symbol UNIB) Current Market Capitalization, just $8. 5 million Trading volume averages 3, 400 shares per day 52 week range: High $2. 20; Low $1. 60 Trading at 12. 5 x Trailing 12 Months Net Income Trading at 4. 5 x 2008 Net Income projection (low end)
Routes to Market Adoption of the Identity Assurance Framework q – – – q q – – – Healthcare RHIOs as Possible Early Adopters of the Identity Assurance Framework What are RHIOs? Why do RHIOs need “credentials” or a “Trust Framework”? HIPAA Example of SEMHIE as possible early adopter Who are the stakeholders of SEMHIE • Major Michigan Employers • State of Michigan • Major healthcare insurers • Major Hospital Chains • University Bank What SEMHIE may want Identity Assurance Federation services supplied by a banking industry consortium • Why they may want this from a banking industry consortium and not from individual large banks Individual members may want Additional Optional Services such as fully electronic payment services from individual banks
Identity Assurance Federation q Why large banks would want to participate (what's in it for them) – How large banks could more readily sell their value added services if they participated in the Identity Assurance Federation to: • End users • Correspondent (smaller) banks q Services that can only be sold by the banking industry via an Identity Assurance Federation – Examples of lucrative services that cannot be supplied by a single large bank but could be supplied by a banking industry Identity Assurance Federation consortium – A bigger revenue pie for all banks who participate q Should the Identity Assurance Federation have a: – Non-profit/cost recovery only business model • (e. g. DTCC or ACH type model)? – For profit/income generating business model • (e. g. VISA/MASTERCARD/ATM network model)?
For More Information Stephen Lange Ranzini President & CEO University Bancorp (Listed NASDAQ – UNIB) (+1(734) 741 -5858 xt 226 [phone] 7+1(734) 741 -5859 [fax] * ranzini@university-bank. com [email] Investor Relations website: www. university-bank. com/bancorp. htm
The Financial Services Technology Consortium Empowering the Industry Through Innovative Ideas FSTC’s 2008 Annual Conference On the Innovative Edge: Successful Strategies for Financial Services Industry Navigators 44
Futurist Closing Luncheon Program: On the Horizon: The Future of Telecommunications and Banking FSTC Santa Rosa 2008 FSTC’s 2008 Annual Conference On the Innovative Edge: Successful Strategies for Financial Services Industry Navigators 45