Surviving Social Engineering and Ransomware Attacks Stu Sjouwerman
- Slides: 26
Surviving Social Engineering and Ransomware Attacks Stu Sjouwerman Founder and CEO Know. Be 4, Inc.
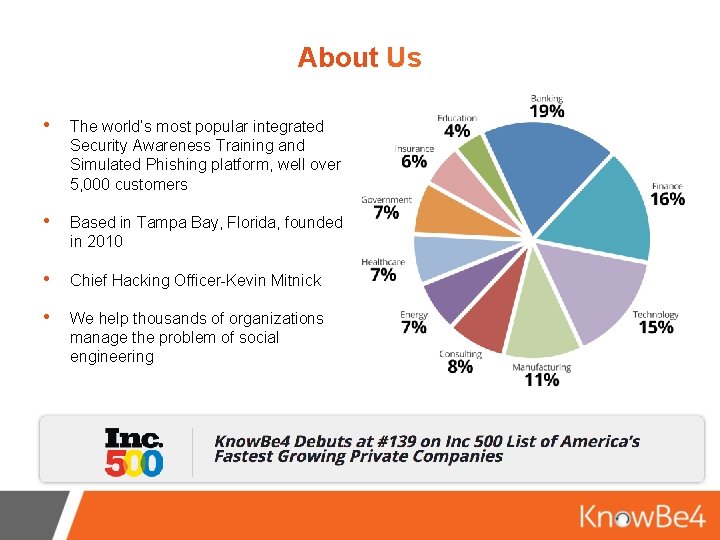
About Us • The world’s most popular integrated Security Awareness Training and Simulated Phishing platform, well over 5, 000 customers • Based in Tampa Bay, Florida, founded in 2010 • Chief Hacking Officer-Kevin Mitnick • We help thousands of organizations manage the problem of social engineering
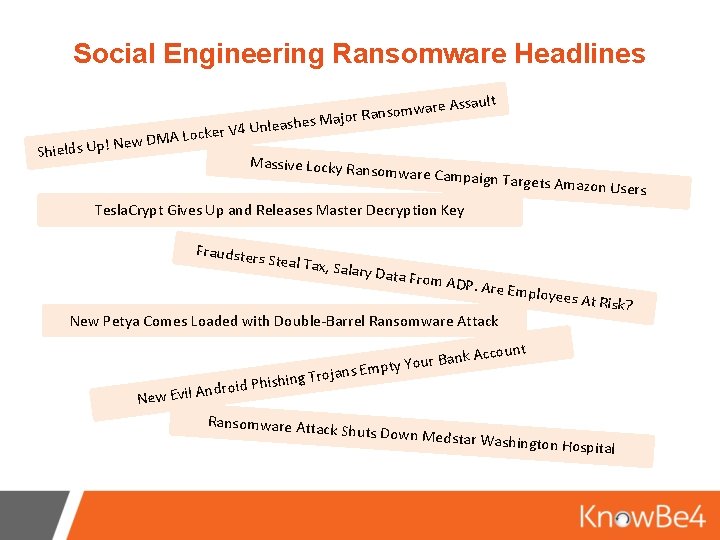
Social Engineering Ransomware Headlines re Assault a w m o s n a hes Major R s a le n U 4 V MA Locker D w e N ! p Shields U Massive Locky Ran somware Campaig n Targets Amazon Users Tesla. Crypt Gives Up and Releases Master Decryption Key Fraudsters Steal Tax, S alary Data From ADP . Are Emp loy ees At Risk New Petya Comes Loaded with Double-Barrel Ransomware Attack nt k Accou n a B r u o s Empty Y n a j o r T g hishin Android P New Evil Ransomware Attack Shuts Down Medst ar Washington Ho sp ital ?
Your Employees Are the Weakest Link in Network Security • 91% of successful data breaches started with a spear phishing attack • CEO Fraud (aka Business Email Compromise) caused $3. 4 billion in damages • W-2 Scams social engineer Accounting/HR to send tax forms to the bad guys • Ransomware on pace to be a 1 billion dollar business in 2016
The Cost of Breaches and Ransomware Attacks • Consolidated total cost of a data breach grew this year from $3. 8 million to $4 million. * • Average data breach cost is $158 ($355 for healthcare) per stolen record. * • Kaspersky Study from September 2016 show an average cost of $861, 000 for large businesses and $86, 500 for SMB. • Reducing the per record cost includes key actions such as employee training and participation in threat sharing. • Cost of downtime can be difficult to estimate due to hidden gotchas. *IBM 2016 Cost of Data Breach Study
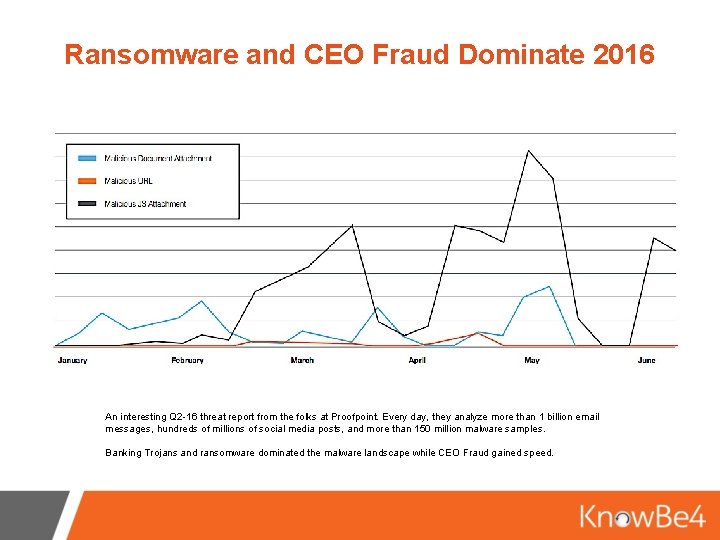
Ransomware and CEO Fraud Dominate 2016 An interesting Q 2 -16 threat report from the folks at Proofpoint. Every day, they analyze more than 1 billion email messages, hundreds of millions of social media posts, and more than 150 million malware samples. Banking Trojans and ransomware dominated the malware landscape while CEO Fraud gained speed.
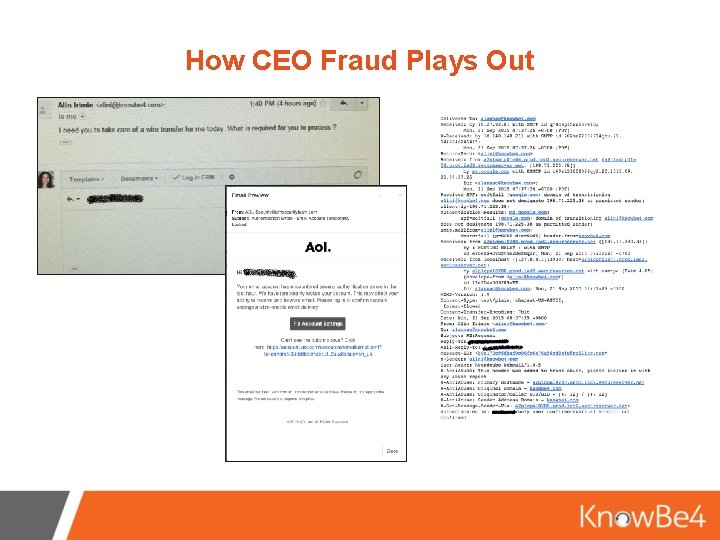
How CEO Fraud Plays Out
US Company Falls Victim to $100 Million CEO Email Fraud • This scam only surfaced as the U. S. government filed a civil forfeiture lawsuit in federal court in Manhattan seeking to recover about $25 million held in at least 20 bank accounts around the world. • Nearly $74 million has been recovered and returned to the American company. • The remaining $25 million was laundered through other accounts in locations including Cyprus, Latvia, Hungary, Estonia, Lithuania, Slovakia, and Hong Kong, authorities said.
$44 Million in a Single CEO Fraud Attack • Leoni AG fell victim to a classic CEO Fraud attack that has cost the company a whopping 44 million dollars. • Attackers crafted emails to appear like legitimate payment requests from the head office in Germany and sent them to a subsidiary of Leoni in Bistrita, Romania. • The scammers had extensive knowledge about the internal procedures for approving and processing transfers, meaning the network had likely been penetrated months earlier.
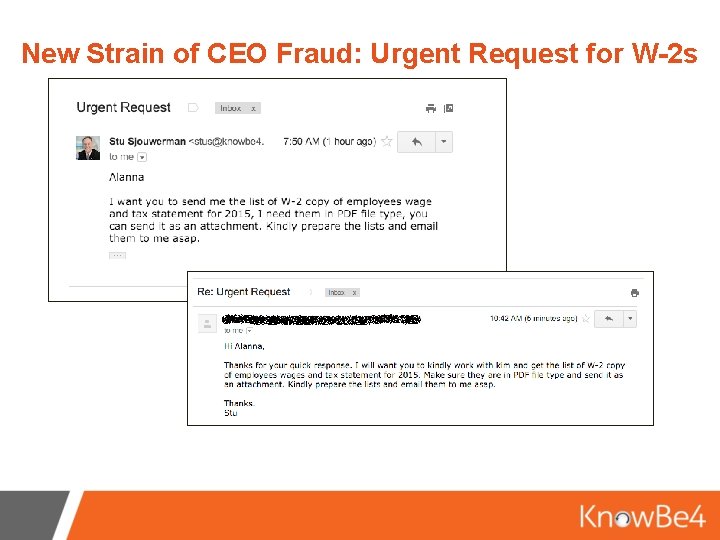
New Strain of CEO Fraud: Urgent Request for W-2 s
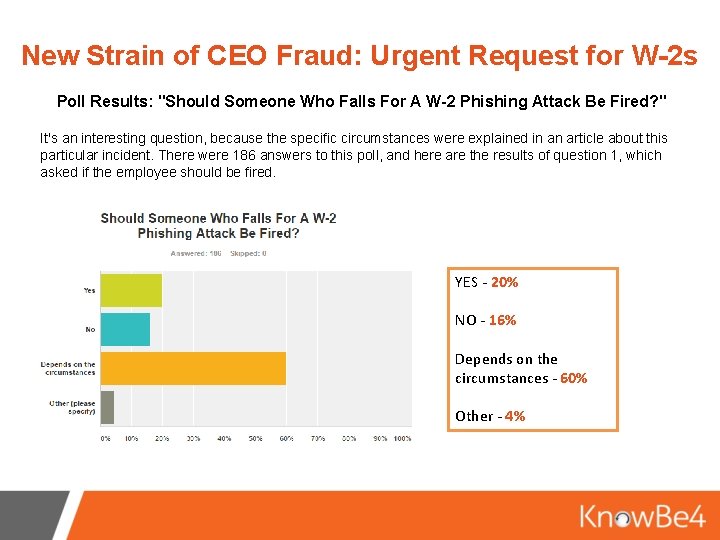
New Strain of CEO Fraud: Urgent Request for W-2 s Poll Results: "Should Someone Who Falls For A W-2 Phishing Attack Be Fired? " It's an interesting question, because the specific circumstances were explained in an article about this particular incident. There were 186 answers to this poll, and here are the results of question 1, which asked if the employee should be fired. YES - 20% NO - 16% Depends on the circumstances - 60% Other - 4%
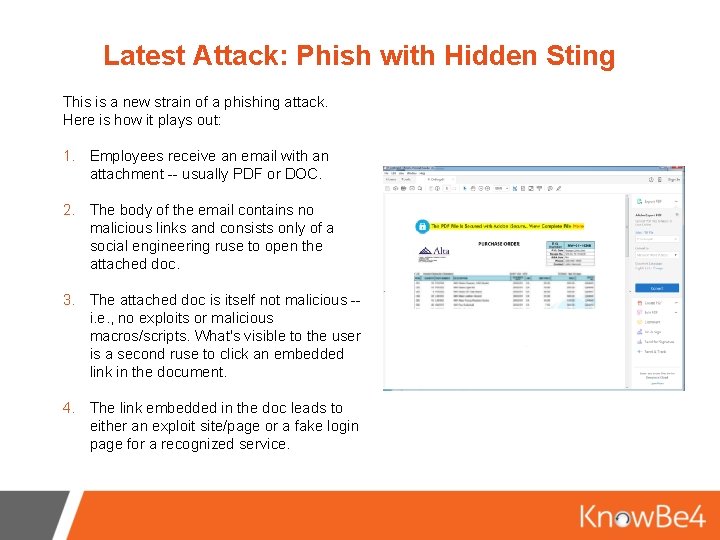
Latest Attack: Phish with Hidden Sting This is a new strain of a phishing attack. Here is how it plays out: 1. Employees receive an email with an attachment -- usually PDF or DOC. 2. The body of the email contains no malicious links and consists only of a social engineering ruse to open the attached doc. 3. The attached doc is itself not malicious -- i. e. , no exploits or malicious macros/scripts. What's visible to the user is a second ruse to click an embedded link in the document. 4. The link embedded in the doc leads to either an exploit site/page or a fake login page for a recognized service.
Latest CEO Fraud Causes $3. 4 Billion in Damages The FBI said in an alert issued to companies in April that businesses had suffered $3. 4 billion globally in losses from CEO email fraud from October 2013 to February of this year. If your company has been victimized by a BEC scam: • Contact your financial institution immediately • Request that they contact the financial institution where the fraudulent transfer was sent • File a complaint—regardless of dollar loss—with the IC 3 FBI Tips for Businesses: • Be wary of email-only wire transfer requests and requests involving urgency • Pick up the phone and verify legitimate business partners • Be cautious of mimicked email addresses • Practice multi-level authentication
Defending Against CEO Fraud Things you can do right now: • Check if your domain is susceptible to spoofing (since 82% are!) • Implement SPF records if you haven’t already • Review your procedures for funds transfer or sensitive information handling • Suggest a “Pick up the phone first” policy • Educate your top leadership ASAP even if you can’t fully train them yet • Test high-risk users by sending a spoofed CEO email as an effective security awareness training exercise
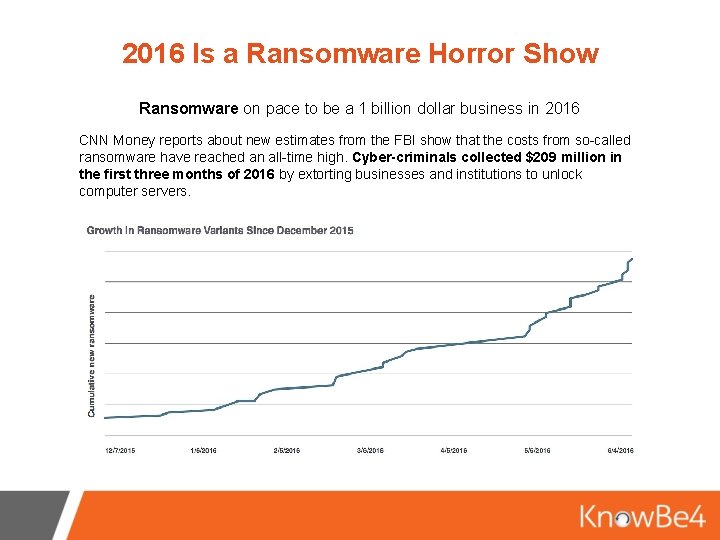
2016 Is a Ransomware Horror Show Ransomware on pace to be a 1 billion dollar business in 2016 CNN Money reports about new estimates from the FBI show that the costs from so-called ransomware have reached an all-time high. Cyber-criminals collected $209 million in the first three months of 2016 by extorting businesses and institutions to unlock computer servers.
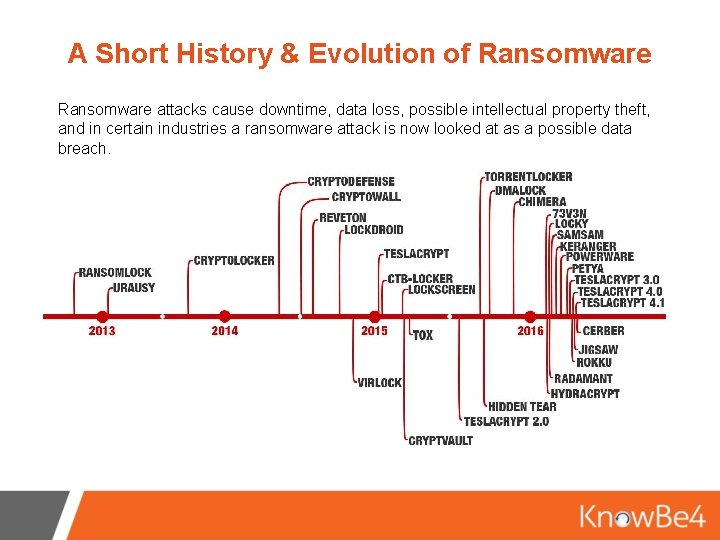
A Short History & Evolution of Ransomware attacks cause downtime, data loss, possible intellectual property theft, and in certain industries a ransomware attack is now looked at as a possible data breach.
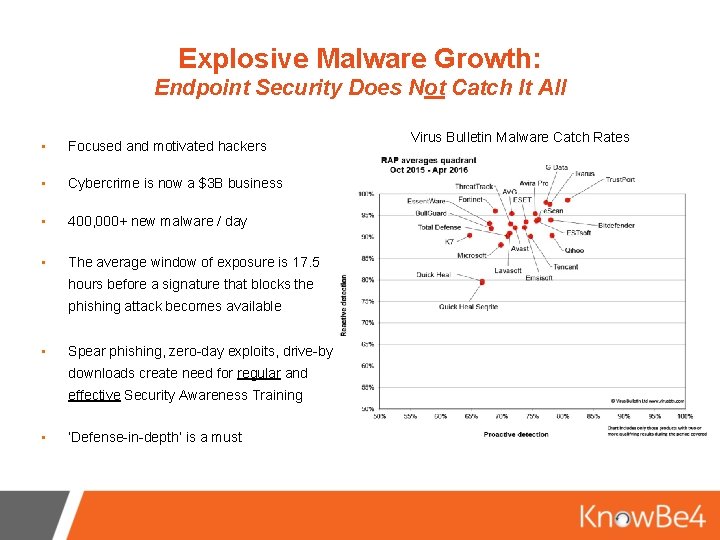
Explosive Malware Growth: Endpoint Security Does Not Catch It All • Focused and motivated hackers • Cybercrime is now a $3 B business • 400, 000+ new malware / day • The average window of exposure is 17. 5 hours before a signature that blocks the phishing attack becomes available • Spear phishing, zero-day exploits, drive-by downloads create need for regular and effective Security Awareness Training • ‘Defense-in-depth’ is a must Virus Bulletin Malware Catch Rates
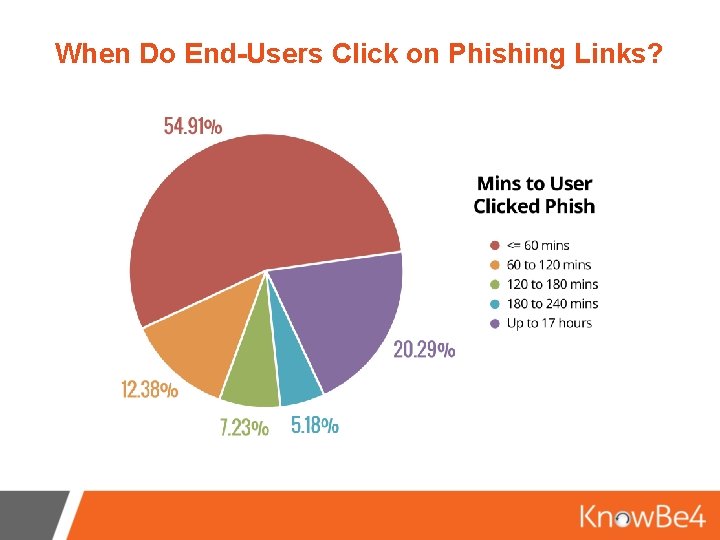
When Do End-Users Click on Phishing Links?
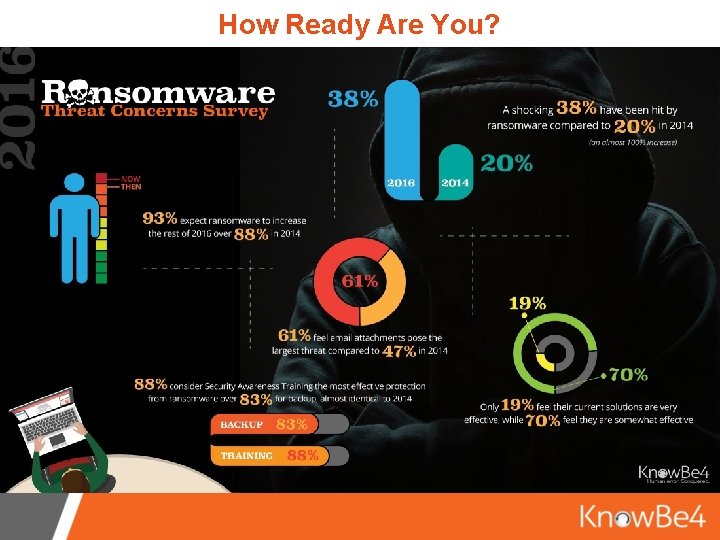
How Ready Are You?
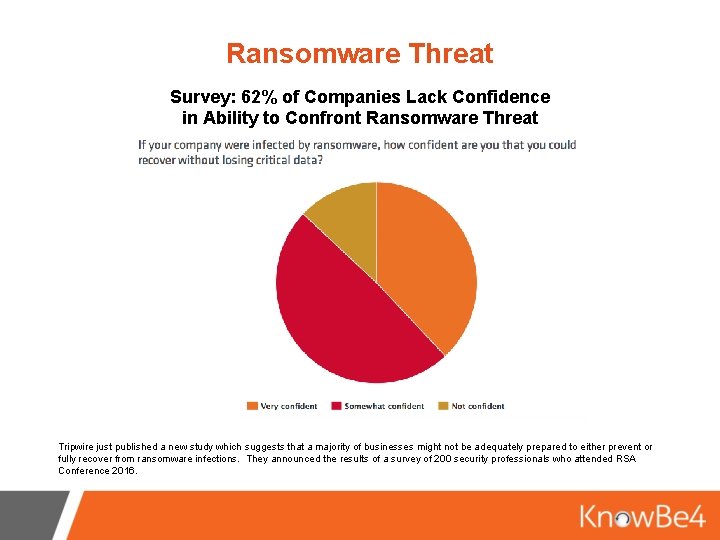
Ransomware Threat Survey: 62% of Companies Lack Confidence in Ability to Confront Ransomware Threat Tripwire just published a new study which suggests that a majority of businesses might not be adequately prepared to either prevent or fully recover from ransomware infections. They announced the results of a survey of 200 security professionals who attended RSA Conference 2016.
Increasing Confidence • Train Your Users – This is our number one suggestion because it works. An untrained staff is an incident waiting to happen. Most technical solutions are reactive and respond after an attack. It is important to have them to minimize the damage, but we prefer to prevent the attack • Have Weapons-grade Backups – Backups do no good if they are encrypted by the ransomware, so they have to be isolated from the network • Segment the Network – Marketing computers rarely need to have network access to the SQL servers or accounting systems • Principle of Least Privilege – Not everyone should be an administrator. The less access users have, the less malware can spread • Monitor the Network – Use a system like a SIEM or IDS to alert on malicious network behavior • Keep Up With Patches – OS and applications need to be kept patched
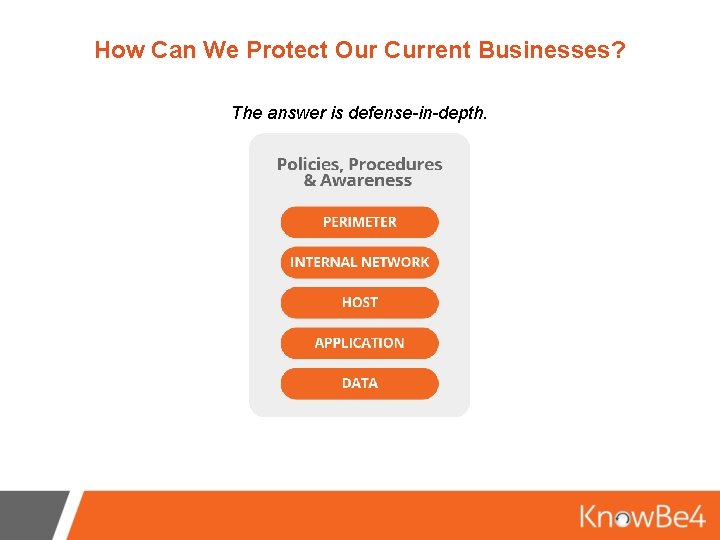
How Can We Protect Our Current Businesses? The answer is defense-in-depth.
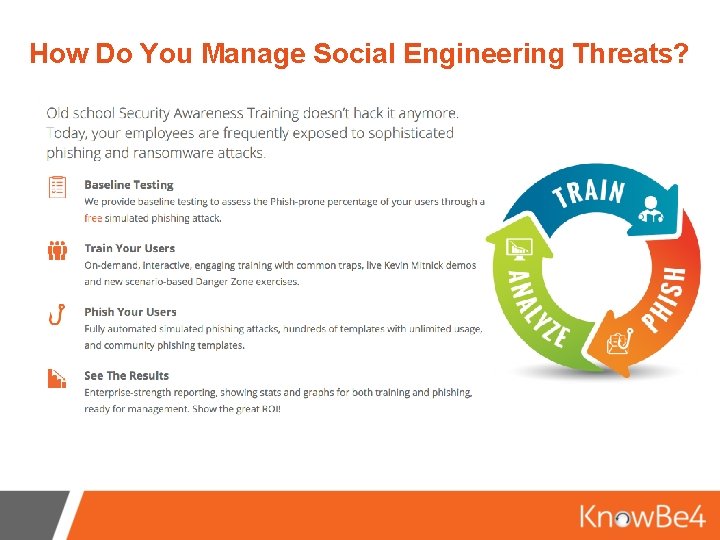
How Do You Manage Social Engineering Threats?
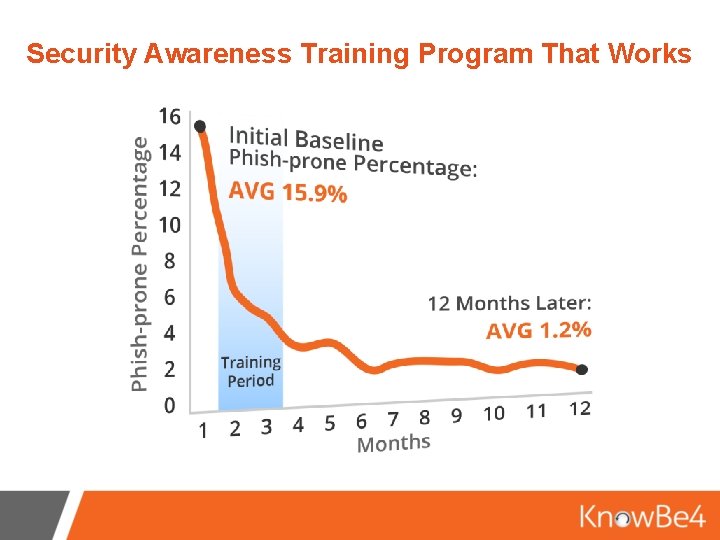
Security Awareness Training Program That Works
Resources Free Phishing Security Test Find out what percentage of your users are Phish-prone. Free Phish Alert Button for Outlook Your employees now have a safe way to report phishing attacks with one click! Free Domain Spoof Test Find out now if hackers can spoof an email address of your own domain. Ransomware Hostage Rescue Manual Get the most complete Ransomware Manual packed with actionable info that you need to have to prevent infections, and what to do when you are hit with ransomware. » Learn More at www. Know. Be 4. com/Resources «
Thank You! Stu Sjouwerman – Founder and CEO Stu. Sjouwerman@Know. Be 4. com Info@Know. Be 4. com www. Know. Be 4. com 855 -566 -9234