DEFEATING FRAUD WITH INTELLIGENT ADAPTIVE AUTHENTICATION AND RISK
- Slides: 24
DEFEATING FRAUD WITH INTELLIGENT ADAPTIVE AUTHENTICATION AND RISK ANALYTICS Giovanni Carnovale – Regional Sales Manager Central & Eastern
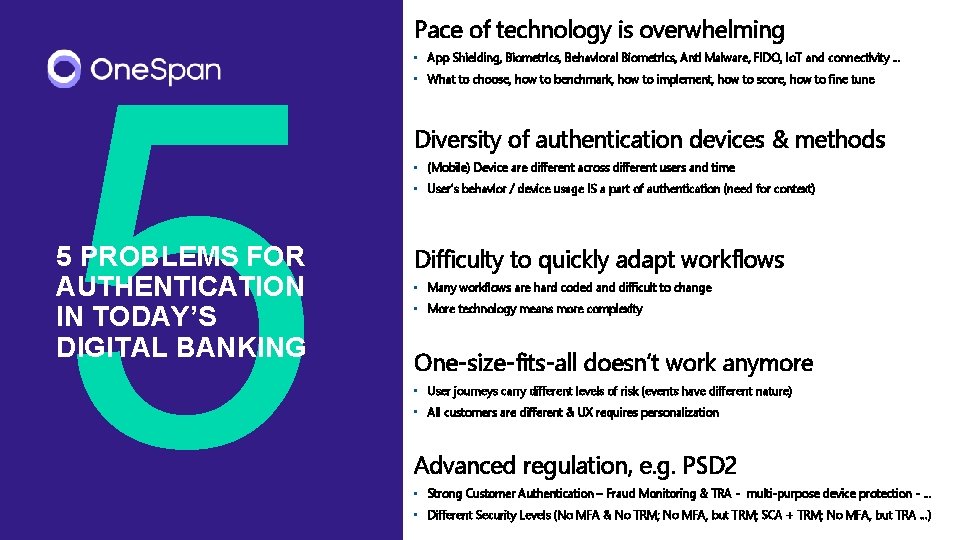
5 5 PROBLEMS FOR AUTHENTICATION IN TODAY’S DIGITAL BANKING Pace of technology is overwhelming • App Shielding, Biometrics, Behavioral Biometrics, Anti Malware, FIDO, Io. T and connectivity … • What to choose, how to benchmark, how to implement, how to score, how to fine tune Diversity of authentication devices & methods • (Mobile) Device are different across different users and time • User’s behavior / device usage IS a part of authentication (need for context) Difficulty to quickly adapt workflows • Many workflows are hard coded and difficult to change • More technology means more complexity One-size-fits-all doesn’t work anymore • User journeys carry different levels of risk (events have different nature) • All customers are different & UX requires personalization Advanced regulation, e. g. PSD 2 • Strong Customer Authentication – Fraud Monitoring & TRA - multi-purpose device protection - … • Different Security Levels (No MFA & No TRM; No MFA, but TRM; SCA + TRM; No MFA, but TRA …)
CHALLENGE 1 - PACE OF TECHNOLOGY IS OVERWHELMING How can you easily test / integrate new technology? App Shielding, (Behavioral) Biometrics, Anti Malware, FIDO, Io. T and connectivity … ? A single interface offering easy access to different solutions across all channels © 2018 One. Span
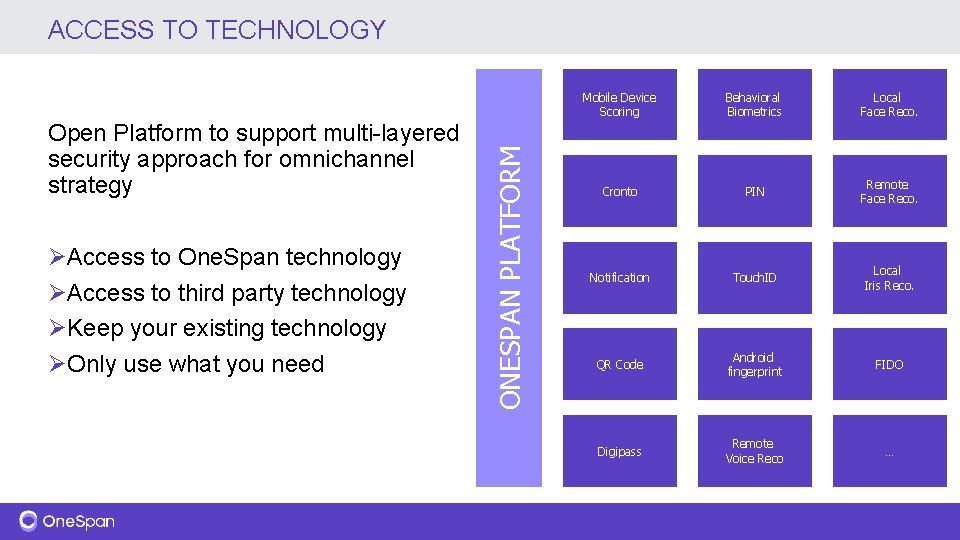
Open Platform to support multi-layered security approach for omnichannel strategy ØAccess to One. Span technology ØAccess to third party technology ØKeep your existing technology ØOnly use what you need ONESPAN PLATFORM ACCESS TO TECHNOLOGY Mobile Device Scoring Behavioral Biometrics Local Face Reco. Cronto PIN Remote Face Reco. Notification Touch. ID Local Iris Reco. QR Code Android fingerprint FIDO Digipass Remote Voice Reco …
CHALLENGE 2 - DIVERSITY OF AUTHENTICATION METHODS (Mobile) Device are different across different users and time User’s behavior / device usage IS a part of authentication (need for context) ? Full monitoring of the mobile devices and their associated risk levels © 2018 One. Span
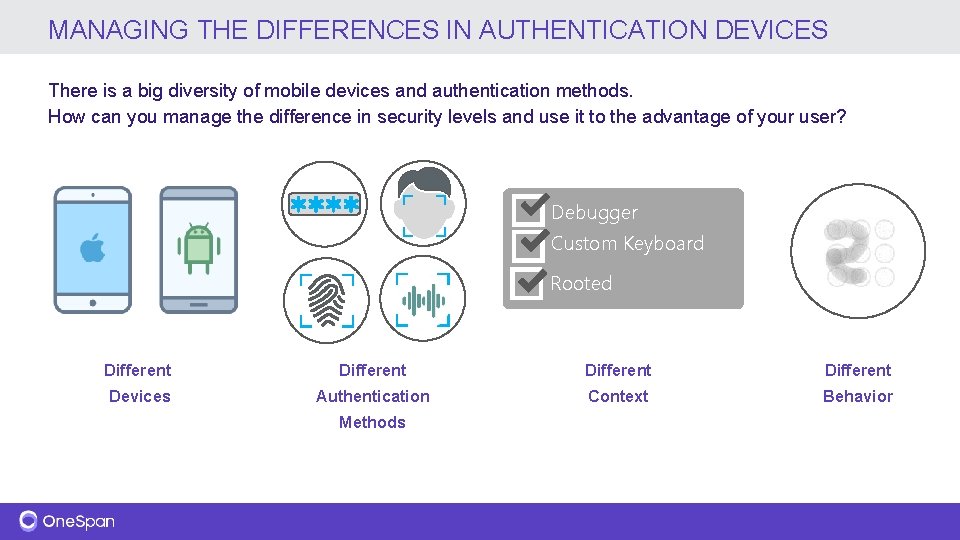
MANAGING THE DIFFERENCES IN AUTHENTICATION DEVICES There is a big diversity of mobile devices and authentication methods. How can you manage the difference in security levels and use it to the advantage of your user? Debugger Device Risk Manager Custom Keyboard Rooted Different Devices Authentication Context Behavior Methods
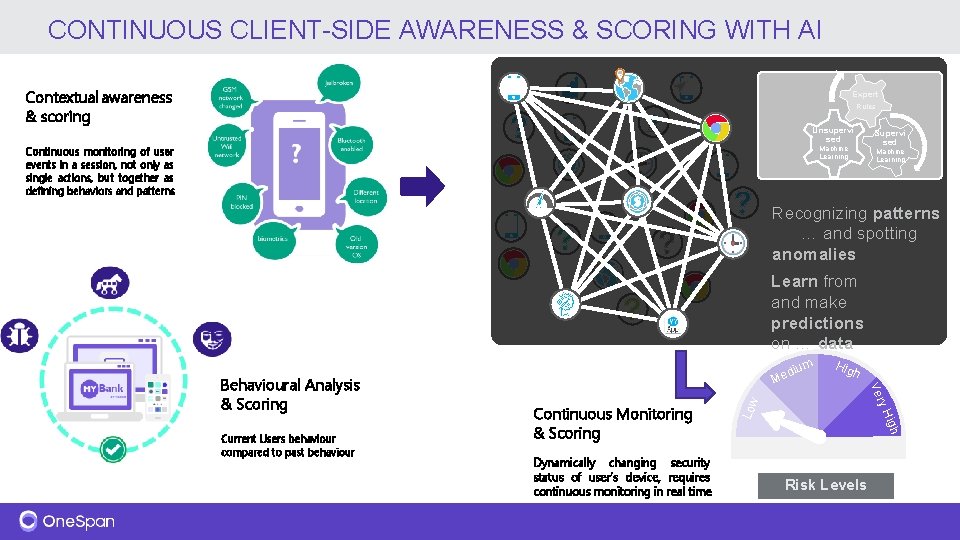
CONTINUOUS CLIENT-SIDE AWARENESS & SCORING WITH AI Contextual awareness & scoring Expert Rules Unsupervi sed Continuous monitoring of user events in a session, not only as single actions, but together as defining behaviors and patterns Machine Learning Supervi sed Machine Learning Recognizing patterns … and spotting anomalies Learn from and make predictions on … data Low igh Dynamically changing security status of user’s device, requires continuous monitoring in real time h y. H Current Users behaviour compared to past behaviour Continuous Monitoring & Scoring Hig Ver Behavioural Analysis & Scoring m diu Me Risk Levels
CHALLENGE 3 - DIFFICULTY TO QUICKLY ADAPT WORKFLOWS Many workflows are hard coded and difficult to change More technology means more complexity ? Orchestration seamlessly managing all bank applications to drive client logic © 2018 One. Span
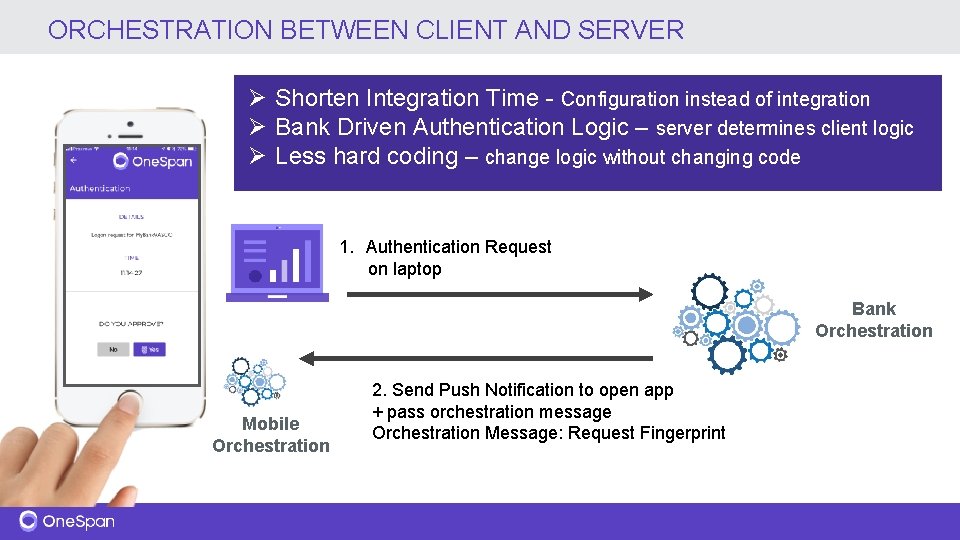
ORCHESTRATION BETWEEN CLIENT AND SERVER Ø Shorten Integration Time - Configuration instead of integration Ø Bank Driven Authentication Logic – server determines client logic Ø Less hard coding – change logic without changing code 1. Authentication Request on laptop Bank Orchestration Mobile Orchestration 2. Send Push Notification to open app + pass orchestration message Orchestration Message: Request Fingerprint
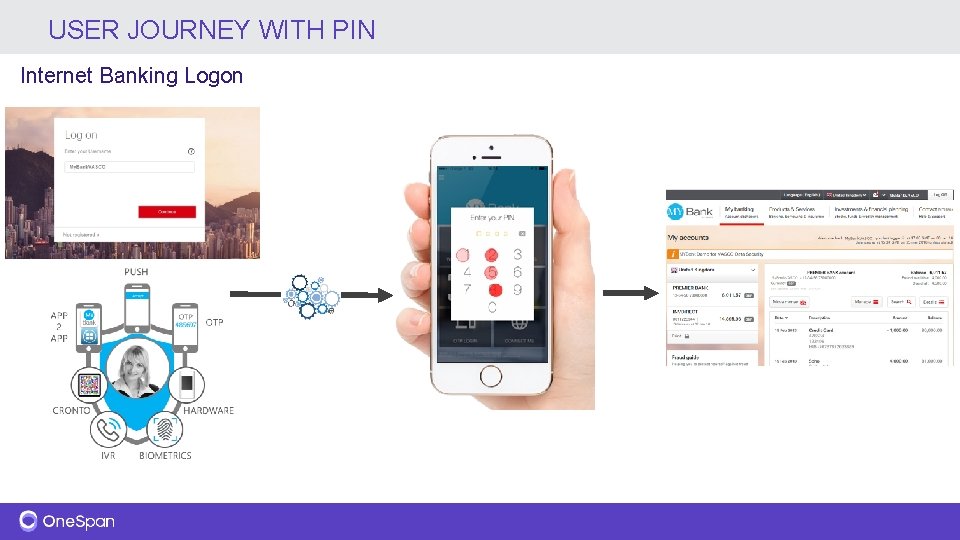
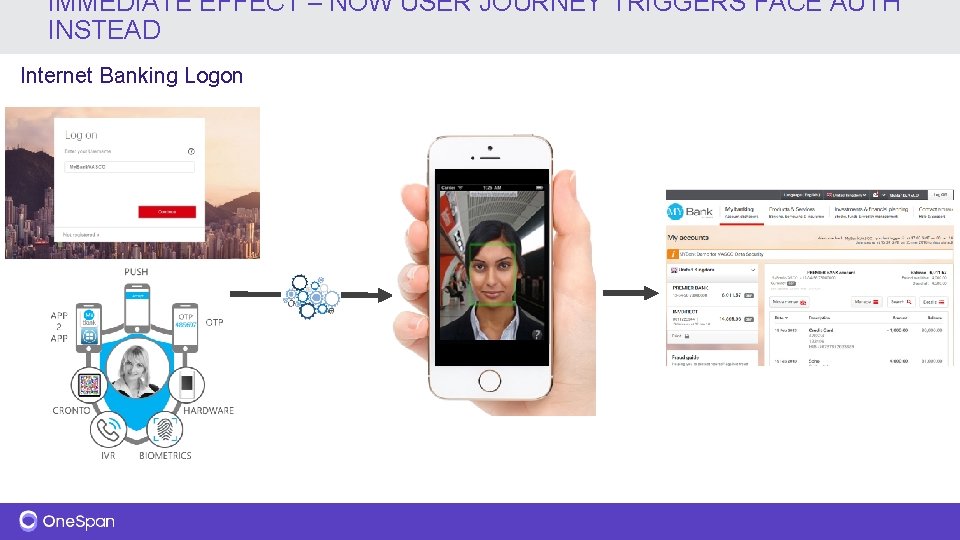
EXAMPLES Example 1 Situation: Bank has not integrated Face Authentiation yet Goal: Bank wants to start using Face Action: Update Orchestration in mobile app if needed + Select Face in dropdown box on server side Example 2 Situation: A security issue with Fingerprint has been published and the bank considers now Fingerprint as insecure Goal: Bank wants to stop using Fingerprint Action: Change the fingerprint action on server side to another authentication method (e. g. PIN that is normally enabled already as fallback)
USER JOURNEY WITH PIN Internet Banking Logon
IMMEDIATE EFFECT – NOW USER JOURNEY TRIGGERS FACE AUTH INSTEAD Internet Banking Logon
CHALLENGE 4 - ONE-SIZE-FITS-ALL DOESN’T WORK ANYMORE User journeys carry different levels of risk (events have different nature) All customers are different & UX requires personalization ? Flexible and adaptive authentication options to deliver the best user experience © 2018 One. Span
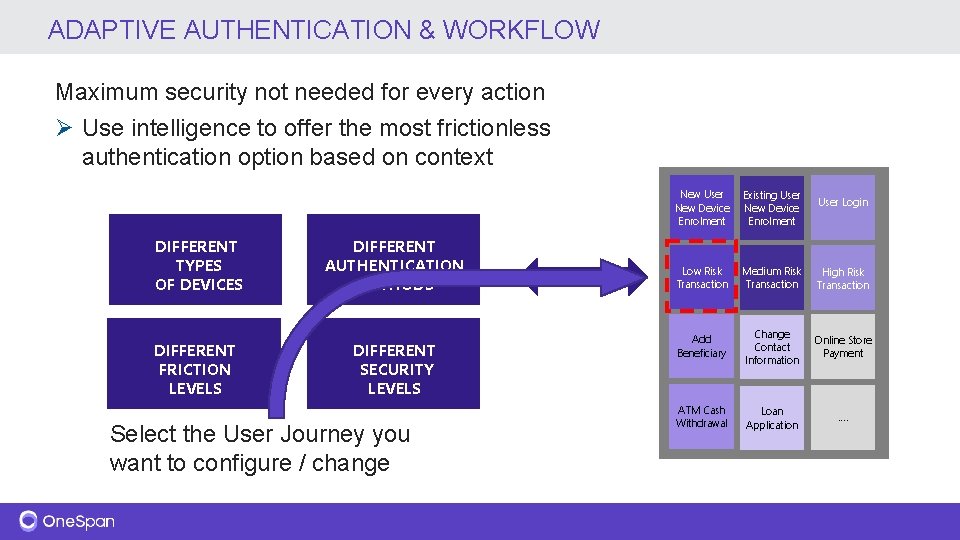
ADAPTIVE AUTHENTICATION & WORKFLOW Maximum security not needed for every action Ø Use intelligence to offer the most frictionless authentication option based on context DIFFERENT TYPES OF DEVICES DIFFERENT FRICTION LEVELS DIFFERENT AUTHENTICATION METHODS DIFFERENT SECURITY LEVELS Select the User Journey you want to configure / change New User New Device Enrolment Existing User New Device Enrolment User Login Low Risk Transaction Medium Risk Transaction High Risk Transaction Add Beneficiary Change Contact Information Online Store Payment ATM Cash Withdrawal Loan Application ….
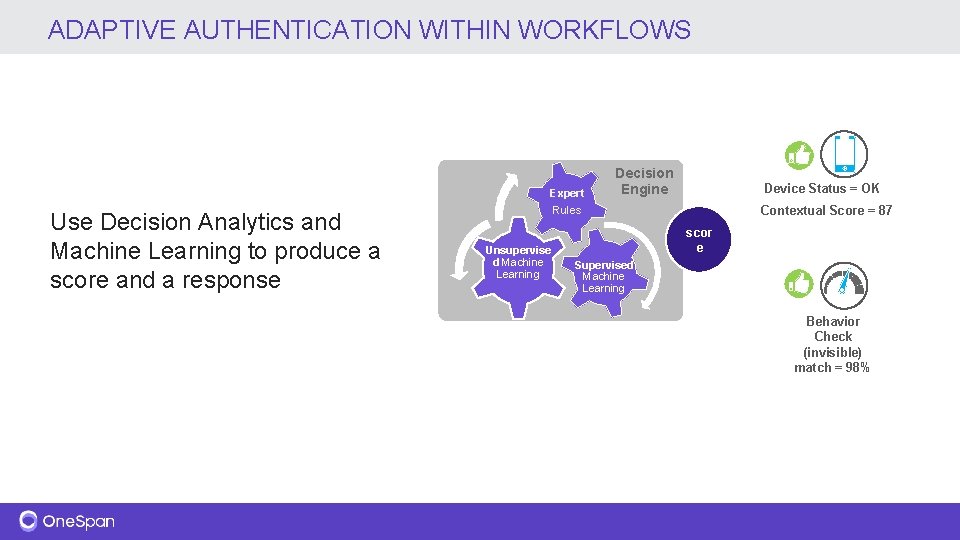
ADAPTIVE AUTHENTICATION WITHIN WORKFLOWS Expert Use Decision Analytics and Machine Learning to produce a score and a response Decision Engine Device Status = OK Contextual Score = 87 Rules Unsupervise d Machine Learning scor e Supervised Machine Learning Behavior Check (invisible) match = 98%
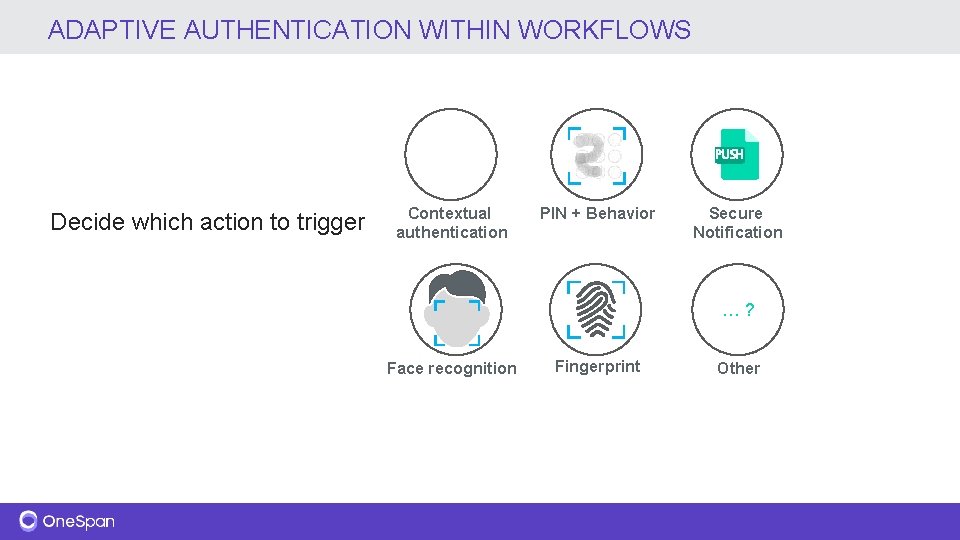
ADAPTIVE AUTHENTICATION WITHIN WORKFLOWS PUSH Decide which action to trigger Contextual authentication PIN + Behavior Secure Notification …? Face recognition Fingerprint Other
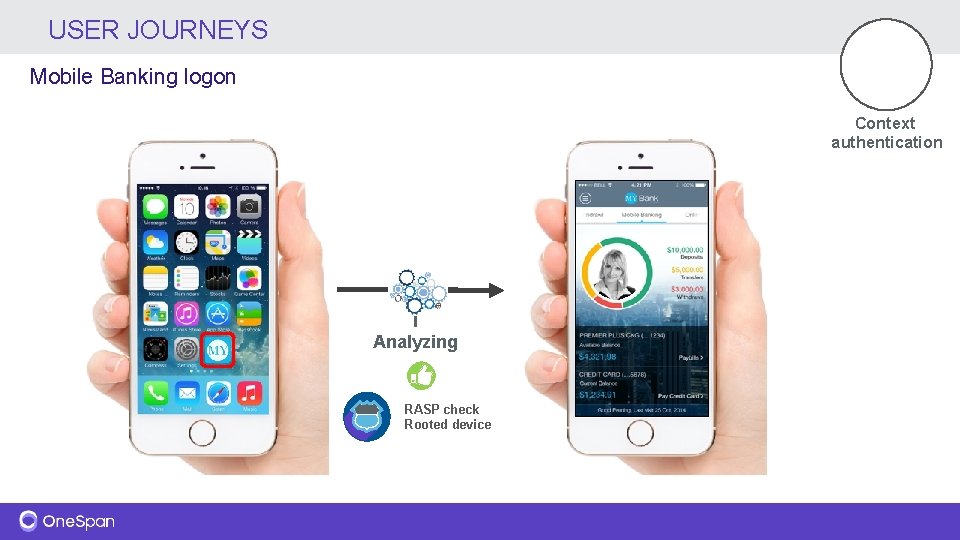
USER JOURNEYS Mobile Banking logon Context authentication Analyzing RASP check Rooted device
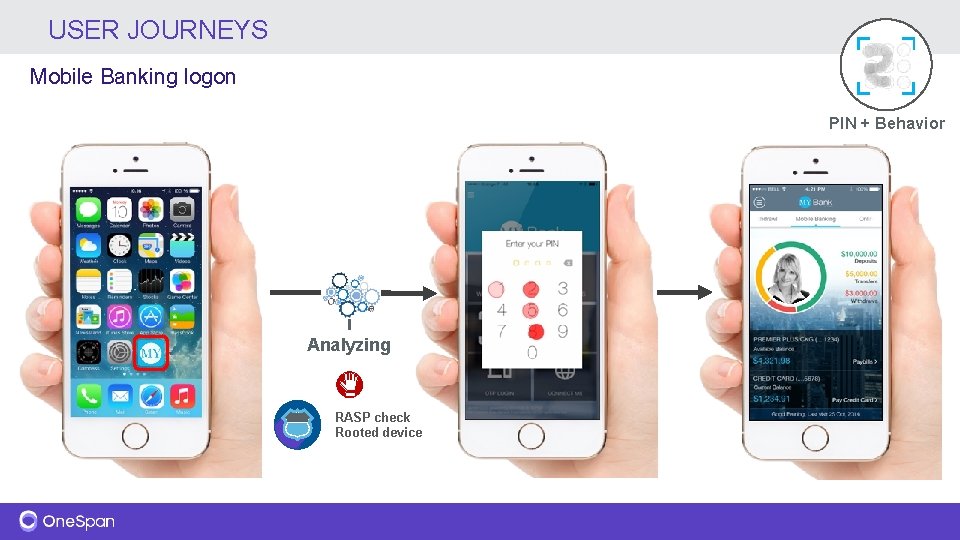
USER JOURNEYS Mobile Banking logon PIN + Behavior Analyzing RASP check Rooted device
CHALLENGE 5 - ADVANCED REGULATION, E. G. PSD 2 Strong Customer Authentication – Fraud Monitoring & TRA - multipurpose device protection - … Different Security Levels (No MFA & No TRM; No MFA, but TRM; SCA + TRM; No MFA, but TRA …) ? One solution allowing banks to be compliant with PSD 2 SCA RTS © 2018 One. Span
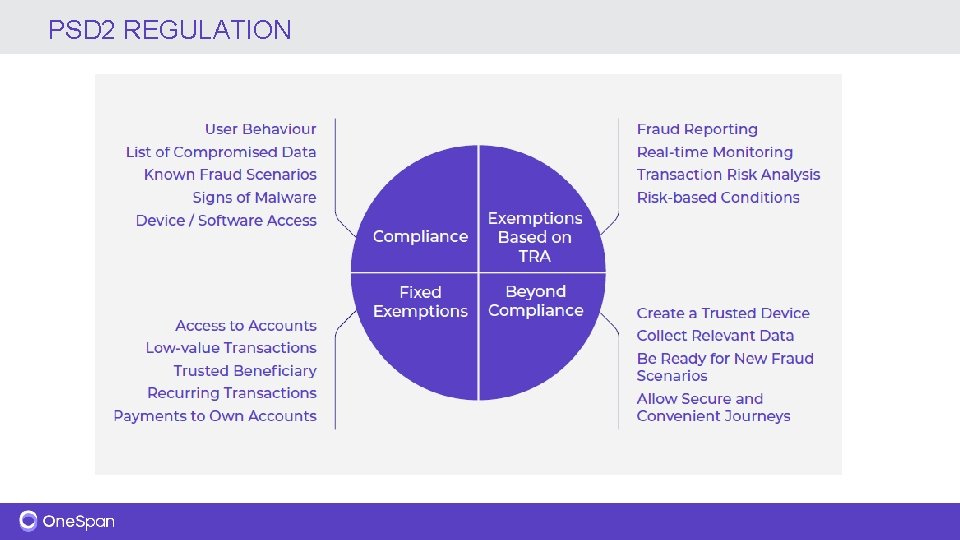
PSD 2 REGULATION
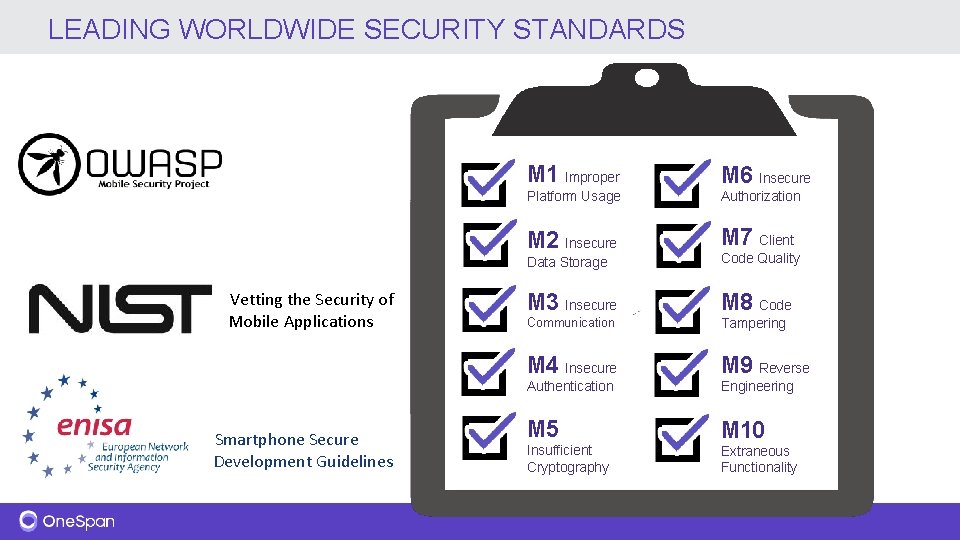
LEADING WORLDWIDE SECURITY STANDARDS Vetting the Security of Mobile Applications Smartphone Secure Development Guidelines M 1 Improper M 6 Insecure Platform Usage Authorization M 2 Insecure M 7 Client Data Storage Code Quality M 3 Insecure M 8 Code Communication Tampering M 4 Insecure M 9 Reverse Authentication Engineering M 5 M 10 Insufficient Cryptography Extraneous Functionality
ONESPAN TRUSTED IDENTITY PLATFORM
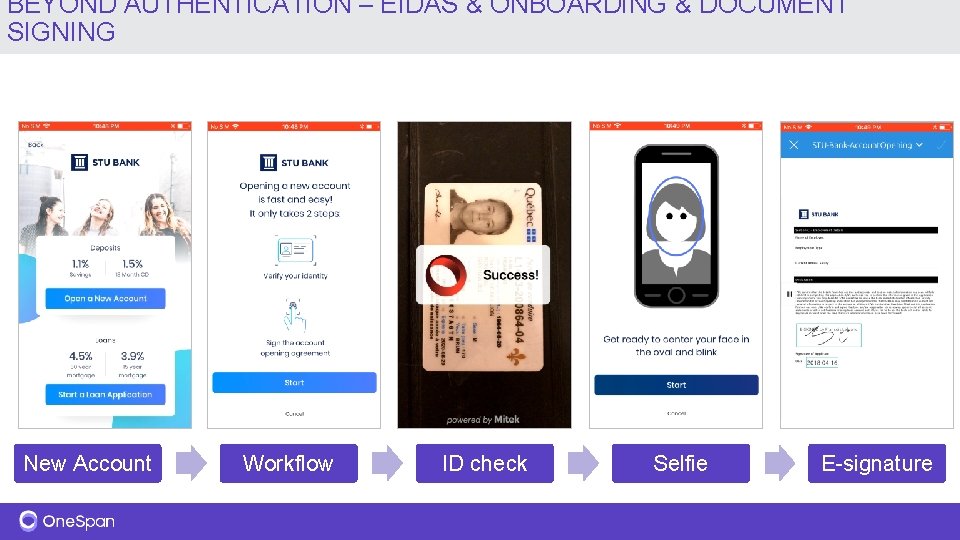
BEYOND AUTHENTICATION – EIDAS & ONBOARDING & DOCUMENT SIGNING Face recognition New Account Workflow ID check Selfie E-signature
THANK YOU! Giovanni Carnovale Regional Sales Manager – Central & Eastern Europe M: +41789645131 Giovanni. Carnovale@onespan. com