Virtual Directory Use Cases Mc Kesson The World
- Slides: 33
Virtual Directory Use Cases Mc. Kesson
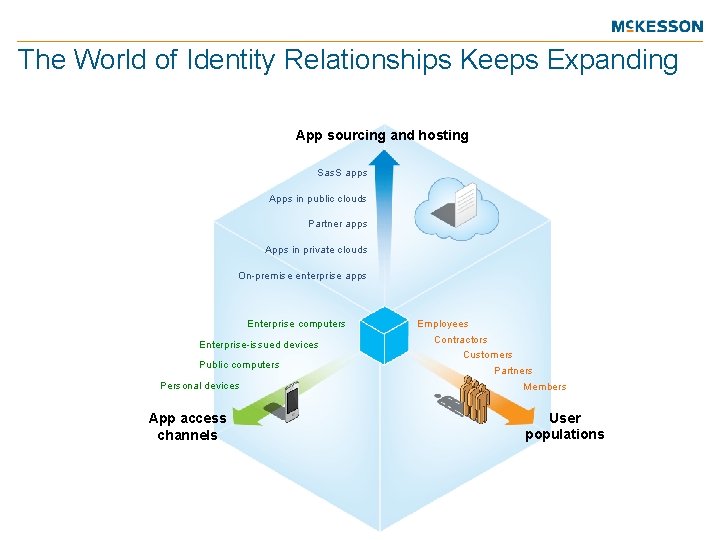
The World of Identity Relationships Keeps Expanding App sourcing and hosting Sas. S apps Apps in public clouds Partner apps Apps in private clouds On-premise enterprise apps Enterprise computers Enterprise-issued devices Public computers Personal devices App access channels Employees Contractors Customers Partners Members User populations
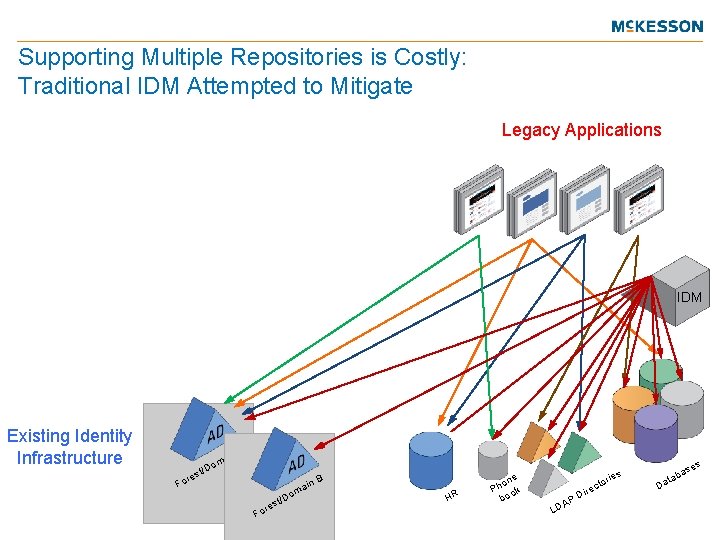
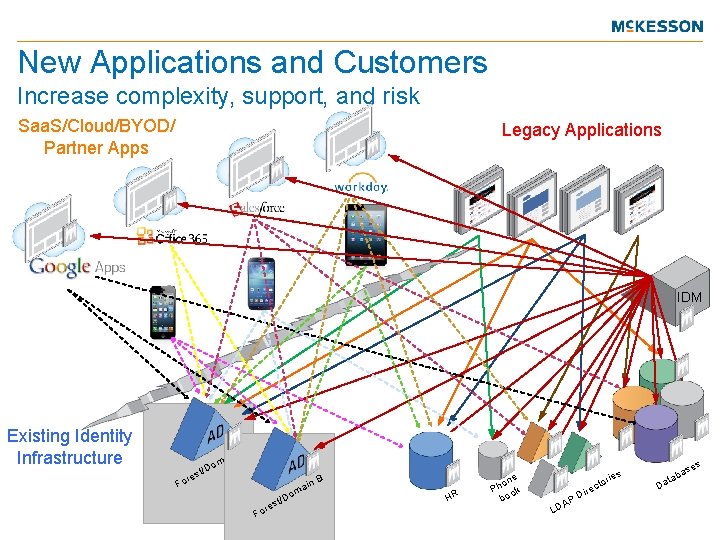
Supporting Multiple Repositories is Costly: Traditional IDM Attempted to Mitigate Legacy Applications IDM Existing Identity Infrastructure F s ore a om A in t/D i ma F Do st/ e r o n B HR e on Ph ok bo rec LD Di AP es as s ie tor D b ata
New Applications and Customers Increase complexity, support, and risk Saa. S/Cloud/BYOD/ Partner Apps Legacy Applications IDM Existing Identity Infrastructure F s ore a om A in t/D i ma F Do st/ e r o n B HR e on Ph ok bo rec ie tor LD Di AP es as s D b ata
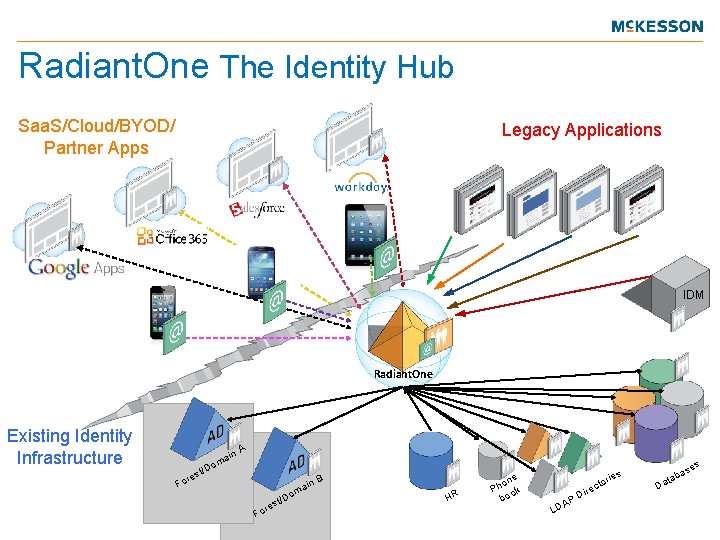
Radiant. One The Identity Hub Saa. S/Cloud/BYOD/ Partner Apps Legacy Applications IDM Radiant. One Existing Identity Infrastructure F s ore a om A in t/D i ma F Do st/ e r o n B HR e on Ph ok bo rec ie tor LD Di AP es as s D b ata
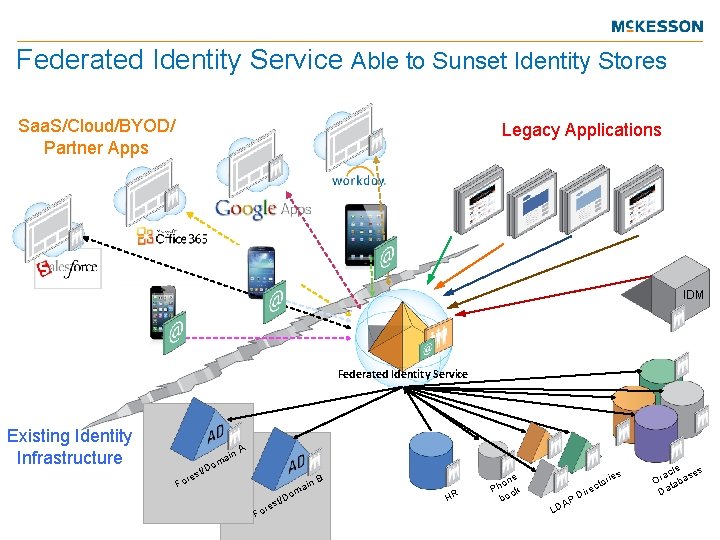
Federated Identity Service Able to Sunset Identity Stores Saa. S/Cloud/BYOD/ Partner Apps Legacy Applications IDM Federated Identity Service Existing Identity Infrastructure A in D st/ re Fo a om m Do F st/ ore B ain HR e on Ph ok bo re L i P D A D ies r cto le es ac s Or taba a D
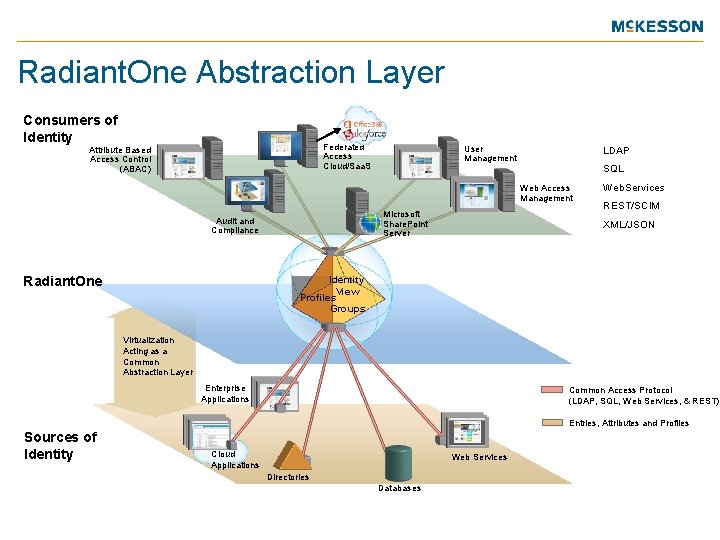
Radiant. One Abstraction Layer Consumers of Identity Federated Access Cloud/Saa. S Attribute Based Access Control (ABAC) User Management LDAP SQL Web Access Management Microsoft Share. Point Server Audit and Compliance Web. Services REST/SCIM XML/JSON Identity View Profiles Groups Radiant. One Virtualization Acting as a Common Abstraction Layer Enterprise Applications Common Access Protocol (LDAP, SQL, Web Services, & REST) Entries, Attributes and Profiles Sources of Identity Cloud Applications Web Services Directories Databases
Mc. Kesson At-a-Glance • Founded in 1833 • Ranked 14 th on Fortune’s list, with $140. 0 billion in revenues • Headquartered in San Francisco • More than 42, 000 employees • Two segments: Distribution Solutions and Technology Solutions • Total focused on health care . and largest services company Mc. Kesson is one of America’s oldest 8 Mc. Kesson Corporation
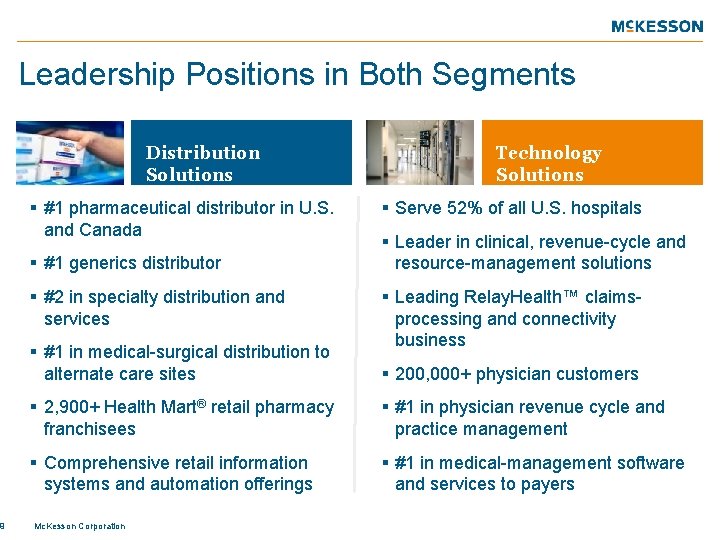
9 Leadership Positions in Both Segments Distribution Solutions § #1 pharmaceutical distributor in U. S. and Canada § #1 generics distributor § #2 in specialty distribution and services § #1 in medical-surgical distribution to alternate care sites Technology Solutions § Serve 52% of all U. S. hospitals § Leader in clinical, revenue-cycle and resource-management solutions § Leading Relay. Health™ claimsprocessing and connectivity business § 200, 000+ physician customers § 2, 900+ Health Mart® retail pharmacy franchisees § #1 in physician revenue cycle and practice management § Comprehensive retail information systems and automation offerings § #1 in medical-management software and services to payers Mc. Kesson Corporation
Information Security Architecture & Services We Deliver Security Solutions to Enable and Protect Businesses by: • Offering a comprehensive portfolio of security services supported by core security capabilities that meet Mc. Kesson customers’ regulatory, industry and internal requirements • Enabling Mc. Kesson business units establish trust between organizations, partners, third party users, and customers through federation, certificate services and secure collaboration • Increasing our competitive advantage in security solutions through ongoing analysis of the latest security architecture trends and product offerings such as cloud security and security as a service We are members of Mc. Kesson’s Information Security and Risk Management, providing a range of services including security consulting and operations, IT risk management and incident management. 10 Mc. Kesson Corporation
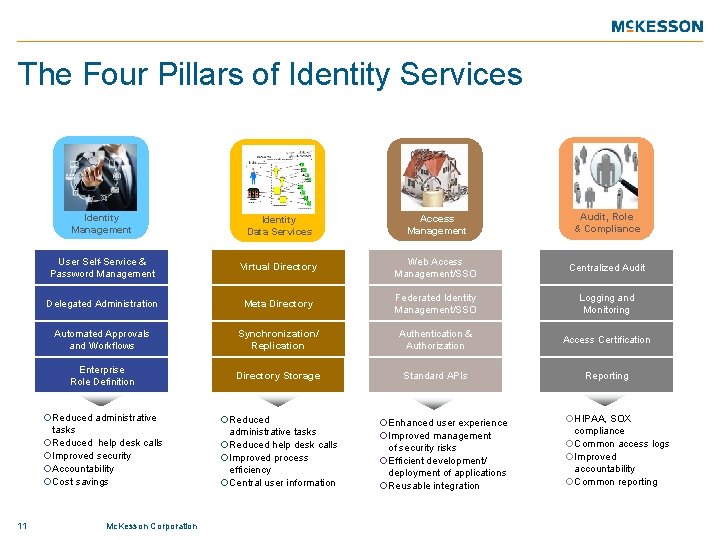
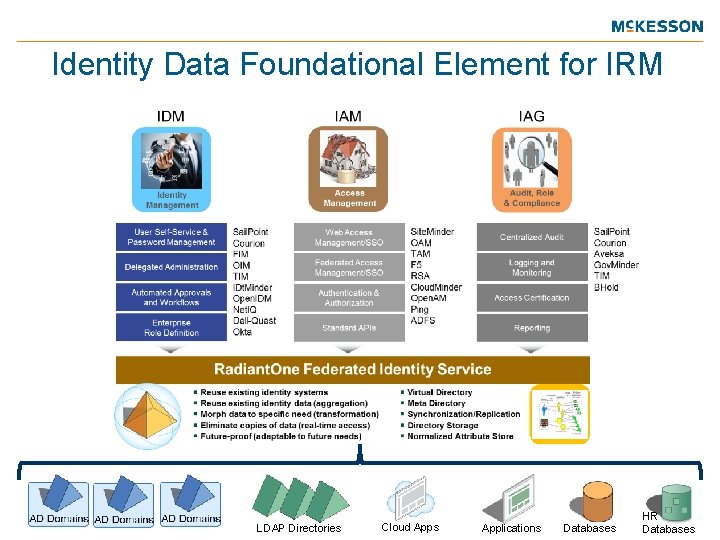
The Four Pillars of Identity Services 11 Identity Management Identity Data Services Access Management Audit, Role & Compliance User Self-Service & Password Management Virtual Directory Web Access Management/SSO Centralized Audit Delegated Administration Meta Directory Federated Identity Management/SSO Logging and Monitoring Automated Approvals and Workflows Synchronization/ Replication Authentication & Authorization Access Certification Enterprise Role Definition Directory Storage Standard APIs Reporting ¡Reduced administrative tasks ¡Reduced help desk calls ¡Improved security ¡Accountability ¡Cost savings ¡Reduced administrative tasks ¡Reduced help desk calls ¡Improved process efficiency ¡Central user information Mc. Kesson Corporation ¡Enhanced user experience ¡Improved management of security risks ¡Efficient development/ deployment of applications ¡Reusable integration ¡HIPAA, SOX compliance ¡Common access logs ¡Improved accountability ¡Common reporting
Identity Data Foundational Element for IRM LDAP Directories Cloud Apps Applications Databases HR Databases
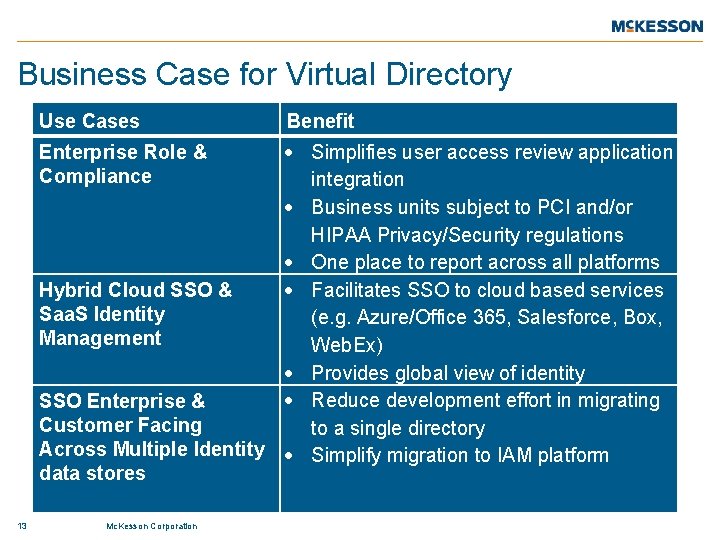
Business Case for Virtual Directory Use Cases Benefit Simplifies user access review application integration Business units subject to PCI and/or HIPAA Privacy/Security regulations One place to report across all platforms Facilitates SSO to cloud based services Hybrid Cloud SSO & Saa. S Identity (e. g. Azure/Office 365, Salesforce, Box, Management Web. Ex) Provides global view of identity Reduce development effort in migrating SSO Enterprise & Customer Facing to a single directory Across Multiple Identity Simplify migration to IAM platform data stores Enterprise Role & Compliance 13 Mc. Kesson Corporation
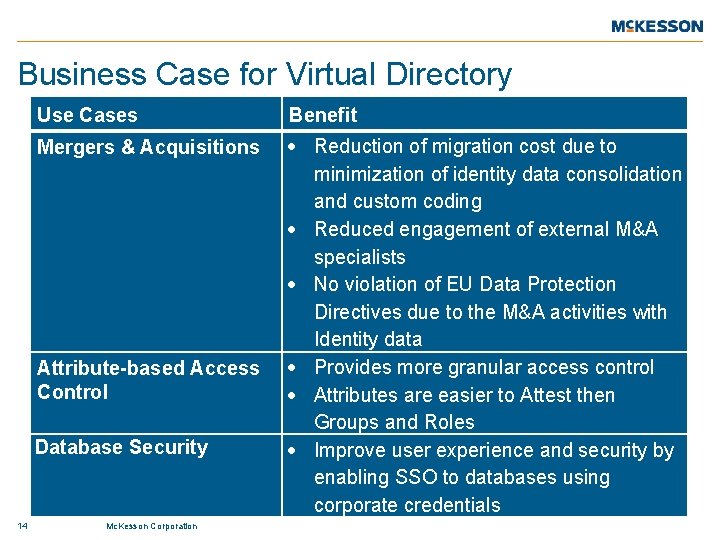
Business Case for Virtual Directory Use Cases Benefit Mergers & Acquisitions Reduction of migration cost due to minimization of identity data consolidation and custom coding Reduced engagement of external M&A specialists No violation of EU Data Protection Directives due to the M&A activities with Identity data Provides more granular access control Attributes are easier to Attest then Groups and Roles Improve user experience and security by enabling SSO to databases using corporate credentials Attribute-based Access Control Database Security 14 Mc. Kesson Corporation
Achieving SSO across Identity Silos 15 Mc. Kesson Corporation Confidential and Proprietary
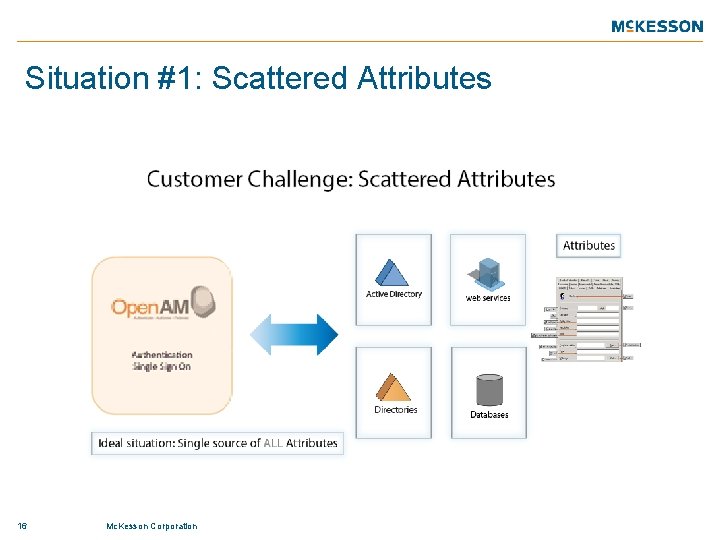
Situation #1: Scattered Attributes 16 Mc. Kesson Corporation
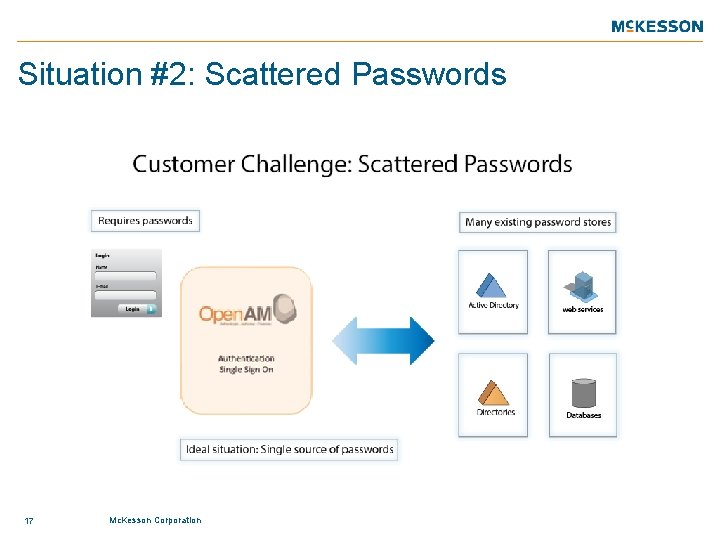
Situation #2: Scattered Passwords 17 Mc. Kesson Corporation
Approach#1: SSO with Open. AM/DJ/IDM Alone • Design Open. DJ schema to store all the user attributes within targeted SSO application(s) – A significant effort if targeted applications have various overlapping user attributes • Migrating existing user authentication store to Open. DJ (leave the user authorization local to the individual applications) – this is a significant effort, especially when user store is RDBMS instead of LDAP • Use Open. AM for access management for the SSO portal • Change each individual application to integrate with Open. AM 18 Mc. Kesson Corporation
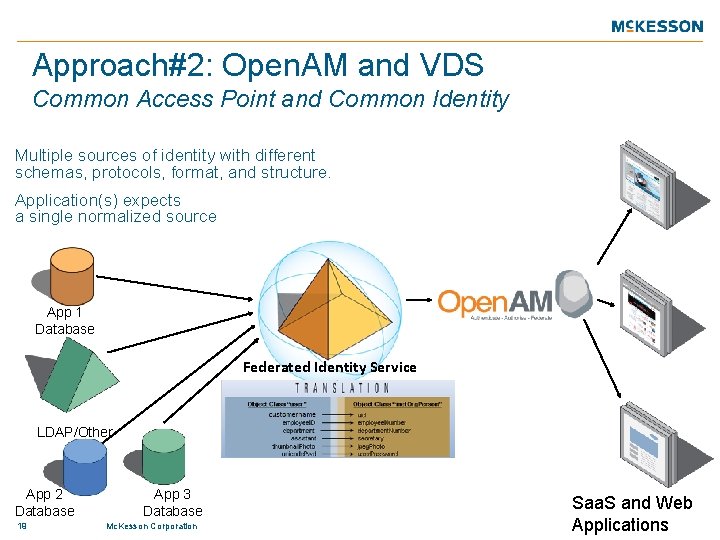
Approach#2: Open. AM and VDS Common Access Point and Common Identity Multiple sources of identity with different schemas, protocols, format, and structure. Application(s) expects a single normalized source App 1 Database Federated Identity Service LDAP/Other App 2 Database 19 App 3 Database Mc. Kesson Corporation Saa. S and Web Applications
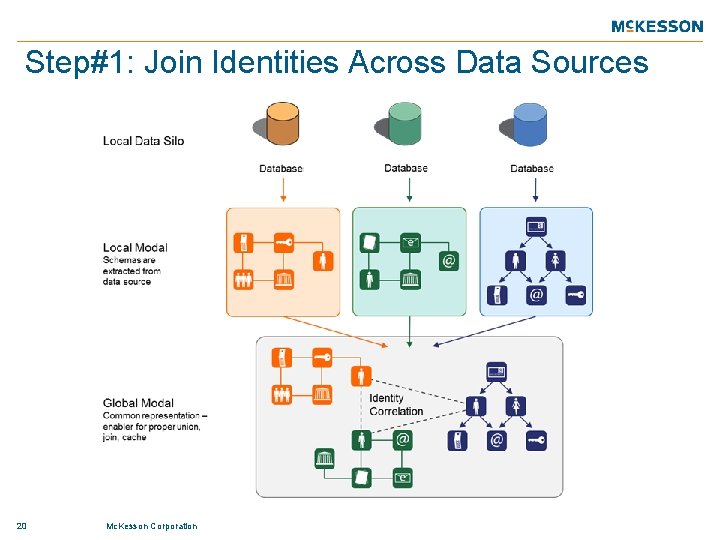
Step#1: Join Identities Across Data Sources 20 Mc. Kesson Corporation
Benefits of Radiant. One and Forge. Rock • Improved user experience where user only needs to login once and be able to access one or multiple applications • SSO implementation has minimal impact on existing applications since there is no user data migration • Self-service password user management enhances usability while increasing security and reduces the need for helpdesk support • Standards-based solution reduces vendor lock-in • Established Identity Data Service benefits mobile and cloud services 22 Mc. Kesson Corporation
Joining Data across AD Domains 23 Mc. Kesson Corporation Confidential and Proprietary
Challenge – Two Autonomous Domains Mc. Kesson employees primarily reside in one AD domain (IT) A business unit’s (BU) employees are being migrated from their AD domain to the IT AD domain The BU domain also includes non-employee accounts that cannot be migrated to the IT domain Distribution lists originating in the BU and migrated to IT may contain nonemployee accounts that will remain in the BU Changes made to the BU distribution lists are automatically replicated to the corresponding IT distribution lists Distribution lists cannot be managed across the BU and IT domains without logging into each domain separately to add and remove uses in each domain Requiring logging in and out of each domain to make a single update introduces unacceptable management overhead and increases risk of error. 24 Mc. Kesson Corporation
Solution Radiant Logic Virtual Directory Service (VDS) is installed and configured to access both AD domains • VDS extracts the users and groups from both domains • A view is created in the VDS as a branch that includes the groups and users from the BU domain including the non-employee accounts • Another view is created in the VDS as a branch that includes the groups and users from the IT domain • Use the VDS Groups Builder to add and remove users to distribution lists in the BU and IT domains in a single interface • Groups Builder allows add user function to provide a pick-list of available user accounts to add or remove. • Creating new distribution groups is also an option 25 Mc. Kesson Corporation
Mergers and Acquisitions (M & A) 26 Mc. Kesson Corporation Confidential and Proprietary
Mergers & Acquisitions Why is it important to the business? • Value of M&A impacted by rate of assimilation of users and resources • M&A targets have vastly different IT structures and conventions • Need a layer to provide translation and transformation • Maintain business continuity (first do no harm!) • Provide access to applications across both environments • Migrate applications and users at desired pace 27 Mc. Kesson Corporation
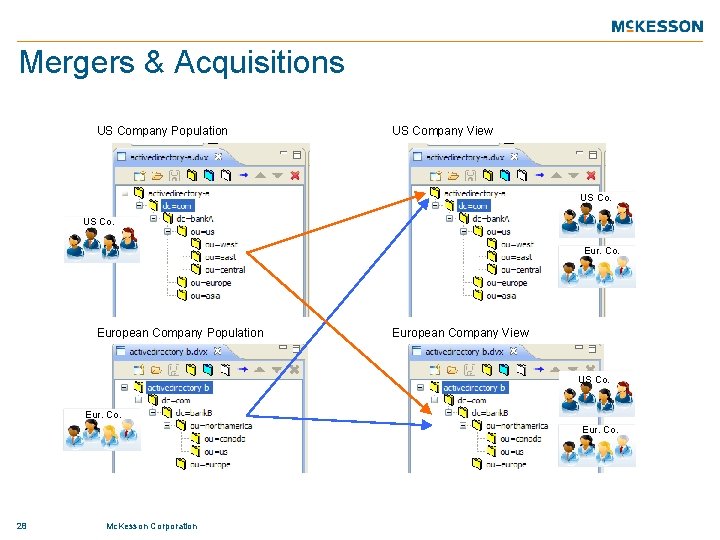
Mergers & Acquisitions US Company Population US Company View US Co. Eur. Co. European Company Population European Company View US Co. Eur. Co. 28 Mc. Kesson Corporation
Configuration and Security Existing synchronization will duplicate additions made to groups in the BU domain to the corresponding groups in the IT domain Filter initial views from BU and IT to only provide access to specific distribution groups and exclude security groups Filter the attributes of the user accounts in the view to simplify display and hide any sensitive data Use ACL’s in VDS to tailor access to the BU and IT views Limit access to view or update the users and distribution groups only to select individuals or members of select security groups 29 Mc. Kesson Corporation
Technical Benefits of Virtual Directory Approach • Build a global list of all identities and a complete profile of each identity usually in days — not months. • Eliminate any manual re-architecting, schema extensions, synchronization, or construction of complex code in order to achieve future state identity repository. • Safely expose true identities to external applications and partners through a secure virtual layer. • Reduce or eliminate the need to establish new trusts across AD domains and forests. • Migrate existing groups, and dynamically create new groups based on attributes found in legacy repositories. • Guarantee directory-like performance 30 Mc. Kesson Corporation
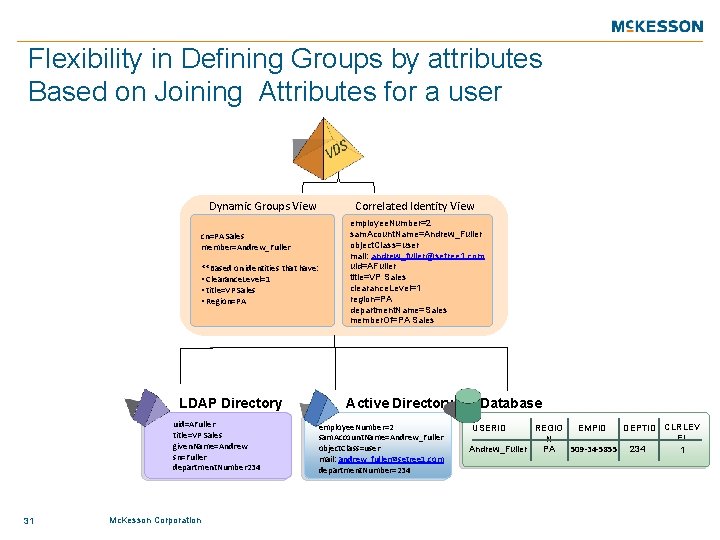
Flexibility in Defining Groups by attributes Based on Joining Attributes for a user Dynamic Groups View Correlated Identity View cn=PA Sales member=Andrew_Fuller **Based on identities that have: • Clearance. Level=1 • title=VP Sales • Region=PA LDAP Directory uid=AFuller title=VP Sales given. Name=Andrew sn=Fuller department. Number 234 31 Mc. Kesson Corporation employee. Number=2 sam. Acount. Name=Andrew_Fuller object. Class=user mail: andrew_fuller@setree 1. com uid=AFuller title=VP Sales clearance. Level=1 region=PA department. Name=Sales member. Of=PA Sales Active Directory employee. Number=2 sam. Account. Name=Andrew_Fuller object. Class=user mail: andrew_fuller@setree 1. com department. Number=234 Database REGIO EMPID DEPTID CLRLEV EL N 509 -34 -5855 234 Andrew_Fuller PA 1 USERID
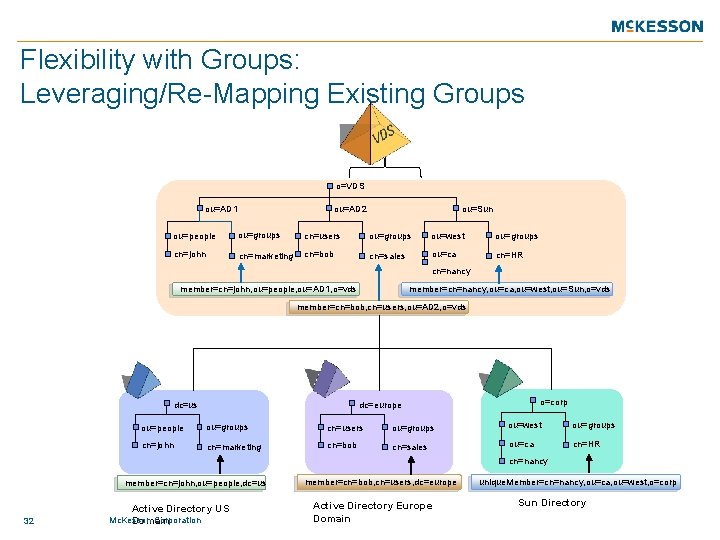
Flexibility with Groups: Leveraging/Re-Mapping Existing Groups o=VDS ou=AD 1 ou=AD 2 ou=Sun ou=people ou=groups cn=users ou=groups ou=west ou=groups cn=john cn=marketing cn=bob cn=sales ou=ca cn=HR cn=nancy member=cn=nancy, ou=ca, ou=west, ou=Sun, o=vds member=cn=john, ou=people, ou=AD 1, o=vds member=cn=bob, cn=users, ou=AD 2, o=vds dc=us o=corp dc=europe ou=people ou=groups cn=users ou=groups ou=west ou=groups cn=john cn=marketing cn=bob cn=sales ou=ca cn=HR cn=nancy member=cn=john, ou=people, dc=us 32 Active Directory US Mc. Kesson Corporation Domain member=cn=bob, cn=users, dc=europe Active Directory Europe Domain unique. Member=cn=nancy, ou=ca, ou=west, o=corp Sun Directory
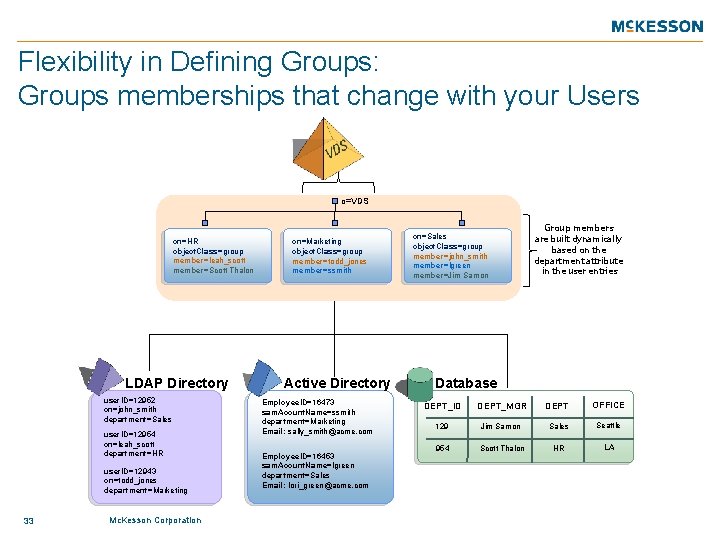
Flexibility in Defining Groups: Groups memberships that change with your Users o=VDS cn=HR object. Class=group member=leah_scott member=Scott Thalon LDAP Directory user. ID=12952 cn=john_smith department=Sales user. ID=12954 cn=leah_scott department=HR user. ID=12943 cn=todd_jones department=Marketing 33 Mc. Kesson Corporation cn=Marketing object. Class=group member=todd_jones member=ssmith Active Directory Employee. ID=16473 sam. Acount. Name=ssmith department=Marketing Email: sally_smith@acme. com Employee. ID=16453 sam. Acount. Name=lgreen department=Sales Email: lori_green@acme. com cn=Sales object. Class=group member=john_smith member=lgreen member=Jim Samon Group members are built dynamically based on the department attribute in the user entries Database DEPT_ID DEPT_MGR DEPT OFFICE 129 Jim Samon Sales Seattle 954 Scott Thalon HR LA
Q&A