Modernizing Your SOC David Swift Security Geek CISSP
- Slides: 14
Modernizing Your SOC David Swift – Security Geek CISSP, GSEC, GCIH, GCIA, GSNA, MCSE, MCNE, ACTP… dswift@securonix. com © 2015 Securonix 1
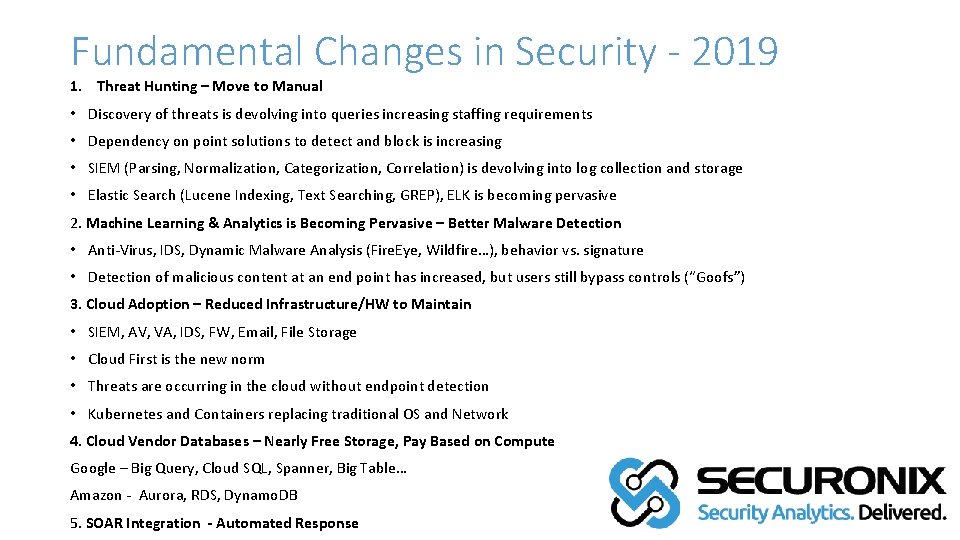
Fundamental Changes in Security - 2019 1. Threat Hunting – Move to Manual • Discovery of threats is devolving into queries increasing staffing requirements • Dependency on point solutions to detect and block is increasing • SIEM (Parsing, Normalization, Categorization, Correlation) is devolving into log collection and storage • Elastic Search (Lucene Indexing, Text Searching, GREP), ELK is becoming pervasive 2. Machine Learning & Analytics is Becoming Pervasive – Better Malware Detection • Anti-Virus, IDS, Dynamic Malware Analysis (Fire. Eye, Wildfire…), behavior vs. signature • Detection of malicious content at an end point has increased, but users still bypass controls (“Goofs”) 3. Cloud Adoption – Reduced Infrastructure/HW to Maintain • SIEM, AV, VA, IDS, FW, Email, File Storage • Cloud First is the new norm • Threats are occurring in the cloud without endpoint detection • Kubernetes and Containers replacing traditional OS and Network 4. Cloud Vendor Databases – Nearly Free Storage, Pay Based on Compute Google – Big Query, Cloud SQL, Spanner, Big Table… Amazon - Aurora, RDS, Dynamo. DB 5. SOAR Integration - Automated Response
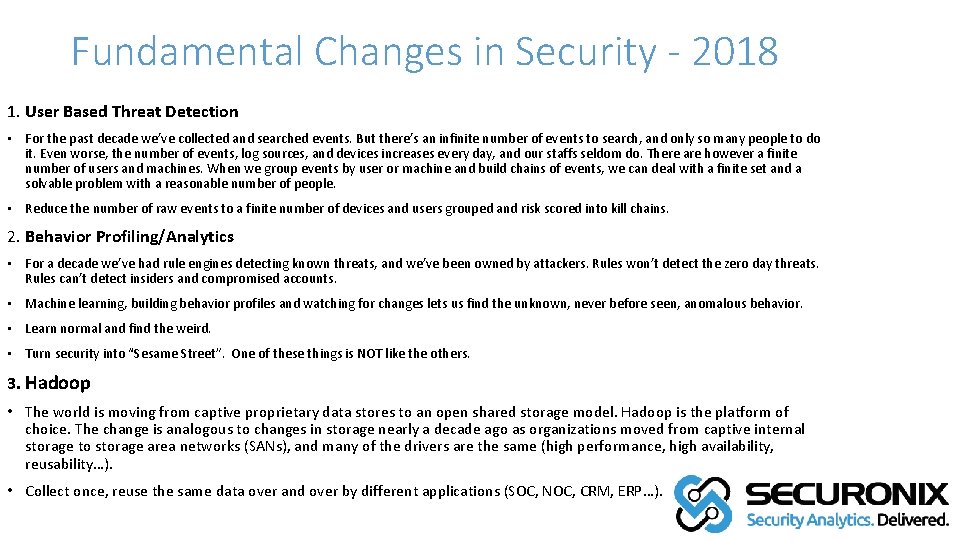
Fundamental Changes in Security - 2018 1. User Based Threat Detection • For the past decade we’ve collected and searched events. But there’s an infinite number of events to search, and only so many people to do it. Even worse, the number of events, log sources, and devices increases every day, and our staffs seldom do. There are however a finite number of users and machines. When we group events by user or machine and build chains of events, we can deal with a finite set and a solvable problem with a reasonable number of people. • Reduce the number of raw events to a finite number of devices and users grouped and risk scored into kill chains. 2. Behavior Profiling/Analytics • For a decade we’ve had rule engines detecting known threats, and we’ve been owned by attackers. Rules won’t detect the zero day threats. Rules can’t detect insiders and compromised accounts. • Machine learning, building behavior profiles and watching for changes lets us find the unknown, never before seen, anomalous behavior. • Learn normal and find the weird. • Turn security into “Sesame Street”. One of these things is NOT like the others. 3. Hadoop • The world is moving from captive proprietary data stores to an open shared storage model. Hadoop is the platform of choice. The change is analogous to changes in storage nearly a decade ago as organizations moved from captive internal storage to storage area networks (SANs), and many of the drivers are the same (high performance, high availability, reusability…). • Collect once, reuse the same data over and over by different applications (SOC, NOC, CRM, ERP…).
Key Security Problems Today • Not Enough People • Process has been Abandoned • Log All and ANALYZE • Collect, Detect, Respond • Garbage In, Garbage Out (GIGO) • Collection without enrichment and correlation makes for a “data swamp” • Search by Meaningful Value Fails • (User Name, Source IP, Department)
One Ring! • Alphabet Soup • SOC, SIEM, UEBA, SOAR • IDS, FW, AV, VA, IAM, EDR, EMR I do NOT Want ANOTHER Damn Tool! One Ring to Rule Them All • Visibility and Targeting • Risk Based Alerting • Threat Triangulation • Automated Response One Integrated Platform and View!
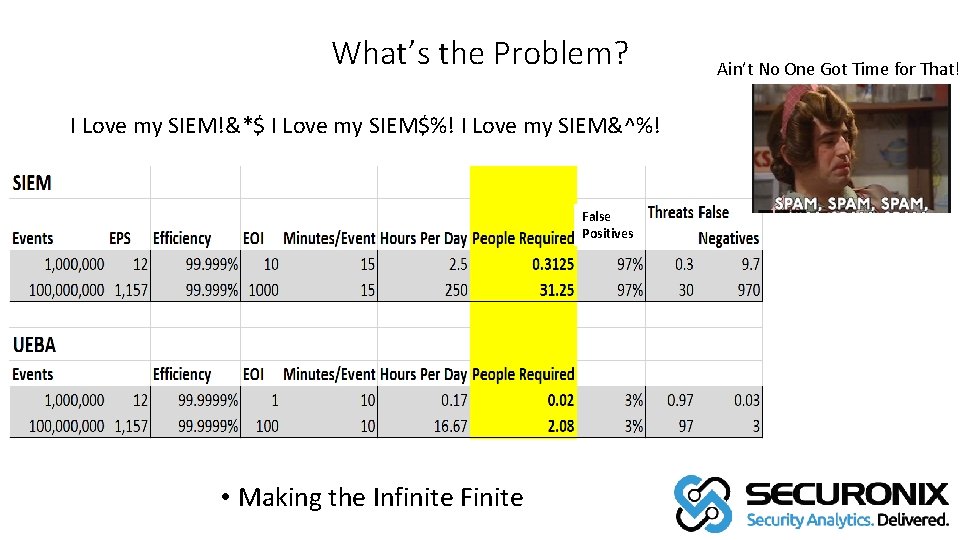
What’s the Problem? I Love my SIEM!&*$ I Love my SIEM$%! I Love my SIEM&^%! False Positives • Making the Infinite Finite Ain’t No One Got Time for That!
Tired of Text? Slack, Email, and SMS, Oh My! If they page me tonight, someone’s Gonna Die!
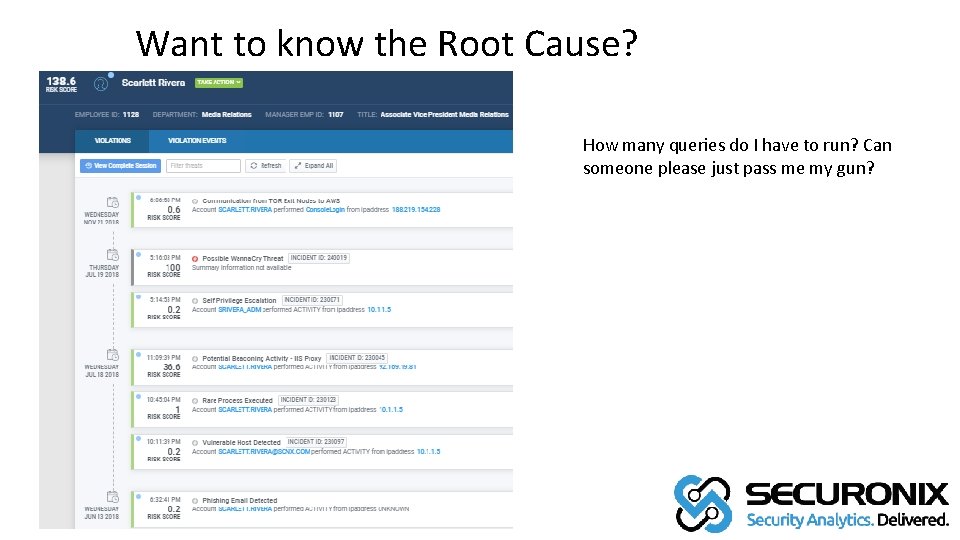
Want to know the Root Cause? How many queries do I have to run? Can someone please just pass me my gun? Want to know the root cause?
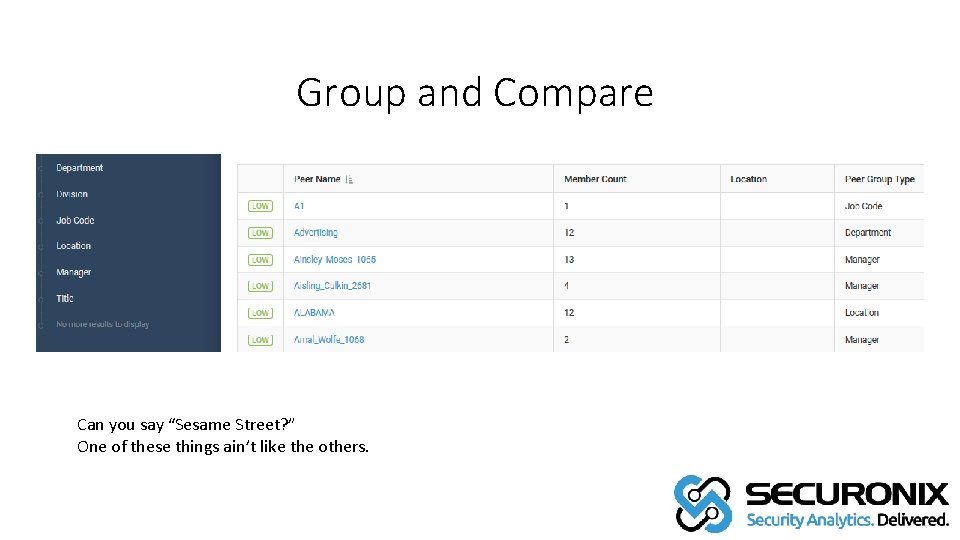
Group and Compare Can you say “Sesame Street? ” One of these things ain’t like the others.
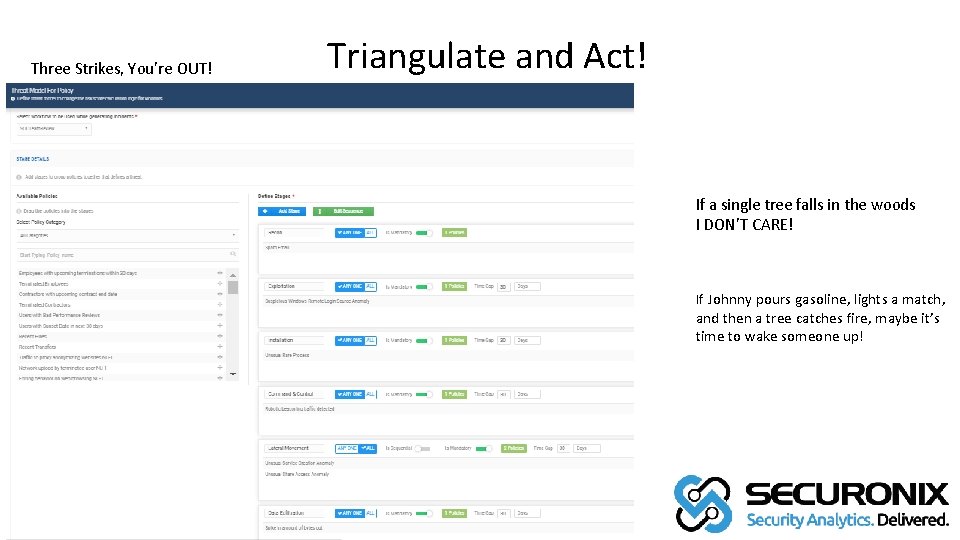
Three Strikes, You’re OUT! Triangulate and Act! If a single tree falls in the woods I DON’T CARE! Triangulate and Act If Johnny pours gasoline, lights a match, and then a tree catches fire, maybe it’s time to wake someone up!
How do we solve for X? A. Collect Logs (Security + Context + Apps) B. Configure Detection for 5 Patterns (EOI) C. Group (by user or machine) D. Model Responses (Playbooks) Five Patterns 1. Repeat Attacks – Everything Counts in Large Amounts 2. Success After Fail – Kept Trying Until they Found a Way In 3. Never Before Seen – First Use, Unusual Activity 4. No One Else Does That – Peer Anomaly 5. How Much? ? - Quantity or Volume Spike
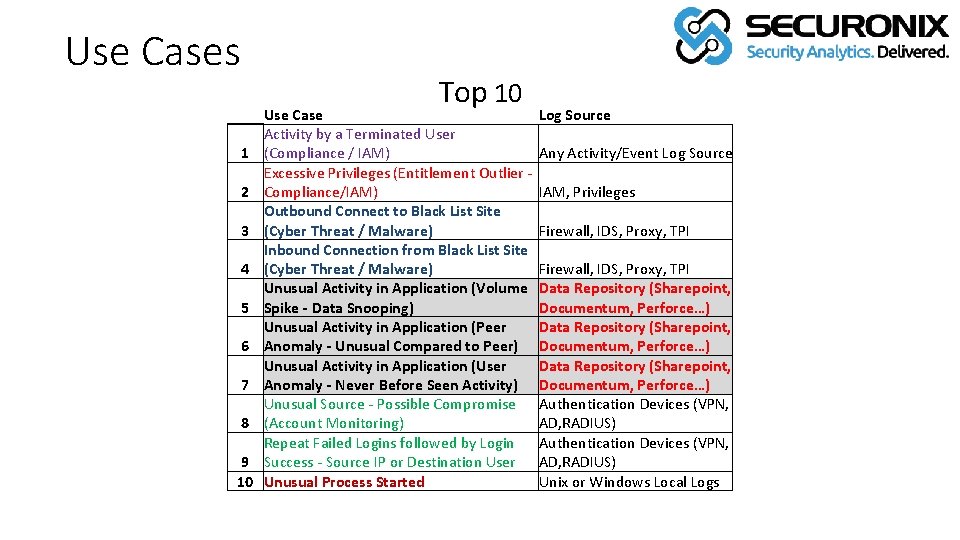
Use Cases Top 10 1 2 3 4 5 6 7 8 9 10 Use Case Log Source Activity by a Terminated User (Compliance / IAM) Any Activity/Event Log Source Excessive Privileges (Entitlement Outlier - Compliance/IAM) IAM, Privileges Outbound Connect to Black List Site (Cyber Threat / Malware) Firewall, IDS, Proxy, TPI Inbound Connection from Black List Site (Cyber Threat / Malware) Firewall, IDS, Proxy, TPI Unusual Activity in Application (Volume Data Repository (Sharepoint, Spike - Data Snooping) Documentum, Perforce…) Unusual Activity in Application (Peer Data Repository (Sharepoint, Anomaly - Unusual Compared to Peer) Documentum, Perforce…) Unusual Activity in Application (User Data Repository (Sharepoint, Anomaly - Never Before Seen Activity) Documentum, Perforce…) Unusual Source - Possible Compromise Authentication Devices (VPN, (Account Monitoring) AD, RADIUS) Repeat Failed Logins followed by Login Authentication Devices (VPN, Success - Source IP or Destination User AD, RADIUS) Unusual Process Started Unix or Windows Local Logs
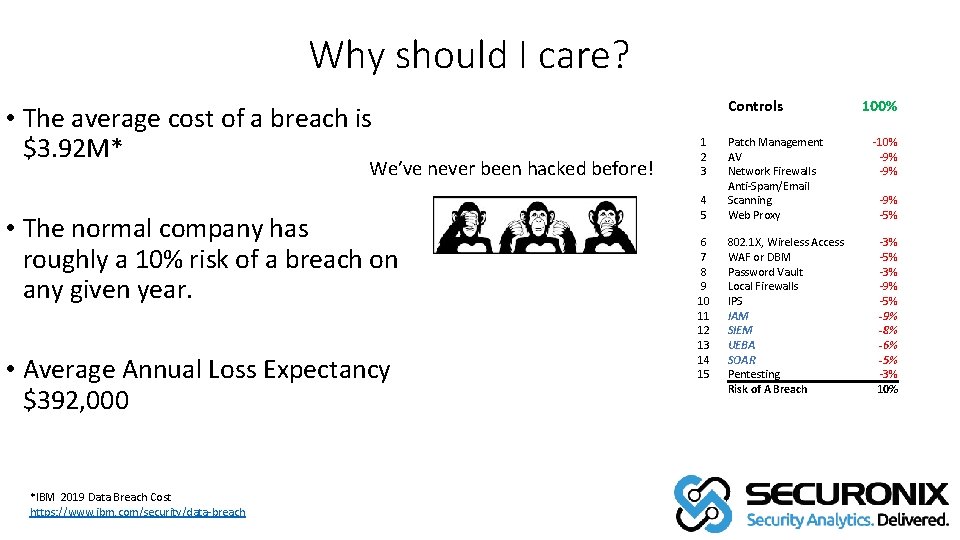
Why should I care? • The average cost of a breach is $3. 92 M* We’ve never been hacked before! • The normal company has roughly a 10% risk of a breach on any given year. • Average Annual Loss Expectancy $392, 000 *IBM 2019 Data Breach Cost https: //www. ibm. com/security/data-breach Controls 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 100% Patch Management AV Network Firewalls Anti-Spam/Email Scanning Web Proxy -10% -9% 802. 1 X, Wireless Access WAF or DBM Password Vault Local Firewalls IPS IAM SIEM UEBA SOAR Pentesting Risk of A Breach -3% -5% -3% -9% -5% -9% -8% -6% -5% -3% 10% -9% -5%
Thank You David Swift dswift@securonix. com 214 -724 -7174 www. securonix. com Offers 1. Deep Dive Demo 2. Use Case Workshop