Intrusion Detection System Snort What is Snort n
- Slides: 10
Intrusion Detection System Snort
What is Snort? n Free and Open Source Intrusion Detection System Monitor network traffic n Scan for protocol anomalies n Scan for packet payload signatures that represent potential attacks, worms, and unusual activities n Monitoring consoles available n Can be configured as an IPS n
Where should it be placed? n Snort Tap Placement n Natural Choke Points n Areas where the network topology creates a single traffic path n Artificial Choke Points n Exist n due to logical topology of the network Intranet Trust/Un-trust Zone Boundaries n Similar to Natural Choke Points but are intranetwork
How does it work? n Snort Rules Primarily a signature based detection engine n Example: n n alert tcp $TELNET_SERVERS 23 -> $EXTERNAL_NET any (msg: "TELNET root login"; flow: from_server, established; content: "login|3 A| root"; classtype: suspicious-login; sid: 719; rev: 7; ) n While indicative of attacks, leaks, and protocol violations, false positives are generated
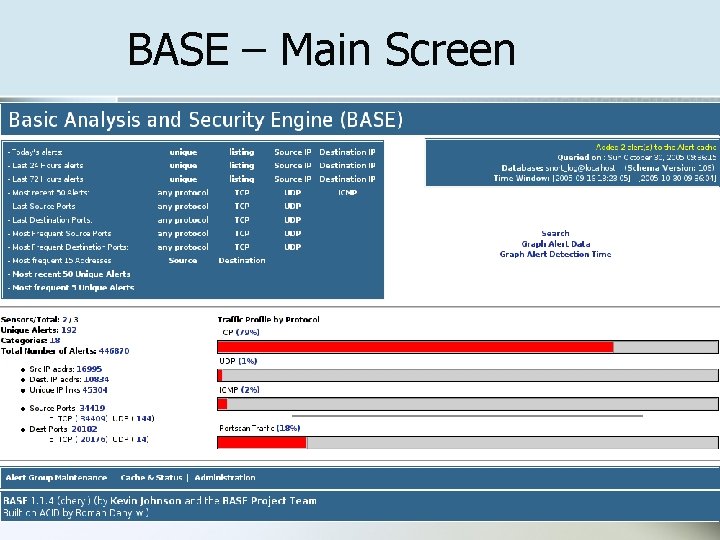
How to monitor? n BASE (Basic Analysis and Security Engine) Number of unique alerts n Alerts ordered by category n Today’s alert n Most frequent src/dest ports n
BASE – Main Screen
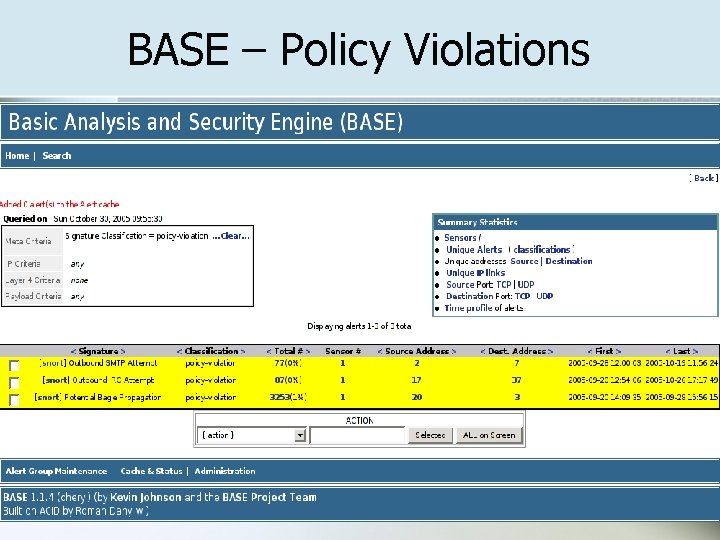
BASE – Policy Violations
Worm Propagation Analysis Example n n n Multiple Layers of Antivirus checkers in place: workstations, servers, email-stores, and email gateways Most active updating checkers gets new signatures every 15 minutes On September 2005, 3 bagle variants were released quickly AV companies alerted us, but workstations were affected Which of the 5000 workstations were affected?
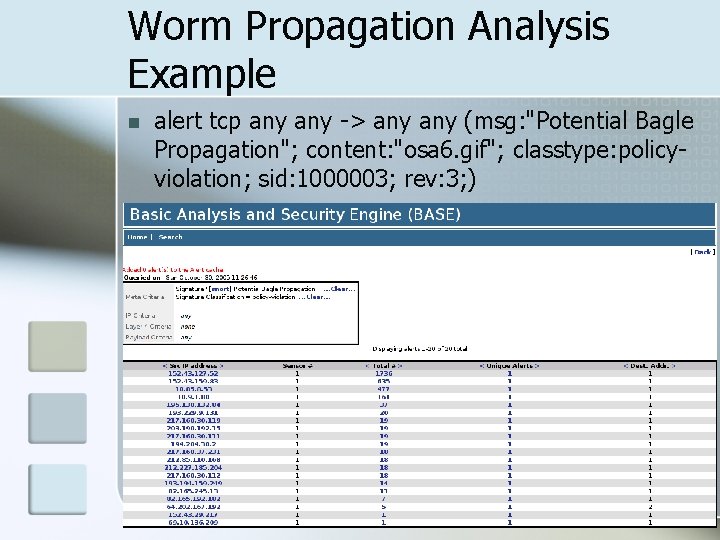
Worm Propagation Analysis Example n alert tcp any -> any (msg: "Potential Bagle Propagation"; content: "osa 6. gif"; classtype: policyviolation; sid: 1000003; rev: 3; )
Conclusion Snort provides another tool in the toolkit and can help provide information about exactly who’s talking to who on the network n “Security is a process, not a product” n