ATIS1000080 Errata Overview David Hancock Comcast Oct 23
- Slides: 7
ATIS-1000080 Errata Overview David Hancock (Comcast) Oct 23, 2018 1
What's Covered • Overview of structures that manage/control STI certificate scope – TN Authorization List certificate extension – ACME TNAuth. List Identifier – SPC Token • ACME certificate ordering procedure changes – #1 – Update Identifier and Token definitions – #2 – Move CSR to new "finalize" step – #3 – Replace GET with POST-as-GET 2
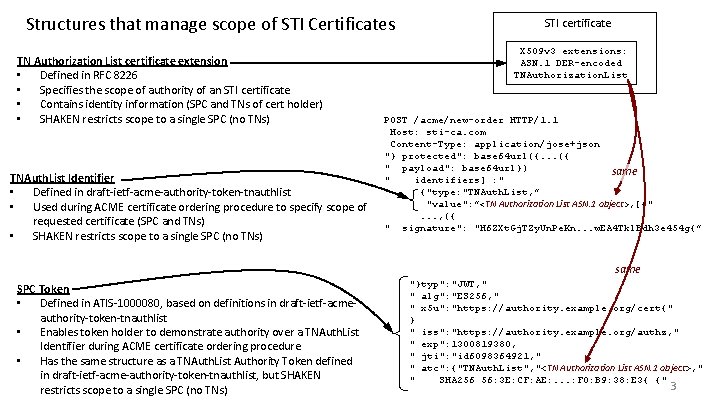
Structures that manage scope of STI Certificates TN Authorization List certificate extension • Defined in RFC 8226 • Specifies the scope of authority of an STI certificate • Contains identity information (SPC and TNs of cert holder) • SHAKEN restricts scope to a single SPC (no TNs) TNAuth. List Identifier • Defined in draft-ietf-acme-authority-token-tnauthlist • Used during ACME certificate ordering procedure to specify scope of requested certificate (SPC and TNs) • SHAKEN restricts scope to a single SPC (no TNs) STI certificate X 509 v 3 extensions: ASN. 1 DER-encoded TNAuthorization. List POST /acme/new-order HTTP/1. 1 Host: sti-ca. com Content-Type: application/jose+json "} protected": base 64 url({. . . ({ " payload": base 64 url}) same " identifiers] : " {"type: "TNAuth. List, ” "value": ”<TN Authorization List ASN. 1 object>, [{". . . , ({ " signature": "H 6 ZXt. Gj. TZy. Un. Pe. Kn. . . w. EA 4 Tkl. Bdh 3 e 454 g{” same SPC Token • Defined in ATIS-1000080, based on definitions in draft-ietf-acmeauthority-token-tnauthlist • Enables token holder to demonstrate authority over a TNAuth. List Identifier during ACME certificate ordering procedure • Has the same structure as a TNAuth. List Authority Token defined in draft-ietf-acme-authority-token-tnauthlist, but SHAKEN restricts scope to a single SPC (no TNs) "}typ": "JWT, " " alg": "ES 256, " " x 5 u": "https: //authority. example. org/cert{" } " iss": "https: //authority. example. org/authz, " " exp": 1300819380, " jti": "id 6098364921, " " atc": {"TNAuth. List", "<TN Authorization List ASN. 1 object>, " " SHA 256 56: 3 E: CF: AE: . . . : F 0: B 9: 38: E 3{ {" 3
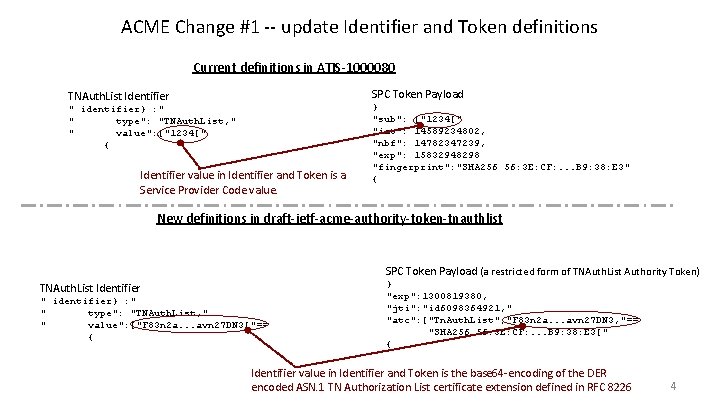
ACME Change #1 -- update Identifier and Token definitions Current definitions in ATIS-1000080 SPC Token Payload TNAuth. List Identifier " identifier} : " " type": "TNAuth. List, " " value": ["1234[" { Identifier value in Identifier and Token is a Service Provider Code value. } "sub": ["1234[" "iat": 14589234802, "nbf": 14782347239, "exp": 15832948298 "fingerprint": "SHA 256 56: 3 E: CF: . . . B 9: 38: E 3" { New definitions in draft-ietf-acme-authority-token-tnauthlist SPC Token Payload (a restricted form of TNAuth. List Authority Token) TNAuth. List Identifier " identifier} : " " type": "TNAuth. List, " " value": ["F 83 n 2 a. . . avn 27 DN 3["== { } "exp": 1300819380, "jti": "id 6098364921, " "atc": ["Tn. Auth. List", "F 83 n 2 a. . . avn 27 DN 3, "== "SHA 256 56: 3 E: CF: . . . B 9: 38: E 3[" { Identifier value in Identifier and Token is the base 64 -encoding of the DER encoded ASN. 1 TN Authorization List certificate extension defined in RFC 8226 4
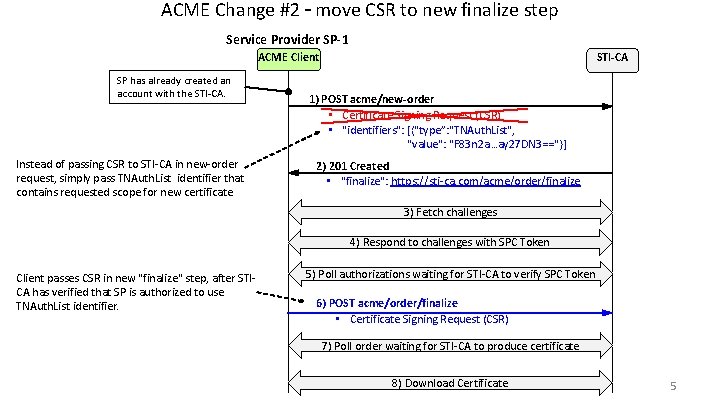
ACME Change #2 – move CSR to new finalize step Service Provider SP-1 ACME Client SP has already created an account with the STI-CA. Instead of passing CSR to STI-CA in new-order request, simply pass TNAuth. List identifier that contains requested scope for new certificate STI-CA 1) POST acme/new-order • Certificate Signing Request (CSR) • "identifiers": [{"type”: "TNAuth. List", "value": "F 83 n 2 a…ay 27 DN 3=="}] 2) 201 Created • "finalize": https: //sti-ca. com/acme/order/finalize 3) Fetch challenges 4) Respond to challenges with SPC Token Client passes CSR in new "finalize" step, after STICA has verified that SP is authorized to use TNAuth. List identifier. 5) Poll authorizations waiting for STI-CA to verify SPC Token 6) POST acme/order/finalize • Certificate Signing Request (CSR) 7) Poll order waiting for STI-CA to produce certificate 8) Download Certificate 5
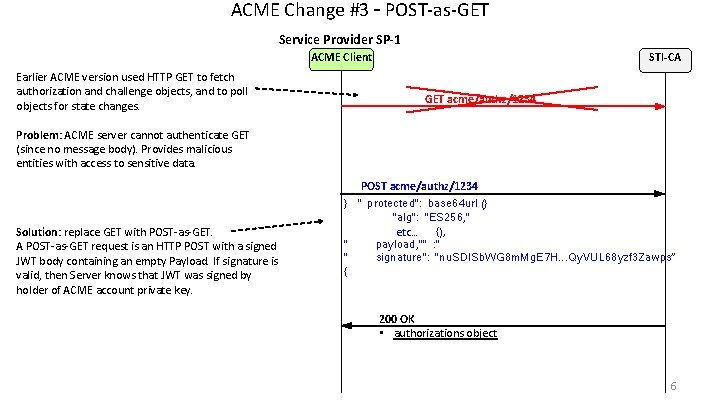
ACME Change #3 – POST-as-GET Service Provider SP-1 ACME Client Earlier ACME version used HTTP GET to fetch authorization and challenge objects, and to poll objects for state changes. STI-CA GET acme/authz/1234 Problem: ACME server cannot authenticate GET (since no message body). Provides malicious entities with access to sensitive data. POST acme/authz/1234 Solution: replace GET with POST-as-GET. A POST-as-GET request is an HTTP POST with a signed JWT body containing an empty Payload. If signature is valid, then Server knows that JWT was signed by holder of ACME account private key. } " protected": base 64 url (} "alg": "ES 256, " etc… {), " payload, "" : " " signature": "nu. SDISb. WG 8 m. Mg. E 7 H. . . Qy. VUL 68 yzf 3 Zawps” { 200 OK • authorizations object 6
Comments/Questions 7