
www oasisopen org Cyber Threat Intelligence Technical Committee
www. oasis-open. org Cyber Threat Intelligence: Technical Committee (CTI TC) Monthly Meetings – 18 January 2018 Session #1 & Session #2 &
www. oasis-open. org Agenda Moderating: Richard Struse - Chair, CTI TC ❖Report from Prague workshop and hackathon ❖EU STIX/TAXII decision ❖STIX update ❖Observables update ➢Ongoing discussions + Patterning ❖TAXII update ➢Discussions on Version 2. 1 ❖Interop update ➢Plans for Upcoming Plugfest ❖Update on Salt Lake City F 2 F
Hackathon @ FIRST/OASIS Event in Prague Richard Struse ❖ ❖ ❖ Friday, December 8 th Provided participants with a corpus of STIX 2 data and a set of suggested challenges/problems to solve. We had STIX 2 data from a variety of sources!
Live Demo Trey Darley https: //notebooks. azure. com/treyka/libraries/jan-cti-tc-demo
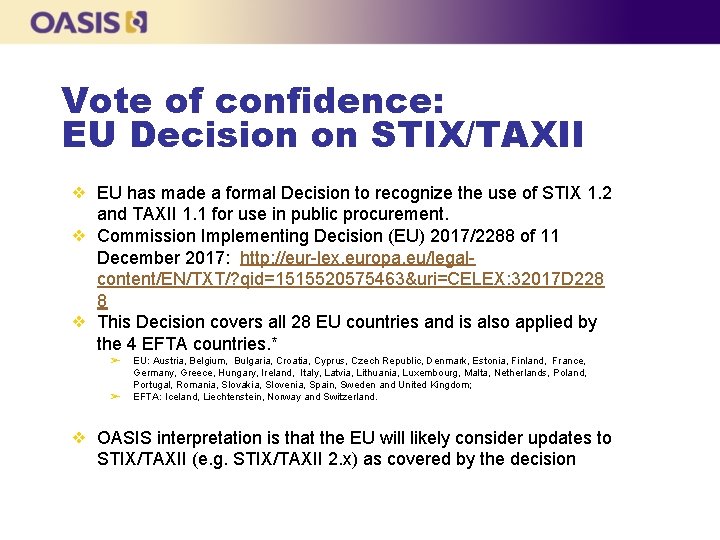
Vote of confidence: EU Decision on STIX/TAXII ❖ EU has made a formal Decision to recognize the use of STIX 1. 2 and TAXII 1. 1 for use in public procurement. ❖ Commission Implementing Decision (EU) 2017/2288 of 11 December 2017: http: //eur-lex. europa. eu/legalcontent/EN/TXT/? qid=1515520575463&uri=CELEX: 32017 D 228 8 ❖ This Decision covers all 28 EU countries and is also applied by the 4 EFTA countries. * ➢ ➢ EU: Austria, Belgium, Bulgaria, Croatia, Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Ireland, Italy, Latvia, Lithuania, Luxembourg, Malta, Netherlands, Poland, Portugal, Romania, Slovakia, Slovenia, Spain, Sweden and United Kingdom; EFTA: Iceland, Liechtenstein, Norway and Switzerland. ❖ OASIS interpretation is that the EU will likely consider updates to STIX/TAXII (e. g. STIX/TAXII 2. x) as covered by the decision
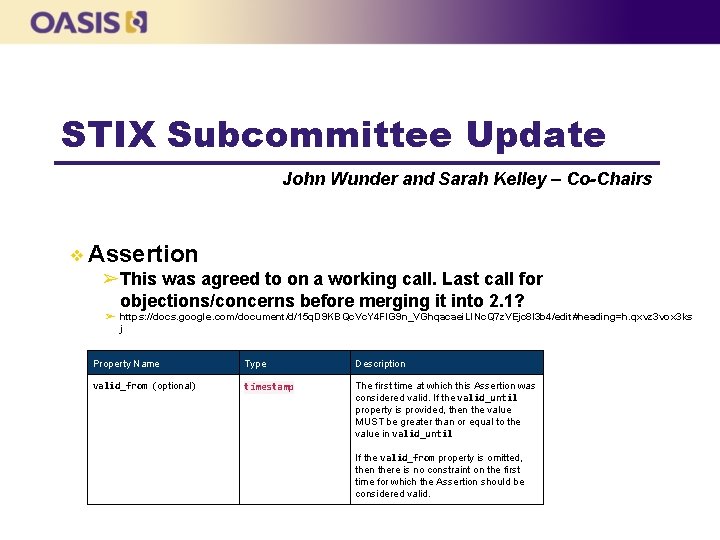
STIX Subcommittee Update John Wunder and Sarah Kelley – Co-Chairs ❖ Assertion ➢This was agreed to on a working call. Last call for objections/concerns before merging it into 2. 1? ➢ https: //docs. google. com/document/d/15 q. D 9 KBQc. Vc. Y 4 Fl. G 9 n_VGhqacaei. Ll. Nc. Q 7 z. VEjc 8 I 3 b 4/edit#heading=h. qxvz 3 vox 3 ks j Property Name Type Description valid_from (optional) timestamp The first time at which this Assertion was considered valid. If the valid_until property is provided, then the value MUST be greater than or equal to the value in valid_until If the valid_from property is omitted, then there is no constraint on the first time for which the Assertion should be considered valid.
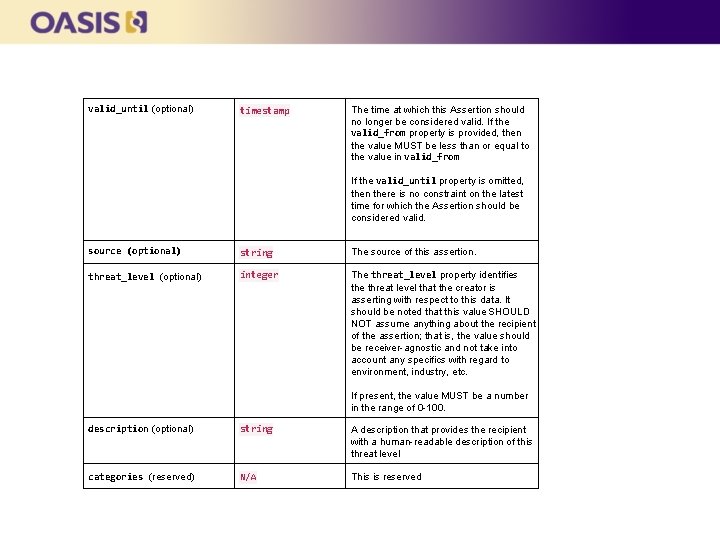
valid_until (optional) timestamp The time at which this Assertion should no longer be considered valid. If the valid_from property is provided, then the value MUST be less than or equal to the value in valid_from If the valid_until property is omitted, then there is no constraint on the latest time for which the Assertion should be considered valid. source (optional) string The source of this assertion. threat_level (optional) integer The threat_level property identifies the threat level that the creator is asserting with respect to this data. It should be noted that this value SHOULD NOT assume anything about the recipient of the assertion; that is, the value should be receiver-agnostic and not take into account any specifics with regard to environment, industry, etc. If present, the value MUST be a number in the range of 0 -100. description (optional) string A description that provides the recipient with a human-readable description of this threat level categories (reserved) N/A This is reserved
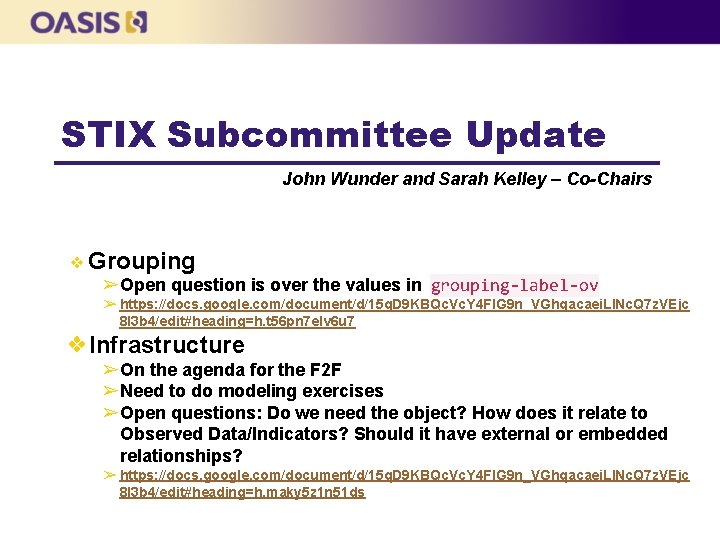
STIX Subcommittee Update John Wunder and Sarah Kelley – Co-Chairs ❖ Grouping ➢Open question is over the values in grouping-label-ov ➢ https: //docs. google. com/document/d/15 q. D 9 KBQc. Vc. Y 4 Fl. G 9 n_VGhqacaei. Ll. Nc. Q 7 z. VEjc 8 I 3 b 4/edit#heading=h. t 56 pn 7 elv 6 u 7 ❖Infrastructure ➢On the agenda for the F 2 F ➢Need to do modeling exercises ➢Open questions: Do we need the object? How does it relate to Observed Data/Indicators? Should it have external or embedded relationships? ➢ https: //docs. google. com/document/d/15 q. D 9 KBQc. Vc. Y 4 Fl. G 9 n_VGhqacaei. Ll. Nc. Q 7 z. VEjc 8 I 3 b 4/edit#heading=h. maky 5 z 1 n 51 ds
STIX Subcommittee Update John Wunder and Sarah Kelley – Co-Chairs ❖IEP ➢We seem to have consensus to add it with a caveat saying we’re adding it to facilitate interchange but not defining how to implement it in tools ➢The doc needs to be cleaned up, the caveat needs to be added and it likely needs to go through a final round of approval. ➢https: //docs. google. com/document/d/1 wi. G 6 Ro. NEFa. E 2 lrblfgjpu 3 RTAJZOK 2 q 0 b 5 Ox. XC a. CV 14/edit#heading=h. 8 tzg 8 tq 7 p 9 du ❖COA ➢On the agenda for the F 2 F ➢ https: //docs. google. com/document/d/1 VVe. Xc. Xs. KHbfjjdgl. Lom. FQl. Xpj. Uhy. Gb. GUBPSBFn. SERY/edit#
Cyber Observables Subcommittee Update Trey Darley & Ivan Kirillov – Co-Chairs ❖DNS-based Patterning looks done for 2. 1 ➢Please review: https: //goo. gl/Ns. Rjb 9 ❖Reviewing Terry Mac. Donald's Webpage and HTTPResponse-ext proposals ❖Reviewing some STIX Patterning fixes (based on implementer feedback)
TAXII Subcommittee Update Bret Jordan and Mark Davidson – Co-Chairs ❖Updates and changes to TAXII 2. 0 ➢Clarifying Text ➢Media Types ➢Return Codes ➢Manifest Resource ➢Pagination ➢Discovery Services ➢API Root Paths
TAXII Subcommittee Update Bret Jordan and Mark Davidson – Co-Chairs ❖New features for TAXII 2. 1 ➢Channels ➢Query ➢Question and Answer ❖Timelines for TAXII 2. 1 - Proposals ➢Address all breaking changes ASAP ➢Release a CSD-01 after the F 2 F ➢Release CSDs as as features for 2. 1 get finished
Interoperability Subcommittee Updates Allan Thomson & Jason Keirstead – Co-Chairs ❖ F 2 F Interop Agenda ➢ Plugfest Debrief & Lessons Learned ➢ Focus on STIX 2. 1 & TAXII 2. 1 test updates ➢ OASIS STIX Preferred logo and brand in progress ❖ Plugfest (Jan 30 2018) ➢ TC Participants: 11 orgs/individuals ➢ Planning document has been completed (except public URLs we will use) ■ Tests cover persona (TXS, DFP, TIP, TMS, TDS, TIS, SIEM) ■ Basic connectivity, sharing and collaboration
Salt Lake City CTI TC F 2 F Bret Jordan of Symantec – Host Wednesday January 31 st & Thursday February 1 st, 2018 Registration is now closed! http: //bit. ly/SLC-CTI_TC_F 2 F
F 2 F Agenda items Bret Jordan of Symantec – Host ❖ Plugfest debrief ❖ Scoping of STIX/TAXII 2. 1 ❖ STIX ➢ Infrastructure ➢ COA ➢ Grouping ❖ TAXII ❖ Cyber Observables ➢ STIX pattering updates/fixes ❖ Interop
Q&A Richard Struse – Chairman, CTI TC Jane Ginn - Secretary, CTI TC Cyber Threat Intelligence Technical Committee
- Slides: 16