
Working Group 6 SIP Security Vulnerabilities Update December
Working Group 6: SIP Security Vulnerabilities Update December 12, 2019 Chair: Danny Mc. Pherson, Verisign
Working Group 6 Members Chair: Danny Mc. Pherson* Jamal Boudhaouia Pierce Gorman Mark Hess* Zeeshan Jahangir Susan M. Miller* Thomas B. Nachbar Jitendra Patel Richard E. Perlotto II* Jon Peterson Brian Rosen Dorothy Spears-Dean* John Totura Brian Trosper* Steve Watkins* Vladimir Wolstencroft Ramon Torres Verisign Century. Link Sprint Comcast T-Mobile ATIS SGE AT&T The Shadowserver Foundation Neustar NENA NASNA Comtech Verizon Cox Communications Twilio Telnyx FCC Liaison: Ahmed Lahjouji *Also CSRIC Member 2
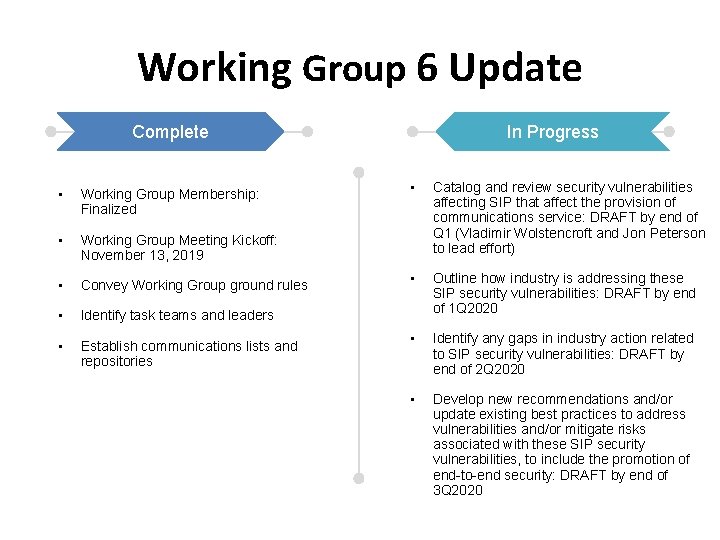
Working Group 6 Update Complete • Working Group Membership: Finalized • Working Group Meeting Kickoff: November 13, 2019 • Convey Working Group ground rules • Identify task teams and leaders • Establish communications lists and repositories In Progress • Catalog and review security vulnerabilities affecting SIP that affect the provision of communications service: DRAFT by end of Q 1 (Vladimir Wolstencroft and Jon Peterson to lead effort) • Outline how industry is addressing these SIP security vulnerabilities: DRAFT by end of 1 Q 2020 • Identify any gaps in industry action related to SIP security vulnerabilities: DRAFT by end of 2 Q 2020 • Develop new recommendations and/or update existing best practices to address vulnerabilities and/or mitigate risks associated with these SIP security vulnerabilities, to include the promotion of end-to-end security: DRAFT by end of 3 Q 2020
Next Steps • Develop work plan (backwards from March 2021) • Execute plan • Final report on “SIP Security Challenges and their Mitigations” due March 2021 4
Working Group 6: SIP Security Vulnerabilities Questions?
- Slides: 5