
WLCG Security A Trust Framework for Security Collaboration
WLCG Security: A Trust Framework for Security Collaboration among Infrastructures David Kelsey (STFC-RAL, UK) CHEP 2013, Amsterdam 17 Oct 2013
And many thanks to SCI members • • • K. Chadwick (FNAL) R. Cowles (Univ of Indiana) I. Gaines (FNAL) D. Groep (Nikhef) U. Kaila (CSC) C. Kanellopoulos (GRNET) J. Marsteller (PSC) R. Niederberger (FZ-Juelich) V. Ribaillier (IDRIS) R. Wartel (CERN) W. Weisz (University of Vienna) J. Wolfrat (SURFsara) 17/10/13 SCI at CHEP 2013 2
Outline • What is Trust and why do we need it? • Early days of cooperation in security policy • Building a new Trust Framework – Security for Collaborating Infrastructures (SCI) • The SCI document • Assessment versus SCI requirements • Future plans 17/10/13 SCI at CHEP 2013 3
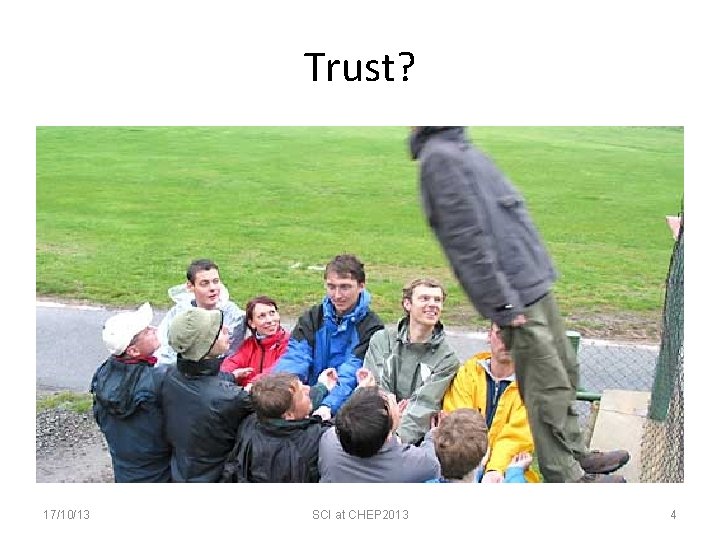
Trust? 17/10/13 SCI at CHEP 2013 4
A better definition of Trust • e. Xtreme Scale Identity Management for Scientific Collaborations XSIM (Bob Cowles) – “Trust is a disposition willingly to accept the risk of reliance on a person, entity, or system to act in ways that benefit, protect, or respect one’s interests in a given domain. ” Based on Nickel & Vaesen, Sabine Roeser, Rafaela Hillerbrand, Martin Peterson & Per Sandin (eds. ), Handbook of Risk Theory. Springer (2012) 17/10/13 SCI at CHEP 2013 5
Risk Management & Trust • Management of IT security – Management of risk – balanced with availability of services • Risk analysis • Security Plan • to mitigate and manage the risks • Security Plan includes various “Controls” – Technical – Operational – Management • Security Policy is part of Management Controls • Agreed policy framework – part of building trust 17/10/13 SCI at CHEP 2013 6
Early days of Grid Security Policy • Joint (WLCG/EGEE) Security Policy Group • We (EGEE, OSG, WLCG) agreed a common version of the Grid Acceptable Use Policy • EGI and WLCG in general continue to use the same Security Policies • BUT often not easy to agree on identical policy words • We need a better way of agreeing policy 17/10/13 SCI at CHEP 2013 7
And now to SCI … 17/10/13 SCI at CHEP 2013 8
Security for Collaborating Infrastructures (SCI) • A collaborative activity of information security officers from large-scale infrastructures – EGI, OSG, PRACE, EUDAT, CHAIN, WLCG, XSEDE, … • Developed out of EGEE – started end of 2011 • We are developing a Trust framework – Enable interoperation (security teams) – Manage cross-infrastructure security risks – Develop policy standards – Especially where not able to share identical security policies 17/10/13 SCI at CHEP 2013 9
SCI Document • V 1 of the SCI document was submitted to ISGC 2013 proceedings – Will (hopefully) be published soon • Latest public draft always at http: //www. eugridpma. org/sci/ 17/10/13 SCI at CHEP 2013 10
SCI: areas addressed • • Operational Security Incident Response Traceability Participant Responsibilities – Individual users – Collections of users – Resource providers, service operators • Legal issues and Management procedures • Protection and processing of Personal Data/Personally Identifiable Information 17/10/13 SCI at CHEP 2013 11
SCI example text: Incident Response Imperative that an infrastructure has an organised approach to addressing and managing events that threaten the security of resources, data and overall project integrity. Each infrastructure must have: [IR 1] Security contact information for all service providers, resource providers and communities together with expected response times for critical situations. [IR 2] A formal Incident Response procedure, which must address roles and responsibilities, identification and assessment of … (text continues) And continues … 17/10/13 SCI at CHEP 2013 12
SCI Assessment of maturity • To evaluate extent to which requirements are met, we recommend Infrastructures to assess the maturity of their implementations • According to following levels – Level 0: Function/feature not implemented – Level 1: Function/feature exists, is operationally implemented but not documented – Level 2: … and comprehensively documented – Level 3: … and reviewed by independent external body 17/10/13 SCI at CHEP 2013 13
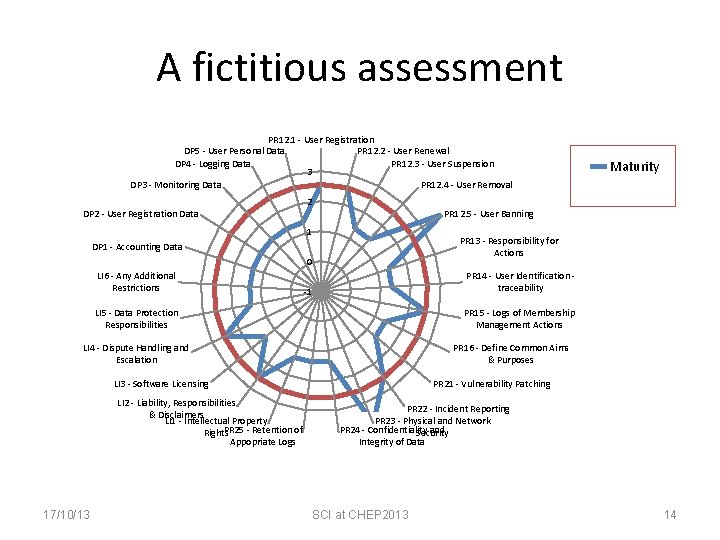
A fictitious assessment PR 12. 1 - User Registration DP 5 - User Personal Data PR 12. 2 - User Renewal DP 4 - Logging Data PR 12. 3 - User Suspension 3 DP 3 - Monitoring Data PR 12. 4 - User Removal DP 2 - User Registration Data 2 PR 12. 5 - User Banning 1 PR 13 - Responsibility for Actions DP 1 - Accounting Data 0 LI 6 - Any Additional Restrictions PR 14 - User Identification traceability -1 LI 5 - Data Protection Responsibilities PR 15 - Logs of Membership Management Actions LI 4 - Dispute Handling and Escalation PR 16 - Define Common Aims & Purposes LI 3 - Software Licensing LI 2 - Liability, Responsibilities & Disclaimers LI 1 - Intellectual Property Rights. PR 25 - Retention of Appopriate Logs 17/10/13 Maturity PR 21 - Vulnerability Patching PR 22 - Incident Reporting PR 23 - Physical and Network PR 24 - Confidentiality and Security Integrity of Data SCI at CHEP 2013 14
Future plans • Version of 1 document – Now working on a background section and a glossary • Consult Infrastructure Management – Feedback on SCI document • Perform self-assessments • Refine the SCI document • Others are welcome to join – Contact me 17/10/13 SCI at CHEP 2013 15
Further info • Security for Collaborating Infrastructures http: //www. eugridpma. org/sci/ • SCI meetings https: //indico. cern. ch/category. Display. py? categ. Id=68 17/10/13 SCI at CHEP 2013 16
Questions? 17/10/13 SCI at CHEP 2013 17
- Slides: 17