
UC IT DDo S Prevention Research Project Matt
- Slides: 23
UC IT DDo. S Prevention Research Project Matt Sheely Devrin Lewis
Overview • • • History Problem Statement Hardware/Software Requirements Design Protocol Demo Testing Risk Management Budget Conclusion
History • UC IT Attack – Distributed Denial of Service (DDo. S) – Crippled UC network – Problem compounded: Blackboard services • Outcome – DDo. S prevention architecture: Net. Zentry • Net. Zentry no longer supported – Outdated definition files in use
Problem Statement Currently, the UC IT department is looking for a new, non service based DDo. S prevention architecture, either a hardware or software implementation, which performs to and/or exceeds the existing DDo. S prevention architecture Net. Zentry.
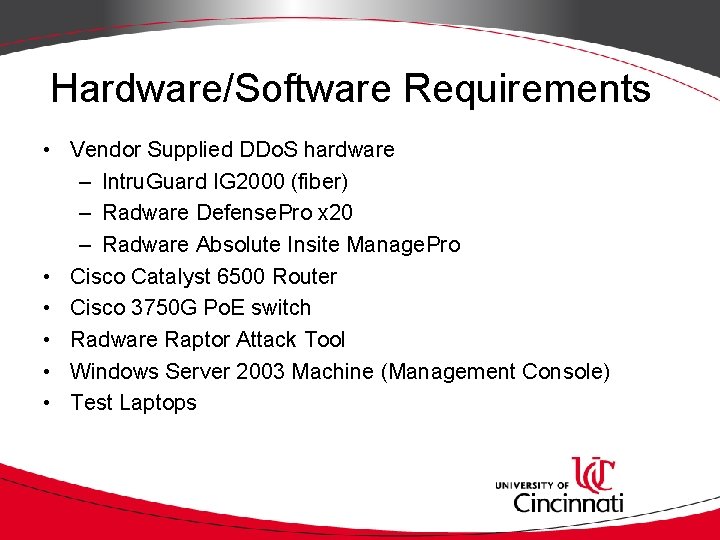
Hardware/Software Requirements • Vendor Supplied DDo. S hardware – Intru. Guard IG 2000 (fiber) – Radware Defense. Pro x 20 – Radware Absolute Insite Manage. Pro • Cisco Catalyst 6500 Router • Cisco 3750 G Po. E switch • Radware Raptor Attack Tool • Windows Server 2003 Machine (Management Console) • Test Laptops
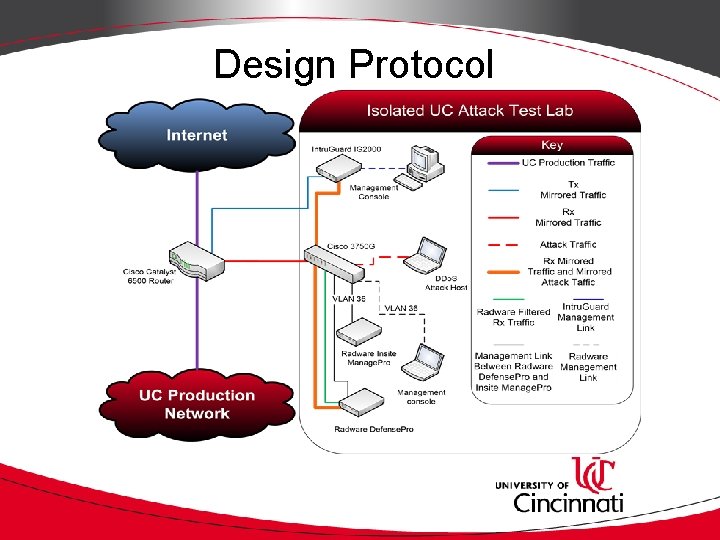
Design Protocol
Demo
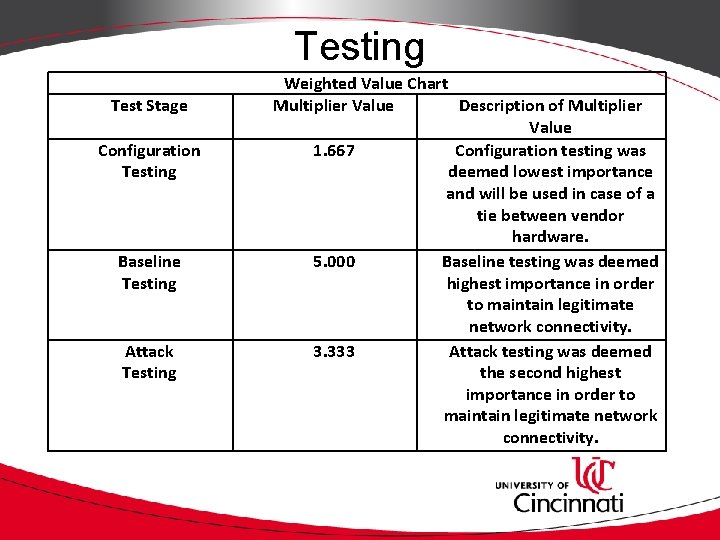
Testing Test Stage Configuration Testing Baseline Testing Attack Testing Weighted Value Chart Multiplier Value Description of Multiplier Value 1. 667 Configuration testing was deemed lowest importance and will be used in case of a tie between vendor hardware. 5. 000 Baseline testing was deemed highest importance in order to maintain legitimate network connectivity. 3. 333 Attack testing was deemed the second highest importance in order to maintain legitimate network connectivity.
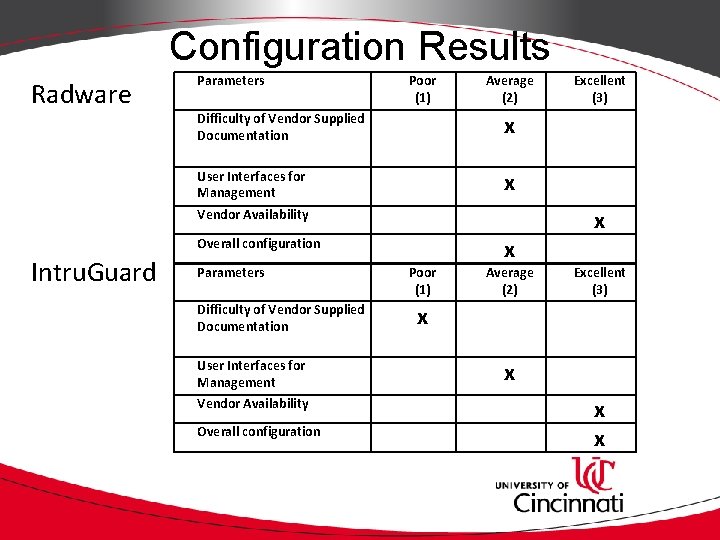
Configuration Results Radware Parameters Poor (1) Average (2) Difficulty of Vendor Supplied Documentation x User Interfaces for Management x Vendor Availability x Overall configuration Intru. Guard Parameters Difficulty of Vendor Supplied Documentation User Interfaces for Management Vendor Availability Overall configuration Poor (1) Average (2) Excellent (3) x x x x
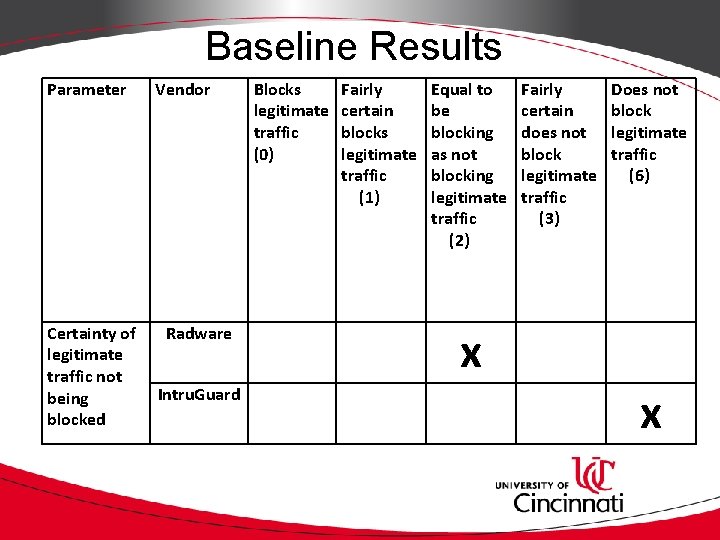
Baseline Results Parameter Vendor Certainty of Radware legitimate traffic not Intru. Guard being blocked Blocks legitimate traffic (0) Fairly certain blocks legitimate traffic (1) Equal to be blocking as not blocking legitimate traffic (2) Fairly certain does not block legitimate traffic (3) Does not block legitimate traffic (6) x x
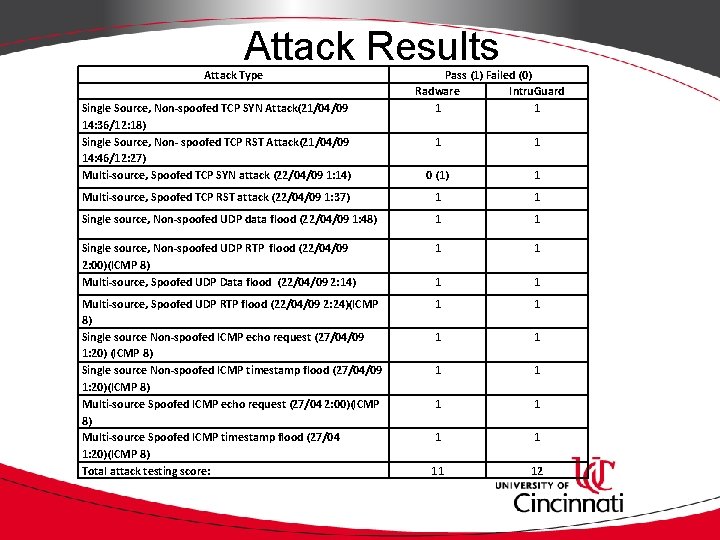
Attack Results Attack Type Single Source, Non-spoofed TCP SYN Attack(21/04/09 14: 36/12: 18) Single Source, Non- spoofed TCP RST Attack(21/04/09 14: 46/12: 27) Multi-source, Spoofed TCP SYN attack (22/04/09 1: 14) Pass (1) Failed (0) Radware Intru. Guard 1 1 0 (1) 1 Multi-source, Spoofed TCP RST attack (22/04/09 1: 37) 1 1 Single source, Non-spoofed UDP data flood (22/04/09 1: 48) 1 1 Single source, Non-spoofed UDP RTP flood (22/04/09 2: 00)(ICMP 8) Multi-source, Spoofed UDP Data flood (22/04/09 2: 14) 1 1 Multi-source, Spoofed UDP RTP flood (22/04/09 2: 24)(ICMP 8) Single source Non-spoofed ICMP echo request (27/04/09 1: 20) (ICMP 8) Single source Non-spoofed ICMP timestamp flood (27/04/09 1: 20)(ICMP 8) Multi-source Spoofed ICMP echo request (27/04 2: 00)(ICMP 8) Multi-source Spoofed ICMP timestamp flood (27/04 1: 20)(ICMP 8) Total attack testing score: 1 1 11 12
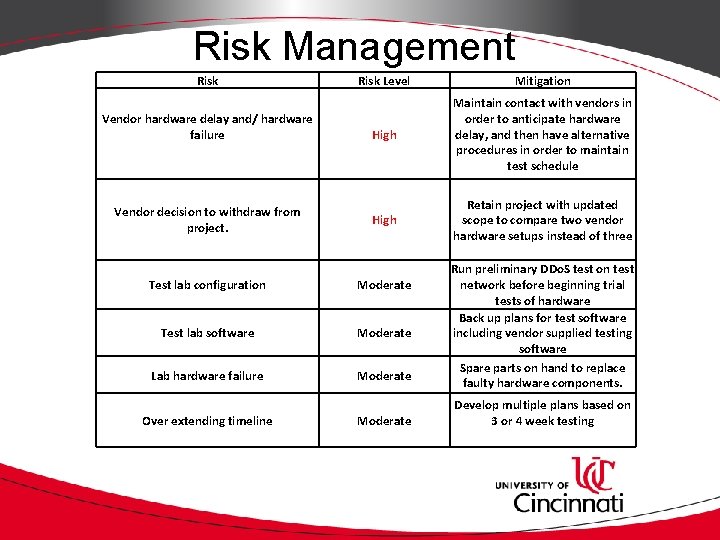
Risk Management Risk Vendor hardware delay and/ hardware failure Vendor decision to withdraw from project. Risk Level Mitigation High Maintain contact with vendors in order to anticipate hardware delay, and then have alternative procedures in order to maintain test schedule High Retain project with updated scope to compare two vendor hardware setups instead of three Test lab configuration Moderate Test lab software Moderate Lab hardware failure Moderate Over extending timeline Moderate Run preliminary DDo. S test on test network before beginning trial tests of hardware Back up plans for test software including vendor supplied testing software Spare parts on hand to replace faulty hardware components. Develop multiple plans based on 3 or 4 week testing
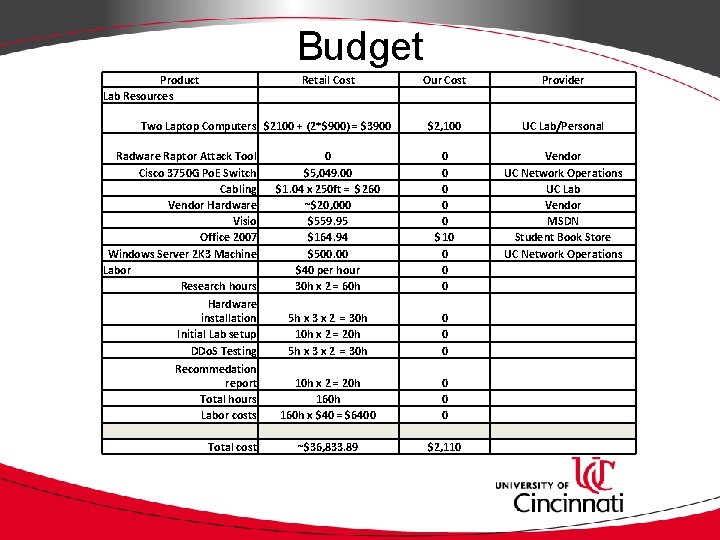
Budget Product Lab Resources Retail Cost Our Cost Provider $2, 100 UC Lab/Personal 0 $5, 049. 00 $1. 04 x 250 ft = $260 ~$20, 000 $559. 95 $164. 94 $500. 00 $40 per hour 30 h x 2 = 60 h 0 0 0 $10 0 Vendor UC Network Operations UC Lab Vendor MSDN Student Book Store UC Network Operations 5 h x 3 x 2 = 30 h 10 h x 2 = 20 h 5 h x 3 x 2 = 30 h 0 0 0 10 h x 2 = 20 h 160 h x $40 = $6400 0 Two Laptop Computers $2100 + (2*$900) = $3900 Radware Raptor Attack Tool Cisco 3750 G Po. E Switch Cabling Vendor Hardware Visio Office 2007 Windows Server 2 K 3 Machine Labor Research hours Hardware installation Initial Lab setup DDo. S Testing Recommedation report Total hours Labor costs Total cost ~$36, 833. 89 $2, 110
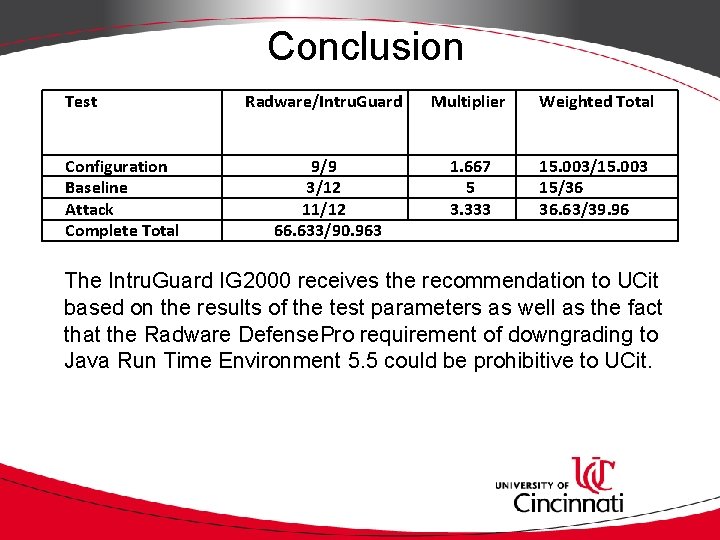
Conclusion Test Radware/Intru. Guard Configuration Baseline Attack Complete Total 9/9 3/12 11/12 66. 633/90. 963 Multiplier Weighted Total 1. 667 5 3. 333 15. 003/15. 003 15/36 36. 63/39. 96 The Intru. Guard IG 2000 receives the recommendation to UCit based on the results of the test parameters as well as the fact that the Radware Defense. Pro requirement of downgrading to Java Run Time Environment 5. 5 could be prohibitive to UCit.
Questions?
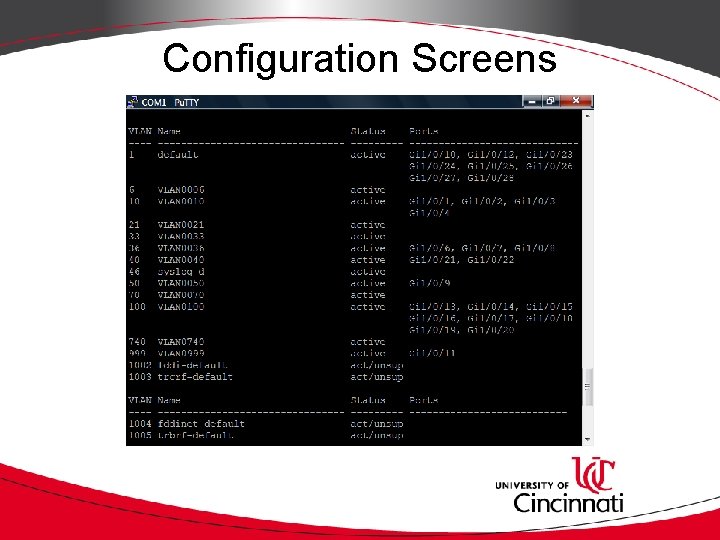
Configuration Screens
User Profile • Network Administrator – Advanced network and security knowledge – Extensive knowledge of current UC network – Strong troubleshooting skills
Deliverables • Installation and configuration process • Documentation of configuration • Analysis and performance report • Recommendation report
For Vendor Responses refer to appropriate attached word documents: Radware_Response Intru. Guard_Response