
Tungsten Fabric Evolution to Microservices ContrailControl 5 daemons
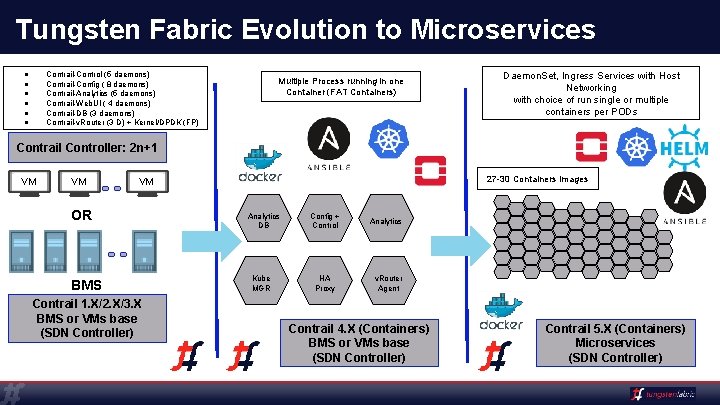
Tungsten Fabric Evolution to Microservices ● ● ● Contrail-Control (5 daemons) Contrail-Config ( 8 daemons) Contrail-Analytics (5 daemons) Contrail-Web. UI ( 4 daemons) Contrail-DB (3 daemons) Contrail-v. Router (3 D) + Kernel/DPDK (FP) Multiple Process running in one Container (FAT Containers) Daemon. Set, Ingress Services with Host Networking with choice of run single or multiple containers per PODs Contrail Controller: 2 n+1 VM VM 27 -30 Containers Images VM OR BMS Contrail 1. X/2. X/3. X BMS or VMs base (SDN Controller) Analytics DB Kube MGR Config + Control HA Proxy Analytics v. Router Agent Contrail 4. X (Containers) BMS or VMs base (SDN Controller) Contrail 5. X (Containers) Microservices (SDN Controller)
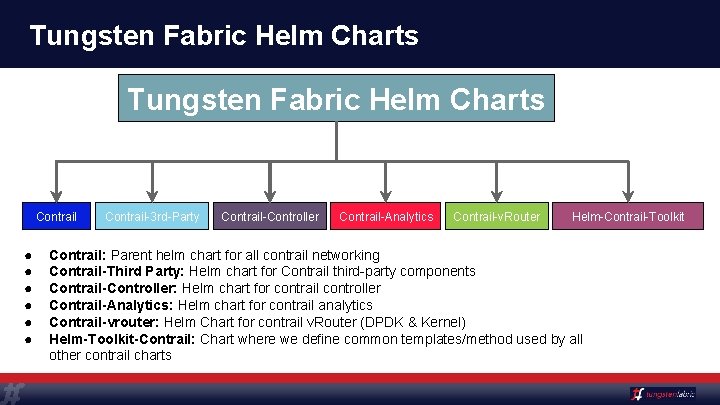
Tungsten Fabric Helm Charts Contrail ● ● ● Contrail-3 rd-Party Contrail-Controller Contrail-Analytics Contrail-v. Router Helm-Contrail-Toolkit Contrail: Parent helm chart for all contrail networking Contrail-Third Party: Helm chart for Contrail third-party components Contrail-Controller: Helm chart for contrail controller Contrail-Analytics: Helm chart for contrail analytics Contrail-vrouter: Helm Chart for contrail v. Router (DPDK & Kernel) Helm-Toolkit-Contrail: Chart where we define common templates/method used by all other contrail charts
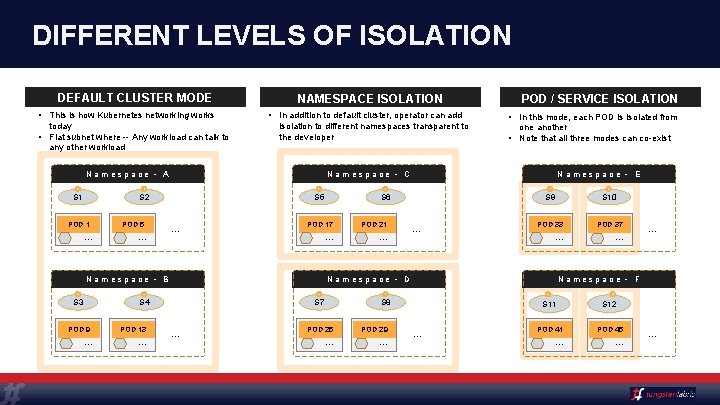
DIFFERENT LEVELS OF ISOLATION DEFAULT CLUSTER MODE NAMESPACE ISOLATION ▪ This is how Kubernetes networking works today ▪ Flat subnet where -- Any workload can talk to any other workload ▪ In addition to default cluster, operator can add isolation to different namespaces transparent to the developer Namespace - A S 1 … POD 5 … S 5 … POD 21 … … … POD 13 … … S 9 S 10 POD 33 POD 37 … … Namespace - D S 4 POD 9 Namespace - E S 6 POD 17 Namespace - B S 3 ▪ In this mode, each POD is isolated from one another ▪ Note that all three modes can co-exist Namespace - C S 2 POD 1 POD / SERVICE ISOLATION S 7 … Namespace - F S 8 POD 25 POD 29 … … S 11 S 12 POD 41 POD 45 … … …
Tungsten Fabric INSTALLATION • Ansible playbook to flexibly deploy Tungsten Fabric binaries • Helm charts to easily operate Tungsten Fabric components on Kubernetes • Install-time option with Open. Shift to deploy with Tungsten Fabric • Tungsten Fabric binaries available on Docker. Hub and we’re improving CI/CD • Commercial integrations into lifecycle tools like RH Open. Stack Director
Tungsten Fabric K 8 s CNI (A single YAML Install) Ubuntu Single YAML Reference: https: //github. com/Juniper/contrail-kubernetes-docs Cent. OS Single YAML
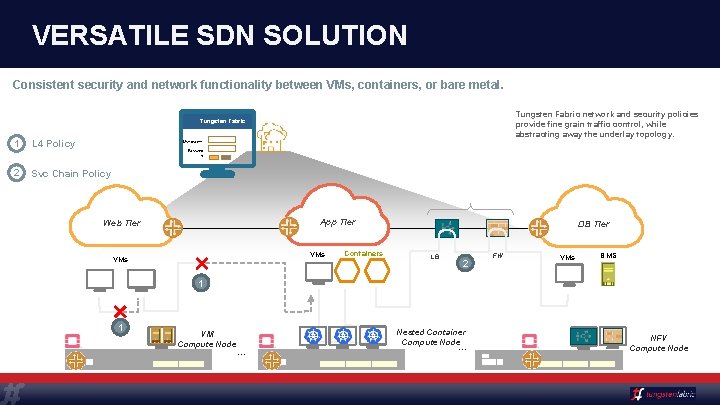
VERSATILE SDN SOLUTION Consistent security and network functionality between VMs, containers, or bare metal. Tungsten Fabric network and security policies provide fine grain traffic control, while abstracting away the underlay topology. Tungsten Fabric 1 L 4 Policy 2 Svc Chain Policy Username Passwor d App Tier Web Tier VMs Containers DB Tier LB 2 FW VMs BMS 1 1 VM Compute Node … Nested Container Compute Node … NFV Compute Node
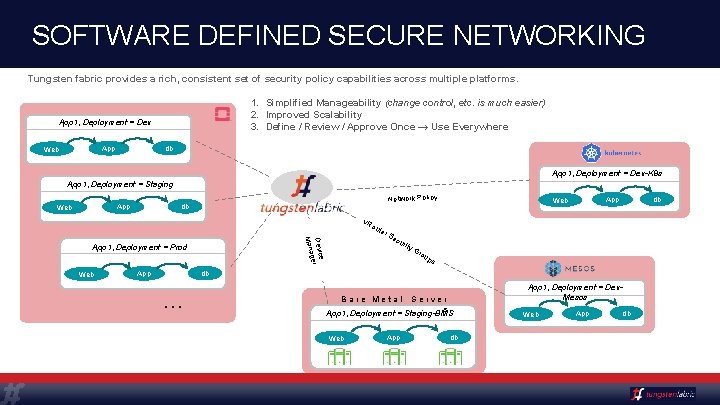
SOFTWARE DEFINED SECURE NETWORKING Tungsten fabric provides a rich, consistent set of security policy capabilities across multiple platforms. 1. Simplified Manageability (change control, etc. is much easier) 2. Improved Scalability 3. Define / Review / Approve Once → Use Everywhere App 1, Deployment = Dev db App Web App 1, Deployment = Dev-K 8 s App 1, Deployment = Staging Network Policy db App Web v. R ou e Devic r ge Mana App 1, Deployment = Prod Web ter Se c uri ty Gr ou db App Web ps db App … Bare Metal Server s App 1, Deployment = Staging-BMS Web App db App 1, Deployment = Dev. Mesos Web App db
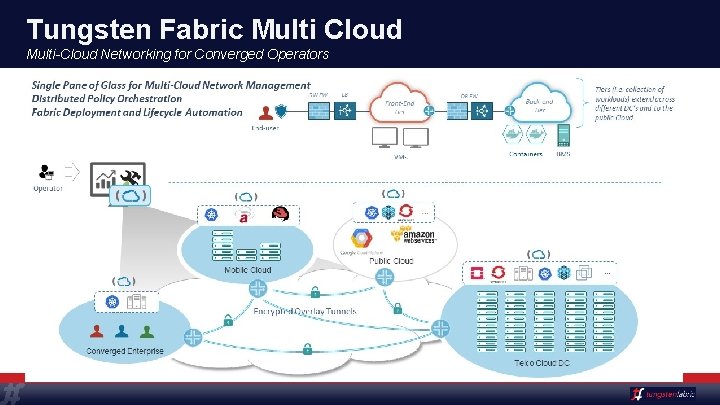
Tungsten Fabric Multi Cloud Multi-Cloud Networking for Converged Operators
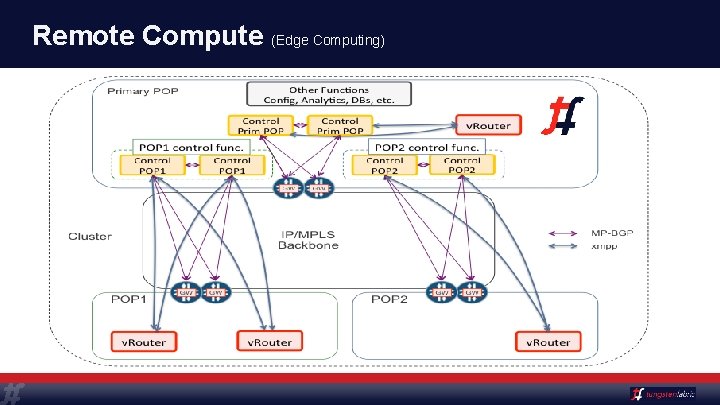
Remote Compute (Edge Computing)
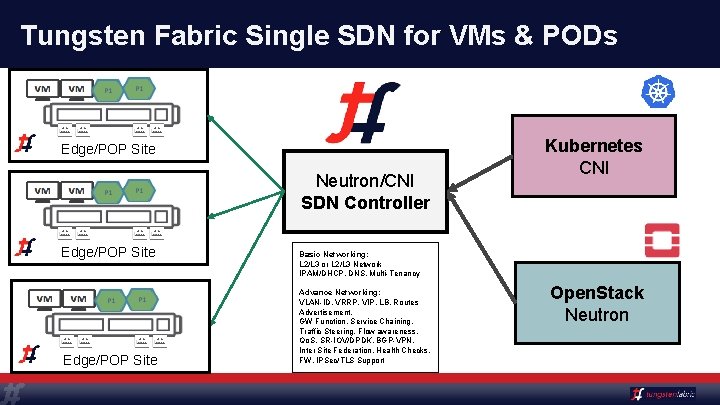
Tungsten Fabric Single SDN for VMs & PODs Edge/POP Site Neutron/CNI SDN Controller Edge/POP Site Kubernetes CNI Basic Networking: L 2/L 3 or L 2/L 3 Network IPAM/DHCP, DNS, Multi-Tenancy Advance Networking: VLAN-ID, VRRP, VIP, LB, Routes Advertisement, GW Function, Service Chaining, Traffic Steering, Flow awareness, Qo. S, SR-IOV/DPDK, BGP-VPN, Inter Site Federation, Health Checks, FW, IPSec/TLS Support Open. Stack Neutron
Carbide Sandbox Environment Tungsten Fabric + Kubernetes on AWS https: //tungsten. io/start/
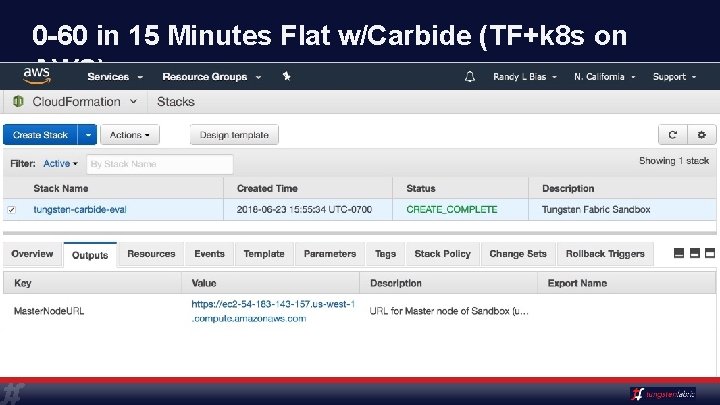
0 -60 in 15 Minutes Flat w/Carbide (TF+k 8 s on AWS)
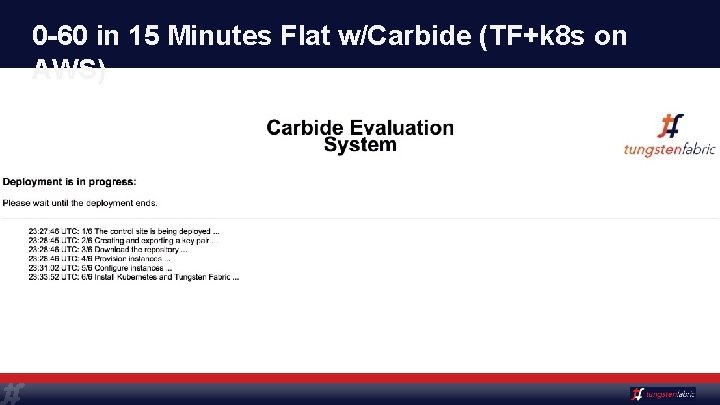
0 -60 in 15 Minutes Flat w/Carbide (TF+k 8 s on AWS)
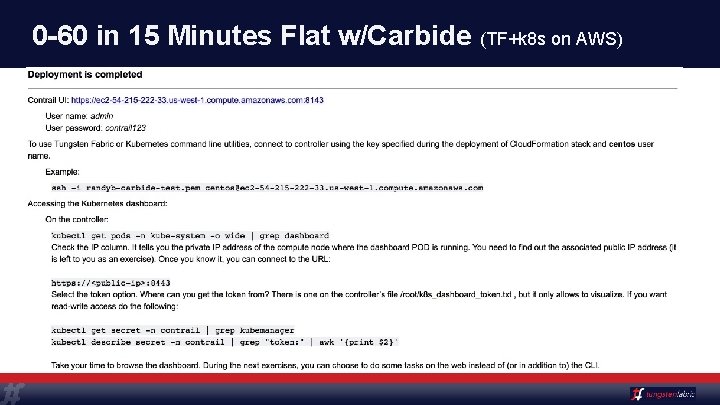
0 -60 in 15 Minutes Flat w/Carbide (TF+k 8 s on AWS)
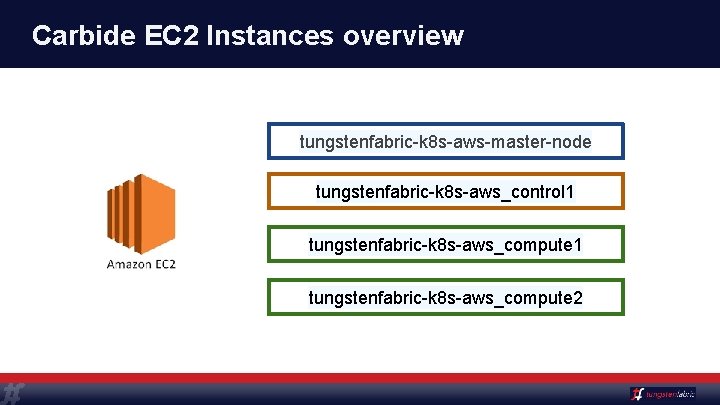
Carbide EC 2 Instances overview tungstenfabric-k 8 s-aws-master-node tungstenfabric-k 8 s-aws_control 1 tungstenfabric-k 8 s-aws_compute 2
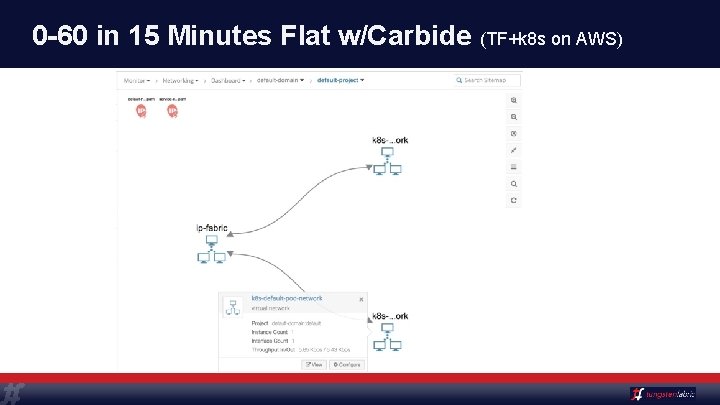
0 -60 in 15 Minutes Flat w/Carbide (TF+k 8 s on AWS)
Try Tungsten Fabric https: //tungstenfabric. github. io/website/Tungsten-Fabric-15 -minute-deploymentwith-k 8 s-on-AWS. html
Other Useful References https: //github. com/qarham/tf-osh-vagrant https: //github. com/qarham/tf-os-k 8 s-vagrant https: //github. com/tonyliu 0592/contrail/wiki/Kubernetes
- Slides: 19