
THREAT LANDSCAPE CYBER Alok Vijayant CAIIB MBAFMS CEH
THREAT LANDSCAPE CYBER Alok Vijayant CAIIB, MBA(FMS), CEH, H 3 X PGDCS, COP(MANDARIN), ADOP(MANDARIN) Director Cyber Security Operations National Technical Research Organization
ALOK VIJAYANT MBA(FMS), CEH, H 3 X, PGDCS, COP (CHINESE), ADOP DIRECTOR (IDG) OFFICE OF NSA (PMO) EDUCATIONAL BRIEF : Schooling at RIMC, Dehradun, B. Sc(Hons) GOVT OF INDIA Physics, DU, MBA(Finance & IT) from FMS, Delhi University, CEH (Certified Ethical Hacking) from EC Council, New York, H 3 X (Ethical Hacking Expert) from Orchid Seven, PGDCS from IMT, Ghaziabad EXPERIENCE: Served RBI for 14 years in various capacities – Fake Currencies, Bank Frauds, Payment Systems, Dealing Rooms Operations Joined NTRO, Country’s premier Technical Intelligence Agency (2005) as Head of IDG (Information Dominance Group) and TFIU (Tech Financial Intelligence Unit) SPEAKER AT INTERNATIONAL CONF : OWASP International Conference 2009, 2010, 2011, 2012 Club. Hack 2008, 2009, 2010, 2011, 2012 SPEAKER AT : Null. Con 2008, 2009, 2010, 2011, 2012 RAW Training Institute C 0 Co. N 2009, 2010, 2011, 2012 BPR&D Mal. Co. N 2010, 2011, 2012 SSB Academy UN Conf on Terrorist Monitoring, Seattle – 2009 CBI Academy Security. Byte Int Conf, 2011 ARTRAC, Defence Black. Hat 2011 NICFS Def. Con 2011 IIMC India Top 100 CISO Award Ceremony, Panelist NCRB Governance Now : Mobility & Reliability – Panelist NDC, Min of Defence National CISO Conference 2012 – Speaker (2012) MCTE, Mhow DIA Conference 2012, 2013
RESOURCES
HUMAN RESOURCE AS A TARGET
TECHNICAL RESOURCE AS A TARGET ESPIONAGE DEGRADATION DESTRUCTION SLEEPER CELL BOTNETS
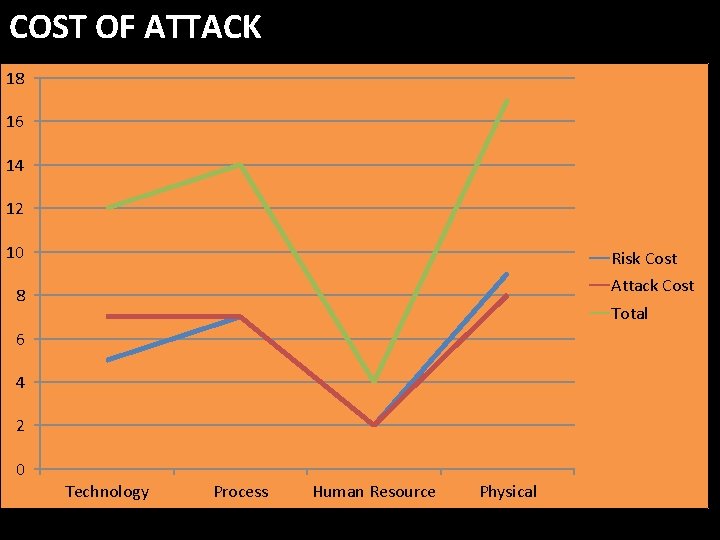
COST OF ATTACK 18 16 14 12 10 Risk Cost Attack Cost 8 Total 6 4 2 0 Technology Process Human Resource Physical
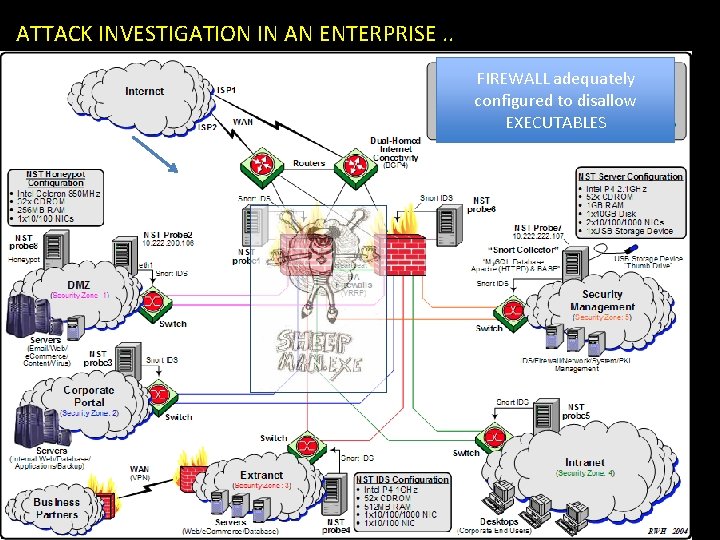
ATTACK INVESTIGATION IN AN ENTERPRISE. . FIREWALL adequately configured to disallow EXECUTABLES
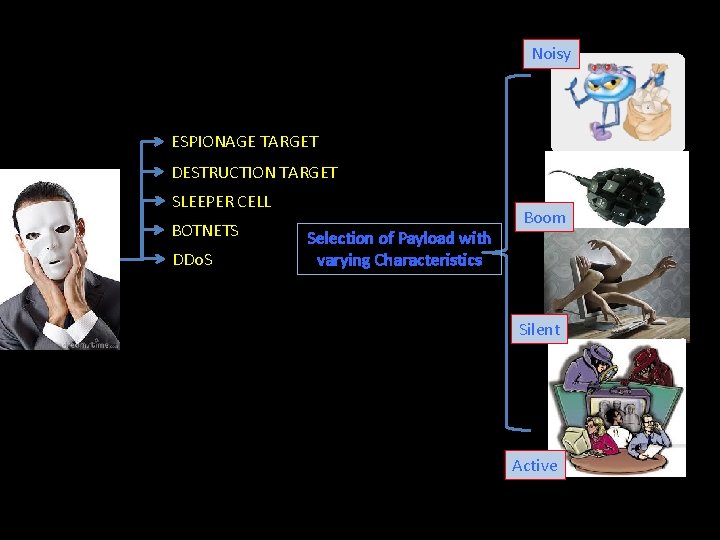
Noisy ESPIONAGE TARGET DESTRUCTION TARGET SLEEPER CELL BOTNETS DDo. S Selection of Payload with varying Characteristics Boom Silent Active
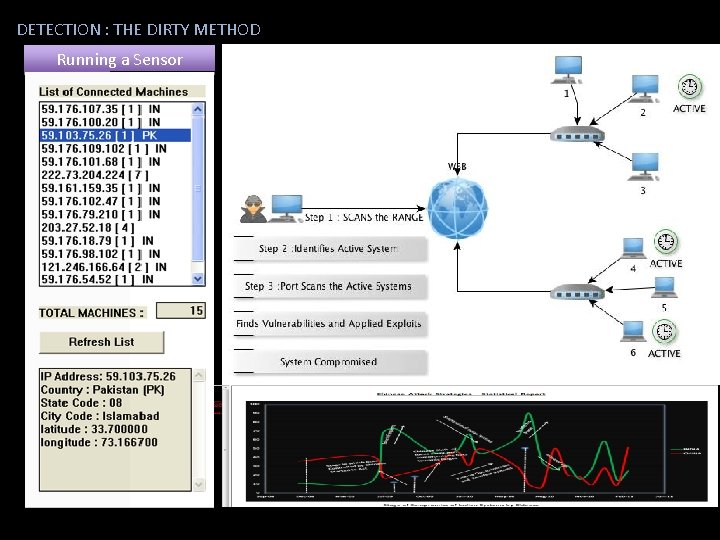
DETECTION : THE DIRTY METHOD Running a Sensor
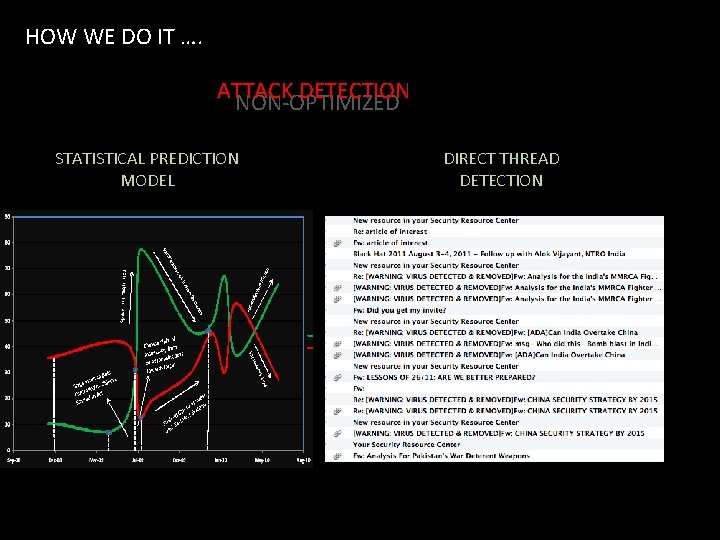
HOW WE DO IT …. ATTACK DETECTION NON-OPTIMIZED STATISTICAL PREDICTION MODEL DIRECT THREAD DETECTION
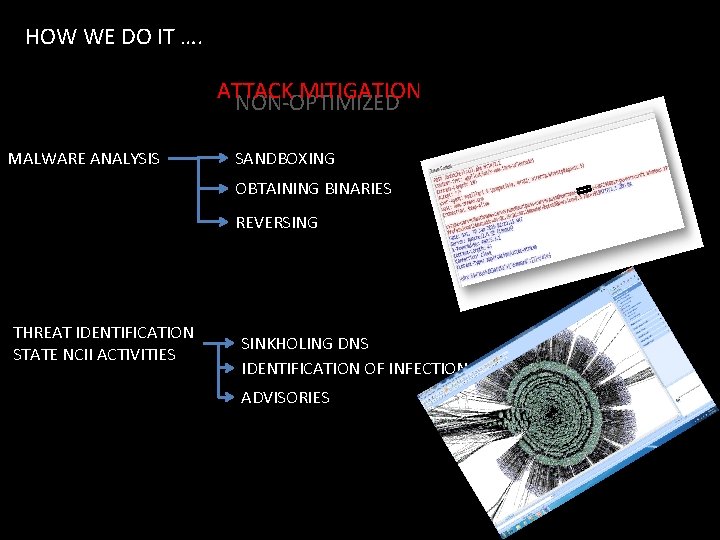
HOW WE DO IT …. ATTACK MITIGATION NON-OPTIMIZED MALWARE ANALYSIS SANDBOXING OBTAINING BINARIES REVERSING THREAT IDENTIFICATION STATE NCII ACTIVITIES SINKHOLING DNS IDENTIFICATION OF INFECTION ADVISORIES
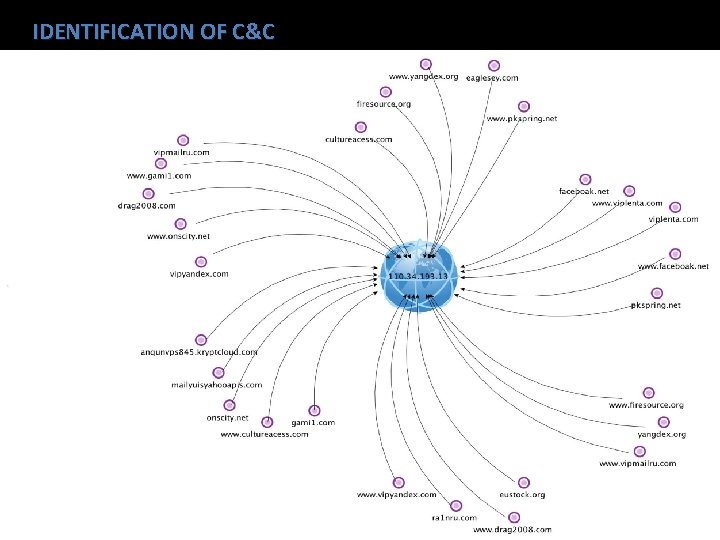
IDENTIFICATION OF C&C
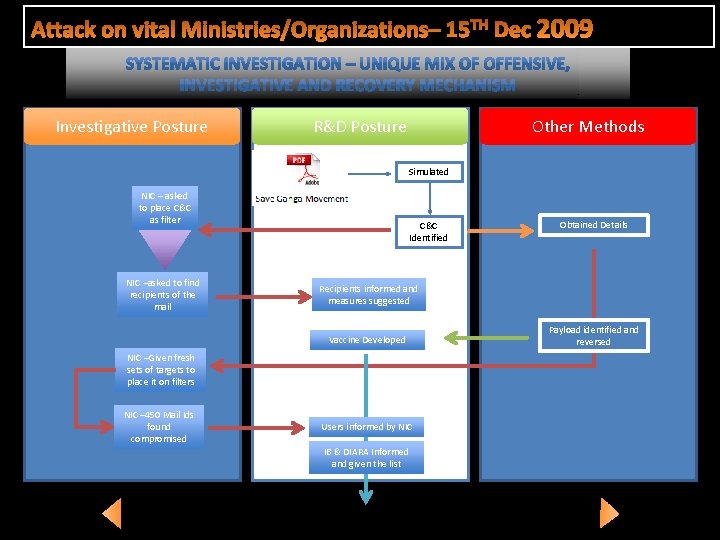
Investigative Posture R&D Posture Other Methods Simulated NIC – asked to place C&C as filter NIC –asked to find recipients of the mail C&C Identified Recipients informed and measures suggested Vaccine Developed NIC –Given fresh sets of targets to place it on filters NIC – 450 Mail Ids found compromised Obtained Details Users informed by NIC IB & DIARA Informed and given the list Users Sanitized Payload identified and reversed
SHADOW IN THE CLOUD
GHOSTNET – II WHAT WAS THE TRIGGER …… NTRO Team has been investigating and reversing various Malwares received on information systems and studying the signatures over a period of time Cyber Sensor “DRISHTI” has been observing the trends in the cyber space by monitoring incidences of attack on Indian Systems (Database Size is Approximately 32000 unique identities) Receipt of distinct signatures of Chinese Information Systems during earlier investigations and analysis by NTRO Team Pilferrage of Data from US/Canadian Investigators pertaining to Indian Logs relating to the GHOST NET II being investigated covertly in US/Canada Matching Data and signature Analysis revealing the existence of same network associated with US/Canada as well as India (Could be leveraged Diplomatically)
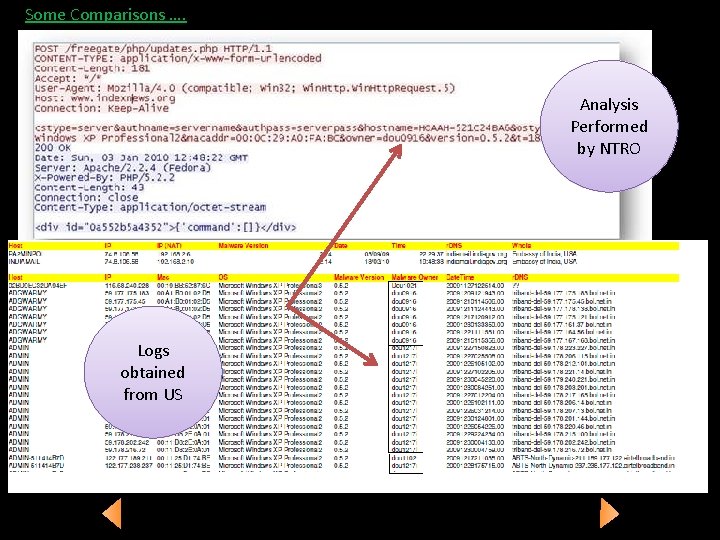
Some Comparisons …. Analysis Performed by NTRO Logs obtained from US
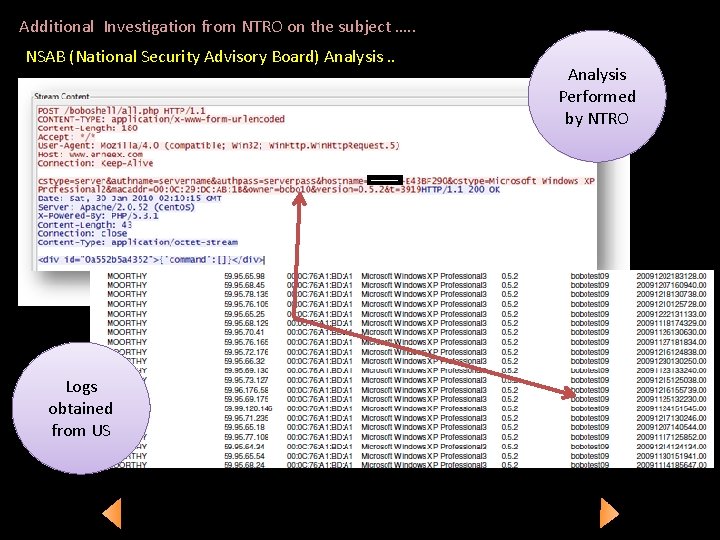
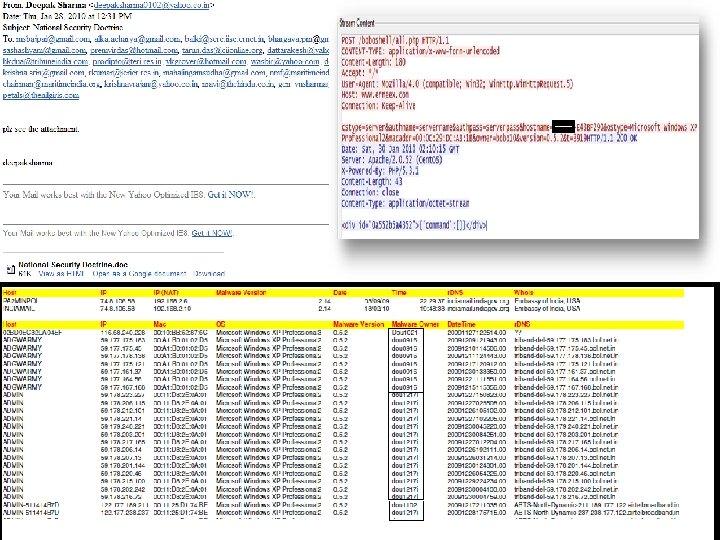
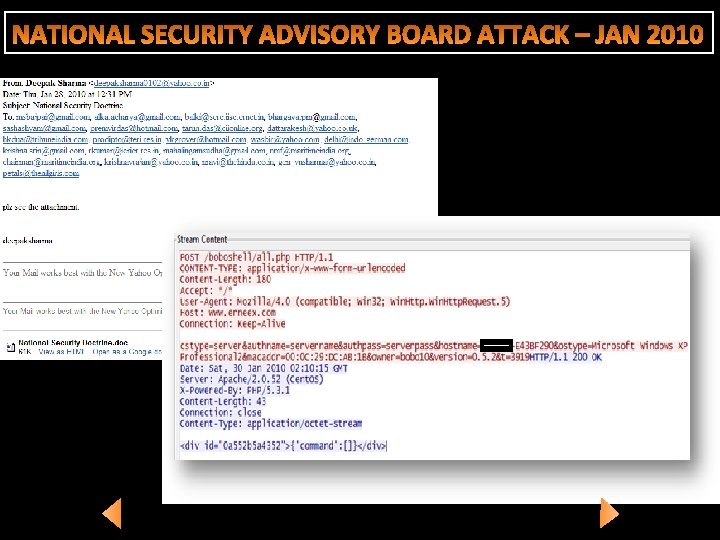
Additional Investigation from NTRO on the subject …. . NSAB (National Security Advisory Board) Analysis. . Logs obtained from US Analysis Performed by NTRO
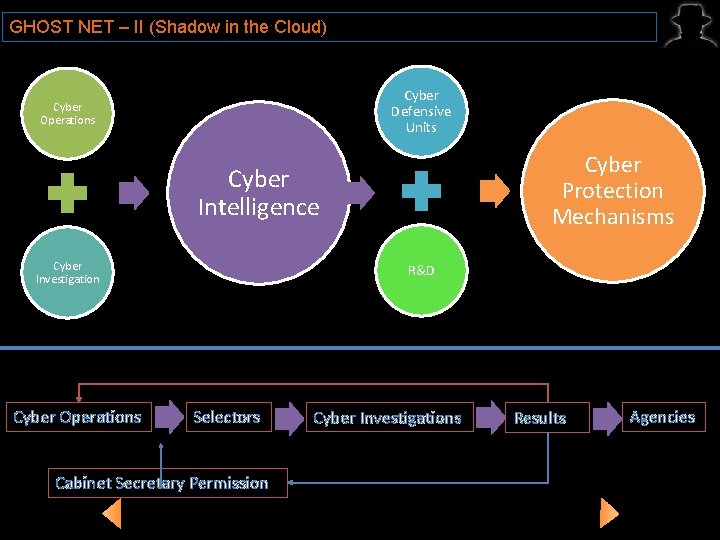
GHOST NET – II (Shadow in the Cloud) Cyber Defensive Units Cyber Operations Cyber Protection Mechanisms Cyber Intelligence Cyber Investigation Cyber Operations R&D Selectors Cabinet Secretary Permission Cyber Investigations Results Agencies
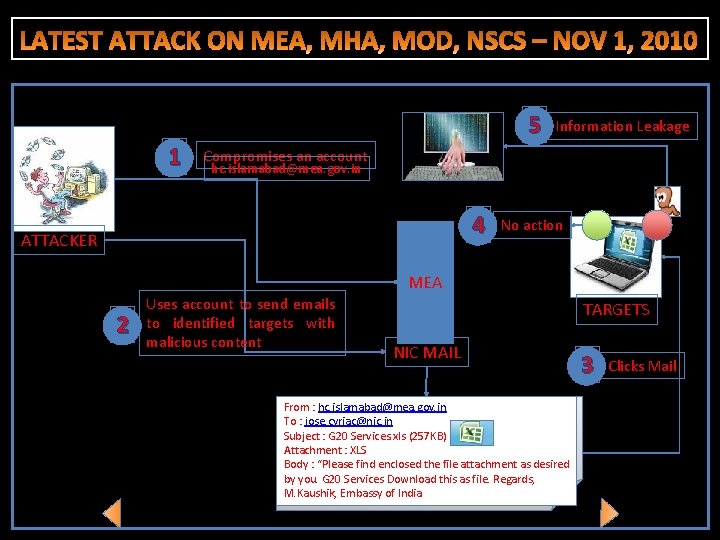
5 1 Information Leakage Compromises an account hc. islamabad@mea. gov. in 4 ATTACKER No action MEA 2 Uses account to send emails to identified targets with malicious content TARGETS NIC MAIL From : hc. islamabad@mea. gov. in To : jose. cyriac@nic. in Subject : G 20 Services. xls (257 KB) Attachment : XLS Body : “Please find enclosed the file attachment as desired by you. G 20 Services Download this as file. Regards, M. Kaushik, Embassy of India 3 Clicks Mail
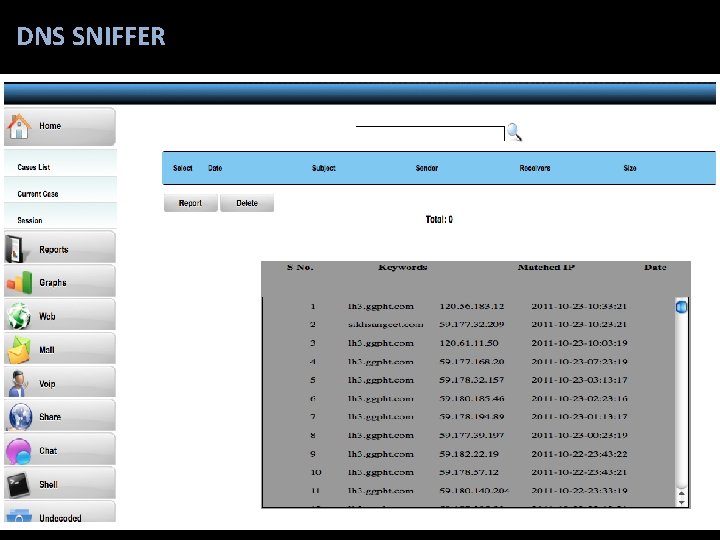
DNS SNIFFER
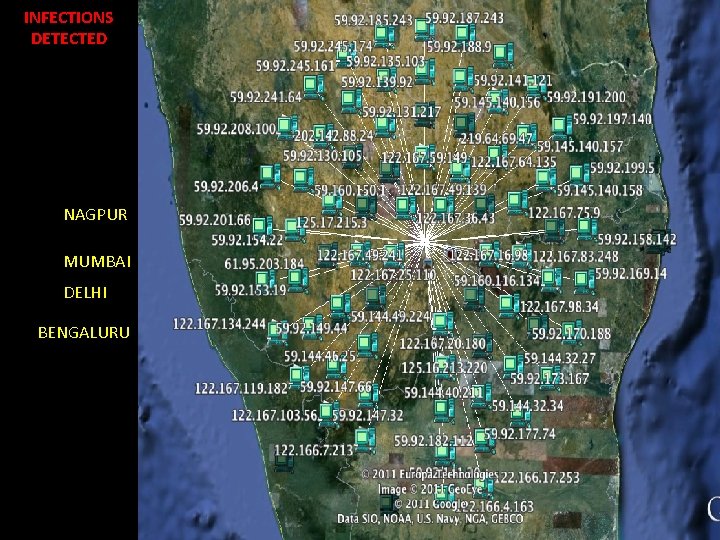
INFECTIONS DETECTED NAGPUR MUMBAI DELHI BENGALURU
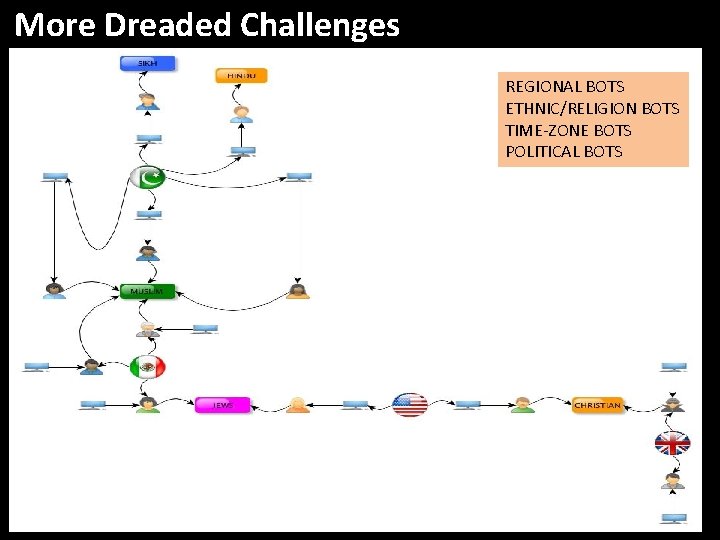
More Dreaded Challenges REGIONAL BOTS ETHNIC/RELIGION BOTS TIME-ZONE BOTS POLITICAL BOTS
DETECTION FOR THE NATIONAL ENTERPRISE The Great Indian Ring of Fire
Suggested Course of Action CIO Forum for CIOs – Indian Infosec Consortium for Indian Infosec Professionals CIO for Head Hunting – IIC for Profile Building for Infosec Professionals IIC – To promote Indigenous Business at the Global Platform Ground. Zero Summit – To be the International Platform for Showcasing Clean Exit from Corporates – Methods of IT Security Rating Standard based on renumeration model Creation of Indian Ring of Fire to protect Businesses in India Creation of System Incubation Facilities for Crowd Sourced Researches. National Cyber Security Academy – First Course due to be launched at OP JINDAL UNIVERSITY
The Hackers Conference
- Slides: 30