
The view from the Cyber Criminals 12 th

The view from the Cyber Criminals 12 th September 2017 John Kennedy, VP, Global Head of Sales Engineering Copyright © Clearswift 2017 www. clearswift. com
Clearswift RUAG Cyber Security • Global cybersecurity coverage with offices in the USA, UK, Australia, Germany and Japan • 30+ years of secure content, email and web security expertise • True “Deep Content Inspection” engine • Innovating in Adaptive Data Loss Prevention and Information Governance Copyright © Clearswift 2017 www. clearswift. com 2
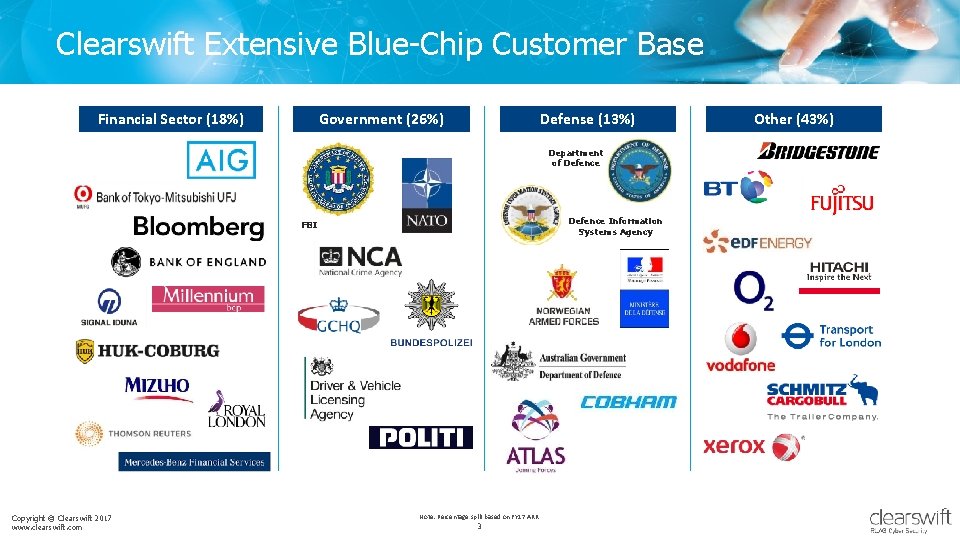
Clearswift Extensive Blue-Chip Customer Base Financial Sector (18%) Government (26%) Defense (13%) Department of Defence Information Systems Agency FBI Copyright © Clearswift 2017 www. clearswift. com Note: Percentage split based on FY 17 ARR. 3 Other (43%)
Evolution or Revolution? Copyright © Clearswift 2017 www. clearswift. com
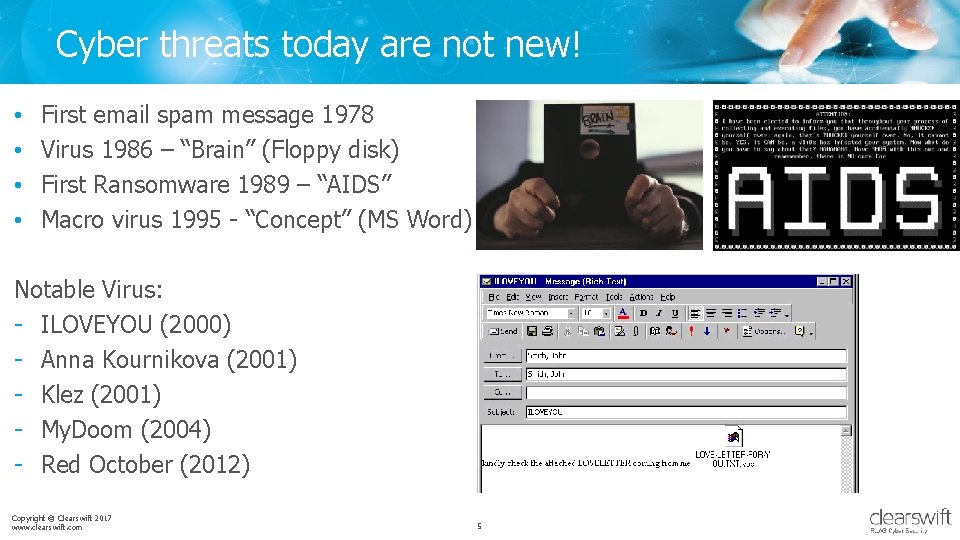
Cyber threats today are not new! • • First email spam message 1978 Virus 1986 – “Brain” (Floppy disk) First Ransomware 1989 – “AIDS” Macro virus 1995 - “Concept” (MS Word) Notable Virus: - ILOVEYOU (2000) - Anna Kournikova (2001) - Klez (2001) - My. Doom (2004) - Red October (2012) Copyright © Clearswift 2017 www. clearswift. com 5
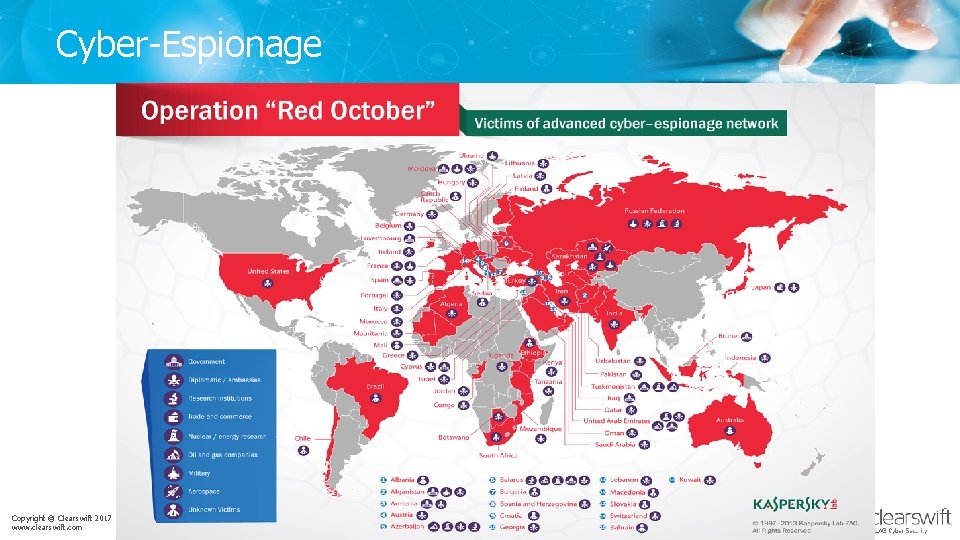
Cyber-Espionage Copyright © Clearswift 2017 www. clearswift. com 6
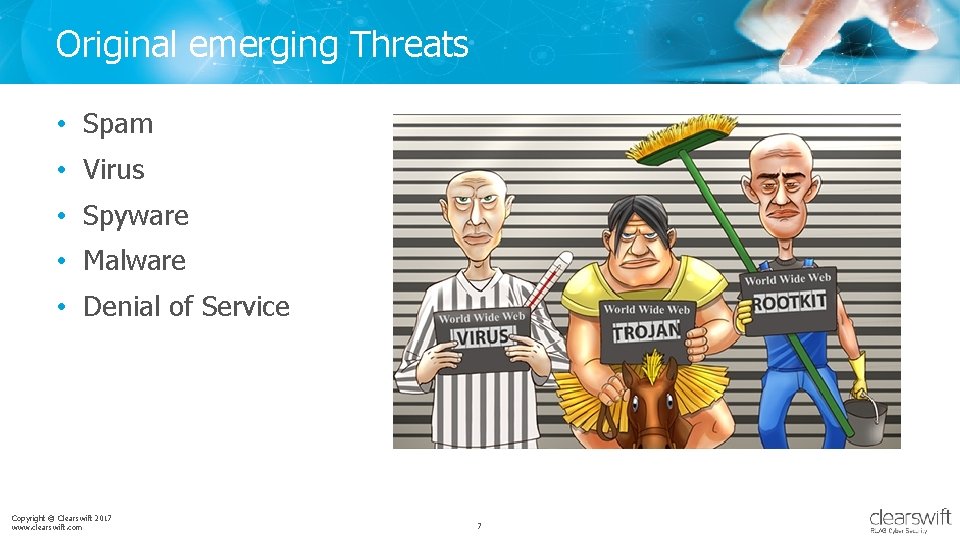
Original emerging Threats • Spam • Virus • Spyware • Malware • Denial of Service Copyright © Clearswift 2017 www. clearswift. com 7
Technology race begins • As fast as security technology is created, the criminals are looking at the next threat vector • Cyber Criminals re-using threat toolkits • Limited toolkits available to Cyber Criminals • Security vendors could focus on single axis of threats (toolkits) Copyright © Clearswift 2017 www. clearswift. com 8
Original Defence solutions • Simple Anti-Virus • Simple Anti-Spam • Sandbox • Web Proxy (URL) • Firewall • Intrusion Detection • User Education Copyright © Clearswift 2017 www. clearswift. com 9
What has changed? Copyright © Clearswift 2017 www. clearswift. com
Fundamental Changes • Internet bandwidth • Internet accessible to more people • Social Media • Increased knowledge • Mobile accessible • Internet of Things • Machine to Machine Copyright © Clearswift 2017 www. clearswift. com 11
There are more boundaries now. • • Securing Email (SMTP) and Web (HTTP/S) are no longer sufficient Internal threats become common place - “W. I. M. P. ” External Collaboration Business requirements change – AWS / Azure / O 365 – Mobile / remote working “One bucket of cloud, please!” Copyright © Clearswift 2017 www. clearswift. com 12
Security Threats today • Toolkits are being developed faster • More mechanisms are being used, increasing the number of axis on the threat landscape • Some threats are focused on single or few targets opposed to “scatter gun” approach • Morphic threats constantly evolving • Virtual Aware threats • Time based threats Copyright © Clearswift 2017 www. clearswift. com 13
Security Solutions today • More advanced Anti-Virus with zero hour, Heuristics and cloud lookups • More advanced Anti-Spam with industry standard connection checks- SPF, DKIM, DMARC, BATV, RBL’s & reputational checks • More advanced Web Proxy technologies with HTTPS inspection, true content detection. • Multi functioning Firewall technologies • Intelligent threat detection • More advanced Intrusion Detection Systems Copyright © Clearswift 2017 www. clearswift. com 14
Information is King • The use of the internet is focused on “Sharing” information • Applications and organisations hold large amounts of personal data • More information is available for Cyber Criminals to use as a basis for attacks Copyright © Clearswift 2017 www. clearswift. com 15
Where is the business balance? • Striking a balance of business needs over security needs is the key • Understanding what data is needed to be exchanged • Understand content AND context • Enable & understand business communication to avoid Shadow IT Copyright © Clearswift 2017 www. clearswift. com 16
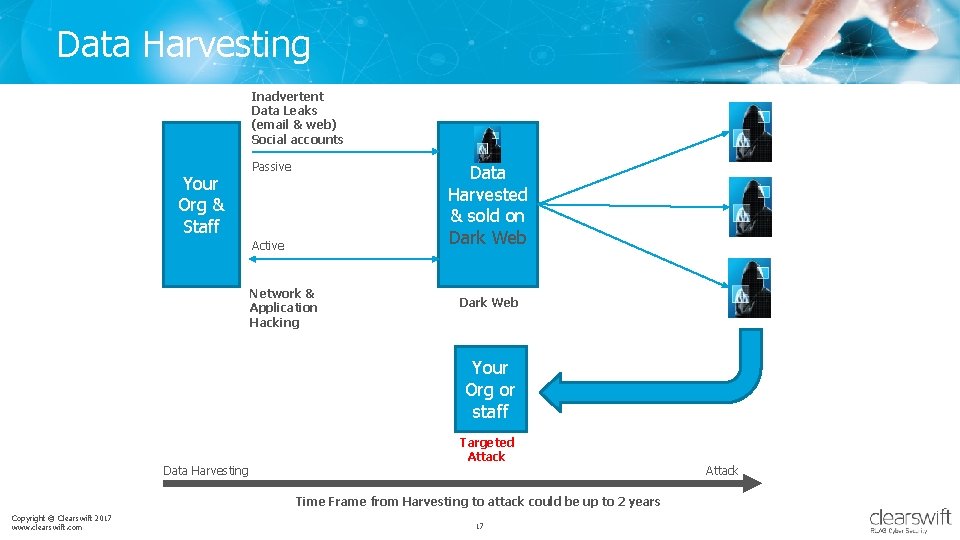
Data Harvesting Inadvertent Data Leaks (email & web) Social accounts Your Org & Staff Passive Data Harvested & sold on Dark Web Active Network & Application Hacking Dark Web Your Org or staff Data Harvesting Targeted Attack Time Frame from Harvesting to attack could be up to 2 years Copyright © Clearswift 2017 www. clearswift. com 17 Attack
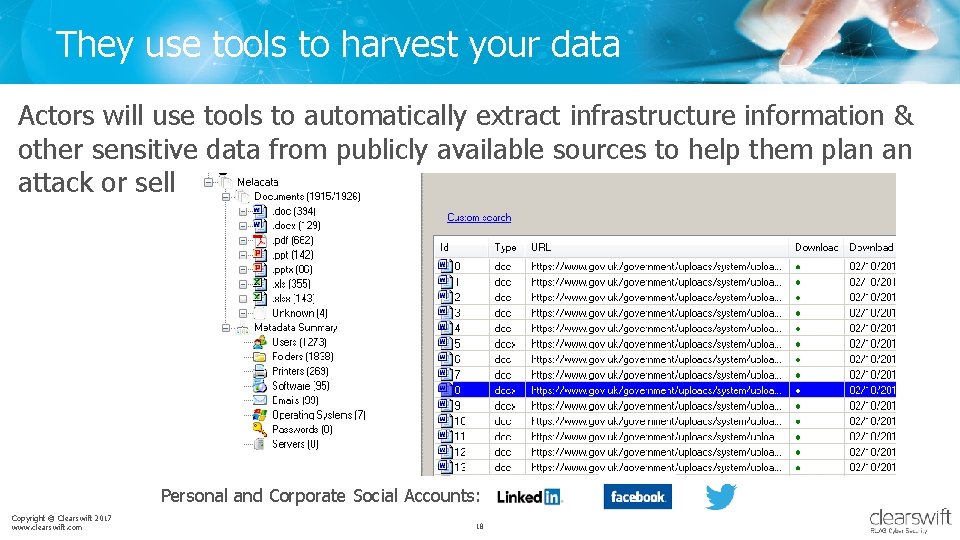
They use tools to harvest your data Actors will use tools to automatically extract infrastructure information & other sensitive data from publicly available sources to help them plan an attack or sell Personal and Corporate Social Accounts: Copyright © Clearswift 2017 www. clearswift. com 18
What do they look for? Vulnerabilities System, Network, Software Pharming, Phishing, Social Engineering Employees, email, websites PII, Metadata Email, documents, websites Infrastructure information “ 101” Copyright © Clearswift 2017 www. clearswift. com Websites 19
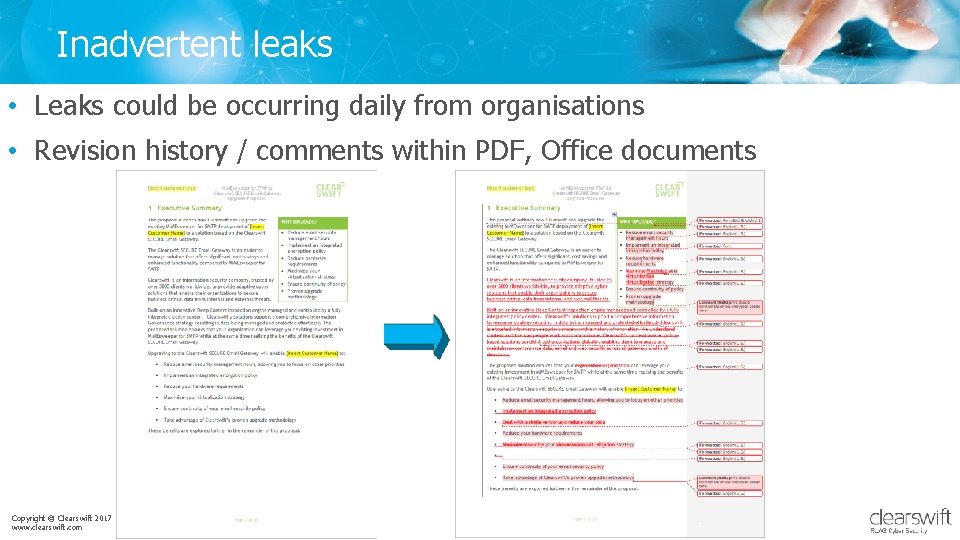
Inadvertent leaks • Leaks could be occurring daily from organisations • Revision history / comments within PDF, Office documents Copyright © Clearswift 2017 www. clearswift. com 20
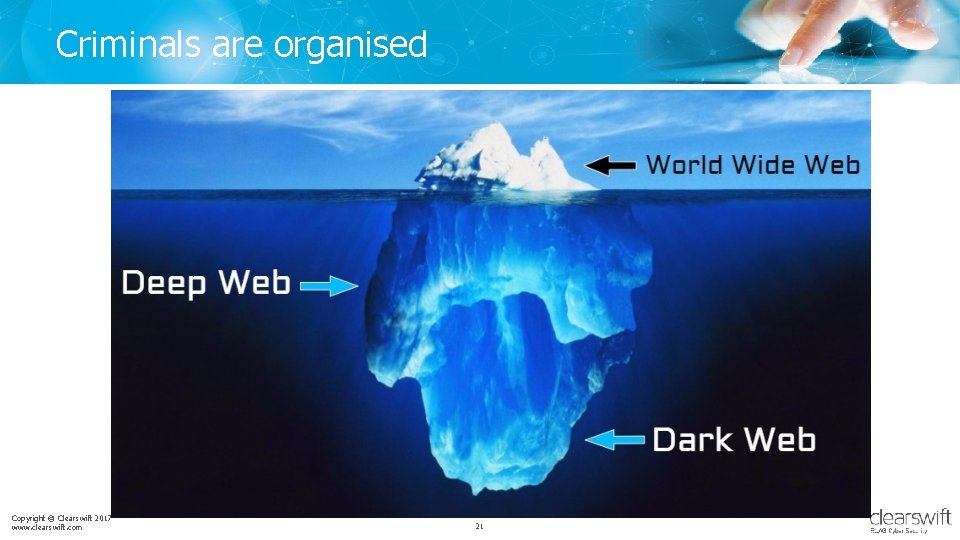
Criminals are organised Copyright © Clearswift 2017 www. clearswift. com 21
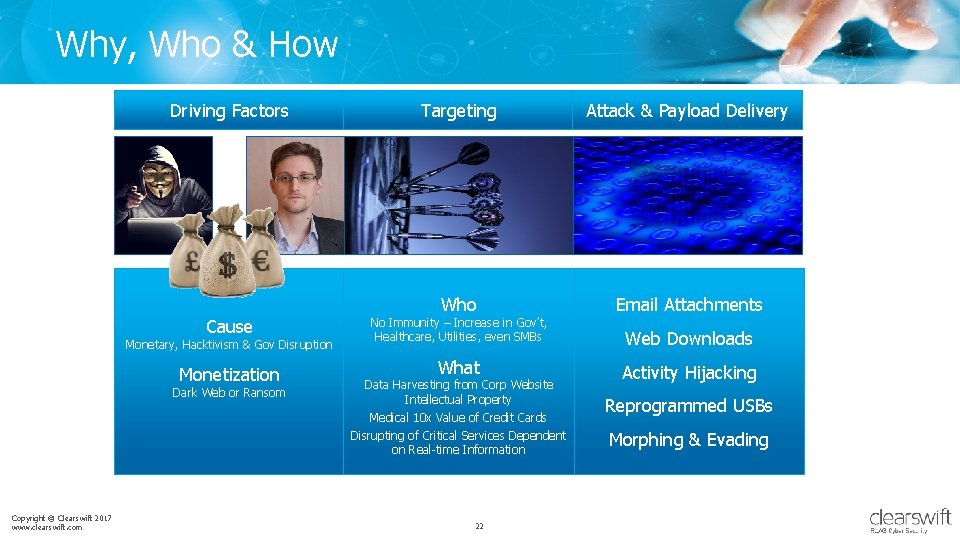
Why, Who & How Driving Factors Cause Monetary, Hacktivism & Gov Disruption Monetization Dark Web or Ransom Copyright © Clearswift 2017 www. clearswift. com Targeting Attack & Payload Delivery Who Email Attachments No Immunity – Increase in Gov’t, Healthcare, Utilities, even SMBs What Data Harvesting from Corp Website Intellectual Property Medical 10 x Value of Credit Cards Disrupting of Critical Services Dependent on Real-time Information 22 Web Downloads Activity Hijacking Reprogrammed USBs Morphing & Evading
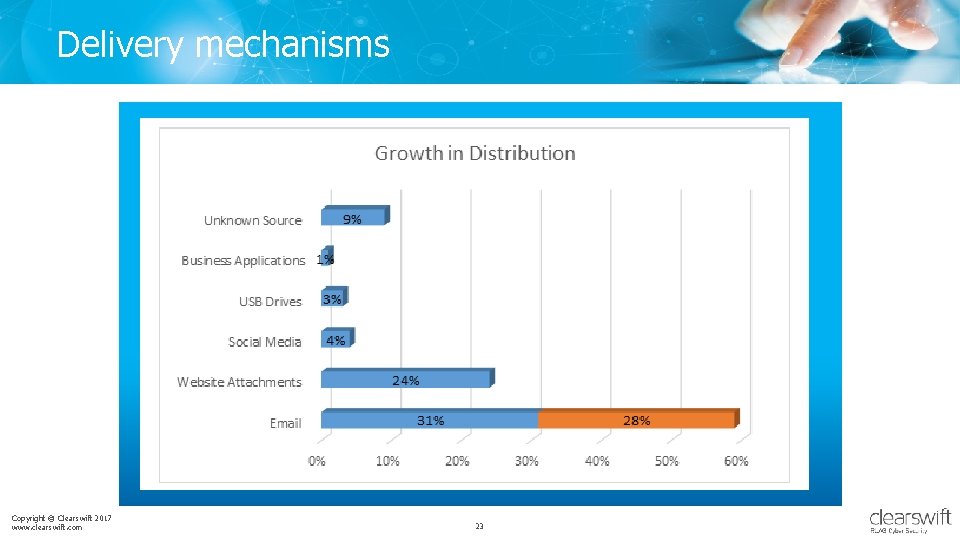
Delivery mechanisms Copyright © Clearswift 2017 www. clearswift. com 23
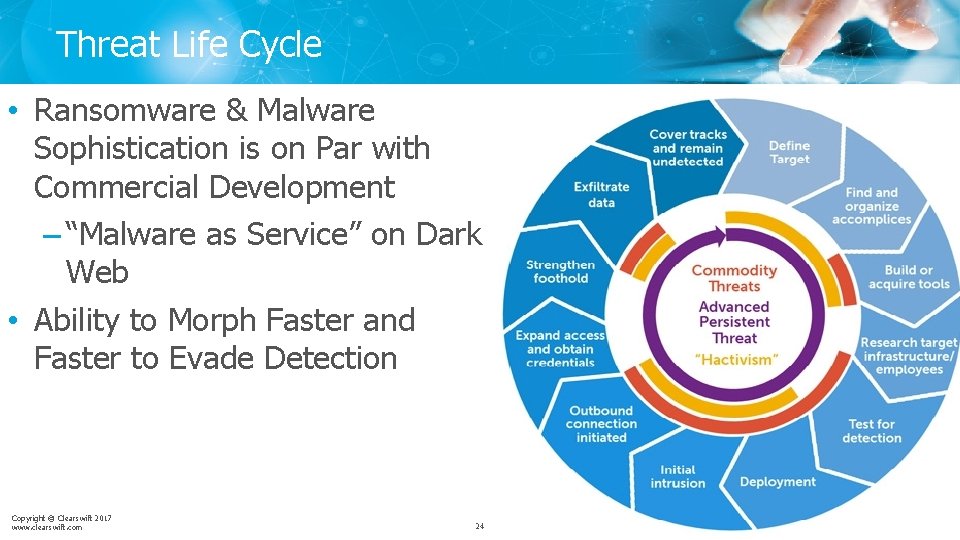
Threat Life Cycle • Ransomware & Malware Sophistication is on Par with Commercial Development – “Malware as Service” on Dark Web • Ability to Morph Faster and Faster to Evade Detection Copyright © Clearswift 2017 www. clearswift. com 24
No honour among thieves • Cobian remote access trojan (RAT) • Toolkit sold on Dark Web to other Cyber criminals • Original dev can take control once deployed “Trojan within a Trojan” • Attackers are compromising other attackers Copyright © Clearswift 2017 www. clearswift. com 25
Attacks explained Copyright © Clearswift 2017 www. clearswift. com
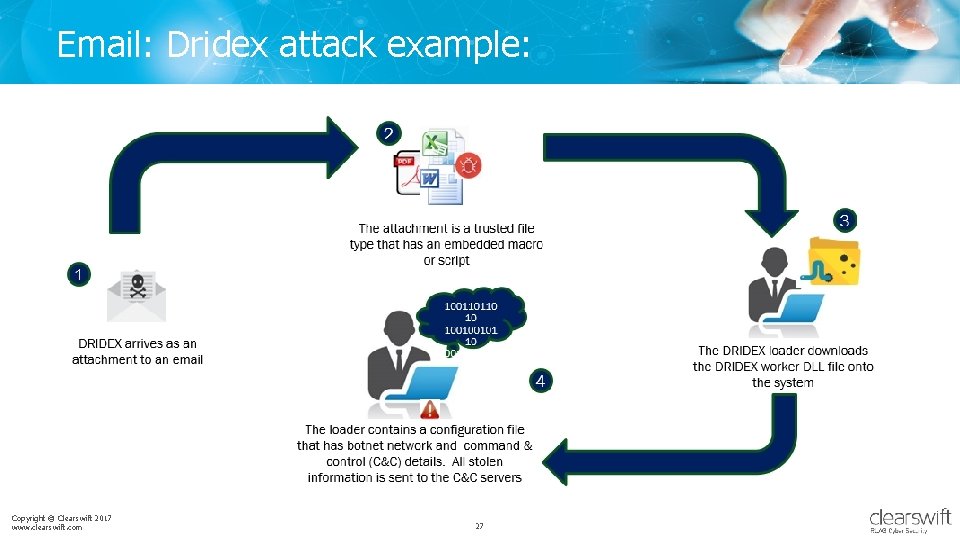
Email: Dridex attack example: Copyright © Clearswift 2017 www. clearswift. com 27
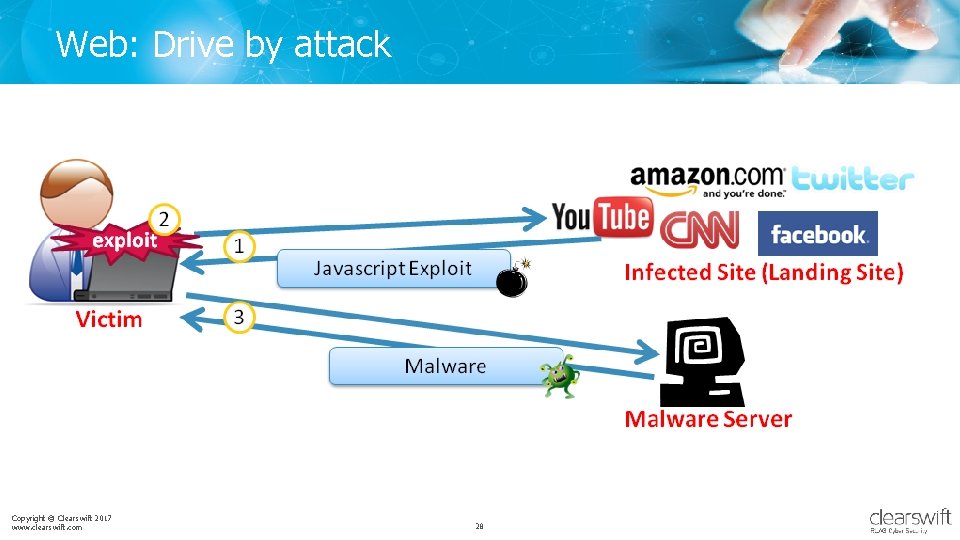
Web: Drive by attack Copyright © Clearswift 2017 www. clearswift. com 28
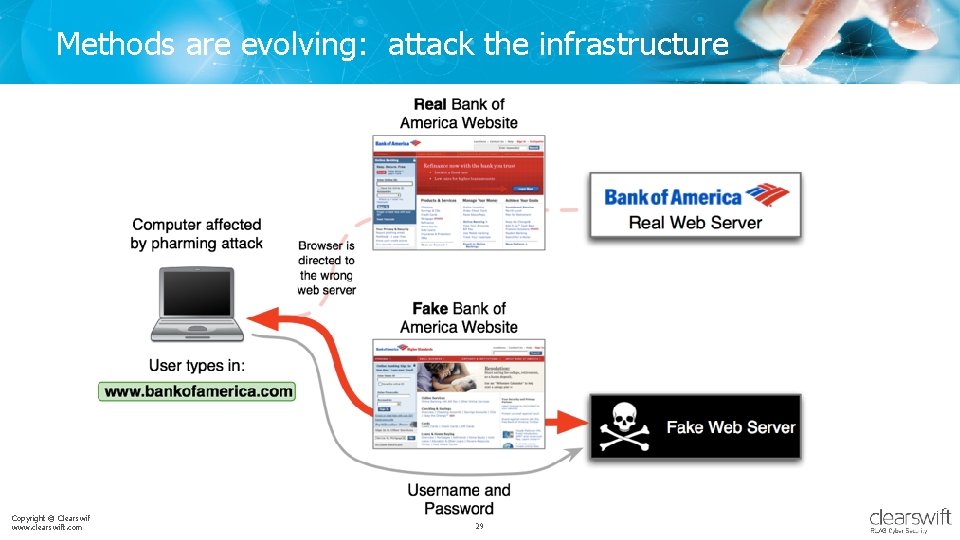
Methods are evolving: attack the infrastructure Copyright © Clearswift 2017 www. clearswift. com 29
RSA • Active Code within Excel spreadsheet via Adobe to create backdoor • Controlled machine used to steal passwords • Using passwords, sensitive information stolen • Analysis showed fingerprints of PRC – Peoples Republic of China? Copyright © Clearswift 2017 www. clearswift. com 30
Sony Corporation • State Sponsored hack by North Korea (allegedly) • Guardians of Peace (GOP) leaked employee information • The film “The Interview” released digitally early • Server Message Block (SMB) Malware vector • GOP stated it had access for over 1 year before leak • Sony Employees sue Sony for leaked data Copyright © Clearswift 2017 www. clearswift. com 31
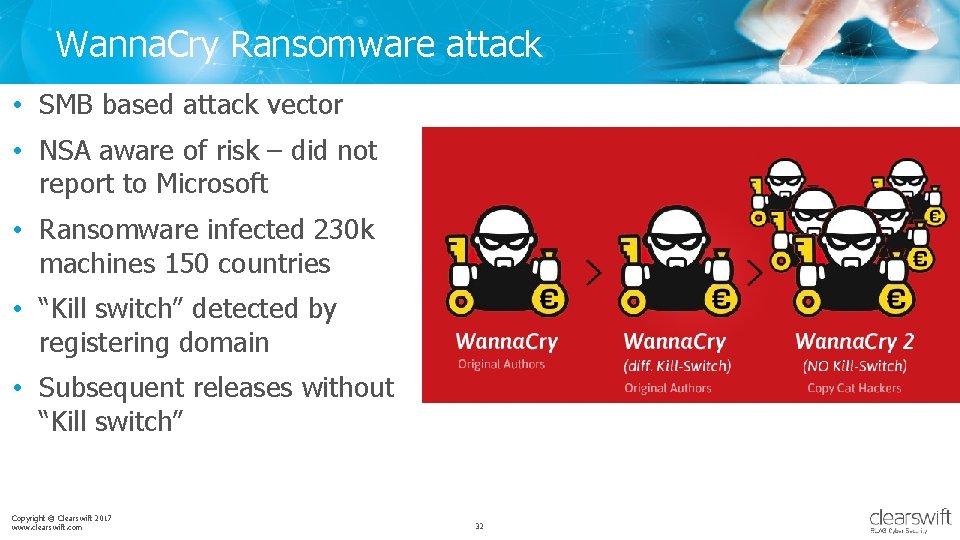
Wanna. Cry Ransomware attack • SMB based attack vector • NSA aware of risk – did not report to Microsoft • Ransomware infected 230 k machines 150 countries • “Kill switch” detected by registering domain • Subsequent releases without “Kill switch” Copyright © Clearswift 2017 www. clearswift. com 32
notpetya ransomware…. • Accounting software firm compromised • Source of the infection was via an update server for Accounting software in the Ukraine • Masked as ransomware asking for £/€/$300 • Actually designed to steal data, passwords Copyright © Clearswift 2017 www. clearswift. com 33
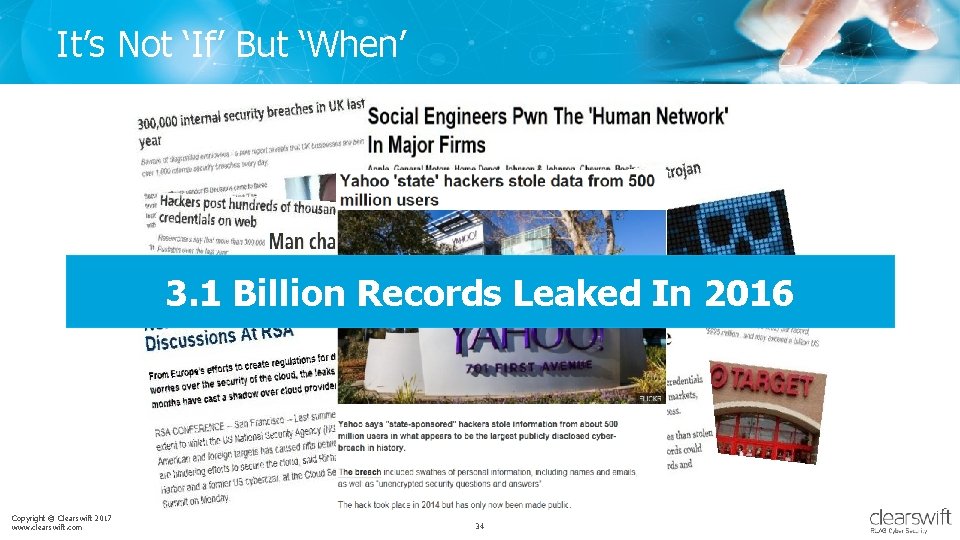
It’s Not ‘If’ But ‘When’ 3. 1 Billion Records Leaked In 2016 Copyright © Clearswift 2017 www. clearswift. com 34
How do other organisations protect data? Copyright © Clearswift 2017 www. clearswift. com
Military (High Security) • Do not comprise on security – example SPF, DKIM • Have a security policy – stick to it and apply the policy to any new projects • Layered security without adding administration overhead • Use Security experts for advice and validation • Everyone is responsible for security - physical and electronic • Keep it simple e. g. Plain text email, No active content etc Copyright © Clearswift 2017 www. clearswift. com 36
Why & What to do? Copyright © Clearswift 2017 www. clearswift. com
Why? • Organisations, both public and private, have had Cyber Security budgets cut • Security Expertise not always available in-house • Time pressures • Resource pressures • Business Vs Security Productivity Copyright © Clearswift 2017 www. clearswift. com Security 38
Business Vs Information Technology • Often a business unit will dictate to IT to implement a new system • Security can be an after thought • Mis-aligned projects or infrastructure design • Limited use of existing solutions • Shadow IT Quotes from organisations: “We just want it to work” “It is cheaper to take the fine” Copyright © Clearswift 2017 www. clearswift. com 39
What about a DLP solution? • “Where is your critical information”? • Huge cost in time & money • No unified solutions • No “silver bullet” solution • Business disruption • No on-going analysis • DLP can become post reporting tool Copyright © Clearswift 2017 www. clearswift. com 40
General Data Privacy Regulation Copyright © Clearswift 2017 www. clearswift. com
GDPR • Structured approach to data privacy security • “Privacy by design” • Total business analysis of data creation, movement, validation & security • Understanding of structured and unstructured data • Start somewhere! “A tiger chasing a group of people, you do not need to be first, just don’t be last” Copyright © Clearswift 2017 www. clearswift. com 42
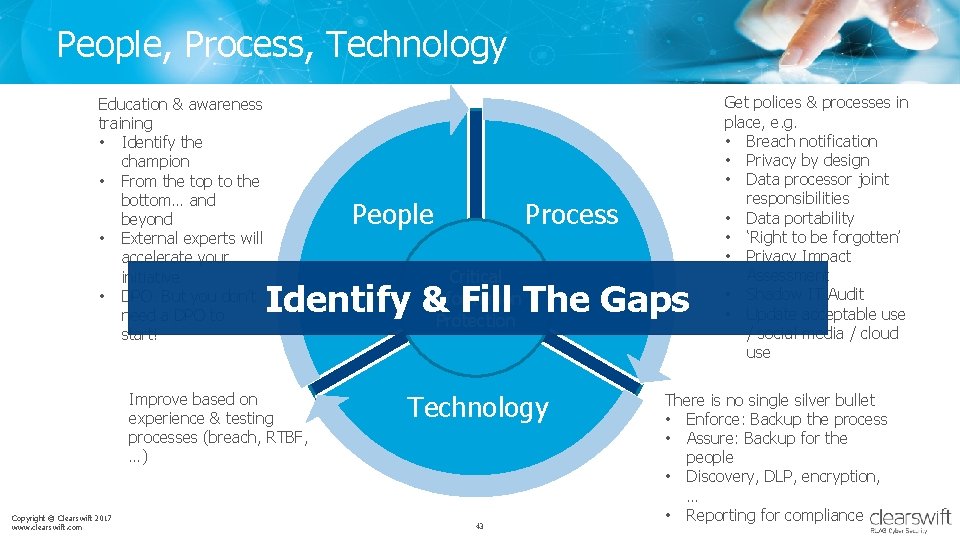
People, Process, Technology Education & awareness training • Identify the champion • From the top to the bottom… and beyond • External experts will accelerate your initiative • DPO. But you don’t need a DPO to start! People Critical Information Protection Identify & Fill The Gaps Improve based on experience & testing processes (breach, RTBF, …) Copyright © Clearswift 2017 www. clearswift. com Process Technology 43 Get polices & processes in place, e. g. • Breach notification • Privacy by design • Data processor joint responsibilities • Data portability • ‘Right to be forgotten’ • Privacy Impact Assessment • Shadow IT Audit • Update acceptable use / social media / cloud use There is no single silver bullet • Enforce: Backup the process • Assure: Backup for the people • Discovery, DLP, encryption, … • Reporting for compliance
When Encryption Isn’t Enough • Encryption keeps information safe from prying eyes • But it needs to be managed – If left to users, encrypted files can be opaque to the business – If passwords are lost then ‘discovery’ becomes impossible • Use an automatic encryption solution to keep organizational control over your information • However…If you send encrypted information to the wrong person – and they can read it, then it is a security breach Copyright © Clearswift 2017 www. clearswift. com 44
Outbound Only? • GDPR is also about looking after other organizations information entrusted to you • Sensitive information can be damaging inside the organization… think everyone’s salary… think PCI data… – Internal DLP – Need to know – Really really need to know Copyright © Clearswift 2017 www. clearswift. com 45
Thank You Copyright © Clearswift 2017 www. clearswift. com
- Slides: 46