
TDL 3 Rootkit A Sans News Bite Analysis
TDL 3 Rootkit A Sans News. Bite Analysis by Marshall Washburn
Topic: TDL 3 Rootkit variant • SANS News. Bites - Volume: XII, Issue: 70 (August 26, 27 & 30, 2010) • TDL 3 Rootkit, version 3. 273 • Combination of MBR rootkit, Rustock. C and old Tdss variants. • Stealthiest in the world.

Rootkits • Wikipedia – “A rootkit is software that enables continued privileged access to a computer, while actively hiding its presence from administrators by subverting standard operating system functionality or other applications” • High risk, 1 -in-5 Windows machines. • “Root” and “kit”
Rootkits • Netsecurity. about. com – “A rootkit allows someone, either legitimate or malicious, to maintain command control over a computer system, without the computer system user knowing about it” • Typically 32 -bit problems

Rootkits • • Rootkit are not really viruses Machine independent Remote access Anti-virus level access
Prevention • Digital Signature check for rogue drivers • “Patch. Guard” prevents some changes to Windows kernel. • Vista and Win 7 do not allow Admin

TDL 3 Rootkit Also known as Alureon rootkit More sophisticated Version 3. 273 Targets 64 -bit machines that were previously considered safer • Spread through websites and exploit kits • •
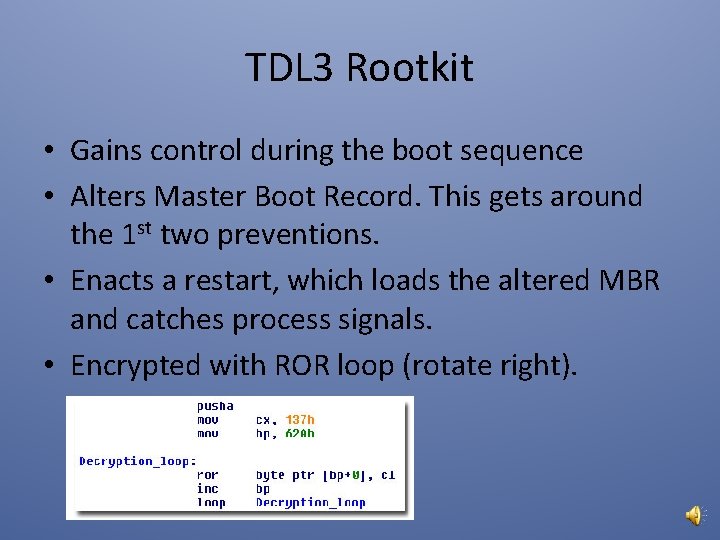
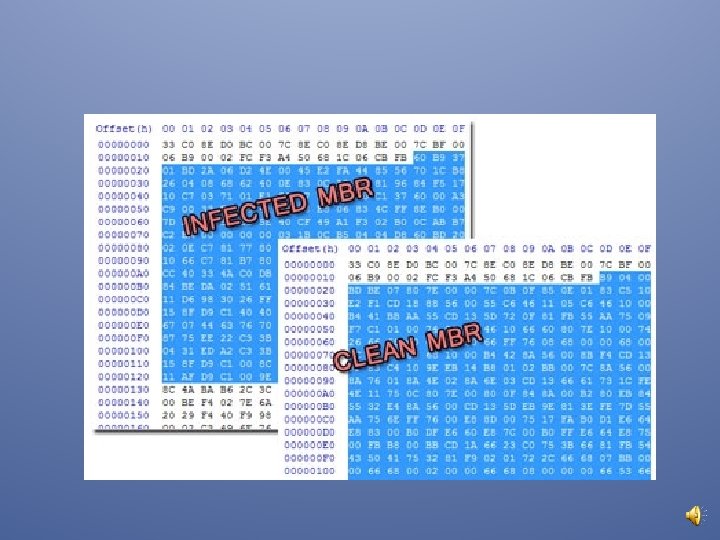
TDL 3 Rootkit • Gains control during the boot sequence • Alters Master Boot Record. This gets around the 1 st two preventions. • Enacts a restart, which loads the altered MBR and catches process signals. • Encrypted with ROR loop (rotate right).
TDL 3 Rootkit Details • Kernel code appears as raw bytes, passes security. • TDL 3 encodes and decodes files on the fly, so it can pass as being a piece of the kernel code. • At startup, hunts for driver object. • Overwrites 824 bytes, avoiding file size check • Fake driver object, captures disk I/O, hunts for kernel 32. dll • Infection
TDL 3 Rootkit • Has a watchdog thread to prevent any change to the service registry key • No one can get a handle to infected driver file(red flag) • In Feb. it caused BSOD with MS 10 -015 update • RVA(Relative Virutal Address) offsets of Windows kernel APIs modified and use them to find functions. On the update, the values were changed. After restart, the rootkit called an invalid address
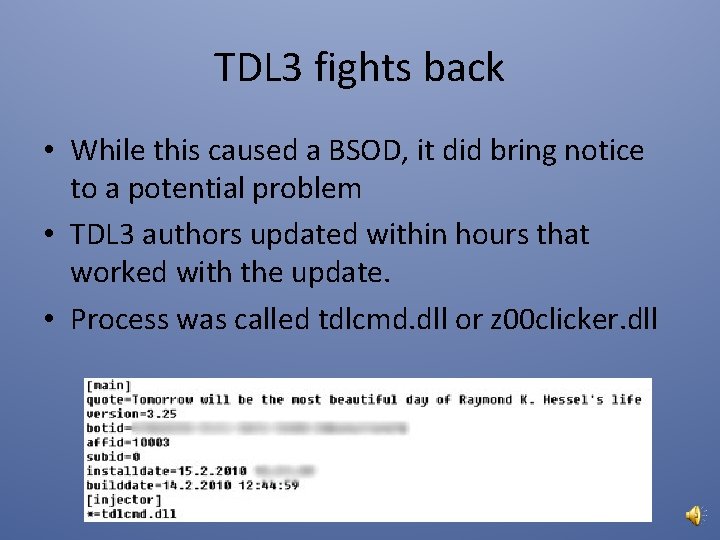
TDL 3 fights back • While this caused a BSOD, it did bring notice to a potential problem • TDL 3 authors updated within hours that worked with the update. • Process was called tdlcmd. dll or z 00 clicker. dll
TDL 3 Rootkit • • First significant 64 -bit rootkit Malware begets more malware Anti-virus lag Security chess match
Cited Sites • http: //www. guidingtech. com/4467/what-is-arootkit/ • http: //www. prevx. com/blog/154/TDL-rootkitx-goes-in-the-wild. html • http: //www. prevx. com/blog/143/BSOD-after. MS-TDL-authors-apologize. html • http: //www. prevx. com/blog/139/Tdss-rootkitsilently-owns-the-net. html
- Slides: 14