
Target Data Breach Cost of the Learning Curve
Target Data Breach – Cost of the Learning Curve Discuss the recent Target data breach and its impact on the industry as well as individuals January 29/30, 2014
Target Data Breach – Cost of the Learning Curve Presentation Overview • • • Overview Chronology of events Customer Communications (unfolding of an incident) Target – Privacy Policy updated Incident response - Target Incident response – Individuals Operation Kaptoxa Black market facts to know What did we learn? – Industry, Individual customers Cost of the learning curve Resources
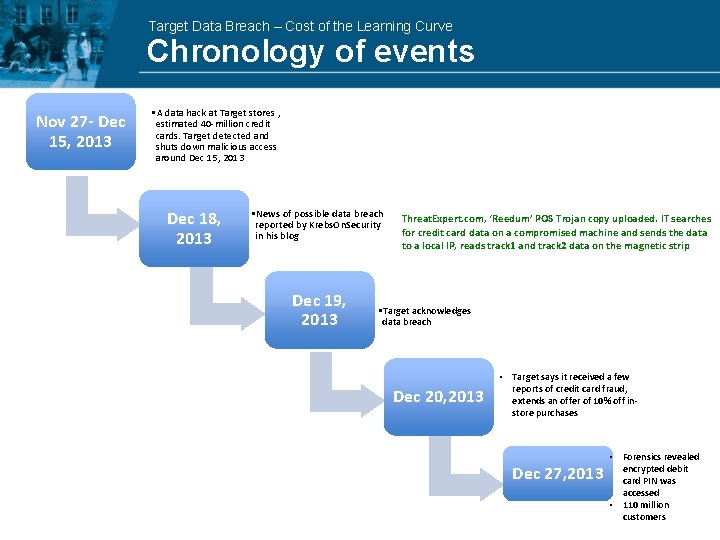
Target Data Breach – Cost of the Learning Curve Chronology of events Nov 27 - Dec 15, 2013 • A data hack at Target stores , estimated 40 -million credit cards. Target detected and shuts down malicious access around Dec 15, 2013 Dec 18, 2013 • News of possible data breach reported by Krebs. On. Security in his blog Dec 19, 2013 Threat. Expert. com, ‘Reedum’ POS Trojan copy uploaded. IT searches for credit card data on a compromised machine and sends the data to a local IP, reads track 1 and track 2 data on the magnetic strip • Target acknowledges data breach Dec 20, 2013 • Target says it received a few reports of credit card fraud, extends an offer of 10% off instore purchases Dec 27, 2013 • Forensics revealed encrypted debit card PIN was accessed • 110 million customers
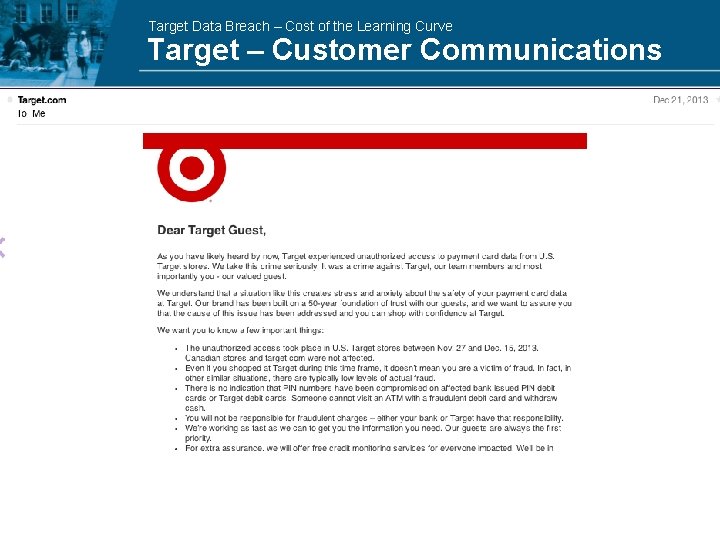
Target Data Breach – Cost of the Learning Curve Target – Customer Communications
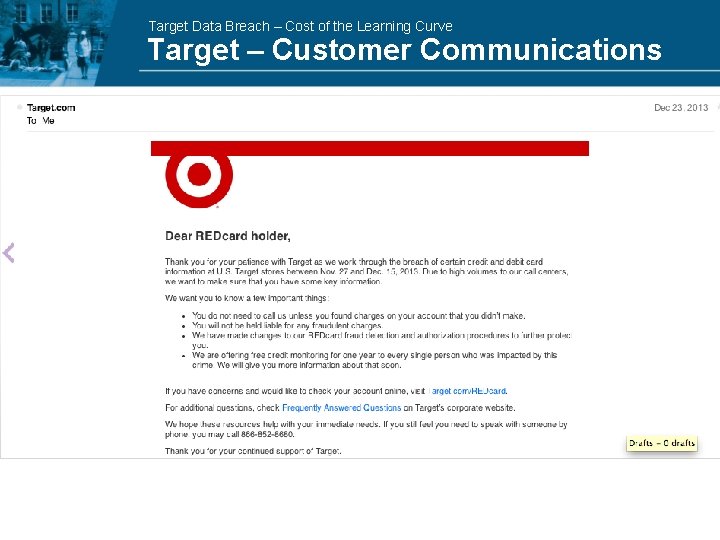
Target Data Breach – Cost of the Learning Curve Target – Customer Communications
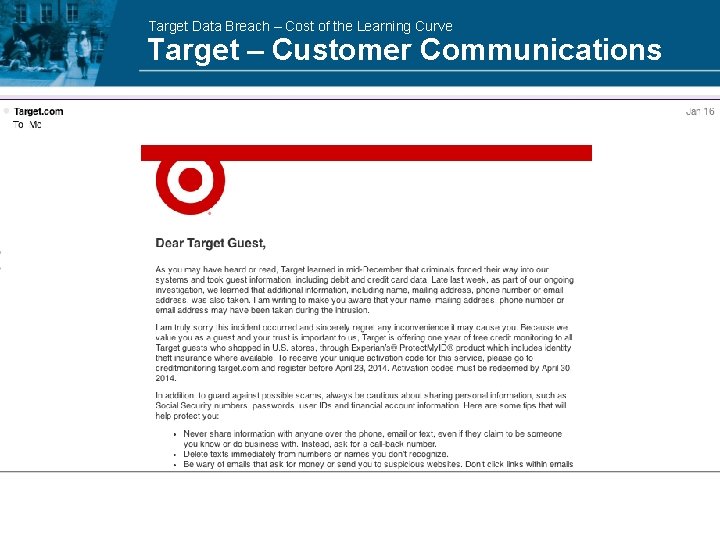
Target Data Breach – Cost of the Learning Curve Target – Customer Communications
Target Data Breach – Cost of the Learning Curve Target - Privacy Policy Updated
Target Data Breach – Cost of the Learning Curve Incident response - Target • • • Preparation Detection and analysis Containment Eradication Recovery Post-incident activity
Target Data Breach – Cost of the Learning Curve Incident response - Individuals
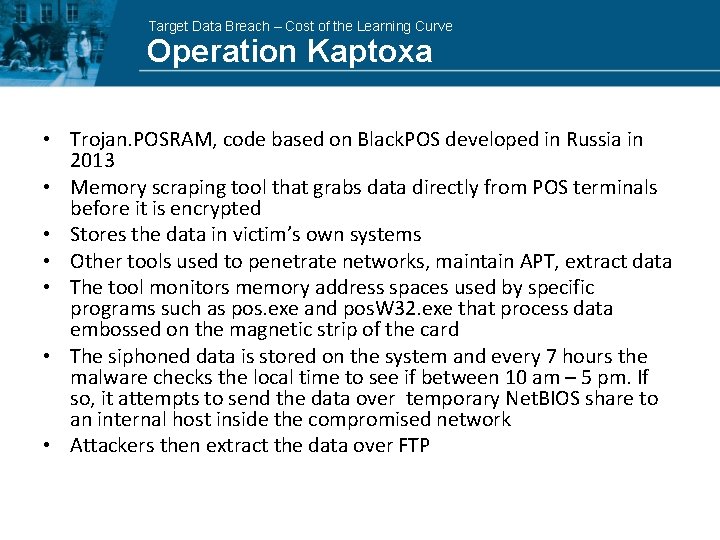
Target Data Breach – Cost of the Learning Curve Operation Kaptoxa • Trojan. POSRAM, code based on Black. POS developed in Russia in 2013 • Memory scraping tool that grabs data directly from POS terminals before it is encrypted • Stores the data in victim’s own systems • Other tools used to penetrate networks, maintain APT, extract data • The tool monitors memory address spaces used by specific programs such as pos. exe and pos. W 32. exe that process data embossed on the magnetic strip of the card • The siphoned data is stored on the system and every 7 hours the malware checks the local time to see if between 10 am – 5 pm. If so, it attempts to send the data over temporary Net. BIOS share to an internal host inside the compromised network • Attackers then extract the data over FTP
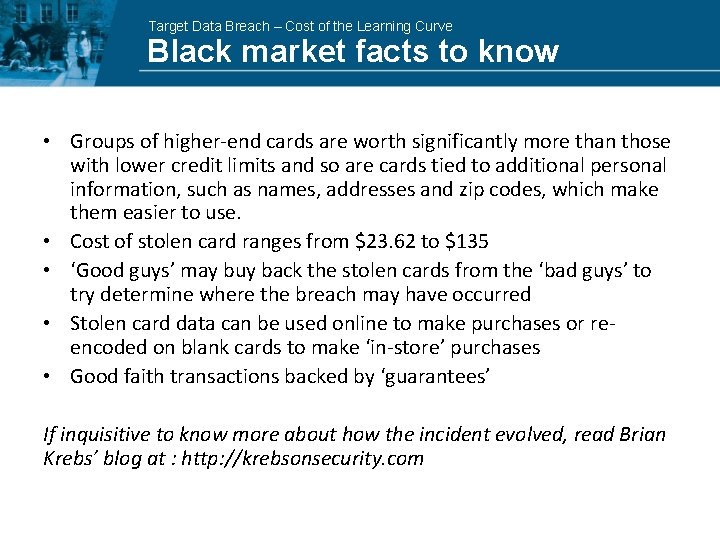
Target Data Breach – Cost of the Learning Curve Black market facts to know • Groups of higher-end cards are worth significantly more than those with lower credit limits and so are cards tied to additional personal information, such as names, addresses and zip codes, which make them easier to use. • Cost of stolen card ranges from $23. 62 to $135 • ‘Good guys’ may buy back the stolen cards from the ‘bad guys’ to try determine where the breach may have occurred • Stolen card data can be used online to make purchases or reencoded on blank cards to make ‘in-store’ purchases • Good faith transactions backed by ‘guarantees’ If inquisitive to know more about how the incident evolved, read Brian Krebs’ blog at : http: //krebsonsecurity. com
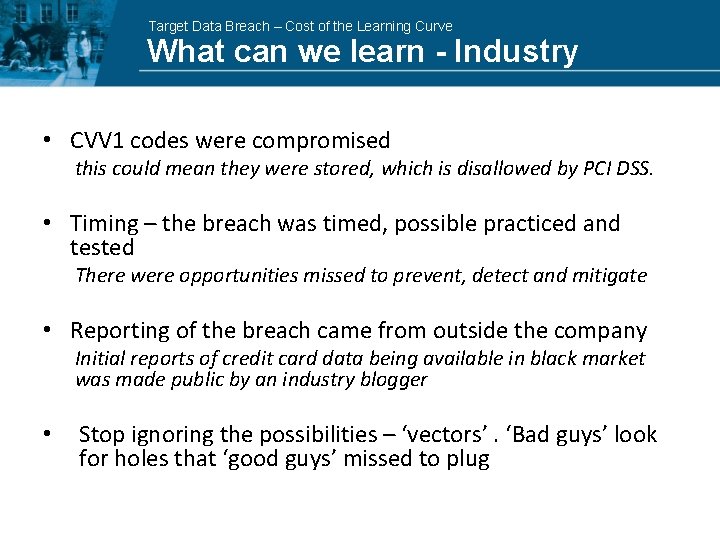
Target Data Breach – Cost of the Learning Curve What can we learn - Industry • CVV 1 codes were compromised this could mean they were stored, which is disallowed by PCI DSS. • Timing – the breach was timed, possible practiced and tested There were opportunities missed to prevent, detect and mitigate • Reporting of the breach came from outside the company Initial reports of credit card data being available in black market was made public by an industry blogger • Stop ignoring the possibilities – ‘vectors’. ‘Bad guys’ look for holes that ‘good guys’ missed to plug
Target Data Breach – Cost of the Learning Curve What can we learn - Individual • • Limit the number of debit & credit cards Use the fraud alert and credit monitoring Consider using ‘pre-paid’ reducing balance cards Protect your ‘privacy’, share information on a ‘need to know’ basis Monitor bank and financial statements Learn to identify phishing scams Apply updates and patches regularly No alternative to better awareness – news, blogs, seminars etc.
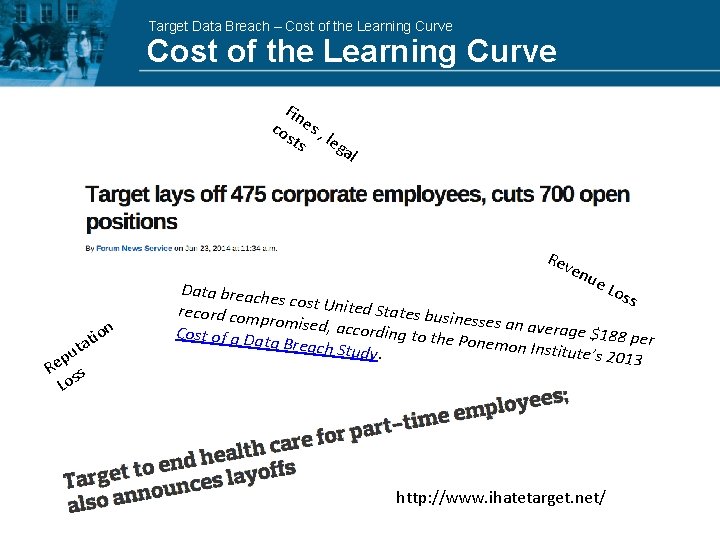
Target Data Breach – Cost of the Learning Curve Fin co es , sts le ga l Rev e nue n io t a ut p Re ss Lo Los Data breach s es cost Unite d S record comp tates busine sses an aver romised, acc age $188 pe ording to th Cost of a Da r e Ponemon ta Breach St Institute’s 2 udy. 013 http: //www. ihatetarget. net/
Target Data Breach – Cost of the Learning Curve Resources • http: //www. isightpartners. com/2014/01/kaptoxa-pos-report-faq/ • Article about the specific malware: http: //www. wired. com/threatlevel/2014/01/target-malware-identified/
Target Data Breach – Cost of the Learning Curve Presented by: Noor Aarohi Senior Analyst – Risk and Compliance GW Division of Information Technology infosec@gwu. edu
- Slides: 16