
SSH Communications Security SSH Access Management Sean Lunell
- Slides: 16
SSH Communications Security SSH Access Management Sean Lunell sean. lunell@ssh. com (408) 568 -8779 ENABLE, MONITOR & MANAGE ENCRYPTED NETWORKS Copyright 2015 SSH Communications Security
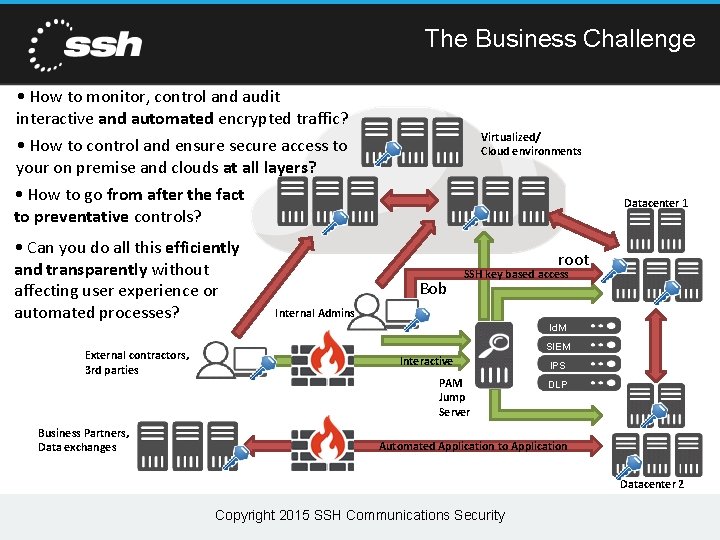
The Business Challenge • How to monitor, control and audit interactive and automated encrypted traffic? • How to control and ensure secure access to your on premise and clouds at all layers? • How to go from after the fact to preventative controls? • Can you do all this efficiently and transparently without affecting user experience or automated processes? External contractors, 3 rd parties Business Partners, Data exchanges Virtualized/ Cloud environments Datacenter 1 root Bob SSH key based access Internal Admins Id. M SIEM Interactive PAM Jump Server IPS DLP Automated Application to Application Datacenter 2 Copyright 2015 SSH Communications Security
What We Have Learned • Average • 80% SSH usage is Machine – Machine ( vs Interactive ) • 50 SSH user keys identified per Host • 10% SSH user keys are unknown AND HAVE ROOT ACCESS • Customer example: • 10, 000 servers on their network • 1. 5 million SSH Keys Identified • 10% (150, 000) user keys unknown with root access Copyright 2015 SSH Communications Security
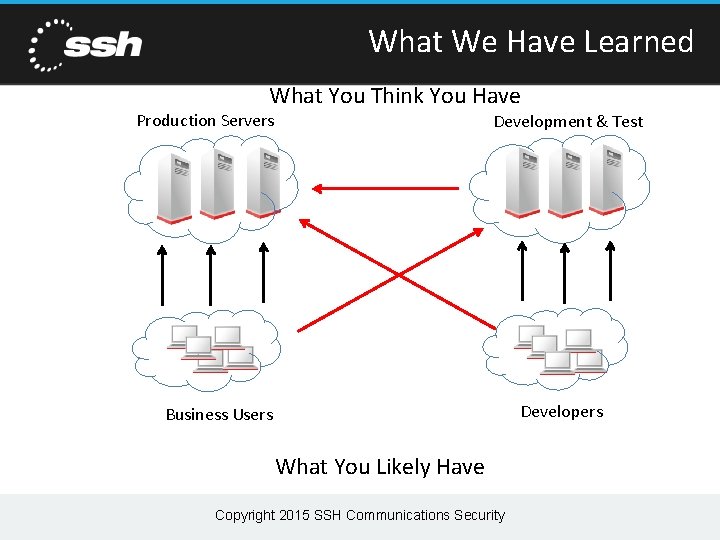
What We Have Learned What You Think You Have Production Servers Development & Test Developers Business Users What You Likely Have Copyright 2015 SSH Communications Security
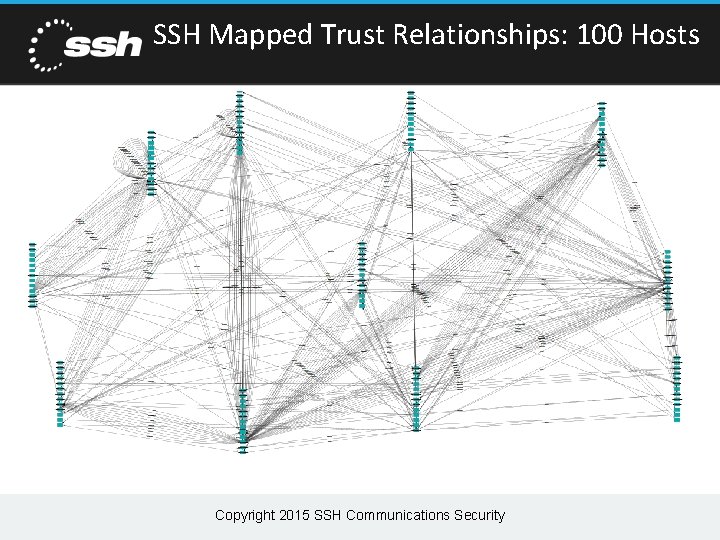
SSH Mapped Trust Relationships: 100 Hosts Copyright 2015 SSH Communications Security
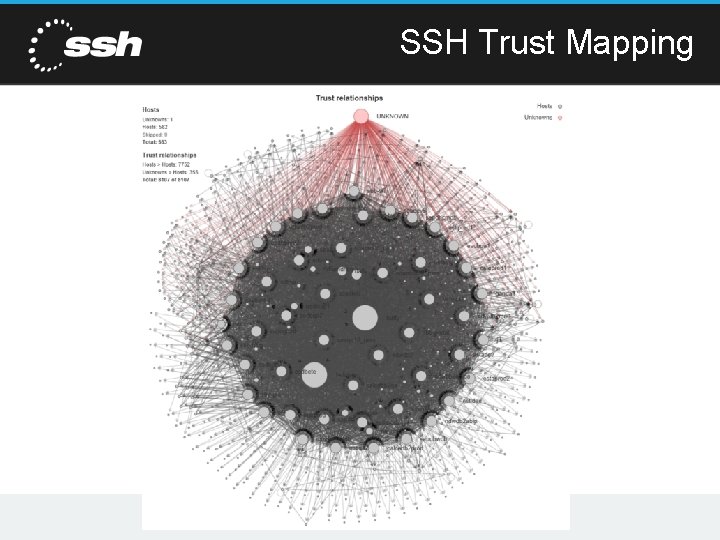
SSH Trust Mapping Copyright 2015 SSH Communications Security
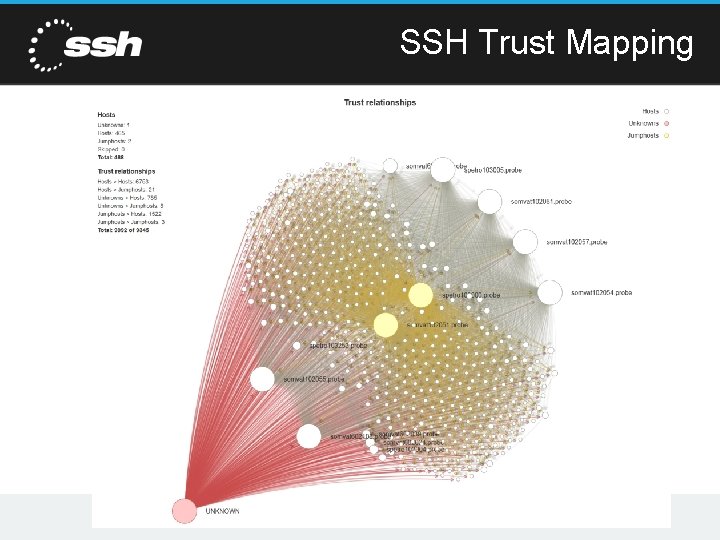
SSH Trust Mapping Copyright 2015 SSH Communications Security
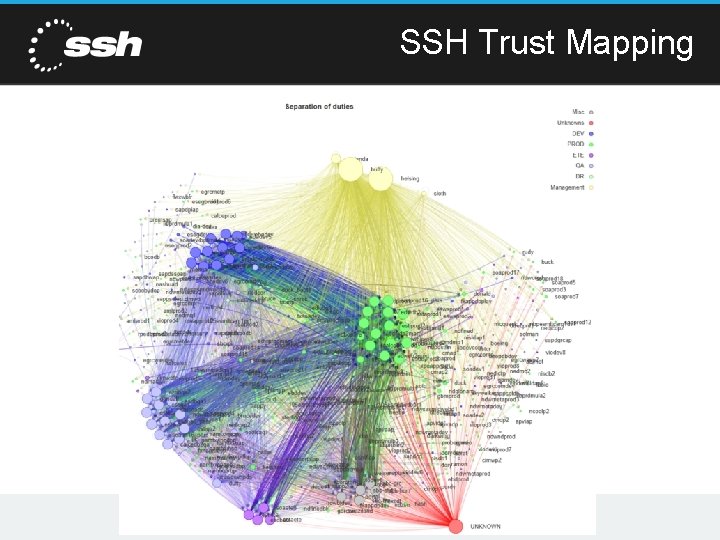
SSH Trust Mapping Copyright 2015 SSH Communications Security
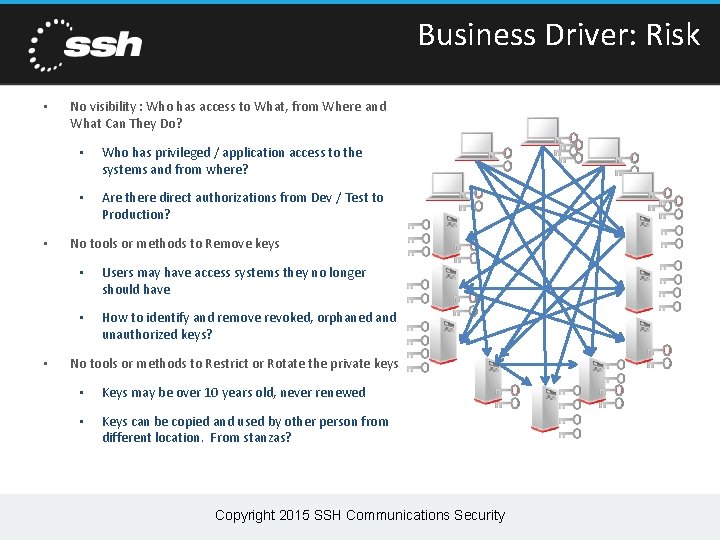
Business Driver: Risk • • • No visibility : Who has access to What, from Where and What Can They Do? • Who has privileged / application access to the systems and from where? • Are there direct authorizations from Dev / Test to Production? No tools or methods to Remove keys • Users may have access systems they no longer should have • How to identify and remove revoked, orphaned and unauthorized keys? No tools or methods to Restrict or Rotate the private keys • Keys may be over 10 years old, never renewed • Keys can be copied and used by other person from different location. From stanzas? Copyright 2015 SSH Communications Security
Business Driver: Compliance • MAS Technology Risk Mgmt Guidelines – Separation of duties, Key activity monitoring ꜜ IETF • ꜜ ꜜ NISTIR 7966 - Publication • Now official • Appendix B Cyber. Security Framework PCI – DSS 3. 0 • • Managing SSH Keys for Automated Access Current Recommended Best Practice Close cooperation with NIST COBIT / SOX Framework, HIPAA Copyright 2015 SSH Communications Security
NIST IR 7966 Best Practices • • Ensure Secure Shell server will not execute if authorized keys file and home directory are insecure • Prevent privilege escalation by process spawning • Segregate system accounts from person accounts • Use controls to limit Secure Shell access to specific commands and source addresses • Rotate keys • Require logging of Secure Shell activity ciphers and specified key lengths • Remove unneeded User Keys Require password protection for private • Document key usage keys • Regular audits Standardize the key configuration across the environment • Authorized key file should not allow end user write access • Centralized key provisioning (no more “self service provisioning). Key provisioning should be centralized and limited to a much smaller number of root level administrators • • Cipher configuration – allow only strong Copyright 2015 SSH Communications Security
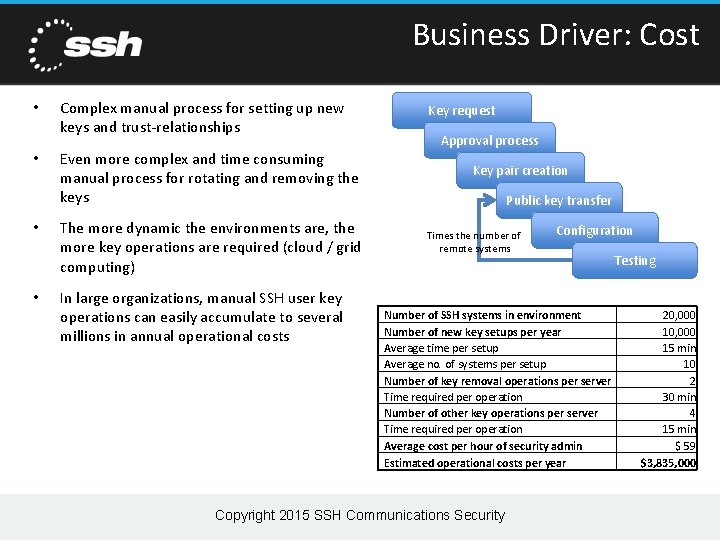
Business Driver: Cost • • Complex manual process for setting up new keys and trust-relationships Even more complex and time consuming manual process for rotating and removing the keys The more dynamic the environments are, the more key operations are required (cloud / grid computing) In large organizations, manual SSH user key operations can easily accumulate to several millions in annual operational costs Key request Approval process Key pair creation Public key transfer Times the number of remote systems Configuration Number of SSH systems in environment Number of new key setups per year Average time per setup Average no. of systems per setup Number of key removal operations per server Time required per operation Number of other key operations per server Time required per operation Average cost per hour of security admin Estimated operational costs per year Copyright 2015 SSH Communications Security Testing 20, 000 15 min 10 2 30 min 4 15 min $ 59 $3, 835, 000
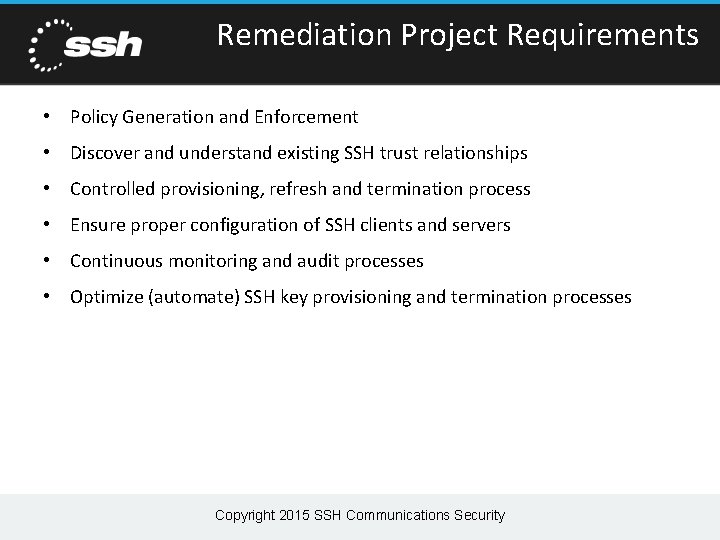
Remediation Project Requirements • Policy Generation and Enforcement • Discover and understand existing SSH trust relationships • Controlled provisioning, refresh and termination process • Ensure proper configuration of SSH clients and servers • Continuous monitoring and audit processes • Optimize (automate) SSH key provisioning and termination processes Copyright 2015 SSH Communications Security
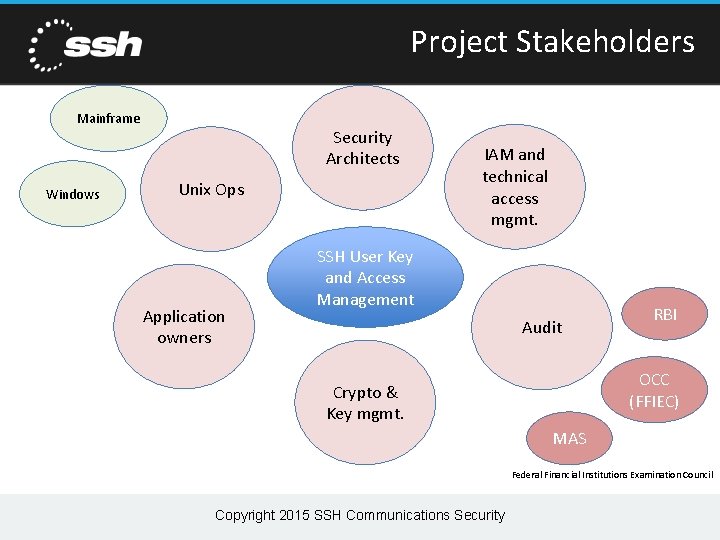
Project Stakeholders Mainframe Windows Security Architects Unix Ops Application owners IAM and technical access mgmt. SSH User Key and Access Management Audit RBI OCC (FFIEC) Crypto & Key mgmt. MAS Federal Financial Institutions Examination Council Copyright 2015 SSH Communications Security
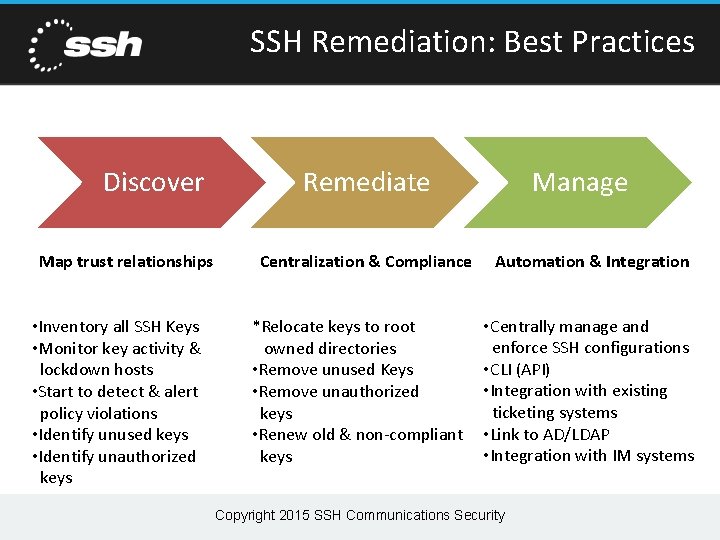
SSH Remediation: Best Practices Discover Map trust relationships • Inventory all SSH Keys • Monitor key activity & lockdown hosts • Start to detect & alert policy violations • Identify unused keys • Identify unauthorized keys Remediate Centralization & Compliance *Relocate keys to root owned directories • Remove unused Keys • Remove unauthorized keys • Renew old & non-compliant keys Manage Automation & Integration • Centrally manage and enforce SSH configurations • CLI (API) • Integration with existing ticketing systems • Link to AD/LDAP • Integration with IM systems Copyright 2015 SSH Communications Security
SSH Communications Security SSH Access Management Sean Lunell sean. lunell@ssh. com (408) 568 -8779 ENABLE, MONITOR & MANAGE ENCRYPTED NETWORKS Copyright 2015 SSH Communications Security