
Speaker Scott Sattler CRISC CCFP CBCP CFE CCNP
Speaker - Scott Sattler, CRISC, CCFP, CBCP, CFE, CCNP, CCDP CISA, CISSP, HCISSP, CISM, ACSA | Automating SIEM Use Cases With Encase Threat Intelligence Processing 1
Information Overload Master Title 300, 000 Events Per Second Classic Problem Statement Do More With Less SIEM One Console Increased Visibility More Information More Incidents Fewer FTE’s 2
Threat - is a possible danger that might exploit a vulnerability to breach security and thus cause possible harm Intelligence - The ability to perceive and/or retain knowledge or information and apply it to itself or other instances of knowledge or information creating referable understanding models of any size, density, or complexity, due to any conscious or subconscious imposed will or instruction to do so 3
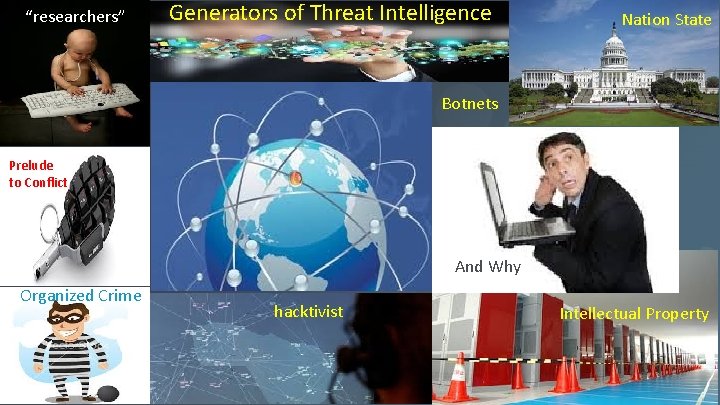
“researchers” Generators of Threat Intelligence Nation State Botnets Prelude to Conflict And Why Organized Crime hacktivist Intellectual Property 4
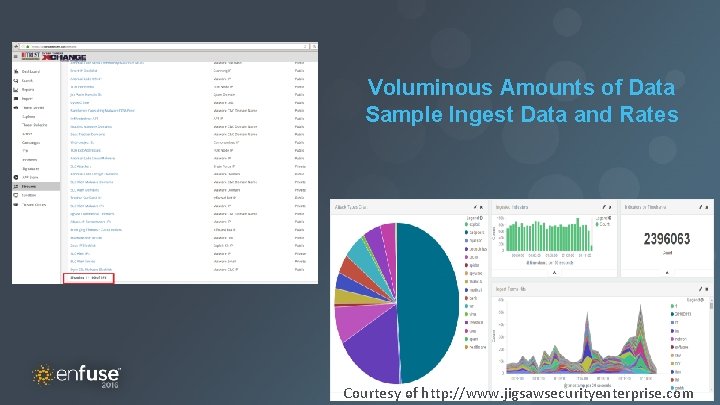
Master Title Voluminous Amounts of Data Sample Ingest Data and Rates 5 Courtesy of http: //www. jigsawsecurityenterprise. com
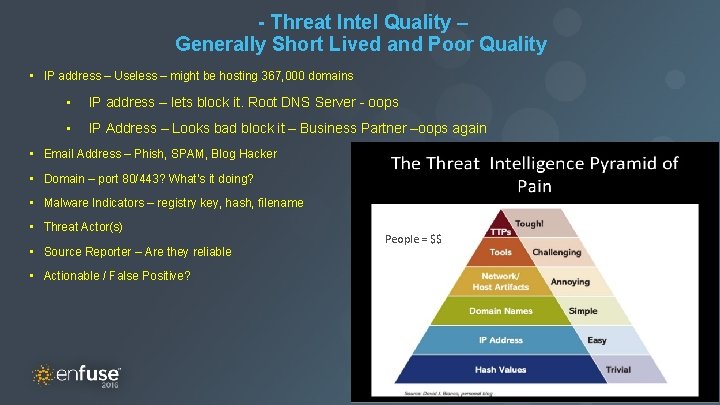
- Threat Intel Quality – Generally Short Lived and Poor Quality Master Title • IP address – Useless – might be hosting 367, 000 domains • IP address – lets block it. Root DNS Server - oops • IP Address – Looks bad block it – Business Partner –oops again • Email Address – Phish, SPAM, Blog Hacker • Domain – port 80/443? What’s it doing? • Malware Indicators – registry key, hash, filename • Threat Actor(s) • Source Reporter – Are they reliable People = $$ • Actionable / False Positive? 6
Threat Intel Master Title Lots of data floating around – easy to get …………. But can your Cyber SECOPS Team • Process the raw data, ingest the data, analyze, integrate, correlate, respond, report and share • And prove the data is worth anything - automatically And then…. how will you react…. . but what if you don’t or can’t keep up? 7
Master Title Threat Intelligence Processing “Inside” and “Outside” Threat Intel 8
Master Title Information Overload 300, 000 Events Per Second SIEM One Console Many Log Sources $Correlated Events$ 9
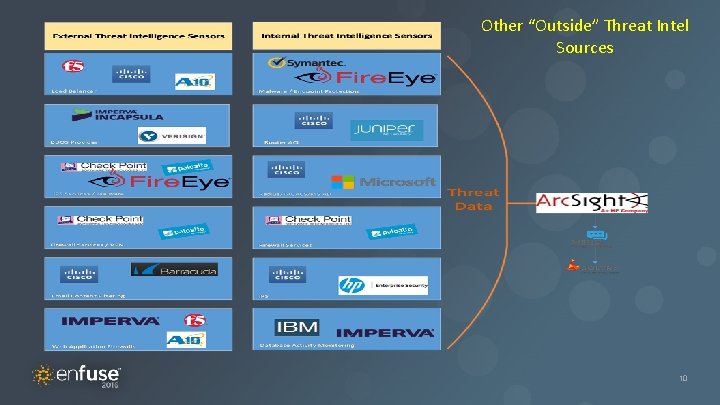
Master Title Other “Outside” Threat Intel Sources 10
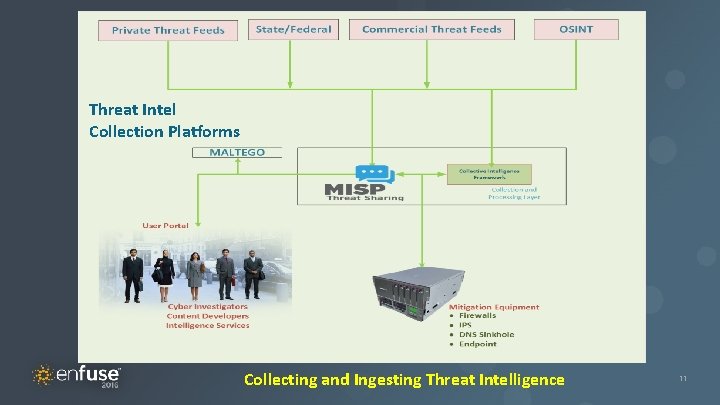
Threat Intel Collection Platforms Collecting and Ingesting Threat Intelligence 11
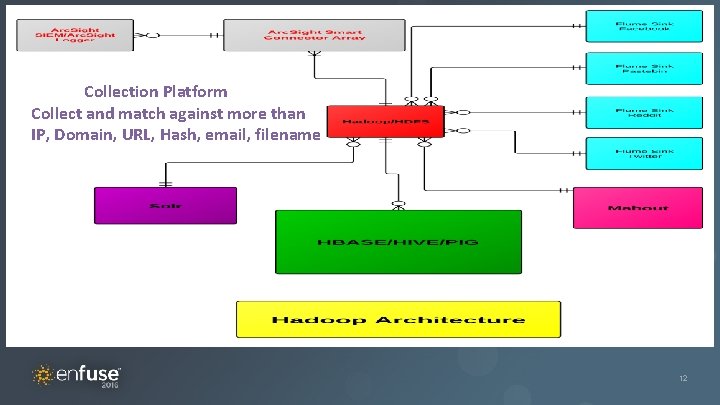
Master Title Collection Platform Collect and match against more than IP, Domain, URL, Hash, email, filename 12
The Problem You Will Find Master Title • • • Lots of SIEM Tickets being generated – Is that Good? Few Cyber Forensic Analyst and costly ones at that Taking too much time to determine event False Positives burning analyst and desktop support time Can’t process all tickets Missing important events 13
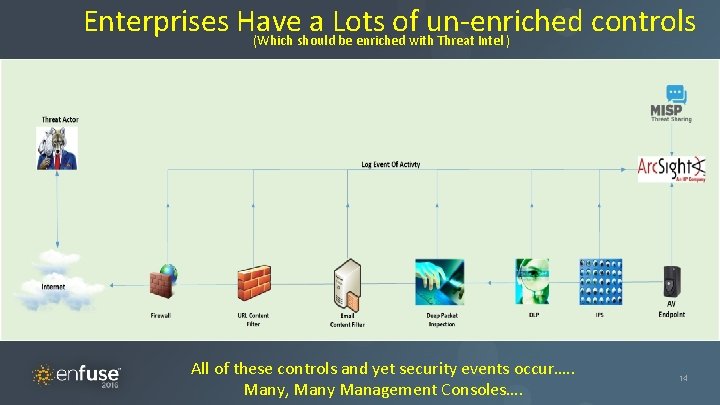
Enterprises Have a Lots of un-enriched controls (Which should be enriched with Threat Intel ) Master Title All of these controls and yet security events occur…. . Many, Many Management Consoles…. 14
Master Title So, How do you Solve 250, 000 + Endpoints Daily 1000’s of tickets matching Threat IOC’s 12 Cyber Forensic Investigators 15
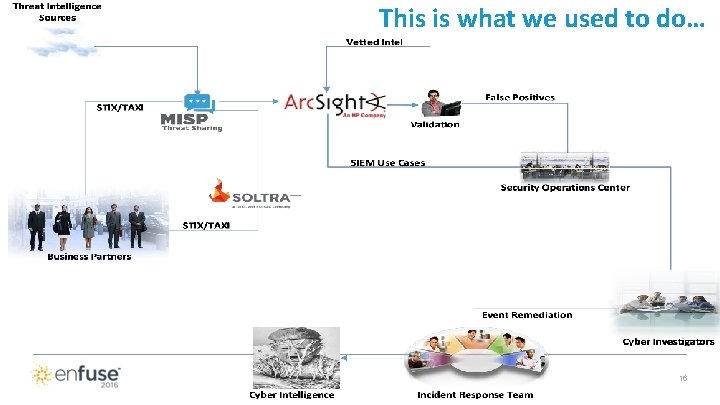
This is what we used to do… 16
Aka - Ticket Hell First Step - Stop the Bleeding Reduce the number of tickets by Correlating with other Security Controls But You will miss critical events Because you truly do not see what is happening with the endpoint 17
How the problem was solved Master Title Part 1 First step enrich the Threat Intel Event Pull Network PCAP from DPI and Return to SIEM Console • Still Required Analyst to review • Wasted Analyst Time • Uncertainty still existed “The Dream - Single Pain of Glass” 18
How the problem was solved r Title Part 2 SIEM correlation off the enriched Threat Event Then use Encase to pull Endpoint snapshots and return the results to the SIEM in an active channel and add to an Activelist and perform event correlation “Closer to Single Pain of Glass” 19
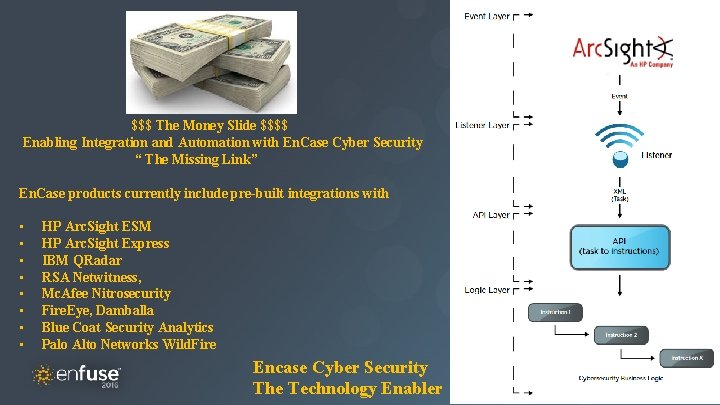
Master Title $$$ The Money Slide $$$$ Enabling Integration and Automation with En. Case Cyber Security “ The Missing Link” En. Case products currently include pre-built integrations with • • HP Arc. Sight ESM HP Arc. Sight Express IBM QRadar RSA Netwitness, Mc. Afee Nitrosecurity Fire. Eye, Damballa Blue Coat Security Analytics Palo Alto Networks Wild. Fire Encase Cyber Security The Technology Enabler 20
How the problem was solved - Part 3 Master Title SIEM now had all the events needed to prove the event: 1. Threat Intel IOC (initial event) 2. Packet Capture of the Event (src, dst, port, url, domain) 3. Endpoint Artifacts from the affected endpoint (dll, ports, tcp) * Key Point Collected Data matched with Cyber Forensic Analyst Business Logic Aka – The Scoring System All these Events were used to determine event escalation and significantly reduce actionable tickets to the Cyber Forensic Team. “Reaching Zero Pain of Glass” 21
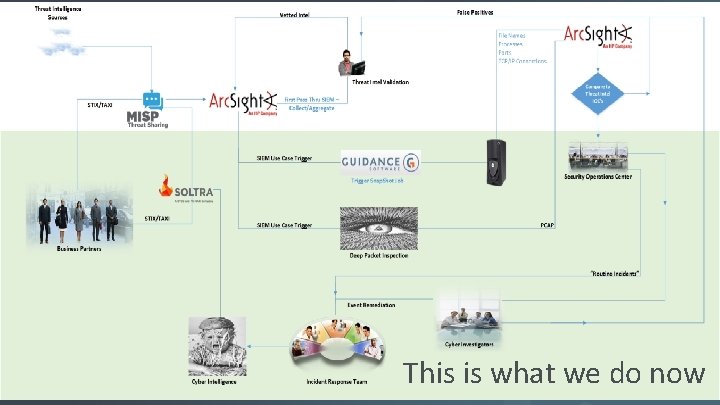
This is what we do now 22
Value Security Operation Center • Less Tickets • More automation for routine malware events (Send right to remediation) Cyber Forensic Investigator • Handle higher number of incidents (force multiplier) • Less frustration with Analyst guessing what really happened Cyber Security Incident Response Team • Less Tickets • Less end user disruption • Less Finger pointing about false positives Desktop Support • Minimized False Positives • Can auto reimage “un-cleanable” machines (No visit to end user) 23
Final Thoughts – Why Use the SIEM For Triggering Events Too disjointed, what control triggered on what logic…. We did not like having limited control on what we could trigger on. With Arcsight, we build additional logic to reduce false positives and control the routing of the incident to the different investigation teams Other Encase Integrations • • HP Arc. Sight ESM HP Arc. Sight Express, IBM QRadar, RSA Netwitness, Mc. Afee Nitrosecurity Fire. Eye, Damballa Blue Coat Security Analytics Palo Alto Networks Wild. Fire Case Management – Otherwise play find the artifacts…. but that’s another presentation 24
Thank You Scott Sattler | Cyber Investigator | Secure Labs Scott@Secure. Labs. Net | 321. 626. 6832 25
- Slides: 25