
SOS An Architecture For Mitigating DDo S Attacks
- Slides: 19
SOS: An Architecture For Mitigating DDo. S Attacks Angelos D. Keromytis, Vishal Misra, Dan Rubenstein ACM SIGCOMM 2002 Presented By: Hiral Chhaya CDA 6133
Outline Introduction SOS Architecture Defense Against Attacks Performance Strength Weaknesses Future Work
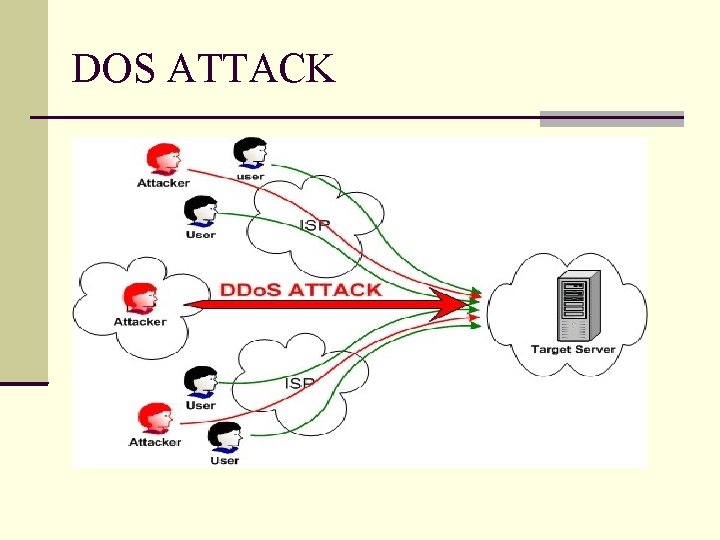
DOS ATTACK
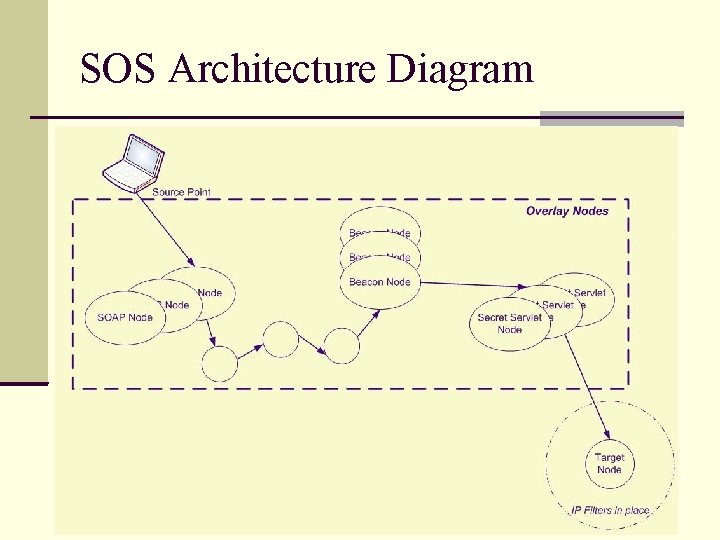
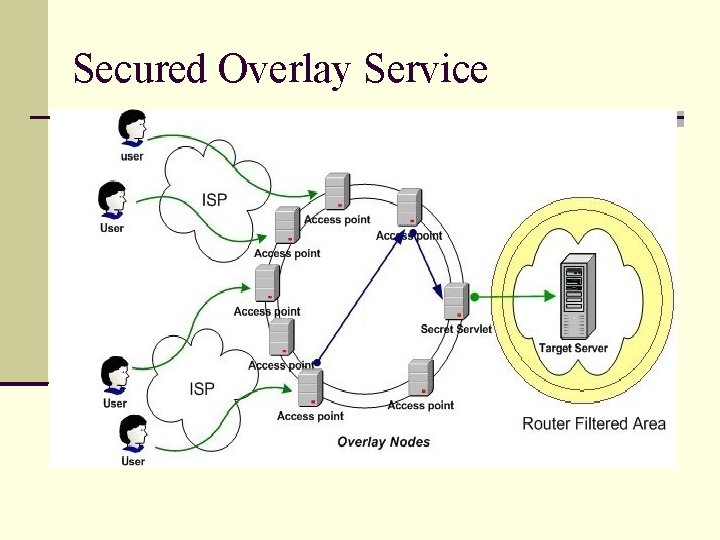
Introduction SOS – Secure Overlay Services Proactively secure communications between known entities against Denial of Service (Do. S) Attacks Assumes a pre-determined set of approved clients communicating with a target Packets are validated at entry points of the overlay and once inside are tunneled securely to secretly designated nodes.
SOS Architecture Diagram
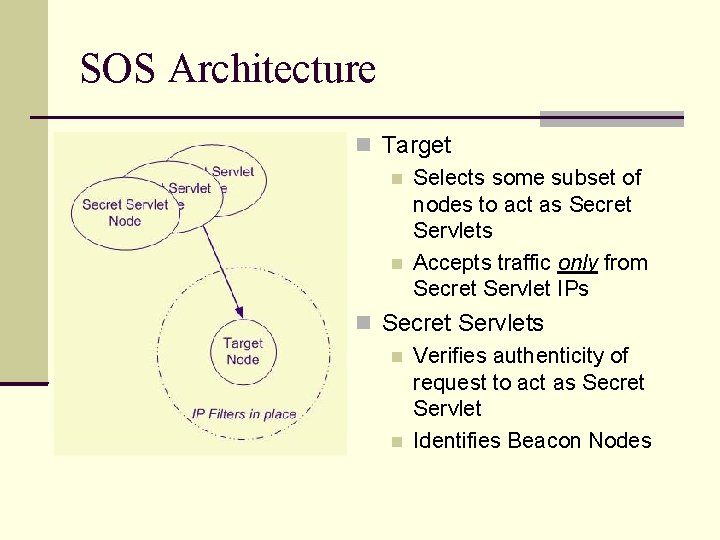
SOS Architecture Target Selects some subset of nodes to act as Secret Servlets Accepts traffic only from Secret Servlet IPs Secret Servlets Verifies authenticity of request to act as Secret Servlet Identifies Beacon Nodes
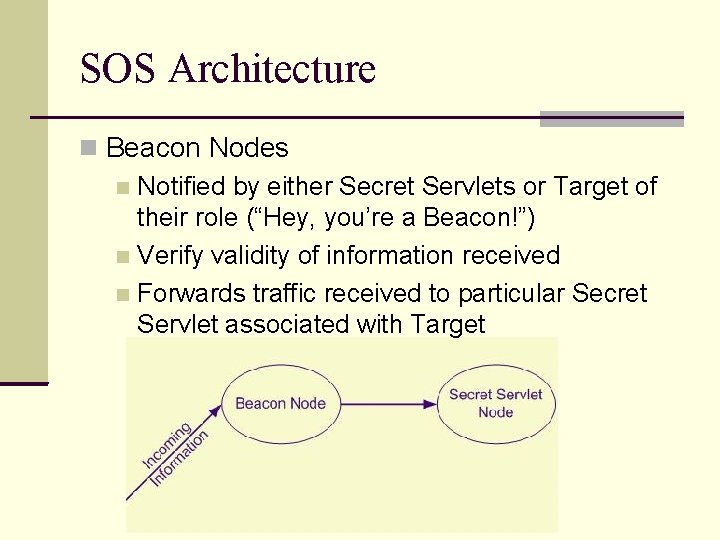
SOS Architecture Beacon Nodes Notified by either Secret Servlets or Target of their role (“Hey, you’re a Beacon!”) Verify validity of information received Forwards traffic received to particular Secret Servlet associated with Target
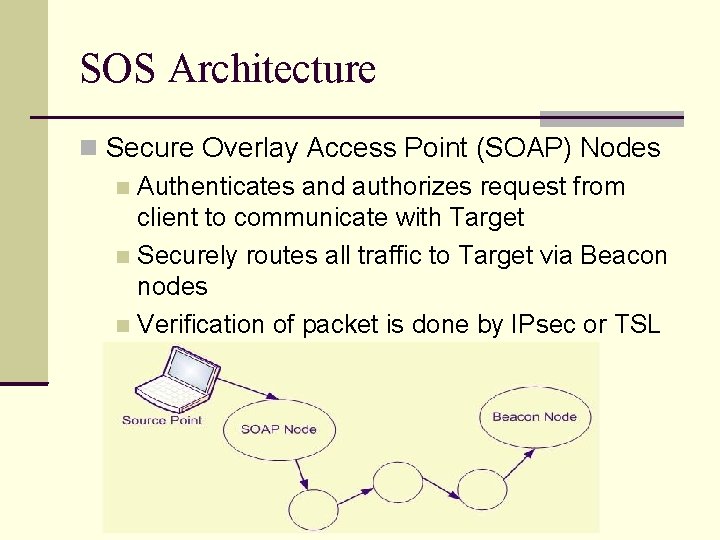
SOS Architecture Secure Overlay Access Point (SOAP) Nodes Authenticates and authorizes request from client to communicate with Target Securely routes all traffic to Target via Beacon nodes Verification of packet is done by IPsec or TSL
Protection Against Do. S If an SOAP node is attacked, source point can enter through an alternate SOAP node If a node within the overlay is attacked, the node “exits” and the overlay provides new paths to Beacons No node is more important or sensitive than any other If Secret Servlet is compromised, new subset of Secret Servlets can be chosen
Secured Overlay Service
Defending Against Attack Security Analysis Assumptions: An attacker knows and can attack overlay nodes Attacker does not know functionality of any given node, and cannot determine it Bandwidth available to launch an attack is limited Different users access overlay via different SOAPs A node can simultaneously act as a SOAP, Beacon and/or Secret Servlet
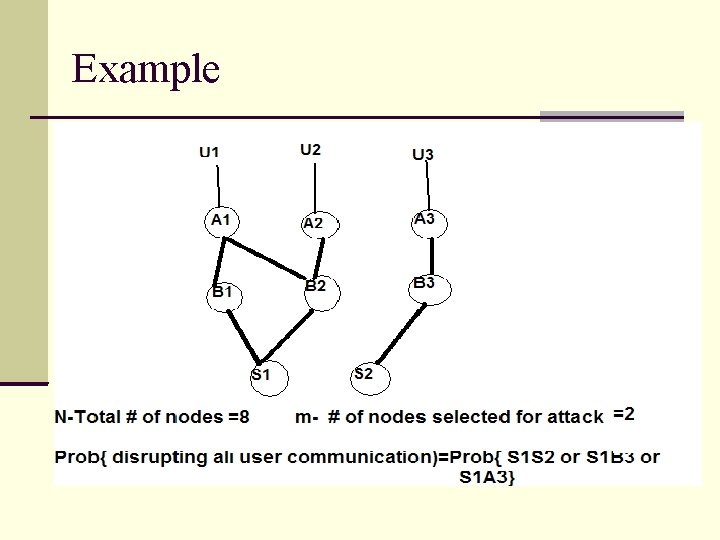
Example
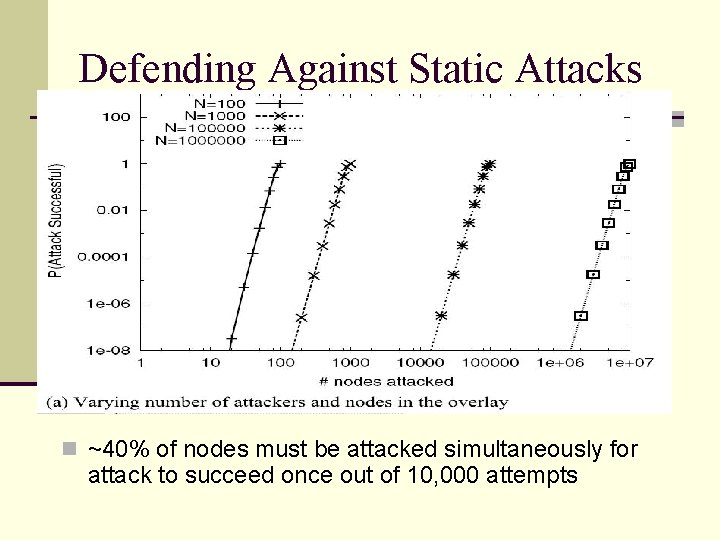
Defending Against Static Attacks ~40% of nodes must be attacked simultaneously for attack to succeed once out of 10, 000 attempts
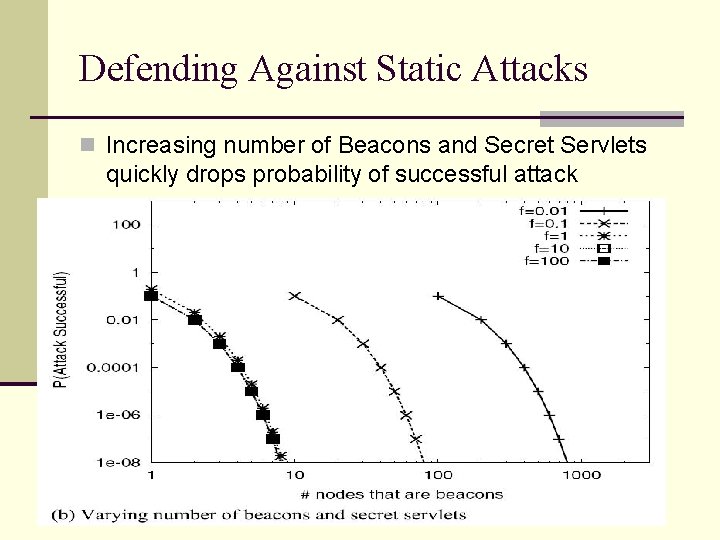
Defending Against Static Attacks Increasing number of Beacons and Secret Servlets quickly drops probability of successful attack
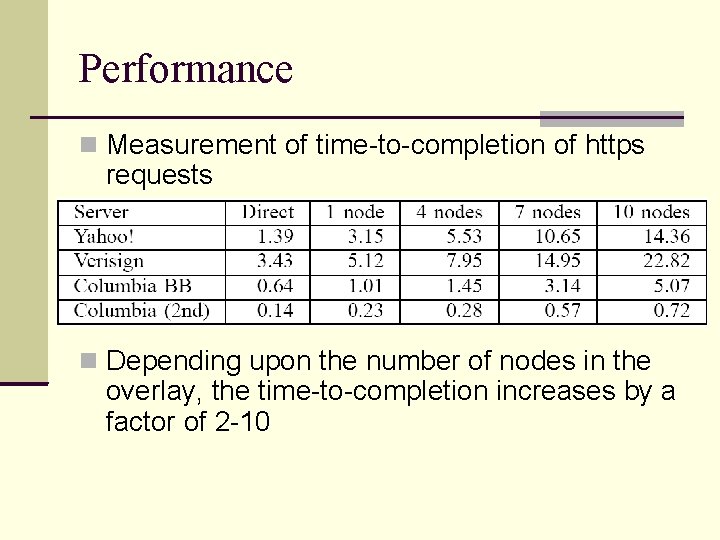
Performance Measurement of time-to-completion of https requests Depending upon the number of nodes in the overlay, the time-to-completion increases by a factor of 2 -10
Strengths Proactive approach to fighting Denial of Service (Do. S) attacks Overlay can self-heal when a participant node is attacked Scalable access control
Weaknesses Assumes, for security analysis, that no attack can come from inside the overlay Assumes that an attacker cannot mask illegitimate traffic to appear legitimate To improve scalability, the number of SOAPs, Beacons, and Secret Servlets are limited – which lessens protection from Do. S attacks Shortcut implementation does not protect secret information
Future Work More details about how repair and attack processes will function Evaluation of damage and attack that can come from inside the overlay Consideration of attack traffic that may be able to pass through overlay Exploration of overlays shared by multiple organizations in a secure manner Investigation of possible shortcuts through the overlay that do not compromise security
Thank You !!!!