
SMIME Capabilities Certificate Extension Stefan Santesson Microsoft The
S/MIME Capabilities Certificate Extension Stefan Santesson Microsoft
The Issue n n S/MIME Capabilities attribute defined in RFC 2633 (Signed attribute in signer. Info) But what if no prior signed message has been received? Today – Must revert to default settings Default setting of large installed base = 40 bit encraption.
Proposed solution n n Add cabability to add S/MIME Capabilities in certificates Preserv data structure and structure OID of the S/MIME Capabilities Attribute (RFC 2633 & PKCS&9)
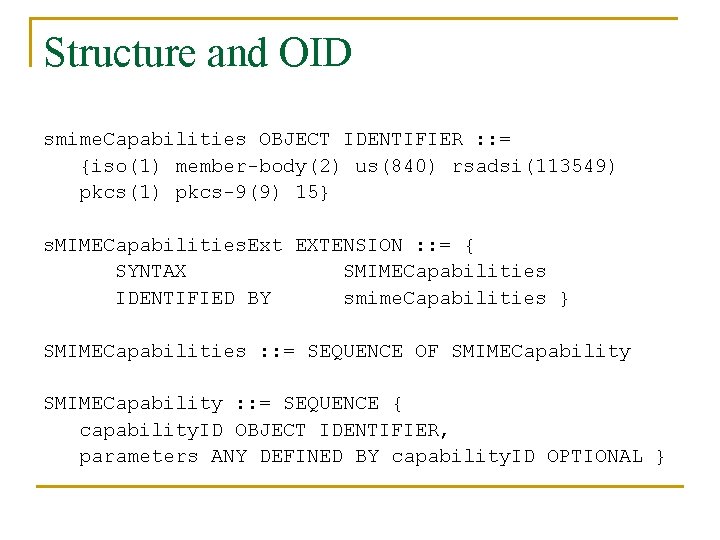
Structure and OID smime. Capabilities OBJECT IDENTIFIER : : = {iso(1) member-body(2) us(840) rsadsi(113549) pkcs(1) pkcs-9(9) 15} s. MIMECapabilities. Ext EXTENSION : : = { SYNTAX SMIMECapabilities IDENTIFIED BY smime. Capabilities } SMIMECapabilities : : = SEQUENCE OF SMIMECapability : : = SEQUENCE { capability. ID OBJECT IDENTIFIER, parameters ANY DEFINED BY capability. ID OPTIONAL }
Current status n n Capacity to process the proposed extension is allready implemented in large installed base. First draft written but not posted (available from http: //www. imc. org/xxxx/draft-ietfsantesson-smimecapext-00. txt)
Issues n n n Is it appropriate to include this info in certificates? Is it reasonable to assume that a CA can have suficient knowledge about the subjects cryptographic capabilities? Is it appropriate to use the existing attribute structure and OID? How does this affect other S/MIME RFC: s? How does this affect PKIX? Is the S/MIME group the right place for this?
- Slides: 6