
Security roles Resource scoping Best Practices in Patch
Security roles & Resource scoping Best Practices in Patch Management Santana Villa EMEA Regional Product Manager Security roles & Resource scoping Best Practices in Patch Management 1
Agenda ü Patch Management ü Common Terms & Key areas ü 4 A Model - Best practices approach ü Security Roles & scoping ü Demo ü Q&A Security roles & Resource scoping Best Practices in Patch Management 2
V e n d Security roles & Resource scoping Best Practices in Patch Management o r s 3
Common Terms & Key Components Security roles & Resource scoping Best Practices in Patch Management 4
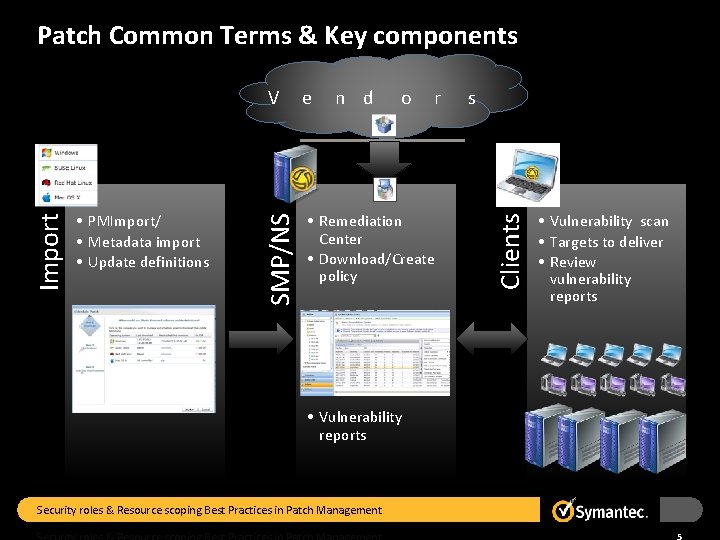
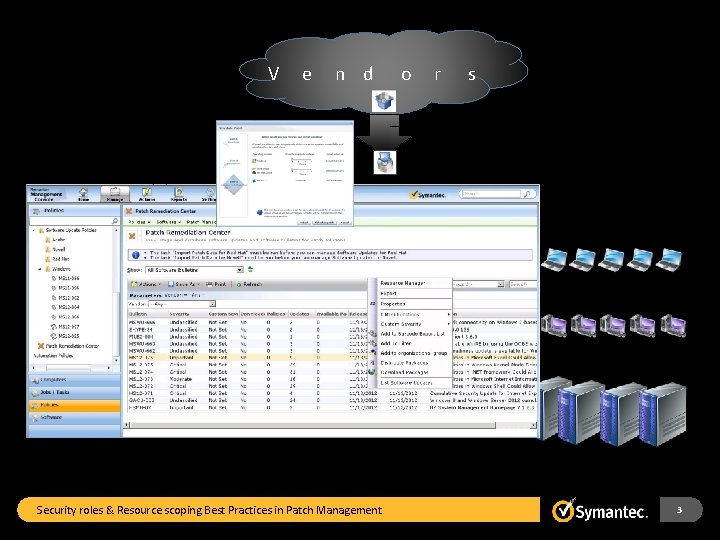
Patch Common Terms & Key components e n d o r • Remediation Center • Download/Create policy • Vulnerability reports Security roles & Resource scoping Best Practices in Patch Management s Clients • PMImport/ • Metadata import • Update definitions SMP/NS Import V • Vulnerability scan • Targets to deliver • Review vulnerability reports
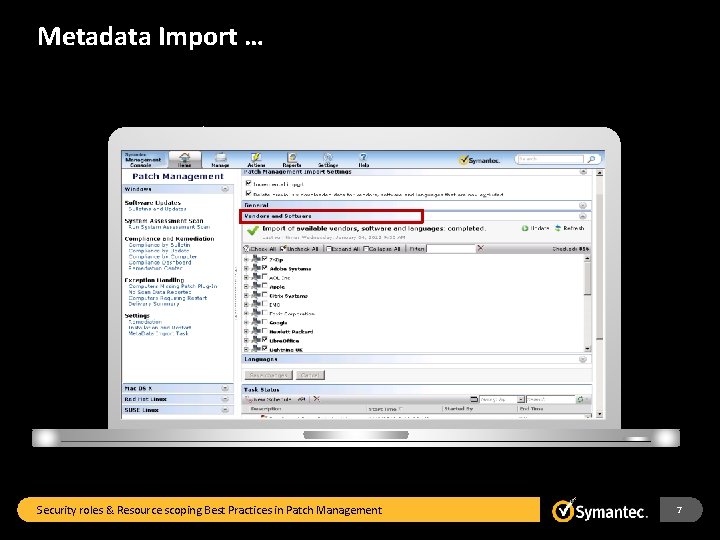
Metadata Import … Security roles & Resource scoping Best Practices in Patch Management 7
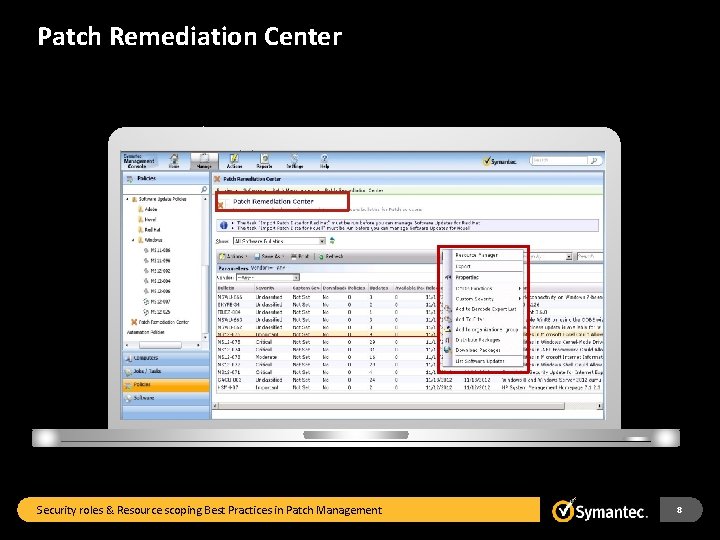
Patch Remediation Center Security roles & Resource scoping Best Practices in Patch Management 8
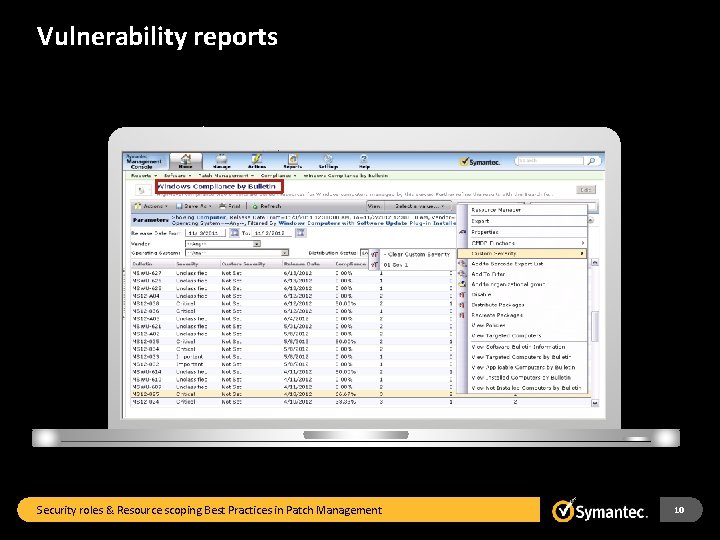
Vulnerability reports Security roles & Resource scoping Best Practices in Patch Management 10
4 A Model - Best practices approach for Optimal Balance Security roles & Resource scoping Best Practices in Patch Management 11
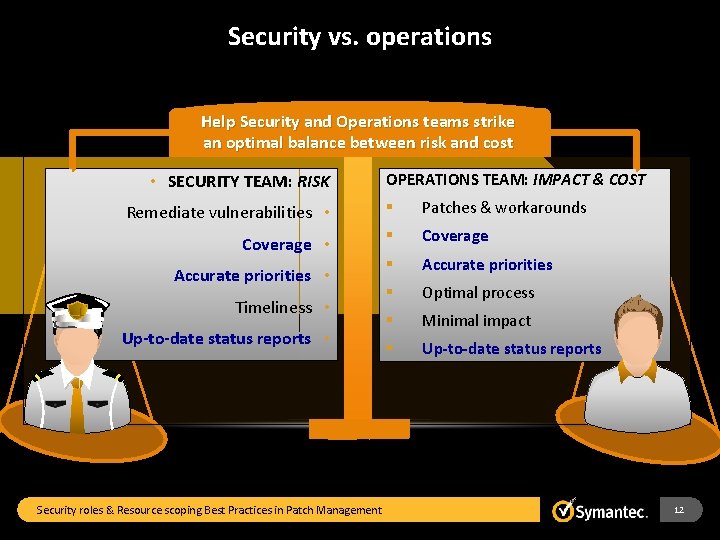
Security vs. operations Help Security and Operations teams strike an optimal balance between risk and cost • SECURITY TEAM: RISK OPERATIONS TEAM: IMPACT & COST Remediate vulnerabilities • § Patches & workarounds Coverage • § Coverage § Accurate priorities § Optimal process § Minimal impact § Up-to-date status reports Accurate priorities • Timeliness • Up-to-date status reports • Security roles & Resource scoping Best Practices in Patch Management 12
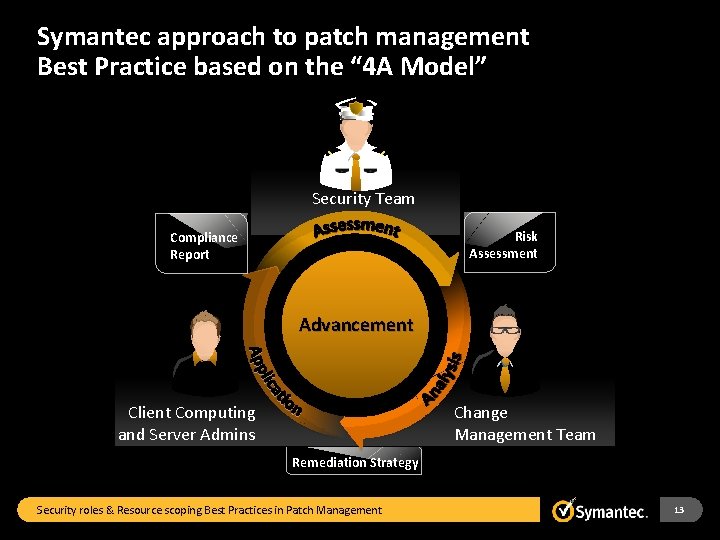
Symantec approach to patch management Best Practice based on the “ 4 A Model” Security Team Risk Assessment Compliance Report Advancement Client Computing and Server Admins Change Management Team Remediation Strategy Security roles & Resource scoping Best Practices in Patch Management 13
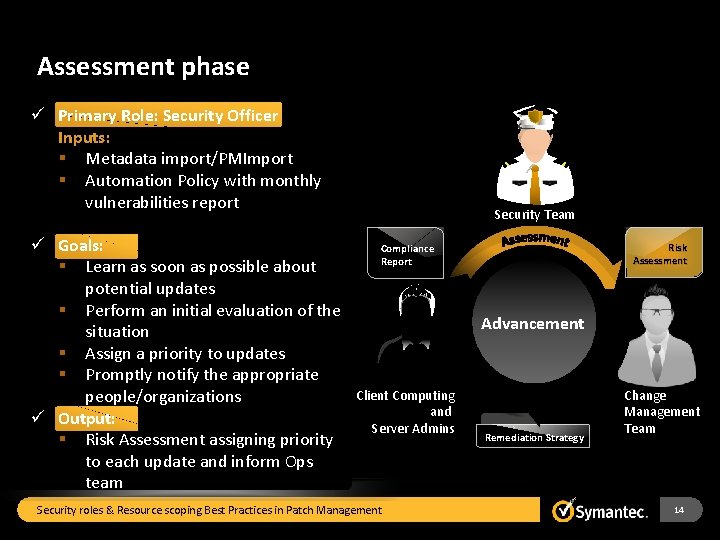
Assessment phase ü Primary Role: Security Officer Inputs: § Metadata import/PMImport § Automation Policy with monthly vulnerabilities report ü Goals: § Learn as soon as possible about potential updates § Perform an initial evaluation of the situation § Assign a priority to updates § Promptly notify the appropriate people/organizations ü Output: § Risk Assessment assigning priority to each update and inform Ops team Security Team Risk Assessment Compliance Report Advancement Client Computing and Server Admins Security roles & Resource scoping Best Practices in Patch Management Remediation Strategy Change Management Team 14
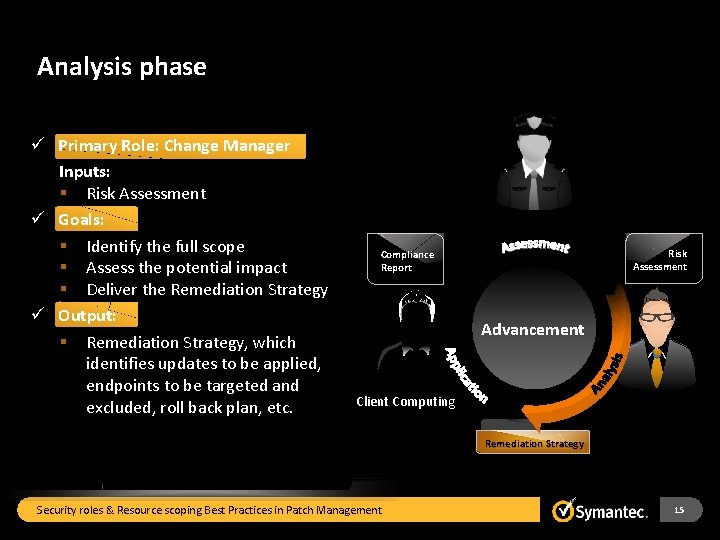
Analysis phase ü Primary Role: Change Manager Inputs: § Risk Assessment ü Goals: § Identify the full scope § Assess the potential impact § Deliver the Remediation Strategy ü Output: § Remediation Strategy, which identifies updates to be applied, endpoints to be targeted and excluded, roll back plan, etc. Security Team Risk Assessment Compliance Report § Advancement Client Computing and Server Admins Security roles & Resource scoping Best Practices in Patch Management Remediation Strategy Change Management Team 15
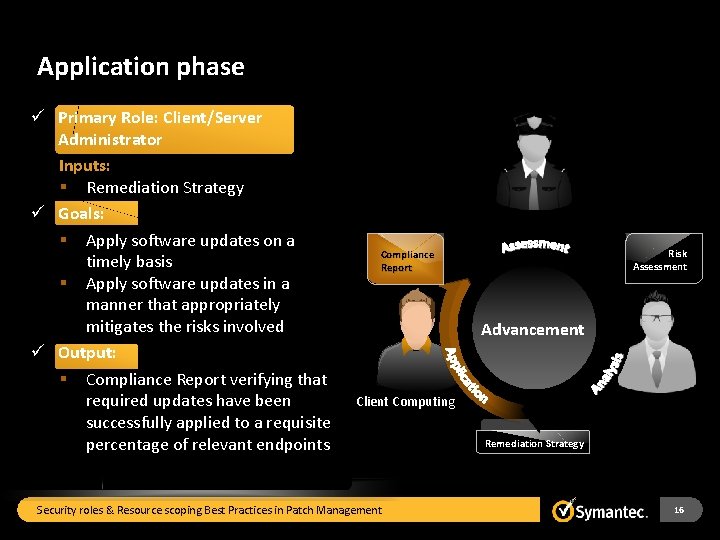
Application phase ü Primary Role: Client/Server Administrator Inputs: § Remediation Strategy ü Goals: § Apply software updates on a timely basis § Apply software updates in a manner that appropriately mitigates the risks involved ü Output: § Compliance Report verifying that required updates have been successfully applied to a requisite percentage of relevant endpoints Security Team Risk Assessment Compliance Report Advancement Client Computing and Server Admins Security roles & Resource scoping Best Practices in Patch Management Remediation Strategy Change Management Team 16
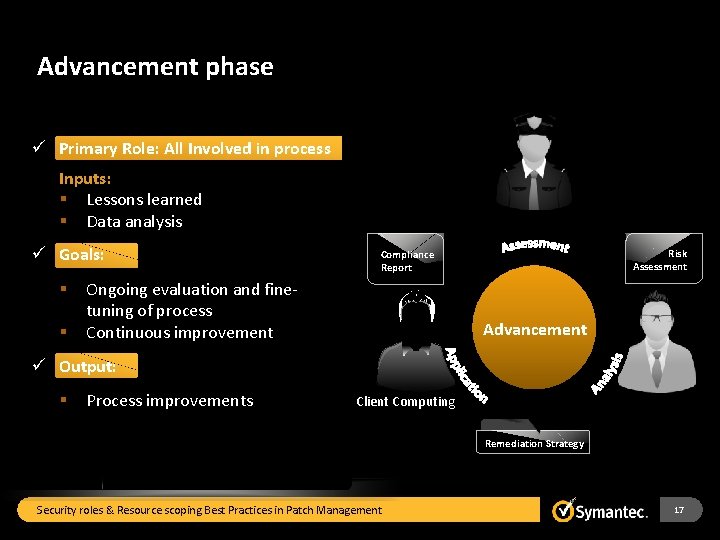
Advancement phase ü Primary Role: All Involved in process Inputs: § Lessons learned § Data analysis ü Goals: § § Security Team Risk Assessment Compliance Report Ongoing evaluation and finetuning of process Continuous improvement Advancement ü Output: § Process improvements Client Computing and Server Admins Security roles & Resource scoping Best Practices in Patch Management Remediation Strategy Change Management Team 17
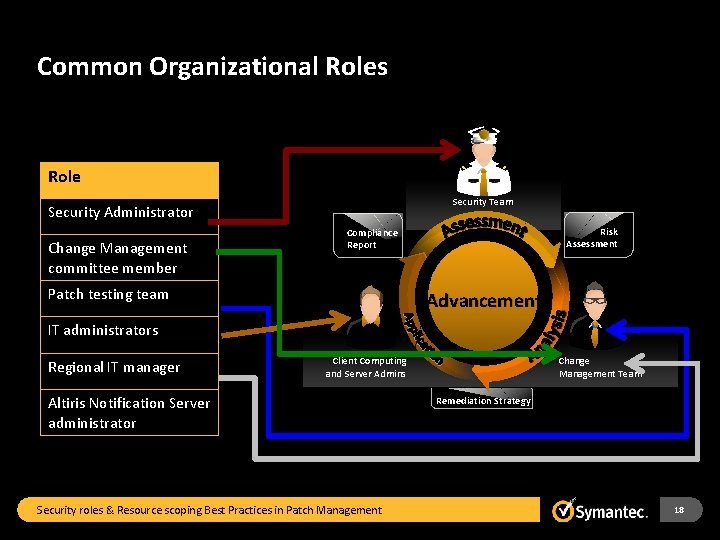
Common Organizational Roles Role Security Team Security Administrator Change Management committee member Risk Assessment Compliance Report Patch testing team Advancement IT administrators Regional IT manager Client Computing and Server Admins Altiris Notification Server administrator Security roles & Resource scoping Best Practices in Patch Management Change Management Team Remediation Strategy 18
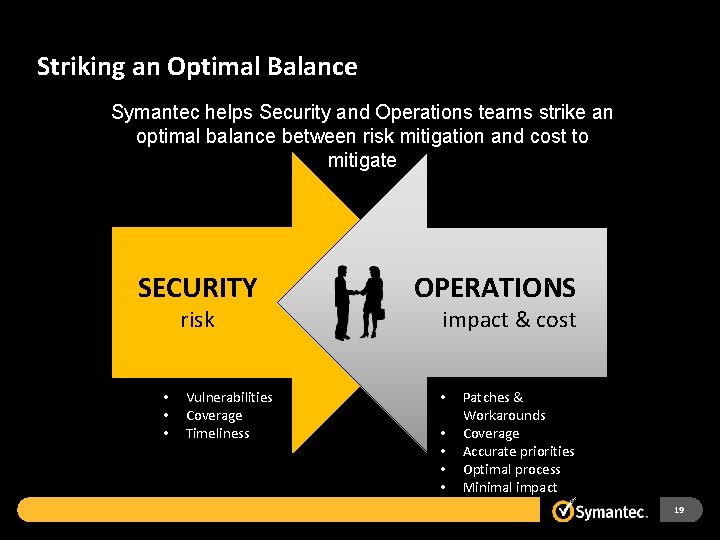
Striking an Optimal Balance Symantec helps Security and Operations teams strike an optimal balance between risk mitigation and cost to mitigate SECURITY risk • • • Vulnerabilities Coverage Timeliness OPERATIONS impact & cost • • • Patches & Workarounds Coverage Accurate priorities Optimal process Minimal impact 19
Security Roles Organization options 1. Out of the box (1 person managing everything) • Symantec Administrator 2. Use existing roles (Existing Roles Match Org) • Patch Management administrator • Patch management rollout 3. Clone/create add or limit access/privileges(Create Roles to Match Org) • Security Officer team • Change management team • Client computing and Server admins team 4. Other options? • Other Alternatives and approaches? Presentation Identifier Goes Here 20
Security Options in SMP 1. Account Management • This is where you create/clone/delete Roles 2. Security Manager • This where we grant access to view • We grant privileges 3. Console Custom Views-(Organization specific) • Security Officer team • Change management team • Client computing and Server admins team Presentation Identifier Goes Here 21
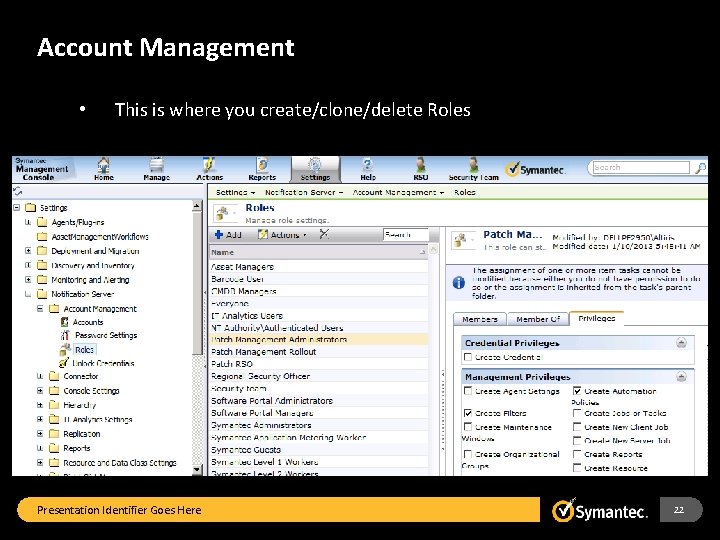
Account Management • This is where you create/clone/delete Roles Presentation Identifier Goes Here 22
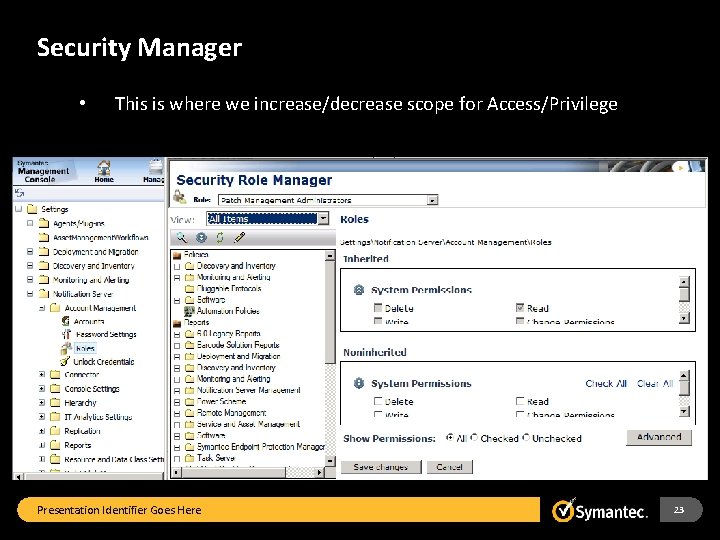
Security Manager • This is where we increase/decrease scope for Access/Privilege Presentation Identifier Goes Here 23
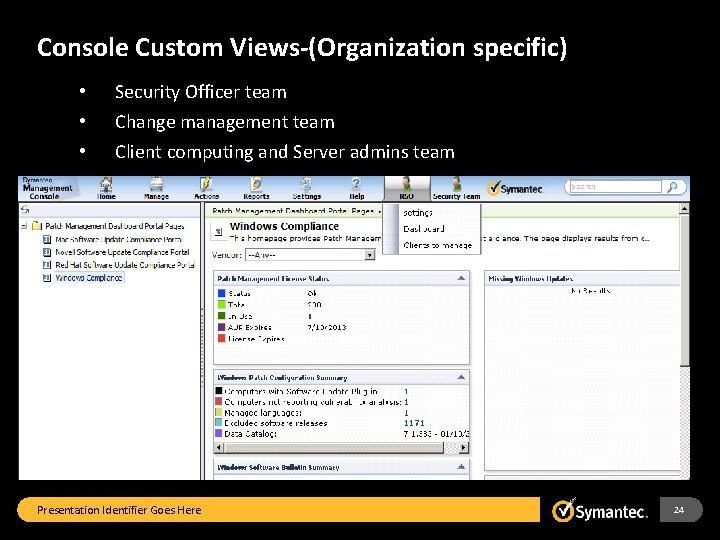
Console Custom Views-(Organization specific) • • • Security Officer team Change management team Client computing and Server admins team Presentation Identifier Goes Here 24
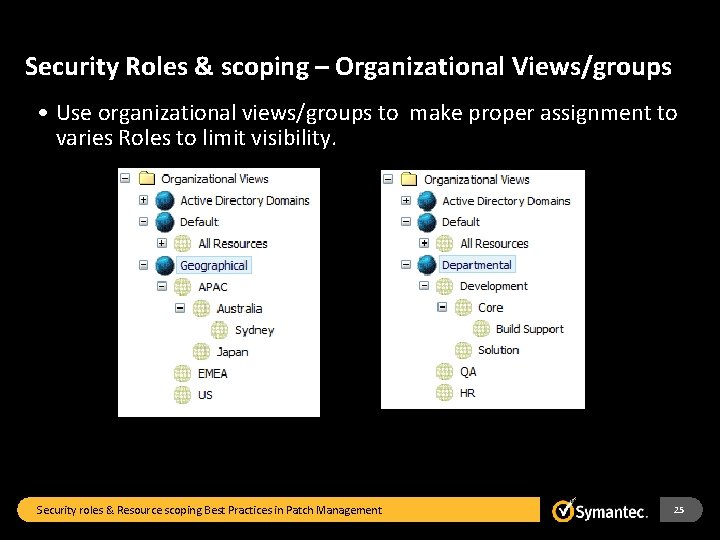
Security Roles & scoping – Organizational Views/groups • Use organizational views/groups to make proper assignment to varies Roles to limit visibility. Security roles & Resource scoping Best Practices in Patch Management 25
Demo Presentation Identifier Goes Here 26
Steps to create a Security role based Menu • Create user(local for test) • Add user to the console and turn it on • Clone/create the security role • Assign the user to that role • Create the Console Menu • Give access to the new Role Menu and limit access to others(Menu item on the console such settings, actions, manage etc. ) Presentation Identifier Goes Here 27
SUMMARY ü Patch Management ? ü Common Terms & Key areas ü 4 A Model - Best practices approach ü Security Roles & scoping ü Demo Security roles & Resource scoping Best Practices in Patch Management 28
Questions? Presentation Identifier Goes Here 29
- Slides: 27