
Security challenges in a networked world Theo Dimitrakos
- Slides: 8
Security challenges in a networked world Theo Dimitrakos Chief Security Researcher –Security Futures Practice, BT Research & Technology Professor of Computer Science – School of Computing, University of Kent Slide 1
Overview • Change factors • New security threats • Research challenges © British Telecommunications plc Slide 2
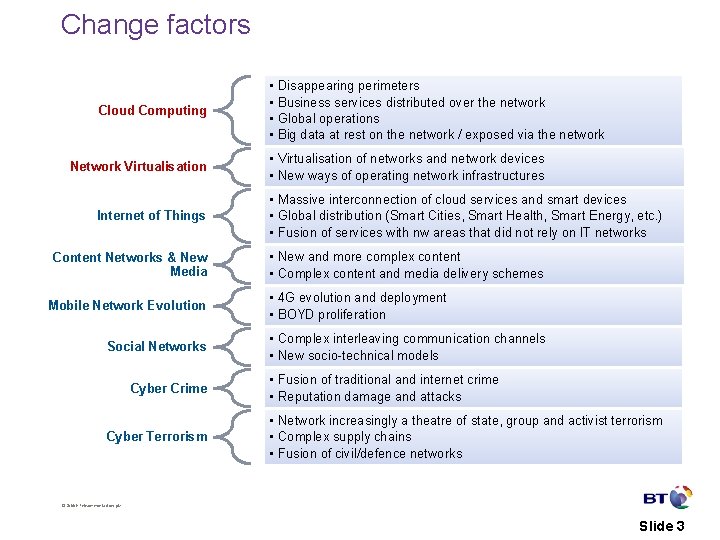
Change factors Cloud Computing Network Virtualisation Internet of Things Content Networks & New Media Mobile Network Evolution Social Networks Cyber Crime Cyber Terrorism • • Disappearing perimeters Business services distributed over the network Global operations Big data at rest on the network / exposed via the network • Virtualisation of networks and network devices • New ways of operating network infrastructures • Massive interconnection of cloud services and smart devices • Global distribution (Smart Cities, Smart Health, Smart Energy, etc. ) • Fusion of services with nw areas that did not rely on IT networks • New and more complex content • Complex content and media delivery schemes • 4 G evolution and deployment • BOYD proliferation • Complex interleaving communication channels • New socio-technical models • Fusion of traditional and internet crime • Reputation damage and attacks • Network increasingly a theatre of state, group and activist terrorism • Complex supply chains • Fusion of civil/defence networks © British Telecommunications plc Slide 3
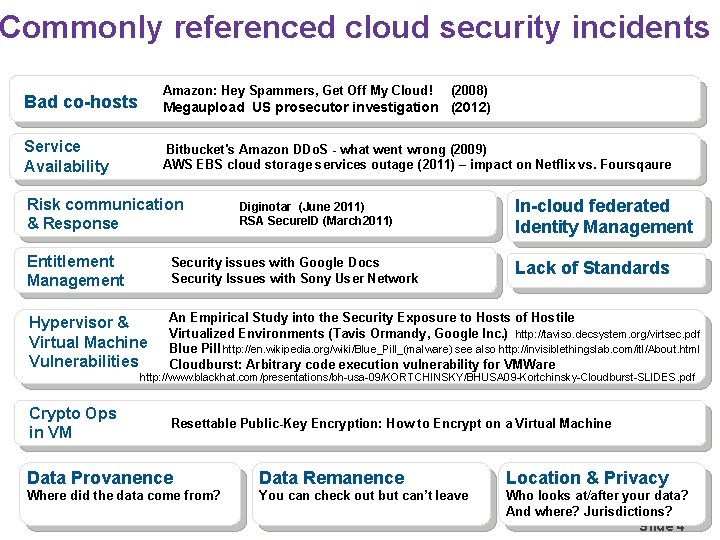
Commonly referenced cloud security incidents Amazon: Hey Spammers, Get Off My Cloud! Bad co-hosts (2008) Megaupload US prosecutor investigation (2012) Service Availability Bitbucket's Amazon DDo. S - what went wrong (2009) AWS EBS cloud storage services outage (2011) – impact on Netflix vs. Foursqaure Risk communication & Response Diginotar (June 2011) RSA Secure. ID (March 2011) In-cloud federated Identity Management Entitlement Management Security issues with Google Docs Security Issues with Sony User Network Hypervisor & Virtual Machine Vulnerabilities An Empirical Study into the Security Exposure to Hosts of Hostile Virtualized Environments (Tavis Ormandy, Google Inc. ) http: //taviso. decsystem. org/virtsec. pdf Blue Pill http: //en. wikipedia. org/wiki/Blue_Pill_(malware) see also http: //invisiblethingslab. com/itl/About. html Cloudburst: Arbitrary code execution vulnerability for VMWare Lack of Standards http: //www. blackhat. com/presentations/bh-usa-09/KORTCHINSKY/BHUSA 09 -Kortchinsky-Cloudburst-SLIDES. pdf Crypto Ops in VM Resettable Public-Key Encryption: How to Encrypt on a Virtual Machine Data Provanence Data Remanence Location & Privacy Where did the data come from? You can check out but can’t leave Who looks at/after your data? And where? Jurisdictions? © British Telecommunications plc Slide 4
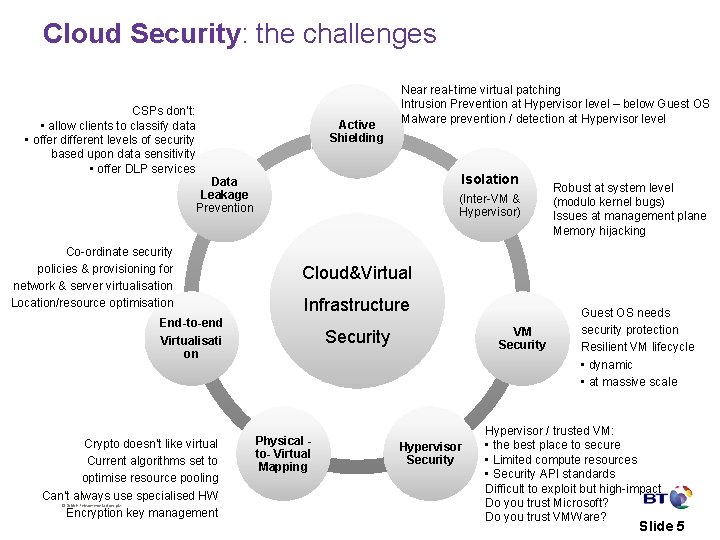
Cloud Security: the challenges CSPs don’t: • allow clients to classify data • offer different levels of security based upon data sensitivity • offer DLP services Active Shielding Near real-time virtual patching Intrusion Prevention at Hypervisor level – below Guest OS Malware prevention / detection at Hypervisor level Isolation Data Leakage Prevention Co-ordinate security policies & provisioning for network & server virtualisation Location/resource optimisation (Inter-VM & Hypervisor) Cloud&Virtual Infrastructure End-to-end VM Security Virtualisati on Crypto doesn’t like virtual Current algorithms set to optimise resource pooling Can’t always use specialised HW © British Telecommunications plc Encryption key management Robust at system level (modulo kernel bugs) Issues at management plane Memory hijacking Physical to- Virtual Mapping Hypervisor Security Guest OS needs security protection Resilient VM lifecycle • dynamic • at massive scale Hypervisor / trusted VM: • the best place to secure • Limited compute resources • Security API standards Difficult to exploit but high-impact Do you trust Microsoft? Do you trust VMWare? Slide 5
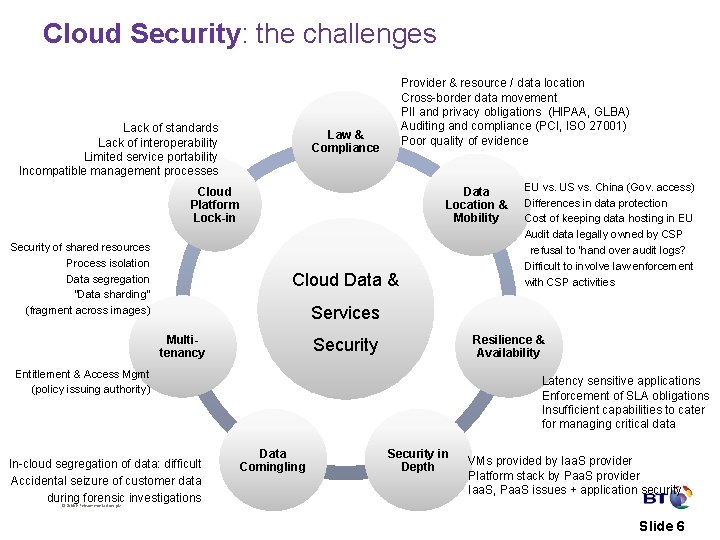
Cloud Security: the challenges Lack of standards Lack of interoperability Limited service portability Incompatible management processes Provider & resource / data location Cross-border data movement PII and privacy obligations (HIPAA, GLBA) Auditing and compliance (PCI, ISO 27001) Poor quality of evidence Law & Compliance Cloud Platform Lock-in Security of shared resources Process isolation Data segregation “Data sharding” (fragment across images) Data Location & Mobility Cloud Data & EU vs. US vs. China (Gov. access) Differences in data protection Cost of keeping data hosting in EU Audit data legally owned by CSP refusal to ‘hand over audit logs? Difficult to involve law enforcement with CSP activities Services Multitenancy Resilience & Availability Security Entitlement & Access Mgmt (policy issuing authority) In-cloud segregation of data: difficult Accidental seizure of customer data during forensic investigations © British Telecommunications plc Latency sensitive applications Enforcement of SLA obligations Insufficient capabilities to cater for managing critical data Data Comingling Security in Depth VMs provided by Iaa. S provider Platform stack by Paa. S provider Iaa. S, Paa. S issues + application security Slide 6
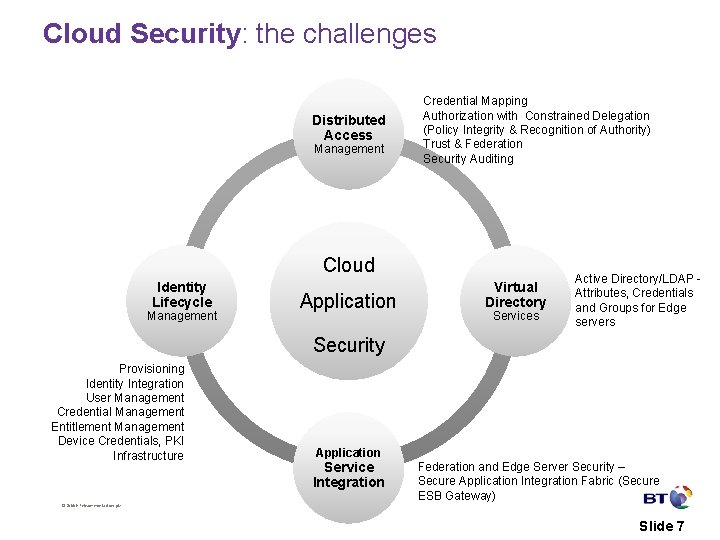
Cloud Security: the challenges Distributed Access Management Credential Mapping Authorization with Constrained Delegation (Policy Integrity & Recognition of Authority) Trust & Federation Security Auditing Cloud Identity Lifecycle Management Application Virtual Directory Services Active Directory/LDAP Attributes, Credentials and Groups for Edge servers Security Provisioning Identity Integration User Management Credential Management Entitlement Management Device Credentials, PKI Infrastructure Application Service Integration Federation and Edge Server Security – Secure Application Integration Fabric (Secure ESB Gateway) © British Telecommunications plc Slide 7
Questions For more information please contact: theo. dimitrakos@bt. com theo. dimitrakos@ifiptm. org © British Telecommunications plc Slide 8