
Securing Browser Frame Navigation and Communication Adam Barth
Securing Browser Frame Navigation and Communication Adam Barth Collin Jackson John C. Mitchell Stanford University
Outline • Frame Isolation – Improving the frame navigation policy • Frame Communication – Fragment identifier messaging + authentication – post. Message + confidentiality

Part I: FRAME ISOLATION
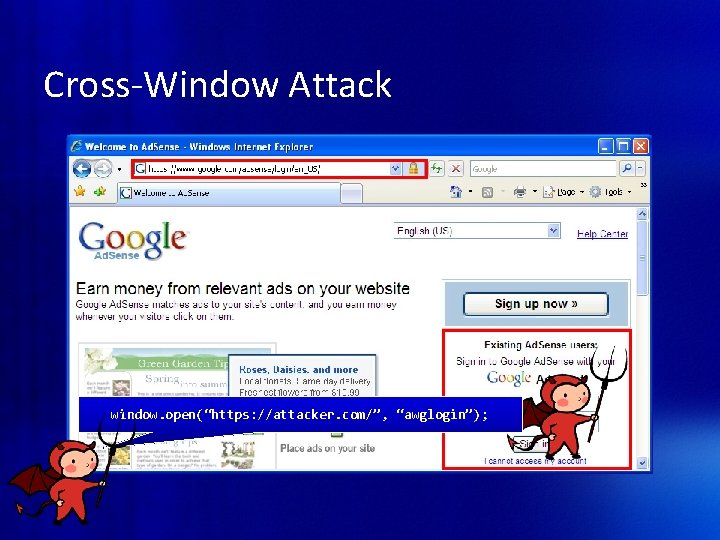
Cross-Window Attack window. open(“https: //attacker. com/”, “awglogin”);
Experiment to Determine Policy • Frame navigation policy not documented – Some comments in Firefox source code, but misleading – No source code available for IE or Opera • “Uber” frame navigation test case – Assumes policy invariants (e. g. , left/right symmetric) – Attempts 176 navigations, records results – Extracted policy for Internet Explorer, Firefox, and Safari
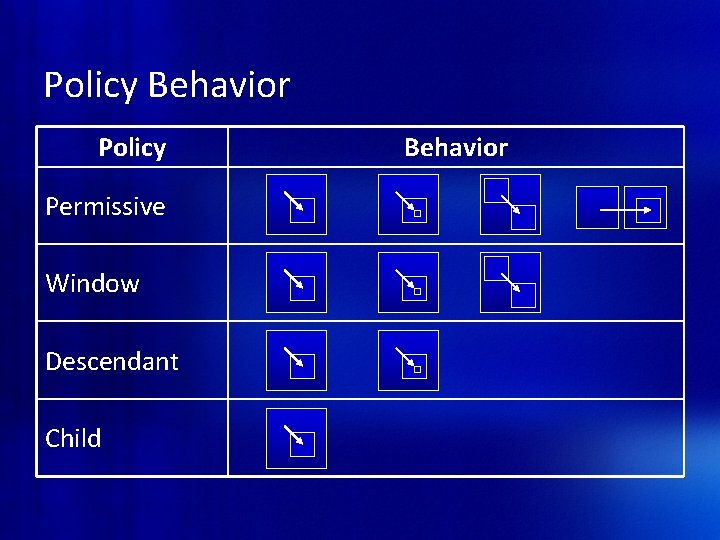
Policy Behavior Policy Permissive Window Descendant Child Behavior
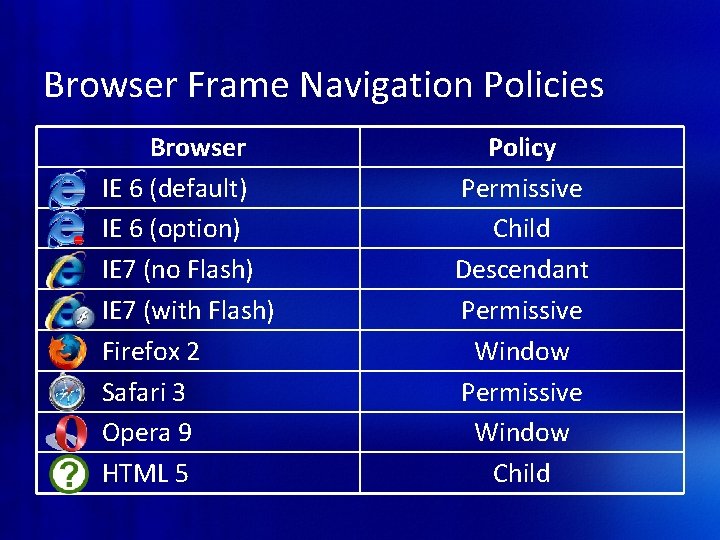
Browser Frame Navigation Policies Browser IE 6 (default) IE 6 (option) IE 7 (no Flash) IE 7 (with Flash) Firefox 2 Safari 3 Opera 9 HTML 5 Policy Permissive Child Descendant Permissive Window Child
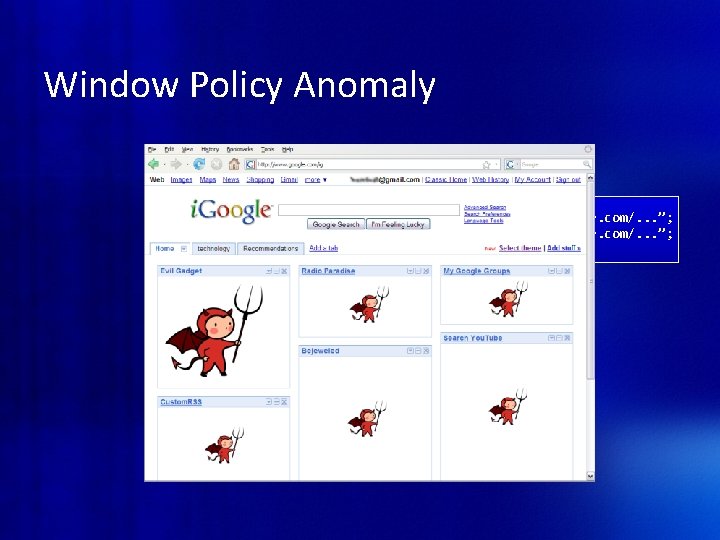
Window Policy Anomaly top. frames[1]. location = “http: //www. attacker. com/. . . ”; top. frames[2]. location = “http: //www. attacker. com/. . . ”; . . .
Principle: Pixel Delegation • Frames delegate screen pixels – Child cannot draw outside its frame – Parent can draw over the child’s pixels • Navigation similar to drawing – Navigation replaces frame contents – “Simulate” by drawing over frame • Policy ought to match pixel delegation – Navigate a frame if can draw over the frame
Solution: Descendant Policy • Best security / compatiblity trade-off – Security: Respects pixel delegation – Compatibility: Least restrictive such policy • Implementation – Wrote patches for Firefox and Safari – Wrote over 1000 lines of regression tests • Deployment – Apple released patch as security update – Mozilla will ship policy in Firefox 3
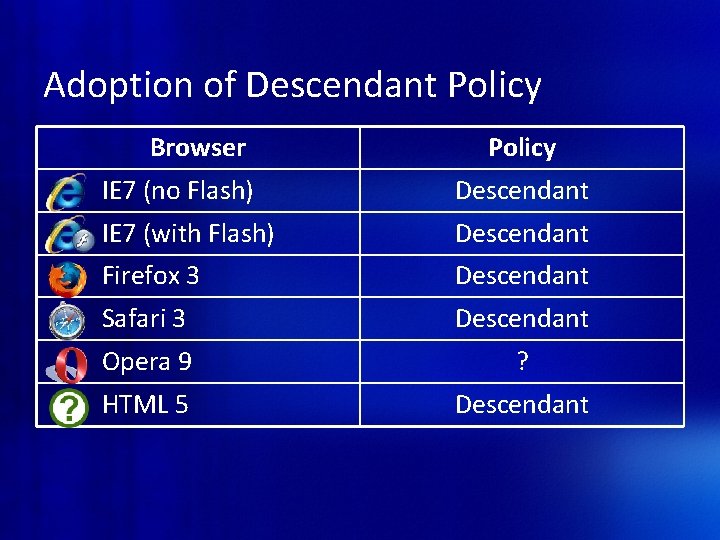
Adoption of Descendant Policy Browser Policy IE 7 (no Flash) Descendant IE 7 (with Flash) Descendant Firefox 3 Descendant Safari 3 Descendant Opera 9 ? HTML 5 Descendant
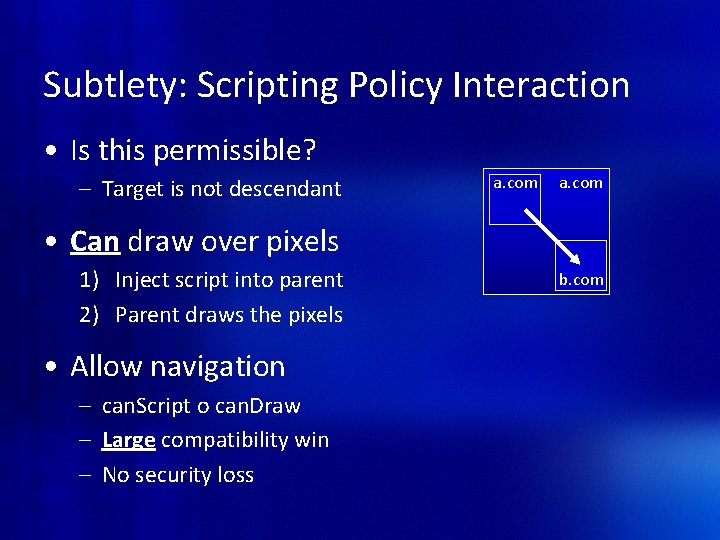
Subtlety: Scripting Policy Interaction • Is this permissible? – Target is not descendant a. com • Can draw over pixels 1) Inject script into parent 2) Parent draws the pixels • Allow navigation – can. Script o can. Draw – Large compatibility win – No security loss b. com
Part II: FRAME COMMUNICATION
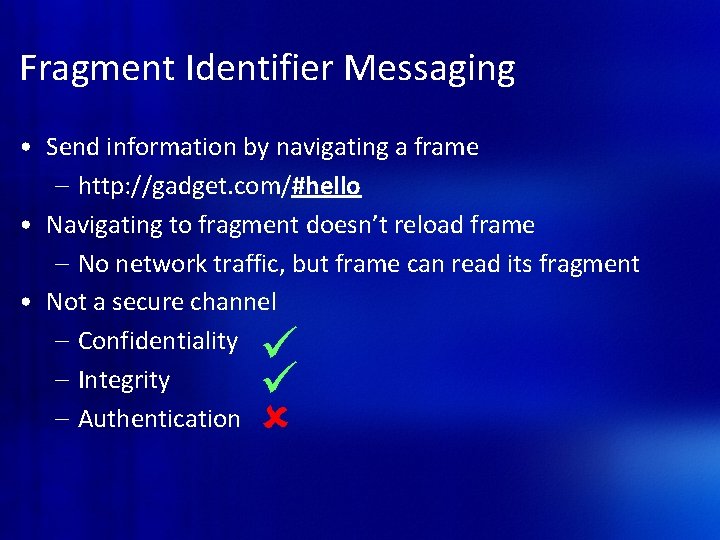
Fragment Identifier Messaging • Send information by navigating a frame – http: //gadget. com/#hello • Navigating to fragment doesn’t reload frame – No network traffic, but frame can read its fragment • Not a secure channel – Confidentiality – Integrity – Authentication
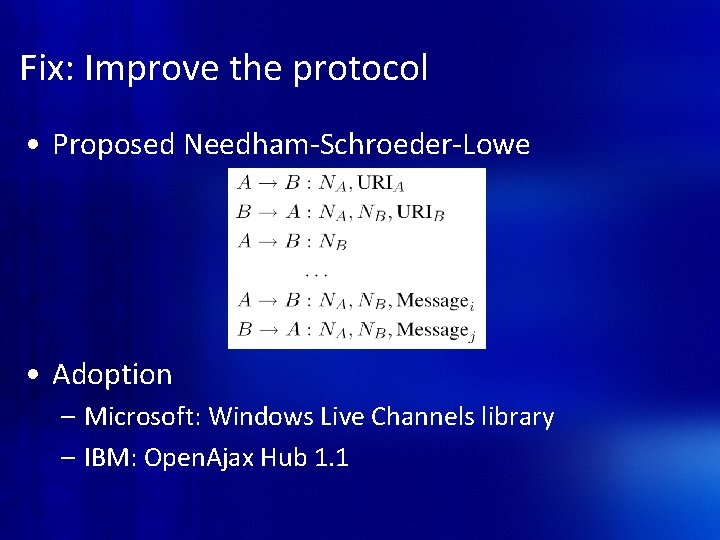
Fix: Improve the protocol • Proposed Needham-Schroeder-Lowe • Adoption – Microsoft: Windows Live Channels library – IBM: Open. Ajax Hub 1. 1
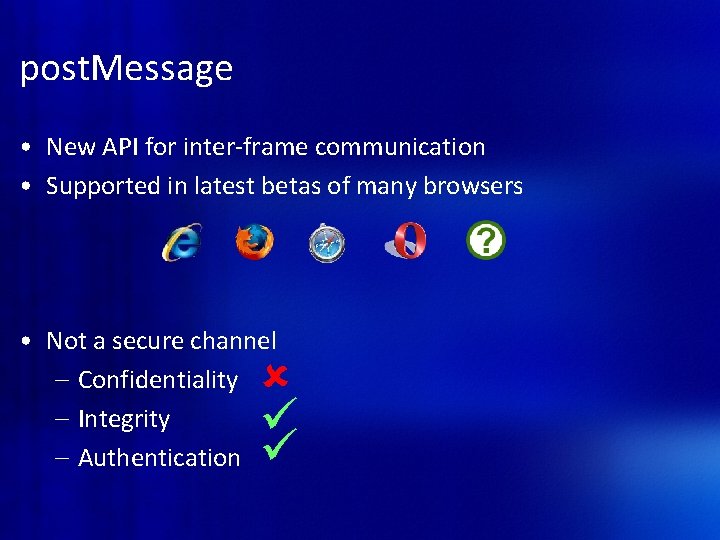
post. Message • New API for inter-frame communication • Supported in latest betas of many browsers • Not a secure channel – Confidentiality – Integrity – Authentication
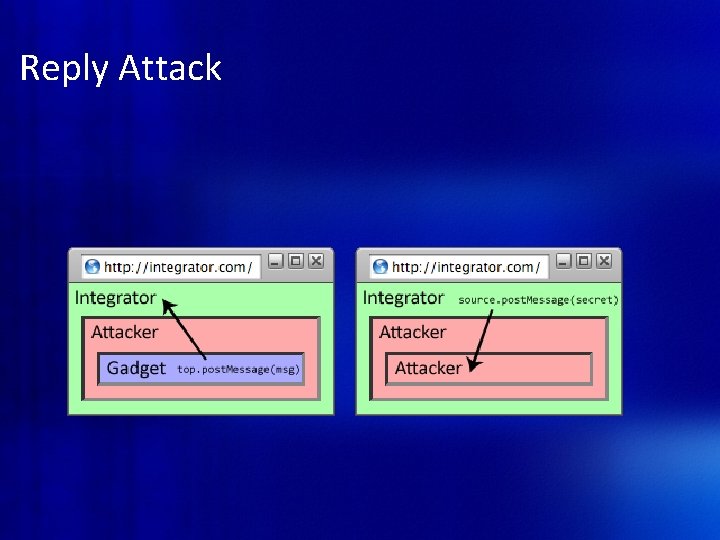
Reply Attack
Fix: Improve the API • Let the sending specify the recipient frame[0]. post. Message("Hello", "http: //gadget. com") – Can use "*" if confidentiality not required • Adoption – Firefox 3 – Internet Explorer 8 – Safari 3. 1
Summary • All proposals deployed to real users • Frame isolation – Improved frame navigation policy • Fixed Guninski and Gadget Hijacking – Drive-by-downloads still a concern… • Frame communication – Secured fragment identifier messaging – Secured new post. Message API
- Slides: 19