
Secure Sharding in Federated Clouds By Anam Zahid
Secure Sharding in Federated Clouds By: Anam Zahid, MS(IT)-13 [NUST 201260763 MSEECS 60012 F] Supervisor: Dr Awais Shibli
Agenda • • Introduction Industrial Motivation Literature Review Problem Statement Proposed Architecture Tools and Technologies Timeline References 2
No. SQL Database • • • Open source Flexible Data model High Scalability and Performance Handles Large volumes of unstructured data Best suitable for Cloud Integrated Caching 3
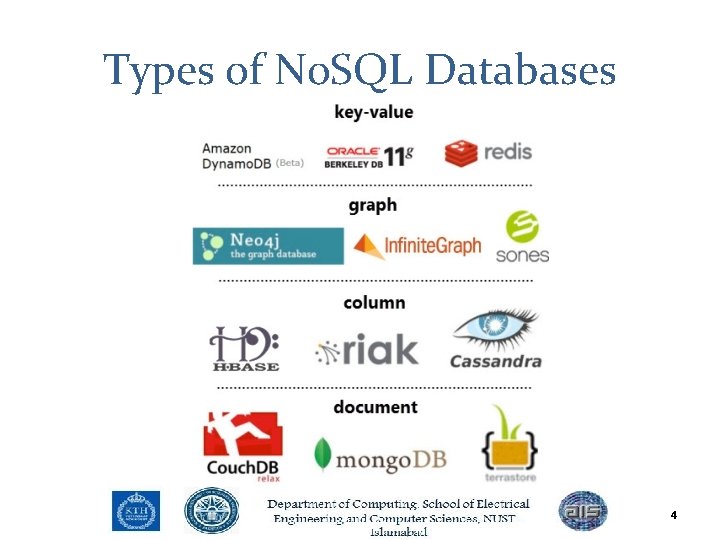
Types of No. SQL Databases 4
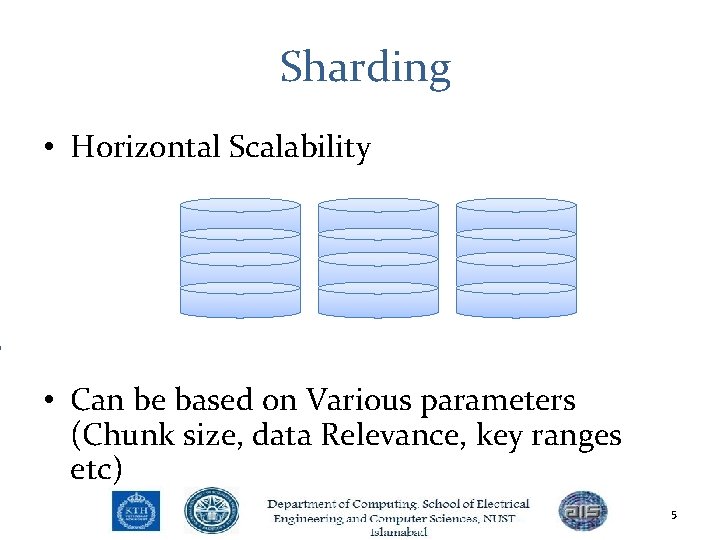
Sharding • Horizontal Scalability • Can be based on Various parameters (Chunk size, data Relevance, key ranges etc) 5
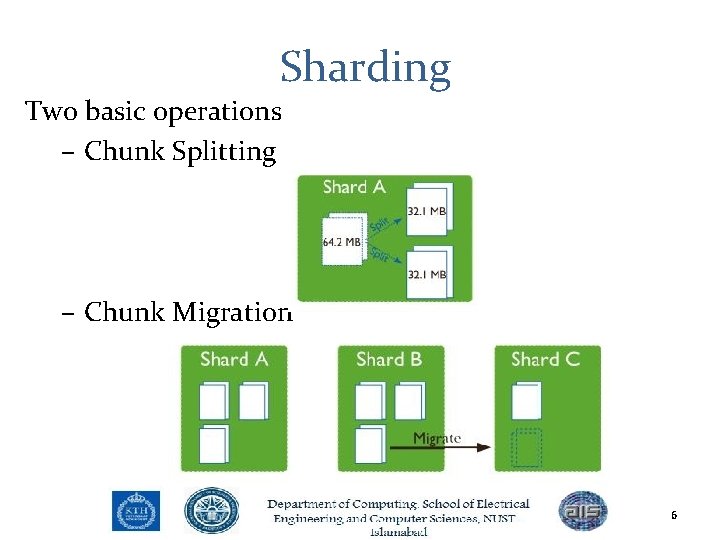
Sharding Two basic operations – Chunk Splitting – Chunk Migration 6
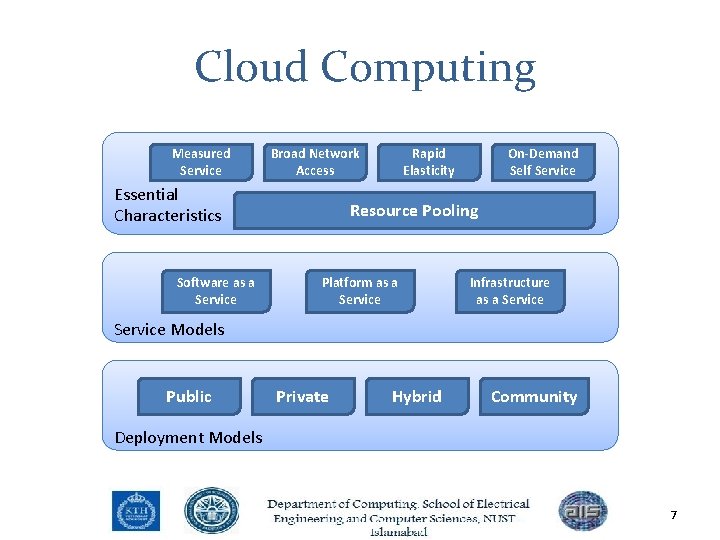
Cloud Computing Measured Service Broad Network Access Essential Characteristics Software as a Service Rapid Elasticity On-Demand Self Service Resource Pooling Platform as a Service Infrastructure as a Service Models Public Private Hybrid Community Deployment Models 7
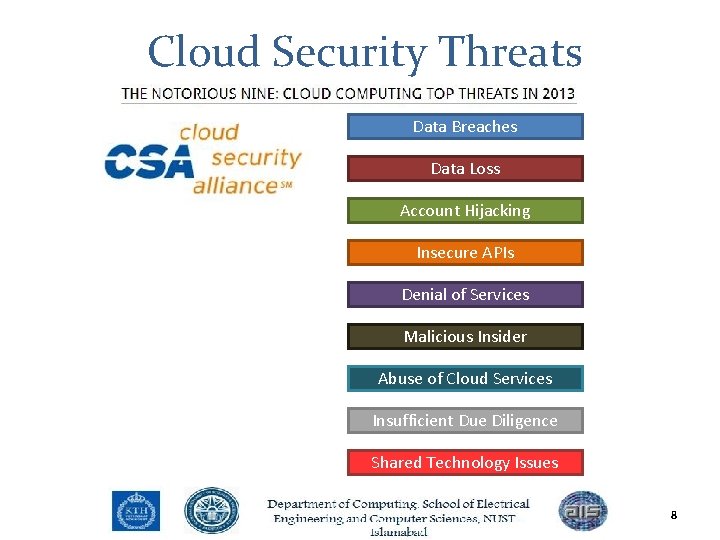
Cloud Security Threats Data Breaches Data Loss Account Hijacking Insecure APIs Denial of Services Malicious Insider Abuse of Cloud Services Insufficient Due Diligence Shared Technology Issues 8
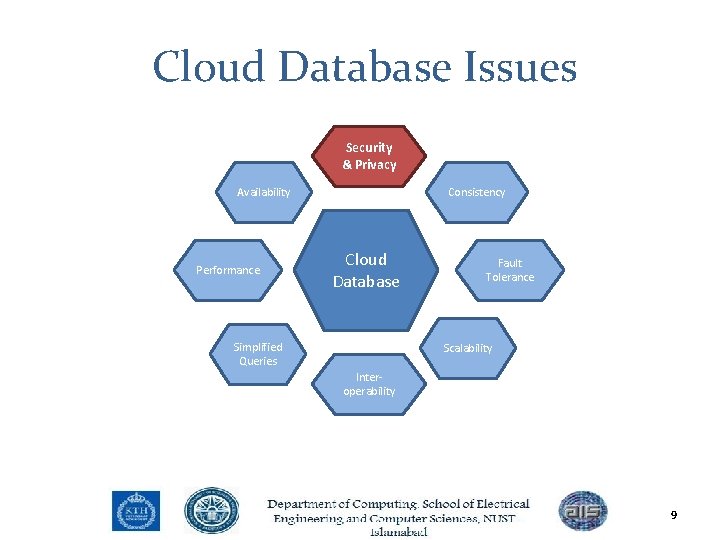
Cloud Database Issues Security & Privacy Availability Performance Consistency Cloud Database Simplified Queries Fault Tolerance Scalability Interoperability 9
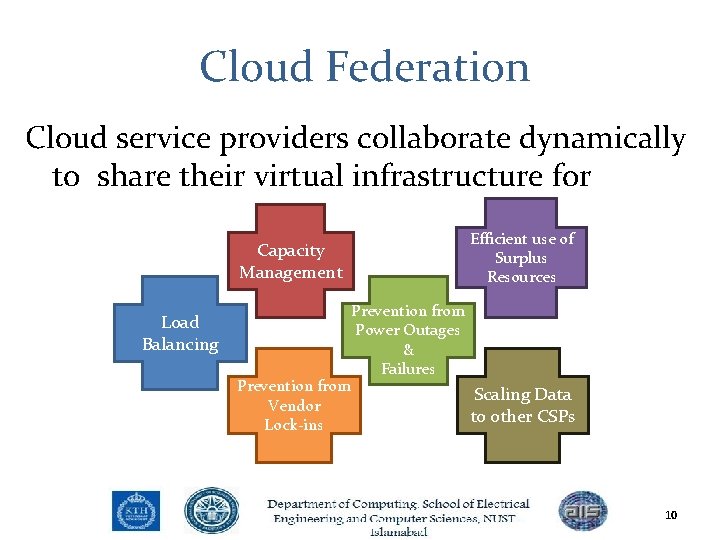
Cloud Federation Cloud service providers collaborate dynamically to share their virtual infrastructure for Efficient use of Surplus Resources Capacity Management Load Balancing Prevention from Vendor Lock-ins Prevention from Power Outages & Failures Scaling Data to other CSPs 10
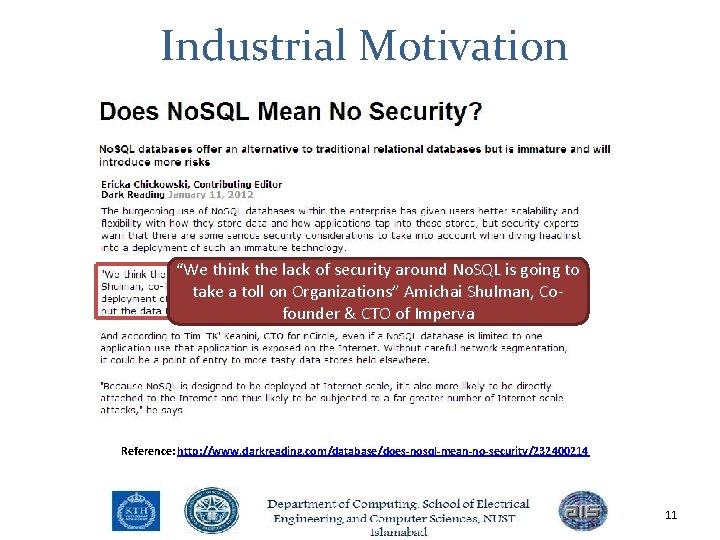
Industrial Motivation “We think the lack of security around No. SQL is going to take a toll on Organizations” Amichai Shulman, Cofounder & CTO of Imperva Reference: http: //www. darkreading. com/database/does-nosql-mean-no-security/232400214 11
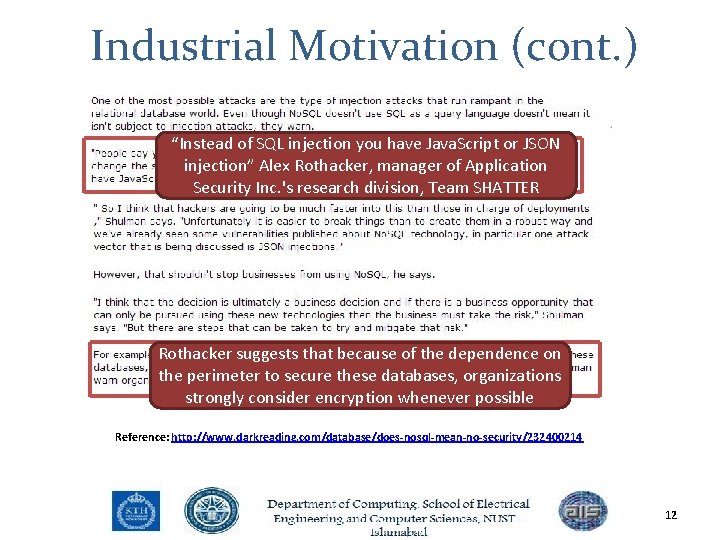
Industrial Motivation (cont. ) “Instead of SQL injection you have Java. Script or JSON injection” Alex Rothacker, manager of Application Security Inc. 's research division, Team SHATTER Rothacker suggests that because of the dependence on the perimeter to secure these databases, organizations strongly consider encryption whenever possible Reference: http: //www. darkreading. com/database/does-nosql-mean-no-security/232400214 12
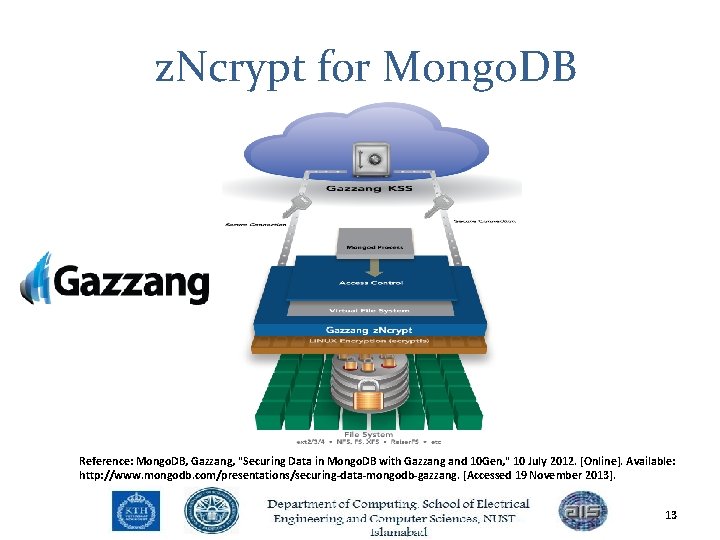
z. Ncrypt for Mongo. DB Reference: Mongo. DB, Gazzang, "Securing Data in Mongo. DB with Gazzang and 10 Gen, " 10 July 2012. [Online]. Available: http: //www. mongodb. com/presentations/securing-data-mongodb-gazzang. [Accessed 19 November 2013]. 13
Literature Review 14
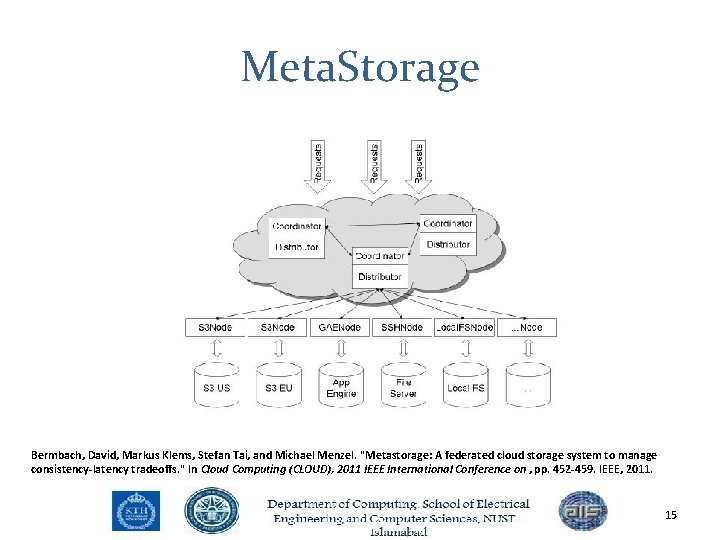
Meta. Storage Bermbach, David, Markus Klems, Stefan Tai, and Michael Menzel. "Metastorage: A federated cloud storage system to manage consistency-latency tradeoffs. " In Cloud Computing (CLOUD), 2011 IEEE International Conference on , pp. 452 -459. IEEE, 2011. 15
Meta. Storage Pros • • • Security maintained through role based user management Increased availability because of multiple storage providers Low latency due to data replication Cons • • No communication security TLS) or security of data at encryption) etc Additional overhead due processing layer Consistency issues due to cloud storage services No scalability limitations (e. g SSL, rest (e. g to data different Bermbach, David, Markus Klems, Stefan Tai, and Michael Menzel. "Metastorage: A federated cloud storage system to manage consistency-latency tradeoffs. " In Cloud Computing (CLOUD), 2011 IEEE International Conference on , pp. 452 -459. IEEE, 2011. 16
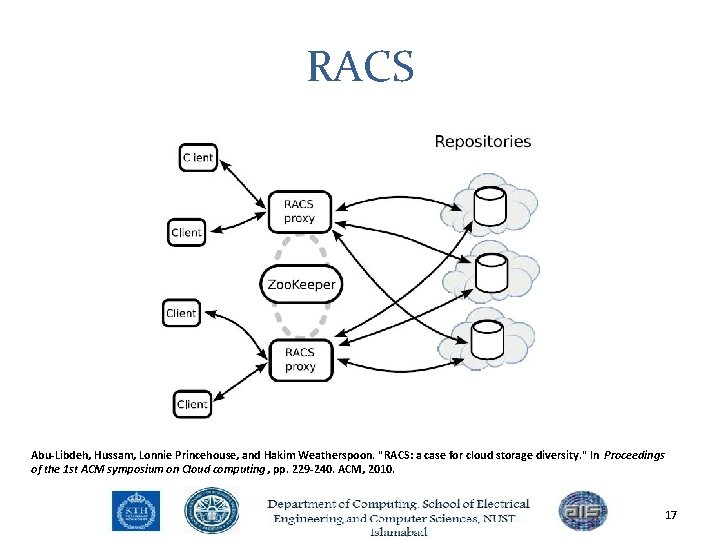
RACS Abu-Libdeh, Hussam, Lonnie Princehouse, and Hakim Weatherspoon. "RACS: a case for cloud storage diversity. " In Proceedings of the 1 st ACM symposium on Cloud computing , pp. 229 -240. ACM, 2010. 17
RACS Pros • • • Each RACS proxy maintains user authentication information and credentials for each repository Use redundancy through fragmentation for high availability Read synchronizations using zookeeper Cons • • • No communication as well as data at rest security High latency due to mutual consistency Data loss when RACS proxy crashes Abu-Libdeh, Hussam, Lonnie Princehouse, and Hakim Weatherspoon. "RACS: a case for cloud storage diversity. " In Proceedings of the 1 st ACM symposium on Cloud computing , pp. 229 -240. ACM, 2010. 18
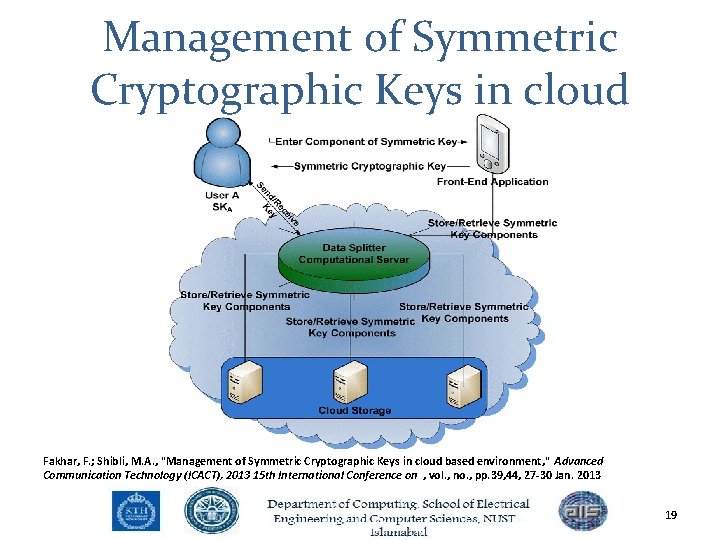
Management of Symmetric Cryptographic Keys in cloud Fakhar, F. ; Shibli, M. A. , "Management of Symmetric Cryptographic Keys in cloud based environment, " Advanced Communication Technology (ICACT), 2013 15 th International Conference on , vol. , no. , pp. 39, 44, 27 -30 Jan. 2013 19
Management of Symmetric Cryptographic Keys in cloud Pros • • • Distributed Key generation on client side Privacy maintained through client’s key component contribution in key regeneration. Recoverable key components except for client side component Cons • • Communication overhead when key to decrypt data is needed in cloud Key combiner on client terminal Fakhar, F. ; Shibli, M. A. , "Management of Symmetric Cryptographic Keys in cloud based environment, " Advanced Communication Technology (ICACT), 2013 15 th International Conference on , vol. , no. , pp. 39, 44, 27 -30 Jan. 2013 20
Summary So, besides providing high availability and throughput because of data fragmentation, there is a need for • strong client authentication and authorization mechanisms • Security of data during transmission (e. g. through TLS, SSL, IPSec etc) • Data-at-rest security (e. g. hashing, encryption etc) 21
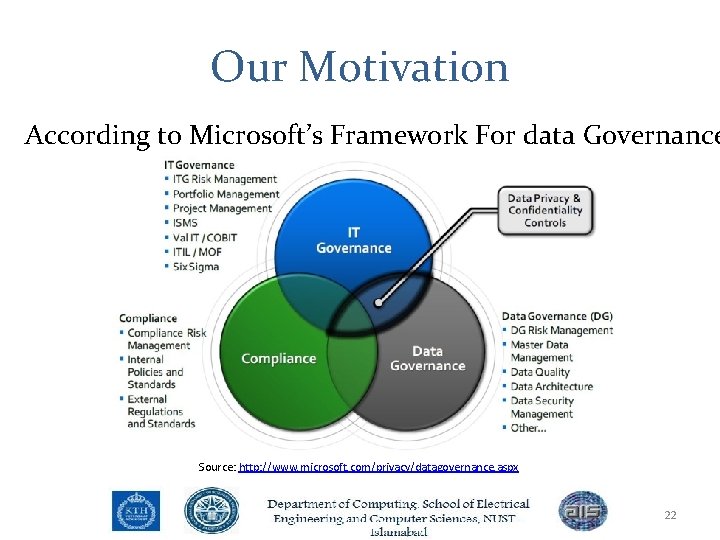
Our Motivation According to Microsoft’s Framework For data Governance Source: http: //www. microsoft. com/privacy/datagovernance. aspx 22
Our motivation Compliance Organizations rules and policies: 23
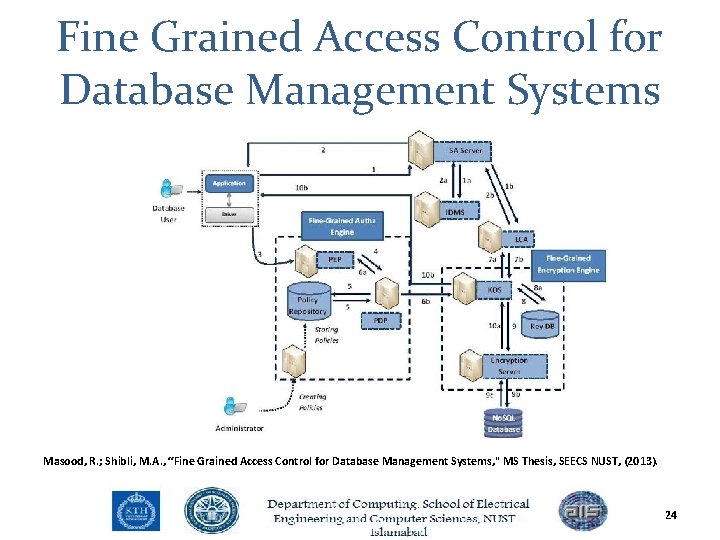
Fine Grained Access Control for Database Management Systems Masood, R. ; Shibli, M. A. , “Fine Grained Access Control for Database Management Systems, " MS Thesis, SEECS NUST, (2013). 24
Problem Statement In order to avoid the prevalent problem of data breaches in distributed cloud environment, there is a need to provide effective access control and encryption to ensure the security of data residing on the domain of various cloud providers. 25
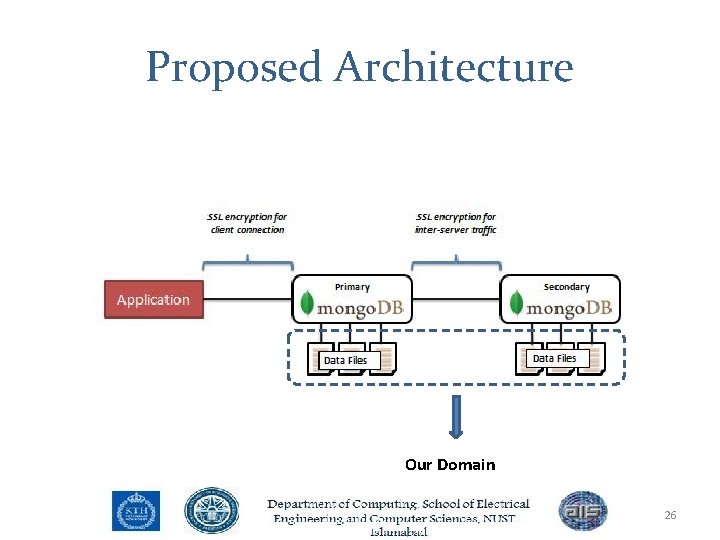
Proposed Architecture Our Domain 26
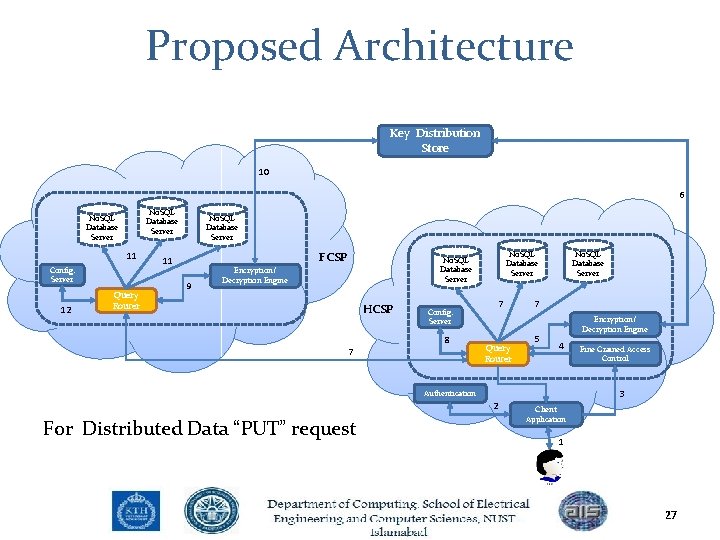
Proposed Architecture Key Distribution Store 10 6 No. SQL Database Server 11 Config. Server 12 Query Router No. SQL Database Server FCSP 11 9 No. SQL Database Server Encryption/ Decryption Engine HCSP 7 7 Config. Server 8 Query Router No. SQL Database Server 7 5 Encryption/ Decryption Engine 4 3 Authentication 2 For Distributed Data “PUT” request Fine Grained Access Control Client Application 1 27
Contribution In our proposed system, data security would be ensured by: • Client side Authentication • Embedded Fine grained authorization • Selective field Encryption of data chunks • Distribution of data across several service providers 28
Tools and Technologies • • Mongo. DB C++ (MS Visual Studio) Open Stack XACML 29
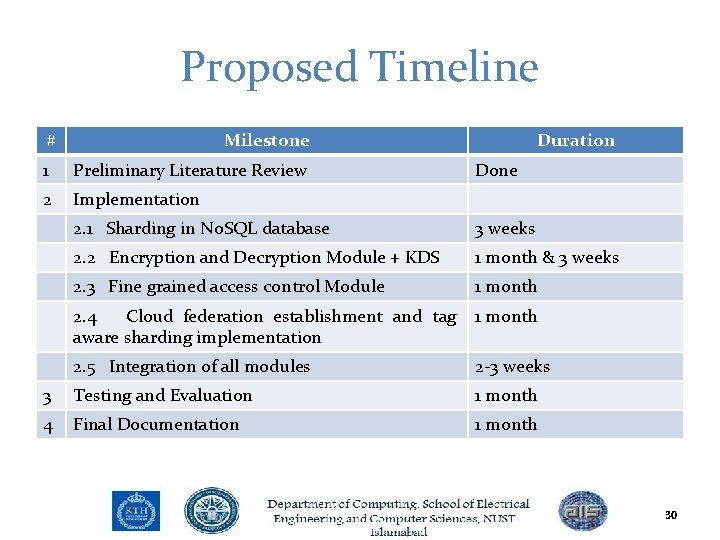
Proposed Timeline # Milestone 1 Preliminary Literature Review 2 Implementation Duration Done 2. 1 Sharding in No. SQL database 3 weeks 2. 2 Encryption and Decryption Module + KDS 1 month & 3 weeks 2. 3 Fine grained access control Module 1 month 2. 4 Cloud federation establishment and tag aware sharding implementation 1 month 2. 5 Integration of all modules 2 -3 weeks 3 Testing and Evaluation 1 month 4 Final Documentation 1 month 30
References [1] view of cloud computing. " Dept. Electrical Eng. and Comput. Sciences, University of California, Berkeley, Rep. UCB/EECS 28 (2009). [2] Arora, Indu, and Anu Gupta. "Cloud Databases: A Paradigm Shift in Databases. "International J. of Computer Science Issues 9, no. 4 (2012): 77 -83. [3] https: //downloads. cloudsecurityalliance. org/initiatives/top_threats/The_Notorious_Nine_Cloud_Computing_Top_Threats_in_2013. pdf ell, Peter, and Timothy Grance. "The NIST definition of cloud computing (draft). " NIST [4] special publication 800, 145 no. (2011): 7. [5] Mongo. DB, Gazzang, "Securing Data in Mongo. DB with Gazzang and 10 Gen, " 10 July 2012. [Online]. Available: http: //www. mongodb. com/presentations/securing-data-mongodb-gazzang. [Accessed 19 November 2013]. [6] http: //www. forbes. com/sites/benkepes/2013/11/04/was-garantia-is-now-redisdb-either-way-nosql-is-hot/ [7] http: //www. darkreading. com/database/does-nosql-mean-no-security/232400214 [8] Bermbach, David, Markus Klems, Stefan Tai, and Michael Menzel. "Metastorage: A federated cloud storage system to manage consistency-latency tradeoffs. " In Cloud Computing (CLOUD), 2011 IEEE International Conference on, pp. 452 -459. IEEE, 2011. [9] Abu-Libdeh, Hussam, Lonnie Princehouse, and Hakim Weatherspoon. "RACS: a case for cloud storage diversity. " In Proceedings of the 1 st ACM symposium on Cloud computing, pp. 229 -240. ACM, 2010. [10] Fakhar, F. ; Shibli, M. A. , "Management of Symmetric Cryptographic Keys in cloud based environment, " Advanced Communication Technology (ICACT), 2013 15 th International Conference on , vol. , no. , pp. 39, 44, 27 -30 Jan. 2013 [11] computing. " Journal of Internet Services and Applications 4, no. 1 (2013): 1 -13. [12] Chandra, Deka Ganesh, Ravi Prakash, and Swati Lamdharia. "A Study on Cloud Database. " In Computational Intelligence and Communication Networks (CICN), 2012 Fourth International Conference on, pp. 513 -519. IEEE, 2012. [13] Subashini, S. , and V. Kavitha. "A survey on security issues in service delivery models of cloud computing. " Journal of Network and Computer Applications 34, no. 1 (2011): 1 -11. 31
THANK YOU !!!! 32
- Slides: 32