
q Nessus q q q Computer Center National
- Slides: 38
大綱 q. Nessus介紹 q報表分析 q風險評分標準及相關資料庫 q案例 Computer Center, National Central University.
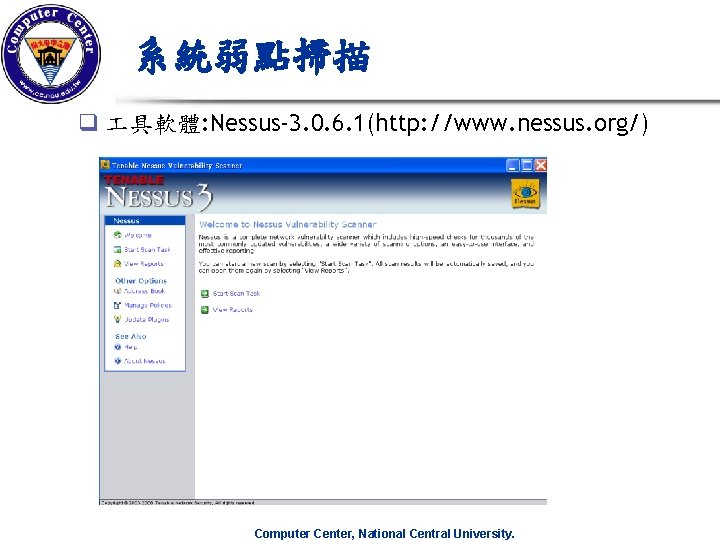
系統弱點掃描 q 具軟體: Nessus-3. 0. 6. 1(http: //www. nessus. org/) Computer Center, National Central University.
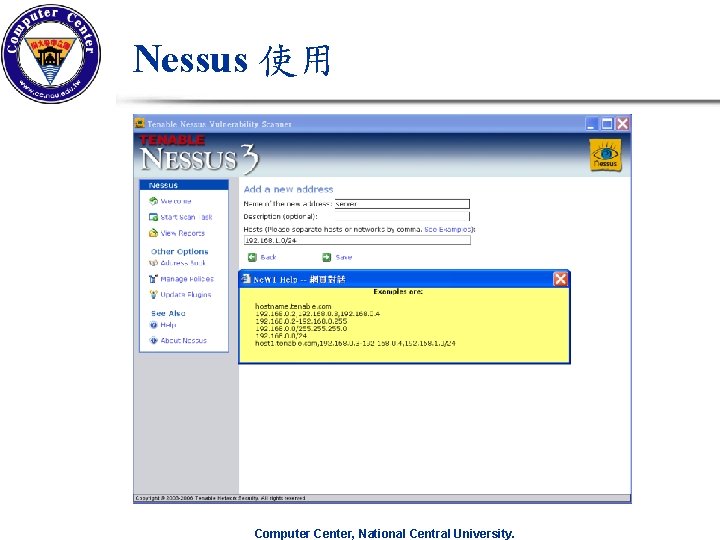
Nessus 使用 Computer Center, National Central University.
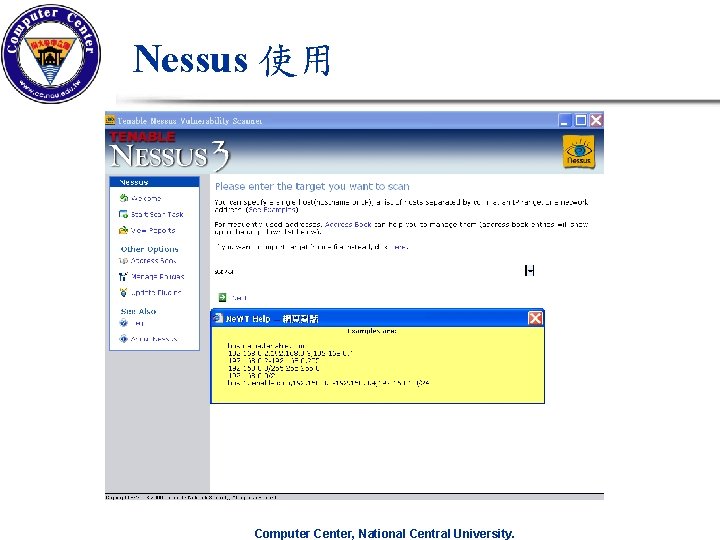
Nessus 使用 Computer Center, National Central University.
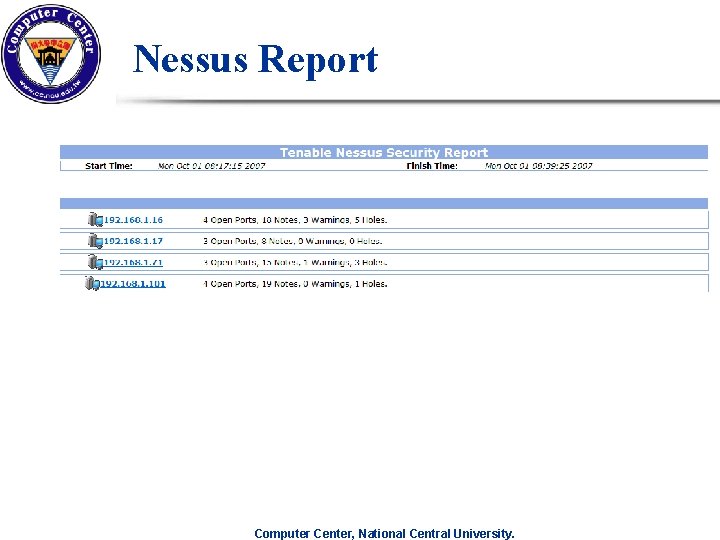
Nessus Report Computer Center, National Central University.
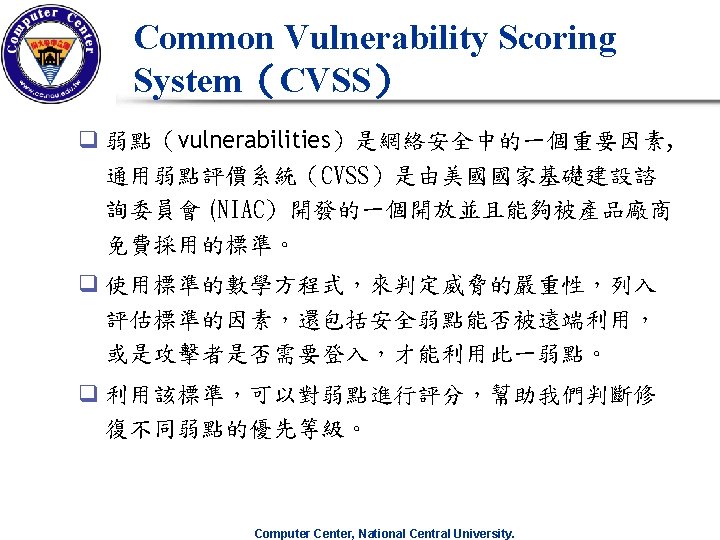
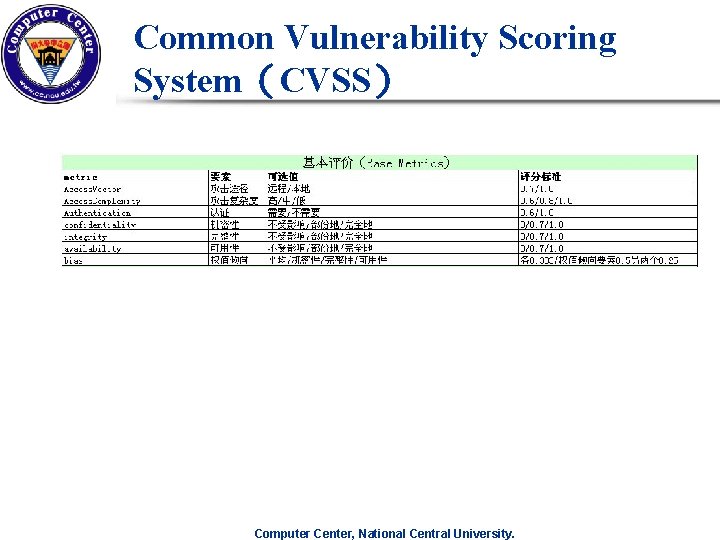
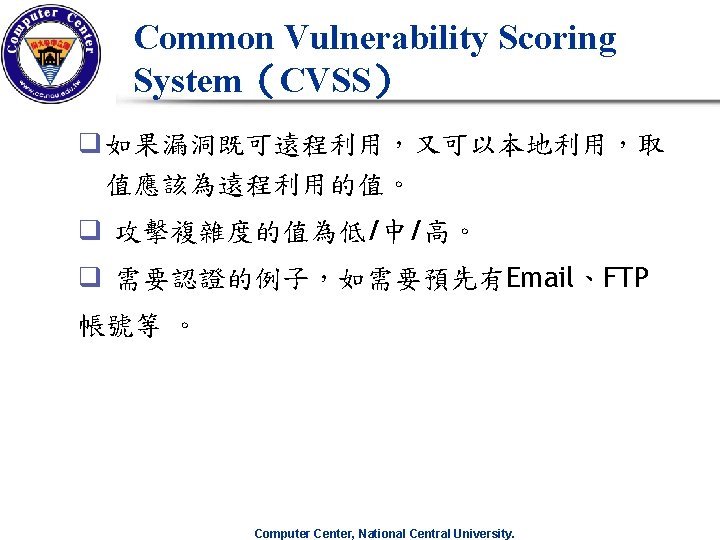
Common Vulnerability Scoring System(CVSS) Computer Center, National Central University.
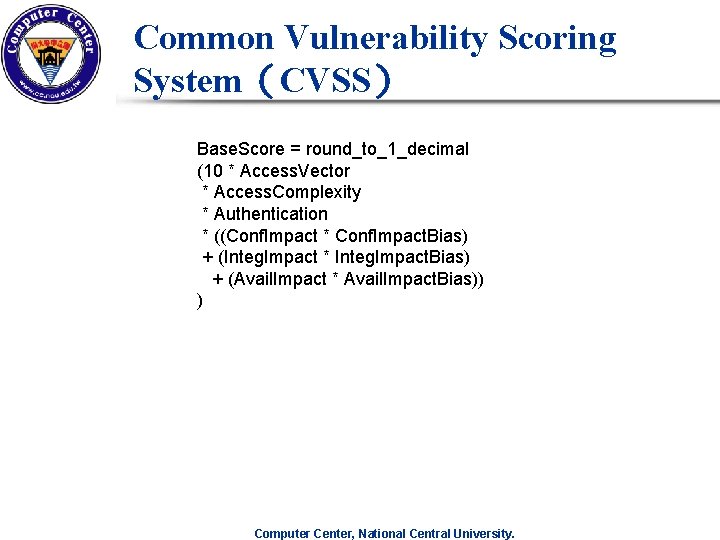
Common Vulnerability Scoring System(CVSS) Base. Score = round_to_1_decimal (10 * Access. Vector * Access. Complexity * Authentication * ((Conf. Impact * Conf. Impact. Bias) + (Integ. Impact * Integ. Impact. Bias) + (Avail. Impact * Avail. Impact. Bias)) ) Computer Center, National Central University.
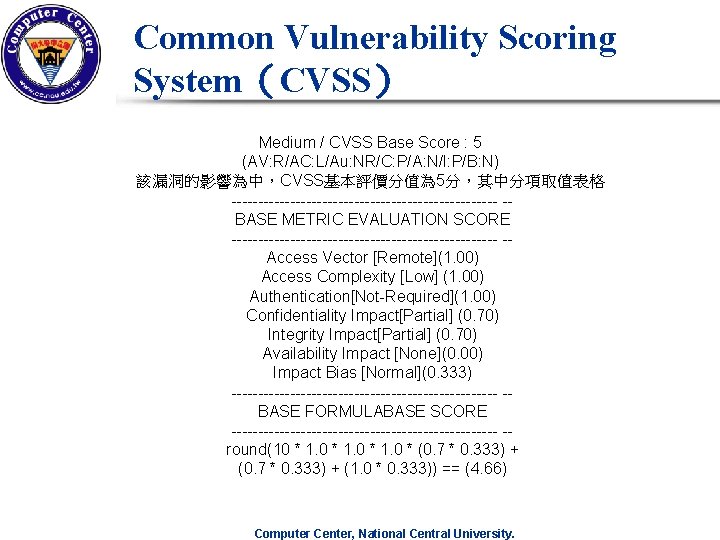
Common Vulnerability Scoring System(CVSS) Medium / CVSS Base Score : 5 (AV: R/AC: L/Au: NR/C: P/A: N/I: P/B: N) 該漏洞的影響為中,CVSS基本評價分值為 5分,其中分項取值表格 ------------------------- -BASE METRIC EVALUATION SCORE ------------------------- -Access Vector [Remote](1. 00) Access Complexity [Low] (1. 00) Authentication[Not-Required](1. 00) Confidentiality Impact[Partial] (0. 70) Integrity Impact[Partial] (0. 70) Availability Impact [None](0. 00) Impact Bias [Normal](0. 333) ------------------------- -BASE FORMULABASE SCORE ------------------------- -round(10 * 1. 0 * (0. 7 * 0. 333) + (1. 0 * 0. 333)) == (4. 66) Computer Center, National Central University.
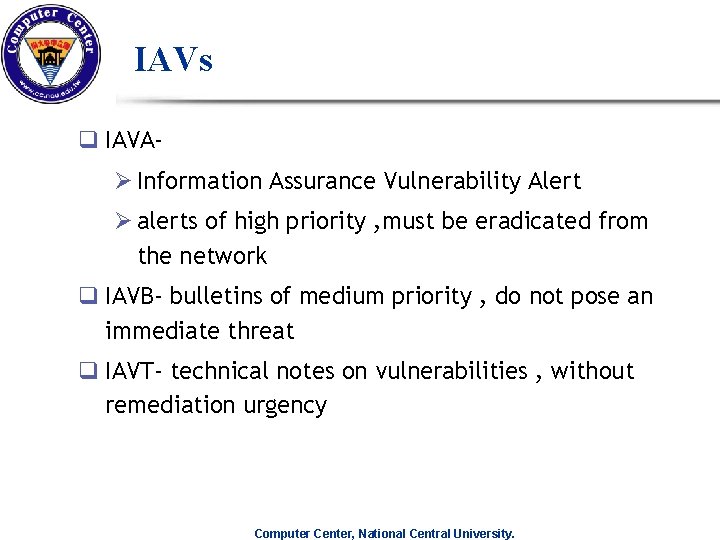
IAVs q IAVAØ Information Assurance Vulnerability Alert Ø alerts of high priority , must be eradicated from the network q IAVB- bulletins of medium priority , do not pose an immediate threat q IAVT- technical notes on vulnerabilities , without remediation urgency Computer Center, National Central University.
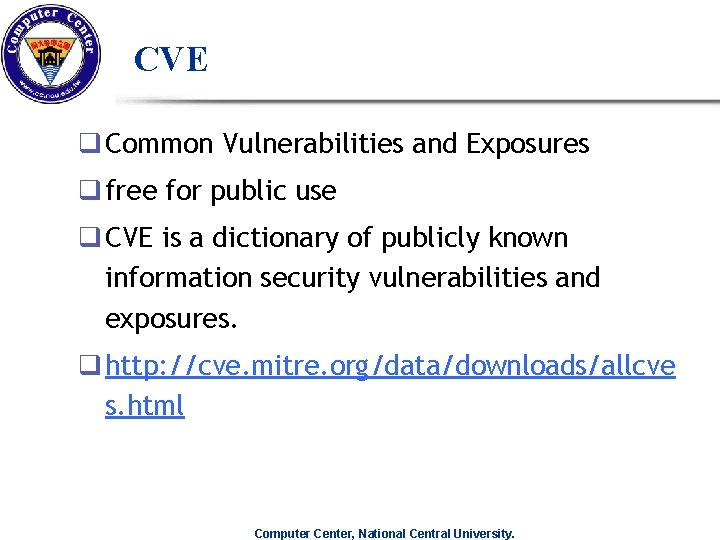
CVE q Common Vulnerabilities and Exposures q free for public use q CVE is a dictionary of publicly known information security vulnerabilities and exposures. q http: //cve. mitre. org/data/downloads/allcve s. html Computer Center, National Central University.
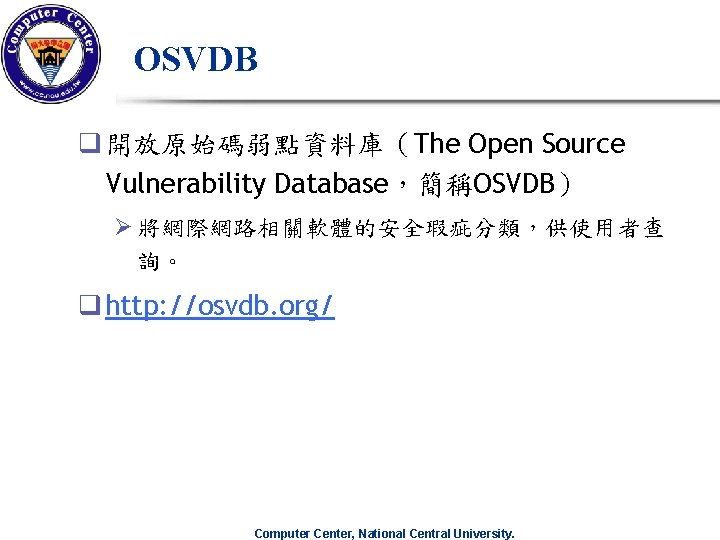
OSVDB q 開放原始碼弱點資料庫(The Open Source Vulnerability Database,簡稱OSVDB) Ø 將網際網路相關軟體的安全瑕疵分類,供使用者查 詢。 q http: //osvdb. org/ Computer Center, National Central University.
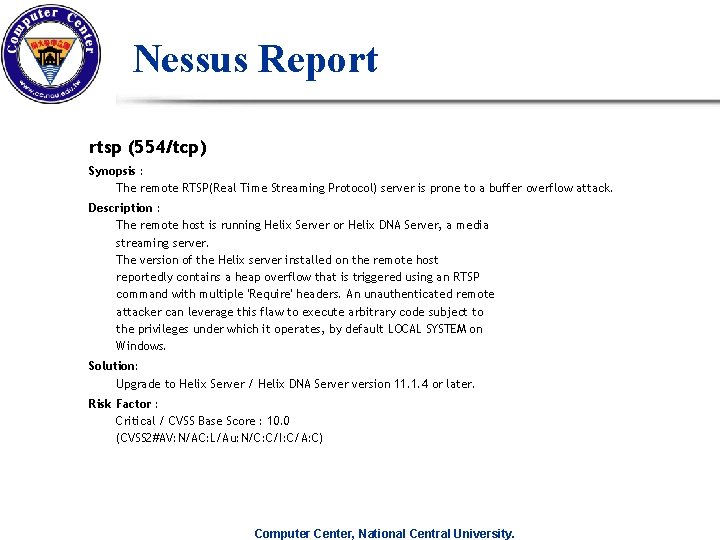
Nessus Report rtsp (554/tcp) Synopsis : The remote RTSP(Real Time Streaming Protocol) server is prone to a buffer overflow attack. Description : The remote host is running Helix Server or Helix DNA Server, a media streaming server. The version of the Helix server installed on the remote host reportedly contains a heap overflow that is triggered using an RTSP command with multiple 'Require' headers. An unauthenticated remote attacker can leverage this flaw to execute arbitrary code subject to the privileges under which it operates, by default LOCAL SYSTEM on Windows. Solution: Upgrade to Helix Server / Helix DNA Server version 11. 1. 4 or later. Risk Factor : Critical / CVSS Base Score : 10. 0 (CVSS 2#AV: N/AC: L/Au: N/C: C/I: C/A: C) Computer Center, National Central University.
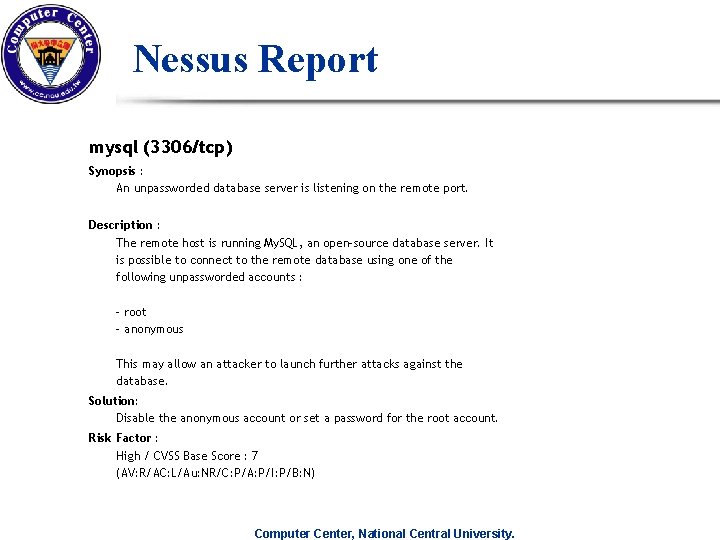
Nessus Report mysql (3306/tcp) Synopsis : An unpassworded database server is listening on the remote port. Description : The remote host is running My. SQL, an open-source database server. It is possible to connect to the remote database using one of the following unpassworded accounts : - root - anonymous This may allow an attacker to launch further attacks against the database. Solution: Disable the anonymous account or set a password for the root account. Risk Factor : High / CVSS Base Score : 7 (AV: R/AC: L/Au: NR/C: P/A: P/I: P/B: N) Computer Center, National Central University.
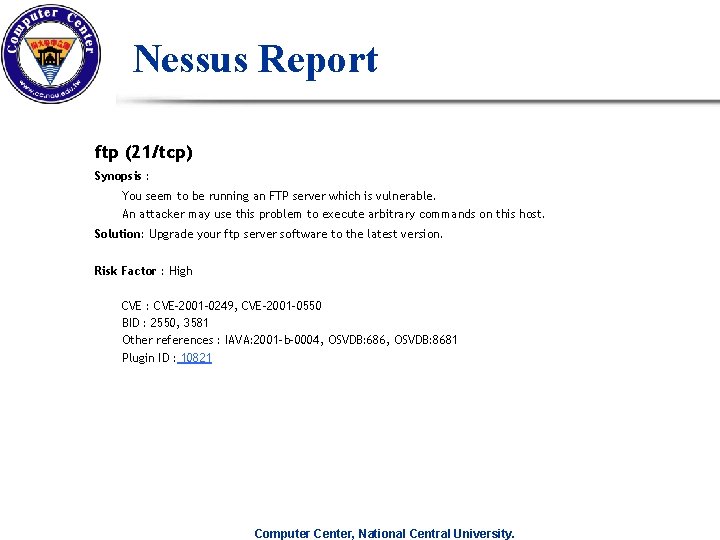
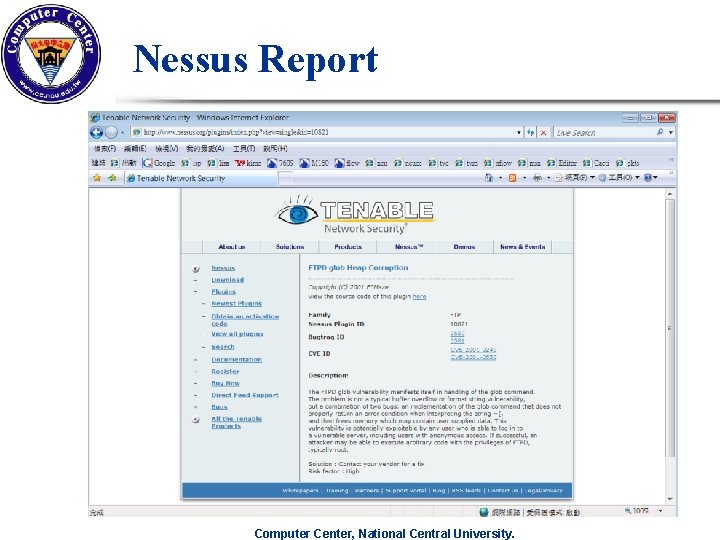
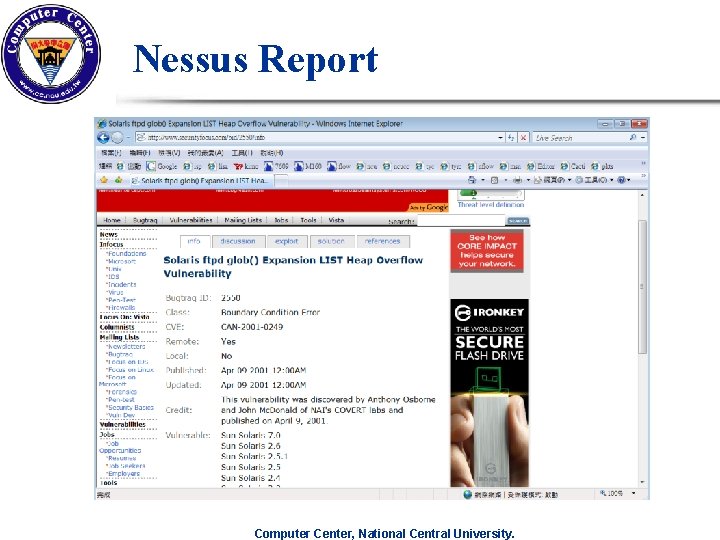
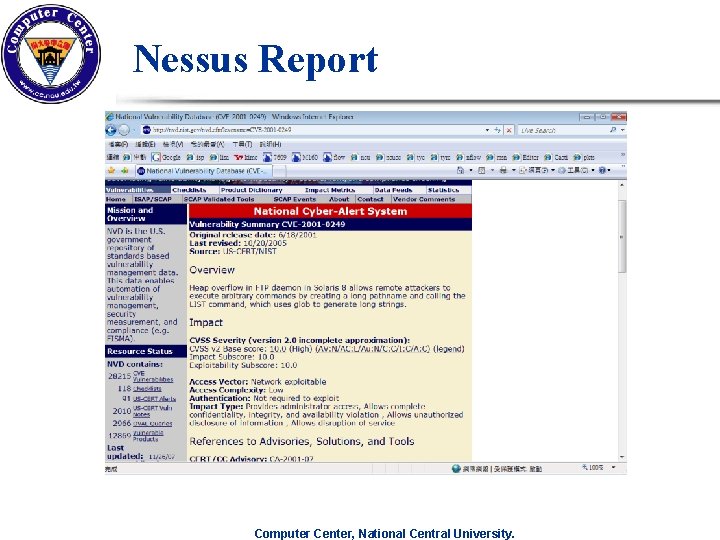
Nessus Report ftp (21/tcp) Synopsis : You seem to be running an FTP server which is vulnerable. An attacker may use this problem to execute arbitrary commands on this host. Solution: Upgrade your ftp server software to the latest version. Risk Factor : High CVE : CVE-2001 -0249, CVE-2001 -0550 BID : 2550, 3581 Other references : IAVA: 2001 -b-0004, OSVDB: 686, OSVDB: 8681 Plugin ID : 10821 Computer Center, National Central University.
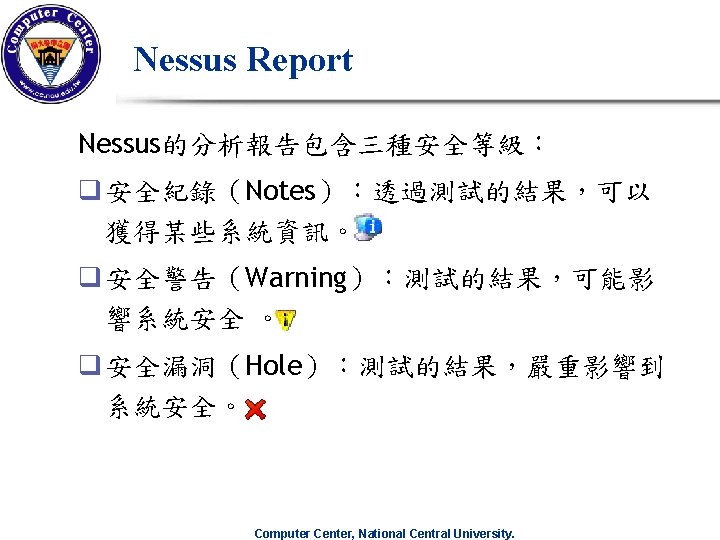
Nessus Report Computer Center, National Central University.
Nessus Report Computer Center, National Central University.
Nessus Report Computer Center, National Central University.
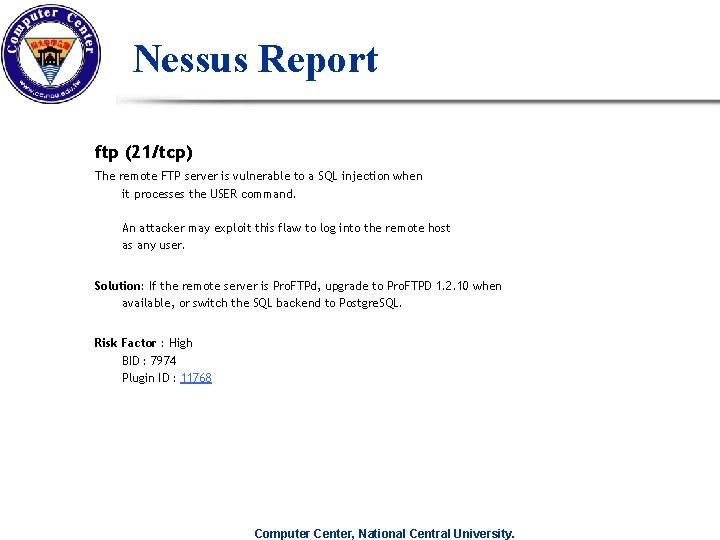
Nessus Report ftp (21/tcp) The remote FTP server is vulnerable to a SQL injection when it processes the USER command. An attacker may exploit this flaw to log into the remote host as any user. Solution: If the remote server is Pro. FTPd, upgrade to Pro. FTPD 1. 2. 10 when available, or switch the SQL backend to Postgre. SQL. Risk Factor : High BID : 7974 Plugin ID : 11768 Computer Center, National Central University.
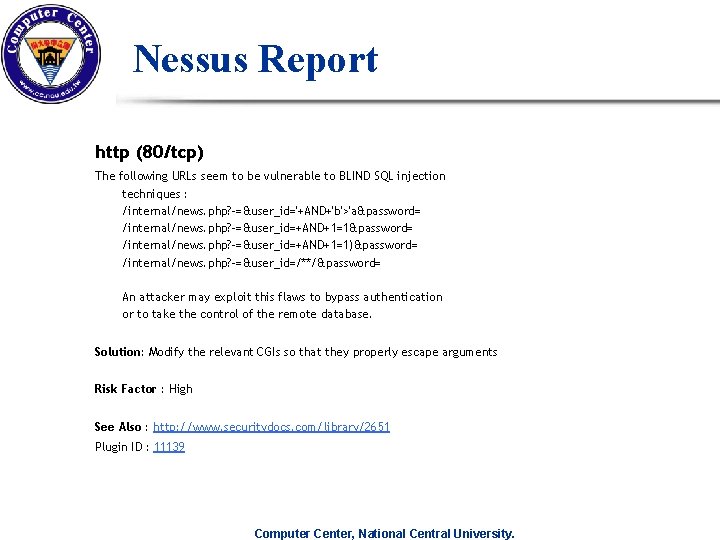
Nessus Report http (80/tcp) The following URLs seem to be vulnerable to BLIND SQL injection techniques : /internal/news. php? -=&user_id='+AND+'b'>'a&password= /internal/news. php? -=&user_id=+AND+1=1)&password= /internal/news. php? -=&user_id=/**/&password= An attacker may exploit this flaws to bypass authentication or to take the control of the remote database. Solution: Modify the relevant CGIs so that they properly escape arguments Risk Factor : High See Also : http: //www. securitydocs. com/library/2651 Plugin ID : 11139 Computer Center, National Central University.
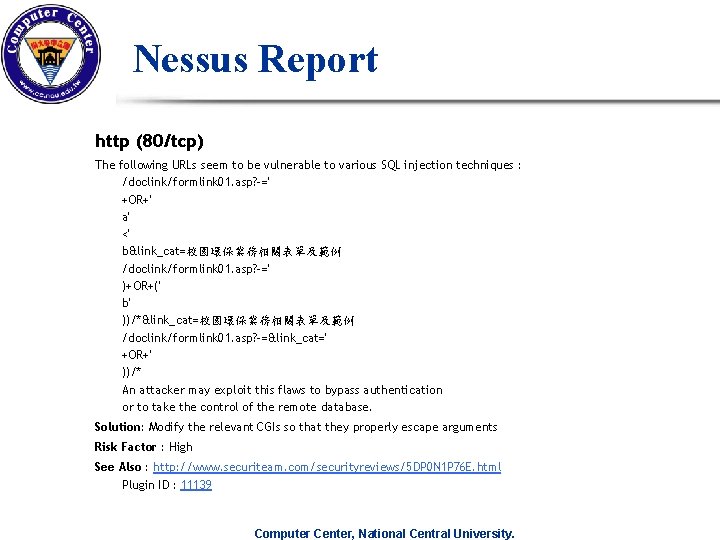
Nessus Report http (80/tcp) The following URLs seem to be vulnerable to various SQL injection techniques : /doclink/formlink 01. asp? -=' +OR+' a' <' b&link_cat=校園環保業務相關表單及範例 /doclink/formlink 01. asp? -=' )+OR+(' b' ))/*&link_cat=校園環保業務相關表單及範例 /doclink/formlink 01. asp? -=&link_cat=' +OR+' ))/* An attacker may exploit this flaws to bypass authentication or to take the control of the remote database. Solution: Modify the relevant CGIs so that they properly escape arguments Risk Factor : High See Also : http: //www. securiteam. com/securityreviews/5 DP 0 N 1 P 76 E. html Plugin ID : 11139 Computer Center, National Central University.
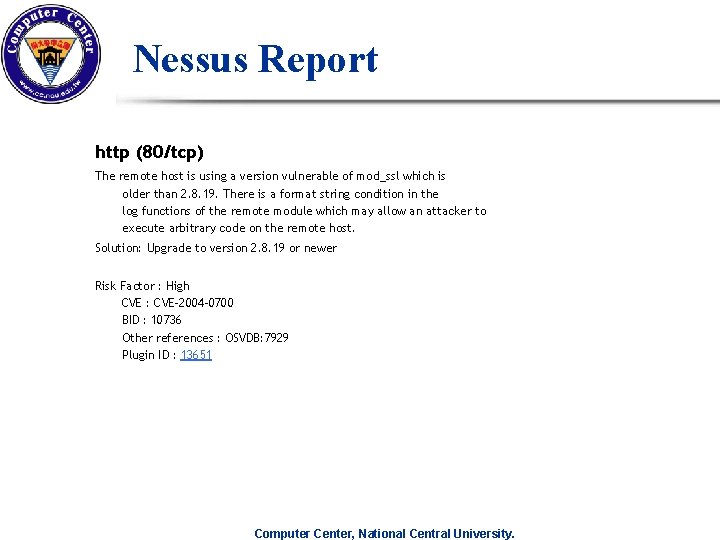
Nessus Report http (80/tcp) The remote host is using a version vulnerable of mod_ssl which is older than 2. 8. 19. There is a format string condition in the log functions of the remote module which may allow an attacker to execute arbitrary code on the remote host. Solution: Upgrade to version 2. 8. 19 or newer Risk Factor : High CVE : CVE-2004 -0700 BID : 10736 Other references : OSVDB: 7929 Plugin ID : 13651 Computer Center, National Central University.
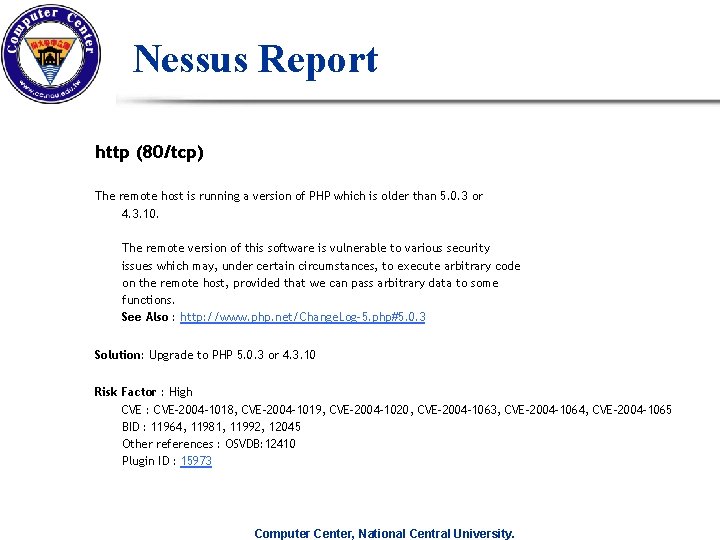
Nessus Report http (80/tcp) The remote host is running a version of PHP which is older than 5. 0. 3 or 4. 3. 10. The remote version of this software is vulnerable to various security issues which may, under certain circumstances, to execute arbitrary code on the remote host, provided that we can pass arbitrary data to some functions. See Also : http: //www. php. net/Change. Log-5. php#5. 0. 3 Solution: Upgrade to PHP 5. 0. 3 or 4. 3. 10 Risk Factor : High CVE : CVE-2004 -1018, CVE-2004 -1019, CVE-2004 -1020, CVE-2004 -1063, CVE-2004 -1064, CVE-2004 -1065 BID : 11964, 11981, 11992, 12045 Other references : OSVDB: 12410 Plugin ID : 15973 Computer Center, National Central University.
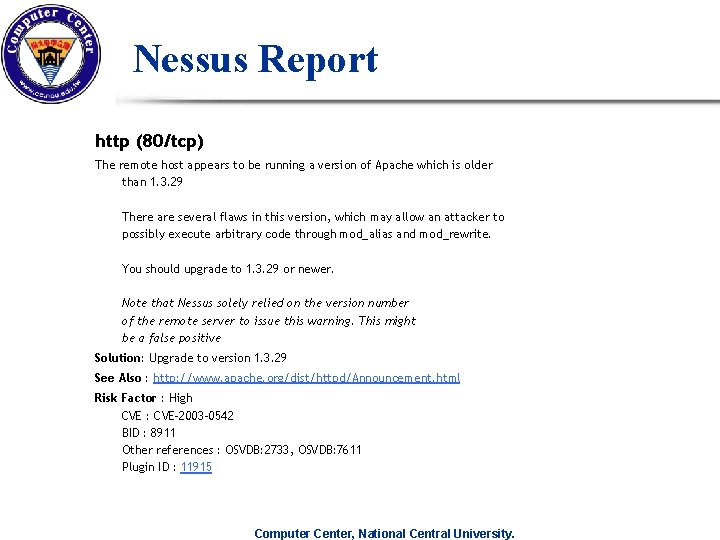
Nessus Report http (80/tcp) The remote host appears to be running a version of Apache which is older than 1. 3. 29 There are several flaws in this version, which may allow an attacker to possibly execute arbitrary code through mod_alias and mod_rewrite. You should upgrade to 1. 3. 29 or newer. Note that Nessus solely relied on the version number of the remote server to issue this warning. This might be a false positive Solution: Upgrade to version 1. 3. 29 See Also : http: //www. apache. org/dist/httpd/Announcement. html Risk Factor : High CVE : CVE-2003 -0542 BID : 8911 Other references : OSVDB: 2733, OSVDB: 7611 Plugin ID : 11915 Computer Center, National Central University.
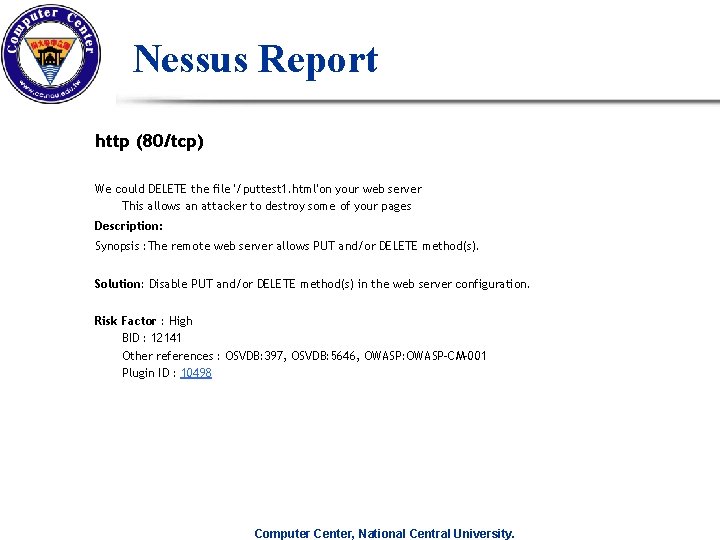
Nessus Report http (80/tcp) We could DELETE the file '/puttest 1. html'on your web server This allows an attacker to destroy some of your pages Description: Synopsis : The remote web server allows PUT and/or DELETE method(s). Solution: Disable PUT and/or DELETE method(s) in the web server configuration. Risk Factor : High BID : 12141 Other references : OSVDB: 397, OSVDB: 5646, OWASP: OWASP-CM-001 Plugin ID : 10498 Computer Center, National Central University.
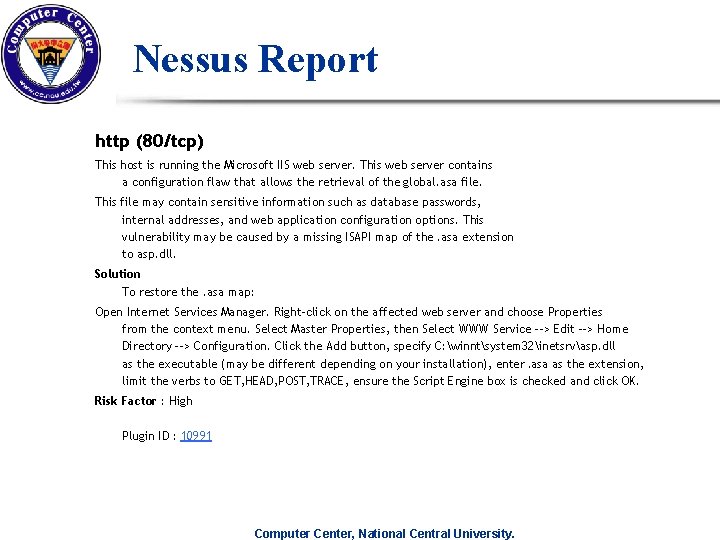
Nessus Report http (80/tcp) This host is running the Microsoft IIS web server. This web server contains a configuration flaw that allows the retrieval of the global. asa file. This file may contain sensitive information such as database passwords, internal addresses, and web application configuration options. This vulnerability may be caused by a missing ISAPI map of the. asa extension to asp. dll. Solution To restore the. asa map: Open Internet Services Manager. Right-click on the affected web server and choose Properties from the context menu. Select Master Properties, then Select WWW Service --> Edit --> Home Directory --> Configuration. Click the Add button, specify C: winntsystem 32inetsrvasp. dll as the executable (may be different depending on your installation), enter. asa as the extension, limit the verbs to GET, HEAD, POST, TRACE, ensure the Script Engine box is checked and click OK. Risk Factor : High Plugin ID : 10991 Computer Center, National Central University.
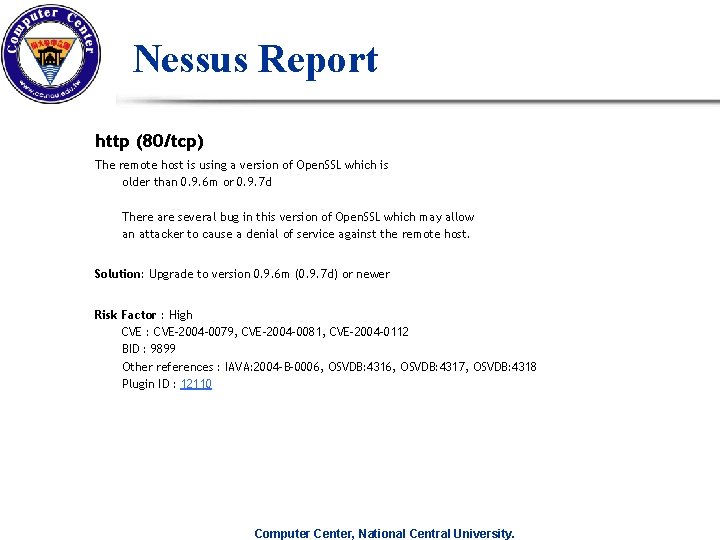
Nessus Report http (80/tcp) The remote host is using a version of Open. SSL which is older than 0. 9. 6 m or 0. 9. 7 d There are several bug in this version of Open. SSL which may allow an attacker to cause a denial of service against the remote host. Solution: Upgrade to version 0. 9. 6 m (0. 9. 7 d) or newer Risk Factor : High CVE : CVE-2004 -0079, CVE-2004 -0081, CVE-2004 -0112 BID : 9899 Other references : IAVA: 2004 -B-0006, OSVDB: 4317, OSVDB: 4318 Plugin ID : 12110 Computer Center, National Central University.
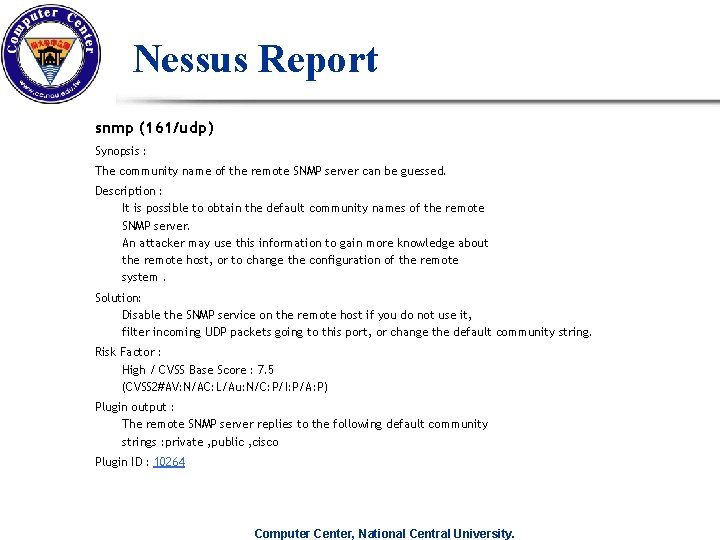
Nessus Report snmp (161/udp) Synopsis : The community name of the remote SNMP server can be guessed. Description : It is possible to obtain the default community names of the remote SNMP server. An attacker may use this information to gain more knowledge about the remote host, or to change the configuration of the remote system. Solution: Disable the SNMP service on the remote host if you do not use it, filter incoming UDP packets going to this port, or change the default community string. Risk Factor : High / CVSS Base Score : 7. 5 (CVSS 2#AV: N/AC: L/Au: N/C: P/I: P/A: P) Plugin output : The remote SNMP server replies to the following default community strings : private , public , cisco Plugin ID : 10264 Computer Center, National Central University.
Nessus Report compaq-evm (619/tcp) The remote NFS server allows users to use a 'cd. . ' command to access other directories besides the NFS file system. The listing of /cdrom is : -. -. . After having sent a 'cd. . ' request, the list of files is : - dev – backup – home – tmp - usr - var – stand – etc – cdrom – bin – boot – lib - libexec - mnt – proc – rescue – root – sbin – sys -. cshrc -. profile – COPYRIGHT – compat - entropy An attacker may use this flaw to read every file on this host Solution: Contact your vendor for a patch Risk Factor : High CVE : CVE-1999 -0166 Plugin ID : 11357 Computer Center, National Central University.
Thank You! Computer Center, National Central University.