
Preparing your school for GDPR Presented by Konrad
Preparing your school for GDPR Presented by: Konrad Kawalec GDPR Essentials. . Note: This presentation and supporting materials do not constitute legal advice.
Housekeeping: • Timings • Facilities • Fire details • Phones GDPR Essentials. .
What we will we cover: • What’s in GDPR • ICO’s 12 steps to compliance • Practical workshops on ‘record of compliance’, Data Protection Impact Assessments, GDPR Essentials. .
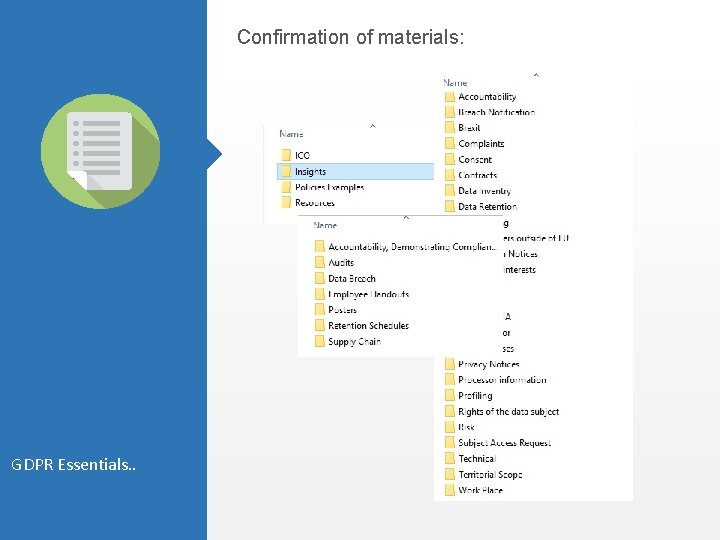
Confirmation of materials: GDPR Essentials. .
What does GDPR stand for? GDPR… an overview General Data Protection Regulation What is it? It is the change of a generation for individual data privacy brought into law by Europe through a framework or regulation, to harmonise and enforce the rights of every resident to data privacy. Whilst there are unchangeable elements of the regulation, each member state is required to enact a local law to confirm certain local aspects such as age of consent for children, legitimate interests etc. GDPR Essentials. . The Data Protection Bill 2017 is currently going through parliament and will be enacted before the 25 th May.
1. The right to be informed Data privacy rights 2. The right of access 3. The right to rectification 4. The right to erasure (be forgotten) 5. The right to restrict processing 6. The right to data portability 7. The right to object 8. Rights in relation to automated decision making and profiling. GDPR Essentials. .
GDPR… Definition of terms ICO – Information Commissioners Office UK supervisory authority Data Controller Organisation which determines the purpose & means of data processing Data Processor Organisation who's sole aim is to process the data in-lieu of the controller Data Subject – Individual who’s data you hold i. e. student, staff etc. Third Party – Any person or organisation you are sharing data with but not directly involved in the delivery of the services between the Data processor and the Data Controller i. e. Police etc. DPO – Data Protection Officer Named individual responsible for guidance and compliance GDPR Essentials. .
GDPR… Definition of terms PIMS – Personal information management systems Description of process’s, procedures or systems which allow a subject to control their personal data in line with their rights ISMS – Information security management systems Description of policies, procedures and records of security measures used to keep information secure. Risk – Probability of something happening multiplied by its impact (Hint: you do this everyday within a school). Risk appetite – How much risk you wish to accept GDPR Essentials. .
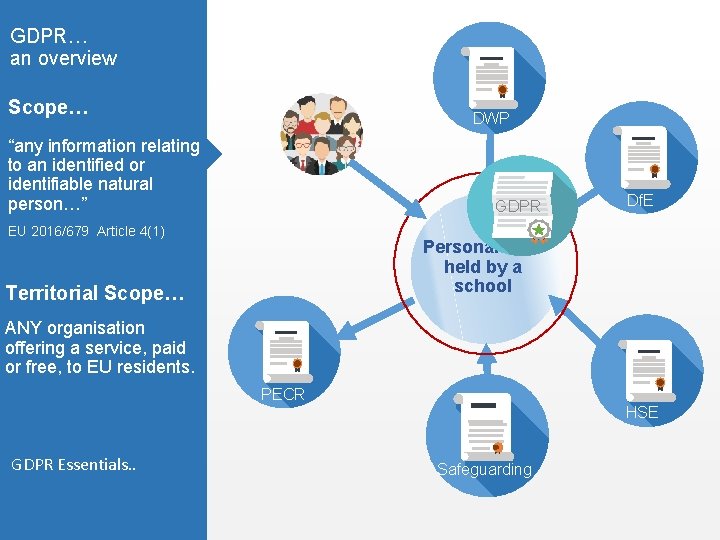
GDPR… an overview Scope… DWP “any information relating to an identified or identifiable natural person…” GDPR EU 2016/679 Article 4(1) Df. E Personal Data held by a school Territorial Scope… ANY organisation offering a service, paid or free, to EU residents. PECR HSE GDPR Essentials. . Safeguarding
Does this replace other legislation i. e. Safeguarding? GDPR… an overview NO The GDPR is there to protect the data. Other legislation will dictate what you collect, with whom you should share it, how long you should keep it. The Information commissioners office have produced a data sharing checklist which contains the paragraph: “Have you assessed the potential benefits and risks to individuals and/or society of sharing or not sharing? . . GDPR Essentials. . Source: ICO Data sharing checklist – systematic data sharing
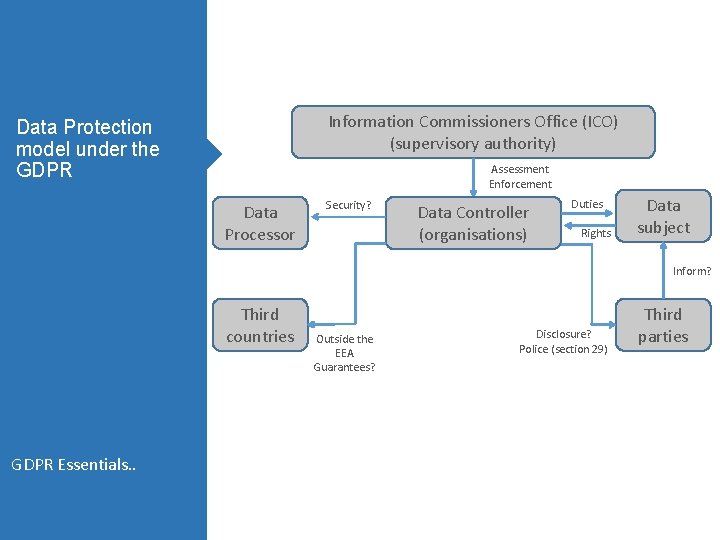
Information Commissioners Office (ICO) (supervisory authority) Data Protection model under the GDPR Assessment Enforcement Data Processor Security? Data Controller (organisations) Duties Rights Data subject Inform? Third countries GDPR Essentials. . Outside the EEA Guarantees? Disclosure? Police (section 29) Third parties
Data Controllers determine 'the purposes and the means of the processing of personal data'. This applies to both public and private sectors. Data Controller For instance, a company is the controller of data on its clients and employees; a sports club is controller of its members' data and a library of its borrowers' data. Data controllers must respect the privacy and data protection rights of those whose personal data is entrusted to them. They must: • • GDPR Essentials. . Collect and process personal data only when this is legally permitted; Respect certain obligations regarding the processing of personal data; Respond to complaints regarding breaches of data protection rules; Collaborate with national data protection supervisory authorities. Source: http: //ec. europa. eu/justice/data-protection/data-collection/index_en. htm
Important Responsibilities as a Data Controller Data controllers may only appoint data processors which provide sufficient guarantees to implement appropriate technical and organisational measures to ensure processing meets the requirements of the GDPR. • Personal Data must be processed legally and fairly; • It must be collected for explicit and legitimate purposes and used accordingly; • It must be adequate, relevant and not excessive in relation to the purposes for which it is collected and/or further processed; • It must be accurate, and updated where necessary; • Data controllers must ensure that data subjects can rectify, remove or block incorrect data about themselves; GDPR Essentials. . • Data that identifies individuals (personal data) must not be kept any longer than necessary;
Data Processors ‘process the personal data only on documented instructions from the controller'. This applies to both public and private sectors. Data Processor Data processors must also respect the privacy and data protection rights of those whose personal data is entrusted to them. They must: GDPR Essentials. . • Ensure the persons authorised to process data have committed themselves to data confidentiality. • Assist the controller by appropriate technical and organisational measures, insofar as is possible. • Assist the Controller in ensuring compliance with its obligations. • Delete or return all data to the Controller at the end of provision of services, unless there is a legal requirement to retain.
Data Protection Officer GDPR Essentials. . DPO, who can be a staff member or contractor, shall be designated on the basis of professional qualities and, in particular, expert knowledge of data protection law and practices and the ability to fulfil the tasks referred to in Article 39. These are: • Inform and advise the controller or processor and the employees of those organisations. • Monitor compliance with GDPR, including the assignment of responsibilities, awareness and training of staff involved in data processing and related audits. • Provide advice on the data protection impact assessment and monitor its performance. • Cooperate with the supervisory authority (ICO); • Act as the contact point for the supervisory authority on issues related to the processing of personal data. DPO position can be contracted out (outsourced) to an external individual or company if no other access is possible.
There are 6 legal bases for processing of personal data. These are: • Contract Performance of a contract, or required to enter into a contract. Note: Use for Staff as consent cannot be deemed to be given freely. Legal basis for processing • Legal obligation Processing of personal data to fulfil a legal obligation of a UK or EU law, not to be used in either contract or non EU member law. • Vital interests Protection of vital interests of data subject i. e. processing to ensure subject survival in an emergency if no other option. • Public interests or Public Task Necessary for the public interest or exercise of official authority of controller. . i. e Whistle blower, journalism, administration of justice etc. • Legitimate interests Of controller or third party, unless overridden by rights of subject. i. e. debt collection, warranty on goods, promotion of services B 2 B. • Consent GDPR Essentials. . Very tight conditions on informed, explicit and evidenced…most schools will only used for services outside the normal school day. i. e. before/after school club, school community news letter etc.
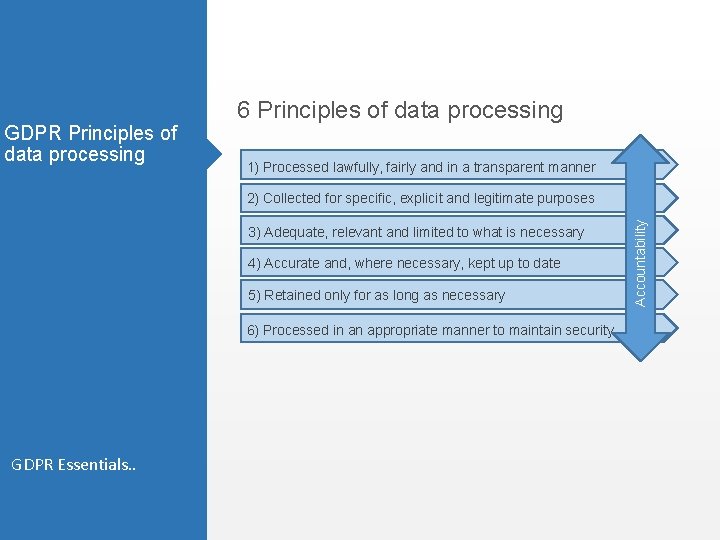
GDPR Principles of data processing 6 Principles of data processing 1) Processed lawfully, fairly and in a transparent manner 3) Adequate, relevant and limited to what is necessary 4) Accurate and, where necessary, kept up to date 5) Retained only for as long as necessary 6) Processed in an appropriate manner to maintain security GDPR Essentials. . Accountability 2) Collected for specific, explicit and legitimate purposes
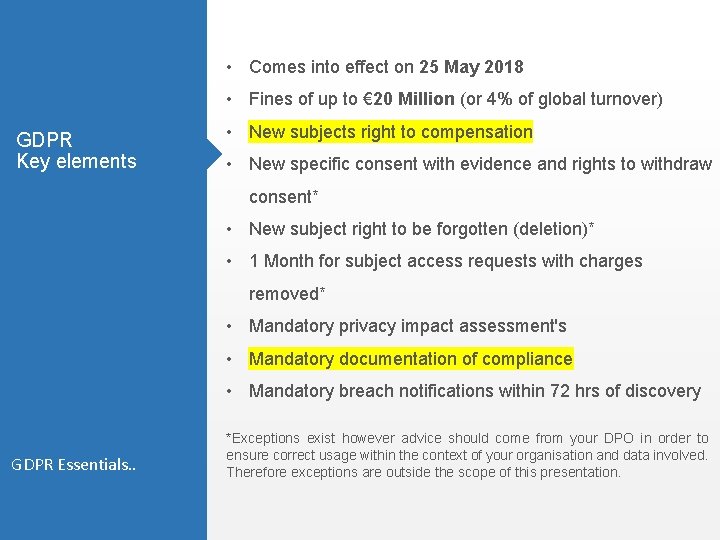
• Comes into effect on 25 May 2018 • Fines of up to € 20 Million (or 4% of global turnover) GDPR Key elements • New subjects right to compensation • New specific consent with evidence and rights to withdraw consent* • New subject right to be forgotten (deletion)* • 1 Month for subject access requests with charges removed* • Mandatory privacy impact assessment's • Mandatory documentation of compliance • Mandatory breach notifications within 72 hrs of discovery GDPR Essentials. . *Exceptions exist however advice should come from your DPO in order to ensure correct usage within the context of your organisation and data involved. Therefore exceptions are outside the scope of this presentation.
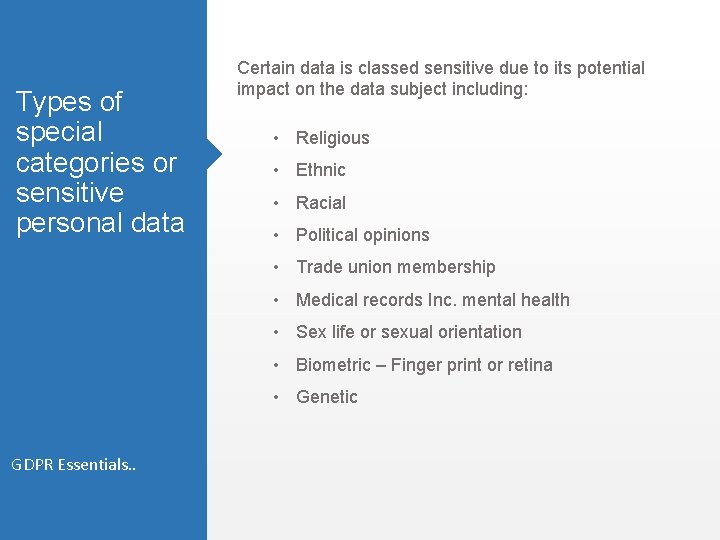
Types of special categories or sensitive personal data Certain data is classed sensitive due to its potential impact on the data subject including: • Religious • Ethnic • Racial • Political opinions • Trade union membership • Medical records Inc. mental health • Sex life or sexual orientation • Biometric – Finger print or retina • Genetic GDPR Essentials. .
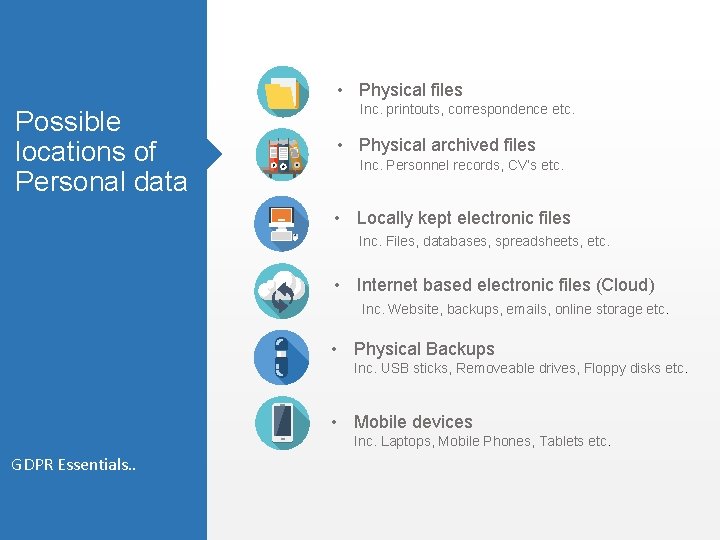
• Physical files Possible locations of Personal data Inc. printouts, correspondence etc. • Physical archived files Inc. Personnel records, CV’s etc. • Locally kept electronic files Inc. Files, databases, spreadsheets, etc. • Internet based electronic files (Cloud) Inc. Website, backups, emails, online storage etc. • Physical Backups Inc. USB sticks, Removeable drives, Floppy disks etc. • Mobile devices Inc. Laptops, Mobile Phones, Tablets etc. GDPR Essentials. .
Risk = Impact x Probability Scales of impact: What is risk. . • • • Incident - Loss of telephone list Minor – Loss of encrypted USB stick Moderate – Loss of laptop Major – Loss of your MIS system Extreme – Loss of your admin server Scales of probability: • • • GDPR Essentials. . Frequent Likely Possible Unlikely Rare When you cannot reduce the impact, the only way to reduce risk is to reduce probability - through culture, awareness, training and procedures.
Reducing risk through… Privacy culture Some of the most common privacy breaches happen when personal information is stolen, lost or mistakenly disclosed. What’s needed is an environment, or “culture, ” where protecting data privacy is top of the mind for every employee whenever that person handles personal information—a privacy culture. Individuals responsible for privacy should: • Closely align the importance of privacy with the schools values • Implement strategies to convert the knowledge about privacy and belief in its importance into repeated practices that will shape the culture over time. GDPR Essentials. . Source: IAPP - International Association of Privacy Professionals
Human factor Reducing risk through… Keep it simple and realistic Privacy culture Use technology as much as possible to simplify training e. g. auto home folder redirection on login, folder/filling structure etc. Create systems and process’s to cement a privacy culture and meet the accountability requirements of GDPR Create an ongoing program of induction and annual refresher training. Create a supportive culture of continuous learning GDPR Essentials. .
ISMS – Information Security Management Systems (ISO 27001) Reducing risk through… Privacy culture ISMS is a set of policies and procedures for systematically managing an organization's data in order to reduce risk. These can be either physical or technological such as: • Backups • Anti virus software / system updates • Encryption • User account creation and password policies GDPR Essentials. . • Theft prevention of physical documents, data or IT hardware
PIMS – Personal Information Management System (BS 10012) Reducing risk through… Privacy culture PIMS are services that help individuals gather, manage and use information, including personal information, to help them manage their lives better and achieve their own goals in line with their rights. • Provide, update and withdraw consent • Issue a subject access requests • Request for erasure of records • Request cessation of processing • Record a complaint GDPR Essentials. . Note: Very good method of allowing subjects to update data and demonstrate a strong culture of privacy.
Demonstrating Compliance • Subject access requests • Data transfers • User account creation • Privacy impact assessments • Mobile devices • Breach notifications (A sample, not a complete list) GDPR Essentials. . Accountability Unfortunately, under the GDPR, there is an increased emphasis on accountability or demonstration of compliance including policies, procedures and records for:
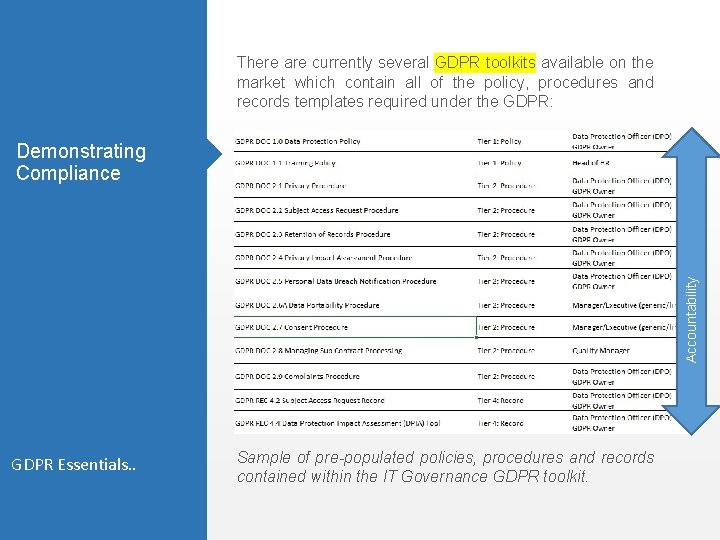
There are currently several GDPR toolkits available on the market which contain all of the policy, procedures and records templates required under the GDPR: Accountability Demonstrating Compliance GDPR Essentials. . Sample of pre-populated policies, procedures and records contained within the IT Governance GDPR toolkit.
Subject access request key points: Subject Access Requests • No charge – unless manifestly unfounded or excessive then “reasonable” • Response within one month – or two months if multiple or complex (you must notify them within the month if intent to extend) • There are exemptions – risk to others, unable to confirm identity, legal action etc. (details within the SAR section of the insights library) • GDPR Essentials. . You must remove/redact information referencing persons other than the subject Example SAR policies in the SAR folder of the insights library
Data Protection Impact Assessment (sometimes known as a private impact assessment or PIA) DPIA Data protection impact assessments (DPIA) are addressed in the GDRP in Article 35, which states: “Where a type of processing in particular using new technologies…context and purposes of the processing, is likely to result in a high risk to the rights and freedoms of natural persons, the controller shall, prior to the processing, carry out an assessment of the impact of the envisaged processing operations on the protection of personal data. ” GDPR Essentials. . • Mandatory after 25 th May • Not required retrospectively even if high risk • To be carried out in high risk situations i. e. server change, new cloud service etc. • Must be done with the DPO - outside the scope of this day
Concept for data security contains: Concept of security • Confidentiality – controlling access through either physical or digital means. • Integrity – ensuring accuracy and providing a simple process to update • Accessibility – increased access will reduce the use of other non secure means such as printouts, temporary backups etc. GDPR Essentials. .
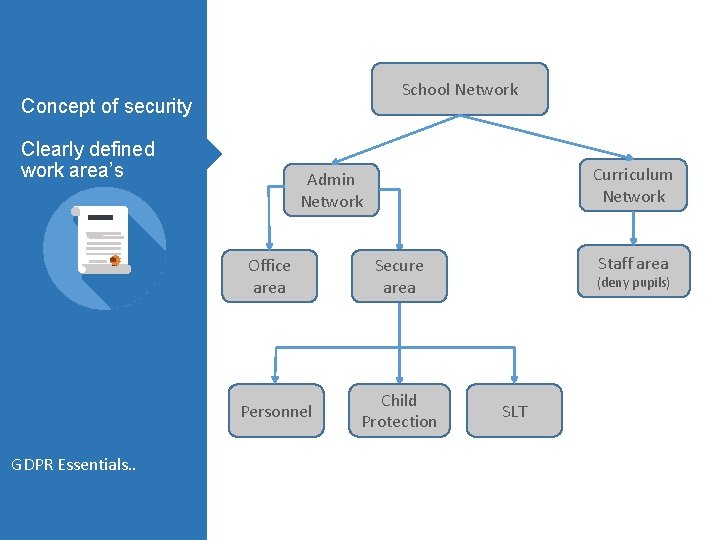
School Network Concept of security Clearly defined work area’s Office area Personnel GDPR Essentials. . Curriculum Network Admin Network Staff area Secure area Child Protection (deny pupils) SLT
Types of risk within your school: types of risk within the school GDPR Essentials. . • Inappropriate viewing- over the shoulder • Lost password – using others • Printouts – in transit, storage, in use • Transfers to local authority – left over files • Transfer to data processor – lack of justification
Key areas of risk within your school: Areas of risk within the school • BYOD – Laptops, tablets and USB sticks • Data Collection sheets – Locked when not in use • Data sharing - School Nurse, external agencies etc. • Laptop transfers and repairs • Poor backup procedures and reviews Are you aware of the data risks in your school Example policies for clear desk and using removable devices can be seen in resources section of resource kit. GDPR Essentials. .
Data mapping to create a record of processing activity Each controller and, where applicable, the controller's representative, shall maintain a record of processing activities under its responsibility – Article 30 Where possible, a general description of the technical and organisational security measures referred to in Article 32 GDPR Essentials. . • Unfortunately it is statutory just like your SCR • It must be kept up to date and available for inspection as requested
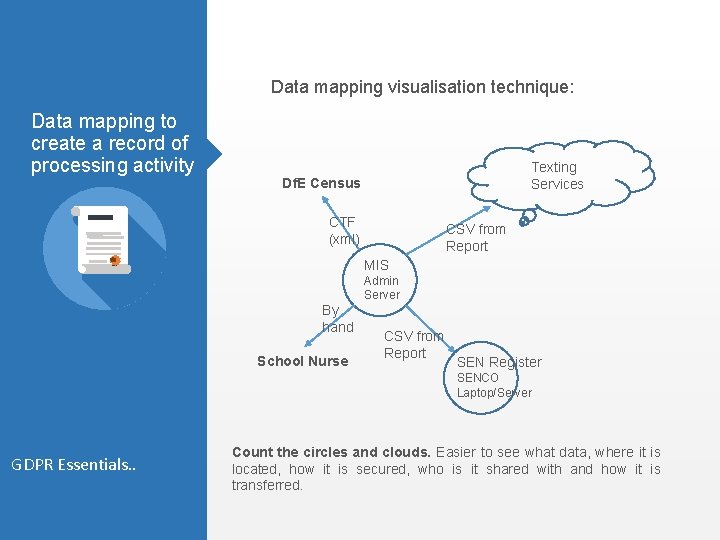
Data mapping visualisation technique: Data mapping to create a record of processing activity Texting Services Df. E Census CTF (xml) CSV from Report MIS Admin Server By hand School Nurse CSV from Report SEN Register SENCO Laptop/Server GDPR Essentials. . Count the circles and clouds. Easier to see what data, where it is located, how it is secured, who is it shared with and how it is transferred.
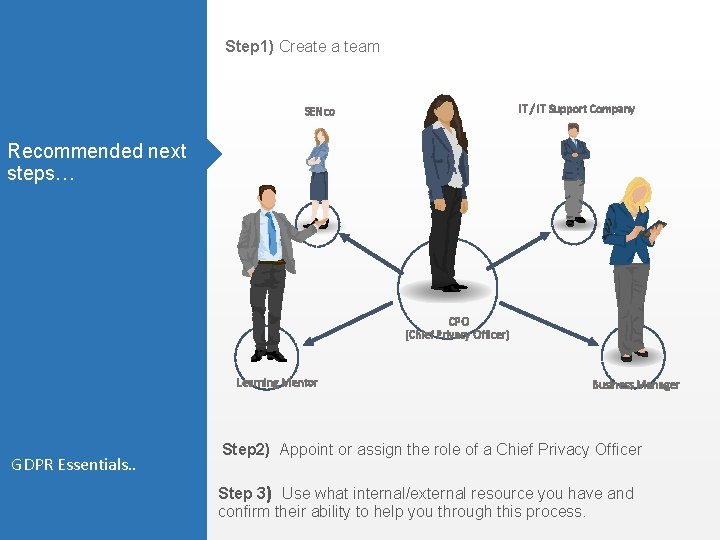
Step 1) Create a team IT / IT Support Company SENco Recommended next steps… CPO (Chief Privacy Officer) Learning Mentor GDPR Essentials. . Business Manager Step 2) Appoint or assign the role of a Chief Privacy Officer Step 3) Use what internal/external resource you have and confirm their ability to help you through this process.
Step 4) Identify if you have access to a DPO either local authority or outsourced. Step 5) Choose the GDPR toolkit you want to use, produce policies and have FGB approve asap. Recommended next steps… Step 6) Ask IT to perform a full audit inc. hardware, software backups and network security. Step 7) Audit what data you have, as a team, including archived records, spreadsheets, manual records etc. Step 8) Use supplier letter in resources to request “sufficient guarantees to implement appropriate organisation and technical measures” Step 9) Ensure all staff within your school are trained and aware. . Don’t forget to update your governors on progress. Step 10) Publish your updated privacy notice Step 11) Create your register of data processing activity GDPR Essentials. . Step 12) Embed a culture of “Ask…Don’t guess” within your school (just as you do for safeguarding).
Questions Thank you Opportunity for feedback. . GDPR Essentials. .
Additional training available: Questions GDPR Essentials. . See our buy Doncaster offering; https: //ico. org. uk/for-organisations/guide-to-the-generaldata-protection-regulation-gdpr/lawful-basis-forprocessing/special-category-data/
- Slides: 39