
Platinum GDPR Regine Bonneau RB Advisory LLC October
Platinum GDPR Regine Bonneau - RB Advisory LLC October 13, 2017 Property of RB Advisory LLC
Agenda • Global Data Protection Regulation (GDPR) • What is it? • Deadline • Why GDPR? • Scope - Territorial • Who are the key players? • Controllers • Processors • Data Protection Officers (DPO) • Why is the GDPR important to Company and Security Professionals? • Data • Breach Notifications • Key Individual Rights • Penalties • Challenges to the GDPR – Data Complexity • Technical Guides / or Solutions • Frameworks • Categories • Steps to Get Ready • Case Study – Equifax – Fast Forward to May 25, 2018 • Resources • Q&A • Audience Poll Property of RB Advisory LLC 2
General Data Protection Regulation (GDPR) Property of RB Advisory LLC 3
Property of RB Advisory LLC 4
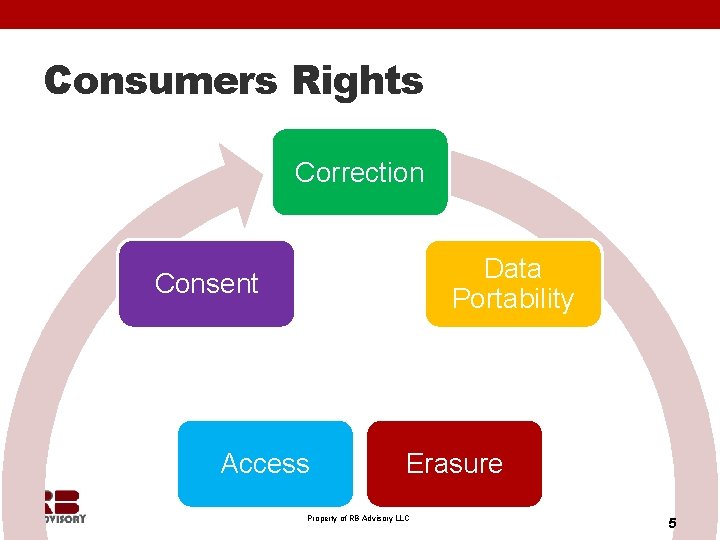
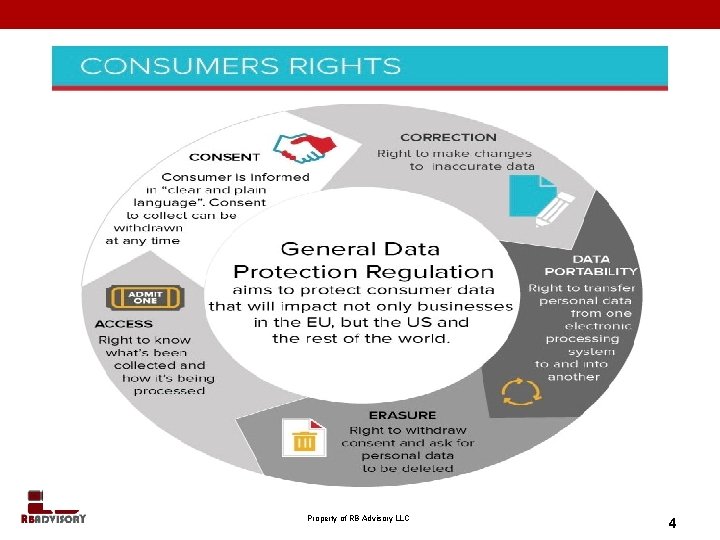
Consumers Rights Correction Data Portability Consent Access Erasure Property of RB Advisory LLC 5
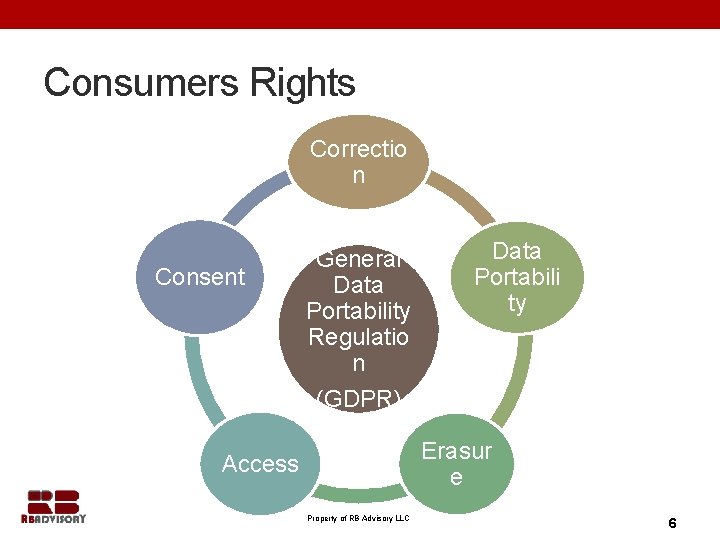
Consumers Rights Correctio n Consent General Data Portability Regulatio n (GDPR) Data Portabili ty Erasur e Access Property of RB Advisory LLC 6
• What is it? • The General Data Protection Regulation (GDPR) will harmonize data protection laws in the EU to help bring better transparency for support of individuals’ rights • It consists of 99 Articles with sub definitions • Deadline • It was revised from its 1995 form to keep up with technology of today and the way information is being obtained, processed, shared and retained. • Adopted on April 27, 2016 and will become law on May 25, 2018. Very short window to start complying. Property of RB Advisory LLC 7
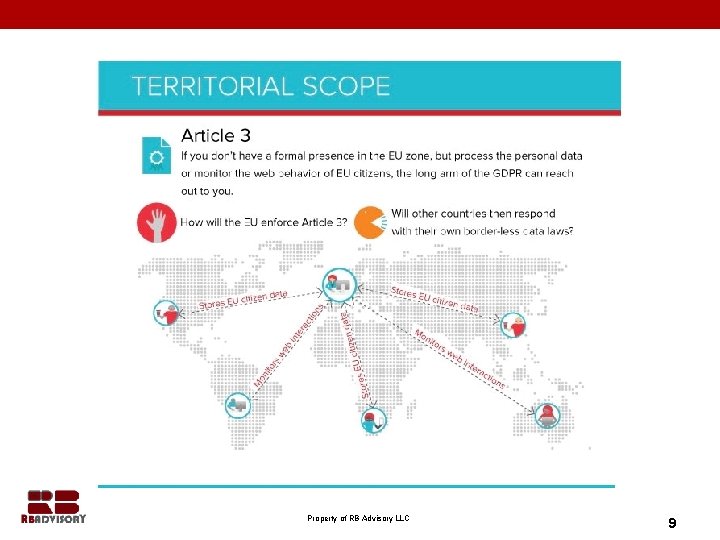
WHY GDPR? The General Data Protection Regulation will help with: • The checks and balances of the massive global exchange of personal data. • Unifying each country’s laws to endorse the free cross-border of data sharing, including non-EU territories. • Forcing a far-reaching consideration of privacy rights • The significant shift of the international privacy landscape SCOPE • Covers data processors (organizations) and data subjects (individuals) within the EU • GDPR applies to any organization processing the details of EU individuals • If you do business in the EU or EU individuals, or a company that does business with the EU, you are subject to the GDPR Property of RB Advisory LLC 8
Property of RB Advisory LLC 9
Who are the Key Players? Property of RB Advisory LLC 10
GDPR Accountability • Accountability is one of the centerpiece concepts found in the new framework • It will be expected of both Data controllers and processors to draft formal policies to document an organization’s data privacy and protection posture and how it addresses the precepts of the GDPR • Policies will need to be created based on the following: • The nature, scope, context, and purposes of processing personal data • And outline foreseeable risks to the rights of individuals Property of RB Advisory LLC 11
GDPR Accountability - Controllers • Detail must be kept at high standards: • The name and contact information of the controller and Data Protection Officer • Purposes of processing personal data • Categories of data subjects, data, and recipients • International data transfers and related safeguards for those transfers • Data retention periods, and • Data security measures employed Property of RB Advisory LLC 12
GDPR Accountability - Processors • Have to formally keep similar materials that outline as the Controller: • The name and contact details of the processor and all engaged controllers • Categories of processing for each controller • International data transfers and related safeguards for those transfers, and • Data security measures employed Property of RB Advisory LLC 13

GDPR Accountability – Data Protection Officers • Articles 35, 37, 38 & 39 • Under the GDPR framework, any private sector organization that • carries out “regular and systematic monitoring of data subjects” as • part of its principal business activities will be required to employ • a Data Protection Officer (DPO) by the May 25 th, 2018 enforcement date. This includes American and Canadian companies that routinely process large scale or sensitive EU data. Property of RB Advisory LLC 14
DPO – Roles and Responsibilities • Article 39 of GDPR, “Tasks of the data protection officer, ” • • outlines the overall roles and responsibilities of the DPO. It states that the primary function of the Data Protection Officer is to inform and advise the data controller on how to “monitor compliance” with GDPR. This includes conducting privacy awareness training, performing compliance audits, and, wherever appropriate, issuing privacy impact assessments. DPOs are also responsible for acting as the liaison between the company and a supervisory authority. Property of RB Advisory LLC 15
GDPR’s importance to Company & Security Property of RB Advisory LLC 16
• Every organizations who offers products, services, or • • • handles data to EU citizens are to adhere to strict privacy and security measures Business leaders, Privacy experts, Legal professionals, and Security leaders should be discussing compliance measures. Security Leaders are the ones to address the changes to people, process, and technology to meet the requirements Penalties for violations “Personal Data” definition expanded Technical and organizational measures require adequate general information security controls The jurisdictional reach includes organizations outside of the EU Property of RB Advisory LLC 17
Data • Data Security • GDPR has made several critical updates to data security requirements, which will provide greater protection for personal data and hold companies responsible for security failures. Now, data controllers and processors must implement new security measures and comply with uniform breach notification laws. • Security Controls • GDPR requires that “taking into account the state of the art, the costs of implementation and the nature, scope, context and purposes of processing as well as the risk of varying likelihood and severity for the rights and freedoms of natural persons, the controller and the processor shall implement appropriate technical and organizational measures to ensure a level of security appropriate to the risk. ” • Not only must data processors and controllers adopt proper security measures to ensure the confidentiality, integrity, and accountability of personal data, GDPR now explicitly mentions specific security controls that organizations must implement. Property of RB Advisory LLC 18
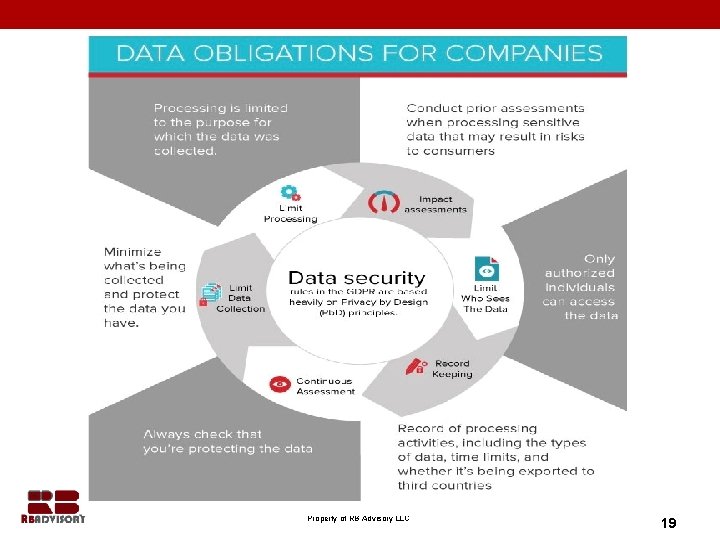
Property of RB Advisory LLC 19
Data Protection by Design (Privacy by Design) • The GDPR requires data protection and processing safeguards to become part of all systems and processes. • Data protection by design is based on 7 foundational principles • Proactive not reactive • Privacy as the ‘default’ setting • Privacy embedded into design • Full functionality: positive sum, not zero sum • End-to-End security: full lifecycle protection • Visibility and transparency : keep it open • Respect for user privacy: keep it user-centric Property of RB Advisory LLC 20
Data Protection by Design and By Default (Privacy by Design) Checklist • The GDPR is making companies rethink how data protection and privacy are met and managed by the organization: • Analyze the gap between current and mandated position • Assign required budget and resources • Assign a data protection officer if criteria met • Align with best-practice mandates • Review and update data-handling procedures • Develop a workplace education program Property of RB Advisory LLC 21
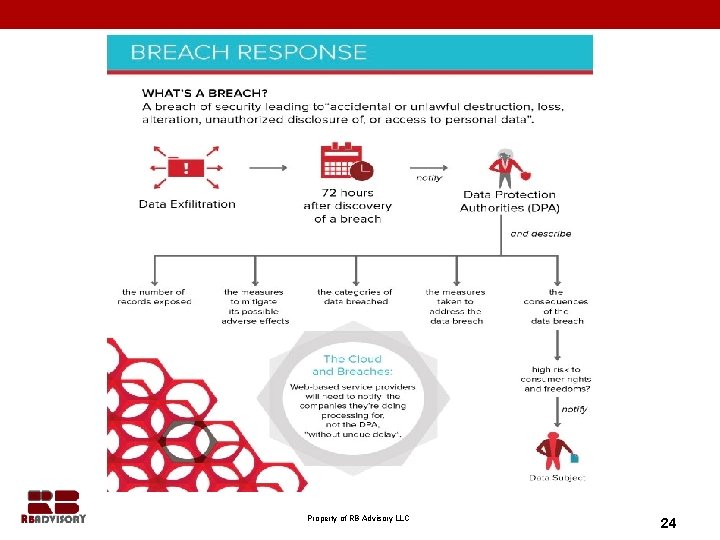
Breach Notifications Laws • Security is a high priority within GDPR that EU regulators have included a detailed breach notification rule. The inclusion of a breach notification rule not only highlights the importance of data security, but also holds organizations accountable for their personal data security failures. Property of RB Advisory LLC 22
• The following notifications are required under the GDPR breach notification rule: • Data controllers must report breaches of personal data to Supervisory Authorities (SAs) without undue delay and, where feasible, within 72 hours of becoming aware of the breach. • If the controller can demonstrate that the data incident is unlikely to result in a risk to the rights and freedoms of natural persons, there is no need to report the incident to SAs. • If a data controller determines that a breach would result in a High privacy risk, then the data controller must also notify the affected individual(s) of the breach without undue delay. • Data processors must notify data controllers of all breaches without undue delay, but processors have no other notification obligations under GDPR. This means the company will need to ensure that they notify their consumers once alerted of a breach by a data processor (third party vendors). Property of RB Advisory LLC 23
Property of RB Advisory LLC 24

Reporting Data breach checklist • The GDPR will require companies to develop or update internal breach notification procedures to meet the 72 hour reporting requirement: • Timely detection of breaches • Reporting and alarms • Mitigation through automation • Investigation capabilities (case management and forensics) Property of RB Advisory LLC 25
Key Changes to Individual Rights • You should check your procedures to ensure they cover all the rights individuals have, including how you would delete personal data or provide data electronically and in a commonly used format. These are covered under Articles 4: Section 11, 17, 21, 33, & 34. • The GDPR includes the following rights for individuals: • • The right to be informed; The right of access; The right to rectification; The right to erasure; The right to restrict processing; The right to data portability; The right to object; and The right not to be subject to automated decision-making including profiling. • The right to data portability is new. It only applies: • • To personal data an individual has provided to a controller; Where the processing is based on the individual’s consent or for the performance of a contract; and When processing is carried out by automated means. Property of RB Advisory LLC 26

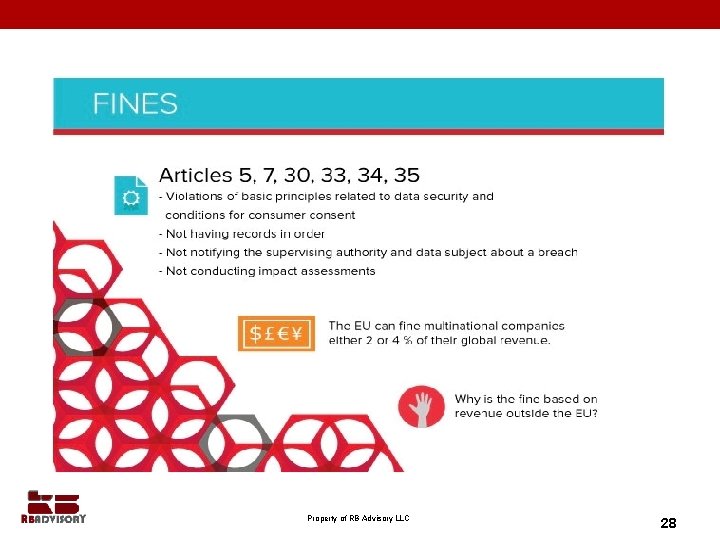
Penalties – Cost of Non. Compliance • Penalties are calculated on Global Annual Revenue • This could mean bankruptcy for some companies • Notification breach: • A maximum fine of € 10, 000 or up to 2% of total annual global turnover (not profit) of the preceding financial year, whichever is greater. • Data subject information breach: • A maximum of € 20, 000 or up to 4%percent of global annual revenue – whichever is greater Property of RB Advisory LLC 27
Property of RB Advisory LLC 28
Challenges to GDPR – Data Complexity Property of RB Advisory LLC 29
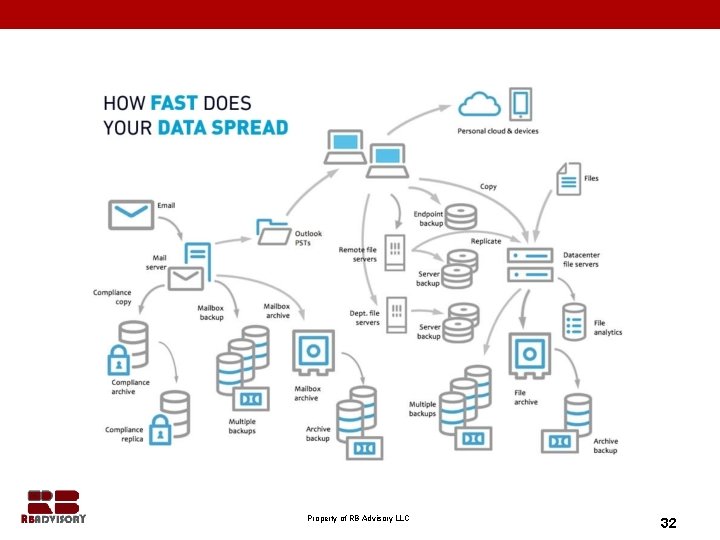
• The biggest challenge in complying with the GDPR is the fact that personal data can be located anywhere. Just think about how many copies of someone's personal data might be spread across your organization. • If an individual asks you to delete their personal data, do you know where it all lives • How will you ensure compliance with the GDPR across all your unstructured data sources? Laptops, mobile devices and other endpoints? Email? Personal clouds? File servers and content management systems with hundreds or thousands of authorized users? Dev/test copies? Business intelligence and analytics applications? Property of RB Advisory LLC 30
• To comply with the GDPR, you'll likely need to make fundamental changes to the way you look at data: • Collection • Storage • Management • Usage • Data Mapping and Workflow Property of RB Advisory LLC 31
Property of RB Advisory LLC 32
Solutions or Technical Guide Current Frameworks that will help when properly implemented and monitored: • ISO/IEC 27001 – Standards framework for Information protection • ISO/IEC 27002: • Information Security Incident Management • Information Security Aspects of Business Continuity Management • ISO/IEC 27018 – Standards for protecting privacy in the cloud • NIST Cybersecurity Framework: • Respond Function • Recover Function • SP 800 -39 Managing Information Security Risk • SP 800 -60 Guide for Mapping Information and Information Systems to Security Categories • SP 800 -53 Security and Privacy Controls • SOC 2 • CIS Control Property of RB Advisory LLC 33

Categories • Risk Assessment: • ISO/IEC 27001 Implementation of Data Protection Impact Assessment • Control A. 8. 2. 1 – Classification of Information • Compliance: • CIS Controls 1, 2, 3, 4, 5 • ISO/IEC 27001 • • • Control A. 18. 1. 1 – Identification of Applicable legislation and contractual requirements Control A. 18. 1. 4 – Privacy and Protection of Personally Identifiable Information (PII) ISO/IEC 27018 • Control A. 11. 1 – Geographical location of PII • Breach Notification: • CIS Controls 1, 2, 3, 4, 5 • ISO/IEC 27001 • • Control A. 16. 1 – Management of Information Security Incidents and Improvements ISO/IEC 27018 • Control A. 9. 1 – Notification of a Data Breach involving PII Property of RB Advisory LLC 34
Categories - continued • Asset Management: • • CIS Controls 1, 2, 3, 4, 5 ISO/IEC 27001 • • Privacy by Design: • • CIS Controls 1, 2, 3, 4, 5, 13, 14 NIST • • • SP 800 -39 Managing Information Security Risk SP 800 -60 Guide for Mapping Information and Information Systems to Security Categories SP 800 -53 Security and Privacy Controls ISO/IEC 27018 • Control A. 4. 2 – Recommends secure erasure of temporary files should be considered as a requirement for information systems development ISO/IEC 27001 • • Control A. 8 – Asset Management for inclusion of personal data Control A. 14 – System Acquisitions, development and maintenance Supplier Relationships: • • CIS Controls 1, 2, 3, 4, 5 ISO/IEC 27001 • • Control A. 15. 1 – Information Security Supplier Relationships ISO/IEC 27018 • Recommends explicit definition of responsibilities of cloud service provider, sub-contractors, and cloud service customers Property of RB Advisory LLC 35
Case Study: Equifax – Fast Forward to May 25, 2018 • Brief History: • Established in 1899 in Atlanta, GA • 118 years old • Operates in 26 Countries: USA Australia Cambodia Chile Ecuador Honduras Malaysia New Zealand Peru Russia Singapore UK Argentina Brazil Canada Costa Rica El Salvador India Mexico Paraguay Portugal Saudi Arabia Spain Uruguay 2016 - Stats Revenue: Operating Income: Net Income: Total Assets: Total Equity: Property of RB Advisory LLC $3. 144 Billion $817. 9 Million $488. 8 Million $6. 664 Billion $2. 662 Billion 36
Breach • Period: March 2017, May – July 2017 • Date of Discovery: July 29, 2017 • Date of Report: September 7, 2017 • Affected: 143 Million equivalent 44% of US Population Property of RB Advisory LLC 37
• What caused the Breach: • Failed to fix a security flaw and Data not encrypted when at rest • Known vulnerability and did not patch the system Property of RB Advisory LLC 38
• What was exposed: • Full Name • Social Security Numbers • Birth Dates • Addresses • Driver’s License Nuber • At least 209, 000 Consumer Credit Card Credentials taken • 15. 2 Million U. K. consumer records stolen Property of RB Advisory LLC 39
Cost of Breach • Expected: • $200, 000 Million - $300, 000 Million • Loss of Revenue thus far: • $4, 000, 000 Billion • Ripple Effect: • Services provided to: • Fortune 100 firms • Financial Institutions • Government Agencies • Universities Property of RB Advisory LLC 40
GDPR – May 25, 2018 GDPR Penalty at 4% of Global Revenue: • $124, 000 Million Property of RB Advisory LLC 41
Resources Property of RB Advisory LLC 42
95/46/EC http: //eur-lex. europa. eu/legal-content/EN/TXT/HTML/? uri=CELEX: 52016 PC 0214&from=EN https: //iapp. org/news/a/study-at-least-28000 -dpos-needed-to-meet-gdpr-requirements/ General Data Protection Regulation (GDPR) (Regulation (EU) 2016/679), Article 37(1)(b) General Data Protection Regulation (GDPR) (Regulation (EU) 2016/679), Article 39(2) General Data Protection Regulation (GDPR) (Regulation (EU) 2016/679), Article 37(5) General Data Protection Regulation (GDPR) (Regulation (EU) 2016/679), Article 37(6) General Data Protection Regulation (GDPR) (Regulation (EU) 2016/679), Article 39(1)(e) General Data Protection Regulation (GDPR) (Regulation (EU) 2016/679), Article 38(3) http: //eur-lex. europa. eu/legal-content/EN/TXT/PDF/? uri=CELEX: 32016 R 0679&from=EN https: //ico. org. uk/for-organisations/data-protection-reform/overview-of-the-gdpr/individuals-rights/rights-related-to-automateddecision-making-and-profiling/ http: //privacylawblog. fieldfisher. com/2015/getting-to-know-the-gdpr-part-4 -souped-up-individual-rights/ https: //www. dataprotection. ie/docs/EU-Directive-95 -46 -EC-Chapter-2/93. htm The GDPR (Regulation (EU) 2016/679) can be read at eur-lex. europa. eu. http: //www. eugdpr. org/the-regulation. html www. forcepoint. com/GDPR www. logrhythm. com https: //iapp. org/news/a/top-10 -operational-impacts-of-the-gdpr-part-1 -data-security-and-breach-notification/ Property of RB Advisory LLC 43
Q&A Property of RB Advisory LLC 44
Audience Poll With What you know now, is your organization impacted by the GDPR? q WHAT q YES q NO q Not Sure Property of RB Advisory LLC 45
Audience Poll If impacted, how confident are you that your organization will meet the requirements by May 2018? q Very Confident q Moderately Confident q Somewhat Confident q Not Confident Property of RB Advisory LLC 46
Contact: Regine Bonneau RB Advisory LLC rbonneau@rbadvisoryllc. com 407. 796. 8079 954. 330. 6015 www. rbadvisoryllc. com Property of RB Advisory LLC 47
- Slides: 47