
PERSONAL DATA PROTECTION ACT 2010 TO COMPLY IS

- Slides: 59
PERSONAL DATA PROTECTION ACT 2010 TO COMPLY IS TO KNOW Professor Abu Bakar Munir Faculty of Law, University of Malaya & Associate Professor Siti Hajar Mohd Yasin Faculty of Law, Universiti Teknologi MARA SEMINAR KESEDARAN AKTA PERLINDUNGAN DATA PERIBADI 9 February 2012 Kuala Lumpur 1
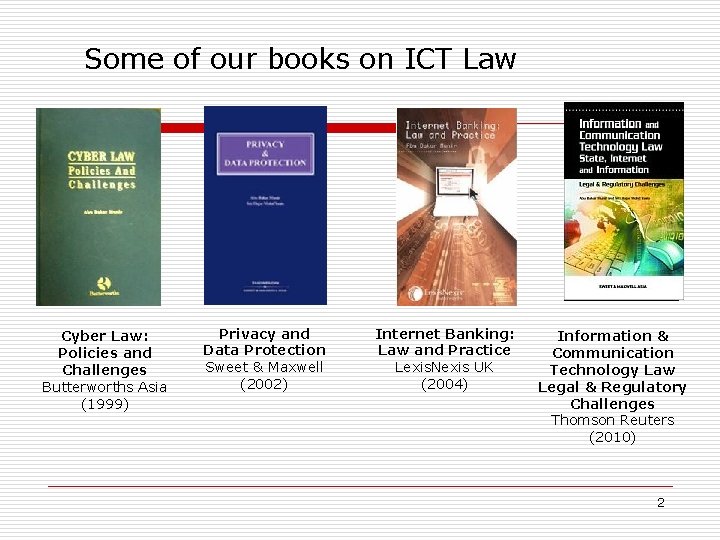
Some of our books on ICT Law In Print Cyber Law: Policies and Challenges Butterworths Asia (1999) Privacy and Data Protection Sweet & Maxwell (2002) Internet Banking: Law and Practice Lexis. Nexis UK (2004) Information & Communication Technology Law Legal & Regulatory Challenges Thomson Reuters (2010) 2
Please read this book.
THE WORLD’S GREATEST NEWSPAPER 1843 -2011 4
Reality Check o The efficiency of computer network has caused more and more personal data be stored in computers o The n n n o Users globally send around 47 billion (non-spam) emails and submits 95 millions tweets o Each month users share about 30 billion pieces of contents on facebook o Personal data is the new oil of the Internet and the new currency of the digital world o Greater concerns about privacy invasion world has reaped the benefits of the fast flow information and personal data: Ten years ago – gigabytes of data, Five years ago – terabytes of data, Today, petabytes of data, are being transferred and stored on daily basis. 6
7
8
Types of Privacy o o o The right to be left alone Bodily privacy Privacy of communications Territorial privacy Informational privacy
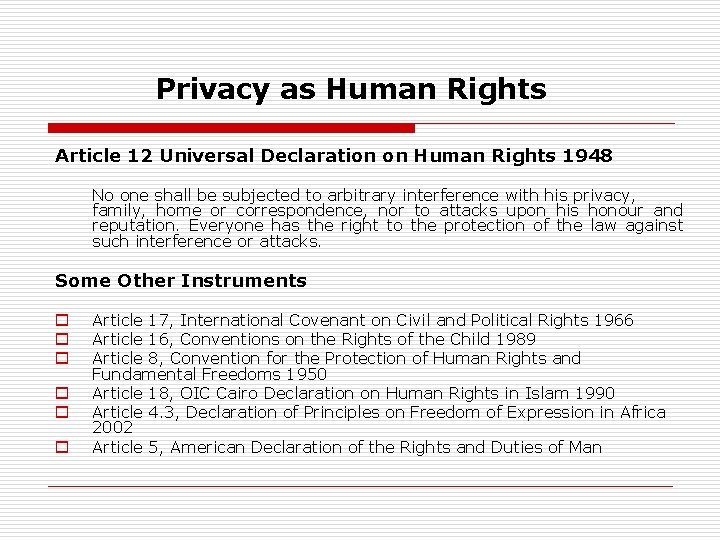
Privacy as Human Rights Article 12 Universal Declaration on Human Rights 1948 No one shall be subjected to arbitrary interference with his privacy, family, home or correspondence, nor to attacks upon his honour and reputation. Everyone has the right to the protection of the law against such interference or attacks. Some Other Instruments o o o Article 17, International Covenant on Civil and Political Rights 1966 Article 16, Conventions on the Rights of the Child 1989 Article 8, Convention for the Protection of Human Rights and Fundamental Freedoms 1950 Article 18, OIC Cairo Declaration on Human Rights in Islam 1990 Article 4. 3, Declaration of Principles on Freedom of Expression in Africa 2002 Article 5, American Declaration of the Rights and Duties of Man
Informational Privacy The rights of an individual to have control over his personal information Informational Privacy = Personal Data Protection
Why countries protect personal data? o o International obligation Competitiveness Human right International influence 12
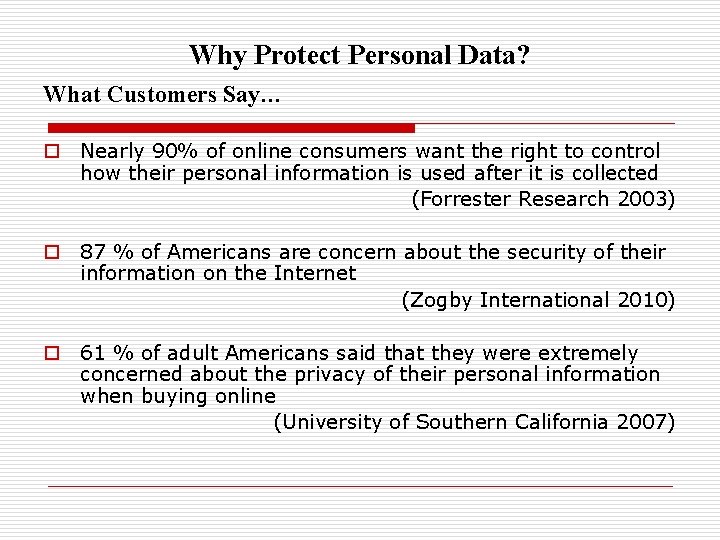
Why Protect Personal Data? What Customers Say… o Nearly 90% of online consumers want the right to control how their personal information is used after it is collected (Forrester Research 2003) o 87 % of Americans are concern about the security of their information on the Internet (Zogby International 2010) o 61 % of adult Americans said that they were extremely concerned about the privacy of their personal information when buying online (University of Southern California 2007)
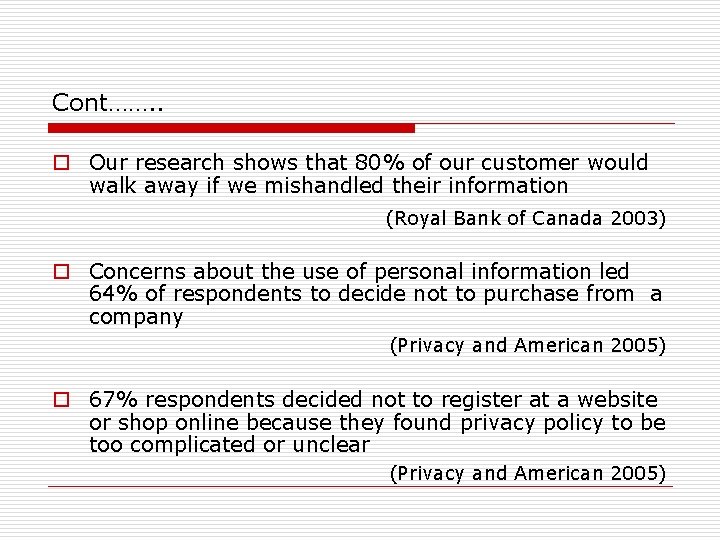
Cont……. . o Our research shows that 80% of our customer would walk away if we mishandled their information (Royal Bank of Canada 2003) o Concerns about the use of personal information led 64% of respondents to decide not to purchase from a company (Privacy and American 2005) o 67% respondents decided not to register at a website or shop online because they found privacy policy to be too complicated or unclear (Privacy and American 2005)
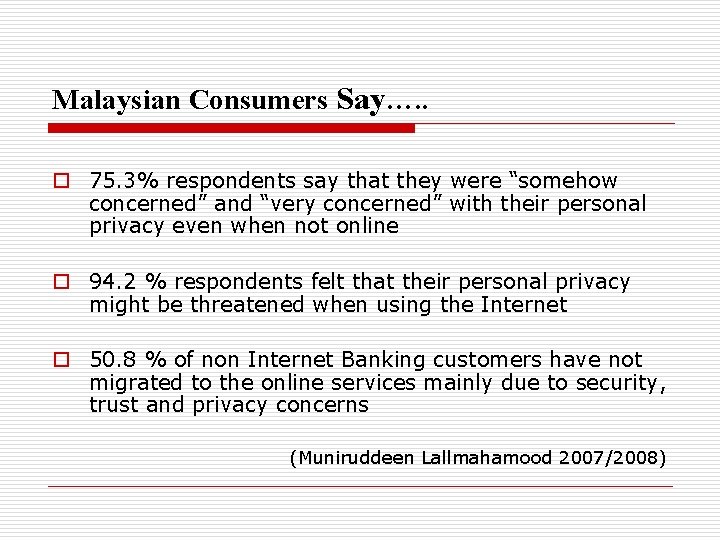
Malaysian Consumers Say…. . o 75. 3% respondents say that they were “somehow concerned” and “very concerned” with their personal privacy even when not online o 94. 2 % respondents felt that their personal privacy might be threatened when using the Internet o 50. 8 % of non Internet Banking customers have not migrated to the online services mainly due to security, trust and privacy concerns (Muniruddeen Lallmahamood 2007/2008)
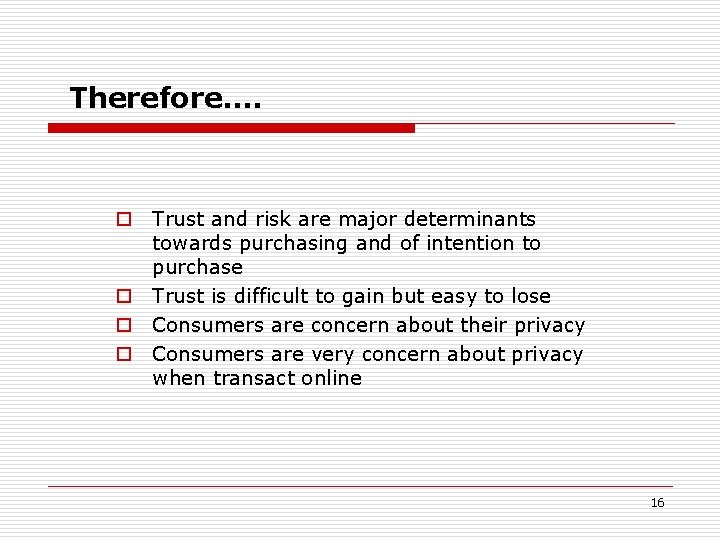
Therefore…. o Trust and risk are major determinants towards purchasing and of intention to purchase o Trust is difficult to gain but easy to lose o Consumers are concern about their privacy o Consumers are very concern about privacy when transact online 16
GOOD PRIVACY, GOOD BUSINESS “Privacy is good for business” Harriet Pearson IBM Chief Privacy Officer 17
How? Potential Risks o Breaches of data protection law o Damage to organization’s reputation and brand o Physical, psychological and economic harm to customers o Financial losses associated with deterioration in quality and integrity of personal data due to customers’ distrusts o Loss of market share or a drop in stock prizes due to negative publicity/ failure or delay in the implementation of new product / service due to privacy concern 18
Benefits o More positive organizational image and significant edge over the competition o Business development via expansion into jurisdiction requiring clear privacy standard o Enhanced data quality and integrity o Fostering better customer service and more strategic business decision making o Enhanced customer trusts and loyalty 19
20
21
(Reuters) - HSBC Holdings, Europe's biggest bank, was fined 3. 2 million pounds on Wednesday for information security breaches, the biggest fine the country's financial regulator has ever imposed for data security lapses. (2007, 2008) 22
Insurance giant Norwich Union has been fined £ 1. 26 million by the Financial Services Authority (FSA) for security systems failures (2007) 23
DATA PROTECTION COMMISSIONER’S OFFICE Press Release For immediate release Date: 13 November 2012 2007 XYZ SDN. BERHAD IS IN BREACH OF THE PERSONAL DATA PROTECTION ACT 2010 The Data Protection Commissioner's Office (DPCO) has found that the XYZ SDN. BERHAD is in beach of the Personal Data Protection Act 2010 following an investigation into the complaint of ……………………… ………AB H………. . DATA PROTECTION COMMISSIONER 24
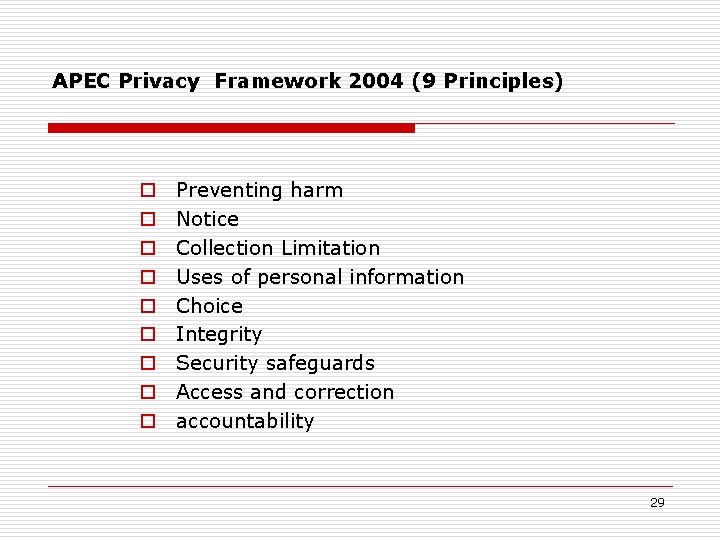
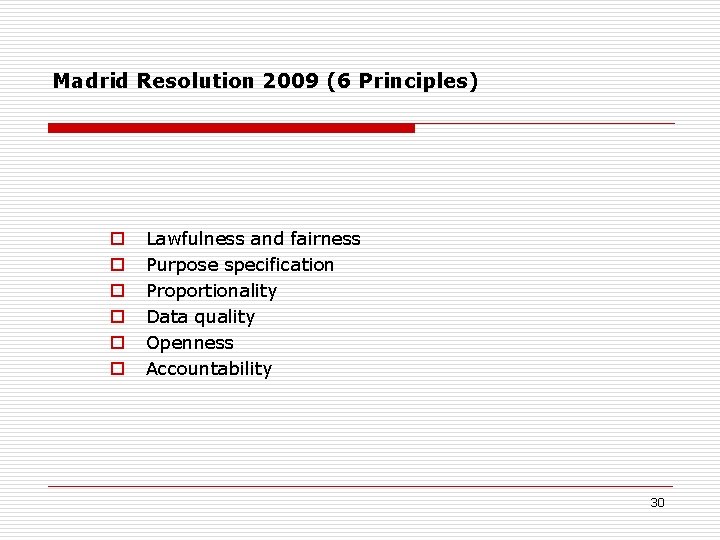
International Instruments o o o OECD Guidelines 1980 Council of Europe Convention 1981 European Directive 1995 APEC Privacy Framework 2004 Madrid Resolution 2009 EU Proposed Directive (25 Jan 2012) 25
OECD Guidelines 1980 (8 Principles) o o o o Collection limitation Data Quality Purpose Specification Use Limitation Security Openness Individual Participation Accountability 26
Council of Europe Convention 1981 Personal Data shall be: o obtained fairly and lawfully o stored for specified and legitimate purposes and not used in a way incompatible with those purposes o adequate, relevant and not excessive o accurate and, where necessary kept up to date o preserved in a form which permits identification of the data subjects for no longer than is required for the purpose for which those data are stored 27
European Directive 1995 Personal data must be; o Processed fairly and lawfully o Collected for specified, explicit and legitimate purposes and not further processed in a way incompatible with those purposes o adequate, relevant and not excessive o accurate and, where necessary kept up to date 28
APEC Privacy Framework 2004 (9 Principles) o o o o o Preventing harm Notice Collection Limitation Uses of personal information Choice Integrity Security safeguards Access and correction accountability 29
Madrid Resolution 2009 (6 Principles) o o o Lawfulness and fairness Purpose specification Proportionality Data quality Openness Accountability 30
EU Proposed Directive 31
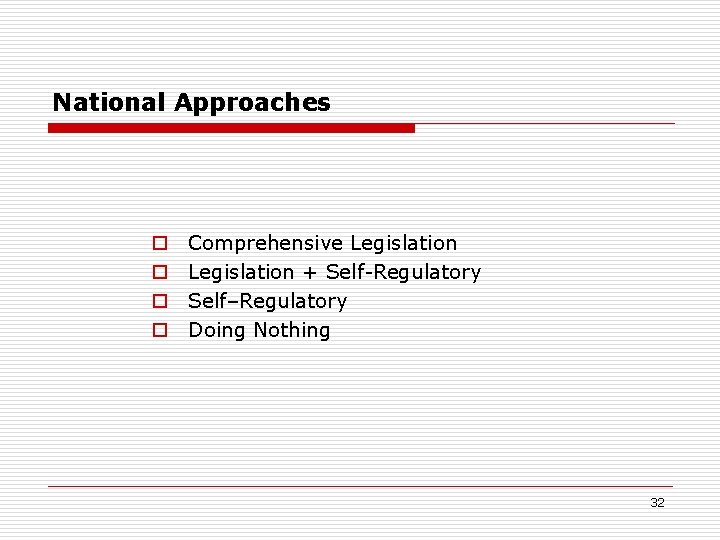
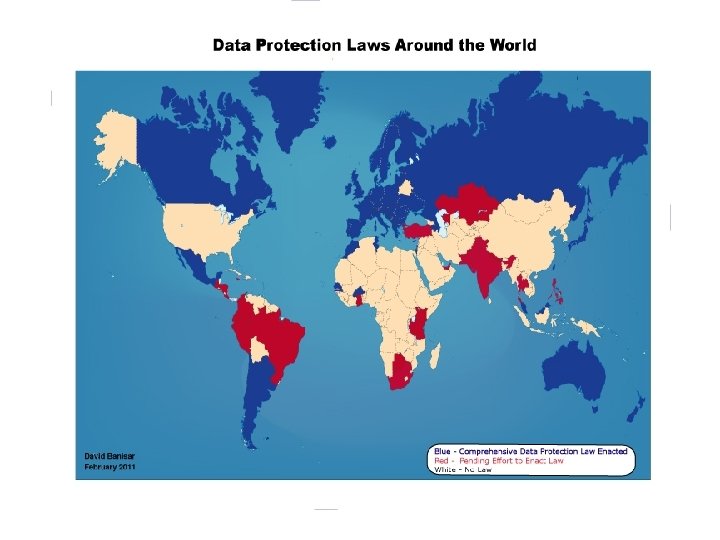
National Approaches o o Comprehensive Legislation + Self-Regulatory Self–Regulatory Doing Nothing 32
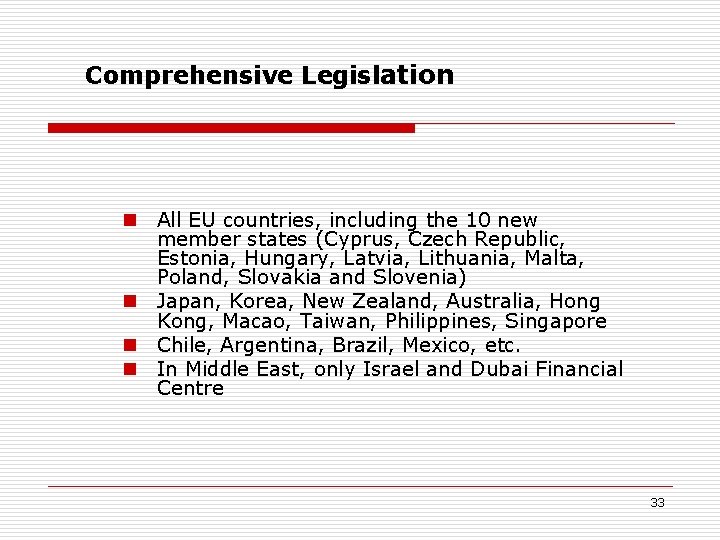
Comprehensive Legislation n All EU countries, including the 10 new member states (Cyprus, Czech Republic, Estonia, Hungary, Latvia, Lithuania, Malta, Poland, Slovakia and Slovenia) n Japan, Korea, New Zealand, Australia, Hong Kong, Macao, Taiwan, Philippines, Singapore n Chile, Argentina, Brazil, Mexico, etc. n In Middle East, only Israel and Dubai Financial Centre 33
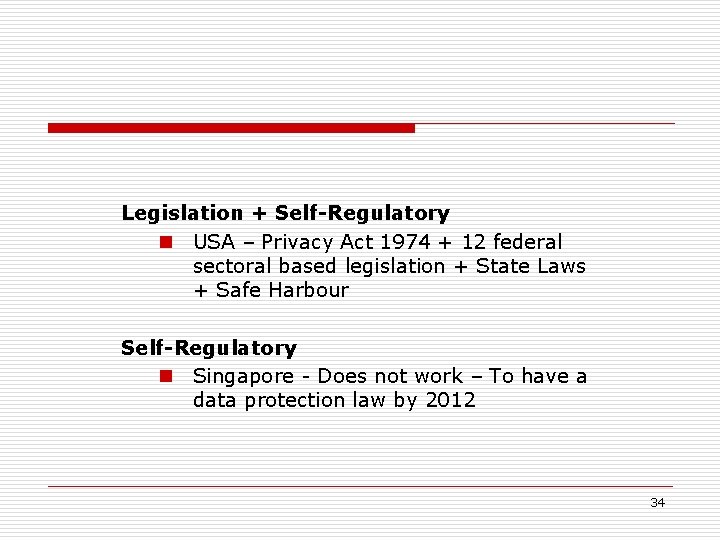
Legislation + Self-Regulatory n USA – Privacy Act 1974 + 12 federal sectoral based legislation + State Laws + Safe Harbour Self-Regulatory n Singapore - Does not work – To have a data protection law by 2012 34
Doing Nothing so far o o o Brunei Vietnam Laos Cambodia Many more 35
36
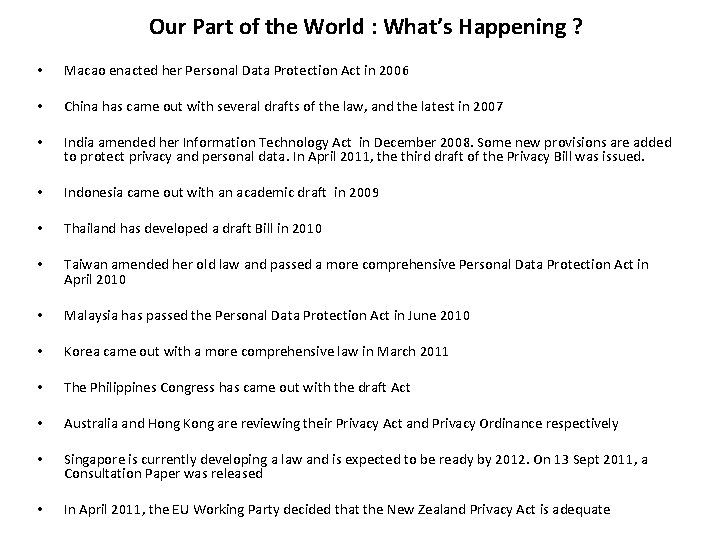
Our Part of the World : What’s Happening ? • Macao enacted her Personal Data Protection Act in 2006 • China has came out with several drafts of the law, and the latest in 2007 • India amended her Information Technology Act in December 2008. Some new provisions are added to protect privacy and personal data. In April 2011, the third draft of the Privacy Bill was issued. • Indonesia came out with an academic draft in 2009 • Thailand has developed a draft Bill in 2010 • Taiwan amended her old law and passed a more comprehensive Personal Data Protection Act in April 2010 • Malaysia has passed the Personal Data Protection Act in June 2010 • Korea came out with a more comprehensive law in March 2011 • The Philippines Congress has came out with the draft Act • Australia and Hong Kong are reviewing their Privacy Act and Privacy Ordinance respectively • Singapore is currently developing a law and is expected to be ready by 2012. On 13 Sept 2011, a Consultation Paper was released • In April 2011, the EU Working Party decided that the New Zealand Privacy Act is adequate
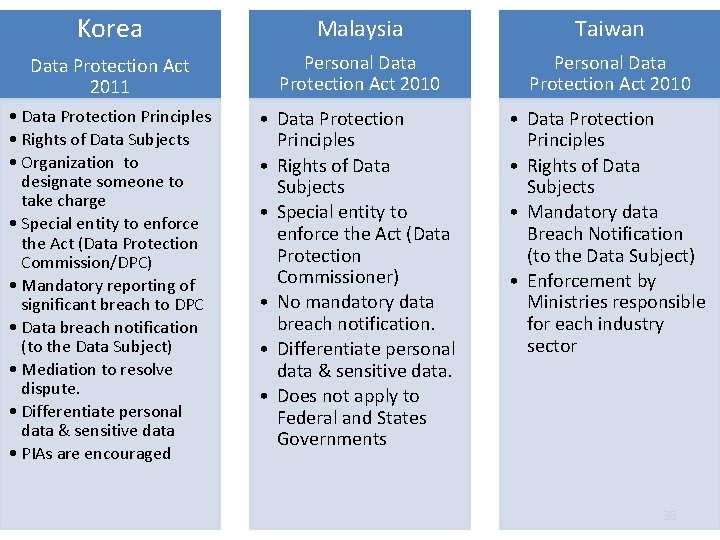
Korea Malaysia Taiwan Data Protection Act 2011 Personal Data Protection Act 2010 • Data Protection Principles • Rights of Data Subjects • Organization to designate someone to take charge • Special entity to enforce the Act (Data Protection Commission/DPC) • Mandatory reporting of significant breach to DPC • Data breach notification (to the Data Subject) • Mediation to resolve dispute. • Differentiate personal data & sensitive data • PIAs are encouraged • Data Protection Principles • Rights of Data Subjects • Special entity to enforce the Act (Data Protection Commissioner) • No mandatory data breach notification. • Differentiate personal data & sensitive data. • Does not apply to Federal and States Governments • Data Protection Principles • Rights of Data Subjects • Mandatory data Breach Notification (to the Data Subject) • Enforcement by Ministries responsible for each industry sector 38
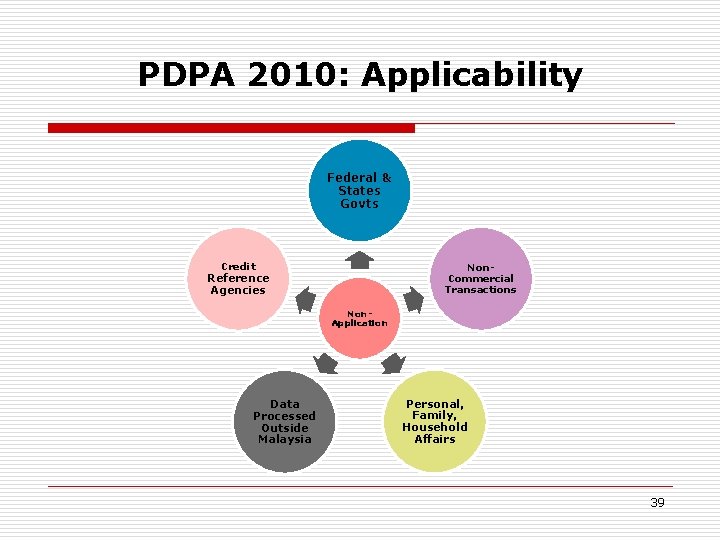
PDPA 2010: Applicability Federal & States Govts Credit Non. Commercial Transactions Reference Agencies Non. Application Data Processed Outside Malaysia Personal, Family, Household Affairs 39
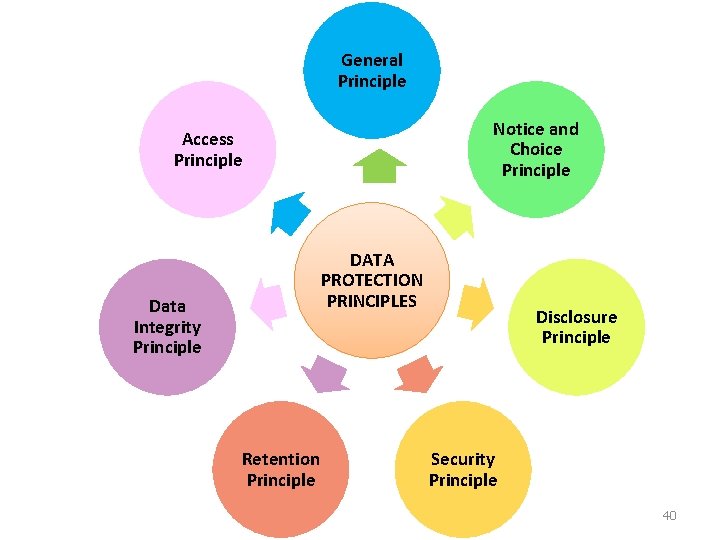
General Principle Notice and Choice Principle Access Principle DATA PROTECTION PRINCIPLES Data Integrity Principle Retention Principle Disclosure Principle Security Principle 40
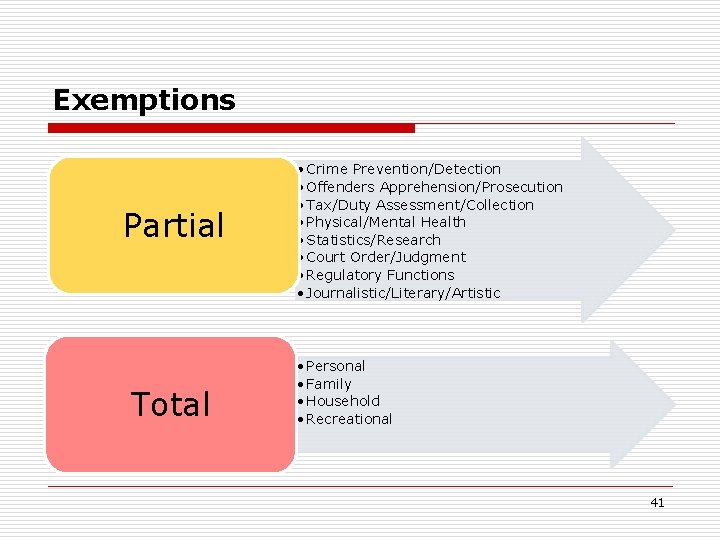
Exemptions Partial Total • Crime Prevention/Detection • Offenders Apprehension/Prosecution • Tax/Duty Assessment/Collection • Physical/Mental Health • Statistics/Research • Court Order/Judgment • Regulatory Functions • Journalistic/Literary/Artistic • Personal • Family • Household • Recreational 41
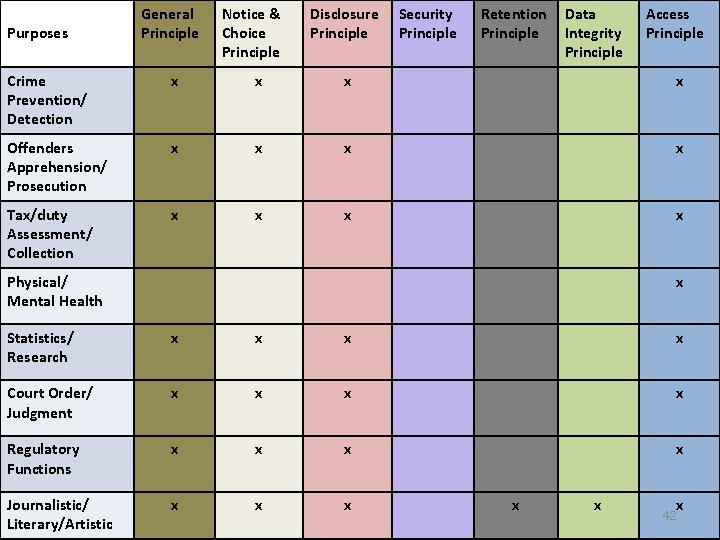
Purposes General Principle Notice & Choice Principle Disclosure Principle Security Principle Retention Principle Data Integrity Principle Access Principle Crime Prevention/ Detection x x Offenders Apprehension/ Prosecution x x Tax/duty Assessment/ Collection x x Physical/ Mental Health x Statistics/ Research x x Court Order/ Judgment x x Regulatory Functions x x Journalistic/ Literary/Artistic x x x 42
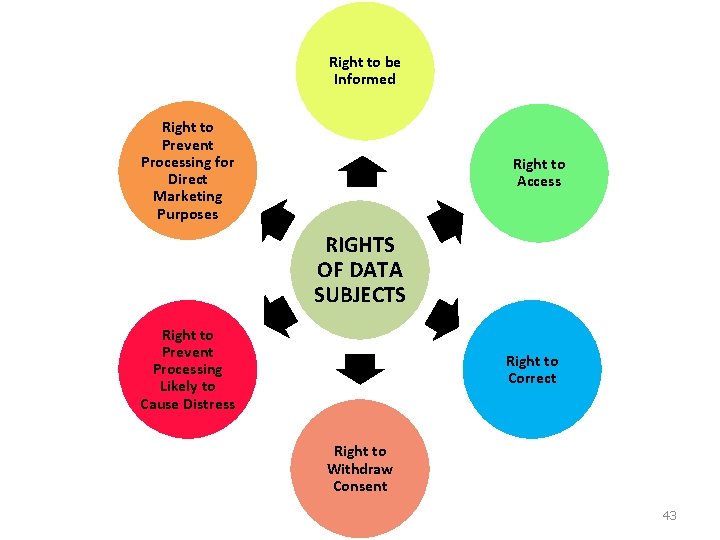
Right to be Informed Right to Prevent Processing for Direct Marketing Purposes Right to Access RIGHTS OF DATA SUBJECTS Right to Prevent Processing Likely to Cause Distress Right to Correct Right to Withdraw Consent 43
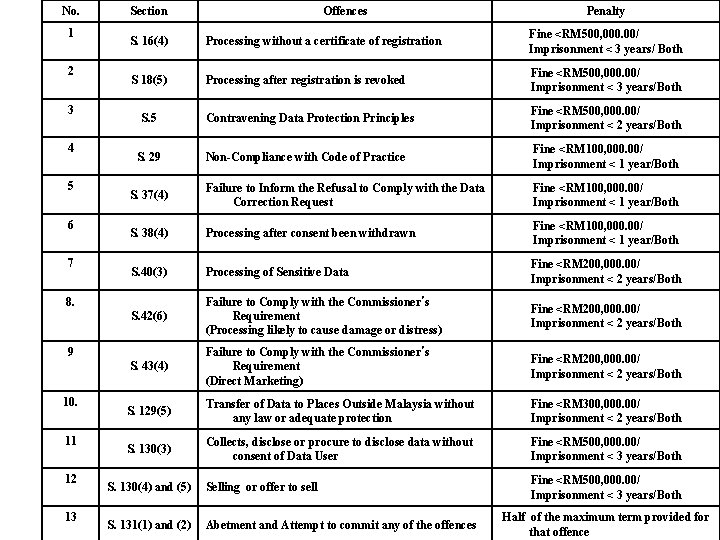
No. 1 2 3 4 5 6 7 Section Processing without a certificate of registration Fine <RM 500, 000. 00/ Imprisonment < 3 years/ Both S 18(5) Processing after registration is revoked Fine <RM 500, 000. 00/ Imprisonment < 3 years/Both Contravening Data Protection Principles Fine <RM 500, 000. 00/ Imprisonment < 2 years/Both Non-Compliance with Code of Practice Fine <RM 100, 000. 00/ Imprisonment < 1 year/Both S. 37(4) Failure to Inform the Refusal to Comply with the Data Correction Request Fine <RM 100, 000. 00/ Imprisonment < 1 year/Both S. 38(4) Processing after consent been withdrawn Fine <RM 100, 000. 00/ Imprisonment < 1 year/Both S. 40(3) Processing of Sensitive Data Fine <RM 200, 000. 00/ Imprisonment < 2 years/Both S. 42(6) Failure to Comply with the Commissioner’s Requirement (Processing likely to cause damage or distress) Fine <RM 200, 000. 00/ Imprisonment < 2 years/Both S. 43(4) Failure to Comply with the Commissioner’s Requirement (Direct Marketing) Fine <RM 200, 000. 00/ Imprisonment < 2 years/Both S. 129(5) Transfer of Data to Places Outside Malaysia without any law or adequate protection Fine <RM 300, 000. 00/ Imprisonment < 2 years/Both S. 130(3) Collects, disclose or procure to disclose data without consent of Data User Fine <RM 500, 000. 00/ Imprisonment < 3 years/Both S. 130(4) and (5) Selling or offer to sell Fine <RM 500, 000. 00/ Imprisonment < 3 years/Both S. 131(1) and (2) Abetment and Attempt to commit any of the offences S. 5 S. 29 9 11 12 13 Penalty S. 16(4) 8. 10. Offences Half of the maximum term provided for that offence
Offences by a body corporate A director, chief executive officer, chief operating officer, manager, secretary; or other similar officer of the body corporate or was purporting to act in any such capacity or was in any manner or to any extent responsible for the management of any of the affairs of the body corporate or was assisting in such management - may be charged severally or jointly in the same proceeding with the body corporate; and If the body corporate is found to have committed the offence, he shall be deemed to have committed the offences unless, having regard to the nature of his functions in that capacity and to all circumstances, he proves : that the offences was committed without his knowledge, consent or connivance; and that he had taken all reasonable precautions and exercised due diligence to prevent the commission of the offence. (s. 133) 45
Abetment and Attempt to Commit Offence A person who abets the data user in the commission of any offence under this Act commits an offence, and shall, on conviction, be liable to the punishment provided for that offence. (s. 132(1) A person who attempts to commit an offence punishable under this Act commits an offence and shall be liable to imprisonment not exceeding one half of the maximum term provided for that offence. 46
Transfer of Data to Outside Malaysia What PDPA says… o Sect 129 No transfer unless to such places specified by the Minister o The Minister may specify if: a) there is a law substantially similar to PDPA, or b) there is a law that serves the same purpose as PDPA, or c) that place ensures an adequate level of protection equivalent to the protection afforded by PDPA
Enforcement Mechanisms o o o o Data Protection Commissioner Advisory Committee Appeal Tribunal Codes of Practice Enforcement Notice Prosecution Revocation of Registration 48
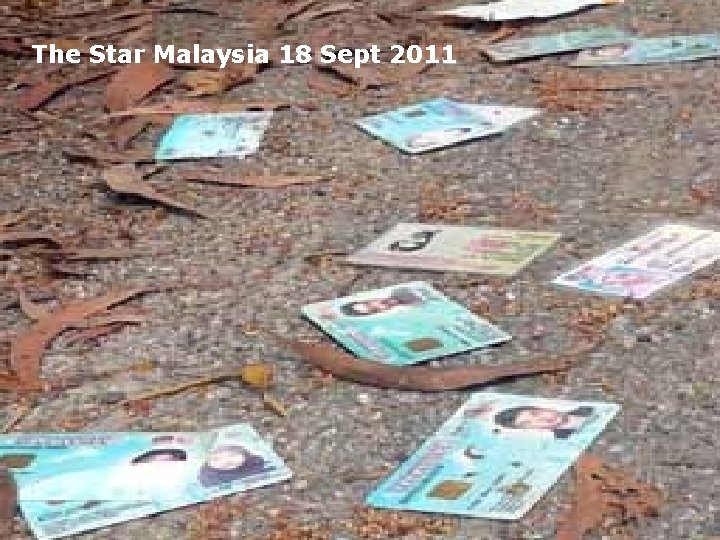
Enough is Enough 49
The Star Malaysia 18 Sept 2011 50
Telco A o “Personal information held by Telco A may include your name, date of birth, current address, telephone/mobile phone number, email address, credit cards details, occupation, user ID or password… as well as certain details about your personal interest. ” o “Telco A complies with and is registered under the data protection law in Malaysia and…” 51
Bank A “Any information sent to Bank A Bhd through the use of this site will be deemed not to be confidential and be deemed to remain the property of Bank A Bhd who shall be free to use, copy, publish, reproduce, distribute and/or transmit all such information at Bank A Bhd’s absolute discretion for any purpose and…” 52
Bank C “Bank C Group may also use your personal information to market Bank C Group’s products, and services to you based on your interest and…” “Our use of your information may also extend to other purposes… which may at our sole discretion be made available to our third party vendors, advertisers, affiliates or relevant third parties” 53
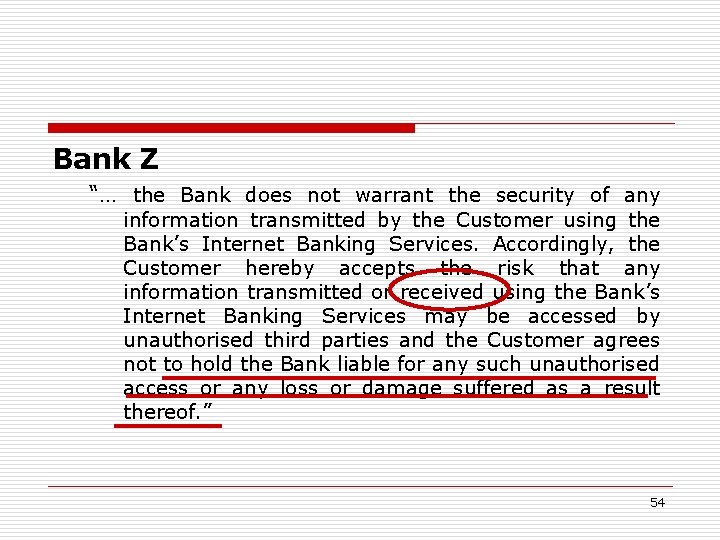
Bank Z “… the Bank does not warrant the security of any information transmitted by the Customer using the Bank’s Internet Banking Services. Accordingly, the Customer hereby accepts the risk that any information transmitted or received using the Bank’s Internet Banking Services may be accessed by unauthorised third parties and the Customer agrees not to hold the Bank liable for any such unauthorised access or any loss or damage suffered as a result thereof. ” 54
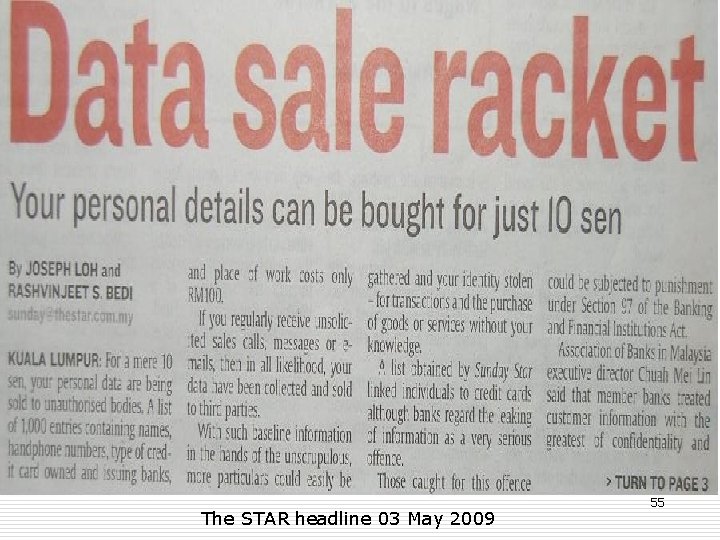
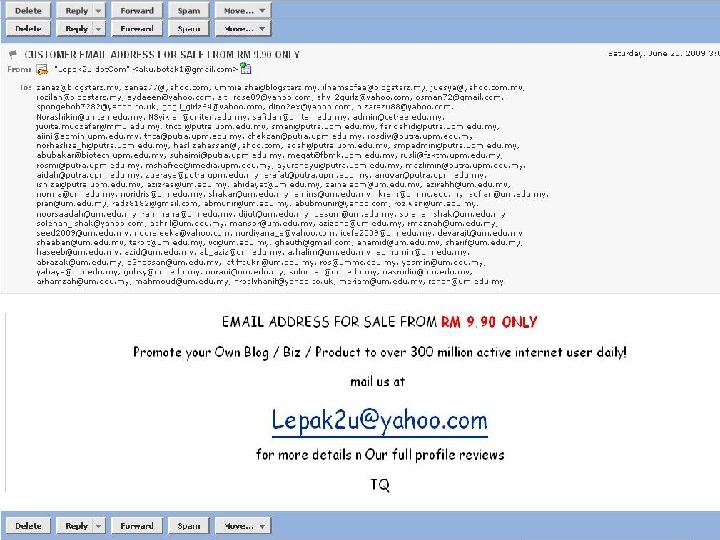
The STAR headline 03 May 2009 55
56
57
58
abmunir@um. edu. my http: //profabm. blogspot. com +60122185242 sitihajar 425@salam. uitm. edu. my +60123455537 59