
Page 1 California Dental Association HIPAA Privacy Officer
- Slides: 66
Page 1 | California Dental Association
HIPAA Privacy Officer and Security Officer: Overview of Responsibilities Page 2 | California Dental Association
Disclaimer This presentation is a summary of federal and California privacy, security and breach notification laws as they apply to California dental practices. It is intended to provide basic information so you understand the scope of the requirements. Additional resources are provided throughout the presentation and links to applicable laws are provided at the end. You should consult with your own attorney on questions specific to your situation. General inquiries can be directed to CDA Practice Support at practicesupport@cda. org. Page 3 | California Dental Association
Objectives • Understand key elements of HIPAA and state privacy laws. • Know which responsibilities are shared by the dental practice privacy officer and security officer. • Privacy officer and security officer understand their respective separate responsibilities. • Know training topics for staff. • Identify HIPAA business associates. Page 4 | California Dental Association
Acronyms HIPAA HITECH Health Information Portability and Accountability Act Health Information Technology for Economic and Clinical Health (the law that amended HIPAA) CMIA Confidentiality of Medical Information Act (state law) HHS OCR U. S. Dept. of Health & Human Services Office of Civil Rights (the enforcement agency) PHI/e. PHI Protected health information/electronic PHI (individually identifiable information linked to health information or health care entity) CE Covered entity (entities that conduct certain transactions electronically and therefore must comply with HIPAA) BA/BAA Business associate/business associate agreement Page 5 | California Dental Association
Definitions Minimum necessary – Standard for using or disclosing PHI; only use or disclose the minimum necessary information to complete the task. Safeguards – Policies, procedures and actions that ensure the privacy, confidentiality, integrity and availability of patient information. Incidental use/disclosure – Allowed if use/disclosure cannot be reasonably prevented and the individual or entity utilizes the minimum necessary rule. Examples: calling patient name in reception area without stating purpose of appointment; reminder postcards. Workforce – Individuals who work for a covered entity or at the CE’s facility; include employees, volunteers, students, independent contractors. Page 6 | California Dental Association
The Laws HIPAA Privacy • Establishes which uses/disclosures of PHI are: – Required. – Permitted without patient authorization. – Prohibited unless patient authorization is obtained. • Establishes patient rights. • Requires the use of privacy safeguards. Page 7 | California Dental Association
The Laws HIPAA Security • Focuses on technology and managing e. PHI. • Sets specific requirements (safeguards) to ensure the confidentiality, integrity and availability of e. PHI. • Requires a comprehensive risk analysis and risk management plan. • Requires continuous assessment and management of risks. Page 8 | California Dental Association
The Laws HIPAA and California Breach Notification requirements: • Require notification of individuals, government agencies and the media when certain information is breached. California laws: • Confidentiality of Medical Information Act and other privacy laws place greater restrictions than HIPAA in certain situations. • California Consumer Protection Act does not apply to information regulated by HIPAA or CMIA. Page 9 | California Dental Association
What is protected by HIPAA? Individually identifiable health information that is a subset of health information, including demographic information collected from an individual, and: i. Created or received by a health care provider, health plan, employer or health care clearinghouse. ii. Relates to the: • Past, present or future physical or mental health condition of an individual. • The provision of health care to an individual. • The past, present or future payment for the provision of health care to an individual. iii. Identifies the individual. iv. With respect to which there is a reasonable basis to believe the information can be used to identify the individual. Page 10 | California Dental Association
What is protected by state law? A person’s first name or first initial and last name in combination with any of the following: • Social Security number. • Driver’s license number or California identification card number. • Account number, credit/debit card number, in combination with any required security code, access code or password that would allow access to the person’s financial account. Page 11 | California Dental Association
• Medical information, defined as “any information regarding an individual’s medical history, mental or physical condition, or medical treatment or diagnosis by a health care professional. ” • Health insurance information, defined as “an individual’s health insurance policy number or subscriber identification number, any unique identifier used by a health insurer to identify the individual or any information in an individual’s application and claims history, including any appeals records. ” • Username or email address in combination with a password or security question and answer that would permit access to an online account. Page 12 | California Dental Association
Who must comply? CMIA All health care providers. HIPAA Covered entity (CE): A health care provider, health plan or health care clearinghouse that conducts certain transactions electronically. Those transactions include filing claims, using a claims clearinghouse that files electronically, checking patients’ eligibility or benefits, seeking approval for care, checking status of a claim and more. Business associate: An individual or organization that uses PHI to provide a nonclinical service to the CE. Page 13 | California Dental Association
Who is responsible for PHI privacy and security? EVERYONE The workforce includes: • Employees. • Independent contractors working within the facility. • Students, interns and other unpaid workers in the practice. • Vendors who use PHI to perform work on behalf of the practice. Page 14 | California Dental Association
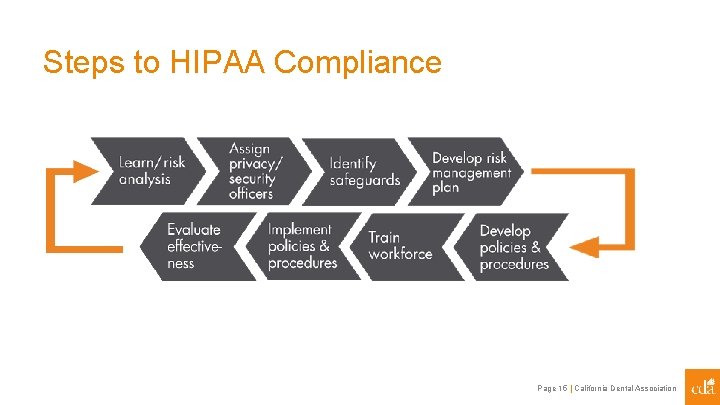
Steps to HIPAA Compliance Page 15 | California Dental Association
Responsibilities Page 16 | California Dental Association
Shared Responsibilities • Analyze how and identify where PHI is received, sent and stored. • Review compliance requirements and develop policies and procedures. • Using minimum necessary rule, determine workforce access to PHI. • Identify business associates and execute business associate agreements. Page 17 | California Dental Association
Shared Responsibilities • Train workforce and highlight sanction policy. • Periodically review effectiveness of policies and procedures; revise as needed. • Conduct breach assessment and, if necessary, notify patients, regulatory agencies and the media. (See “Breach Assessment & Notification” presentation on cda. org/practicesupport. ) Page 18 | California Dental Association
Privacy Officer Responsibilities Includes but is not limited to: • Creating practice-specific Notice of Privacy Practices. • Receiving/responding to inquiries and complaints on practice’s privacy practices. • Receiving/processing requests for access to patient information and for amendments to that information. • Completing documentation and retaining for minimum of six years. • Applying workforce sanctions/discipline in conjunction with practice owner or office manager. • Auditing compliance with practice policies and procedures. Page 19 | California Dental Association
Security Officer Responsibilities • Conduct initial risk analysis that is accurate and thorough, then develop a risk management plan. (See “How to do a HIPAA Risk Analysis” presentation on cda. org/practicesupport. ) • Conduct periodic risk and mitigation assessments. • Ensure practice implementation of required and addressable HIPAA Security Rule safeguards, including: § Establishing access controls/restrictions. § Regular system auditing and monitoring. § Security incident documentation and response. • Monitor/audit access to e. PHI, security incidents. Page 20 | California Dental Association
Develop Policies and Procedures Page 21 | California Dental Association
Options for developing policies and procedures 1. ADA Complete HIPAA Compliance Kit (purchase from ADA Store) and CDA-provided template (free by emailing copy of ADA receipt to practicesupport@cda. org). 2. Consultant-provided template. 3. Develop from scratch. Page 22 | California Dental Association
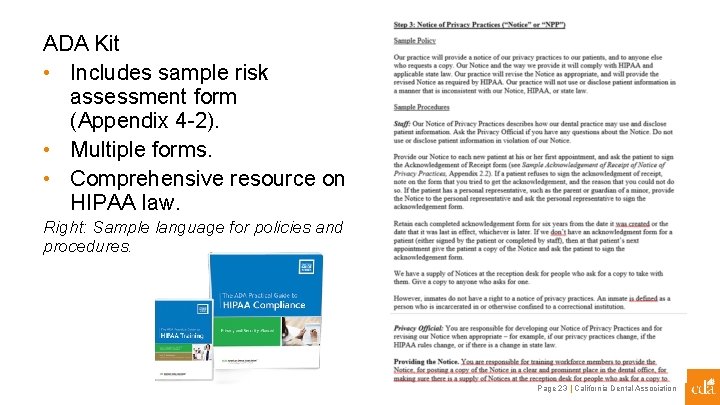
ADA Kit • Includes sample risk assessment form (Appendix 4 -2). • Multiple forms. • Comprehensive resource on HIPAA law. Right: Sample language for policies and procedures. Page 23 | California Dental Association
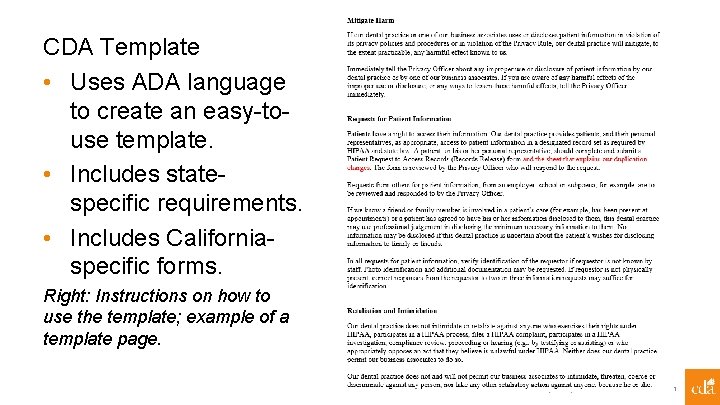
CDA Template • Uses ADA language to create an easy-touse template. • Includes statespecific requirements. • Includes Californiaspecific forms. Right: Instructions on how to use the template; example of a template page. Page 24 | California Dental Association
CDA Template • Organized to allow all workforce members to review the policies and procedures they need to know in the first third of the document. • Remainder of the document provides detailed policies and procedures on how the dental practice complies with applicable privacy and security laws. Both the privacy and security officers contribute to its creation and ensure workforce compliance. Page 25 | California Dental Association
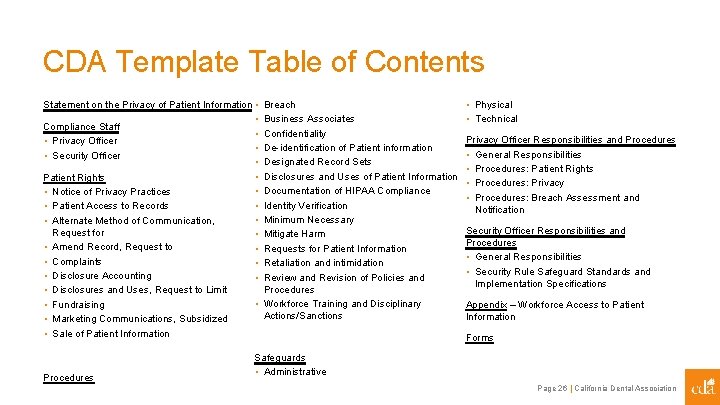
CDA Template Table of Contents Statement on the Privacy of Patient Information • Breach • Business Associates Compliance Staff • Confidentiality • Privacy Officer • De-identification of Patient information • Security Officer • Designated Record Sets • Disclosures and Uses of Patient Information Patient Rights • Documentation of HIPAA Compliance • Notice of Privacy Practices • Identity Verification • Patient Access to Records • Minimum Necessary • Alternate Method of Communication, Request for • Mitigate Harm • Amend Record, Request to • Requests for Patient Information • Complaints • Retaliation and intimidation • Disclosure Accounting • Review and Revision of Policies and Procedures • Disclosures and Uses, Request to Limit • Workforce Training and Disciplinary • Fundraising Actions/Sanctions • Marketing Communications, Subsidized • Sale of Patient Information Procedures • Physical • Technical Privacy Officer Responsibilities and Procedures • General Responsibilities • Procedures: Patient Rights • Procedures: Privacy • Procedures: Breach Assessment and Notification Security Officer Responsibilities and Procedures • General Responsibilities • Security Rule Safeguard Standards and Implementation Specifications Appendix – Workforce Access to Patient Information Forms Safeguards • Administrative Page 26 | California Dental Association
Policy and Procedure Review • Policies and procedures must be reviewed on a regular basis and revised as necessary. Annual review is recommended and not required. • Policies and procedures should be reviewed after any incident involving impermissible use, disclosure, destruction or alteration of PHI and when the covered entity changes operational procedures involving PHI. Page 27 | California Dental Association
Documentation Retention HIPAA-related documents must be retained for six years from the date of the event or from the date policy or procedure was last in effect. These documents include but are not limited to: • • • Policies and procedures. List of designated record sets. Risk analysis. Risk management plan. Workforce training/sanctions/information access level. Access requests. Patient complaints and inquiries and covered entity’s responses. Patient authorizations for uses or disclosures of PHI. Patient requests for alternate method of communication, record amendment, disclosure accounting. Business associate agreements. Security and audit logs and reports. Breach assessment, notification and follow-up documentation. Page 28 | California Dental Association
Determine Workforce Access Levels Page 29 | California Dental Association
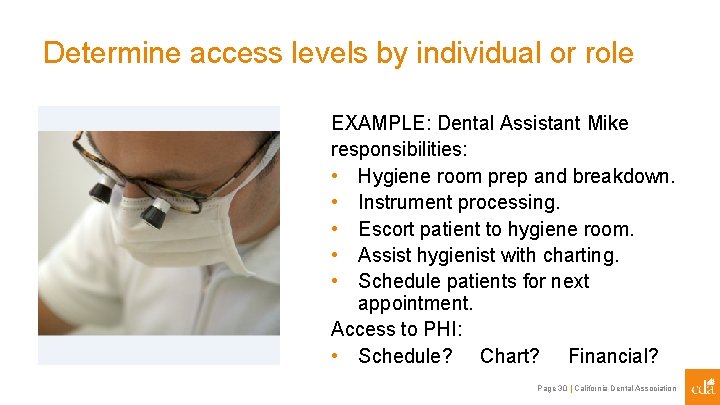
Determine access levels by individual or role EXAMPLE: Dental Assistant Mike responsibilities: • Hygiene room prep and breakdown. • Instrument processing. • Escort patient to hygiene room. • Assist hygienist with charting. • Schedule patients for next appointment. Access to PHI: • Schedule? Chart? Financial? Page 30 | California Dental Association
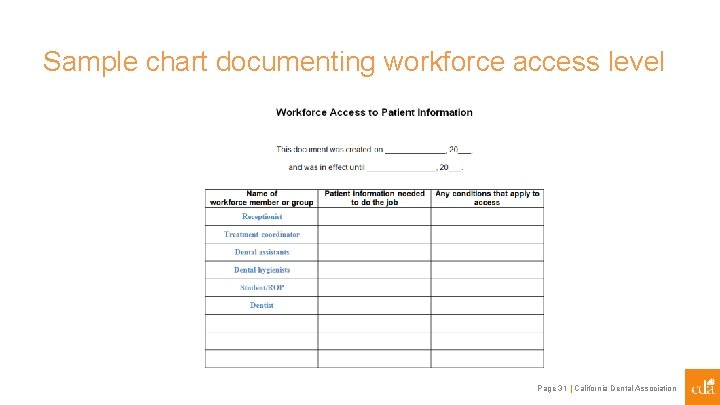
Sample chart documenting workforce access level Page 31 | California Dental Association
Identify Business Associates Page 32 | California Dental Association
Business Associates A HIPAA business associate is an individual or organization that uses or accesses a covered entity’s patient information in the course of performing work (typically nonclinical) on behalf of the covered entity. • Identify and document information about them. • Secure a signed business associate agreement. Page 33 | California Dental Association
Who is a HIPAA business associate? • Claims clearinghouse. • Practice management software vendor. • Cloud provider for data backup and storage. • Practice management consultant. • Third-party document/device shredding company. • Voice over internet protocol (VOIP) provider. • Upon accessing PHI — professional liability carrier, accountant, attorney, bookkeeper. Not business associates: • Dental labs. • Cleaning crew – does not need to use or access patient information to do their job; assumes covered entity takes reasonable steps to safeguard information. • Independent contractor dentists – may be treated as workforce. • Speech/language interpreters – may be treated as workforce. Page 34 | California Dental Association
Business Associate Tracking A covered entity may want to collect in a single document the following information: • Business associate name and address. • Contact name, telephone number and email address. • For what purpose the company/individual is using or accessing the dental practice’s patient information. • Description of the patient information used. • Date contract and business associate agreement were executed. • Expiration date of contract and business associate agreement. • Subcontractor names and nature of the work. • Applicable security issues, for example, remote access. • Whether auditing is conducted and, if yes, types of audits. • Cyber liability coverage if applicable. Page 35 | California Dental Association
Business Associate Agreement Should contain the following elements: 1. Establish the permitted and required uses and disclosures of protected health information by the business associate. 2. Provide that the business associate will not use or further disclose the information other than as permitted or required by the contract or as required by law. 3. Require the business associate to implement appropriate safeguards to prevent unauthorized use or disclosure of the information, including implementing requirements of the Security Rule. 4. Require the business associate to report to the covered entity within a specified period any use or disclosure of the information not provided for by its agreement, including incidents that constitute breaches of unsecured protected health information. 5. Require the business associate to disclose protected health information as specified in its agreement to satisfy a covered entity’s obligation with respect to individuals' requests for copies of their protected health information, as well as make available protected health information for amendments (and incorporate any amendments, if required) and accountings. Page 36 | California Dental Association
Business Associate Agreement 6. To the extent the business associate is to carry out a covered entity’s obligation under the Privacy Rule, require the business associate to comply with the requirements applicable to the obligation. 7. Require the business associate to make available to HHS its internal practices, books and records relating to the use and disclosure of protected health information received from, or created or received by the business associate on behalf of, the covered entity for purposes of HHS determining the covered entity’s compliance with the Privacy Rule. 8. At termination of the business relationship, if feasible, require the business associate to return or destroy all protected health information received from or created or received by the business associate on behalf of the covered entity. 9. Require the business associate to ensure that any subcontractors it may engage on its behalf that will have access to protected health information agree to the same restrictions and conditions that apply to the business associate with respect to such information. 10. Authorize termination of the agreement by the covered entity if the business associate violates a material term of the agreement. Sample agreement is available at cda. org/practicesupport Page 37 | California Dental Association
Train Workforce Page 38 | California Dental Association
Workforce Training Types of training: • Train the trainer (privacy and security officers). • Workforce training: Reading/reviewing office policies and procedures is adequate in many cases. Frequency of training: • Upon hire, before accessing PHI. • As often as needed to ensure staff comprehension and compliance. • When law, policies and procedures change. Page 39 | California Dental Association
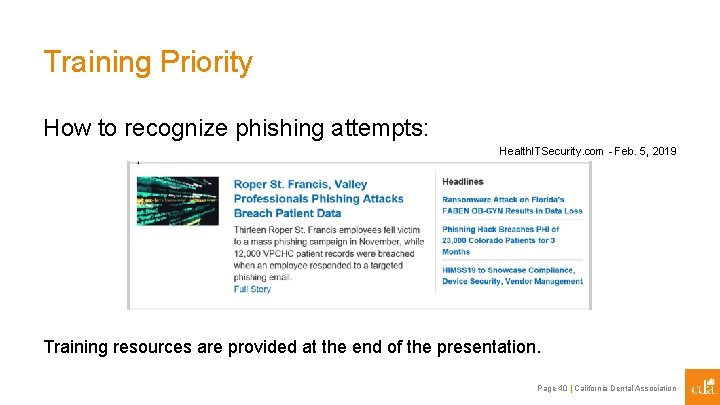
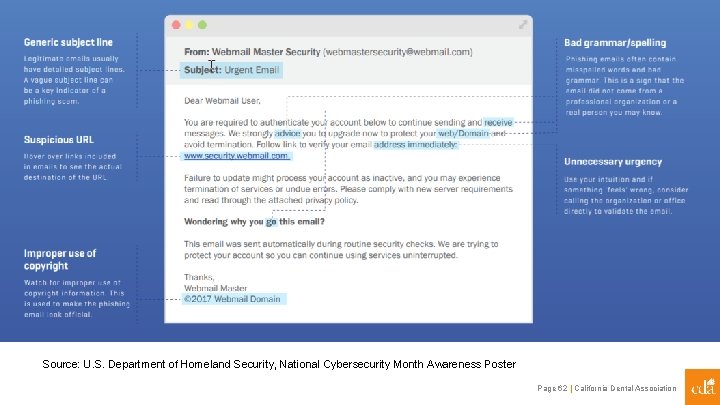
Training Priority How to recognize phishing attempts: Health. ITSecurity. com - Feb. 5, 2019 Training resources are provided at the end of the presentation. Page 40 | California Dental Association
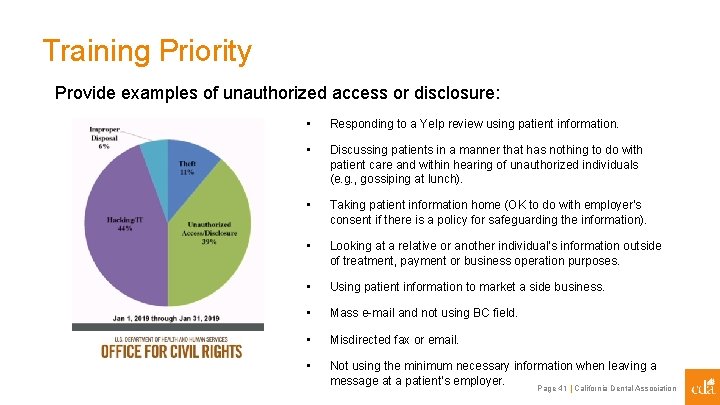
Training Priority Provide examples of unauthorized access or disclosure: • Responding to a Yelp review using patient information. • Discussing patients in a manner that has nothing to do with patient care and within hearing of unauthorized individuals (e. g. , gossiping at lunch). • Taking patient information home (OK to do with employer’s consent if there is a policy for safeguarding the information). • Looking at a relative or another individual’s information outside of treatment, payment or business operation purposes. • Using patient information to market a side business. • Mass e-mail and not using BC field. • Misdirected fax or email. • Not using the minimum necessary information when leaving a message at a patient’s employer. Page 41 | California Dental Association
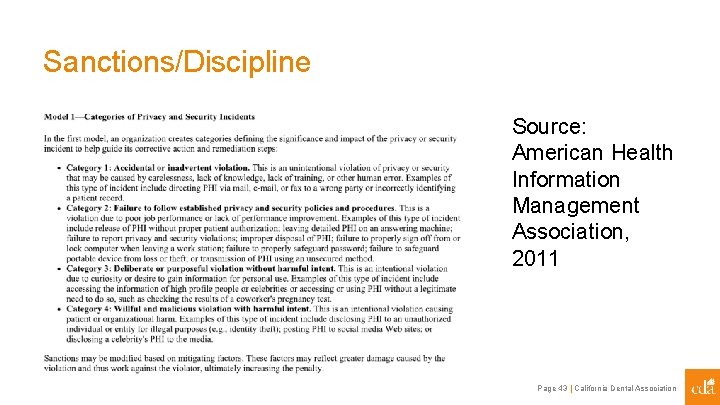
Workforce Sanctions A covered entity must have a policy requiring that workforce members comply with practice policies, procedures and safeguards and stating that it will apply sanctions against workforce members who violate them. Applied sanctions must be documented. The following slide is a model of a sanction policy. Page 42 | California Dental Association
Sanctions/Discipline Source: American Health Information Management Association, 2011 Page 43 | California Dental Association
Enforcement Information Page 44 | California Dental Association
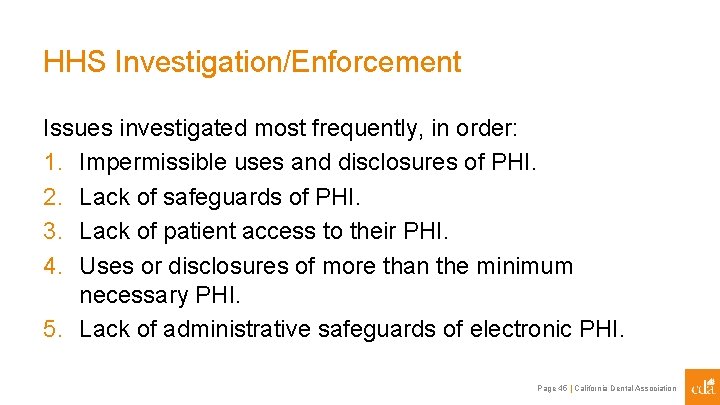
HHS Investigation/Enforcement Issues investigated most frequently, in order: 1. Impermissible uses and disclosures of PHI. 2. Lack of safeguards of PHI. 3. Lack of patient access to their PHI. 4. Uses or disclosures of more than the minimum necessary PHI. 5. Lack of administrative safeguards of electronic PHI. Page 45 | California Dental Association
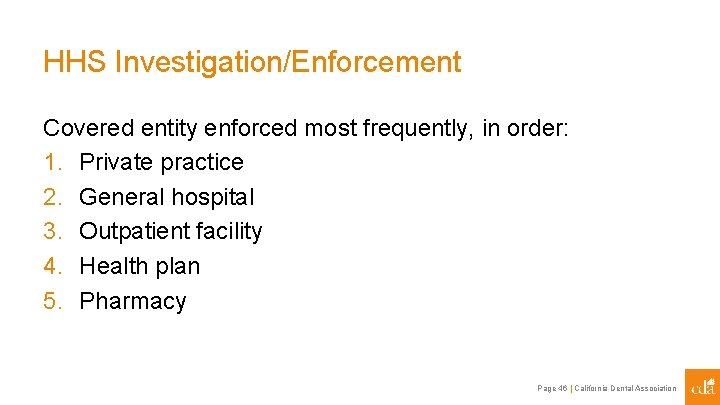
HHS Investigation/Enforcement Covered entity enforced most frequently, in order: 1. Private practice 2. General hospital 3. Outpatient facility 4. Health plan 5. Pharmacy Page 46 | California Dental Association
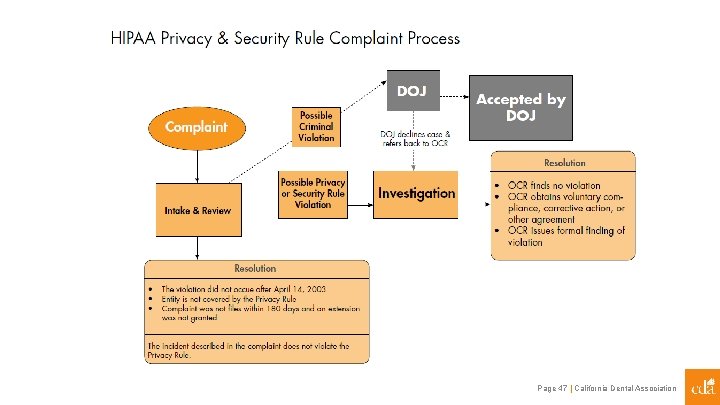
Page 47 | California Dental Association
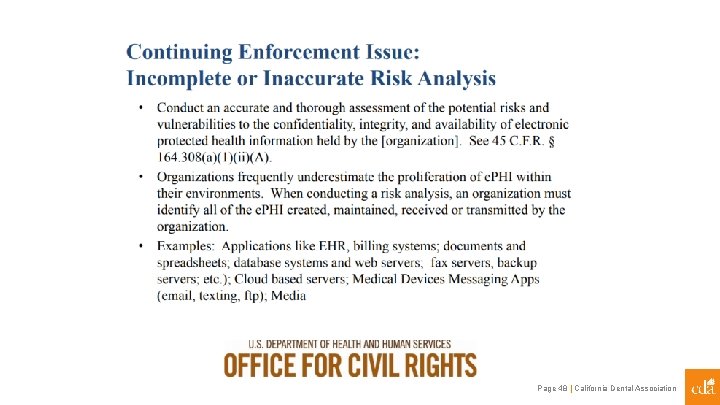
Page 48 | California Dental Association
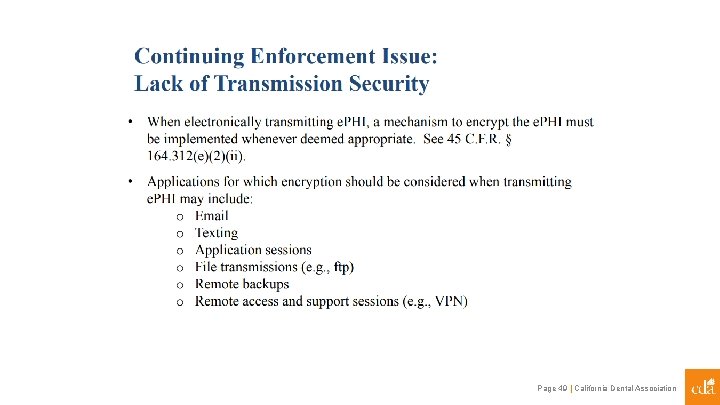
Page 49 | California Dental Association
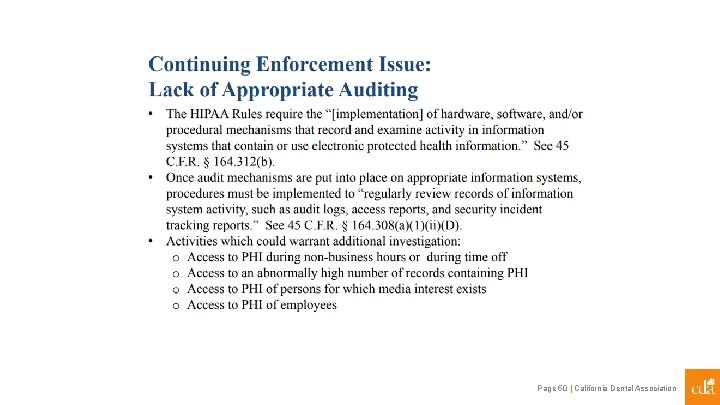
Page 50 | California Dental Association
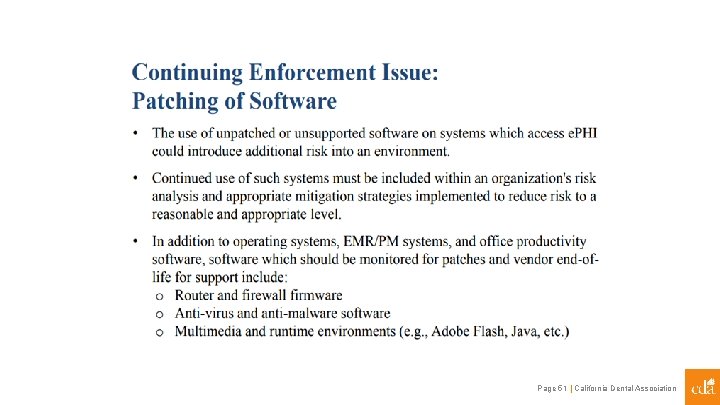
Page 51 | California Dental Association
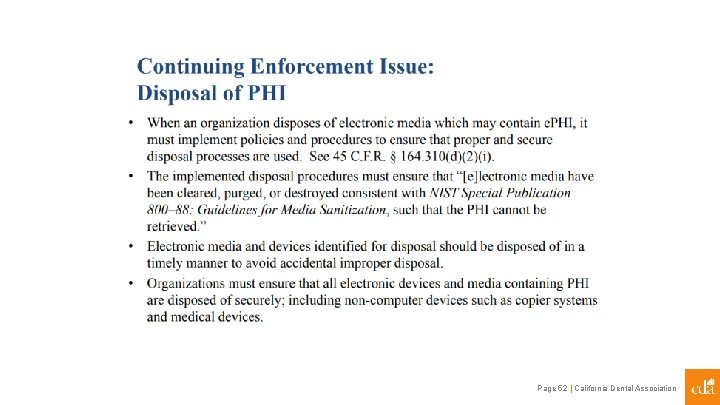
Page 52 | California Dental Association
Proof of Compliance 1. Privacy and security officials designated to manage efforts to safeguard PHI. 2. Risk analysis (of threats and vulnerabilities) conducted and is periodically updated. 3. Risk mitigation strategies identified and safeguards and policies and procedures are based on risk analysis findings. 4. Workforce trained on safeguards and policies and procedures. 5. Sanctions are applied for violations of policies and procedures. 6. Required documentation is complete. Page 53 | California Dental Association
HIPAA Audits HITECH instituted periodic audits for HIPAA compliance. Audits are used to: • Assess compliance efforts largely through desk audits. In-person audits occur less often. • Identify compliance best practices and discover risks that may not have been identified through the HIPAA complaint process. • Aid development of guidance and technical assistance. Serious compliance issues will be investigated. Initial contact with a covered entity is through a letter or email. HHS OCR has not yet implemented regular audits following completion of the 2016 outreach. See https: //www. hhs. gov/hipaa/for-professionals/complianceenforcement/audit/index. html. Page 54 | California Dental Association
Compliance and Training Resources Page 55 | California Dental Association
The Laws Combined text of all HIPAA Rules (45 CFR Parts 160, 162 and 164) https: //www. hhs. gov/hipaa/for-professionals/privacy/lawsregulations/combined-regulation-text/index. html California Confidentiality of Medical Information Act (Civil Code § 56 et seq) http: //leginfo. legislature. ca. gov/faces/codes_displayexpandedbranch. xhtml ? toc. Code=CIV&division=1. &title=&part=2. 6. &chapter=&article= California Breach Notification (Civil Code § 1798. 82) https: //leginfo. legislature. ca. gov/faces/codes_display. Section. xhtml? law. Cod e=CIV§ion. Num=1798. 82 Page 56 | California Dental Association
Page 57 | California Dental Association
https: //www. hhs. gov/hipaa/for-professionals/privacy/guidance/index. html Page 58 | California Dental Association
https: //www. hhs. gov/hipaa/for-professionals/security/guidance/index. html Page 59 | California Dental Association
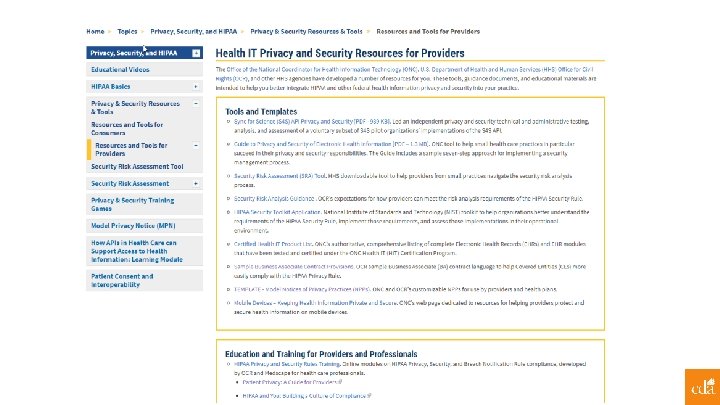
Health. IT. gov https: //www. healthit. gov/topic/privacy-security-and-hipaa Page 60 | California Dental Association
Page 61 | California Dental Association
Source: U. S. Department of Homeland Security, National Cybersecurity Month Awareness Poster Page 62 | California Dental Association
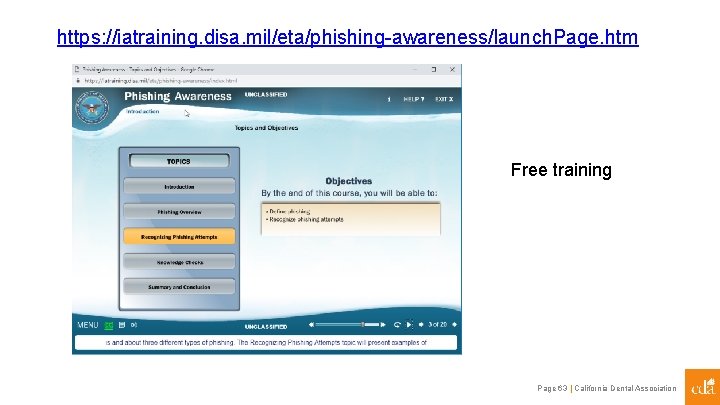
https: //iatraining. disa. mil/eta/phishing-awareness/launch. Page. htm Free training Page 63 | California Dental Association
You. Tube is a resource for educational videos Page 64 | California Dental Association
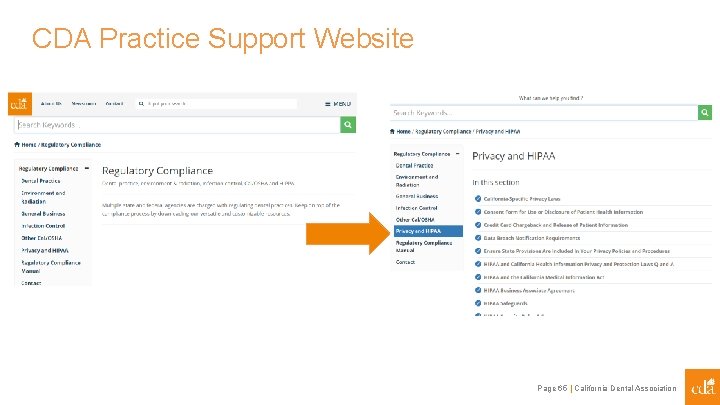
CDA Practice Support Website Page 65 | California Dental Association
CDA Practice Support is here to help you! Find at cda. org/practicesupport: • Business Associate Security Questionnaire • HIPAA Business Associate Agreement • Sample Notice of Privacy Practices • More HIPAA resources Or contact us with your questions 800. 232. 7645 | practicesupport@cda. org Page 66 | California Dental Association